Category Archives: Vulristics

May Microsoft Patch Tuesday

May Microsoft Patch Tuesday

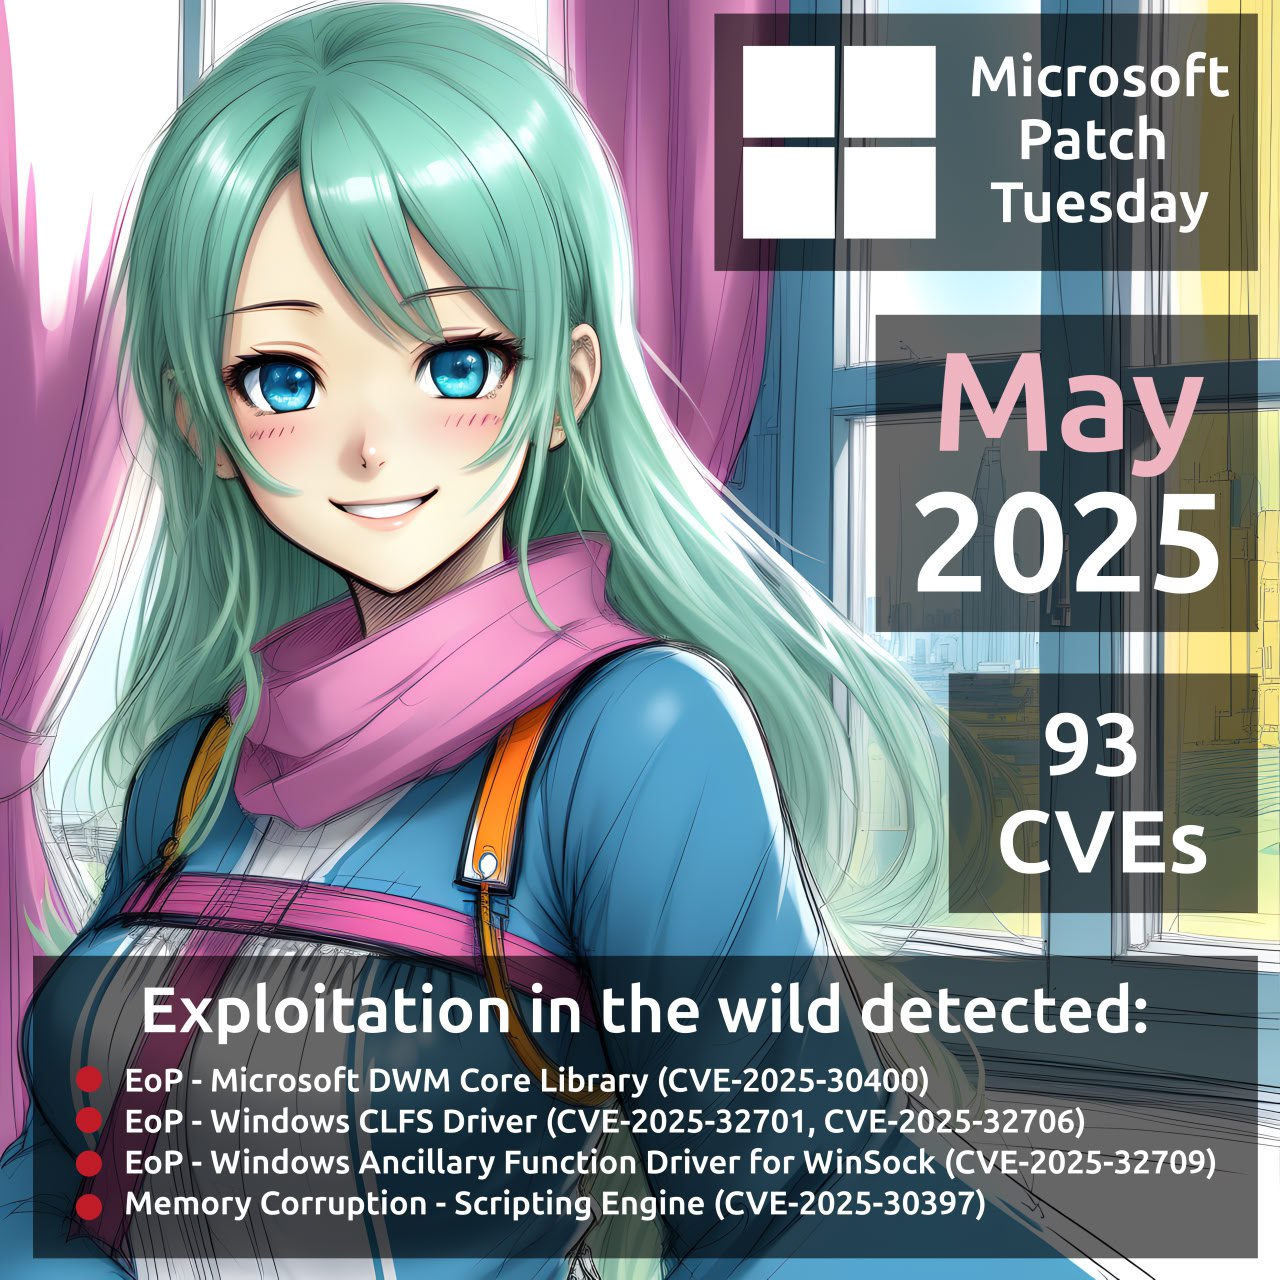
May Microsoft Patch Tuesday. A total of 93 vulnerabilities - about 1.5 times fewer than in April. Of these, 22 were added between the April and May MSPT. There are 5 vulnerabilities show signs of in-the-wild exploitation:

🔻 EoP - Microsoft DWM Core Library (CVE-2025-30400)
🔻 EoP - Windows CLFS Driver (CVE-2025-32701, CVE-2025-32706)
🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2025-32709)
🔻 Memory Corruption - Scripting Engine (CVE-2025-30397). RCE when clicking a malicious link. Exploitation requires the "Allow sites to be reloaded in Internet Explorer" option.

There are currently no vulnerabilities with public exploits.

Notable among the rest:

🔹 RCE - Remote Desktop Client (CVE-2025-29966, CVE-2025-29967), Office (CVE-2025-30377, CVE-2025-30386), Graphics Component (CVE-2025-30388), Visual Studio (CVE-2025-32702)
🔹 EoP - Kernel Streaming (CVE-2025-24063), CLFS Driver (CVE-2025-30385)
🗒 Full Vulristics report

На русском

April Linux Patch Wednesday

April Linux Patch Wednesday

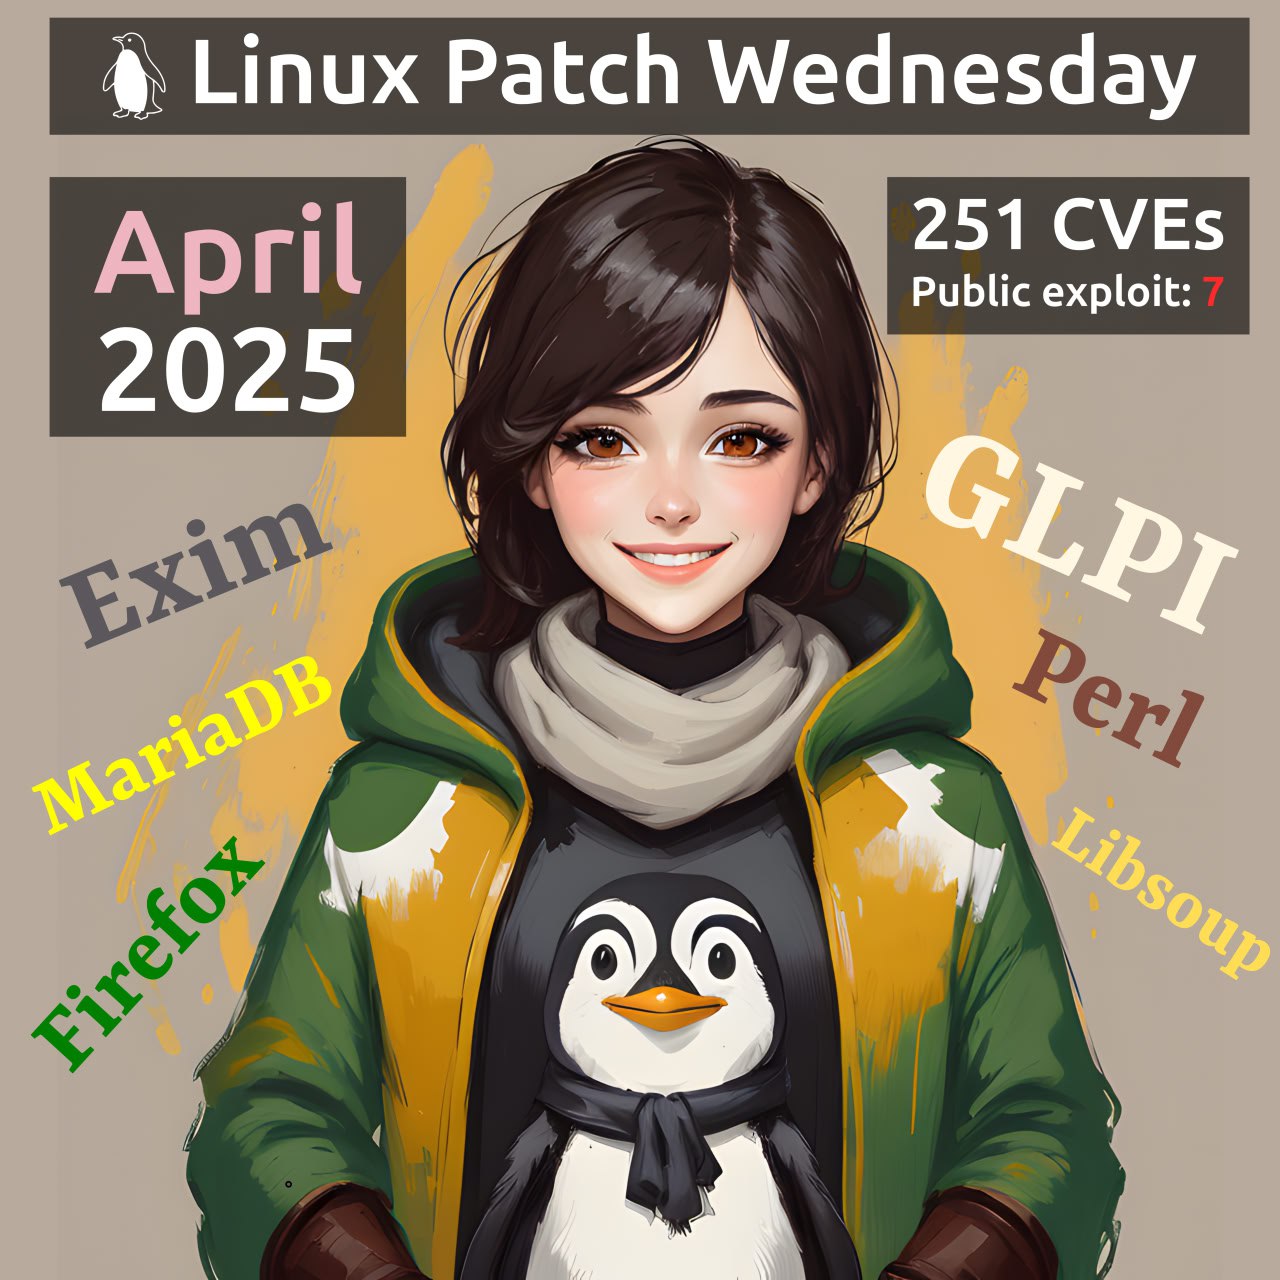
April Linux Patch Wednesday. Total vulnerabilities: 251. 👌 164 in the Linux Kernel. No vulnerabilities show signs of being exploited in the wild. There are 7 vulnerabilities that appear to have publicly available exploits.

For 2 vulnerabilities, exploit code with detailed explanation is available on GitHub. Both were first patched in RedOS packages:

🔸 SQL injection - Exim (CVE-2025-26794)
🔸 Code Injection - MariaDB (CVE-2023-39593)

For the Memory Corruption - Mozilla Firefox (CVE-2025-3028), the NVD states the exploit code is in Mozilla’s bug tracker, but access is restricted. 🤷‍♂️

BDU FSTEC reports public exploits for 4 vulnerabilities:

🔸 Information Disclosure - GLPI (CVE-2025-21626)
🔸 Security Feature Bypass - GLPI (CVE-2025-23024)
🔸 Denial of Service / Remote Code Execution - Perl (CVE-2024-56406)
🔸 Memory Corruption - Libsoup (CVE-2025-32050)

🗒 Full Vulristics report

На русском

April Microsoft Patch Tuesday

April Microsoft Patch Tuesday

April Microsoft Patch Tuesday. A total of 153 vulnerabilities, 2 times more than in March. Of these, 32 were added between the March and April MSPTs. Three vulnerabilities show signs of exploitation in the wild:

🔻 EoP - Windows Common Log File System Driver (CVE-2025-29824). An attacker can gain SYSTEM privileges. No technical details yet.
🔻 SFB - Microsoft Edge (CVE-2025-2783). Sandbox escape with an existing PoC exploit.
🔻 RCE - Microsoft Edge (CVE-2025-24201). Originally reported as a WebKit vuln on Apple OSes. 🤷‍♂️

Microsoft also patched vulnerabilities in Kubernetes with known exploits (CVE-2025-1974, CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, CVE-2025-24513)

Other notable ones:

🔹 RCE - LDAP (CVE-2025-26670, CVE-2025-26663), TCP/IP (CVE-2025-26686), Microsoft Office (CVE-2025-29794, CVE-2025-29793), RDS (CVE-2025-27480, CVE-2025-27482), Hyper-V (CVE-2025-27491)
🔹 SFB - Kerberos (CVE-2025-29809)

🗒 Full Vulristics report

На русском

March Linux Patch Wednesday

March Linux Patch Wednesday

March Linux Patch Wednesday. Total vulnerabilities: 1083. 😱 879 in the Linux Kernel. 🤦‍♂️ Two vulnerabilities show signs of exploitation in the wild:

🔻 Code Injection - GLPI (CVE-2022-35914). An old vulnerability from CISA KEV, but first patched on March 3 in RedOS Linux.
🔻 Memory Corruption - Safari (CVE-2025-24201). Fixed in WebKitGTK packages in Linux repositories.

There are 19 vulnerabilities with publicly available exploits. Notable ones:

🔸 Remote Code Execution - Apache Tomcat (CVE-2025-24813)
🔸 Command Injection - SPIP (CVE-2024-8517)
🔸 Memory Corruption - Assimp (CVE-2025-2152)
🔸 Memory Corruption - libxml2 (CVE-2025-27113)

The Elevation of Privilege vulnerability in the Linux Kernel (CVE-2022-49264) has no public exploit yet. However, it resembles well-known PwnKit (CVE-2021-4034).

🗒 Full Vulristics report

На русском

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday. 77 CVEs, 20 of which were added during the month. 7 vulnerabilities with signs of exploitation in the wild:

🔻 RCE - Windows Fast FAT File System Driver (CVE-2025-24985)
🔻 RCE - Windows NTFS (CVE-2025-24993)
🔻 SFB - Microsoft Management Console (CVE-2025-26633)
🔻 EoP - Windows Win32 Kernel Subsystem (CVE-2025-24983)
🔻 InfDisc - Windows NTFS (CVE-2025-24991, CVE-2025-24984)
🔻 AuthBypass - Power Pages (CVE-2025-24989) - in Microsoft web service, can be ignored

There are no vulnerabilities with public exploits, there are 2 more with private ones:

🔸 RCE - Bing (CVE-2025-21355) - in Microsoft web service, can be ignored
🔸 SFB - Windows Kernel (CVE-2025-21247)

Among the others:

🔹 RCE - Windows Remote Desktop Client (CVE-2025-26645) and Services (CVE-2025-24035, CVE-2025-24045), MS Office (CVE-2025-26630), WSL2 (CVE-2025-24084)
🔹 EoP - Windows Win32 Kernel Subsystem (CVE-2025-24044)

🗒 Full Vulristics report

На русском

February Linux Patch Wednesday

February Linux Patch Wednesday

February Linux Patch Wednesday. There are 561 vulnerabilities in total. 338 in Linux Kernel. Formally, there is one vulnerability with a sign of exploitation in the wild: RCE - 7-Zip (CVE-2025-0411). But it is about Windows MoTW and, naturally, is not exploitable on Linux.

There are public exploits for 21 vulnerabilities.

Among them there are 5 Cacti vulnerabilities:

🔸 RCE - Cacti (CVE-2025-24367)
🔸 Command Injection - Cacti (CVE-2025-22604)
🔸 SQLi - Cacti (CVE-2024-54145, CVE-2025-24368)
🔸 Path Traversal - Cacti (CVE-2024-45598)

2 OpenSSH vulnerabilities discovered by Qualys:

🔸 DoS - OpenSSH (CVE-2025-26466)
🔸 Spoofing/MiTM - OpenSSH (CVE-2025-26465)

Of the rest, the most interesting are:

🔸 RCE - Langchain (CVE-2023-39631), Snapcast (CVE-2023-36177), Checkmk (CVE-2024-13723),
🔸 EoP - Linux Kernel (CVE-2024-50066)
🔸 SQLi - PostgreSQL (CVE-2025-1094)
🔸 XSS - Checkmk (CVE-2024-13722), Thunderbird (CVE-2025-1015)

🗒 Full Vulristics report

На русском

February Microsoft Patch Tuesday

February Microsoft Patch Tuesday

February Microsoft Patch Tuesday. 89 CVEs, 33 added since January. Two with signs of exploitation in the wild:

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2025-21418)
🔻 EoP - Windows Storage (CVE-2025-21391)

There are no vulnerabilities with public exploits, but there are 7 with private ones:

🔸 RCE - Microsoft Edge (CVE-2025-21279, CVE-2025-21283)
🔸 Auth. Bypass - Azure (CVE-2025-21415)
🔸 EoP - Windows Setup Files Cleanup (CVE-2025-21419)
🔸 Spoofing - Windows NTLM (CVE-2025-21377)
🔸 Spoofing - Microsoft Edge (CVE-2025-21267, CVE-2025-21253)

Among the rest, the following can be highlighted:

🔹 RCE - Windows LDAP (CVE-2025-21376), Microsoft Excel (CVE-2025-21381, CVE-2025-21387), Microsoft SharePoint Server (CVE-2025-21400), DHCP Client Service (CVE-2025-21379)
🔹 EoP - Windows Core Messaging (CVE-2025-21184, CVE-2025-21358, CVE-2025-21414), Windows Installer (CVE-2025-21373)

🗒 Full Vulristics report

На русском