The Vulners team has introduced a new AI-powered product - Cube

The Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - Cube

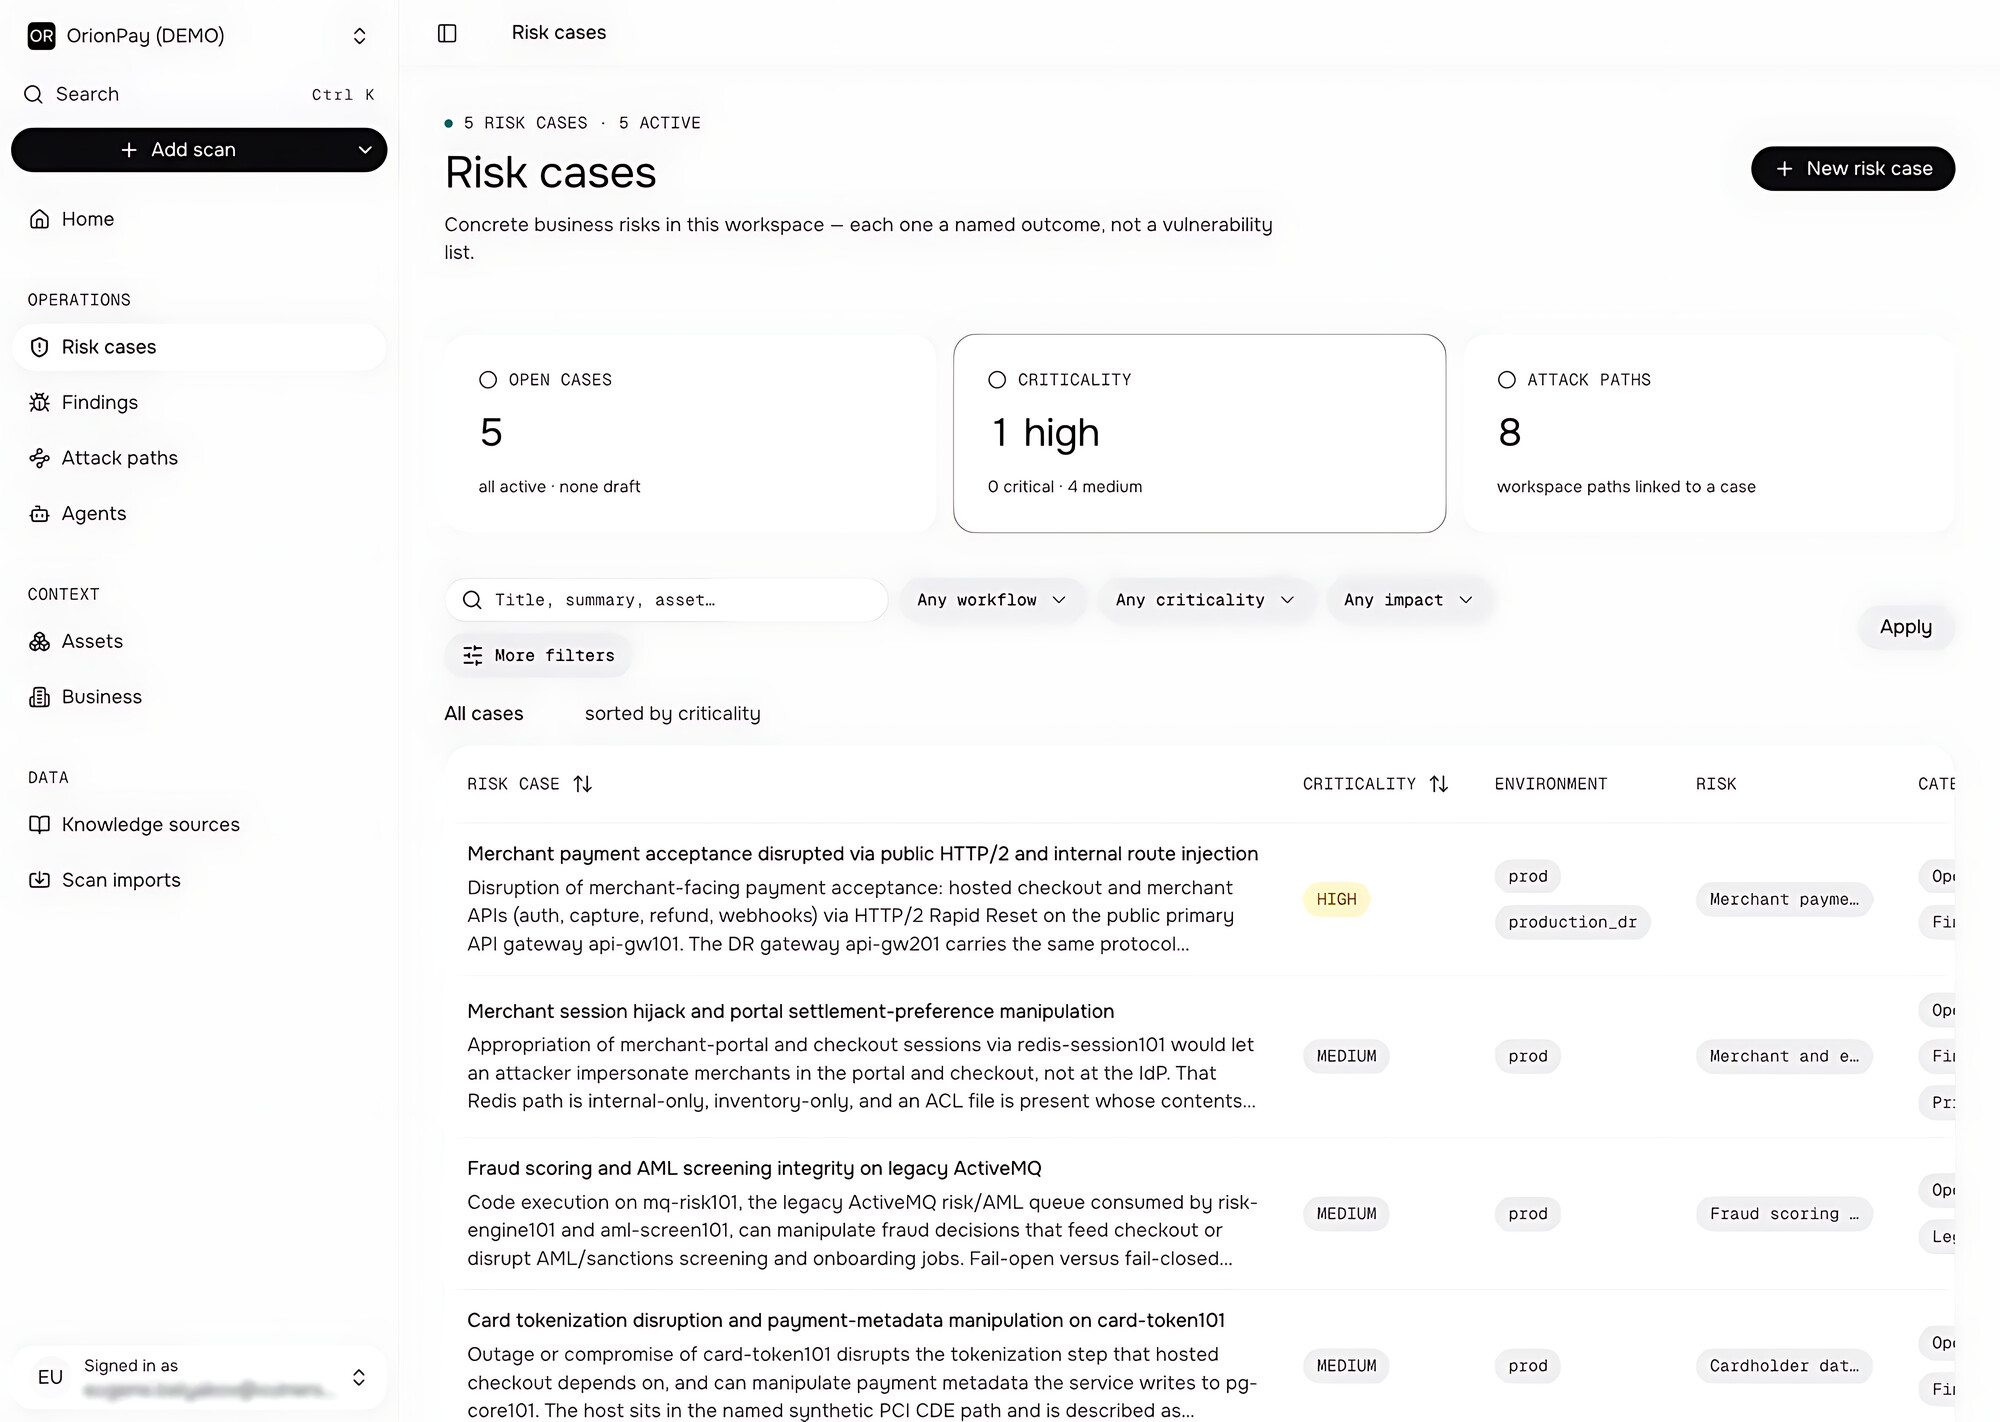
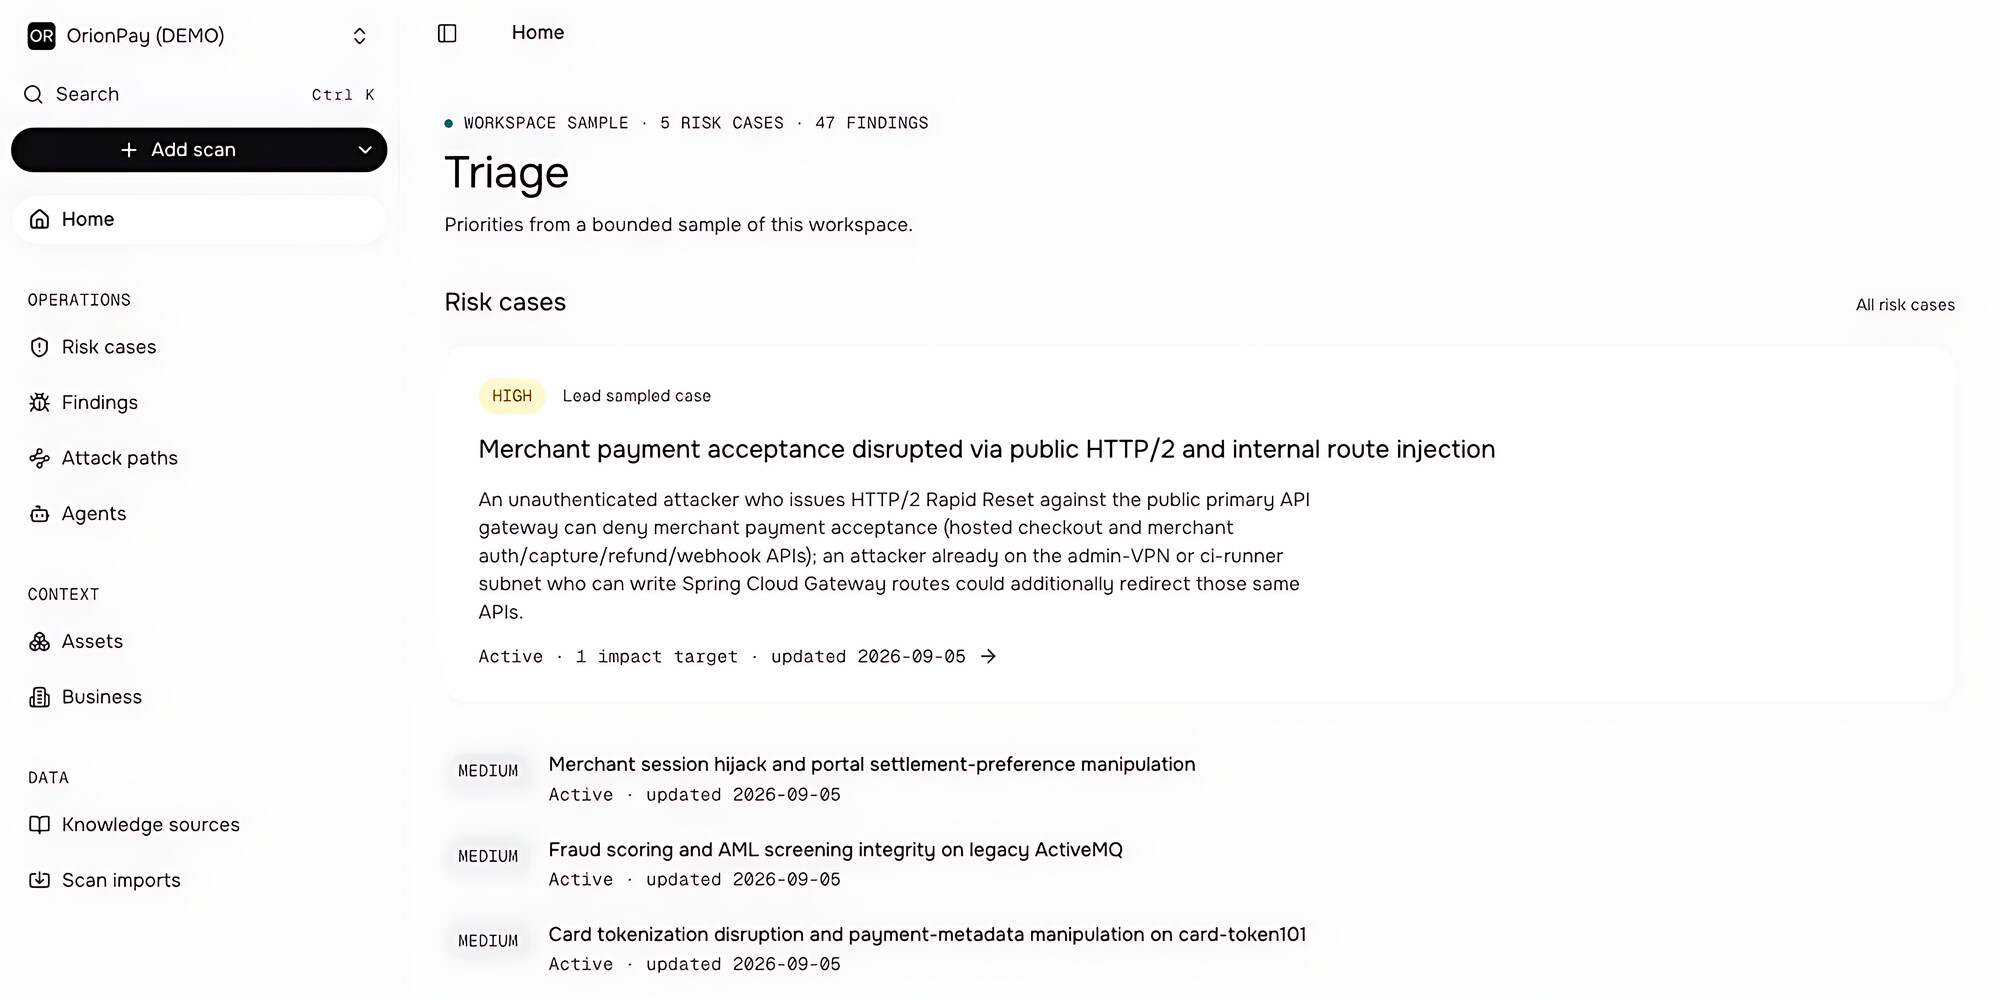
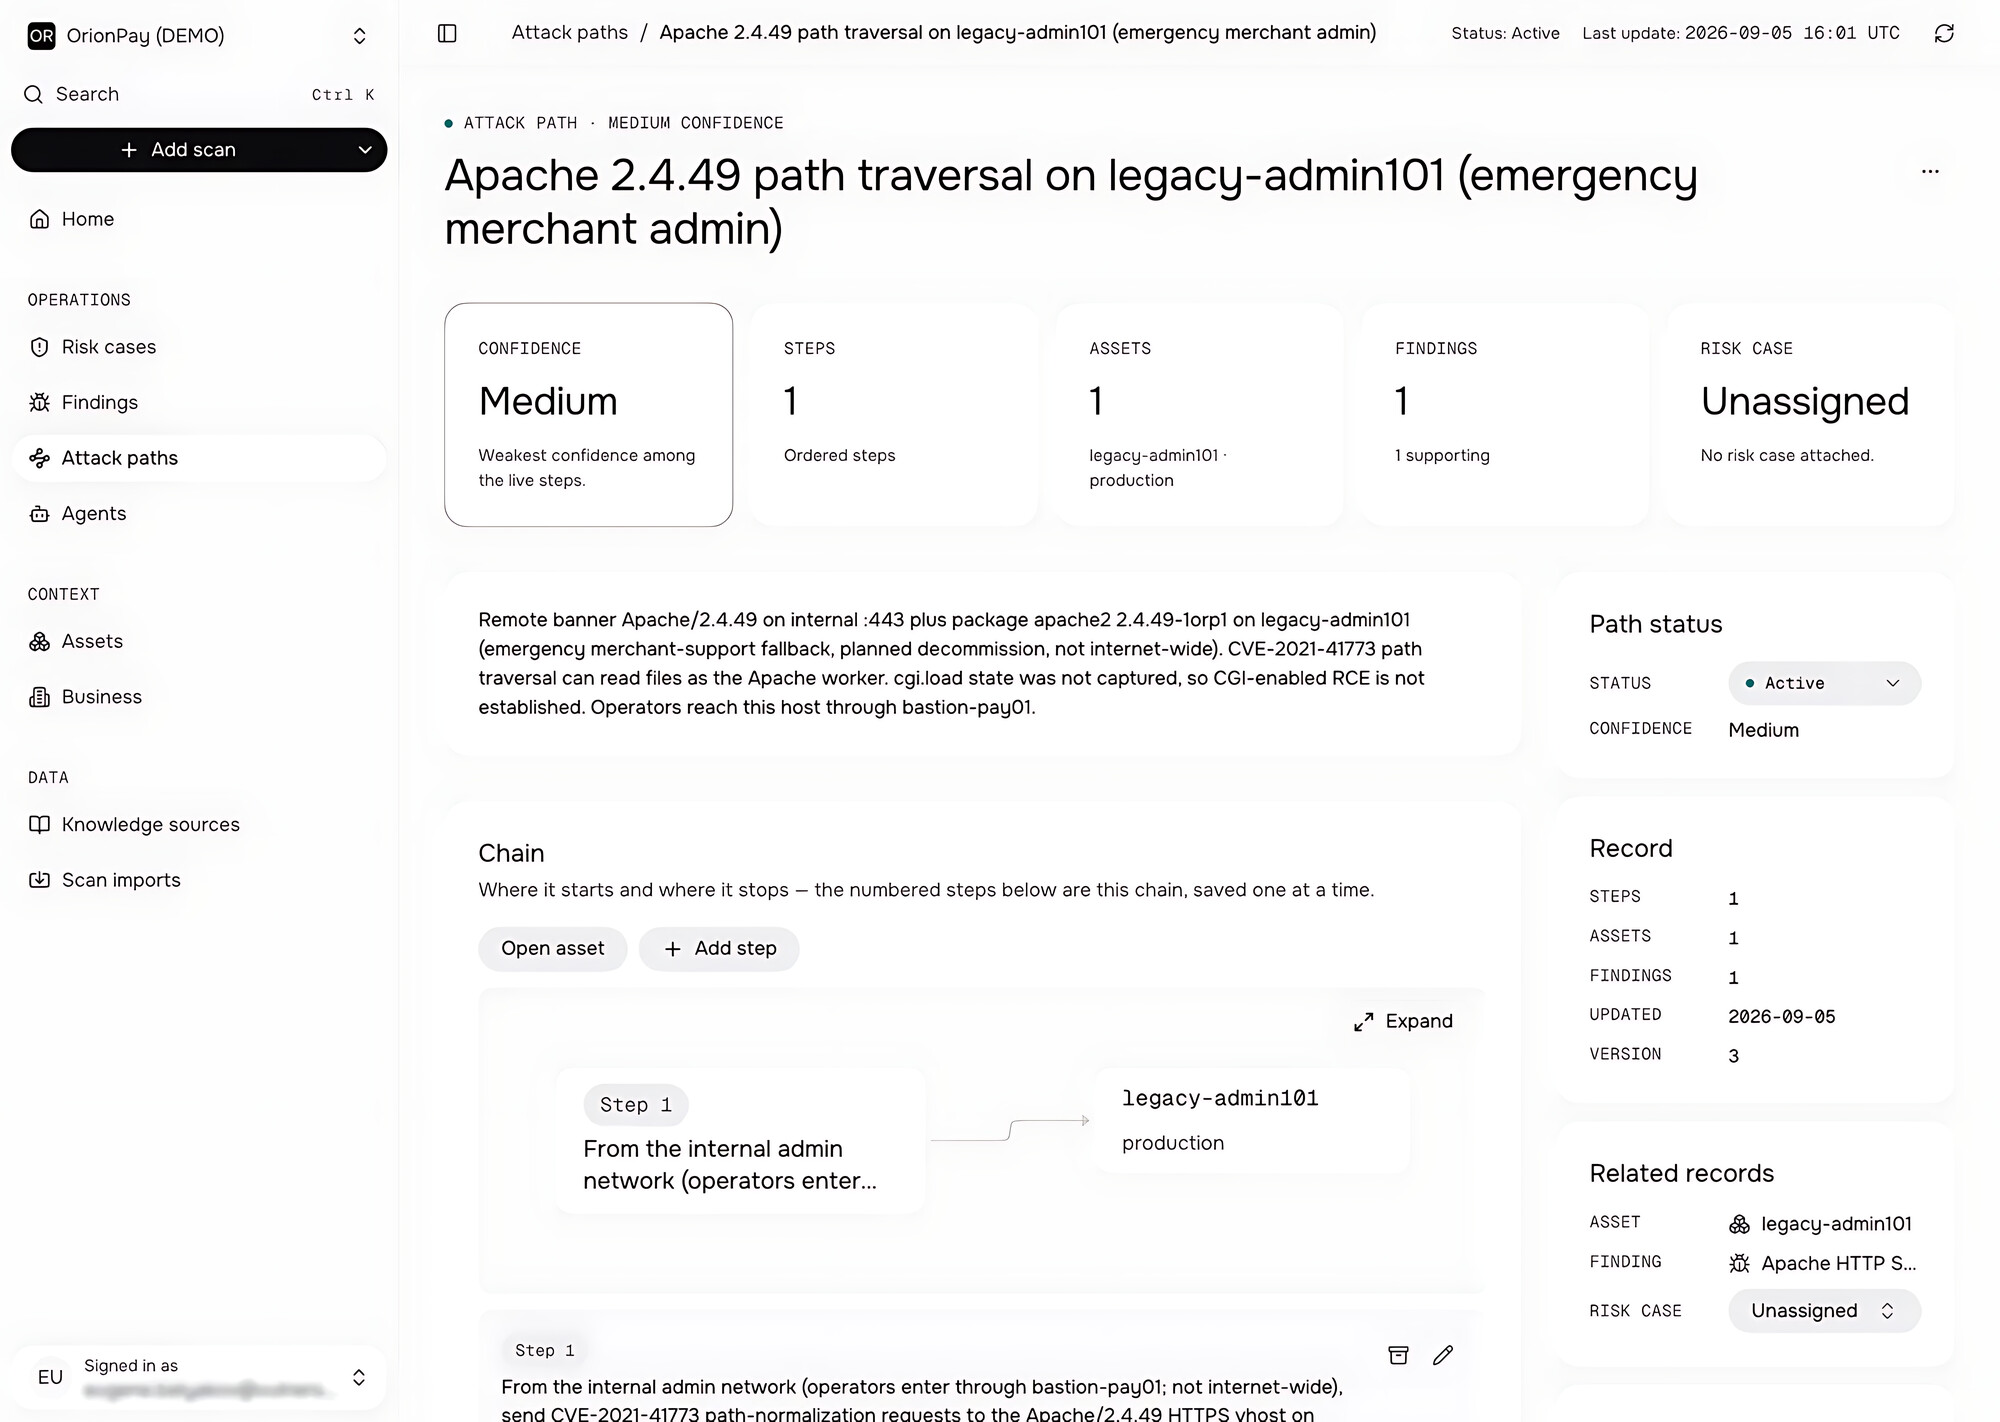
The Vulners team has introduced a new AI-powered product - Cube. The platform provides contextual analysis of vulnerability scan results, correlating technical findings with information about an organization's infrastructure and business processes.

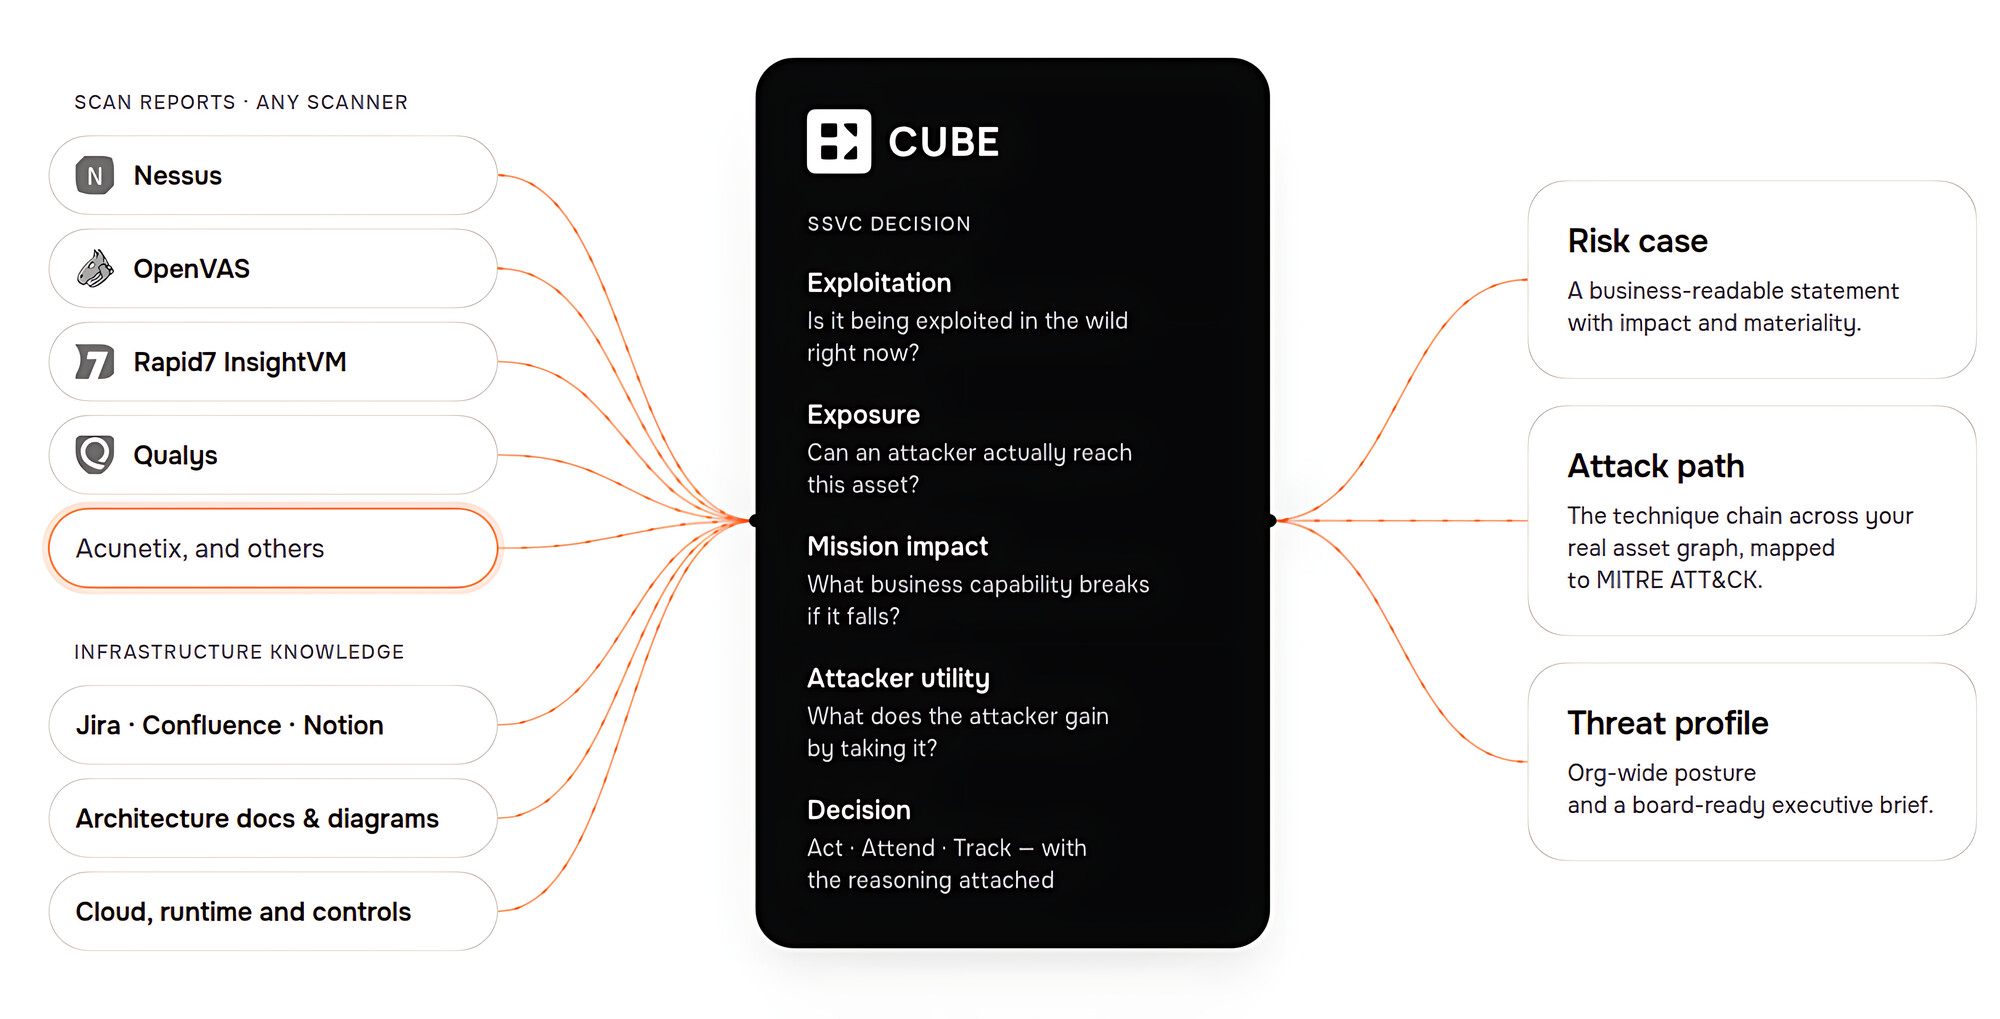
Cube is built around three core layers:

📥 Evidence Layer - collects reports from existing vulnerability scanners, including Nessus, OpenVAS, Qualys, Rapid7 InsightVM, Acunetix, and others. It processes the findings and maps them to actual infrastructure assets.

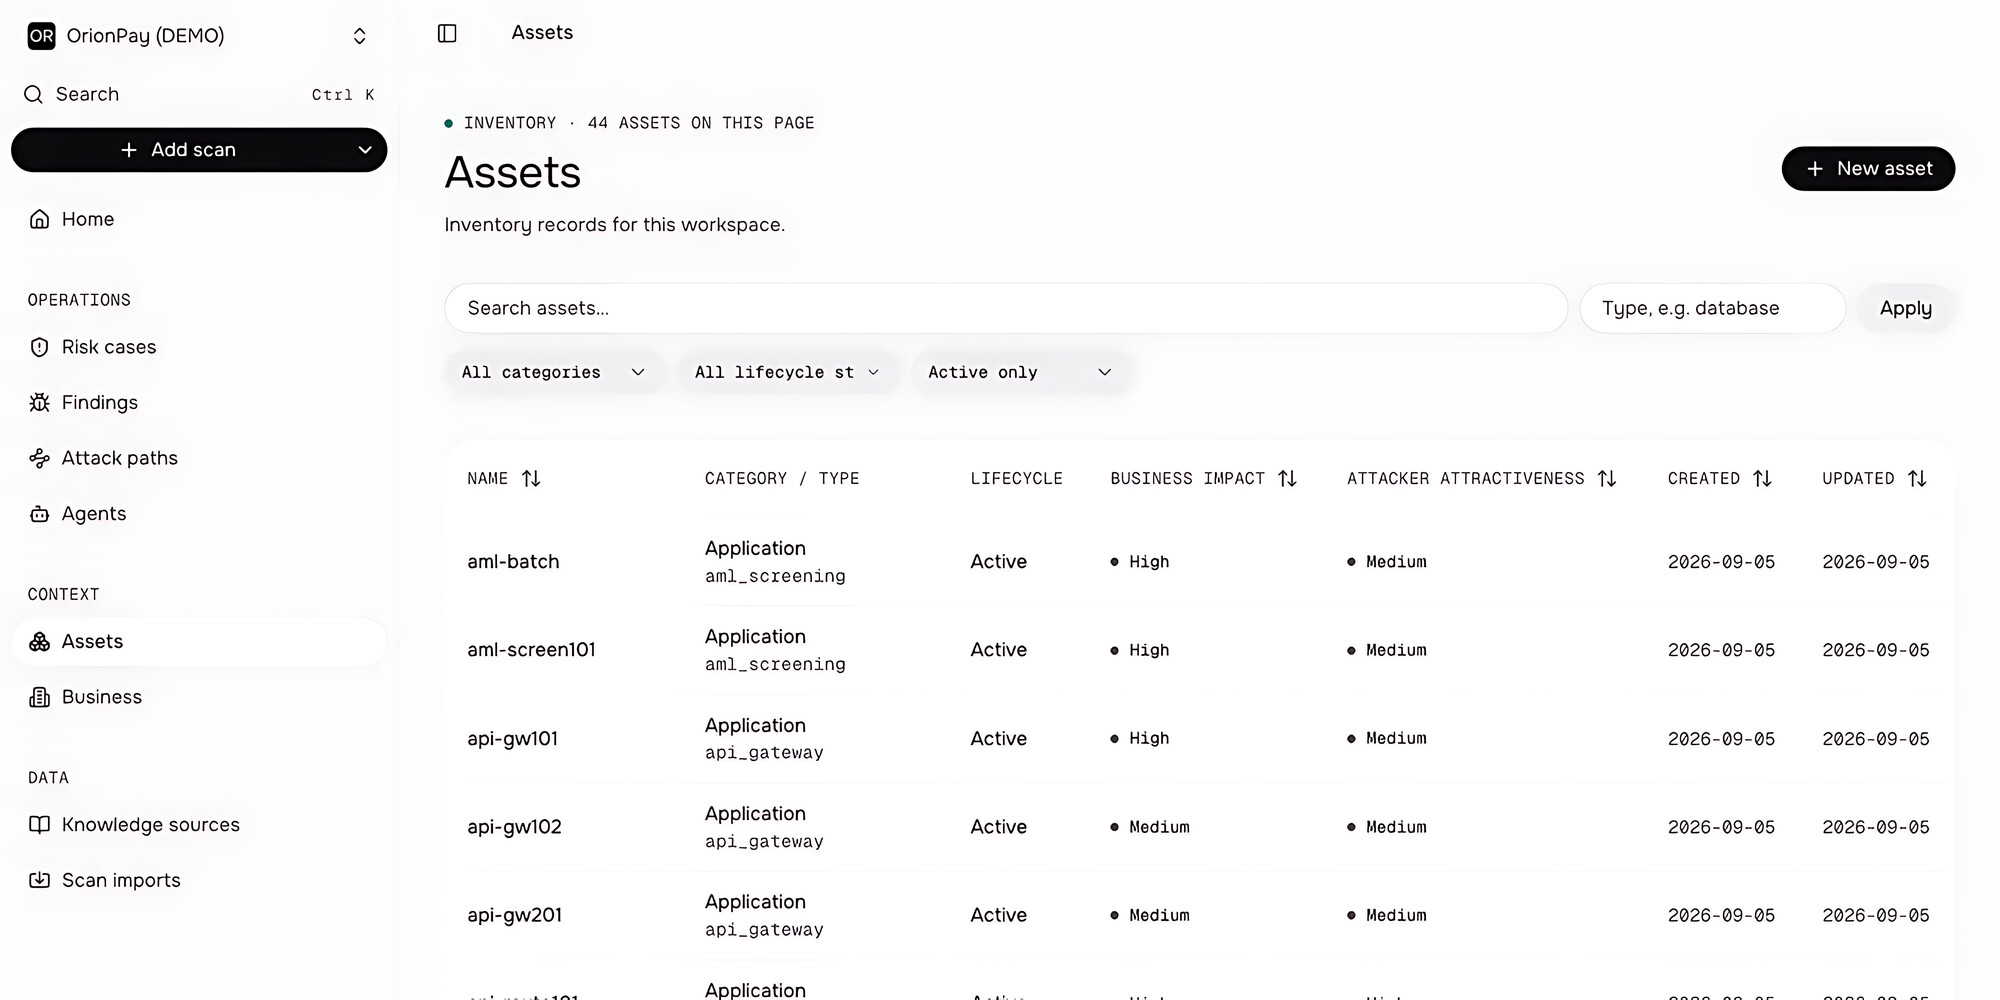
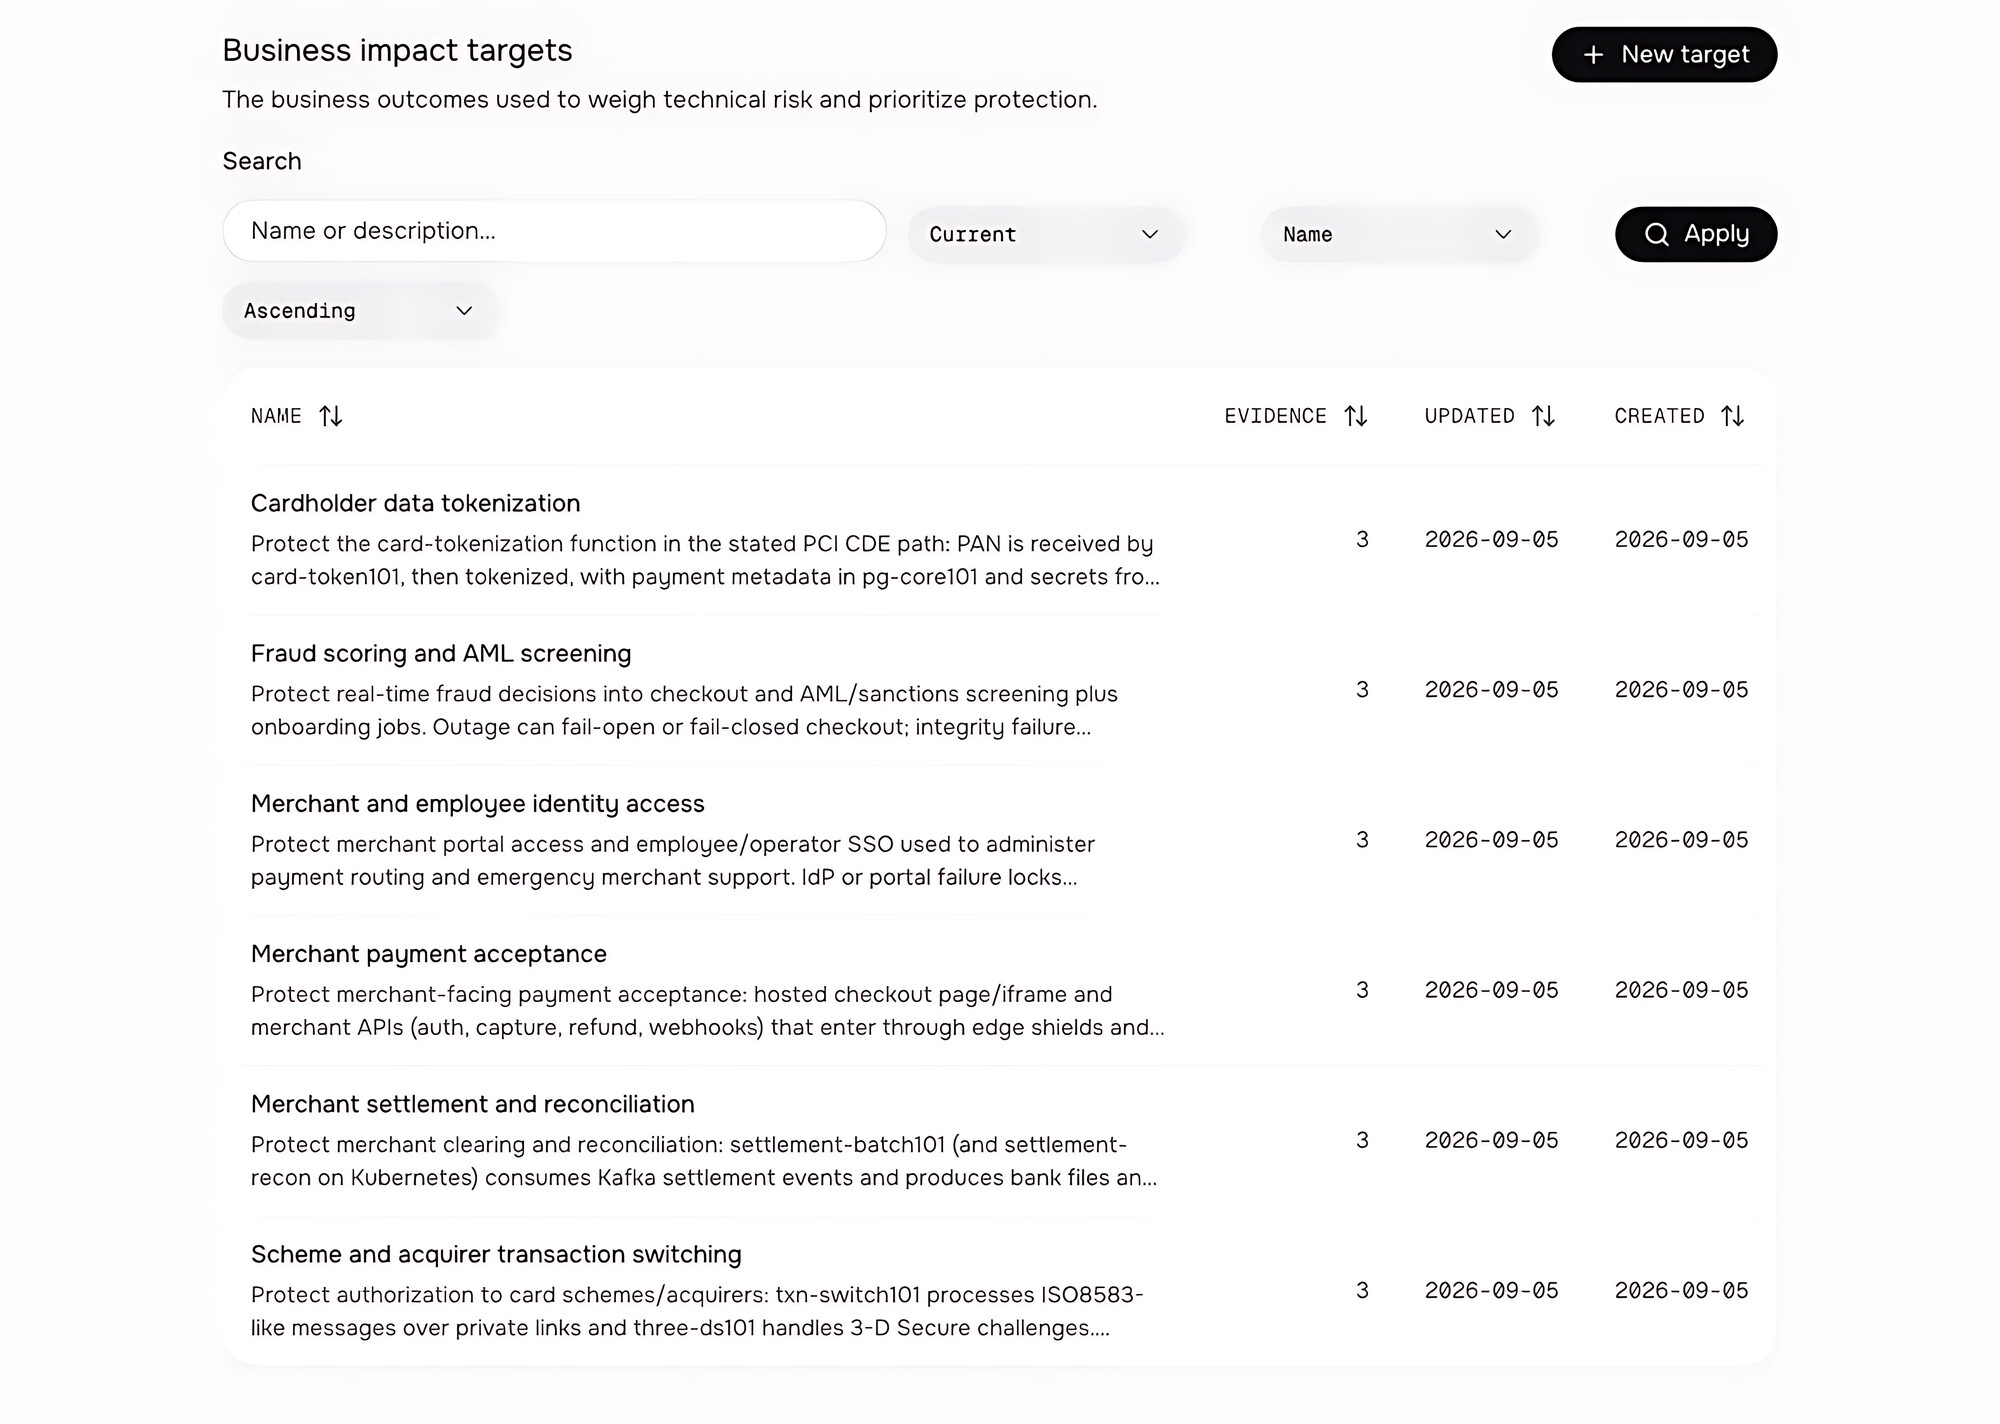
🗺️ Context Layer - enriches scan results with infrastructure data from architectural documentation, diagrams, task tracker tickets, cloud environments, and business processes. It builds a contextual model of the infrastructure, including a CMDB and network graph, helping identify affected assets, evaluate their exposure, and understand their role in business operations.

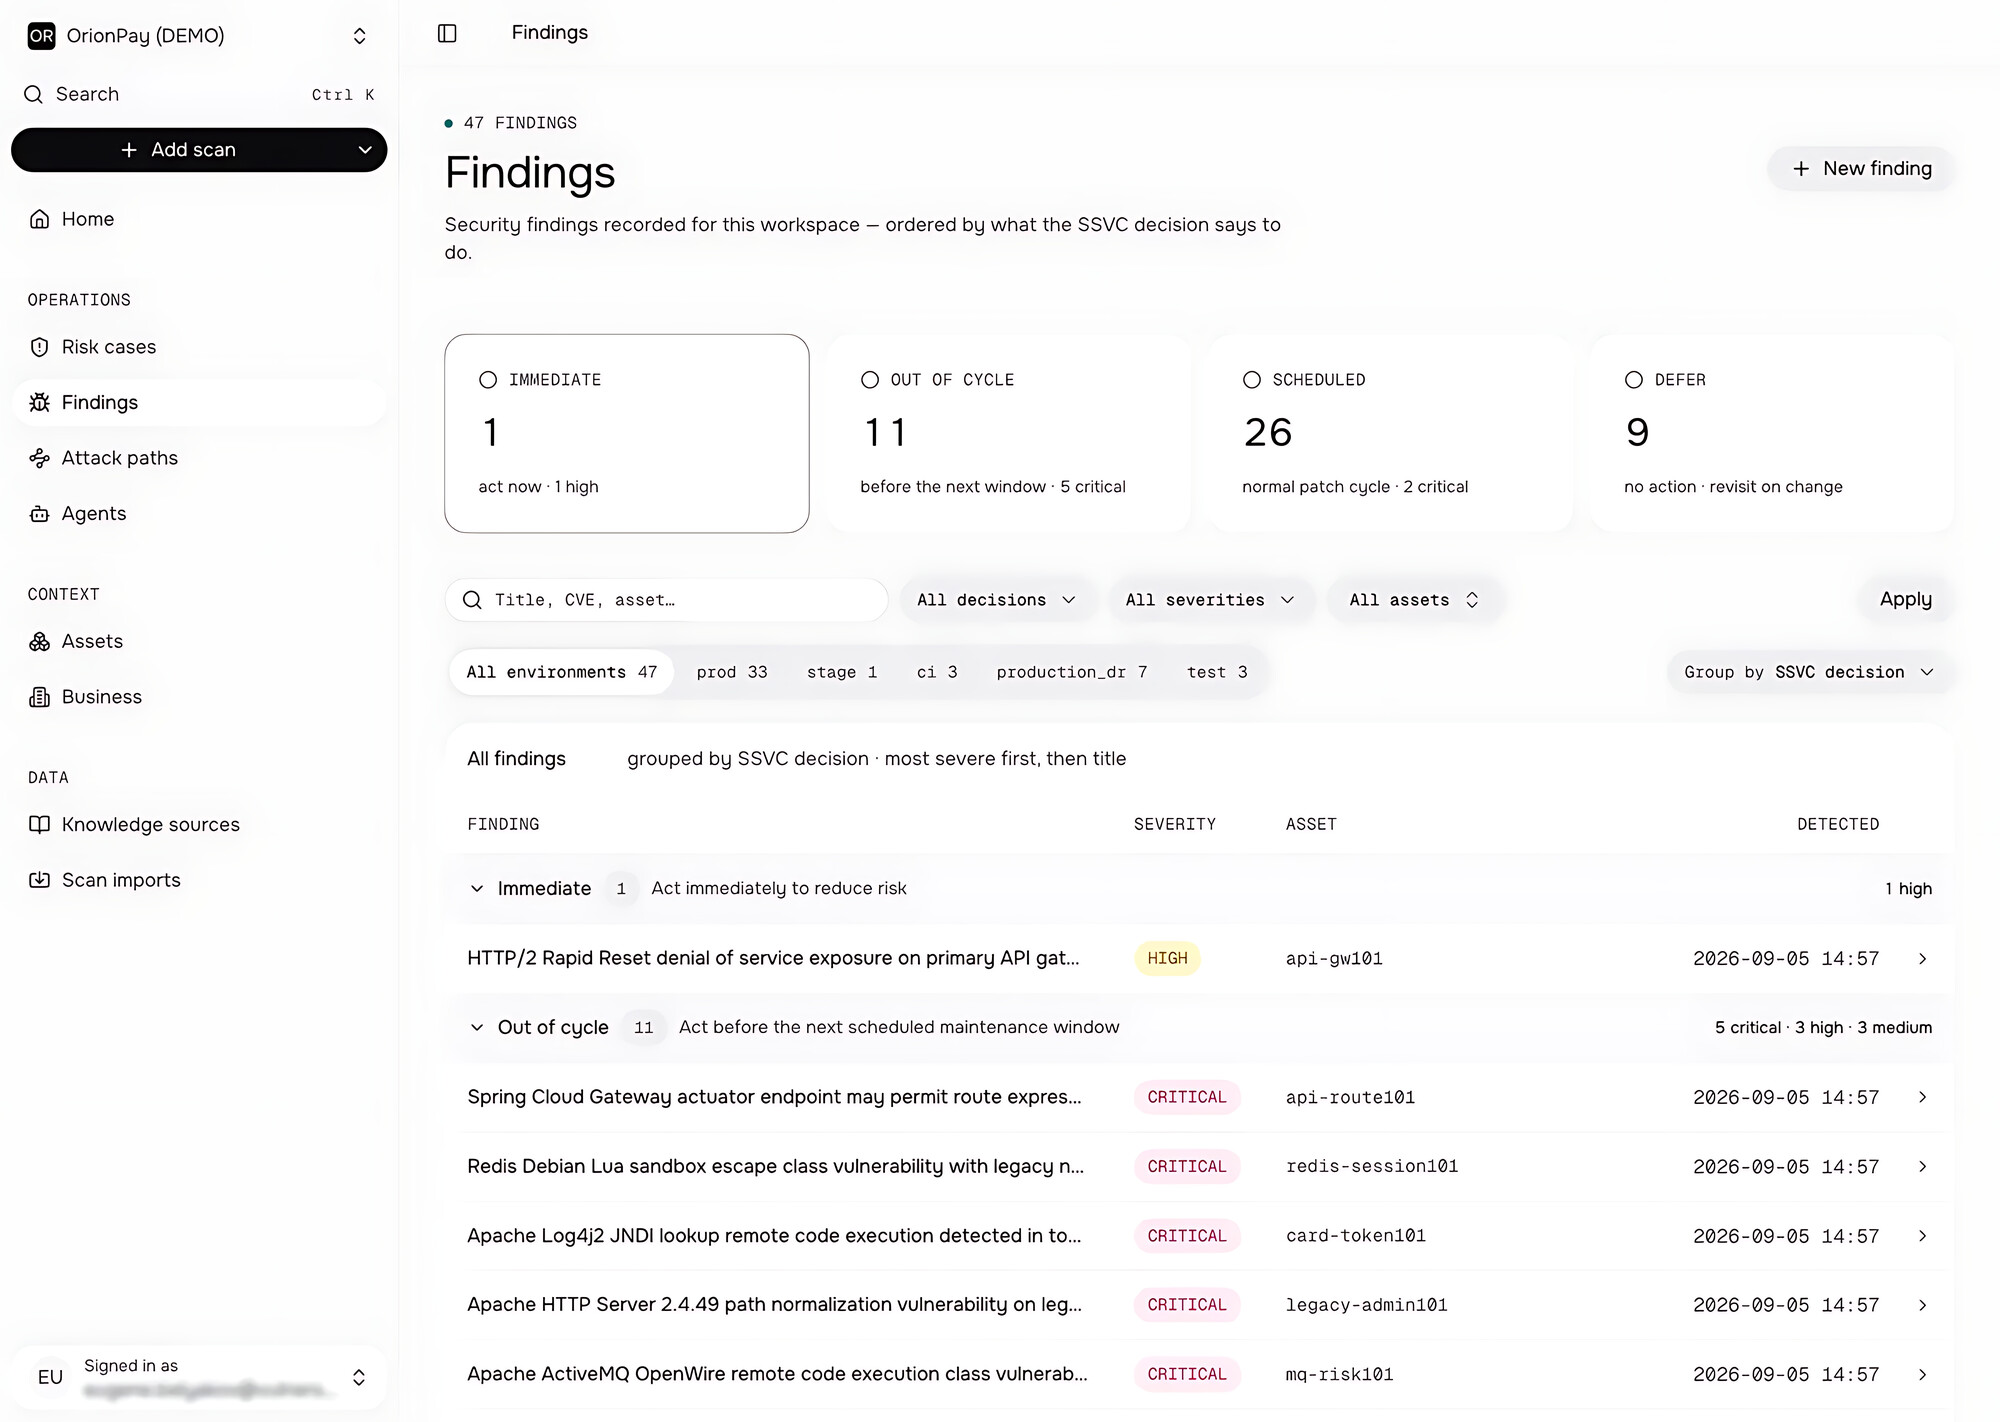
🧠 Decision Layer - uses the CISA SSVC (Stakeholder-Specific Vulnerability Categorization) methodology to prioritize remediation efforts. Unlike CVSS, which focuses on the technical severity of vulnerabilities, SSVC uses a decision tree that takes exploitation conditions and potential business impact into account.

The CISA SSVC model defines four possible decision outcomes:

🟢 Track - vulnerability remediation follows the standard Vulnerability Management process. The vulnerability is monitored and addressed according to standard software update timelines.

🟡 Track* - the vulnerability requires closer monitoring, with its assessment revisited as new information or circumstances emerge.

🟠 Attend - the vulnerability requires increased attention from security teams and relevant management. This may involve bringing in additional experts and notifying key stakeholders. Remediation should be accelerated.

🔴 Act - the vulnerability requires escalation to senior management, with response efforts coordinated across departments. A coordinated action plan is developed, the necessary stakeholders are engaged, and remediation is carried out as soon as possible.

SSVC therefore determines not only which vulnerabilities should be addressed first, but also the level of organizational response required to address them.

Cube provides users with several types of results:

🎯 Risk Cases - grouped findings accompanied by severity ratings and assessments of potential business impact.

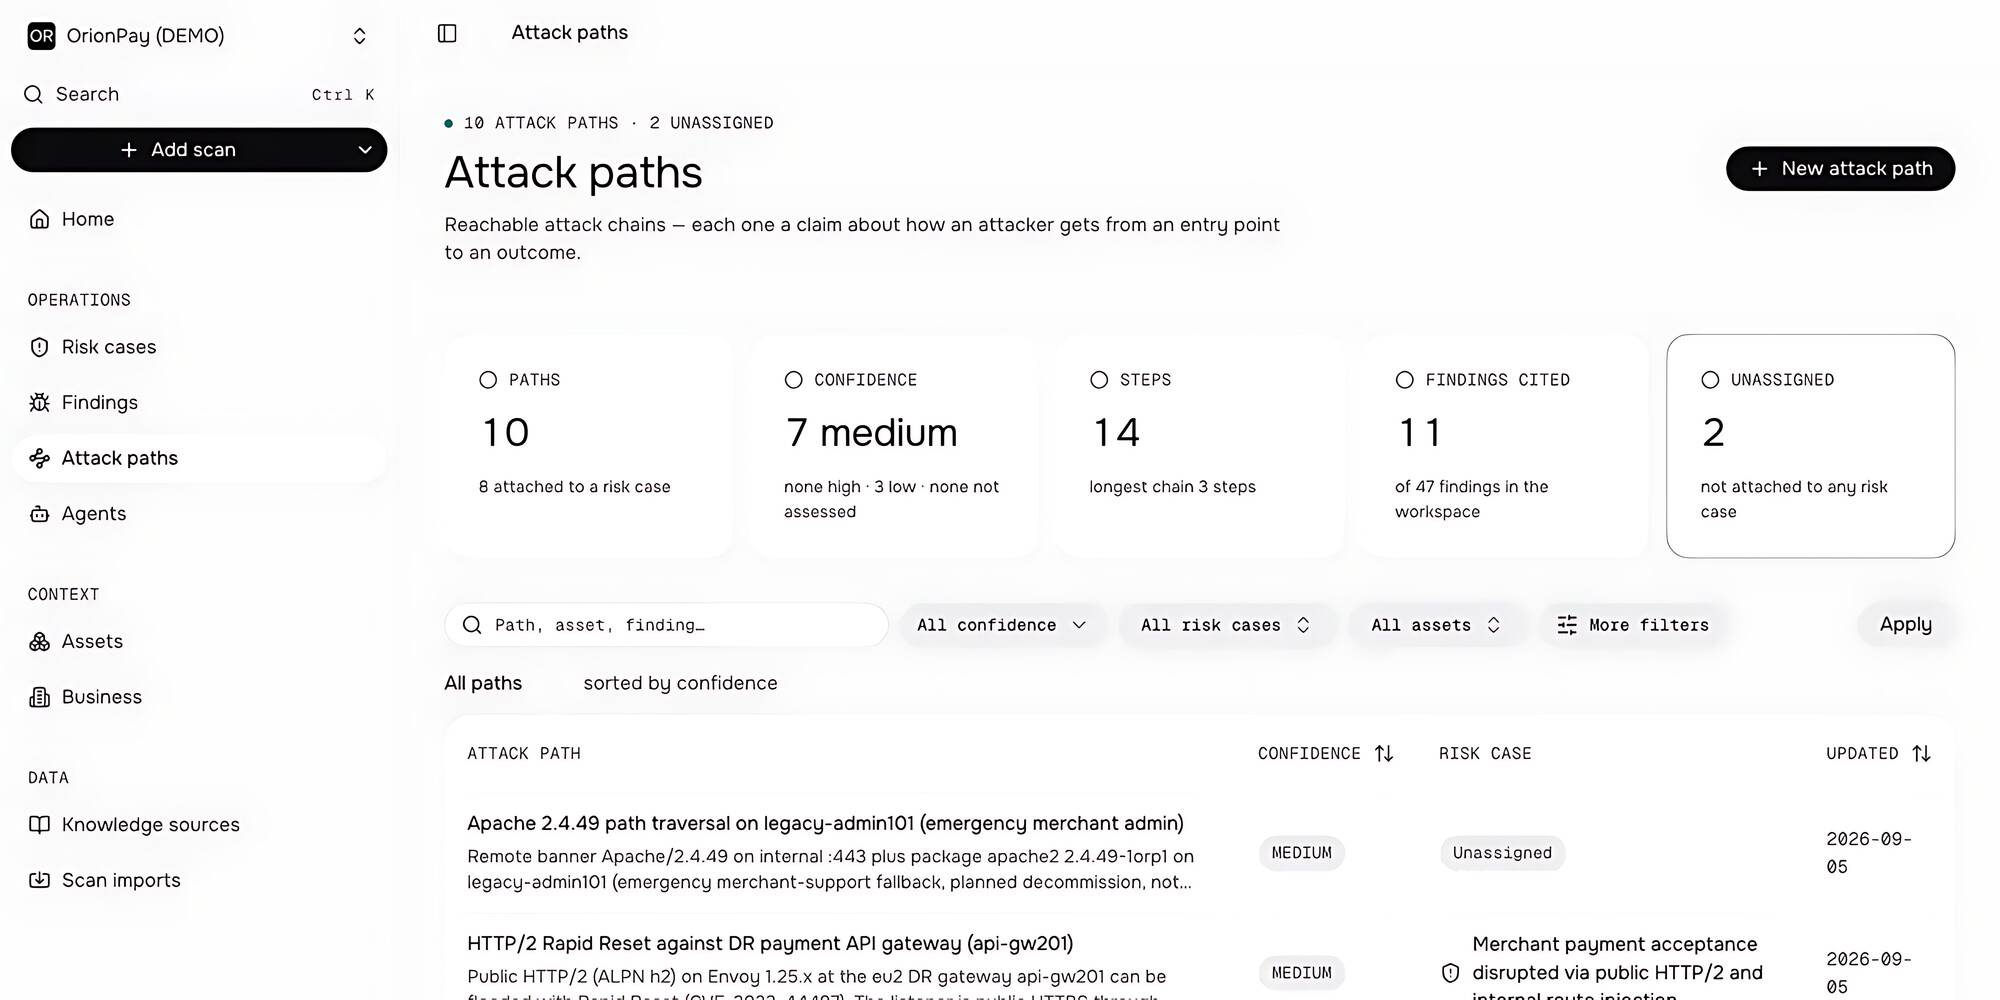
🛤️ Attack Paths - potential attack paths between assets, aligned with the MITRE ATT&CK framework.

🛡️ Threat Profile - an overview of the threat landscape and the current state of the infrastructure.

📋 Decision Rationale - explanations of decisions, linked to the original reports, assessments, and infrastructure data.

For example, a vulnerability with a CVSS score of 9.8 on an isolated internal build server may be assigned a lower priority than a vulnerability with a CVSS score of 7.5 on a publicly accessible payment gateway. In the latter case, the potential business impact is significantly greater.

The platform is deployed within the customer's own infrastructure (on-premises) and supports any LLM with an OpenAI- or Anthropic-compatible API, including proprietary models running on the customer's GPU servers. This means Cube does not lock customers into a specific AI provider. Vulners does not charge for token usage, leaving customers in control of their LLM costs. According to Vulners, running the model in a medium-sized infrastructure costs approximately $1,000 per month.

To summarize, Cube enriches traditional Vulnerability Management by linking technical vulnerabilities to infrastructure assets, operational processes, and potential business impact.
October Linux Patch Wednesday

October Linux Patch Wednesday

October Linux Patch Wednesday. There are 4,946 vulnerabilities in total. By comparison, there were 2,653 in September. That's an 86% increase! This time, there are 1,954 vulnerabilities in the Linux Kernel and 814 in Chromium. Together, they make up 56% of all vulnerabilities.

Six vulnerabilities show signs of being exploited in the wild:

🔻 RCE - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619). PHP is a popular programming language widely used for web application development. CVE-2026-109618 is an out-of-memory (OOM) handling vulnerability that allows remote code execution when an application receives a specially crafted request. CVE-2026-109619 is a use-after-free vulnerability that allows PHP to access stale references to freed memory, potentially leading to remote code execution. Linux distributions began releasing patches on the day the vulnerabilities were disclosed, October 21. More than 470 links to public exploits are available on GitHub. Both vulnerabilities were added to the CISA KEV on October 26.

🔻 SFB - Linux Kernel "PwnEscape" (CVE-2026-99999). The vulnerability affects the Linux kernel's networking stack and allows an attacker inside a KVM guest virtual machine to corrupt the host kernel's memory. This could expose sensitive host memory contents or cause the host system to crash. Researchers demonstrated a complete escape from a guest VM to the host. Linux distributions began releasing patched packages on October 16, and public exploits appeared on GitHub the same day. The vulnerability was added to the VulnCheck KEV on October 19.

🔻 RCE - WordPress (CVE-2026-87902). WordPress is a popular content management system (CMS) for building websites and blogs. Under certain conditions, this vulnerability allows an unauthenticated attacker to execute arbitrary code remotely on the server. Public exploits have been available on GitHub since September 22. The vulnerability was added to the CISA KEV on September 25. Debian released patched packages on September 28.

🔻 XSS - WordPress "Comment2Shell" (CVE-2026-93485). The vulnerability allows an unauthenticated attacker to inject JavaScript code through a specially crafted comment. The code is executed in the browser when an administrator views the comment, allowing the attacker to hijack his session and potentially execute arbitrary code on the server. The vulnerability was added to the VulnCheck KEV on September 18. Public exploits have been available on GitHub since September 22. Patched packages have been available in Debian since September 28.

🔻 AFR - Gradio (CVE-2026-28414). Gradio is a Python library for quickly building machine learning interfaces. The vulnerability allows unauthenticated attackers to read arbitrary files from a Windows server running Python 3.13 or later, even when Gradio authentication is enabled. A public exploit appeared on February 27. The vulnerability was added to the VulnCheck KEV on May 31. ALT Linux has been providing patched packages since October 1.

Another 335 vulnerabilities have no known signs of exploitation in the wild, but public exploits are available for them. Notable examples include:

🔸 EoP - Linux Kernel (CVE-2026-98260). This use-after-free vulnerability in the POSIX CPU timers mechanism allows a local unprivileged user to escalate privileges to root. Researcher v4bel demonstrated a root shell on Ubuntu 26.04 running kernel 7.0.0-30-generic as part of the Infinity Core project. The exploit is also reported to enable container escapes and privilege escalation on Android. Patched packages have been available since October 15. A public exploit was published on GitHub on October 17.

🔸 RCE - Pillow (CVE-2026-112900). Pillow is a Python library for image processing. An attacker can upload an EPS file to execute arbitrary code on the server. Patched packages have been available in Debian since October 21. Public exploits have been available on GitHub since October 23.

🗒 Full Vulristics report (ZIP; 1.7 MB)

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday. A total of 1,409 vulnerabilities. For comparison, there were 973 in September, an increase of about 45%. 🙈 Thirteen products had fixes for 20 or more vulnerabilities: Microsoft Office Excel (68), Windows Kernel (46), Role: DNS Server (41), Windows Installer (38), Microsoft Office SharePoint (35), Windows Win32k (31), Windows NTFS (26), .NET (25), Microsoft Windows Search Component (23), Microsoft Office Word (22), Windows Error Reporting (21), Windows Broadcast DVR User Service (20), and Microsoft SQL Server (20). A total of 416 vulnerabilities were fixed in these products. That's 30% of all vulnerabilities. One vulnerability is flagged as exploited in the wild:

🔻 SFB - Windows Shell (CVE-2026-96951). The vulnerability allows an attacker to bypass Mark of the Web (MOTW), a Windows feature that marks files downloaded from the Internet. To exploit it, the attacker must trick the user into opening a malicious file or clicking a malicious link.

There are two vulnerabilities with public exploits:

🔸 RCE - Raw Image Extension (CVE-2026-21413). A heap-based buffer overflow in Windows Raw Image Extension allows an attacker to execute arbitrary code remotely using a specially crafted file. A technical write-up of the vulnerability, which NVD classifies as an exploit, was published on the Cisco Talos blog on April 7.

🔸 EoP - Windows Health and Optimized Experiences Service (CVE-2026-85884). Missing authentication for a critical function in Windows Health and Optimized Experiences Service allows a local attacker to gain SYSTEM privileges. A public exploit has been available on GitHub since October 13.

Other notable vulnerabilities include:

🔹 RCE - Microsoft Exchange (CVE-2026-70571). An unauthenticated attacker can send a specially crafted email to a vulnerable Exchange server and execute arbitrary code on the server. The attack requires an in-depth understanding of the target environment. No user interaction is required.

🔹 RCE - Microsoft Office Outlook (CVE-2026-70242, CVE-2026-97749, CVE-2026-97016, CVE-2026-88156, CVE-2026-70291). An attacker can execute arbitrary code on the victim's device by sending a specially crafted email. To exploit the vulnerability, the victim only needs to view the email in Outlook's reading pane without opening it or taking any further action.

🔹 RCE - Windows Domain Name Service (CVE-2026-96113). A heap-based buffer overflow in DNS Server allows an unauthorized attacker to execute code over a network.

🔹 SFB - .NET Framework (CVE-2026-108398). An authenticated attacker can place a specially crafted .NET assembly on an affected system and register it to be loaded by a protected process. This allows the attacker to bypass Windows Defender Application Control (WDAC) restrictions and run unauthorized code within the protected process. No user interaction is required.

🔹 Spoofing - Microsoft Exchange (CVE-2026-70279). An attacker can send a specially crafted link to a user and trick them into opening it. No authentication is required. If the user has administrator privileges, the attacker could act as that user and access or modify the organization's data.

🗒 Full Vulristics report

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability. Check Point Quantum Security Gateway is an enterprise security gateway and next-generation firewall (NGFW) designed to protect network infrastructure from cyberattacks and unauthorized access. It provides network traffic filtering, intrusion prevention (IPS), application control, and secure VPN connectivity. Improper validation of trust in an X.509 certificate during VPN negotiation on Check Point Quantum Security Gateway may allow an unauthenticated remote attacker to execute arbitrary code on the gateway with the privileges of a system process.

An attacker may use the compromised gateway to perform internal network reconnaissance (including port and service scanning), intercept VPN traffic, steal credentials and configuration files, including certificates, IPsec/VPN keys, and administrator credentials, and compromise VPN tunnels connecting the organization's network to branch offices and partner networks.

The vulnerability also affects Spark Firewall devices, a family of firewalls developed by Check Point primarily to protect the networks of small and medium-sized businesses, branch offices, and remote locations.

⚙️ Security updates and mitigation measures have been available on the vendor's website since September 9.

👾 Check Point experts began observing exploitation attempts on September 12. On September 22, the vulnerability was added to the CISA KEV catalog.

🛠 A public exploit has been available on GitHub since October 7.

🌐 As of October 12, Shodan had identified 11,849 potentially vulnerable Check Point gateways exposed to the Internet, 143 of them in Russia.

September Linux Patch Wednesday

September Linux Patch Wednesday

September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.

🗒 Full Vulristics report