Category Archives: Vulristics

October Linux Patch Wednesday

October Linux Patch Wednesday

October Linux Patch Wednesday. There are 4,946 vulnerabilities in total. By comparison, there were 2,653 in September. That's an 86% increase! This time, there are 1,954 vulnerabilities in the Linux Kernel and 814 in Chromium. Together, they make up 56% of all vulnerabilities.

Six vulnerabilities show signs of being exploited in the wild:

🔻 RCE - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619). PHP is a popular programming language widely used for web application development. CVE-2026-109618 is an out-of-memory (OOM) handling vulnerability that allows remote code execution when an application receives a specially crafted request. CVE-2026-109619 is a use-after-free vulnerability that allows PHP to access stale references to freed memory, potentially leading to remote code execution. Linux distributions began releasing patches on the day the vulnerabilities were disclosed, October 21. More than 470 links to public exploits are available on GitHub. Both vulnerabilities were added to the CISA KEV on October 26.

🔻 SFB - Linux Kernel "PwnEscape" (CVE-2026-99999). The vulnerability affects the Linux kernel's networking stack and allows an attacker inside a KVM guest virtual machine to corrupt the host kernel's memory. This could expose sensitive host memory contents or cause the host system to crash. Researchers demonstrated a complete escape from a guest VM to the host. Linux distributions began releasing patched packages on October 16, and public exploits appeared on GitHub the same day. The vulnerability was added to the VulnCheck KEV on October 19.

🔻 RCE - WordPress (CVE-2026-87902). WordPress is a popular content management system (CMS) for building websites and blogs. Under certain conditions, this vulnerability allows an unauthenticated attacker to execute arbitrary code remotely on the server. Public exploits have been available on GitHub since September 22. The vulnerability was added to the CISA KEV on September 25. Debian released patched packages on September 28.

🔻 XSS - WordPress "Comment2Shell" (CVE-2026-93485). The vulnerability allows an unauthenticated attacker to inject JavaScript code through a specially crafted comment. The code is executed in the browser when an administrator views the comment, allowing the attacker to hijack his session and potentially execute arbitrary code on the server. The vulnerability was added to the VulnCheck KEV on September 18. Public exploits have been available on GitHub since September 22. Patched packages have been available in Debian since September 28.

🔻 AFR - Gradio (CVE-2026-28414). Gradio is a Python library for quickly building machine learning interfaces. The vulnerability allows unauthenticated attackers to read arbitrary files from a Windows server running Python 3.13 or later, even when Gradio authentication is enabled. A public exploit appeared on February 27. The vulnerability was added to the VulnCheck KEV on May 31. ALT Linux has been providing patched packages since October 1.

Another 335 vulnerabilities have no known signs of exploitation in the wild, but public exploits are available for them. Notable examples include:

🔸 EoP - Linux Kernel (CVE-2026-98260). This use-after-free vulnerability in the POSIX CPU timers mechanism allows a local unprivileged user to escalate privileges to root. Researcher v4bel demonstrated a root shell on Ubuntu 26.04 running kernel 7.0.0-30-generic as part of the Infinity Core project. The exploit is also reported to enable container escapes and privilege escalation on Android. Patched packages have been available since October 15. A public exploit was published on GitHub on October 17.

🔸 RCE - Pillow (CVE-2026-112900). Pillow is a Python library for image processing. An attacker can upload an EPS file to execute arbitrary code on the server. Patched packages have been available in Debian since October 21. Public exploits have been available on GitHub since October 23.

🗒 Full Vulristics report (ZIP; 1.7 MB)
October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

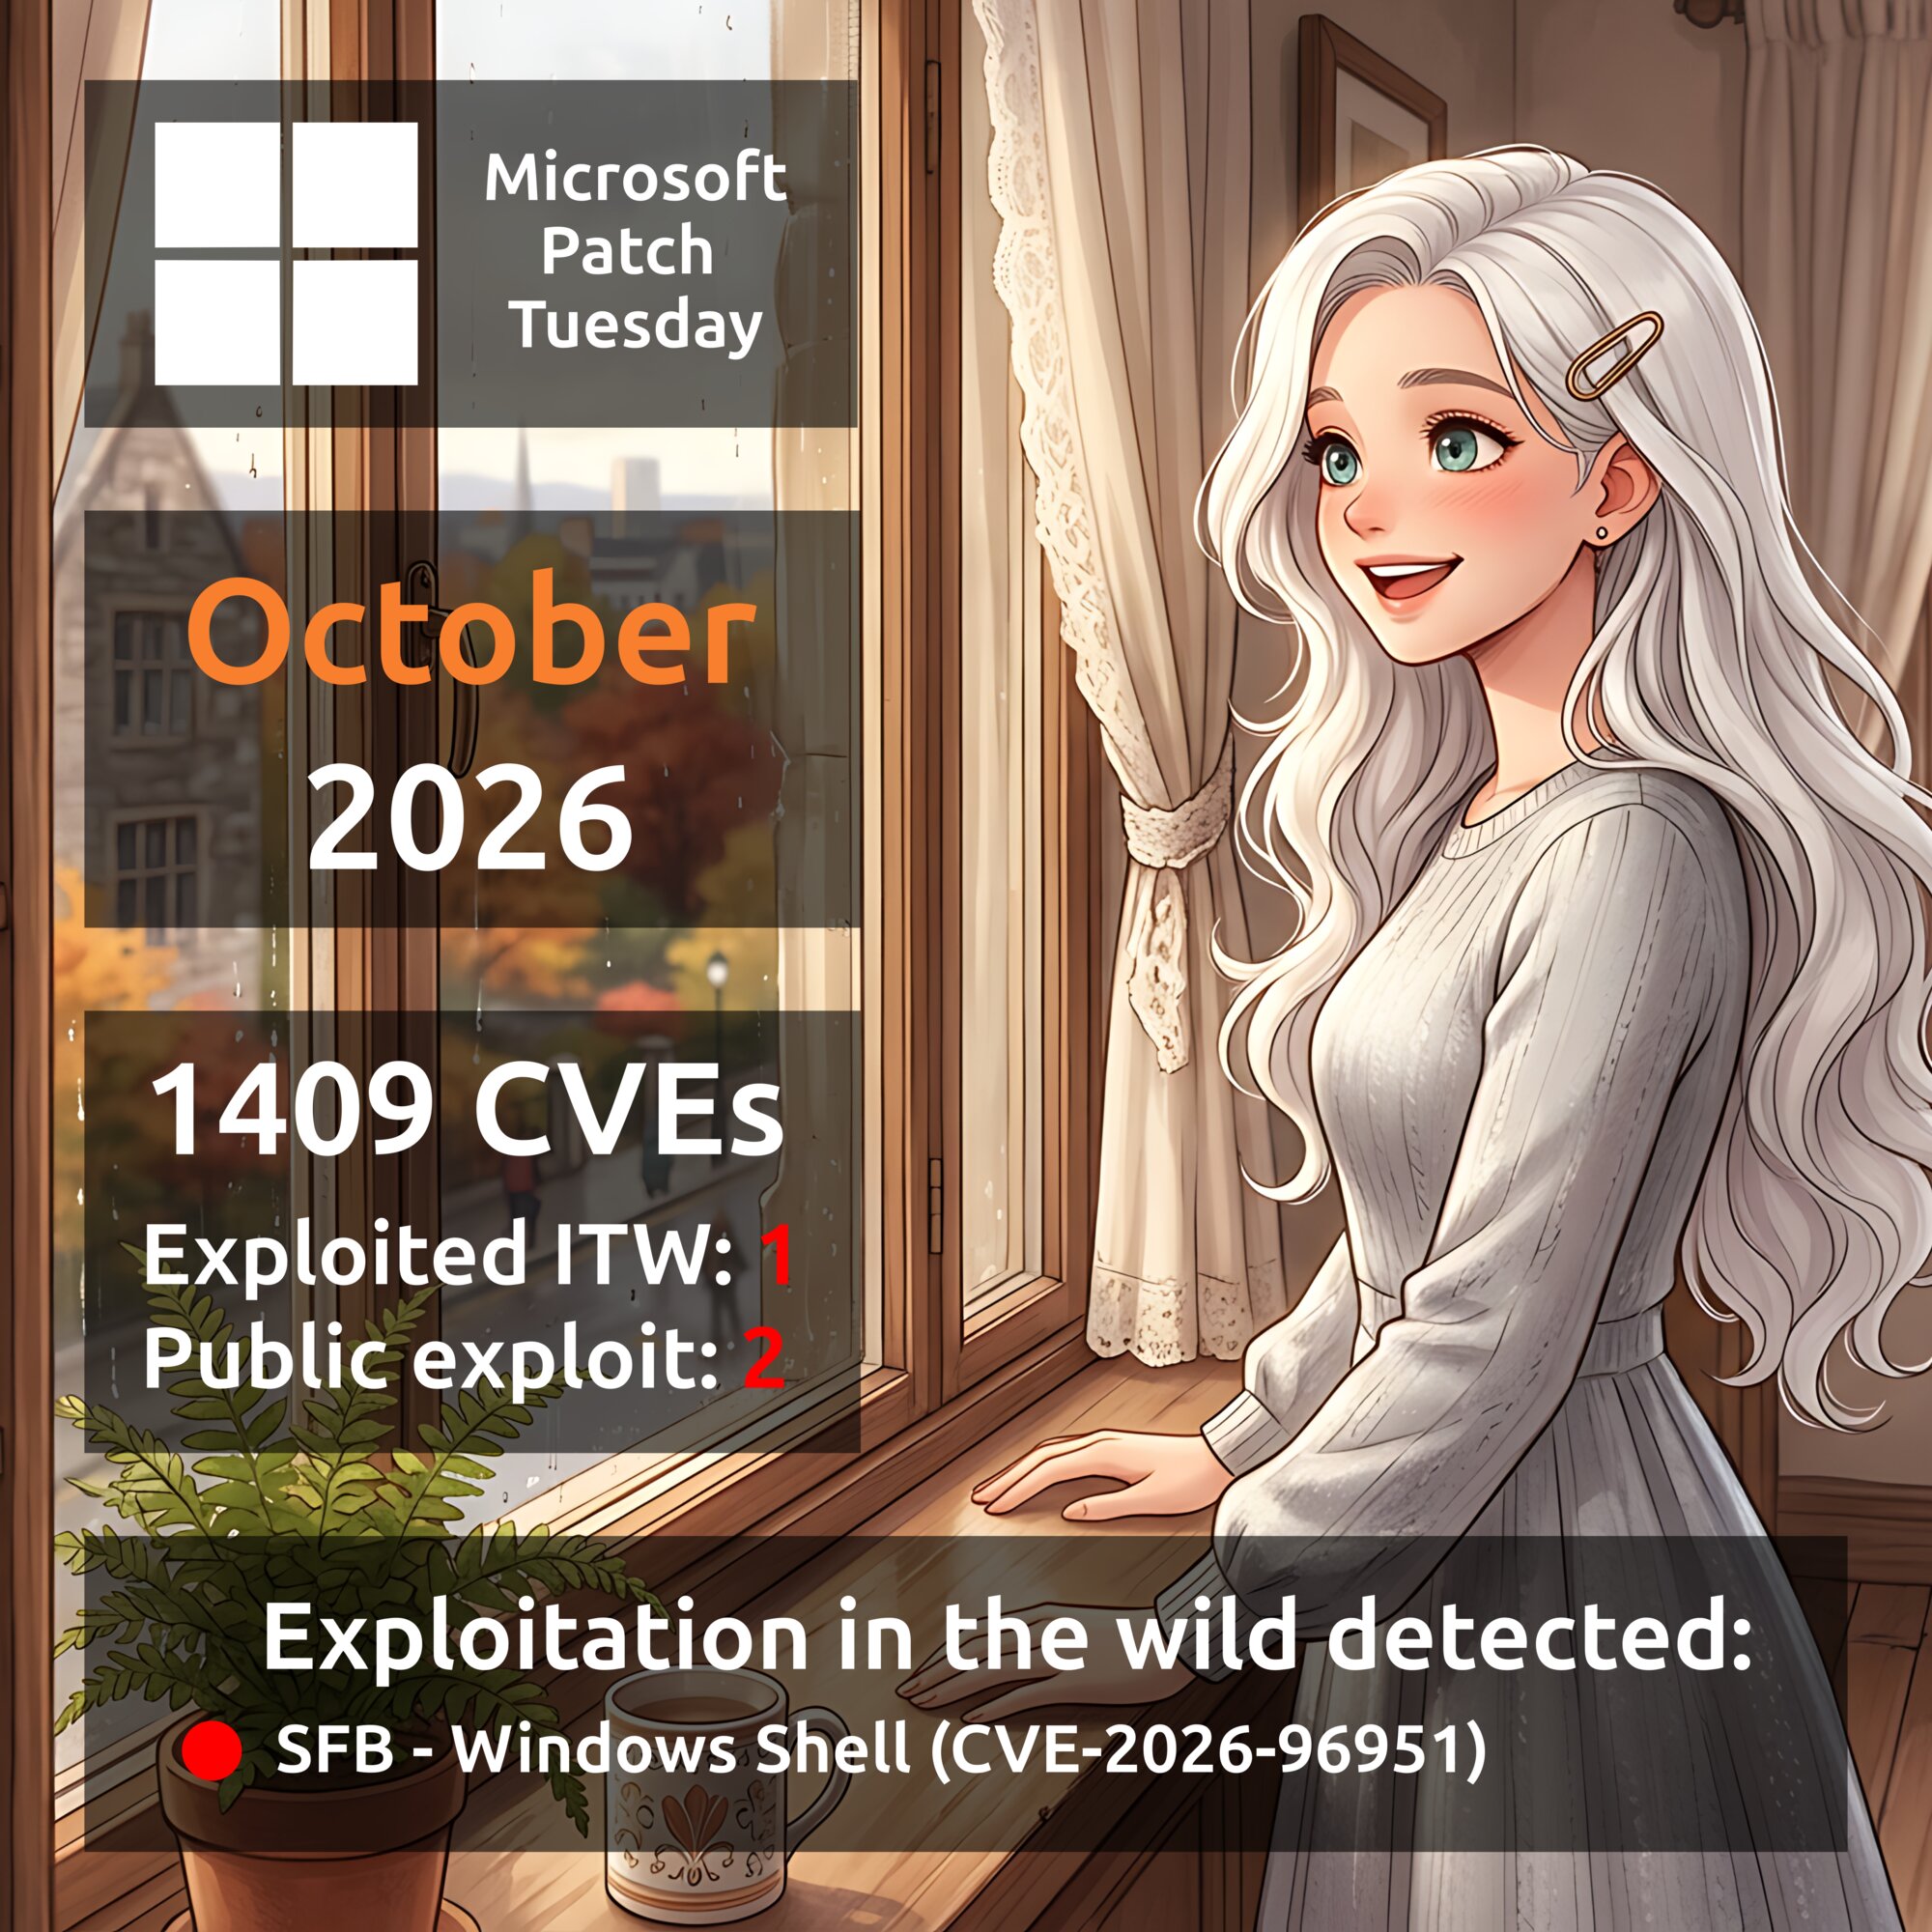
October Microsoft Patch Tuesday. A total of 1,409 vulnerabilities. For comparison, there were 973 in September, an increase of about 45%. 🙈 Thirteen products had fixes for 20 or more vulnerabilities: Microsoft Office Excel (68), Windows Kernel (46), Role: DNS Server (41), Windows Installer (38), Microsoft Office SharePoint (35), Windows Win32k (31), Windows NTFS (26), .NET (25), Microsoft Windows Search Component (23), Microsoft Office Word (22), Windows Error Reporting (21), Windows Broadcast DVR User Service (20), and Microsoft SQL Server (20). A total of 416 vulnerabilities were fixed in these products. That's 30% of all vulnerabilities. One vulnerability is flagged as exploited in the wild:

🔻 SFB - Windows Shell (CVE-2026-96951). The vulnerability allows an attacker to bypass Mark of the Web (MOTW), a Windows feature that marks files downloaded from the Internet. To exploit it, the attacker must trick the user into opening a malicious file or clicking a malicious link.

There are two vulnerabilities with public exploits:

🔸 RCE - Raw Image Extension (CVE-2026-21413). A heap-based buffer overflow in Windows Raw Image Extension allows an attacker to execute arbitrary code remotely using a specially crafted file. A technical write-up of the vulnerability, which NVD classifies as an exploit, was published on the Cisco Talos blog on April 7.

🔸 EoP - Windows Health and Optimized Experiences Service (CVE-2026-85884). Missing authentication for a critical function in Windows Health and Optimized Experiences Service allows a local attacker to gain SYSTEM privileges. A public exploit has been available on GitHub since October 13.

Other notable vulnerabilities include:

🔹 RCE - Microsoft Exchange (CVE-2026-70571). An unauthenticated attacker can send a specially crafted email to a vulnerable Exchange server and execute arbitrary code on the server. The attack requires an in-depth understanding of the target environment. No user interaction is required.

🔹 RCE - Microsoft Office Outlook (CVE-2026-70242, CVE-2026-97749, CVE-2026-97016, CVE-2026-88156, CVE-2026-70291). An attacker can execute arbitrary code on the victim's device by sending a specially crafted email. To exploit the vulnerability, the victim only needs to view the email in Outlook's reading pane without opening it or taking any further action.

🔹 RCE - Windows Domain Name Service (CVE-2026-96113). A heap-based buffer overflow in DNS Server allows an unauthorized attacker to execute code over a network.

🔹 SFB - .NET Framework (CVE-2026-108398). An authenticated attacker can place a specially crafted .NET assembly on an affected system and register it to be loaded by a protected process. This allows the attacker to bypass Windows Defender Application Control (WDAC) restrictions and run unauthorized code within the protected process. No user interaction is required.

🔹 Spoofing - Microsoft Exchange (CVE-2026-70279). An attacker can send a specially crafted link to a user and trick them into opening it. No authentication is required. If the user has administrator privileges, the attacker could act as that user and access or modify the organization's data.

🗒 Full Vulristics report

September Linux Patch Wednesday

September Linux Patch Wednesday

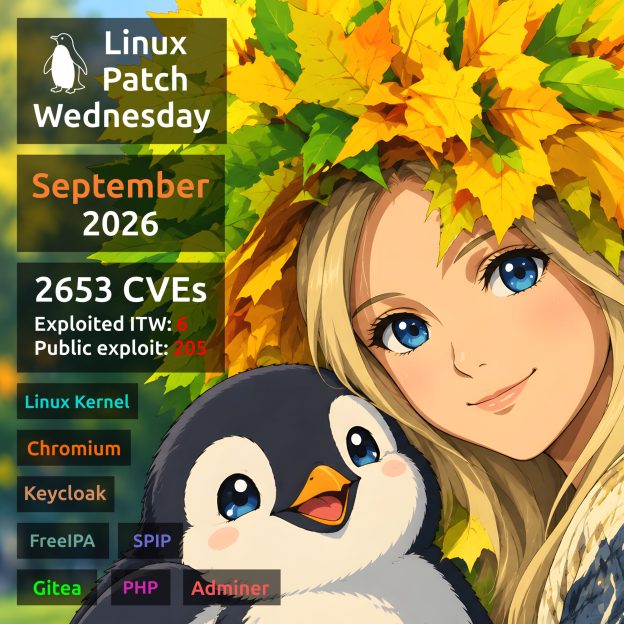
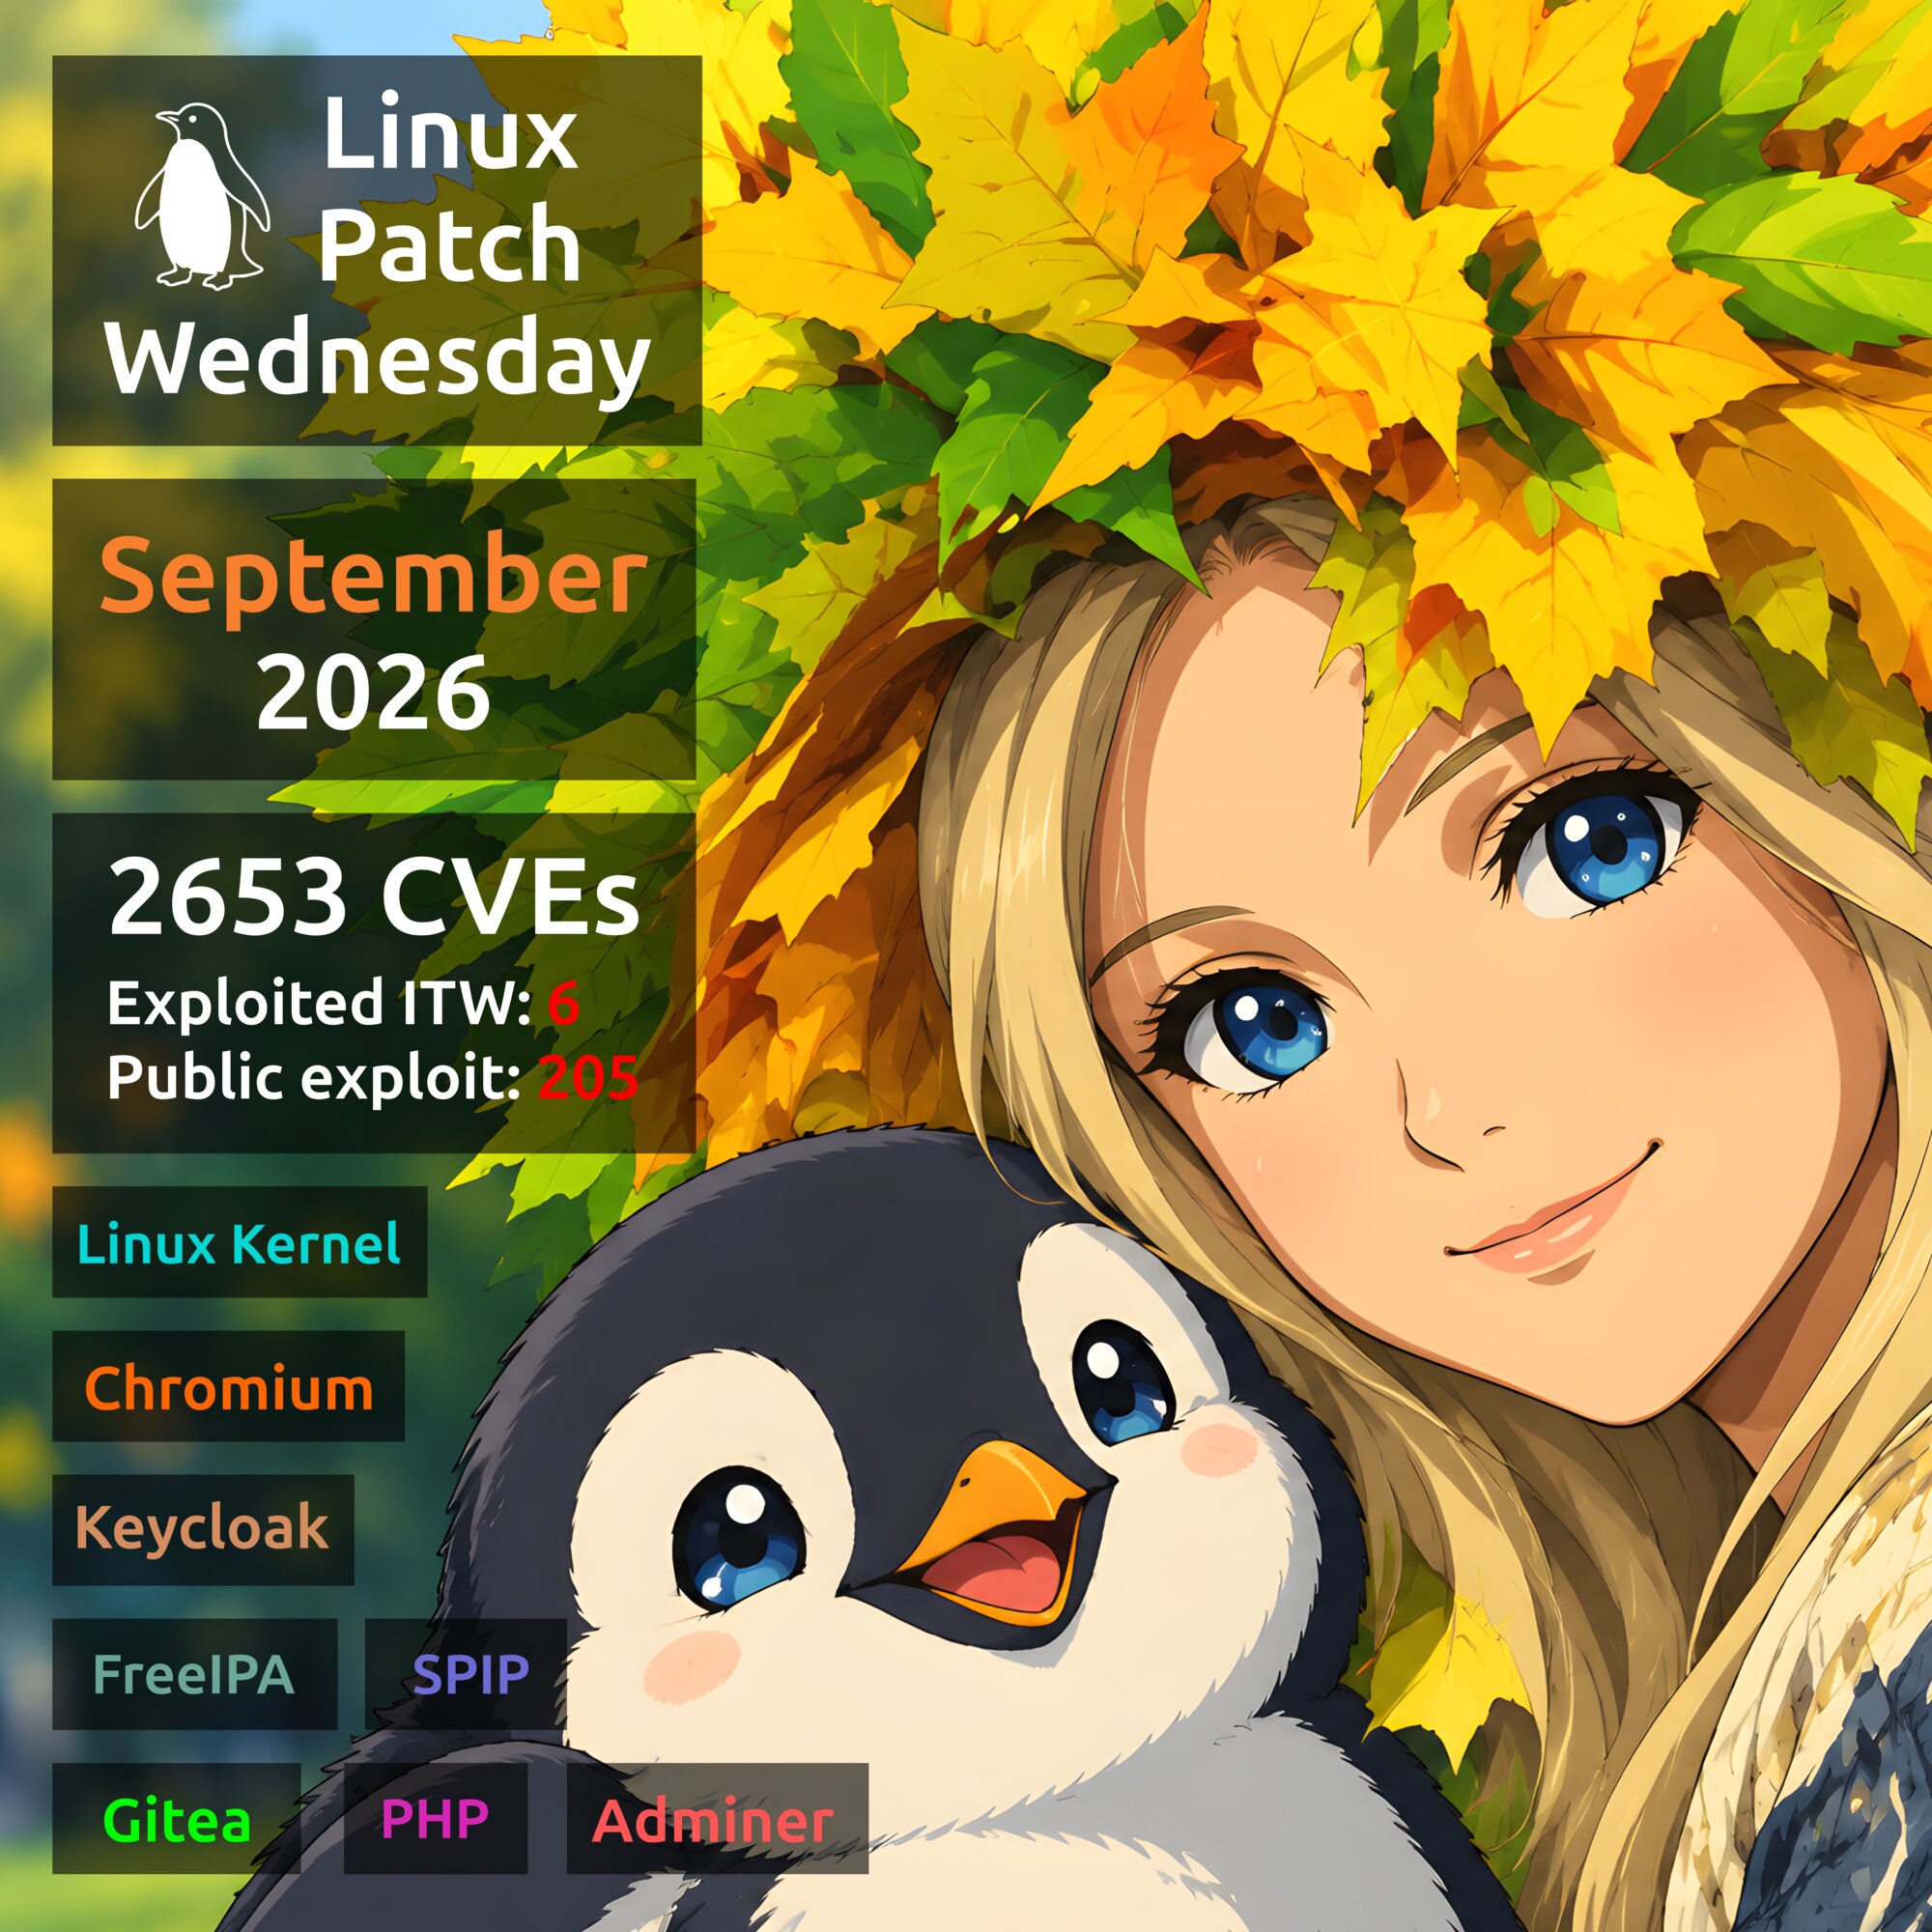
September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.

🗒 Full Vulristics report

September Microsoft Patch Tuesday

September Microsoft Patch Tuesday

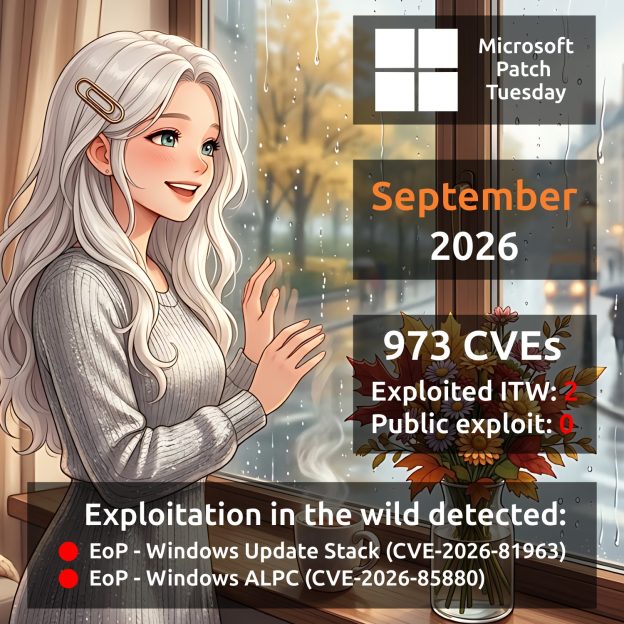
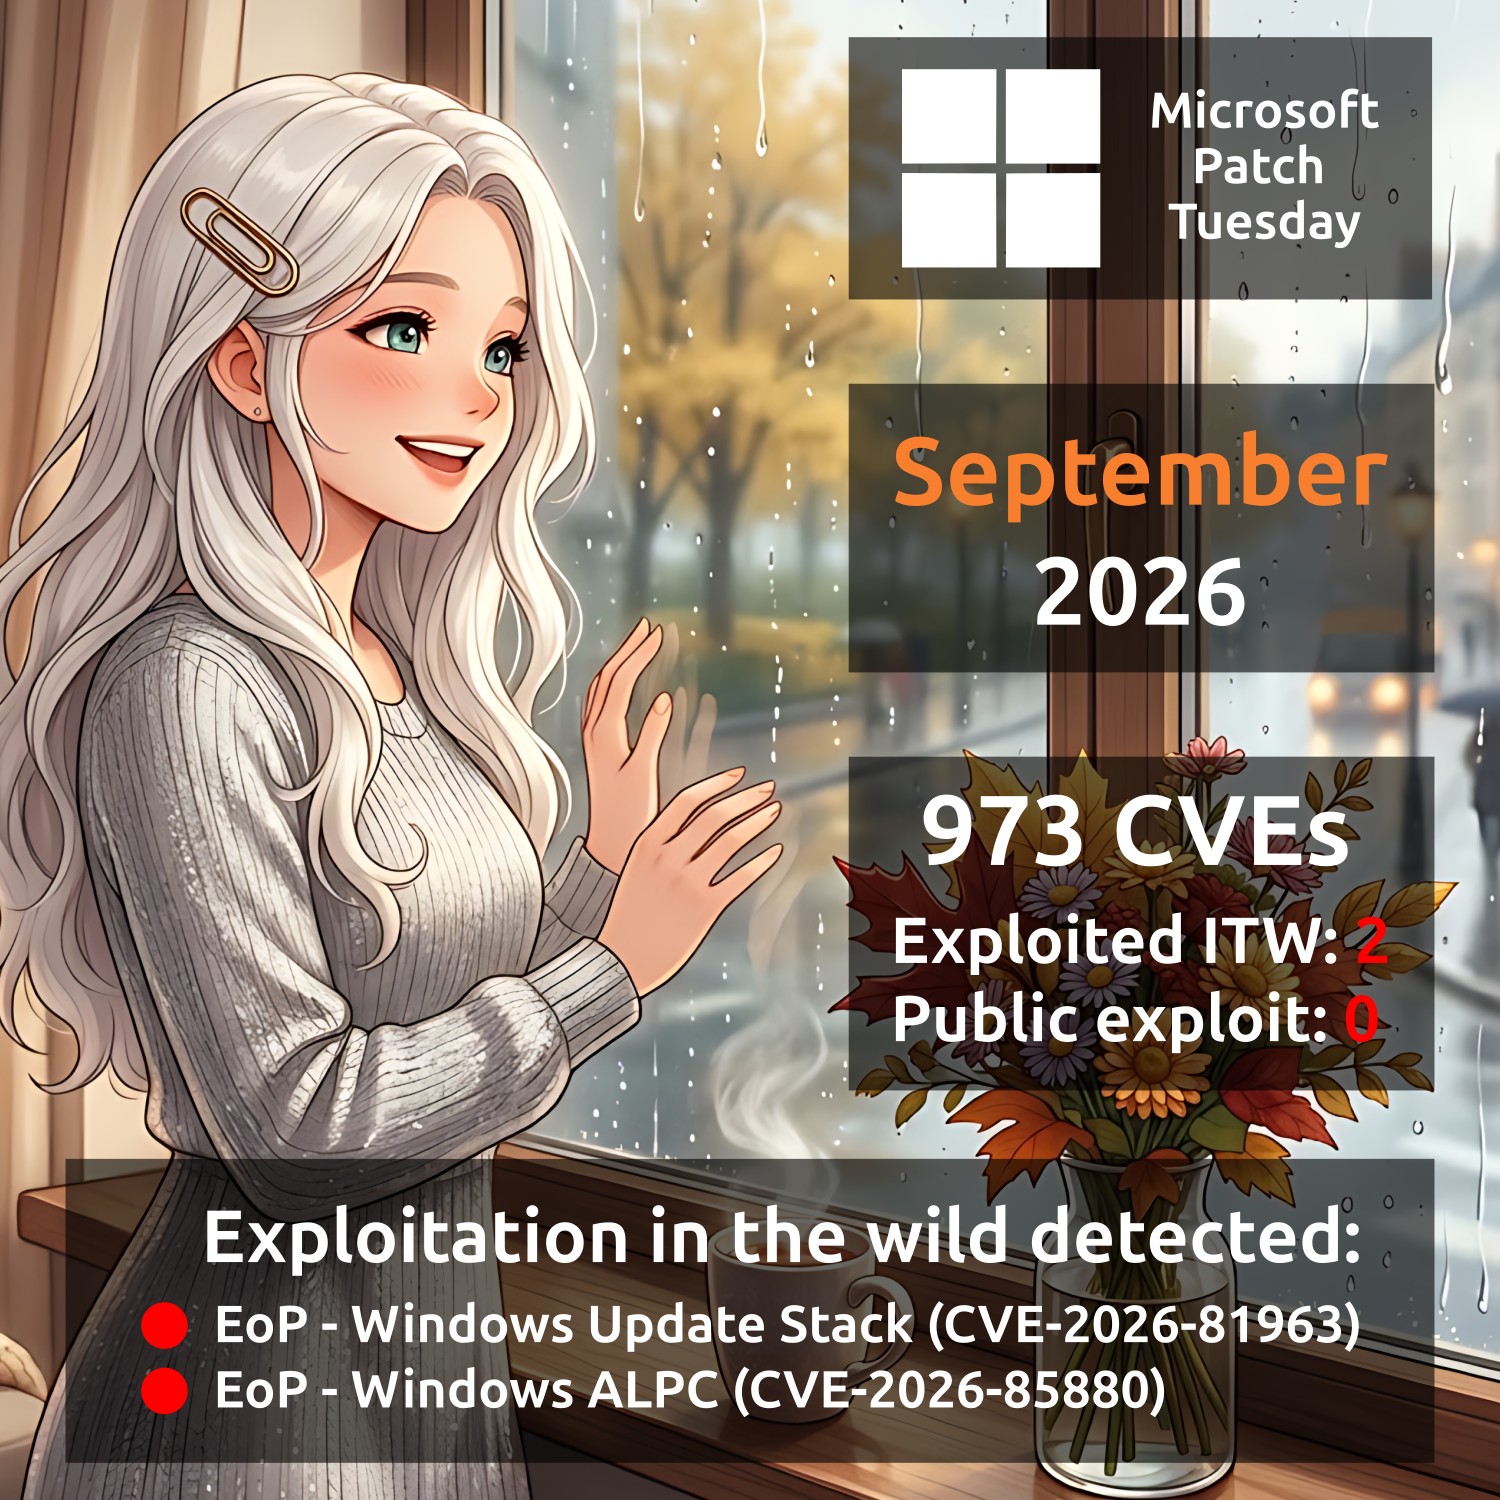
September Microsoft Patch Tuesday. A total of 973 vulnerabilities were addressed - more than twice as many as in August. Seven products had 20 or more vulnerabilities fixed: Windows Biometric Service (64), Microsoft SQL Server (54), Windows DHCP Server (36), Microsoft Office Word (35), Windows NTFS (29), Microsoft Excel (28), and Windows Win32k (24). Vulnerabilities affecting these products account for just under one-third of the total. Two vulnerabilities are known to have been exploited in the wild:

🔻 EoP - Windows Update Stack (CVE-2026-81963). A link following flaw in the Windows Update Stack (CWE-59) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

🔻 EoP - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880). A heap-based buffer overflow flaw in Windows ALPC (CWE-122) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

There are no vulnerabilities with public exploits yet. Of the remaining vulnerabilities, the following can be highlighted:

🔹 RCE - Microsoft Exchange (CVE-2026-55007). A remote, unauthenticated attacker could achieve code execution on a vulnerable Exchange server by sending an email containing a malicious Visio attachment. The code is executed when the server processes the message, without requiring the victim to open it or use the Preview Pane.

🔹 RCE - Remote Desktop Services (CVE-2026-69525). Successful exploitation of this flaw would allow an unauthenticated attacker to execute arbitrary code by exploiting a use-after-free flaw.

🔹 RCE - Windows DNS Server (CVE-2026-69730). According to the advisory, an unauthenticated, remote attacker could send a crafted packet to exploit a use-after-free flaw in Windows DNS in order to achieve remote code execution.

🔹 RCE - Windows USB Mass Storage Class Driver (CVE-2026-68839). Successful exploitation of this vulnerability could allow an attacker the ability to gain remote code execution via an in-network attacker calling arbitrary endpoints.

🔹 RCE - Windows Kerberos (CVE-2026-69676). An authentication-bypass flaw via capture-replay in Windows Kerberos may allow an authenticated attacker to execute code over a network.

🔹 RCE - Windows Key Distribution Center (CVE-2026-69712). A use-after-free flaw in the Windows Key Distribution Center may allow an authenticated attacker to execute code over a network.

🔹 EoP - Microsoft Exchange (CVE-2026-69380). An authenticated attacker with access to a mailbox through a low-privileged user account could exploit this vulnerability to gain access to other mailboxes. Successful exploitation would allow the attacker to send and receive emails on behalf of other Exchange users as well as access attachments.

🗒 Full Vulristics report

August Linux Patch Wednesday

August Linux Patch Wednesday

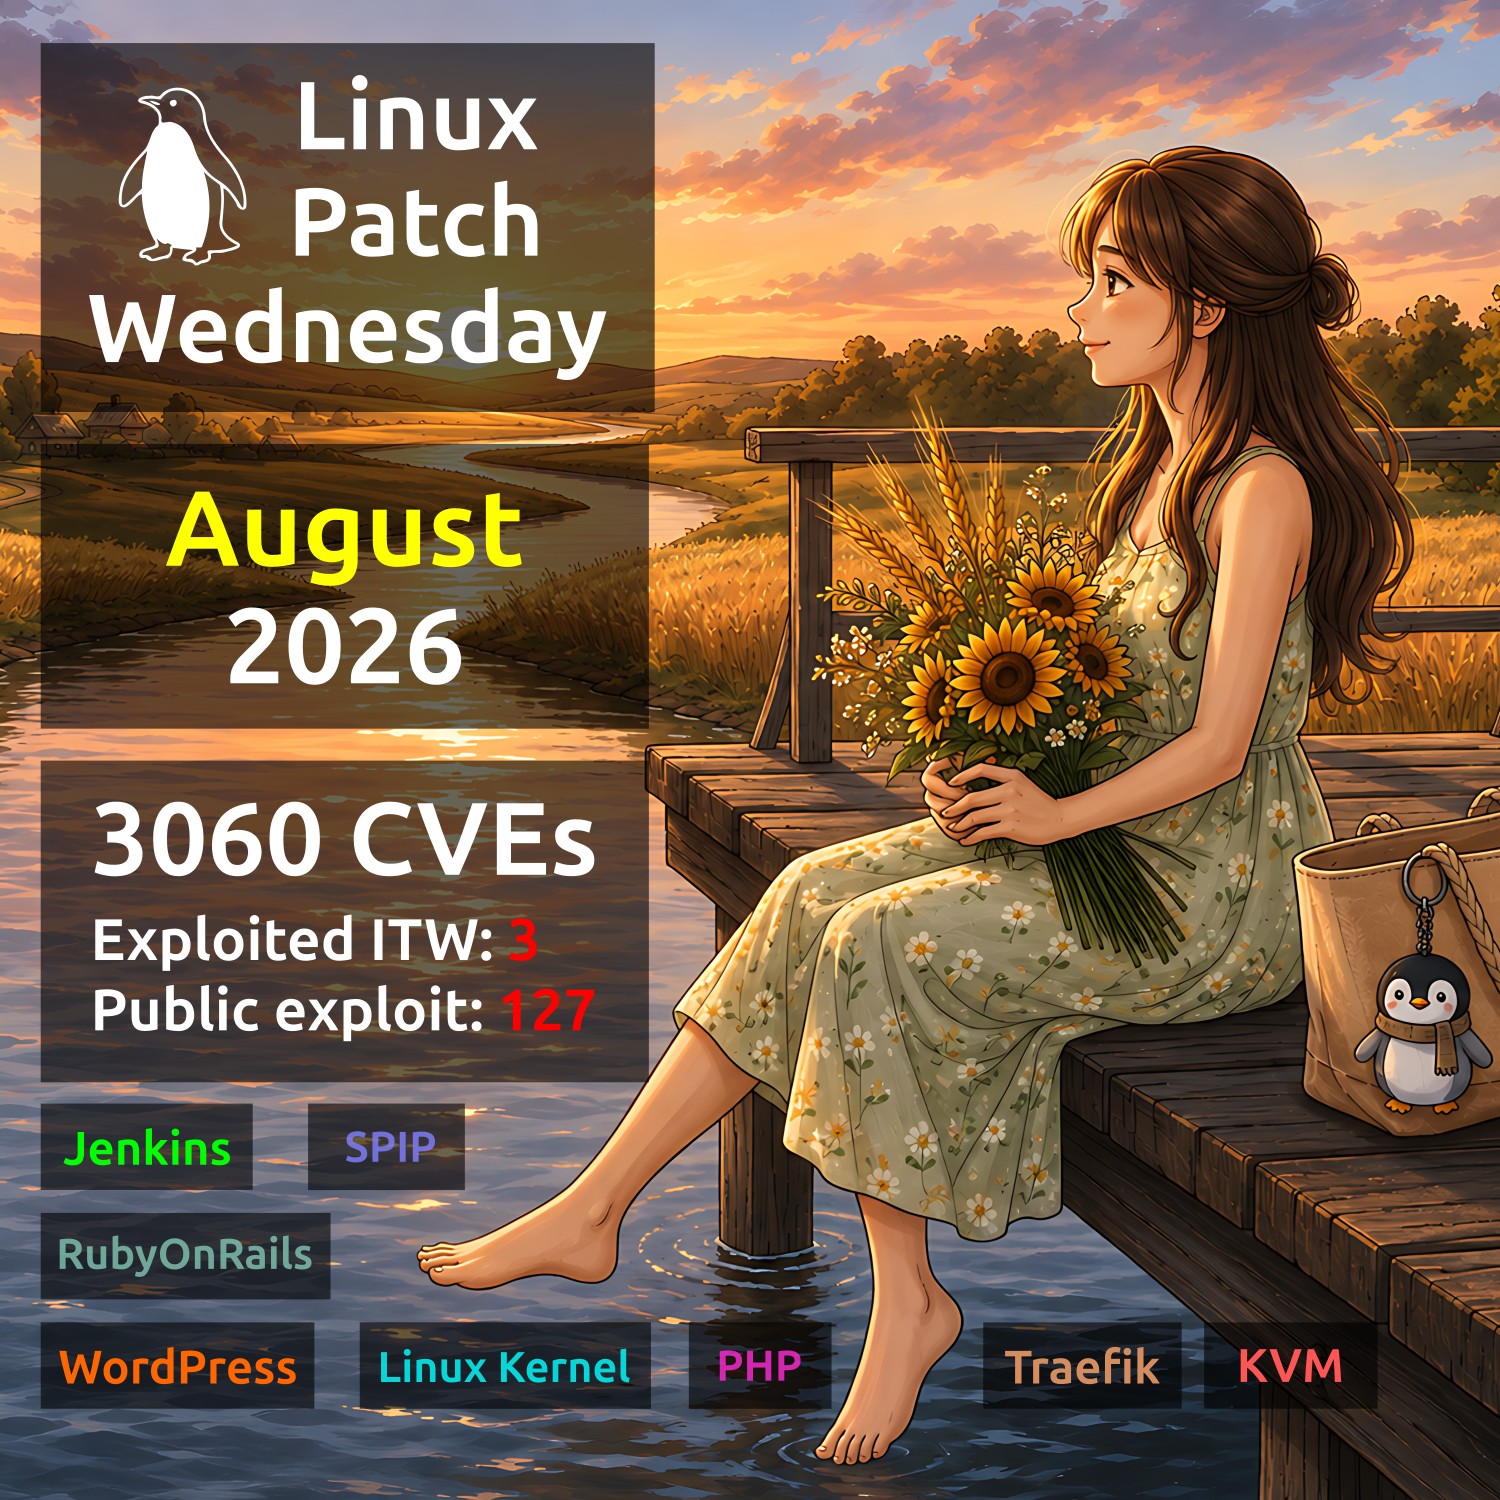
August Linux Patch Wednesday. A total of 3,060 vulnerabilities. For comparison, there were 2,017 in July. That's a 52% increase and another new record. This time, there are 1,354 vulnerabilities in the Linux Kernel and 447 in Chromium. For 3 vulnerabilities, there are signs of exploitation in the wild:

🔻 RCE - Jenkins (CVE-2026-53435). Jenkins is a development automation server used to build, test, and deploy software. The vulnerability allows a remote authenticated attacker to use the Script Console to execute arbitrary code and read files from the Jenkins controller. The vulnerability was added to the VulnCheck KEV on June 15 and fixed in RedOS on August 12.

🔻 CodeInj - WordPress (CVE-2026-60137). WordPress is a popular open-source CMS for creating websites and blogs. The vulnerability leads to a blind SQL injection in the WordPress core, allowing a remote unauthenticated attacker to read user accounts and password hashes from the WordPress database. Code execution is then possible by installing a malicious plugin. Multiple public exploits are available. The vulnerability was added to the CISA KEV catalog on July 21. A fix for the wordpress package in the Debian repository was released on July 23.

🔻 RCE - SPIP (CVE-2026-77647). SPIP is an open-source CMS for creating and collaboratively editing websites. The vulnerability allows an unauthenticated remote attacker to execute arbitrary PHP code. The vulnerability was added to the VulnCheck KEV on August 20. A fix for the spip package in the Debian repository was released on August 18.

Strictly speaking, the report contains one more vulnerability RCE - WinRAR (CVE-2025-8088) that is being exploited in the wild. The vulnerability was fixed in the clamav package in the Alt Linux repository. However, exploitation is only possible on Windows, so it is out of scope.

Another 127 vulnerabilities are not known to be exploited in the wild, but public exploits are available for them, or there are indications that such exploits exist. Notable examples include:

🔸 RCE - Action Pack "KindaRails2Shell" (CVE-2026-66066). Action Pack is a component of Ruby on Rails responsible for handling web requests, routing, and generating responses. An attacker can upload a specially crafted image to a vulnerable application and achieve remote code execution.

🔸 RCE - WordPress "XSS2Shell" (CVE-2026-64638). The attack chain allows an unauthenticated XSS on the login page to be escalated to arbitrary PHP code execution.

🔸 CodeInj - PHP (CVE-2026-17543). Improper escaping of backslashes in attacker-controlled parameters can lead to a trivial SQL injection in PHP.

🔸 EoP - Linux Kernel "Zapscape" (CVE-2026-64561). This KVM escape vulnerability allows an attacker to break out of a virtual machine in KVM/x86 environments and execute commands on the host with root privileges.

🔸 EoP - Linux Kernel "OVSwrap" (CVE-2026-64531), Linux Kernel "SCTPhantom" (CVE-2026-64564), Linux Kernel "Ubuntu PPPoL2TP" (CVE-2026-68398). These vulnerabilities allow a local attacker to escalate privileges to root.

🔸 AuthBypass - Traefik (CVE-2026-48020). Traefik is an HTTP reverse proxy and load balancer. A high-severity vulnerability in the StripPrefix middleware allows an unauthenticated attacker to bypass route-level authentication and authorization.

🗒 Full Vulristics report

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

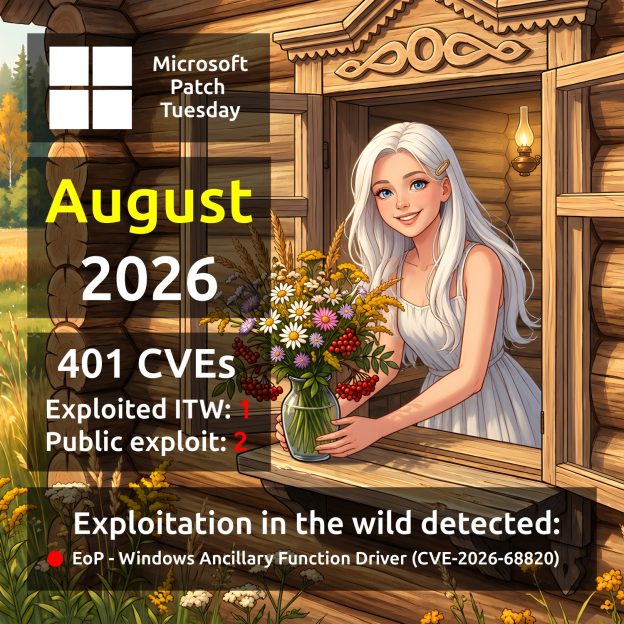
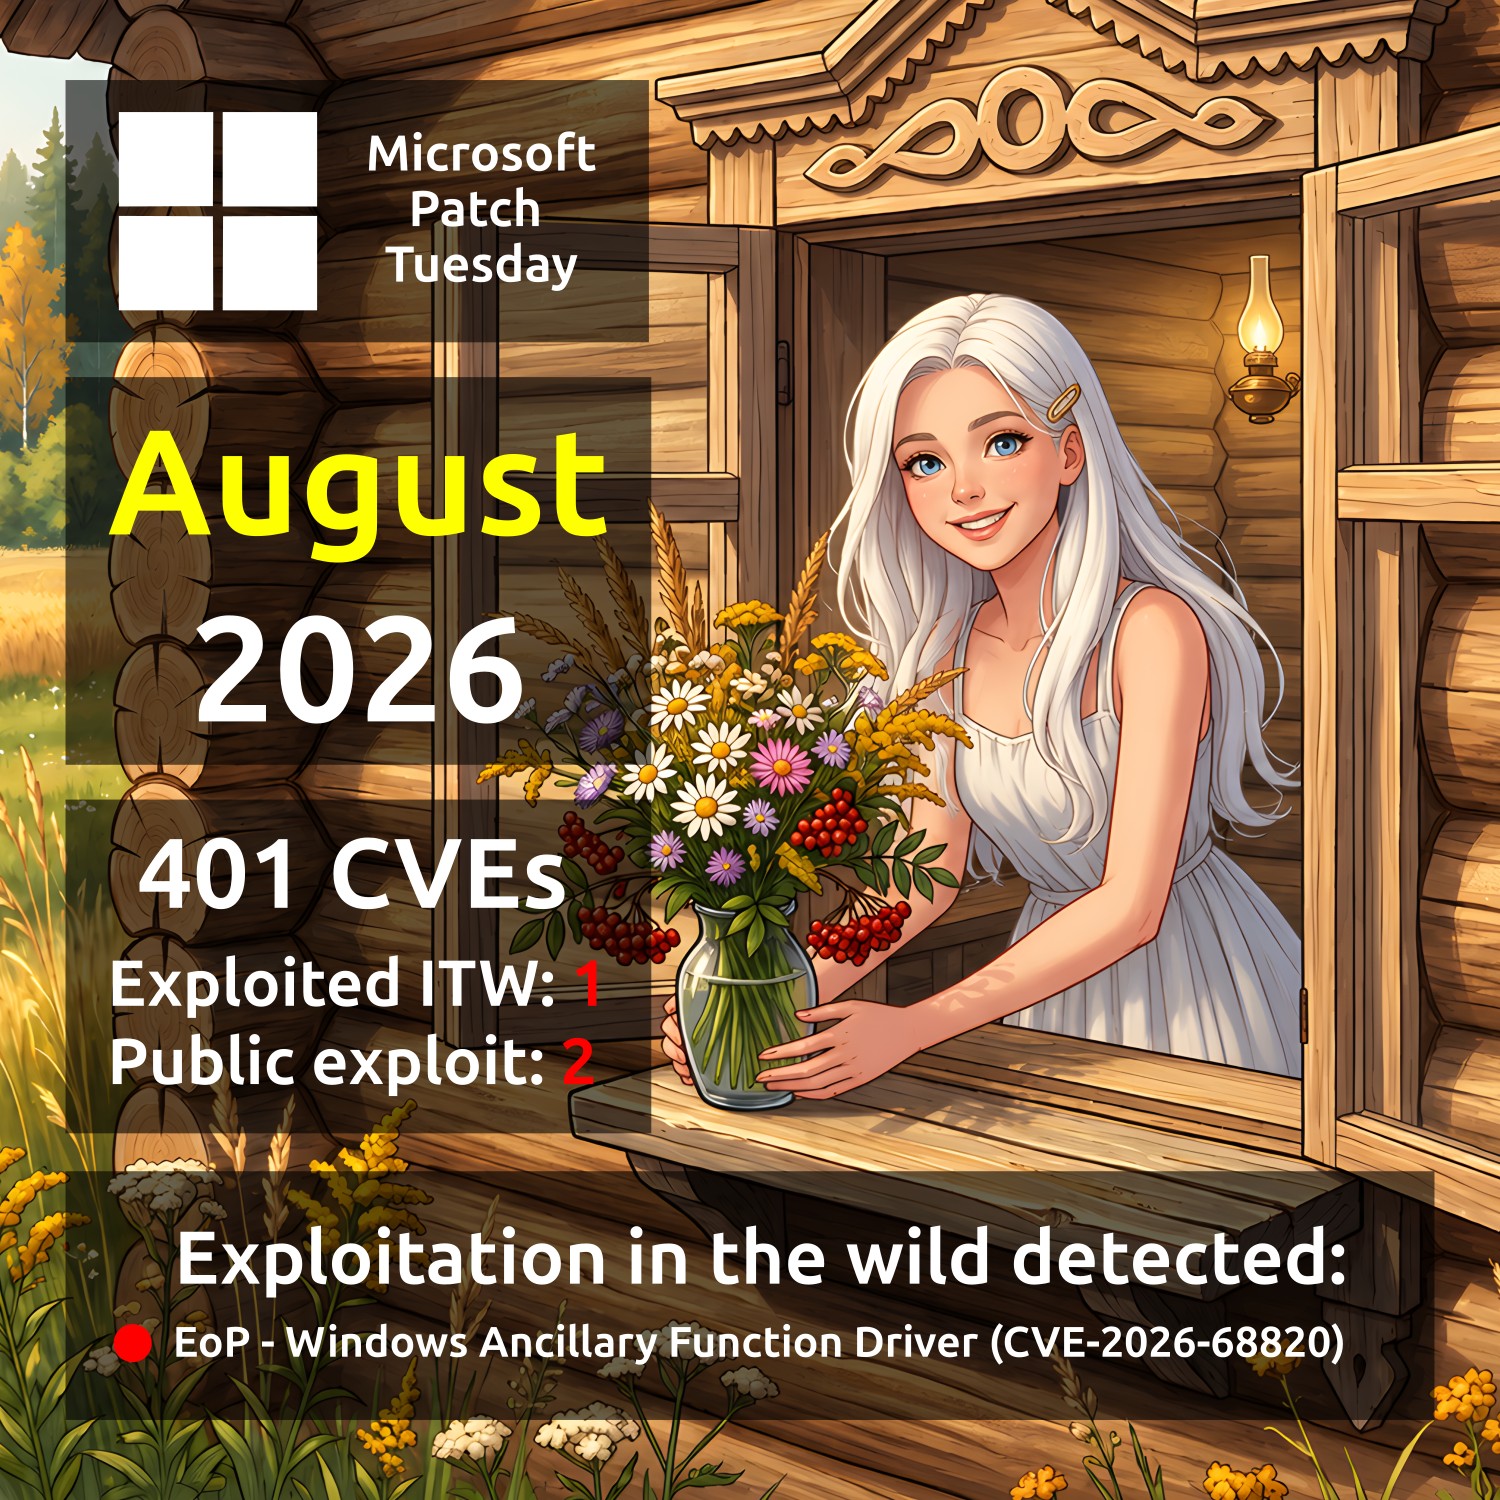
August Microsoft Patch Tuesday. A total of 401 vulnerabilities were addressed - 170 fewer than in July. One of the vulnerabilities is known to be actively exploited in the wild:

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). A local attacker can exploit this vulnerability to gain SYSTEM-level privileges. There is a contradiction in Microsoft's description: the Exploit Code Maturity in CVSS is marked as "Unproven", while at the same time Microsoft states that the vulnerability is being exploited in the wild. 🤷‍♂️

Public exploits are available for two other vulnerabilities:

🔸 EoP - Windows User Profile Service (CVE-2026-62832). This vulnerability allows an authenticated attacker to elevate privileges to ADMINISTRATOR level. Rapid7 believes this vulnerability is related to the LegacyHive exploit, which was published on July 14.

🔸 EoP - Windows Kernel (CVE-2026-62737). This vulnerability allows an authenticated attacker to elevate privileges to SYSTEM level. An exploit has been publicly available since August 11.

Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Windows DNS Server (CVE-2026-62878). This wormable vulnerability allows a remote unauthenticated attacker to execute code on a vulnerable server with elevated privileges. It is recommended to test and install the update as soon as possible, especially on Internet-facing DNS servers.

🔹 RCE - Windows Deployment Services TFTP Server (CVE-2026-62893). This vulnerability, discovered as part of the ZDI (Zero Day Initiative) program, allows an attacker to execute code without authentication or user interaction. TFTP has no authentication mechanism and is available remotely via UDP port 69. Any WDS server serving Windows Imaging Format (WIM) files via TFTP, which is the standard PXE boot scenario, is vulnerable. The issue results from the lack of validation of the existence of an object before performing operations on it. UDP port 69 should be blocked at the perimeter, but attackers could easily use this vulnerability for lateral movement within an organization. If you're using WDS for deployments, test and install this update quickly.

🔹 RCE - Windows DHCP Server (CVE-2026-62823). Successful exploitation of this vulnerability allows a remote unauthenticated attacker to execute arbitrary code from an adjacent network by sending a specially crafted packet that triggers a heap-based buffer overflow.

🔹 EoP - Microsoft Exchange (CVE-2026-62911). This vulnerability allows a remote authenticated attacker (with Privileges Required: Low according to CVSS) to gain control over the mailboxes of all Exchange users, send and read emails, and download attachments. This vulnerability was demonstrated at Pwn2Own Berlin. ZDI researchers provided Microsoft with working exploits.

🔹 RCE - Microsoft QUIC (CVE-2026-62815). This use-after-free vulnerability allows an unauthenticated attacker to execute arbitrary code on a target system by sending a specially crafted network packet. QUIC is an IETF-standardized transport protocol that runs over UDP instead of TCP and serves as the foundation for HTTP/3. The protocol is used by approximately 13.5 million websites.

🔹 Tampering - Windows Container Isolation FS Filter Driver (unionfs.sys) (CVE-2026-72971). This vulnerability reportedly allows an attacker to overwrite certain files. As a result, an attacker could perform an action within a container that could impact the host system.

🗒 Full Vulristics report

July Linux Patch Wednesday

July Linux Patch Wednesday

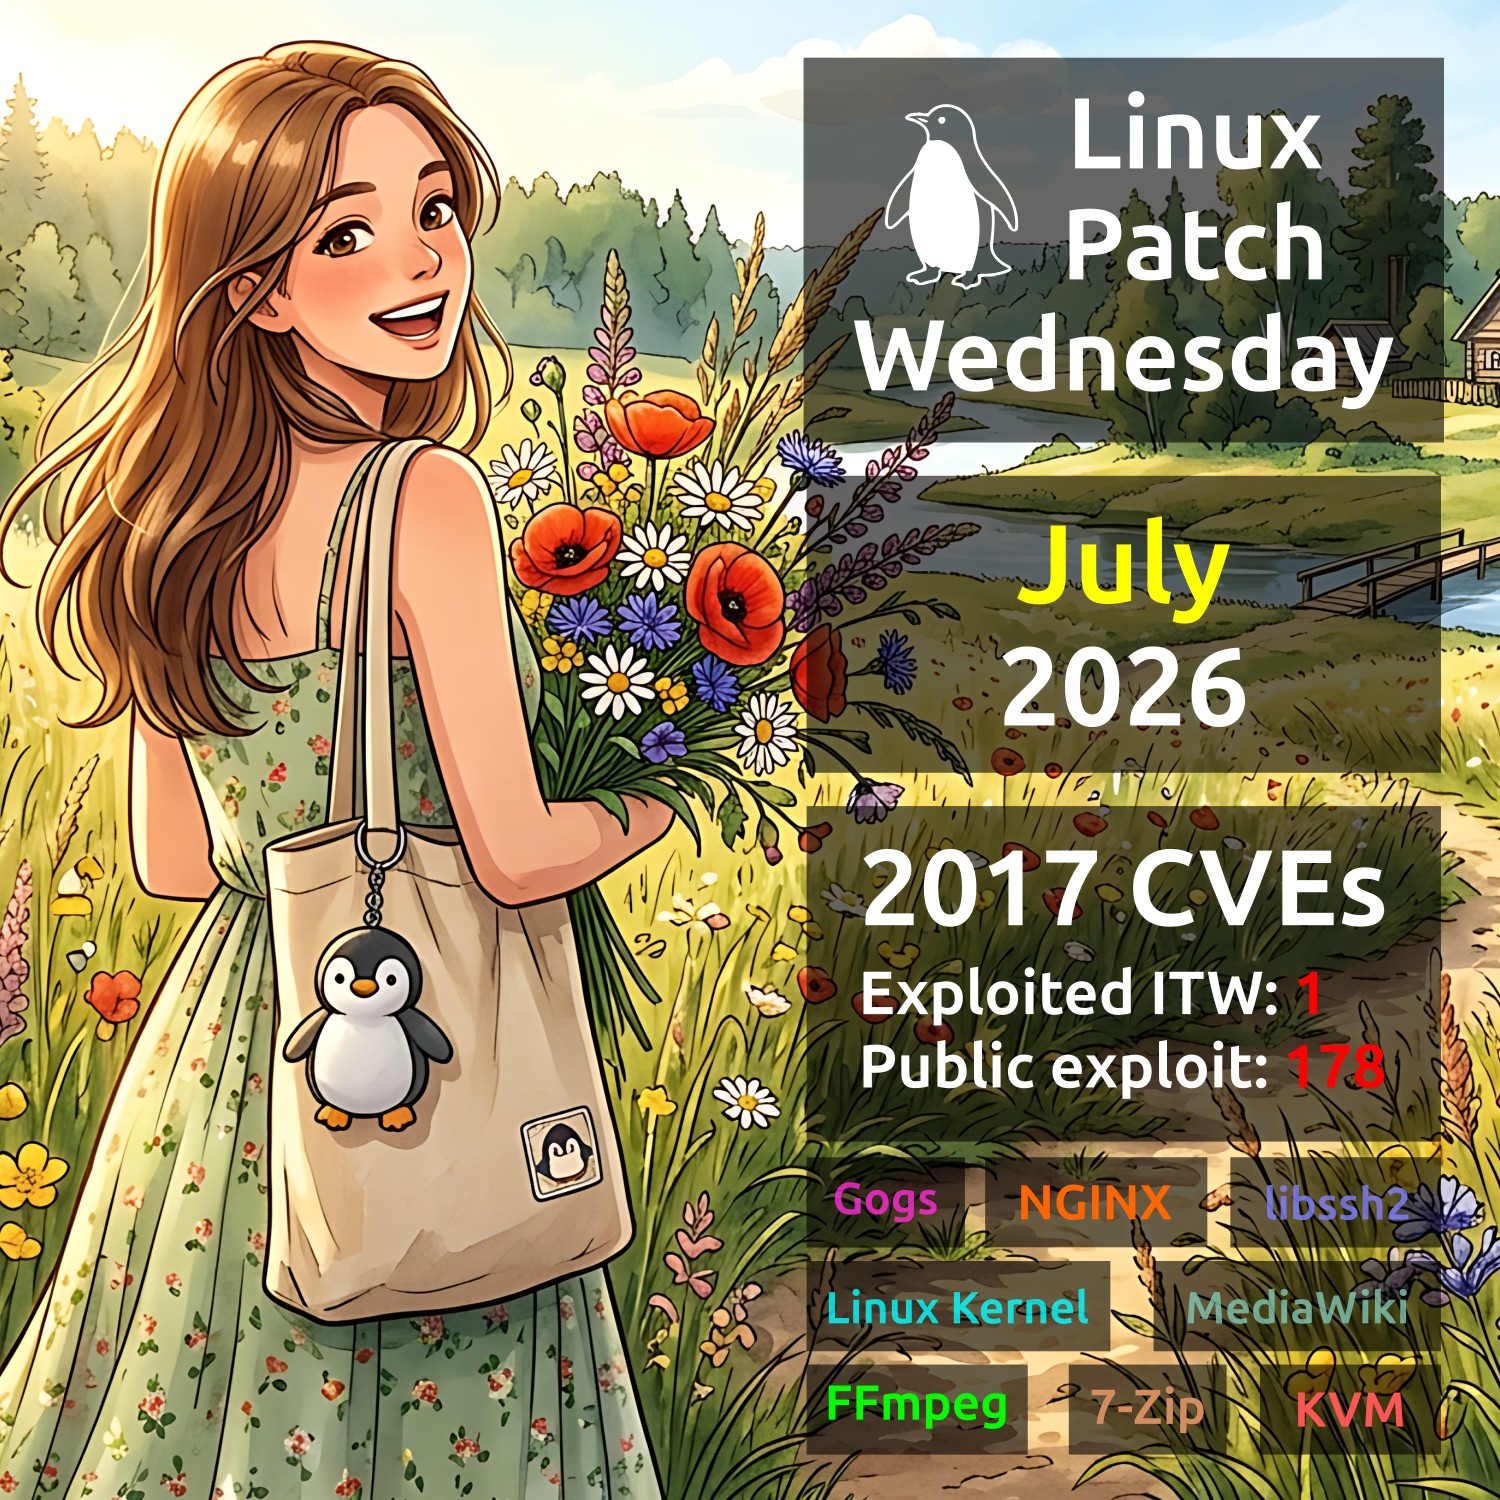
July Linux Patch Wednesday. A total of 2,017 vulnerabilities were addressed (539 in the Linux kernel and 504 in Chromium). For comparison, there were 1,888 vulnerabilities in June. Once again, a new record. Moreover, next month will most likely set another record, as 1,704 vulnerabilities have already been addressed 2.5 weeks before the August LPW. 🤷‍♂️ But for now, let's take a closer look at the July report. Only one vulnerability shows signs of exploitation in the wild:

🔻 RCE - Gogs (CVE-2025-8110). Gogs is a self-hosted web service for managing Git repositories, similar in purpose to GitHub or GitLab. An attacker can achieve remote code execution by manipulating the .git/config file through symbolic link bypasses and injecting commands via sshCommand. Multiple public exploits are available on GitHub. The vulnerability has been added to the CISA KEV catalog.

There are also 178 vulnerabilities with public exploits available or indications that they exist, but there are currently no signs of exploitation in the wild. For comparison, last month there were 109 such vulnerabilities. Among them, the following stand out:

🔸 RCE - NGINX (CVE-2026-42533). NGINX is a web server and software for handling network requests, which is often used as a reverse proxy, load balancer, and gateway for web applications. An unauthenticated attacker can exploit this vulnerability for remote code execution by sending crafted HTTP requests.

🔸 RCE - libssh2 (CVE-2026-55200). libssh2 is a C library that implements the SSH-2 protocol and allows applications to establish secure SSH connections, execute commands, and transfer files via SFTP/SCP. A remote attacker can send crafted SSH packets with excessively large packet_length values to corrupt heap memory and achieve remote code execution.

🔸 RCE - Linux Kernel "RefluXFS" (CVE-2026-64600). An attacker with an ordinary local account can exploit the vulnerability to overwrite protected files on disk and gain root privileges on affected systems, including installations running SELinux in Enforcing mode. In practice, the vulnerability allows an attacker to set an empty root password.

🔸 RCE - Gogs (CVE-2025-64111). Due to an insufficient patch for CVE-2024-56731, it is still possible to modify files in the .git directory and achieve remote command execution. Based on the exploit code, authentication is required for exploitation.

🔸 CodeInj - MediaWiki (CVE-2026-58025). MediaWiki is a free and open-source web platform for creating and managing wiki websites, powering Wikipedia and other collaborative content editing projects. An attacker with the importupload or import permission (default: sysop group) can craft a malicious XML import file containing serialized PHP objects in params fields, triggering arbitrary object instantiation and potentially leading to remote code execution through gadget chains.

🔸 RCE - FFmpeg (CVE-2026-8461). FFmpeg is a free and open-source collection of libraries and utilities for processing audio and video data. An out-of-bounds write vulnerability in FFmpeg's libavcodec library, specifically in the MagicYUV decoder, allows denial-of-service and, in some cases, can be exploited for remote code execution.

🔸 RCE - 7-Zip (CVE-2026-14266). 7-Zip is a free and open-source file archiver that allows users to create and extract archives in various formats, including its native 7z format, ZIP, RAR, and others. Crafted XZ-compressed data can trigger an overflow of a heap-based buffer. An attacker can leverage this vulnerability to execute code in the context of the current process.

🔸 MemCor - Linux Kernel (CVE-2026-53359). This is essentially a KVM vulnerability. KVM (Kernel-based Virtual Machine) is a virtualization technology built into the Linux kernel that allows multiple isolated virtual machines to run on a single physical server. A KVM escape vulnerability lets a guest escape to the host in a KVM/x86 environment. It is triggerable on both Intel and AMD.

🗒 Full Vulristics report