Tag Archives: Excel

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

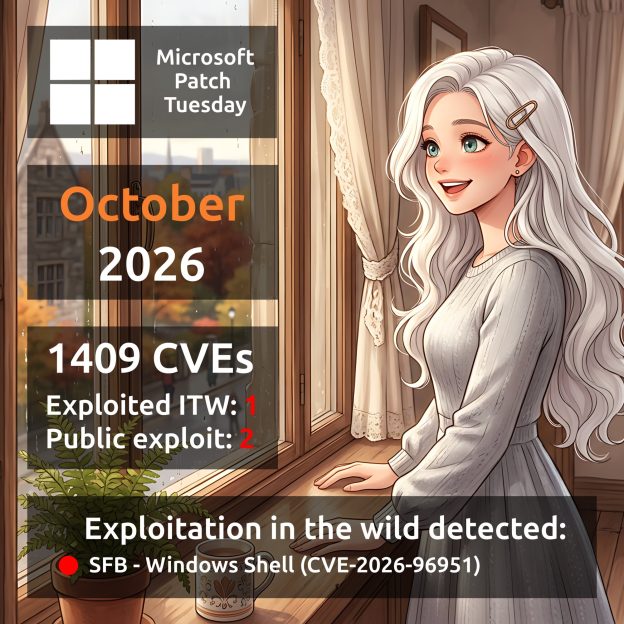
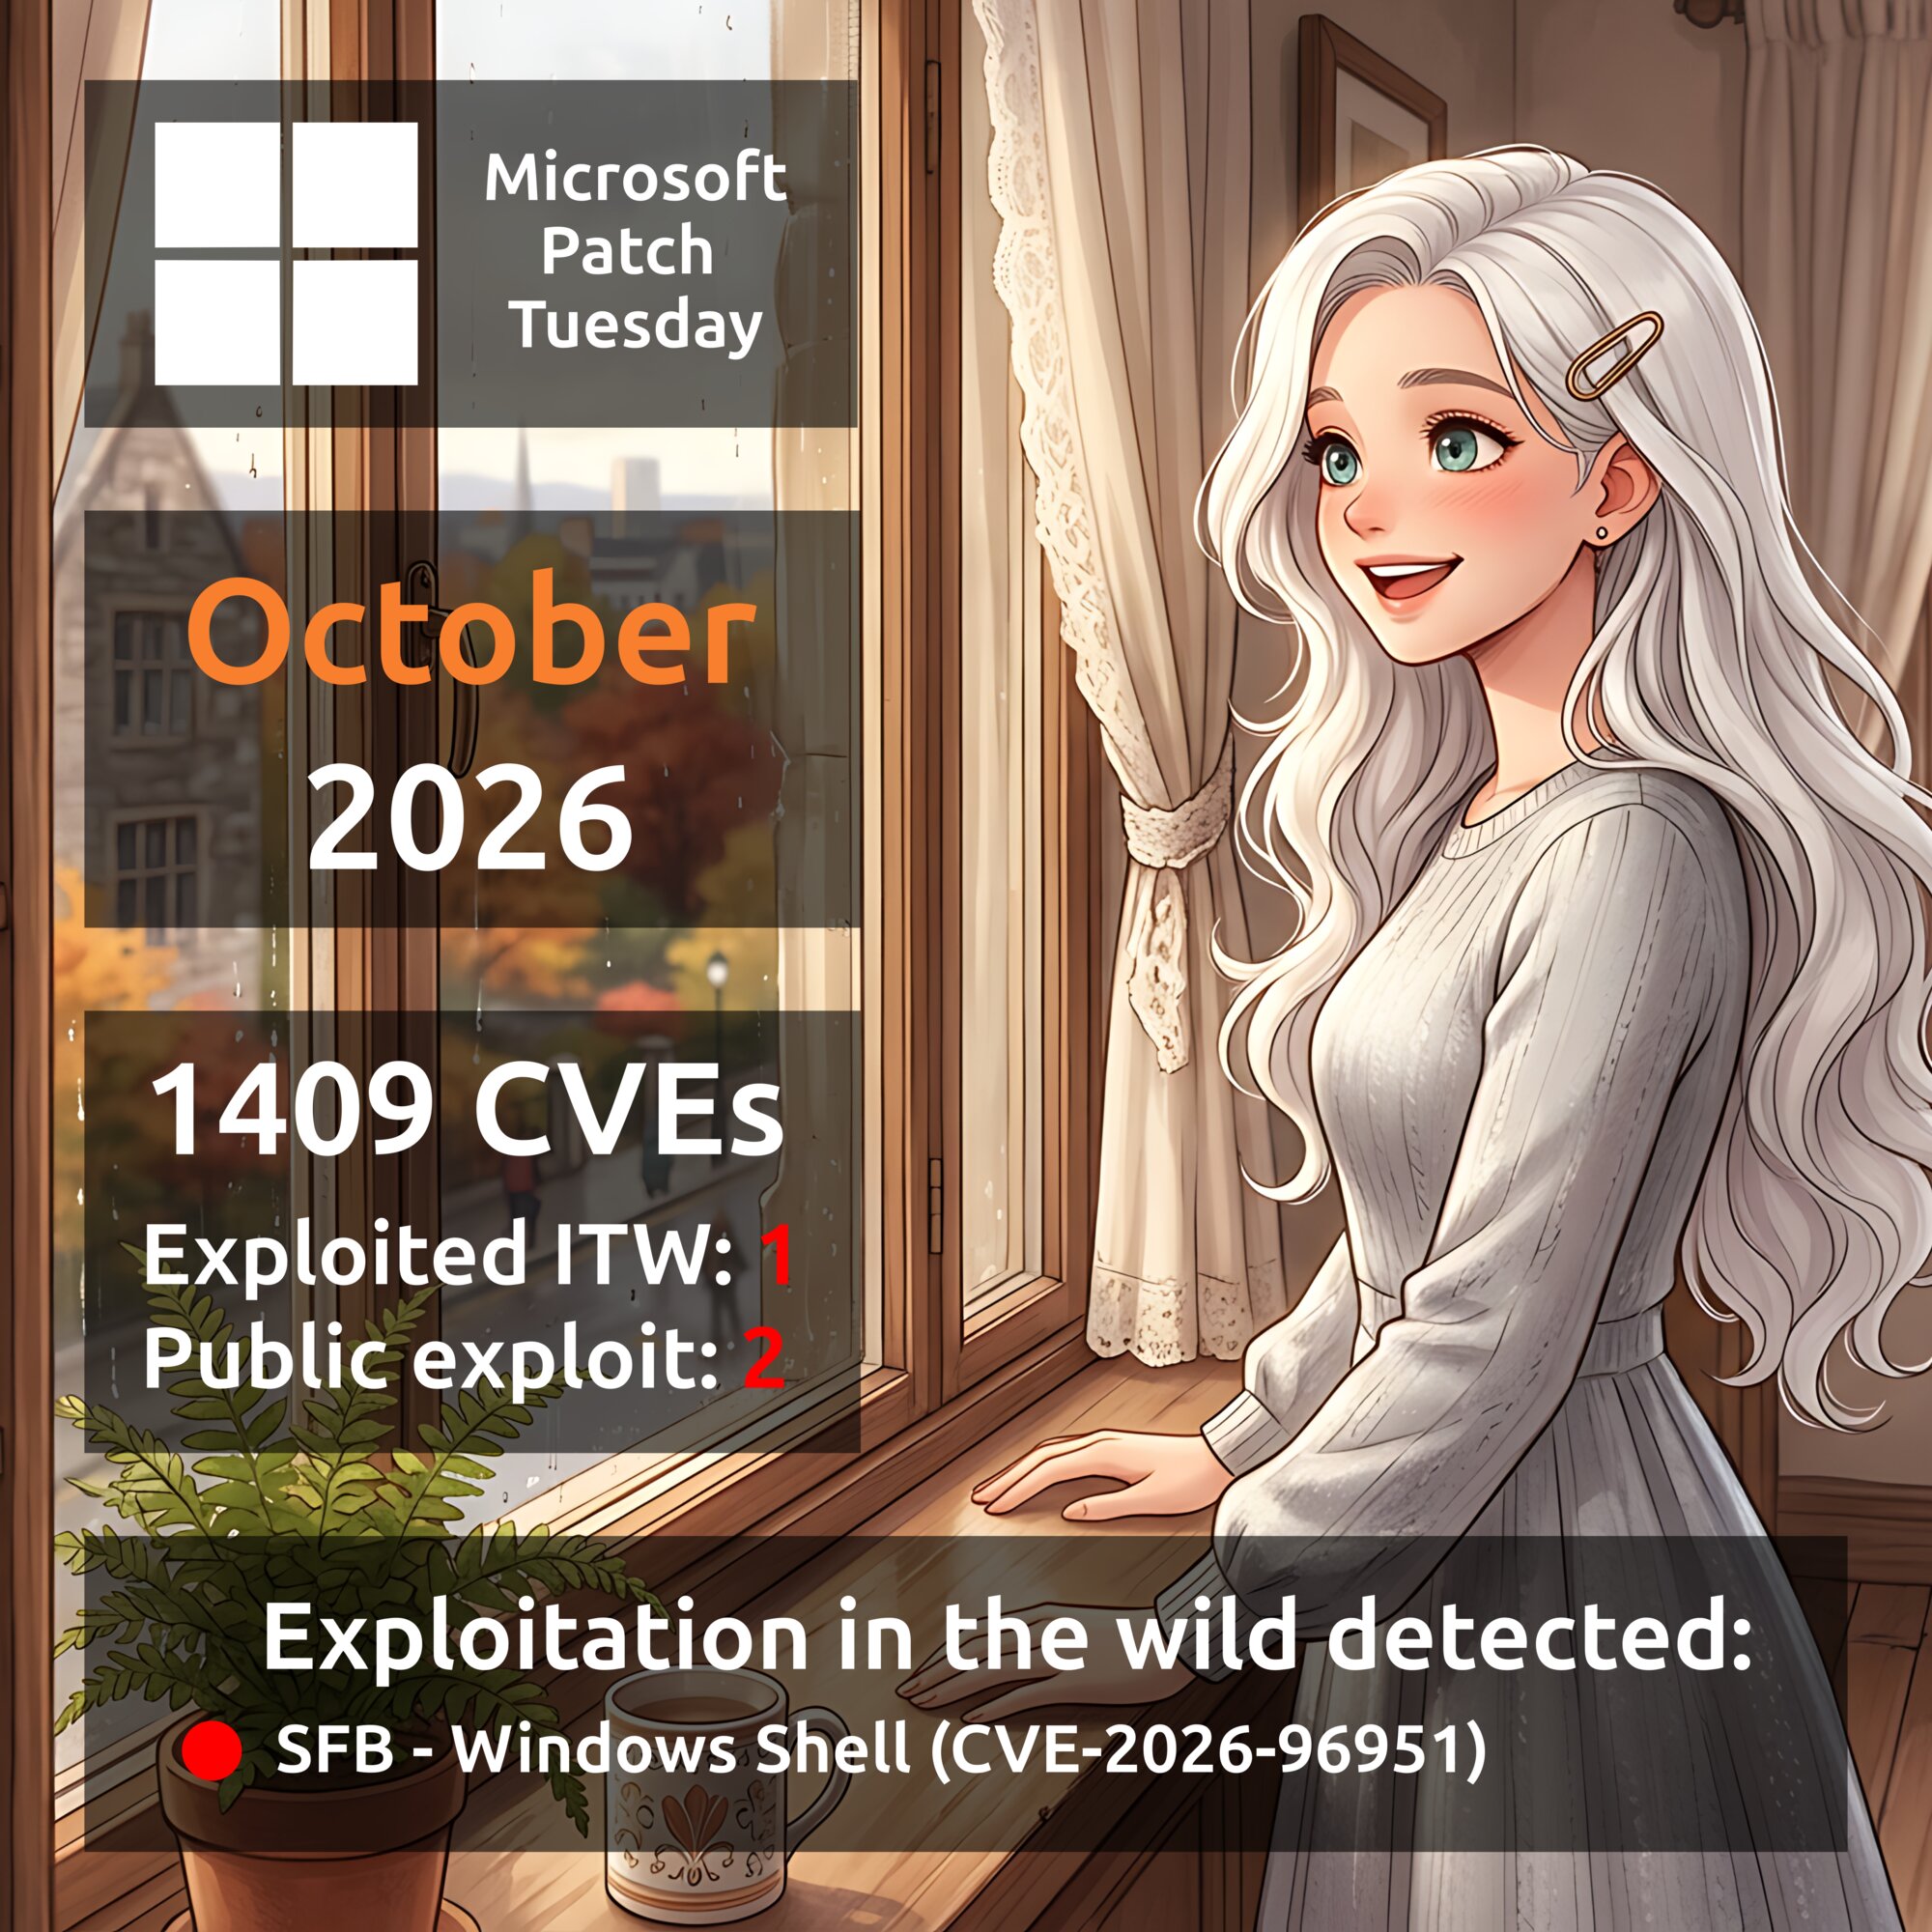
October Microsoft Patch Tuesday. A total of 1,409 vulnerabilities. For comparison, there were 973 in September, an increase of about 45%. 🙈 Thirteen products had fixes for 20 or more vulnerabilities: Microsoft Office Excel (68), Windows Kernel (46), Role: DNS Server (41), Windows Installer (38), Microsoft Office SharePoint (35), Windows Win32k (31), Windows NTFS (26), .NET (25), Microsoft Windows Search Component (23), Microsoft Office Word (22), Windows Error Reporting (21), Windows Broadcast DVR User Service (20), and Microsoft SQL Server (20). A total of 416 vulnerabilities were fixed in these products. That's 30% of all vulnerabilities. One vulnerability is flagged as exploited in the wild:

🔻 SFB - Windows Shell (CVE-2026-96951). The vulnerability allows an attacker to bypass Mark of the Web (MOTW), a Windows feature that marks files downloaded from the Internet. To exploit it, the attacker must trick the user into opening a malicious file or clicking a malicious link.

There are two vulnerabilities with public exploits:

🔸 RCE - Raw Image Extension (CVE-2026-21413). A heap-based buffer overflow in Windows Raw Image Extension allows an attacker to execute arbitrary code remotely using a specially crafted file. A technical write-up of the vulnerability, which NVD classifies as an exploit, was published on the Cisco Talos blog on April 7.

🔸 EoP - Windows Health and Optimized Experiences Service (CVE-2026-85884). Missing authentication for a critical function in Windows Health and Optimized Experiences Service allows a local attacker to gain SYSTEM privileges. A public exploit has been available on GitHub since October 13.

Other notable vulnerabilities include:

🔹 RCE - Microsoft Exchange (CVE-2026-70571). An unauthenticated attacker can send a specially crafted email to a vulnerable Exchange server and execute arbitrary code on the server. The attack requires an in-depth understanding of the target environment. No user interaction is required.

🔹 RCE - Microsoft Office Outlook (CVE-2026-70242, CVE-2026-97749, CVE-2026-97016, CVE-2026-88156, CVE-2026-70291). An attacker can execute arbitrary code on the victim's device by sending a specially crafted email. To exploit the vulnerability, the victim only needs to view the email in Outlook's reading pane without opening it or taking any further action.

🔹 RCE - Windows Domain Name Service (CVE-2026-96113). A heap-based buffer overflow in DNS Server allows an unauthorized attacker to execute code over a network.

🔹 SFB - .NET Framework (CVE-2026-108398). An authenticated attacker can place a specially crafted .NET assembly on an affected system and register it to be loaded by a protected process. This allows the attacker to bypass Windows Defender Application Control (WDAC) restrictions and run unauthorized code within the protected process. No user interaction is required.

🔹 Spoofing - Microsoft Exchange (CVE-2026-70279). An attacker can send a specially crafted link to a user and trick them into opening it. No authentication is required. If the user has administrator privileges, the attacker could act as that user and access or modify the organization's data.
🗒 Full Vulristics report

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday. A total of 79 vulnerabilities, about one and a half times more than in February. What's truly unusual is that this time there were no vulnerabilities with signs of exploitation in the wild or a public exploit! 🤔 At least not yet. 😏

The following vulnerabilities can be highlighted:

🔹 RCE - Print Spooler (CVE-2026-23669), Office (CVE-2026-26110, CVE-2026-26113), Excel (CVE-2026-26107, CVE-2026-26108, CVE-2026-26109, CVE-2026-26112), SharePoint Server (CVE-2026-26106, CVE-2026-26114)
🔹 EoP - SQL Server (CVE-2026-21262, CVE-2026-26115, CVE-2026-26116), Windows Kernel (CVE-2026-24287, CVE-2026-24289, CVE-2026-26132), Windows Win32k (CVE-2026-24285), SMB Server (CVE-2026-24294, CVE-2026-26128), Windows Graphics Component (CVE-2026-23668), .NET (CVE-2026-26131)
🔹 DoS - .NET (CVE-2026-26127)

🗒 Full Vulristics report

На русском

May Microsoft Patch Tuesday

May Microsoft Patch TuesdayMay Microsoft Patch TuesdayMay Microsoft Patch TuesdayMay Microsoft Patch TuesdayMay Microsoft Patch TuesdayMay Microsoft Patch TuesdayMay Microsoft Patch Tuesday

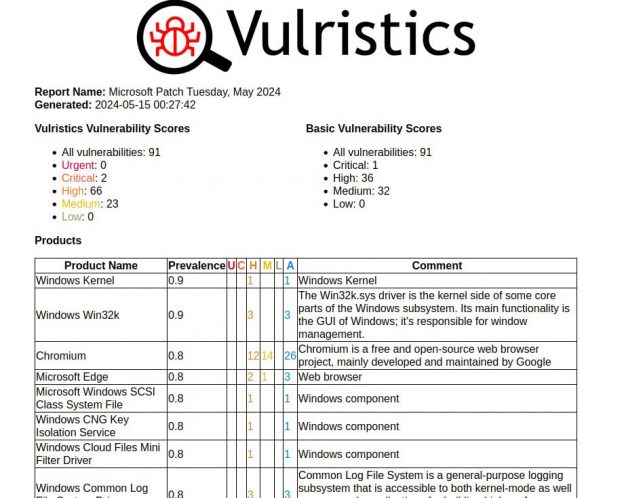
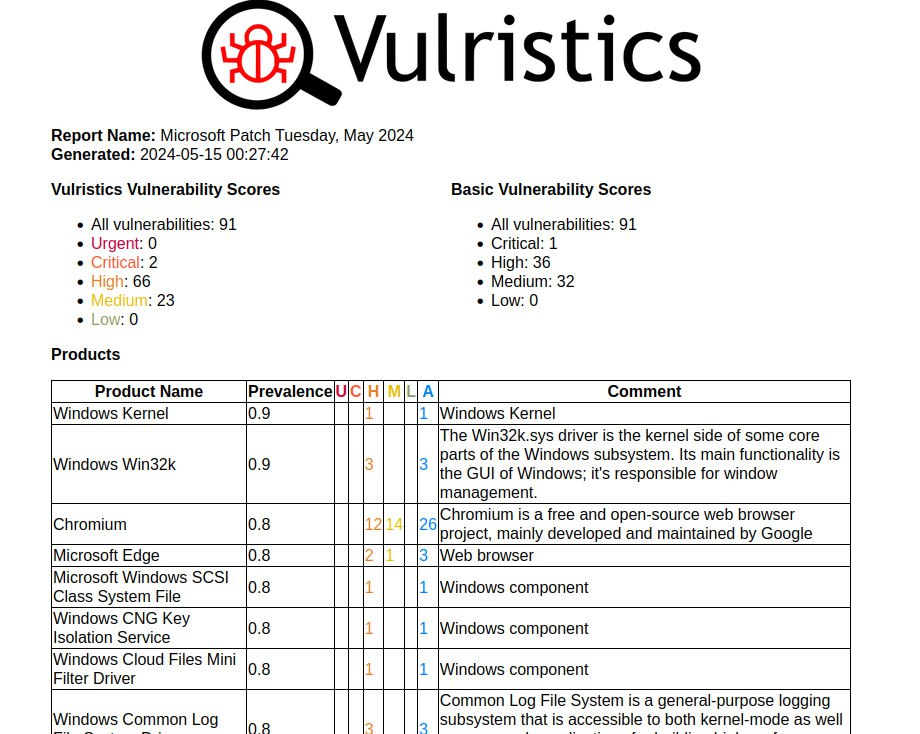
May Microsoft Patch Tuesday. There are 91 vulnerabilities in total. Of those, 29 were added between April and May Patch Tuesday.

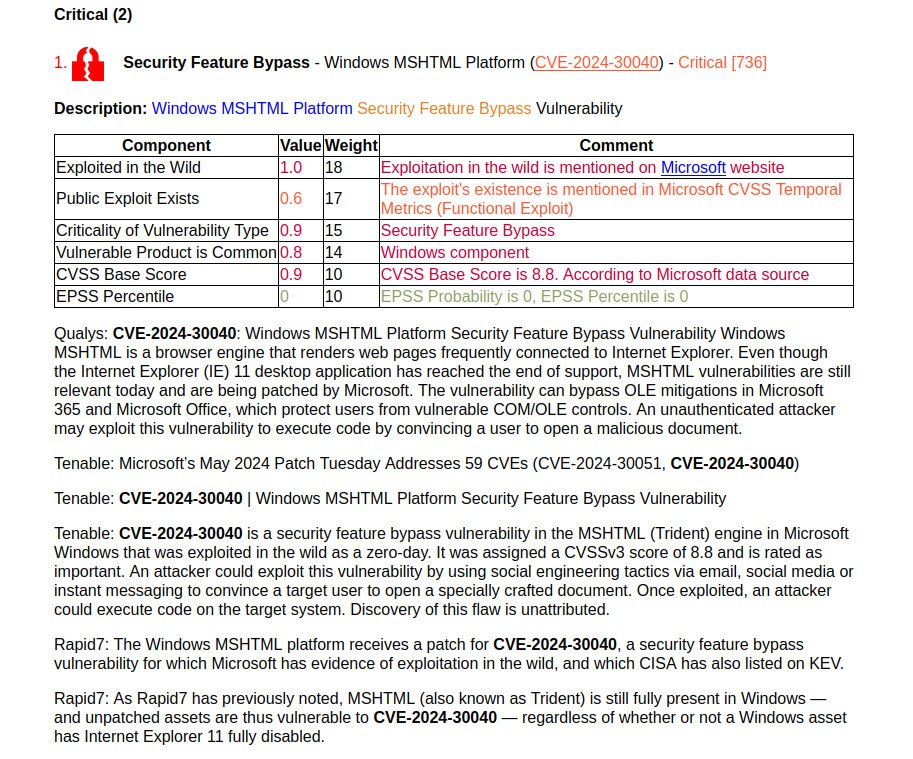
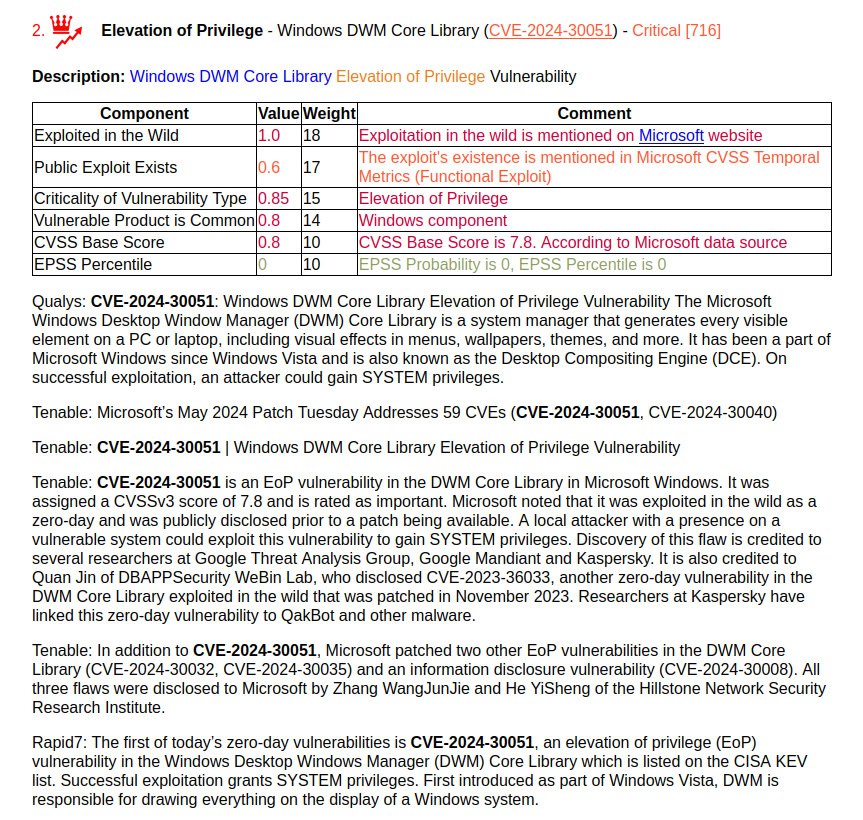
Two vulnerabilities have signs of exploitation in the wild and the presence of a functional exploit (not yet public):

🔻 Security Feature Bypass - Windows MSHTML Platform (CVE-2024-30040). In fact, an attacker can execute arbitrary code when the victim opens a specially crafted document. It is exploited through phishing.
🔻 Elevation of Privilege - Windows DWM Core Library (CVE-2024-30051). A local attacker can gain SYSTEM privileges on the vulnerable host. Microsoft credits four different groups for reporting the bug, indicating that the vulnerability is being widely exploited. The vulnerability is associated with the QakBot malware.

Among the rest we can note:

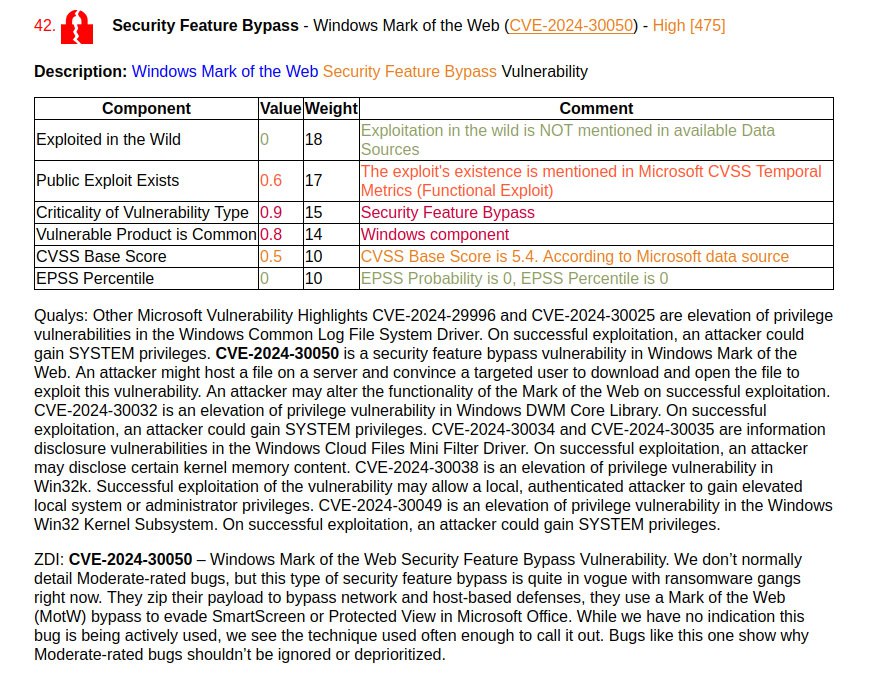
🔸 Security Feature Bypass - Windows Mark of the Web (CVE-2024-30050). Such vulnerabilities have been frequently exploited recently. Microsoft indicates that there is a functional exploit (private) for the vulnerability.
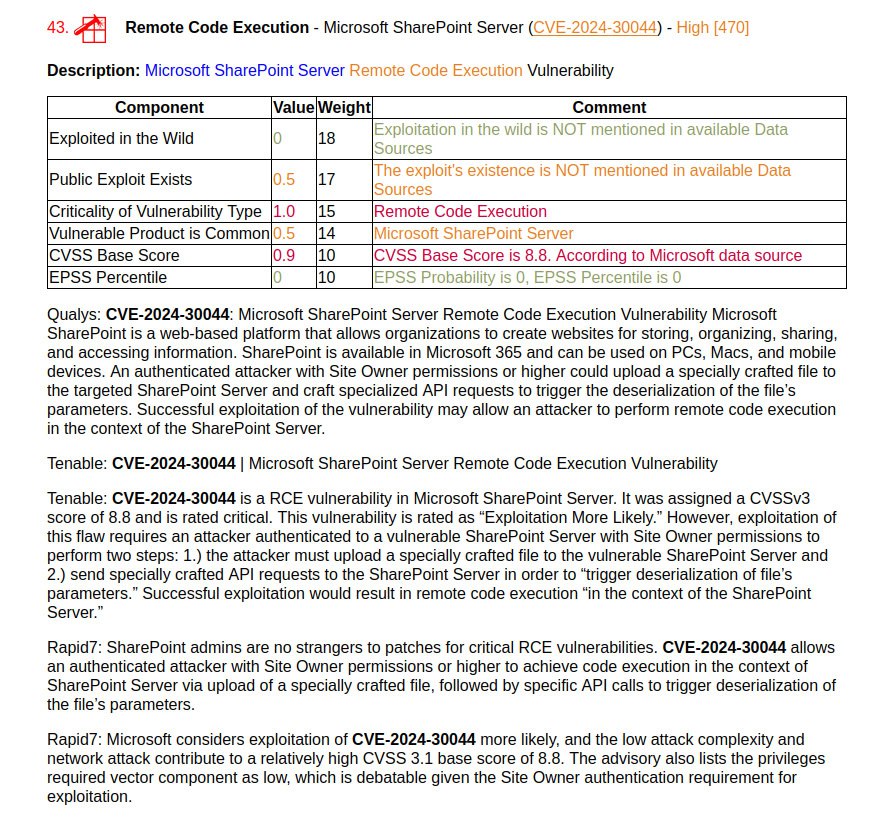
🔸 Remote Code Execution - Microsoft SharePoint Server (CVE-2024-30044). An authenticated attacker with Site Owner privileges or higher can execute arbitrary code in the context of SharePoint Server by uploading a specially crafted file.
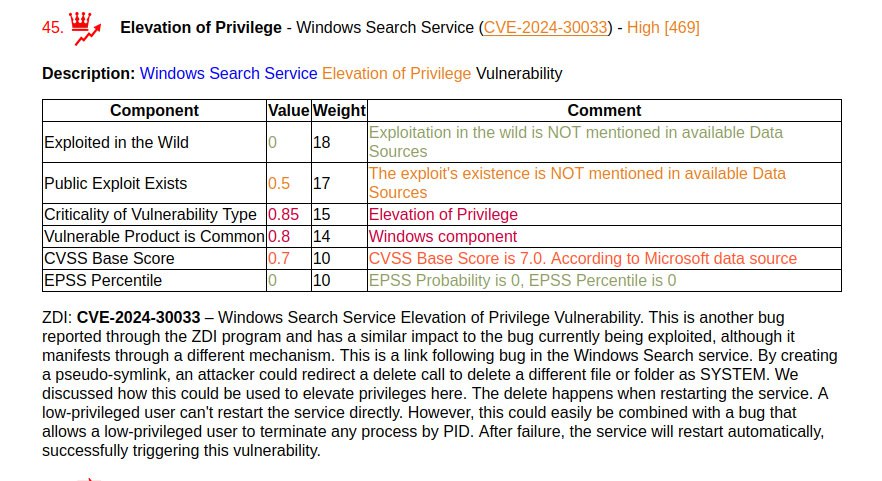
🔸 Elevation of Privilege - Windows Search Service (CVE-2024-30033). ZDI believes that the vulnerability has the potential to be exploited in the wild.
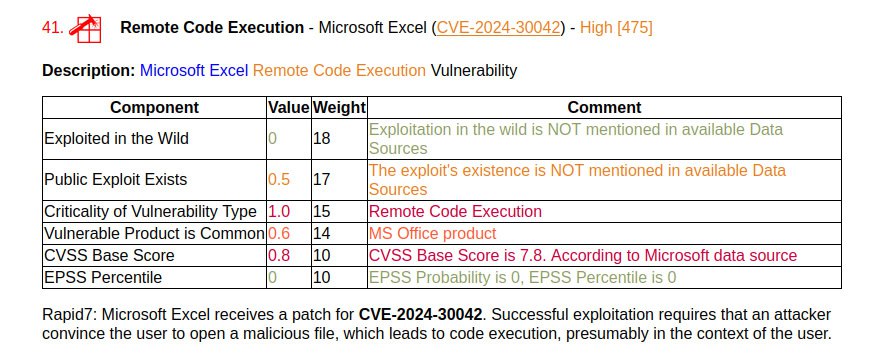
🔸 Remote Code Execution - Microsoft Excel (CVE-2024-30042). An attacker can execute code, presumably in the user's context, when a malicious file is opened.

🗒 Vulristics report

На русском

First impressions of the April Microsoft Patch Tuesday

First impressions of the April Microsoft Patch Tuesday
First impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch TuesdayFirst impressions of the April Microsoft Patch Tuesday

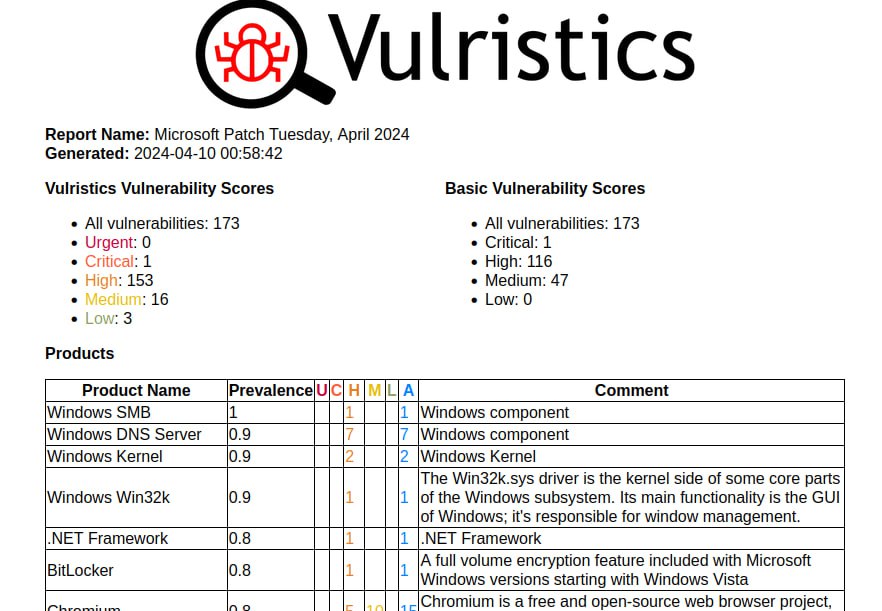
First impressions of the April Microsoft Patch Tuesday. I don't even know what to write. 🤪 Very strange! 173 vulnerabilities, of which 23 were added since the last Patch Tuesday.

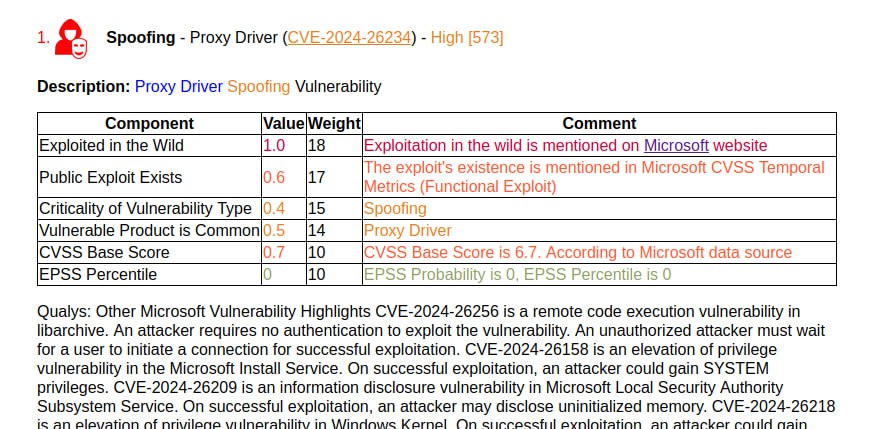
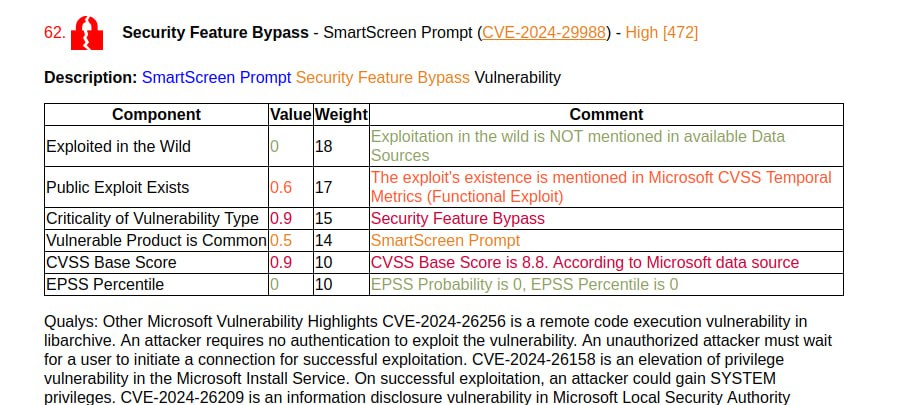
Microsoft flags one vulnerability as being exploited in the wild: Spoofing - Proxy Driver (CVE-2024-26234). And only Qualys briefly mentions it. Literally like this: "Microsoft has not disclosed any information about the vulnerability". 😅 ZDI also claims that Security Feature Bypass - SmartScreen Prompt (CVE-2024-29988) is being exploited in the wild, which is a Mark of the Web (MotW) bypass.

There are no exploits for anything yet. The following vulnerabilities can be highlighted:

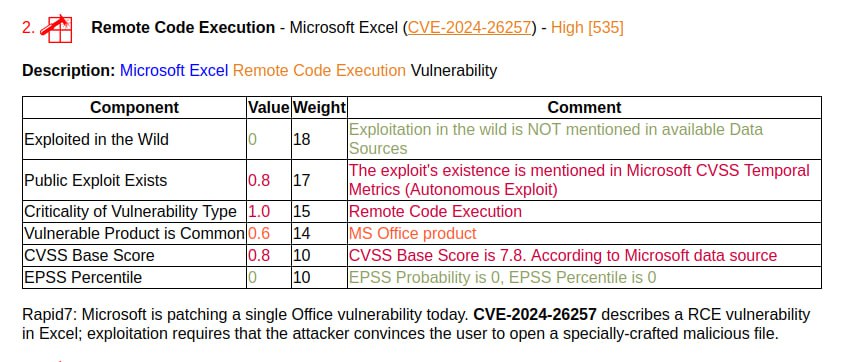
🔸 Remote Code Execution - Microsoft Excel (CVE-2024-26257). Can be exploited by an attacker when the victim opens a specially crafted file.
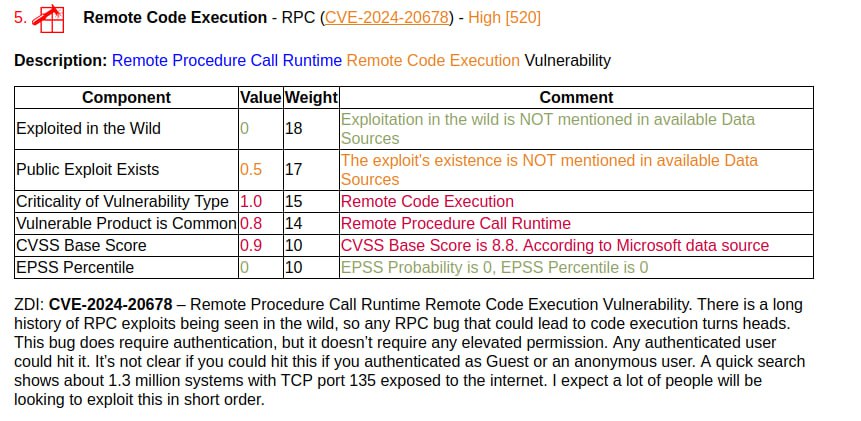
🔸 Remote Code Execution - RPC (CVE-2024-20678). It is highlighted by ZDI, which also claims 1.3 million exposed TCP 135 ports.
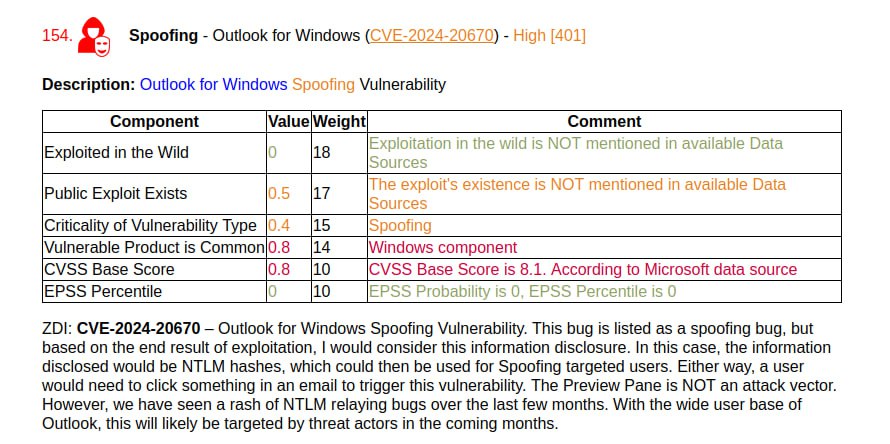
🔸 Spoofing - Outlook for Windows (CVE-2024-20670). ZDI writes that this is an Information Disclosure vulnerability that can be used in NTLM relay attacks.
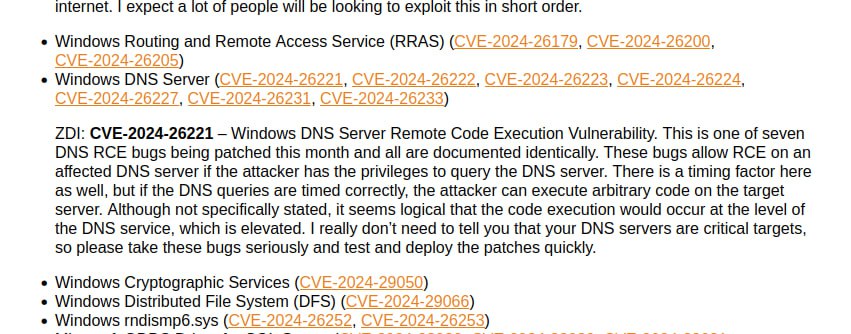
🔸 Remote Code Execution - Windows DNS Server (CVE-2024-26221, CVE-2024-26222, CVE-2024-26223, CVE-2024-26224, CVE-2024-26227, CVE-2024-26231, CVE-2024-26233). Maybe some of this will be exploited in the wild, ZDI particularly highlights CVE-2024-26221.
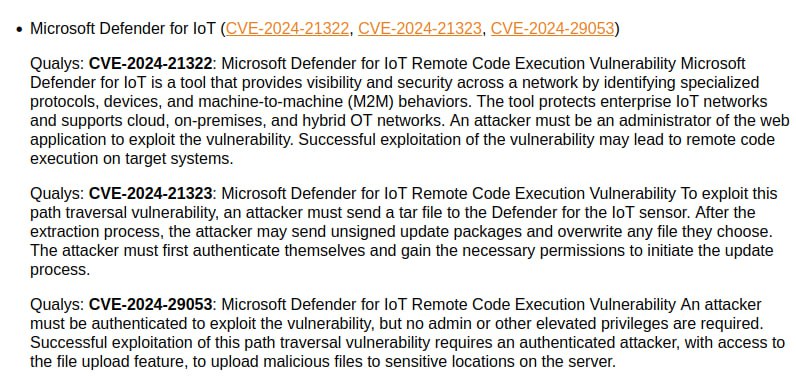
🔸 Remote Code Execution - Microsoft Defender for IoT (CVE-2024-21322, CVE-2024-21323, CVE-2024-29053). It is an IoT and ICS/OT security solution that can be deployed on-prem.

There are simply indecently massive fixes:

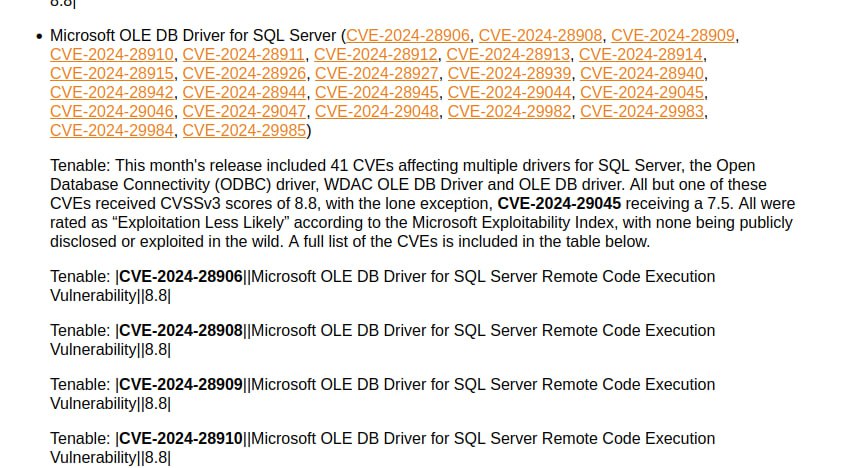
🔹 Remote Code Execution - Microsoft OLE DB Driver for SQL Server / Microsoft WDAC OLE DB Provider for SQL Server / Microsoft WDAC SQL Server ODBC Driver. 28 CVEs! I won’t even list everything here. 😨
🔹 Security Feature Bypass - Secure Boot. 23 CVEs!

🗒 Vulristics report

На русском

Upd. 10.04 I slightly tweaked the vulnerability type detection to increase the priority of the detection based on the Microsoft generated description compared to the detection based on CWE. In particular, the type of vulnerability for Spoofing - Proxy Driver (CVE-2024-26234) and Spoofing - Outlook for Windows (CVE-2024-20670) has changed.

November 2023 - January 2024: New Vulristics Features, 3 Months of Microsoft Patch Tuesdays and Linux Patch Wednesdays, Year 2023 in Review

November 2023 – January 2024: New Vulristics Features, 3 Months of Microsoft Patch Tuesdays and Linux Patch Wednesdays, Year 2023 in Review. Hello everyone! It has been 3 months since the last episode. I spent most of this time improving my Vulristics project. So in this episode, let’s take a look at what’s been done.

Alternative video link (for Russia): https://vk.com/video-149273431_456239139

Also, let’s take a look at the Microsoft Patch Tuesdays vulnerabilities, Linux Patch Wednesdays vulnerabilities and some other interesting vulnerabilities that have been released or updated in the last 3 months. Finally, I’d like to end this episode with a reflection on how my 2023 went and what I’d like to do in 2024.

Continue reading →

Microsoft Patch Tuesday March 2023: Outlook EoP, MOTW Bypass, Excel DoS, HTTP/3 RCE, ICMP RCE, RPC RCE

Microsoft Patch Tuesday March 2023: Outlook EoP, MOTW Bypass, Excel DoS, HTTP/3 RCE, ICMP RCE, RPC RCE. Hello everyone! This episode will be about Microsoft Patch Tuesday for March 2023, including vulnerabilities that were added between February and March Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239119

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Tenable, Rapid7, ZDI Patch Tuesday reviews.

Microsoft Patch Tuesday for March 2023 was quite refreshing. 😈

Continue reading →

Vulristics Command Line Interface, improved Product & Vuln. Type Detections and Microsoft Patch Tuesday November 2021

Vulristics Command Line Interface, improved Product & Vuln. Type Detections and Microsoft Patch Tuesday November 2021. Hello everyone! In this episode I want to highlight the latest changes in my Vulristics project. For those who don’t know, this is a utility for prioritizing CVE vulnerabilities based on data from various sources.. Currently Microsoft, NVD, Vulners, AttackerKB.

Command Line Interface

I started working on the CLI for Vulristics. Of course, it is not normal to edit scripts every time to release a report.

Continue reading →