Tag Archives: Github

September Linux Patch Wednesday

September Linux Patch Wednesday

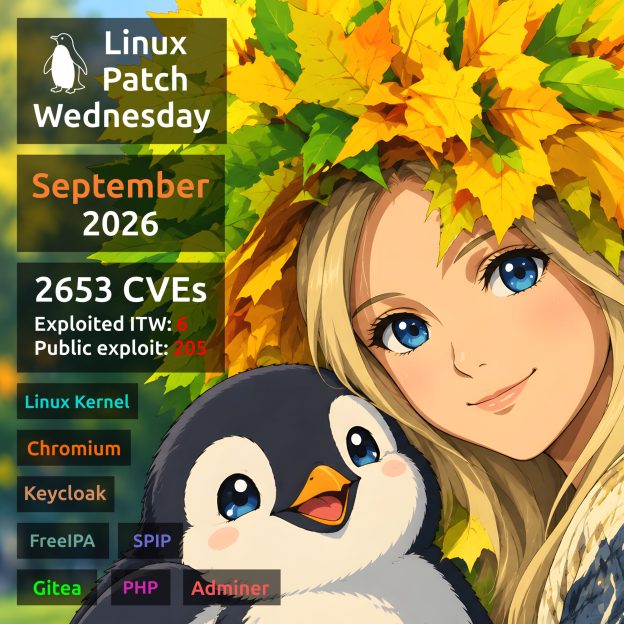
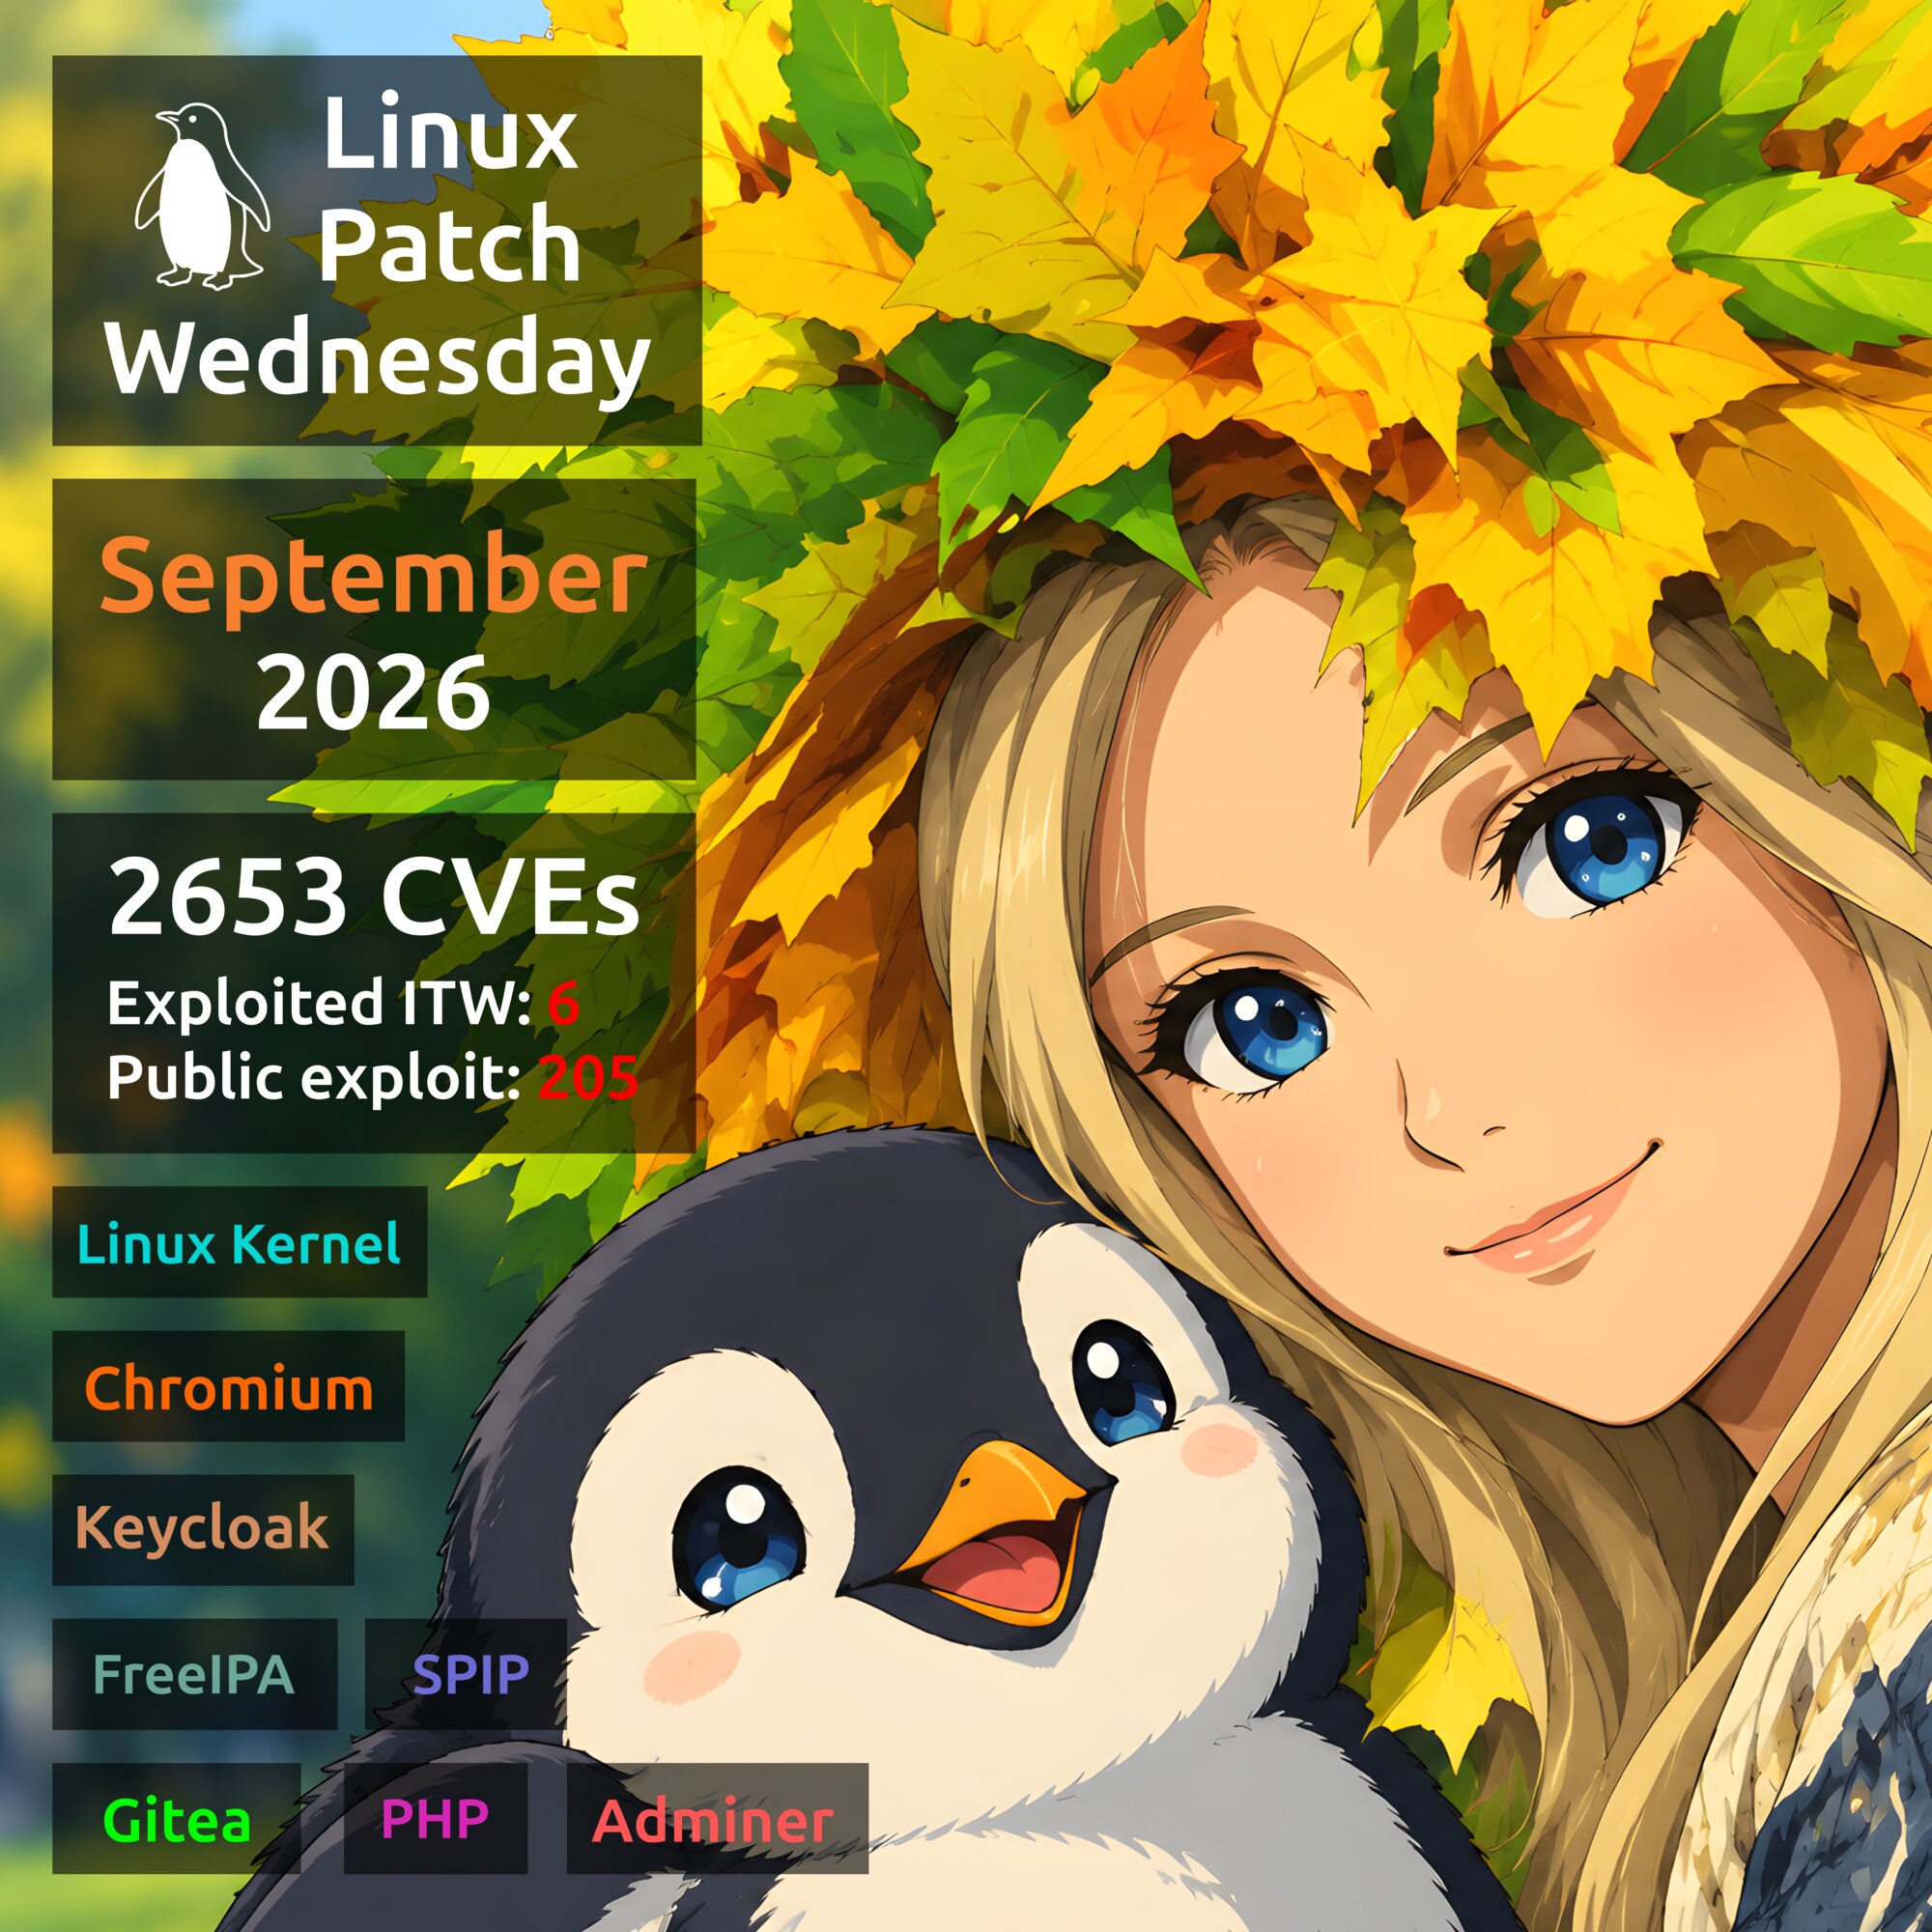
September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.
🗒 Full Vulristics report

July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability

July In the Trend of VM (#29): Microsoft Exchange Server vulnerability

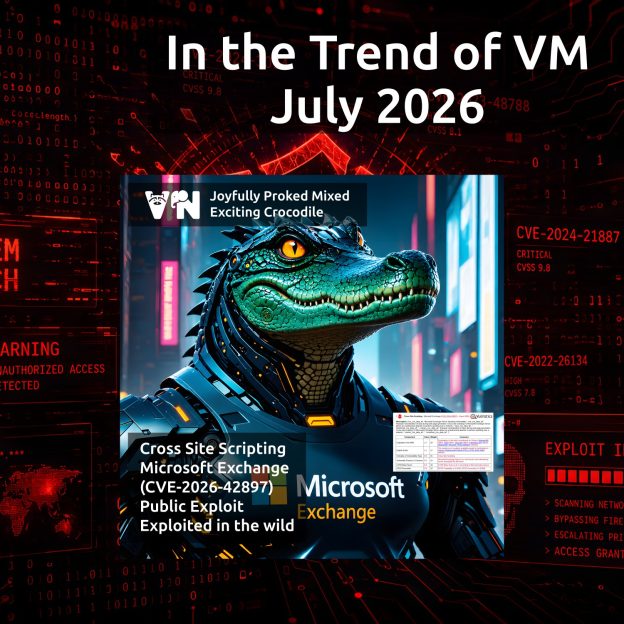
July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability. Here is my traditional monthly roundup of trending vulnerabilities, according to Positive Technologies. The previous June edition featured four vulnerabilities. This time, there's only one.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 XSS - Microsoft Exchange (CVE-2026-42897). The vulnerability allows attackers to execute arbitrary JavaScript in a user's browser when the user opens a malicious email in Outlook Web Access (OWA). A public proof-of-concept exploit is available, and the vulnerability has already been exploited in the wild.

🟥 The full list of trending vulnerabilities is available on the portal

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability. The vulnerability was fixed on May 14 outside the regular Microsoft Patch Tuesday cycle. Improper neutralization of input during web page generation (CWE-79, XSS) in Microsoft Exchange Server allows an unauthorized attacker to perform spoofing over a network. In practical terms, this means that a remote attacker could exploit this vulnerability by sending a specially crafted email to a user. If the user opens the email in Outlook Web Access and certain interaction conditions are met, arbitrary JavaScript can be executed in the browser context. As a result, the attacker may gain control of the user's mailbox by using an active user session.

👾 Microsoft experts immediately reported signs of active exploitation in the wild for this vulnerability. The vulnerability was added to the CISA KEV on May 15.

⚒️ A public exploit for the vulnerability was published on GitHub on May 15 as well.

⚙️ Initially, mitigation measures were recommended to address the vulnerability, delivered via the Exchange Emergency Mitigation (EM) service or by using the Exchange on-premises Mitigation Tool (EOMT) script. Security updates that fix the vulnerability in Microsoft Exchange Server Subscription Edition RTM, Exchange Server 2016, and Exchange Server 2019 were released almost a month later, on June 9. Microsoft experts recommended keeping the mitigations enabled even after applying the patch, as they provide an additional layer of protection. However, applying these mitigations may cause issues (for example, errors when printing calendars and displaying images in OWA).

⚠️ Please note that Exchange Server 2016 and 2019, which are out of support, are also affected by this vulnerability. Only customers enrolled in the Period 2 Extended Security Update (ESU) program are eligible to receive Exchange Server 2016 and 2019 security updates released between May and October 2026.

June "In the Trend of VM" (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities

June In the Trend of VM (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities

June "In the Trend of VM" (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous May edition, we covered four vulnerabilities. This time, there are also four vulnerabilities associated with five CVE identifiers.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Dirty Frag" (CVE-2026-43284, CVE-2026-43500). A chain of vulnerabilities with a public exploit to obtain root access. There are signs of in-the-wild exploitation.

🔻 EoP - Linux Kernel "Fragnesia" (CVE-2026-46300). Another vulnerability for gaining root access with a public exploit.

🔻 EoP - Microsoft Defender "RedSun" (CVE-2026-41091). A privilege escalation vulnerability leading to SYSTEM-level access, with a public exploit available and indications of in-the-wild exploitation. Pay special attention to Windows server and desktop environments where Microsoft Defender is enabled but there is no Internet access for regular updates.

🔻 RCE - PAN-OS (CVE-2026-0300). An unauthenticated RCE with root privileges affecting PA-Series and VM-Series firewalls. A public exploit exists, and there are indications of in-the-wild exploitation.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Microsoft Defender "RedSun" (CVE-2026-41091) vulnerability

About Elevation of Privilege - Microsoft Defender RedSun (CVE-2026-41091) vulnerability

About Elevation of Privilege - Microsoft Defender "RedSun" (CVE-2026-41091) vulnerability. Microsoft Defender is a built-in security solution developed by Microsoft to protect the Windows operating system and user data from viruses, malware, and other cyber threats in real time. An improper link resolution vulnerability prior to file access ("link following", CWE-59) in Microsoft Defender, specifically within the Malware Protection Engine component, allows an authenticated local attacker to escalate privileges to SYSTEM level. As a result, an attacker could gain full control over the affected system, including unrestricted access to data, the ability to modify system settings, install software, manage user accounts, and disable security protections.

🛠 An exploit for the vulnerability was published on GitHub by security researcher Nightmare Eclipse on April 15, alongside exploits targeting other Windows component vulnerabilities. The account was later removed by GitHub administrators; however, this did not prevent the exploit code from spreading further.

⚙️ The security advisory and patches were released on May 19 outside Microsoft's regular Patch Tuesday schedule. Versions of Microsoft Malware Protection Engine from 1.1.26030.3008 through 1.1.26040.8 are affected. Systems with Microsoft Defender disabled are not vulnerable. By default, Microsoft Defender automatically updates Windows security components, antivirus definitions, and Microsoft Malware Protection Engine, so no additional user action is typically required. Malware Protection Engine is updated monthly or as new threats emerge, while antivirus definitions are updated several times per day. Update checks may run automatically anywhere from once to several times daily when an Internet connection is available. Manual update checks are also supported.

👾 According to Microsoft, the vulnerability is being exploited in the wild. The vulnerability was added to the CISA KEV catalog on May 20.

💡 Special attention should be paid to server and desktop Windows hosts where Microsoft Defender is not disabled, but Internet access is unavailable for regular updates.

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper. Hello everyone! This month I decided NOT to make an episode completely dedicated to Microsoft Patch Tuesday. Instead, this episode will be an answer to the question of how my Vulnerability Management month went. A retrospection of some kind.

Alternative video link (for Russia): https://vk.com/video-149273431_456239134

Continue reading →

Microsoft Patch Tuesday June 2023: Edge type confusion, Git RCE, OneNote Spoofing, PGM RCE, Exchange RCE, SharePoint EoP

Microsoft Patch Tuesday June 2023: Edge type confusion, Git RCE, OneNote Spoofing, PGM RCE, Exchange RCE, SharePoint EoP. Hello everyone! This episode will be about Microsoft Patch Tuesday for June 2023, including vulnerabilities that were added between May and June Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239127

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Tenable, Rapid7, ZDI Patch Tuesday reviews. This time there were only 3 vulnerabilities used in attacks or with a public exploit. And only one of them is more or less relevant.

Continue reading →