Tag Archives: Microsoft

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability. The Ancillary Function Driver (AFD) is a Windows component that supports Windows Sockets applications and is contained in the afd.sys file. The afd.sys driver runs in kernel mode and manages the Winsock TCP/IP communications protocol. This vulnerability is from the August Microsoft Patch Tuesday. Use-after-free (CWE-416) in the Windows Ancillary Function Driver for WinSock allows an authorized attacker to elevate privileges locally to SYSTEM level. Successful exploitation requires an attacker to win the race condition. As a result, the attacker can gain full control over the Windows host, execute commands with SYSTEM-level privileges, disable security protections, install malware, and access other users' data.

👾 The vulnerability was already being exploited in the wild when it was disclosed as part of Microsoft's August Patch Tuesday on August 11. That same day, it was added to the CISA KEV catalog. Notably, Microsoft listed the Exploit Code Maturity in the CVSS as "Unproven". 🤷‍♂️ Microsoft credited researchers from Check Point for reporting the vulnerability.

Details on how the vulnerability was exploited in attacks were published in a Check Point blog post on August 11. The vulnerability was exploited as part of the "Operation Dream Job" campaign, which targeted organizations worldwide, with a particular focus on the defense sector in Europe and India. The campaign is linked to the Lazarus Group. The campaign begins with targeted phishing messages offering victims attractive job opportunities at well-known companies in the defense, aerospace, and aviation industries. Victims are lured into opening a PDF decoy masquerading as a Lockheed Martin job description. This triggers the execution of a lightweight in-memory loader - MISTPEN. The loader uses the Microsoft Graph API to access OneDrive, from which it retrieves additional modules and runs them in memory. During the initial stages of the infection, the attacker deploys several reconnaissance modules that gather information about the system and running processes. Once the target is deemed of interest, MISTPEN retrieves an additional persistence module, which installs the malware on disk and ensures that MISTPEN is automatically launched after a system reboot. After establishing persistence, MISTPEN loads an in-memory module designed to exploit the CVE-2026-68820 vulnerability. Check Point researchers believe that this vulnerability was already being exploited in the "Operation Dream Job" campaign in early July 2026. Successful exploitation enables the malware to launch FudModule, a Lazarus kernel-level rootkit, with SYSTEM privileges. The final backdoor delivered by MISTPEN - ForestTiger - provides attackers with remote access to the compromised system, allowing them to execute commands, collect host information, and download additional malicious components.

🛠 No public exploits have been observed so far. Some people are offering exploits for sale, but they don't look reliable.

⚙️ Security updates are available for Windows 10, Windows 11, and Windows Server 2019.
September Microsoft Patch Tuesday

September Microsoft Patch Tuesday

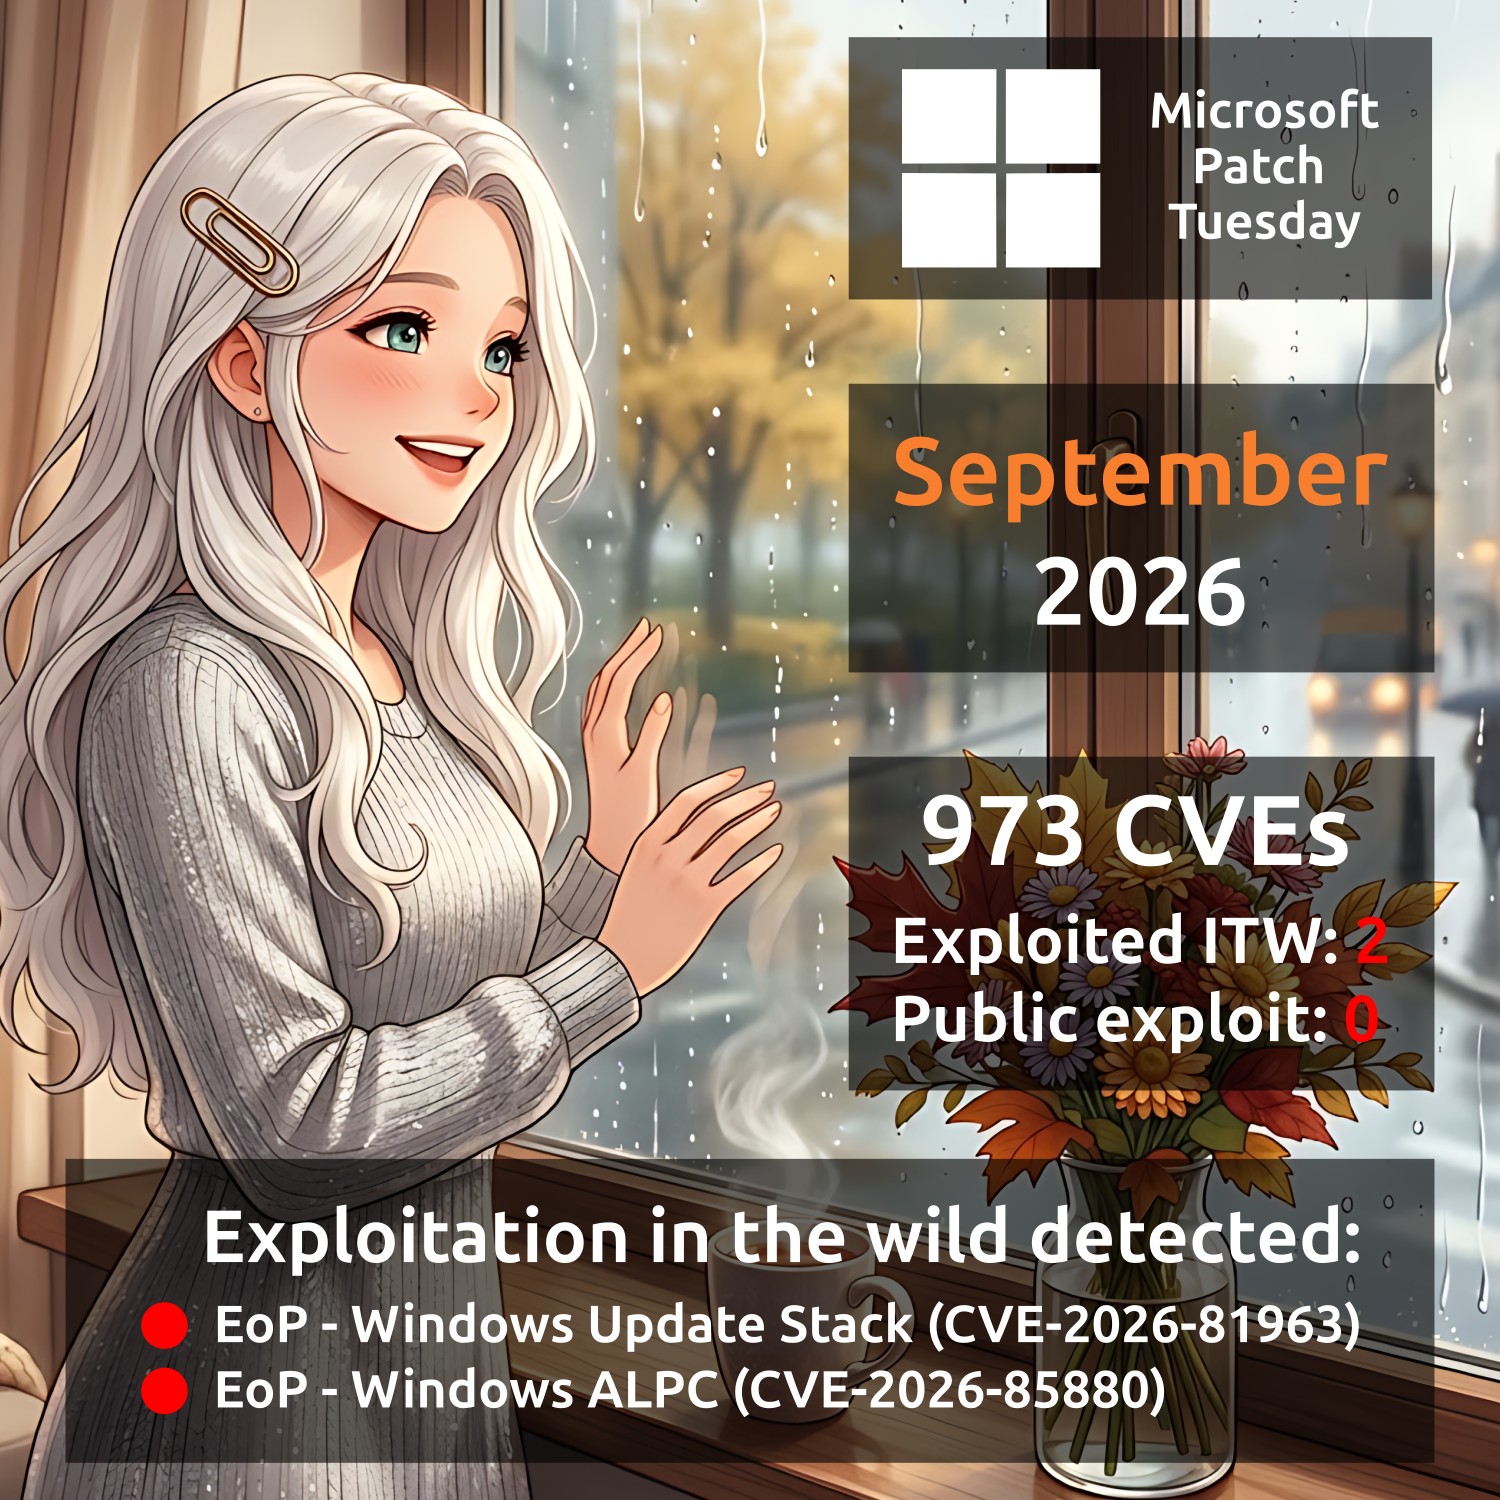
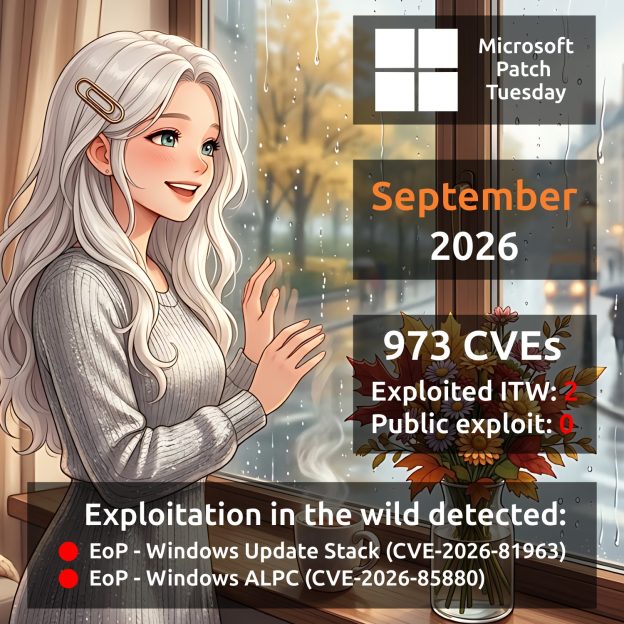
September Microsoft Patch Tuesday. A total of 973 vulnerabilities were addressed - more than twice as many as in August. Seven products had 20 or more vulnerabilities fixed: Windows Biometric Service (64), Microsoft SQL Server (54), Windows DHCP Server (36), Microsoft Office Word (35), Windows NTFS (29), Microsoft Excel (28), and Windows Win32k (24). Vulnerabilities affecting these products account for just under one-third of the total. Two vulnerabilities are known to have been exploited in the wild:

🔻 EoP - Windows Update Stack (CVE-2026-81963). A link following flaw in the Windows Update Stack (CWE-59) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

🔻 EoP - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880). A heap-based buffer overflow flaw in Windows ALPC (CWE-122) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

There are no vulnerabilities with public exploits yet. Of the remaining vulnerabilities, the following can be highlighted:

🔹 RCE - Microsoft Exchange (CVE-2026-55007). A remote, unauthenticated attacker could achieve code execution on a vulnerable Exchange server by sending an email containing a malicious Visio attachment. The code is executed when the server processes the message, without requiring the victim to open it or use the Preview Pane.

🔹 RCE - Remote Desktop Services (CVE-2026-69525). Successful exploitation of this flaw would allow an unauthenticated attacker to execute arbitrary code by exploiting a use-after-free flaw.

🔹 RCE - Windows DNS Server (CVE-2026-69730). According to the advisory, an unauthenticated, remote attacker could send a crafted packet to exploit a use-after-free flaw in Windows DNS in order to achieve remote code execution.

🔹 RCE - Windows USB Mass Storage Class Driver (CVE-2026-68839). Successful exploitation of this vulnerability could allow an attacker the ability to gain remote code execution via an in-network attacker calling arbitrary endpoints.

🔹 RCE - Windows Kerberos (CVE-2026-69676). An authentication-bypass flaw via capture-replay in Windows Kerberos may allow an authenticated attacker to execute code over a network.

🔹 RCE - Windows Key Distribution Center (CVE-2026-69712). A use-after-free flaw in the Windows Key Distribution Center may allow an authenticated attacker to execute code over a network.

🔹 EoP - Microsoft Exchange (CVE-2026-69380). An authenticated attacker with access to a mailbox through a low-privileged user account could exploit this vulnerability to gain access to other mailboxes. Successful exploitation would allow the attacker to send and receive emails on behalf of other Exchange users as well as access attachments.

🗒 Full Vulristics report

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August In the Trend of VM (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

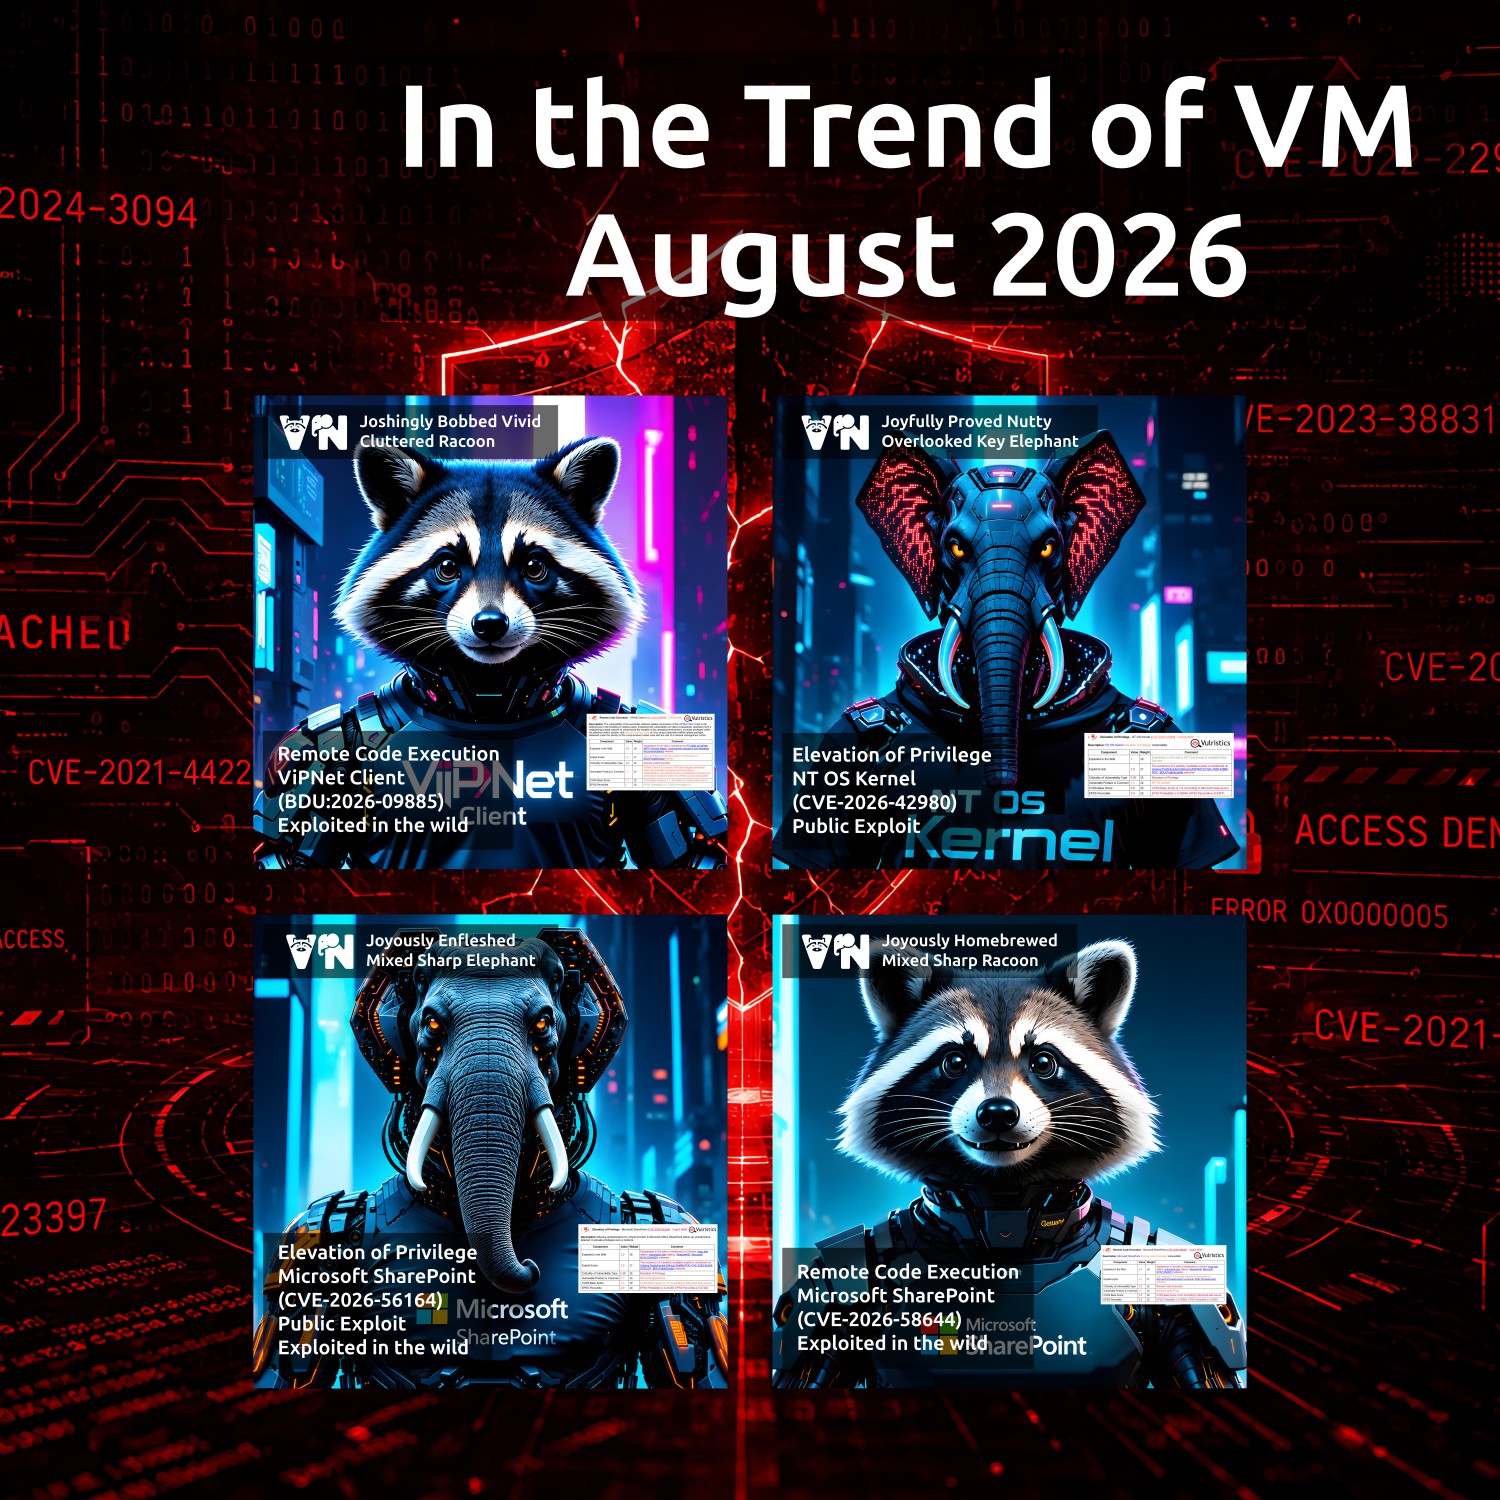
August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint. I present the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous July edition, there was just one vulnerability. This time, there are four.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - ViPNet Client (BDU:2026-09885). The first trending vulnerability in a Russian-made product since the beginning of 2026. Its exploitation was discovered by Positive Technologies experts.

🔻 EoP - NT OS Kernel (CVE-2026-42980). The vulnerability allows an attacker to escalate privileges to NT AUTHORITY\SYSTEM level.

🔻 EoP - Microsoft SharePoint (CVE-2026-56164) and RCE - Microsoft SharePoint (CVE-2026-58644). Two actively exploited vulnerabilities in a popular platform for building corporate websites, managing documents, and collaborating.

🟥 The full list of trending vulnerabilities is available on the portal

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

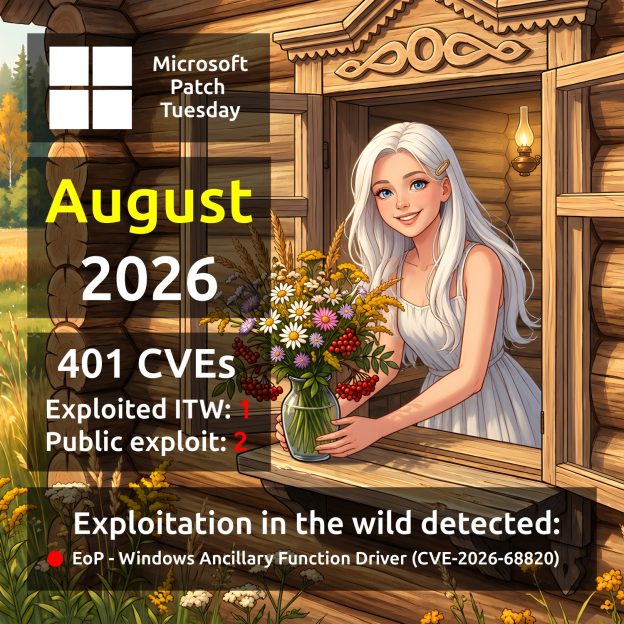
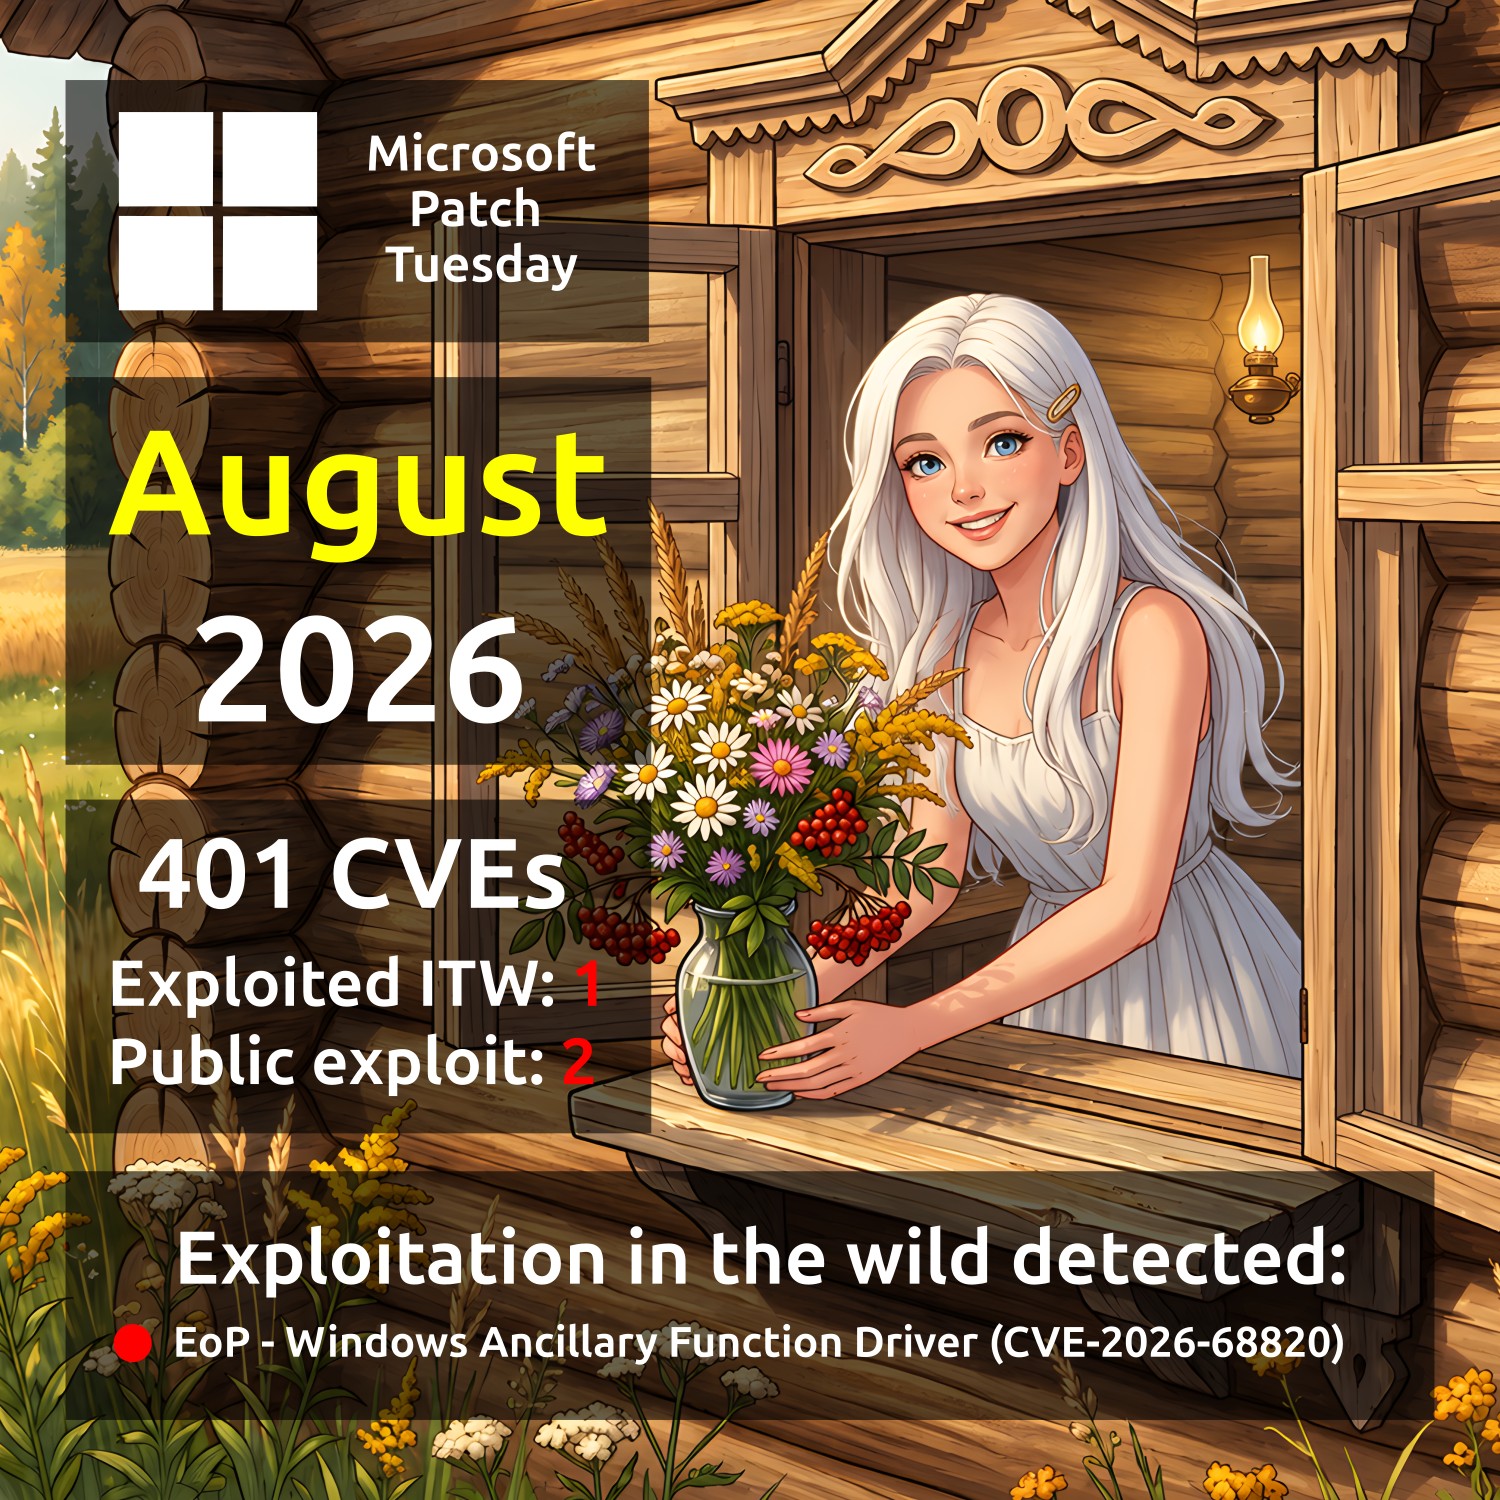
August Microsoft Patch Tuesday. A total of 401 vulnerabilities were addressed - 170 fewer than in July. One of the vulnerabilities is known to be actively exploited in the wild:

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). A local attacker can exploit this vulnerability to gain SYSTEM-level privileges. There is a contradiction in Microsoft's description: the Exploit Code Maturity in CVSS is marked as "Unproven", while at the same time Microsoft states that the vulnerability is being exploited in the wild. 🤷‍♂️

Public exploits are available for two other vulnerabilities:

🔸 EoP - Windows User Profile Service (CVE-2026-62832). This vulnerability allows an authenticated attacker to elevate privileges to ADMINISTRATOR level. Rapid7 believes this vulnerability is related to the LegacyHive exploit, which was published on July 14.

🔸 EoP - Windows Kernel (CVE-2026-62737). This vulnerability allows an authenticated attacker to elevate privileges to SYSTEM level. An exploit has been publicly available since August 11.

Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Windows DNS Server (CVE-2026-62878). This wormable vulnerability allows a remote unauthenticated attacker to execute code on a vulnerable server with elevated privileges. It is recommended to test and install the update as soon as possible, especially on Internet-facing DNS servers.

🔹 RCE - Windows Deployment Services TFTP Server (CVE-2026-62893). This vulnerability, discovered as part of the ZDI (Zero Day Initiative) program, allows an attacker to execute code without authentication or user interaction. TFTP has no authentication mechanism and is available remotely via UDP port 69. Any WDS server serving Windows Imaging Format (WIM) files via TFTP, which is the standard PXE boot scenario, is vulnerable. The issue results from the lack of validation of the existence of an object before performing operations on it. UDP port 69 should be blocked at the perimeter, but attackers could easily use this vulnerability for lateral movement within an organization. If you're using WDS for deployments, test and install this update quickly.

🔹 RCE - Windows DHCP Server (CVE-2026-62823). Successful exploitation of this vulnerability allows a remote unauthenticated attacker to execute arbitrary code from an adjacent network by sending a specially crafted packet that triggers a heap-based buffer overflow.

🔹 EoP - Microsoft Exchange (CVE-2026-62911). This vulnerability allows a remote authenticated attacker (with Privileges Required: Low according to CVSS) to gain control over the mailboxes of all Exchange users, send and read emails, and download attachments. This vulnerability was demonstrated at Pwn2Own Berlin. ZDI researchers provided Microsoft with working exploits.

🔹 RCE - Microsoft QUIC (CVE-2026-62815). This use-after-free vulnerability allows an unauthenticated attacker to execute arbitrary code on a target system by sending a specially crafted network packet. QUIC is an IETF-standardized transport protocol that runs over UDP instead of TCP and serves as the foundation for HTTP/3. The protocol is used by approximately 13.5 million websites.

🔹 Tampering - Windows Container Isolation FS Filter Driver (unionfs.sys) (CVE-2026-72971). This vulnerability reportedly allows an attacker to overwrite certain files. As a result, an attacker could perform an action within a container that could impact the host system.

🗒 Full Vulristics report

About Remote Code Execution - Microsoft SharePoint (CVE-2026-58644) vulnerability

About Remote Code Execution - Microsoft SharePoint (CVE-2026-58644) vulnerability

About Remote Code Execution - Microsoft SharePoint (CVE-2026-58644) vulnerability. Information about this vulnerability was published on July 14 as part of the July Microsoft Patch Tuesday. The vulnerability in Microsoft SharePoint Server, caused by a deserialization flaw (CWE-502), allows an attacker with Site Owner privileges or higher to inject and remotely execute arbitrary code on the SharePoint server. This can result in full server compromise, including the exfiltration of corporate documents and data, their modification or deletion, compromise of credentials accessible to the server, and further lateral movement into the organization's internal infrastructure.

The authentication requirement, of course, makes exploitation of the vulnerability more difficult. However, an attacker could potentially leverage the previously disclosed EoP vulnerability CVE-2026-56164. At the same time, there is currently no confirmation that these vulnerabilities have been exploited together as part of a single attack chain.

👾 Microsoft experts flagged this vulnerability as being exploited in the wild on the day of Patch Tuesday. Two days later, on July 16, the vulnerability was added to the CISA KEV catalog. Details of the attacks are not yet known.

🛠 No public exploits have been observed so far.

⚙️ Updates are available for Microsoft SharePoint Server 2016, 2019, and Subscription Edition.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability. The vulnerability was disclosed in the July Microsoft Patch Tuesday release on July 14. The vulnerability, related to missing authentication for a critical function (CWE-306), allows an unauthenticated attacker to remotely elevate their privileges.

It is quite interesting that the CVSS scores for the vulnerability differ significantly between Microsoft's website and the NVD.

🔹 Microsoft: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N (5.3 MEDIUM)

🔹 NVD: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H (9.8 CRITICAL)

As can be seen, the difference is that Microsof's experts consider the impact of successful exploitation on integrity to be low, while the NVD rates the impact on confidentiality, integrity, and availability as high. This once again highlights the subjective nature of CVSS as a vulnerability prioritization tool. 😉

👾 Microsoft experts flagged this vulnerability as being exploited in the wild on the day of Patch Tuesday. The vulnerability was also added to the CISA KEV catalog on the same day. Microsoft credited Mandiant Incident Response for reporting this vulnerability, which suggests that Mandiant may have been involved in identifying the exploitation activity. There are currently no publicly available details regarding the attacks. However, according to Bleeping Computer, this vulnerability may have been exploited in an attack against the Swiss Federal Office of Information Technology, Systems and Telecommunication (BIT) reported on July 28. During the incident, credentials for around 200 user and technical accounts were compromised on Internet-facing SharePoint servers. The investigation did not reveal any other data breaches. According to BIT, SharePoint vulnerabilities from the July Microsoft Patch Tuesday were exploited on the servers, although the specific CVEs were not disclosed.

🛠 An exploit for the vulnerability has been available on GitHub since August 6. According to the exploit author's description, the vulnerability allows a remote unauthenticated attacker to elevate privileges to the level of Farm Administrator. By abusing request processing and routing mechanisms, an attacker can force a vulnerable server to fall back to an elevated security context instead of rejecting an unauthenticated request. This enables the attacker to access information about site collections, users, and server configuration, add administrators, and execute commands.

⚙️ Updates are available for Microsoft SharePoint Server 2016, 2019, and Subscription Edition. In addition to installing the updates, Microsoft experts recommend enabling the AMSI antimalware scanning interface on the server and setting the Request Body Scan mode to Full to reduce the risk of exploitation.

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability. Information about this vulnerability was disclosed as part of the June Microsoft Patch Tuesday on June 9. The vulnerability was not specifically highlighted in Microsoft Patch Tuesday reviews published by VM vendors. This Microsoft Windows NT OS Kernel elevation of privilege vulnerability is caused by improper handling of integer values during data construction in the Windows Management Instrumentation (WMI) subsystem, resulting in an out-of-bounds write. Successful exploitation allows a local attacker with low privileges (a standard user account) to escalate privileges to NT AUTHORITY\SYSTEM. Obtaining NT AUTHORITY\SYSTEM privileges grants full control over the affected host, enabling an attacker to execute arbitrary commands, modify security settings, access protected data, and use the compromised host as a foothold for further lateral movement within the target environment.

🛠 On July 7, a detailed write-up describing the exploitation of this vulnerability was published. A public proof-of-concept (PoC) exploit is also available on GitHub.

👾 There is currently no evidence of in-the-wild exploitation of this vulnerability.