Tag Archives: Microsoft

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability. The vulnerability was disclosed in the July Microsoft Patch Tuesday release on July 14. The vulnerability, related to missing authentication for a critical function (CWE-306), allows an unauthenticated attacker to remotely elevate their privileges.

It is quite interesting that the CVSS scores for the vulnerability differ significantly between Microsoft's website and the NVD.

🔹 Microsoft: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N (5.3 MEDIUM)

🔹 NVD: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H (9.8 CRITICAL)

As can be seen, the difference is that Microsof's experts consider the impact of successful exploitation on integrity to be low, while the NVD rates the impact on confidentiality, integrity, and availability as high. This once again highlights the subjective nature of CVSS as a vulnerability prioritization tool. 😉

👾 Microsoft experts flagged this vulnerability as being exploited in the wild on the day of Patch Tuesday. The vulnerability was also added to the CISA KEV catalog on the same day. Microsoft credited Mandiant Incident Response for reporting this vulnerability, which suggests that Mandiant may have been involved in identifying the exploitation activity. There are currently no publicly available details regarding the attacks. However, according to Bleeping Computer, this vulnerability may have been exploited in an attack against the Swiss Federal Office of Information Technology, Systems and Telecommunication (BIT) reported on July 28. During the incident, credentials for around 200 user and technical accounts were compromised on Internet-facing SharePoint servers. The investigation did not reveal any other data breaches. According to BIT, SharePoint vulnerabilities from the July Microsoft Patch Tuesday were exploited on the servers, although the specific CVEs were not disclosed.

🛠 An exploit for the vulnerability has been available on GitHub since August 6. According to the exploit author's description, the vulnerability allows a remote unauthenticated attacker to elevate privileges to the level of Farm Administrator. By abusing request processing and routing mechanisms, an attacker can force a vulnerable server to fall back to an elevated security context instead of rejecting an unauthenticated request. This enables the attacker to access information about site collections, users, and server configuration, add administrators, and execute commands.

⚙️ Updates are available for Microsoft SharePoint Server 2016, 2019, and Subscription Edition. In addition to installing the updates, Microsoft experts recommend enabling the AMSI antimalware scanning interface on the server and setting the Request Body Scan mode to Full to reduce the risk of exploitation.

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability. Information about this vulnerability was disclosed as part of the June Microsoft Patch Tuesday on June 9. The vulnerability was not specifically highlighted in Microsoft Patch Tuesday reviews published by VM vendors. This Microsoft Windows NT OS Kernel elevation of privilege vulnerability is caused by improper handling of integer values during data construction in the Windows Management Instrumentation (WMI) subsystem, resulting in an out-of-bounds write. Successful exploitation allows a local attacker with low privileges (a standard user account) to escalate privileges to NT AUTHORITY\SYSTEM. Obtaining NT AUTHORITY\SYSTEM privileges grants full control over the affected host, enabling an attacker to execute arbitrary commands, modify security settings, access protected data, and use the compromised host as a foothold for further lateral movement within the target environment.

🛠 On July 7, a detailed write-up describing the exploitation of this vulnerability was published. A public proof-of-concept (PoC) exploit is also available on GitHub.

👾 There is currently no evidence of in-the-wild exploitation of this vulnerability.

July Microsoft Patch Tuesday

July Microsoft Patch Tuesday

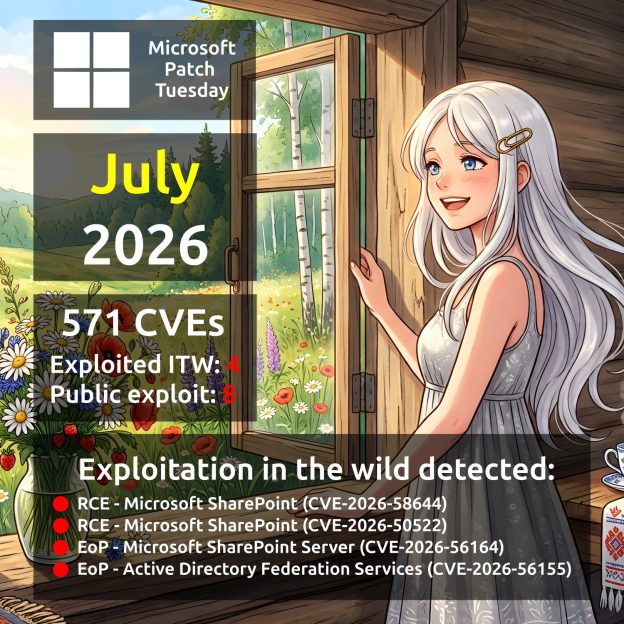
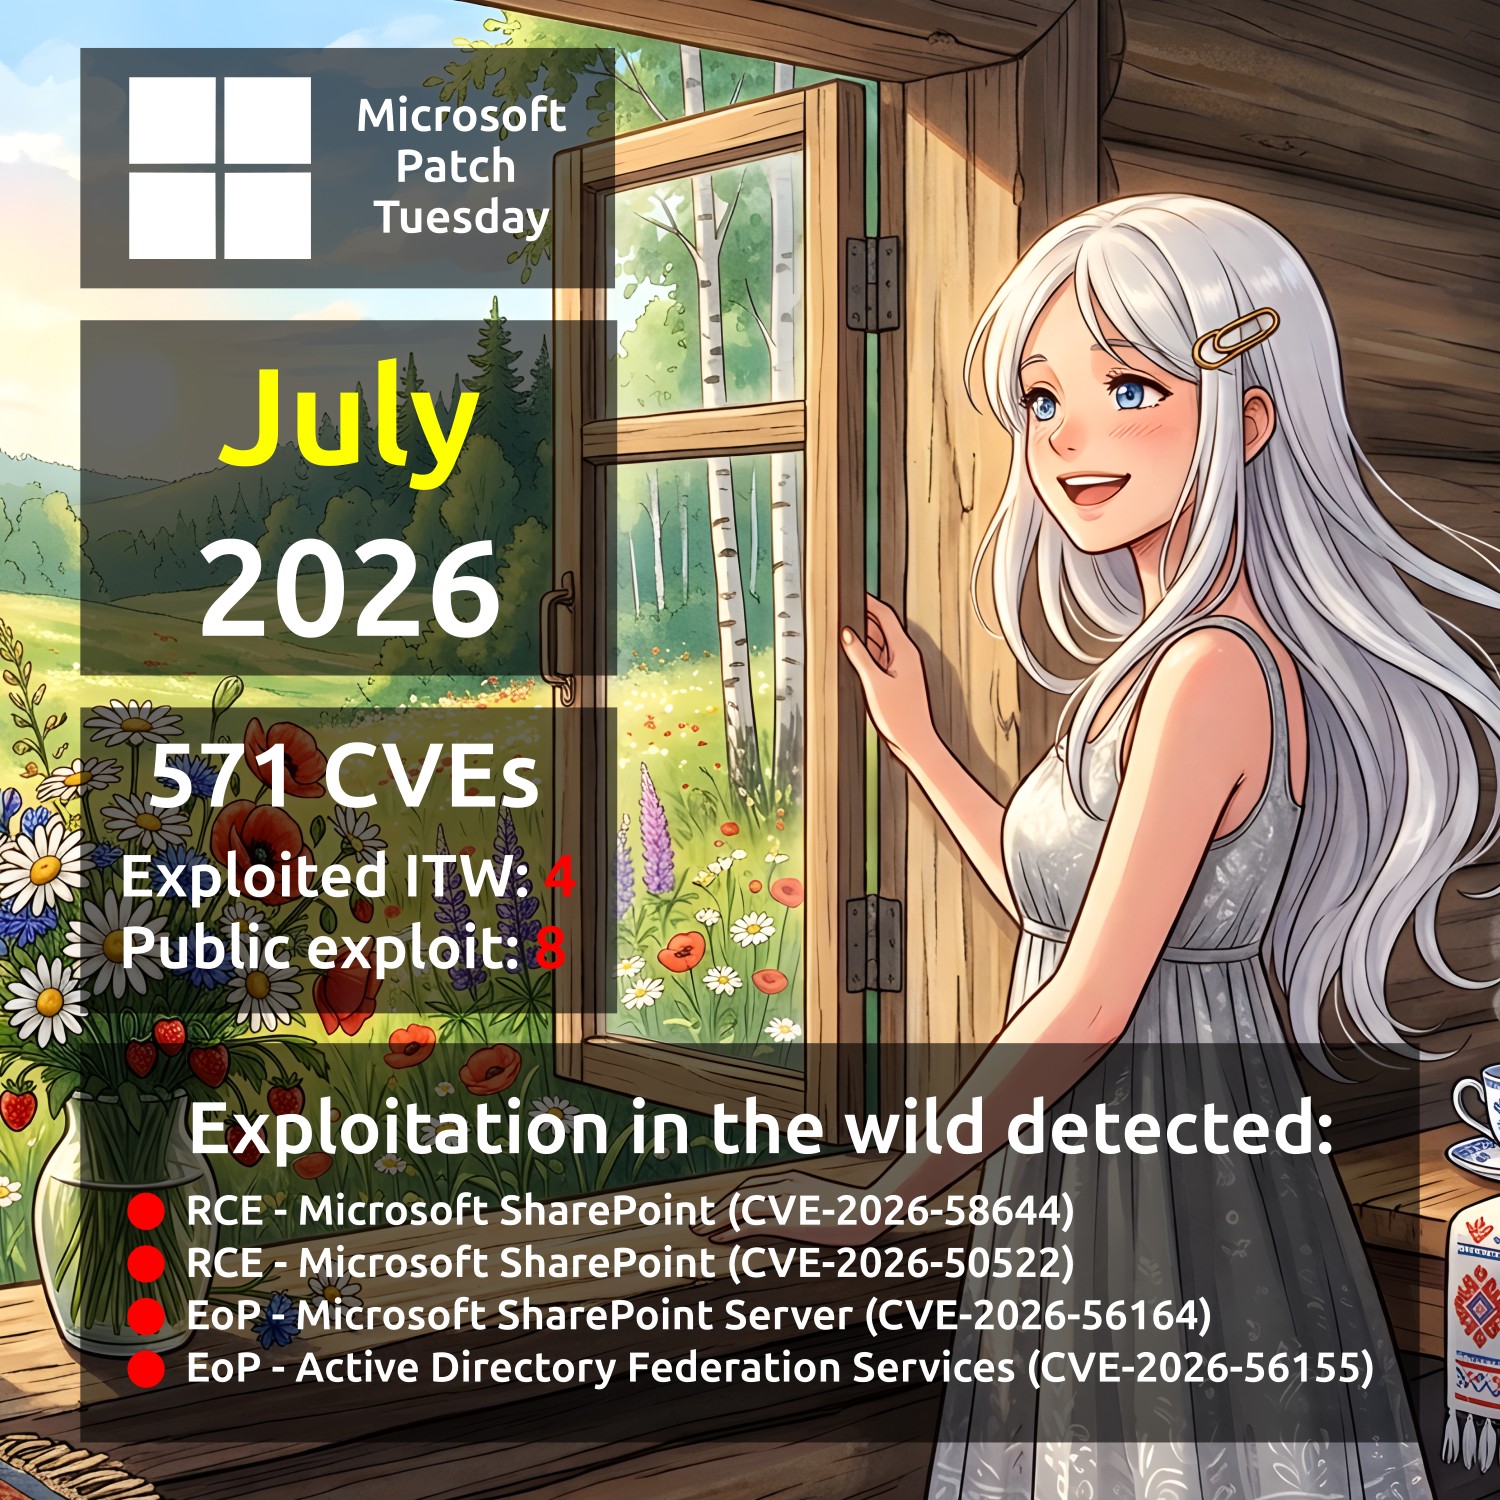
July Microsoft Patch Tuesday. In the second week of July, I was on vacation in St. Petersburg. After that, I got caught up with a bunch of other tasks, so I'm only publishing this roundup now. Better late than never, especially considering how unusual this MSPT turned out to be. 😉 In total, 571 vulnerabilities were addressed - almost three times (❗️) more than in June. There are four vulnerabilities that have been reported as exploited in the wild:

🔻 RCE - Microsoft SharePoint (CVE-2026-58644). An attacker with Site Owner privileges or higher can remotely inject and execute arbitrary code on the SharePoint Server.

🔻 RCE - Microsoft SharePoint (CVE-2026-50522). The vulnerability description is identical to CVE-2026-58644. According to ZDI, the CVE-2026-50522 vulnerability was successfully demonstrated at Pwn2Own Berlin. Despite this, Microsoft rates its Exploit Maturity as "Unknown", even though researchers have already provided a working exploit to the company. This once again shows that organizations should not rely solely on software vendors' assessments and should instead perform their own risk evaluation. If you have Internet-facing SharePoint servers, you should test and deploy the patch addressing this vulnerability as soon as possible.

🔻 EoP - Microsoft SharePoint Server (CVE-2026-56164). Missing authentication for a critical function in Microsoft Office SharePoint could allow an unauthenticated attacker to elevate privileges over a network. Microsoft mentioned in the advisory that enabling the Antimalware Scan Interface (AMSI) on the server and setting the Request Body Scan mode to Full can help mitigate this flaw.

🔻 EoP - Active Directory Federation Services (CVE-2026-56155). Insufficient granularity of access control (CWE-1220) in Active Directory Federation Services (AD FS) allows an authorized attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain administrator privileges.

There are eight more vulnerabilities with publicly available exploits:

🔸 EoP - Windows User Interface Core (CVE-2026-50454). Relative path traversal (CWE-23) allows an authorized attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. The PoC starts from a normal, non-elevated process belonging to a local administrator and opens an interactive command prompt as NT AUTHORITY\SYSTEM.

🔸 EoP - Windows WalletService (CVE-2026-49176). Improper privilege management (CWE-269) allows an authorized attacker to elevate privileges locally. The exploit PoC starts a command prompt as SYSTEM in the active desktop session.

🔸 RCE - Microsoft Message Queuing Queue Manager (CVE-2026-54992). The existing exploit PoC demonstrates denial of service; it does not demonstrate code execution.

🔸 EoP - Windows Narrator Braille (CVE-2026-58635). According to Microsoft's description, an attacker who successfully exploited this vulnerability could execute code in the security context of the NT AUTHORITY\Network Service account. However, the description of the exploit PoC states that an unprivileged attacker would gain NT AUTHORITY\SYSTEM privileges.

🔸 EoP - Windows Cloud Files Mini Filter Driver (CVE-2026-58613). Use after free (CWE-416) in the Windows Cloud Files Mini Filter Driver allows an authorized attacker to elevate privileges locally. An attacker who successfully exploits this vulnerability can gain SYSTEM privileges. Exploitation details are available in the Talos Vulnerability Report TALOS-2026-2426.

🔸 InfDisc - Windows Win32k (CVE-2026-50416). An attacker who successfully exploited this vulnerability could potentially read small portions of heap memory. The exploit PoC description mentions Chrome tabs, Discord, Explorer, Spotify, and tray windows. However, it seems that it will not be possible to intercept passwords using this vulnerability.

🔸 InfDisc - Windows Kernel (CVE-2026-50475). A buffer over-read (CWE-126) in the Windows Kernel allows an authorized attacker to disclose information locally. Exploitation details are available in the Talos Vulnerability Report TALOS-2026-2443.

🔸 EoP - Azure Spring Apps (CVE-2026-50338). An attacker who successfully exploited this vulnerability could gain elevated privileges, potentially allowing them to perform actions beyond their original permissions. According to the author of the exploit PoC, the vulnerability is a Spring Cloud Azure B2C resource server cross-issuer authentication bypass.

Among the remaining vulnerabilities, the following can be highlighted:

🔹 RCE - Windows Remote Desktop Protocol (CVE-2026-56190). An unauthenticated, network-reachable, no user interaction required vulnerability. The root cause is a classic one: the use of an uninitialized resource (CWE-908), meaning specially crafted RDP traffic can interact with memory that was never properly initialized, letting an attacker corrupt memory and potentially steer code execution. RDP Servers are a common target, so audit your systems to see which are internet accessible and start from there.

🔹 RCE - Microsoft Dynamics NAV and Microsoft Dynamics 365 Business Central (On Premises) (CVE-2026-55944). Successful exploitation can be achieved by sending a crafted login request to an affected Dynamics NAV or Business Central server in order to trigger a deserialization of untrusted data vulnerability. Microsoft's advisory cautions that no user-interaction is required, nor is authentication a requirement in order to successfully exploit this vulnerability.

🔹 EoP - Microsoft Windows VMSwitch (CVE-2026-57092). It's a use-after-free that lets a low-privileged attacker escalate to full host compromise across a VM boundary. ZDI reported that a similar exploit was demonstrated on ESXi at Pwn2Own Berlin, but this issue is not limited to ESXi. If you use VMSwitch in Hyper-V deployments (which is likely), test and deploy the fix quickly.

🔹 Spoofing - Microsoft Exchange (CVE-2026-55008). An attacker can send a specially crafted email that runs arbitrary JavaScript when the victim opens it in OWA. No attachment or macro is required - simply viewing the email is enough. If your organization uses OWA, it is recommended to test and deploy the fix as soon as possible.

🔹 RCE - Windows DHCP Server (CVE-2026-50518, CVE-2026-56159, CVE-2026-48564, CVE-2026-50370), Windows DHCP Client (CVE-2026-54128), Windows Message Queuing Service (MSMQ) (CVE-2026-50447), Windows Admin Center (WAC) (CVE-2026-56196), Windows FTP Service (CVE-2026-49172), Windows GDI+ (CVE-2026-50380), Windows Server Network driver (CVE-2026-56188), Microsoft Exchange (CVE-2026-55005), Windows Active Directory Domain Services (CVE-2026-49178), Windows Remote Desktop Client (CVE-2026-50474), Windows Remote Desktop Client (CVE-2026-54990, CVE-2026-58594), Windows TCP/IP (CVE-2026-54999), Windows Print Spooler (CVE-2026-58608), Windows Reliable Multicast Transport Driver (RMCAST) (CVE-2026-54982, CVE-2026-54995), Microsoft SQL Server (CVE-2026-54117), Microsoft Copilot (CVE-2026-48561).

🔹 SFB - Microsoft SharePoint Server (CVE-2026-55040).

🔹 EoP - Windows Server Update Service (WSUS) (CVE-2026-50444), Active Directory Certificate Services (CVE-2026-54121).

There is also a rather curious vulnerability:

RCE - Game: Age of Empires II: Definitive Edition (CVE-2026-50663). 😃 A relative path traversal in Age of Empires II: Definitive Edition Game allows an unauthorized attacker to execute code over a network. Age of Empires II is a cult classic real-time strategy game by Microsoft, set in the medieval era. Players develop chosen civilizations, manage resources, research technologies, and command armies in historical campaigns and multiplayer battles. The Definitive Edition features improved graphics, updated audio, and additional content. If you're still playing this game, be sure to update. 😉

🗒 Full Vulristics Report
July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability

July In the Trend of VM (#29): Microsoft Exchange Server vulnerability

July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability. Here is my traditional monthly roundup of trending vulnerabilities, according to Positive Technologies. The previous June edition featured four vulnerabilities. This time, there's only one.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 XSS - Microsoft Exchange (CVE-2026-42897). The vulnerability allows attackers to execute arbitrary JavaScript in a user's browser when the user opens a malicious email in Outlook Web Access (OWA). A public proof-of-concept exploit is available, and the vulnerability has already been exploited in the wild.

🟥 The full list of trending vulnerabilities is available on the portal

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability. The vulnerability was fixed on May 14 outside the regular Microsoft Patch Tuesday cycle. Improper neutralization of input during web page generation (CWE-79, XSS) in Microsoft Exchange Server allows an unauthorized attacker to perform spoofing over a network. In practical terms, this means that a remote attacker could exploit this vulnerability by sending a specially crafted email to a user. If the user opens the email in Outlook Web Access and certain interaction conditions are met, arbitrary JavaScript can be executed in the browser context. As a result, the attacker may gain control of the user's mailbox by using an active user session.

👾 Microsoft experts immediately reported signs of active exploitation in the wild for this vulnerability. The vulnerability was added to the CISA KEV on May 15.

⚒️ A public exploit for the vulnerability was published on GitHub on May 15 as well.

⚙️ Initially, mitigation measures were recommended to address the vulnerability, delivered via the Exchange Emergency Mitigation (EM) service or by using the Exchange on-premises Mitigation Tool (EOMT) script. Security updates that fix the vulnerability in Microsoft Exchange Server Subscription Edition RTM, Exchange Server 2016, and Exchange Server 2019 were released almost a month later, on June 9. Microsoft experts recommended keeping the mitigations enabled even after applying the patch, as they provide an additional layer of protection. However, applying these mitigations may cause issues (for example, errors when printing calendars and displaying images in OWA).

⚠️ Please note that Exchange Server 2016 and 2019, which are out of support, are also affected by this vulnerability. Only customers enrolled in the Period 2 Extended Security Update (ESU) program are eligible to receive Exchange Server 2016 and 2019 security updates released between May and October 2026.

June "In the Trend of VM" (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities

June In the Trend of VM (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities

June "In the Trend of VM" (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous May edition, we covered four vulnerabilities. This time, there are also four vulnerabilities associated with five CVE identifiers.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Dirty Frag" (CVE-2026-43284, CVE-2026-43500). A chain of vulnerabilities with a public exploit to obtain root access. There are signs of in-the-wild exploitation.

🔻 EoP - Linux Kernel "Fragnesia" (CVE-2026-46300). Another vulnerability for gaining root access with a public exploit.

🔻 EoP - Microsoft Defender "RedSun" (CVE-2026-41091). A privilege escalation vulnerability leading to SYSTEM-level access, with a public exploit available and indications of in-the-wild exploitation. Pay special attention to Windows server and desktop environments where Microsoft Defender is enabled but there is no Internet access for regular updates.

🔻 RCE - PAN-OS (CVE-2026-0300). An unauthenticated RCE with root privileges affecting PA-Series and VM-Series firewalls. A public exploit exists, and there are indications of in-the-wild exploitation.

🟥 The full list of trending vulnerabilities is available on the portal

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday. Last week I was on vacation in Veliky Novgorod, so I'm publishing this overview only now. A total of 202 vulnerabilities were addressed, approximately twice as many as in May. There are currently no vulnerabilities marked as exploited in the wild. However, there are two vulnerabilities with publicly available exploits:

🔸 RCE - HTTP.sys (CVE-2026-47291). This critical vulnerability allows remote, unauthenticated attackers to execute arbitrary code on affected systems without user interaction. However, systems using the default MaxRequestBytes registry value in the Windows HTTP stack are not affected. If needed, you can change this registry setting to protect systems while testing and deploying the patch. Microsoft's security bulletin includes instructions and a PowerShell script for this workaround.

🔸 DoS - HTTP.sys (CVE-2026-49160). The same exploit is used as for the previous RCE vulnerability.

It is also worth paying attention to vulnerabilities that Microsoft has flagged as having a publicly available exploit:

🔹 SFB - Windows BitLocker (CVE-2026-50507). A successful attacker could bypass the BitLocker Device Encryption feature on the system storage device. An attacker with physical access to the target could exploit this vulnerability to gain access to encrypted data. According to Tenable, this is the "Bitskrieg" vulnerability discovered by the researcher known as Chaotic Eclipse/Nightmare Eclipse.

🔹 SFB - Secure Boot (CVE-2026-48570). An attacker who successfully exploited this vulnerability could bypass Secure Boot. This vulnerability was reported by Alon Leviev (STORM), who is known for previous research related to BootKitty and BlackLotus.

Among the remaining vulnerabilities, the following are worth highlighting:

🔹 RCE - Windows Kernel (CVE-2026-45657). This vulnerability allows remote, unauthenticated attackers to run code with SYSTEM privileges without any user interaction. In other words, it could be used to spread automatically between systems. The issue is caused by how the Windows kernel processes TCP/IP traffic. Microsoft rated this as "Exploitation Less Likely", but security researchers and exploit developers are already analyzing the patch and trying to build an exploit. Test and deploy this patch as soon as possible.

🔹 EoP - Windows Collaborative Translation Framework (CTFMON) (CVE-2026-45586). This vulnerability affects a component used for voice and handwriting recognition. If exploited, an attacker could gain SYSTEM privileges. Microsoft rates this vulnerability as "Exploitation More Likely".

🔹 RCE - Windows Remote Desktop Client (CVE-2026-42909, CVE-2026-42913, CVE-2026-42985, CVE-2026-42992, CVE-2026-42993, CVE-2026-44799, CVE-2026-44801, CVE-2026-47289, CVE-2026-47653, CVE-2026-47654, CVE-2026-48563). Successful exploitation would require a victim to connect to an attacker-controlled server using an affected version of the Remote Desktop Client. This action could trigger a heap-based buffer overflow, resulting in remote code execution.

🔹 RCE - DHCP Client Service (CVE-2026-44815). This vulnerability allows remote, unauthenticated attackers to execute code on affected systems without user interaction. Because the DHCP client is widely enabled across Windows systems, this vulnerability presents a broad attack surface. Organizations should prioritize testing and deploying the patch for this vulnerability as soon as possible.

🗒 Full Vulristics report