Tag Archives: NGFW

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

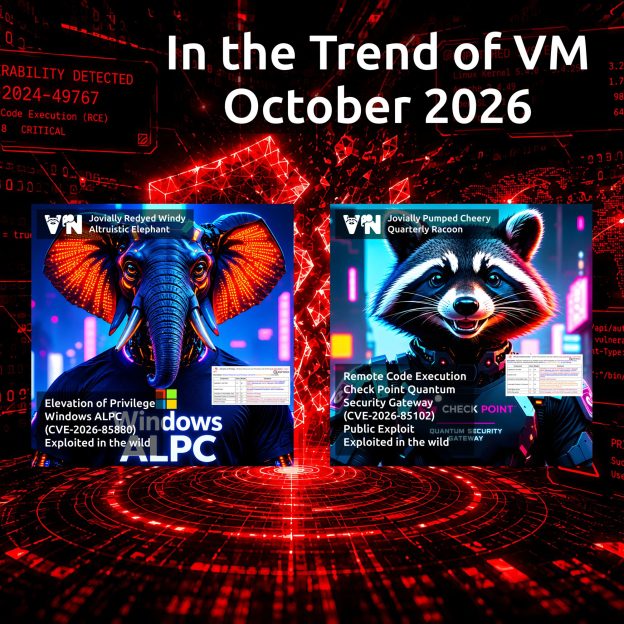
🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

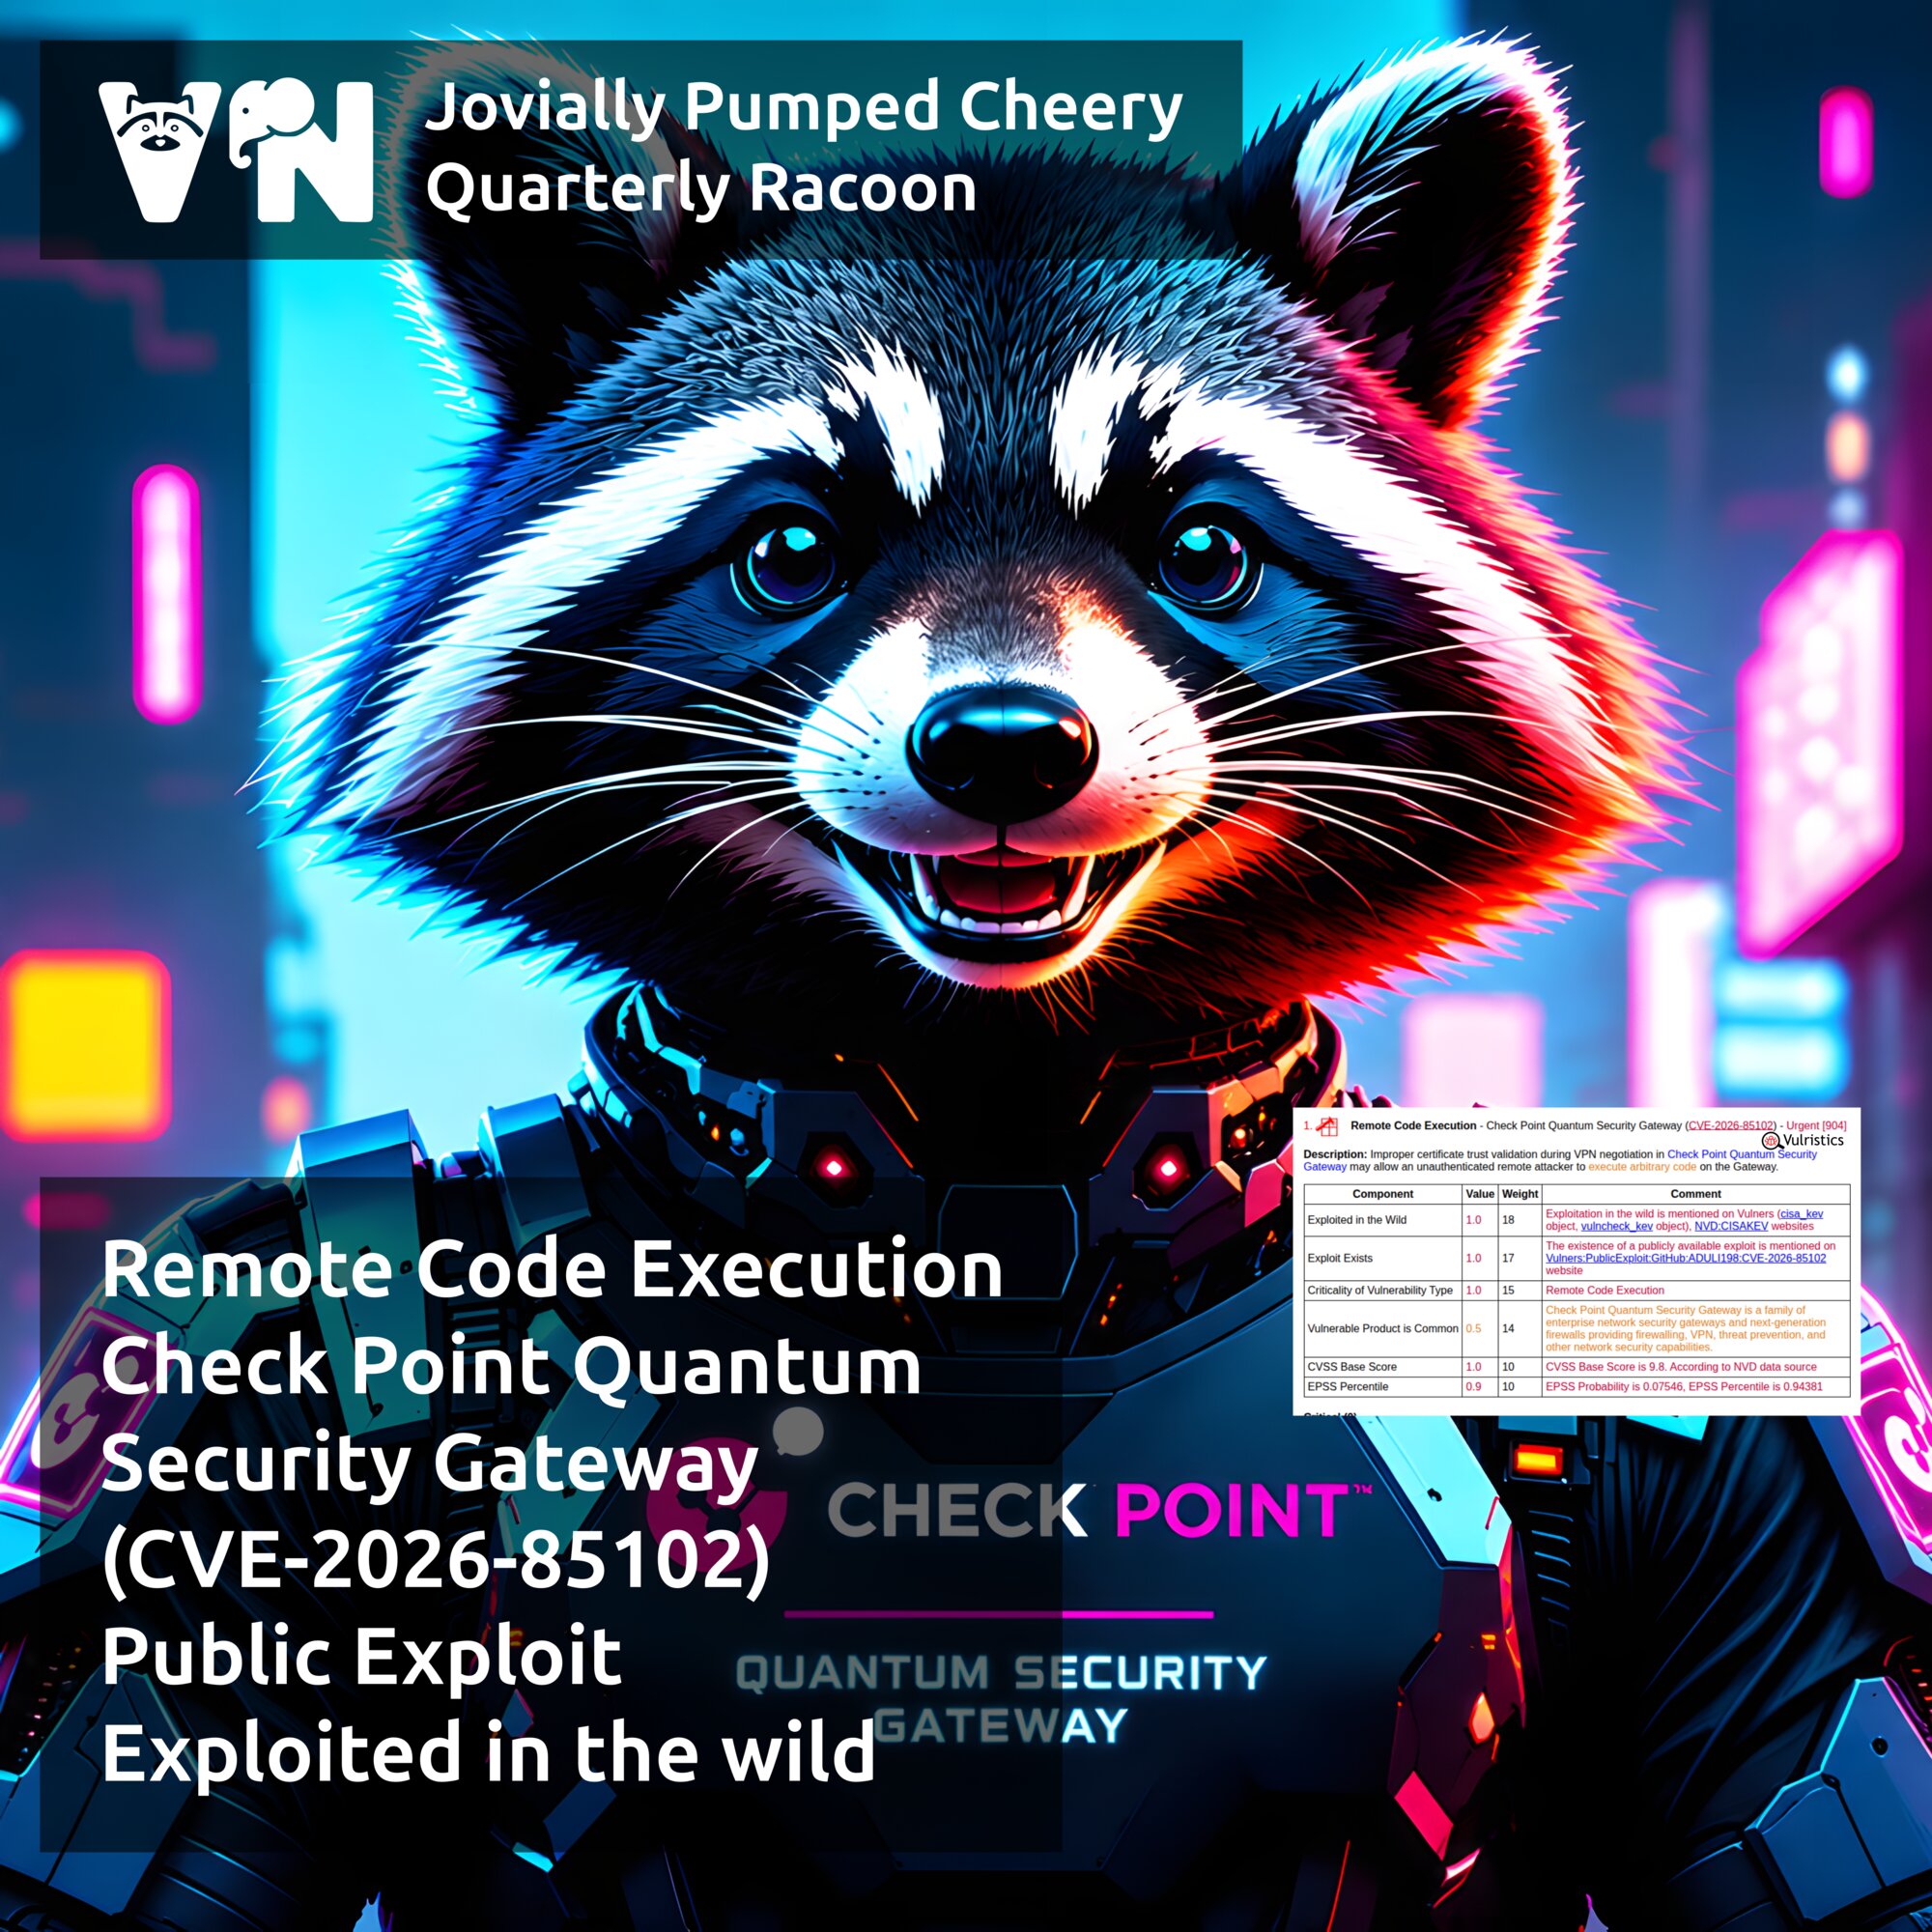
🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability. Check Point Quantum Security Gateway is an enterprise security gateway and next-generation firewall (NGFW) designed to protect network infrastructure from cyberattacks and unauthorized access. It provides network traffic filtering, intrusion prevention (IPS), application control, and secure VPN connectivity. Improper validation of trust in an X.509 certificate during VPN negotiation on Check Point Quantum Security Gateway may allow an unauthenticated remote attacker to execute arbitrary code on the gateway with the privileges of a system process.

An attacker may use the compromised gateway to perform internal network reconnaissance (including port and service scanning), intercept VPN traffic, steal credentials and configuration files, including certificates, IPsec/VPN keys, and administrator credentials, and compromise VPN tunnels connecting the organization's network to branch offices and partner networks.

The vulnerability also affects Spark Firewall devices, a family of firewalls developed by Check Point primarily to protect the networks of small and medium-sized businesses, branch offices, and remote locations.

⚙️ Security updates and mitigation measures have been available on the vendor's website since September 9.

👾 Check Point experts began observing exploitation attempts on September 12. On September 22, the vulnerability was added to the CISA KEV catalog.

🛠 A public exploit has been available on GitHub since October 7.

🌐 As of October 12, Shodan had identified 11,849 potentially vulnerable Check Point gateways exposed to the Internet, 143 of them in Russia.

June "In the Trend of VM" (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities

June In the Trend of VM (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities

June "In the Trend of VM" (#28): Linux kernel, Microsoft Defender, and Palo Alto Networks device vulnerabilities. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous May edition, we covered four vulnerabilities. This time, there are also four vulnerabilities associated with five CVE identifiers.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Dirty Frag" (CVE-2026-43284, CVE-2026-43500). A chain of vulnerabilities with a public exploit to obtain root access. There are signs of in-the-wild exploitation.

🔻 EoP - Linux Kernel "Fragnesia" (CVE-2026-46300). Another vulnerability for gaining root access with a public exploit.

🔻 EoP - Microsoft Defender "RedSun" (CVE-2026-41091). A privilege escalation vulnerability leading to SYSTEM-level access, with a public exploit available and indications of in-the-wild exploitation. Pay special attention to Windows server and desktop environments where Microsoft Defender is enabled but there is no Internet access for regular updates.

🔻 RCE - PAN-OS (CVE-2026-0300). An unauthenticated RCE with root privileges affecting PA-Series and VM-Series firewalls. A public exploit exists, and there are indications of in-the-wild exploitation.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - PAN-OS (CVE-2026-0300) vulnerability

About Remote Code Execution - PAN-OS (CVE-2026-0300) vulnerability

About Remote Code Execution - PAN-OS (CVE-2026-0300) vulnerability. PAN-OS is an operating system for Palo Alto Networks firewalls and security platforms. User-ID™ Authentication Portal (also known as Captive Portal) is a non-default PAN-OS feature used to map IP addresses to usernames. By exploiting a buffer overflow vulnerability (CWE-787), an unauthenticated remote attacker can send specially crafted packets to a device with the Authentication Portal enabled, achieving arbitrary code execution with root privileges on the affected device. No authentication or user interaction is required. If the vulnerability is successfully exploited, the attacker gains full control over network traffic: they can intercept, modify, or block connections, access sensitive data, bypass security policies, hide traces of compromise, install backdoors, and use the device as a foothold for attacks on internal infrastructure.

⚙️ The vendor security advisory was published on May 6. PA-Series and VM-Series firewalls are affected. Prisma Access, Cloud NGFW, and Panorama appliances are not impacted by this vulnerability. Security updates for affected devices became available on May 13. As a workaround, the vendor recommended restricting User-ID™ Authentication Portal access to only trusted internal zones or disabling the User-ID™ Authentication Portal entirely if it is not required.

👾 On the same day, May 6, researchers from Palo Alto Networks Unit 42 published a report on active exploitation of the vulnerability in the wild. Post-exploitation activity includes deployment of publicly available tunneling tools (EarthWorm, ReverseSocks5), Active Directory enumeration using credentials likely obtained from the firewall, and systematic destruction of logs and other evidence of compromise. On the same day, the vulnerability was added to the CISA KEV catalog.

🛠 A public exploit was also published on GitHub on May 6.

🌐 PAN-OS is among the most widely deployed enterprise firewall operating systems in the world. As of June 5, Shodan identifies approximately 135,755 internet-facing PAN-OS instances, representing a significant attack surface.
About Denial of Service - PAN-OS (CVE-2024-3393) vulnerability

About Denial of Service - PAN-OS (CVE-2024-3393) vulnerability

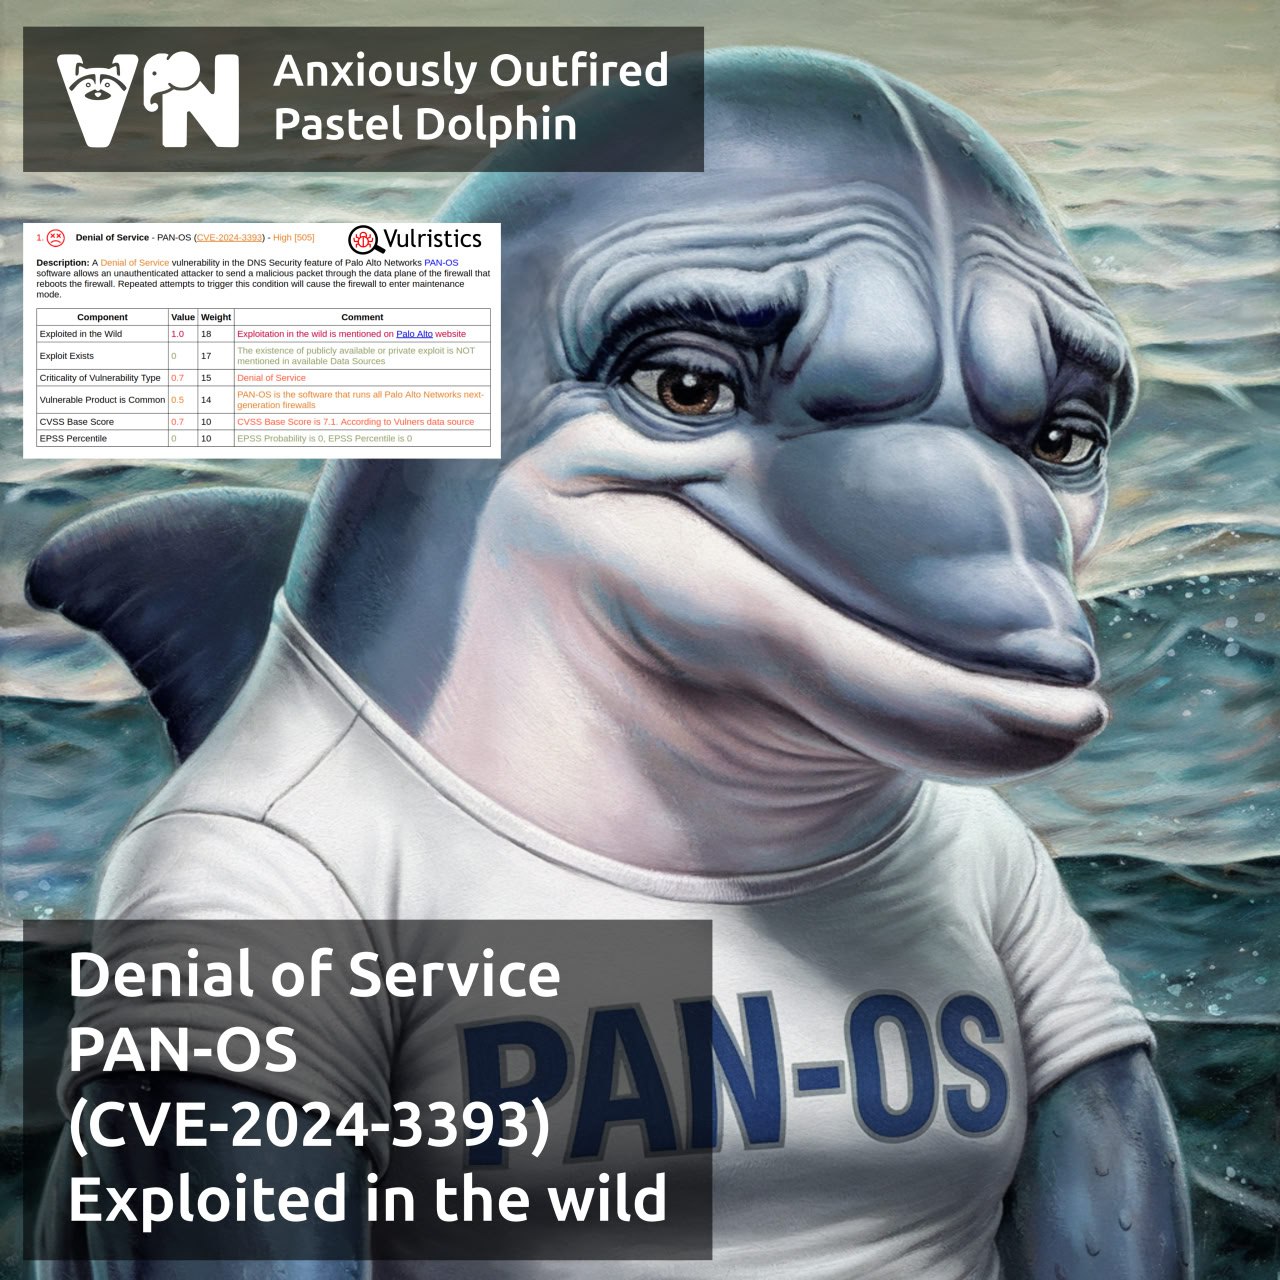
About Denial of Service - PAN-OS (CVE-2024-3393) vulnerability. PAN-OS is the operating system that runs all Palo Alto Network NGFWs. The vendor's advisory was released on December 27. Аn unauthenticated attacker can send a malicious packet through the data plane of the firewall, causing it to reboot. Repeated attempts to trigger this condition will cause the firewall to enter maintenance mode. For exploitation the logging option of the "DNS Security" feature must be enabled.

👾 Palo Alto has already detected attacks that exploit this vulnerability. There are no public exploits yet.

👀 CyberOK detects more than 500 PAN-OS installations in RuNet, of which 32 are potentially vulnerable. Additionally, 218 hosts are running PAN-OS version 11.0.x, which is no longer supported by the vendor since November 17.

🔧 To fix the vulnerability, you need to update your device or, as a workaround, disable the logging option of the "DNS Security" function.

На русском

What I expect from IT Asset Inventory

What I expect from IT Asset Inventory. The main problem of vulnerability management, in my opinion, is that it is not always clear whether we know about ALL network hosts existing in our infrastructure or not. So, not the actual process of scanning and the detection of vulnerabilities, but the lack of knowledge what we should scan.

Knowing the total number of active hosts, this must be such a simple and basic thing. But for a large organization, this is not so trivial. To tell the truth, I do not know how to do IT Asset Inventory right. I’m not even sure who should be responsible this. There are so many different technological and organizational nuances. I will mention some of them below.

Who is responsible for inventorying IT assets?

But I can say with confidence that my basic requirement for IT Asset Inventory system will be the completeness of the scope, not the number of collected parameters. The very minimum is just to see that some network host existed and seemed active at some time.

Continue reading →

Retrieving Palo Alto NGFW security events via API

Retrieving Palo Alto NGFW security events via API. It may seem like NGFW topic is not really related to vulnerability assessment and vulnerability management. In fact, correlation of security events in traffic with vulnerability scan data sometimes may give very interesting results. For example, if we have a Windows desktop host with critical vulnerabilities, it won’t be a big surprise to detect some botnet activity related to this host. Fixing of this hosts should be a high priority task. Moreover, Palo Alto NGFW now supports signatures for vulnerability detection, like Tenable PVS. It’s pretty logical: if you are already searching something in the network traffic, why not to look also for vulnerable software versions in the packet headers?

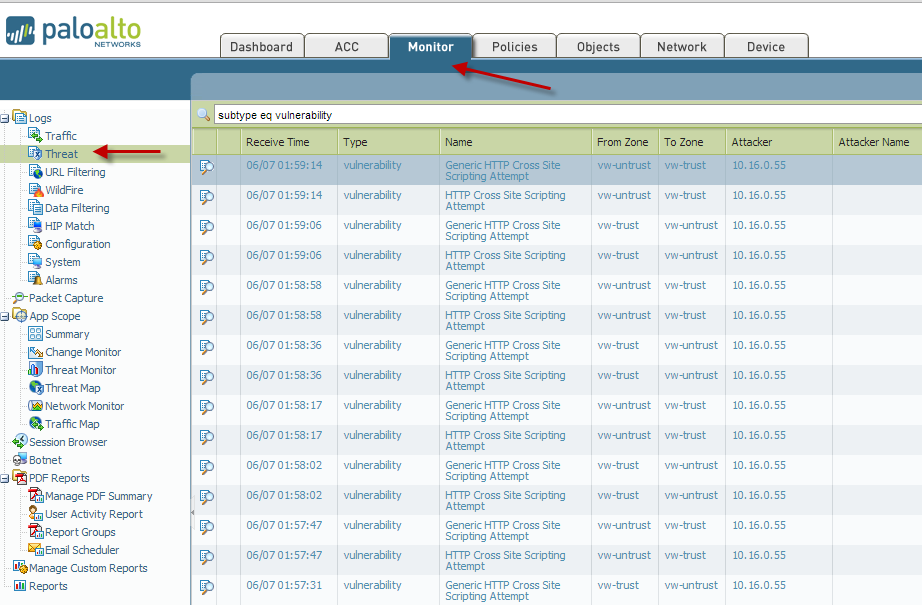
Palo Alto Monitor

I took this image from the official manual

At the “Monitoring” tab of Palo Alto NGFW GUI web-interface you can see a flow of security events, produced by Palo Alto security rules, standard or custom. With PA query language you may easily filter this events. It is also possible to produce reports. However, the standard reports Palo Alto are not very informative and only represent some statistics of attacks without any additional information. Much more interesting reports you can make using Palo Alto API.

Continue reading →