Tag Archives: KEV

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

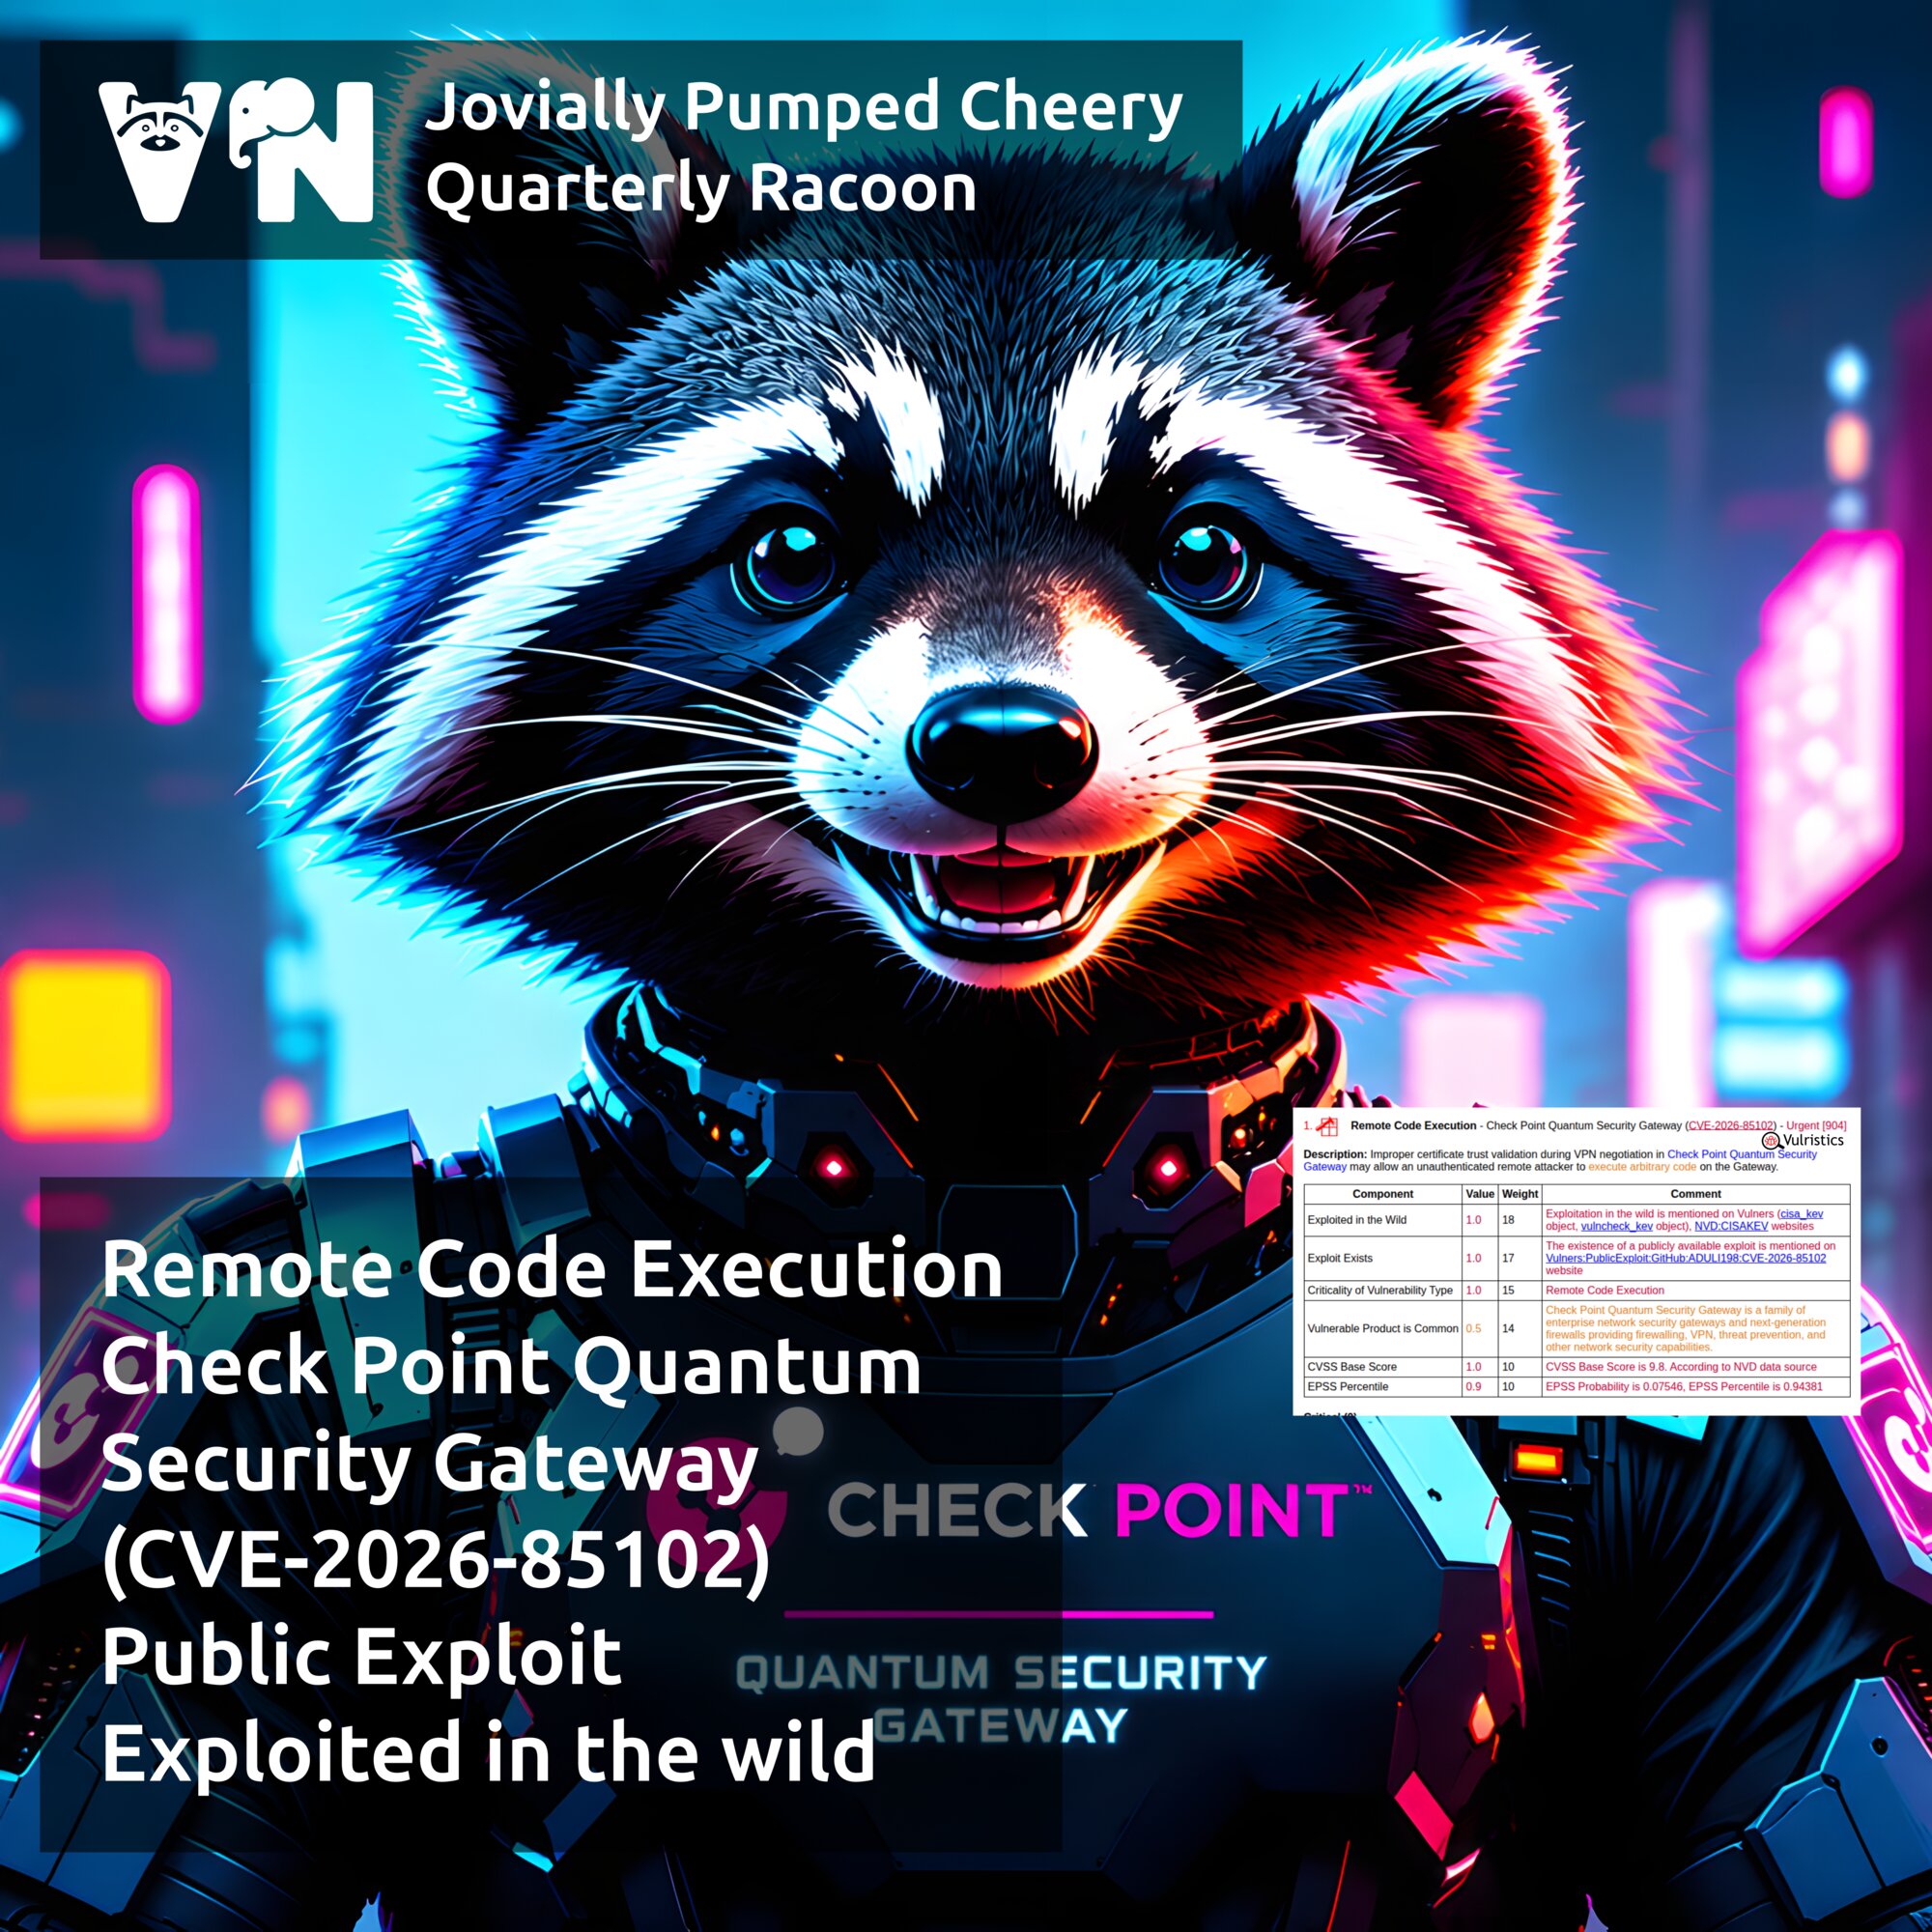
🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability. Check Point Quantum Security Gateway is an enterprise security gateway and next-generation firewall (NGFW) designed to protect network infrastructure from cyberattacks and unauthorized access. It provides network traffic filtering, intrusion prevention (IPS), application control, and secure VPN connectivity. Improper validation of trust in an X.509 certificate during VPN negotiation on Check Point Quantum Security Gateway may allow an unauthenticated remote attacker to execute arbitrary code on the gateway with the privileges of a system process.

An attacker may use the compromised gateway to perform internal network reconnaissance (including port and service scanning), intercept VPN traffic, steal credentials and configuration files, including certificates, IPsec/VPN keys, and administrator credentials, and compromise VPN tunnels connecting the organization's network to branch offices and partner networks.

The vulnerability also affects Spark Firewall devices, a family of firewalls developed by Check Point primarily to protect the networks of small and medium-sized businesses, branch offices, and remote locations.

⚙️ Security updates and mitigation measures have been available on the vendor's website since September 9.

👾 Check Point experts began observing exploitation attempts on September 12. On September 22, the vulnerability was added to the CISA KEV catalog.

🛠 A public exploit has been available on GitHub since October 7.

🌐 As of October 12, Shodan had identified 11,849 potentially vulnerable Check Point gateways exposed to the Internet, 143 of them in Russia.

August Linux Patch Wednesday

August Linux Patch Wednesday

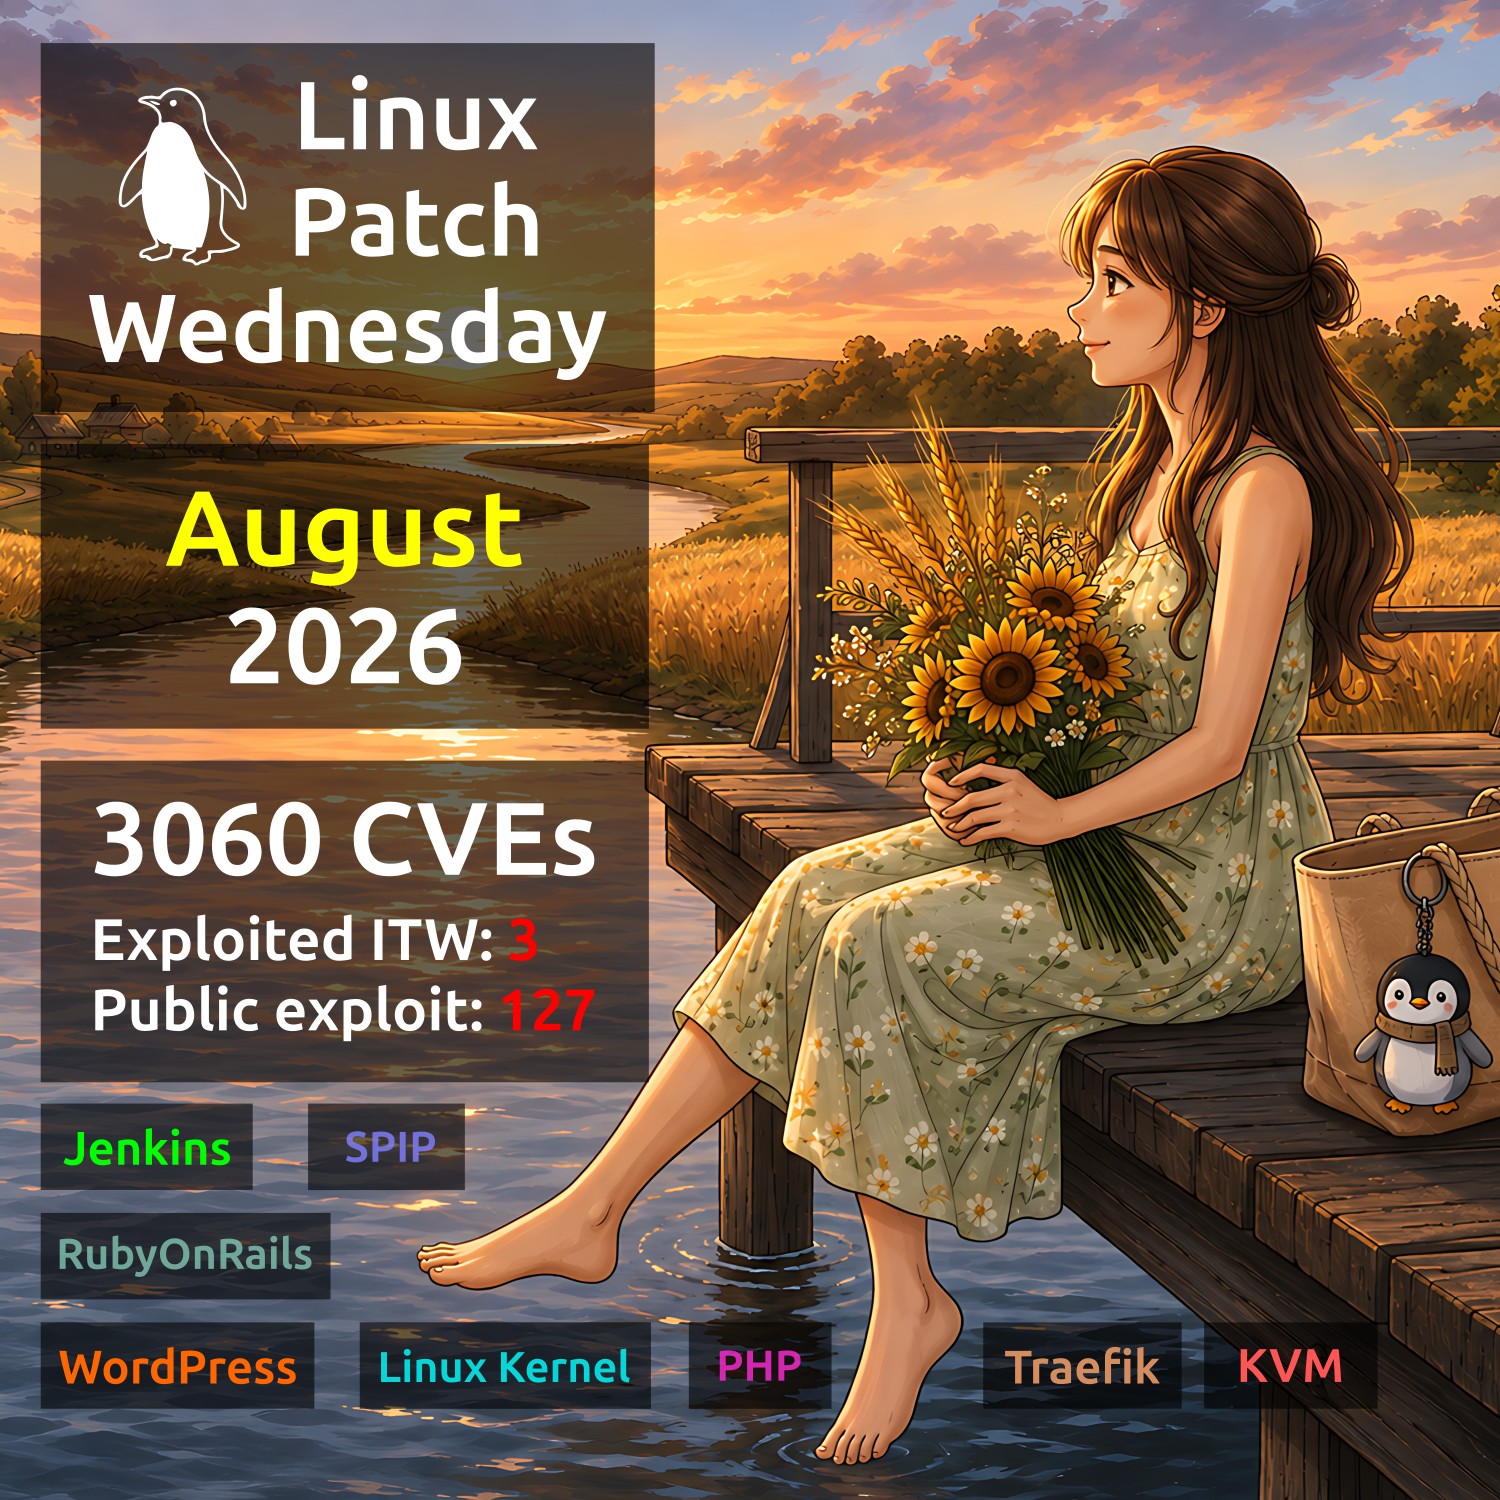
August Linux Patch Wednesday. A total of 3,060 vulnerabilities. For comparison, there were 2,017 in July. That's a 52% increase and another new record. This time, there are 1,354 vulnerabilities in the Linux Kernel and 447 in Chromium. For 3 vulnerabilities, there are signs of exploitation in the wild:

🔻 RCE - Jenkins (CVE-2026-53435). Jenkins is a development automation server used to build, test, and deploy software. The vulnerability allows a remote authenticated attacker to use the Script Console to execute arbitrary code and read files from the Jenkins controller. The vulnerability was added to the VulnCheck KEV on June 15 and fixed in RedOS on August 12.

🔻 CodeInj - WordPress (CVE-2026-60137). WordPress is a popular open-source CMS for creating websites and blogs. The vulnerability leads to a blind SQL injection in the WordPress core, allowing a remote unauthenticated attacker to read user accounts and password hashes from the WordPress database. Code execution is then possible by installing a malicious plugin. Multiple public exploits are available. The vulnerability was added to the CISA KEV catalog on July 21. A fix for the wordpress package in the Debian repository was released on July 23.

🔻 RCE - SPIP (CVE-2026-77647). SPIP is an open-source CMS for creating and collaboratively editing websites. The vulnerability allows an unauthenticated remote attacker to execute arbitrary PHP code. The vulnerability was added to the VulnCheck KEV on August 20. A fix for the spip package in the Debian repository was released on August 18.

Strictly speaking, the report contains one more vulnerability RCE - WinRAR (CVE-2025-8088) that is being exploited in the wild. The vulnerability was fixed in the clamav package in the Alt Linux repository. However, exploitation is only possible on Windows, so it is out of scope.

Another 127 vulnerabilities are not known to be exploited in the wild, but public exploits are available for them, or there are indications that such exploits exist. Notable examples include:

🔸 RCE - Action Pack "KindaRails2Shell" (CVE-2026-66066). Action Pack is a component of Ruby on Rails responsible for handling web requests, routing, and generating responses. An attacker can upload a specially crafted image to a vulnerable application and achieve remote code execution.

🔸 RCE - WordPress "XSS2Shell" (CVE-2026-64638). The attack chain allows an unauthenticated XSS on the login page to be escalated to arbitrary PHP code execution.

🔸 CodeInj - PHP (CVE-2026-17543). Improper escaping of backslashes in attacker-controlled parameters can lead to a trivial SQL injection in PHP.

🔸 EoP - Linux Kernel "Zapscape" (CVE-2026-64561). This KVM escape vulnerability allows an attacker to break out of a virtual machine in KVM/x86 environments and execute commands on the host with root privileges.

🔸 EoP - Linux Kernel "OVSwrap" (CVE-2026-64531), Linux Kernel "SCTPhantom" (CVE-2026-64564), Linux Kernel "Ubuntu PPPoL2TP" (CVE-2026-68398). These vulnerabilities allow a local attacker to escalate privileges to root.

🔸 AuthBypass - Traefik (CVE-2026-48020). Traefik is an HTTP reverse proxy and load balancer. A high-severity vulnerability in the StripPrefix middleware allows an unauthenticated attacker to bypass route-level authentication and authorization.

🗒 Full Vulristics report

The Vulners team has released nmap-vulners 2.0

The Vulners team has released nmap-vulners 2.0

The Vulners team has released nmap-vulners 2.0. This plugin (an NSE script) turns the popular Nmap port scanner into a black-box vulnerability scanner. Simply run $ nmap -sV --script vulners <target> to get a prioritized report on vulnerabilities and exploits. And all of this is available for free with no limitations. 🆓😉

How exactly does this plugin work?

To find vulnerabilities, the software is identified first:

🔹 The service's CPE identifier may be provided by Nmap itself (using the -sV option).

🔹 If Nmap fails to identify the service, the plugin attempts to determine the CPE identifier from the raw banner using rules for FTP, SMTP, SSH, MySQL, DNS, NTP, LDAP, and other services. Starting with version 2.0, the fingerprint catalog is updated weekly based on Recog, Wappalyzer, WhatWeb, FingerprintHub, and nuclei-templates. The latest catalog is automatically fetched when the plugin runs.

🔹 If an HTTP service is detected, nmap-vulners also attempts to identify the web stack, including the framework, CMS, or PHP version behind a reverse proxy. It analyzes Server and X-Powered-By headers, cookies, the page title, meta tags, filenames in script src, and page content. The plugin includes more than 700 rules. In version 2.0, the number of HTTP path fingerprints increased from 125 to 939, while parallelization kept the processing time at around 6 seconds per port.

🔹 If a product is identified but its version is unknown, the plugin makes a single request to a known file that contains version information, such as /CHANGELOG.txt for Drupal or /administrator/manifests/files/joomla.xml for Joomla. This works with Concrete5, Drupal, Jira, Joomla, Apache Tomcat, and WordPress.

🔹 Finally, if a service cannot be identified, Smart Audit can be used. The raw banner is sent to the Vulners server, which identifies the software and its version and then looks for related vulnerabilities. This is the only paid feature! Each unique request costs 1 credit, and results are cached. The number of requests is limited by the vulners.max_items parameter, which defaults to 32. Smart Audit can be disabled entirely with --script-args vulners.max_items=0.

The service data is then sent to the Vulners server, which returns a prioritized vulnerability report. For each vulnerability or exploit, the report includes its ID, SEVERITY level, CVSS and EPSS scores, Vulners AI score, KEV and EXP flags, and a link to its page on the Vulners website.

So, is an API key actually required?

🔹 The plugin can work without an API key. However, detection will use the legacy endpoint, and some vulnerability and exploit data will not be available.

🔹 Adding an API key, even without credits, enables the "EXP" flag for vulnerabilities and the "KEV" flag for both vulnerabilities and exploits. It also adds an EPSS score column, providing more complete prioritization: KEV → CISA SSVC Exploitation Active → exploits → EPSS → CVSS. So, an API key is recommended. 😉

🔹 If your API key has credits, the Smart Audit feature is also available (see above).

Installation

To install the plugin, simply run the one-line script. The installer automatically finds Nmap and its NSE script directory, installs the latest vulners.nse version, and removes old 1.x files. It then runs nmap --script-updatedb and verifies the installation. The --user and --prefix options let you specify the installation directory, while --uninstall removes the plugin. If needed, the installer prompts for a Vulners API key, validates it, and saves it to ~/.nmap/vulners.key with permissions set to 600.
August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August In the Trend of VM (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

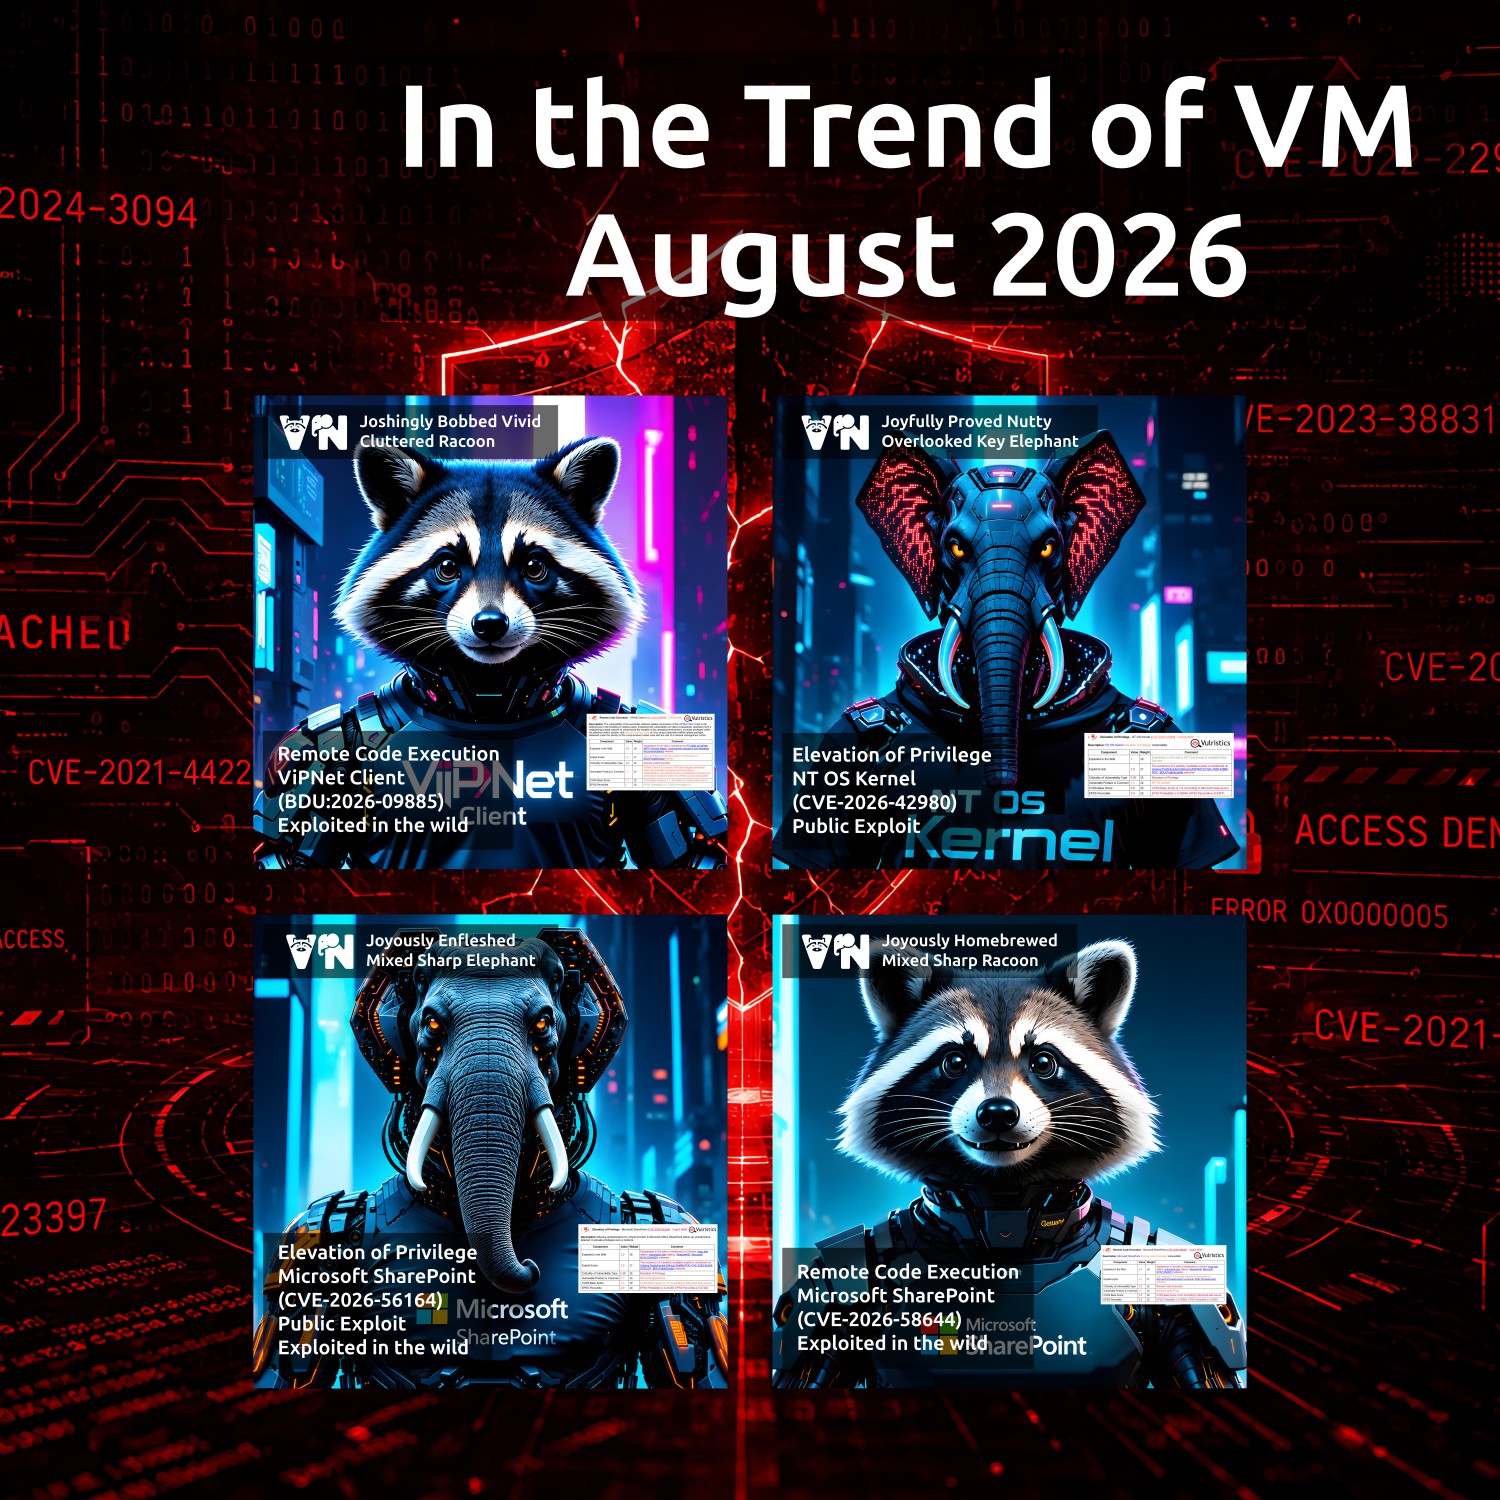
August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint. I present the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous July edition, there was just one vulnerability. This time, there are four.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - ViPNet Client (BDU:2026-09885). The first trending vulnerability in a Russian-made product since the beginning of 2026. Its exploitation was discovered by Positive Technologies experts.

🔻 EoP - NT OS Kernel (CVE-2026-42980). The vulnerability allows an attacker to escalate privileges to NT AUTHORITY\SYSTEM level.

🔻 EoP - Microsoft SharePoint (CVE-2026-56164) and RCE - Microsoft SharePoint (CVE-2026-58644). Two actively exploited vulnerabilities in a popular platform for building corporate websites, managing documents, and collaborating.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - Microsoft SharePoint (CVE-2026-58644) vulnerability

About Remote Code Execution - Microsoft SharePoint (CVE-2026-58644) vulnerability

About Remote Code Execution - Microsoft SharePoint (CVE-2026-58644) vulnerability. Information about this vulnerability was published on July 14 as part of the July Microsoft Patch Tuesday. The vulnerability in Microsoft SharePoint Server, caused by a deserialization flaw (CWE-502), allows an attacker with Site Owner privileges or higher to inject and remotely execute arbitrary code on the SharePoint server. This can result in full server compromise, including the exfiltration of corporate documents and data, their modification or deletion, compromise of credentials accessible to the server, and further lateral movement into the organization's internal infrastructure.

The authentication requirement, of course, makes exploitation of the vulnerability more difficult. However, an attacker could potentially leverage the previously disclosed EoP vulnerability CVE-2026-56164. At the same time, there is currently no confirmation that these vulnerabilities have been exploited together as part of a single attack chain.

👾 Microsoft experts flagged this vulnerability as being exploited in the wild on the day of Patch Tuesday. Two days later, on July 16, the vulnerability was added to the CISA KEV catalog. Details of the attacks are not yet known.

🛠 No public exploits have been observed so far.

⚙️ Updates are available for Microsoft SharePoint Server 2016, 2019, and Subscription Edition.

July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability

July In the Trend of VM (#29): Microsoft Exchange Server vulnerability

July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability. Here is my traditional monthly roundup of trending vulnerabilities, according to Positive Technologies. The previous June edition featured four vulnerabilities. This time, there's only one.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 XSS - Microsoft Exchange (CVE-2026-42897). The vulnerability allows attackers to execute arbitrary JavaScript in a user's browser when the user opens a malicious email in Outlook Web Access (OWA). A public proof-of-concept exploit is available, and the vulnerability has already been exploited in the wild.

🟥 The full list of trending vulnerabilities is available on the portal