Tag Archives: Nessus

The Vulners team has introduced a new AI-powered product - Cube

The Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - CubeThe Vulners team has introduced a new AI-powered product - Cube

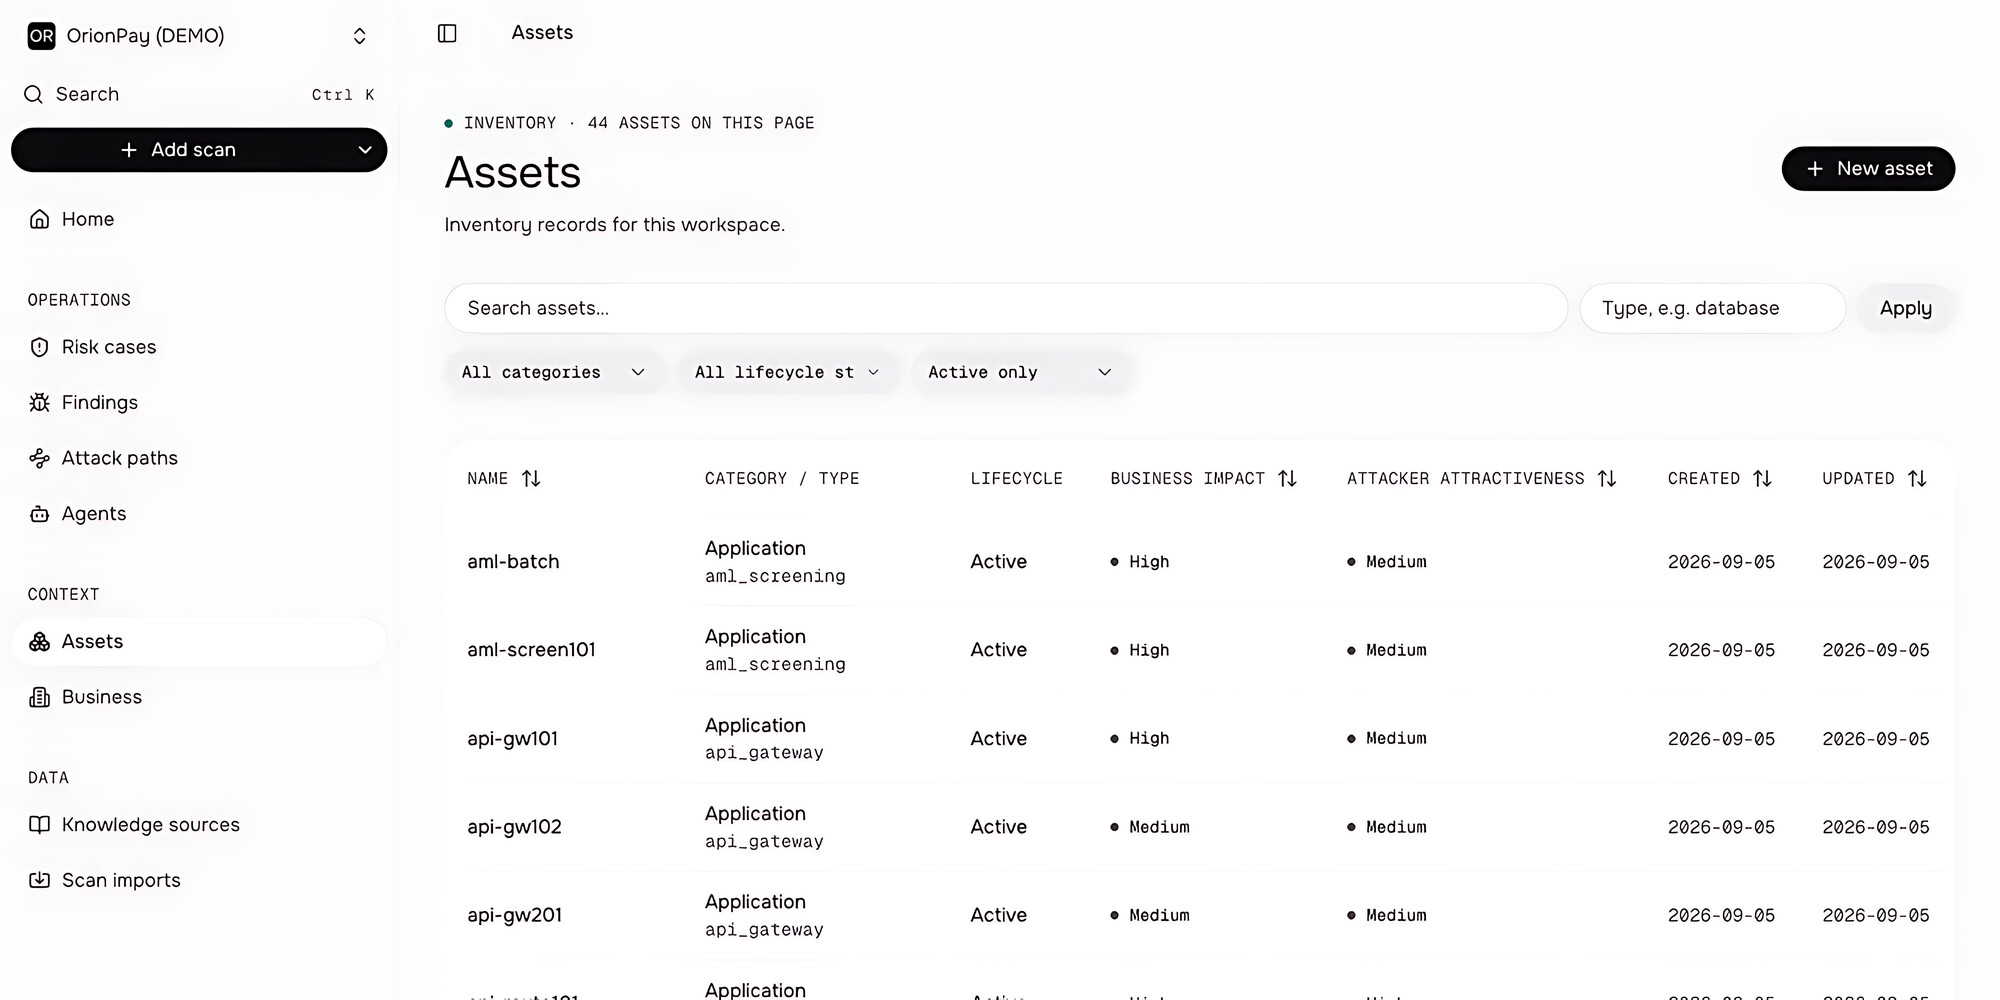
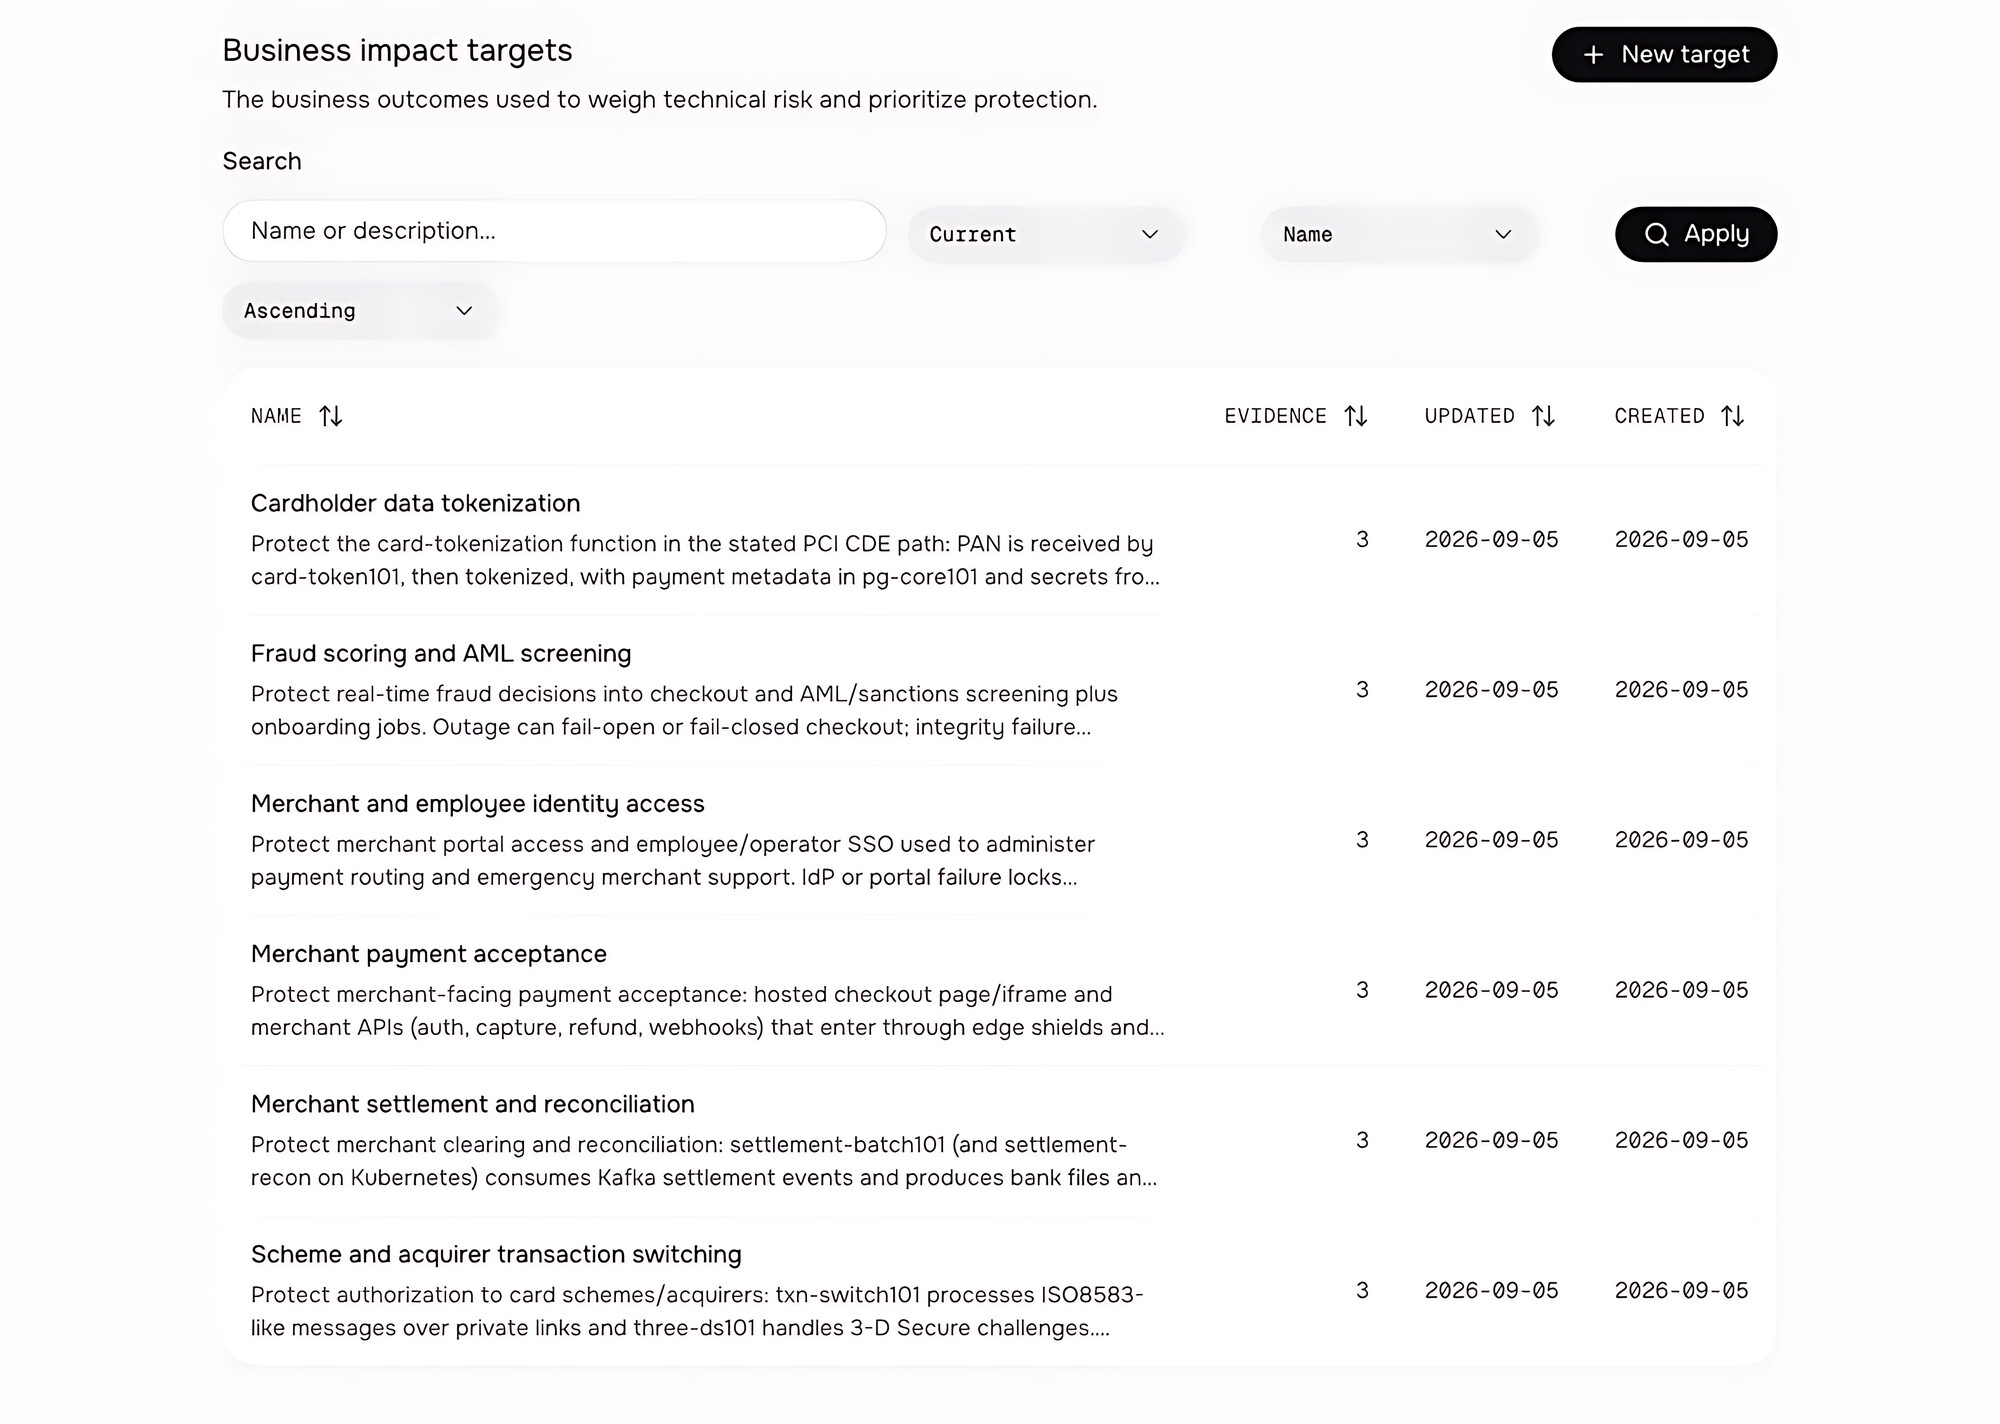
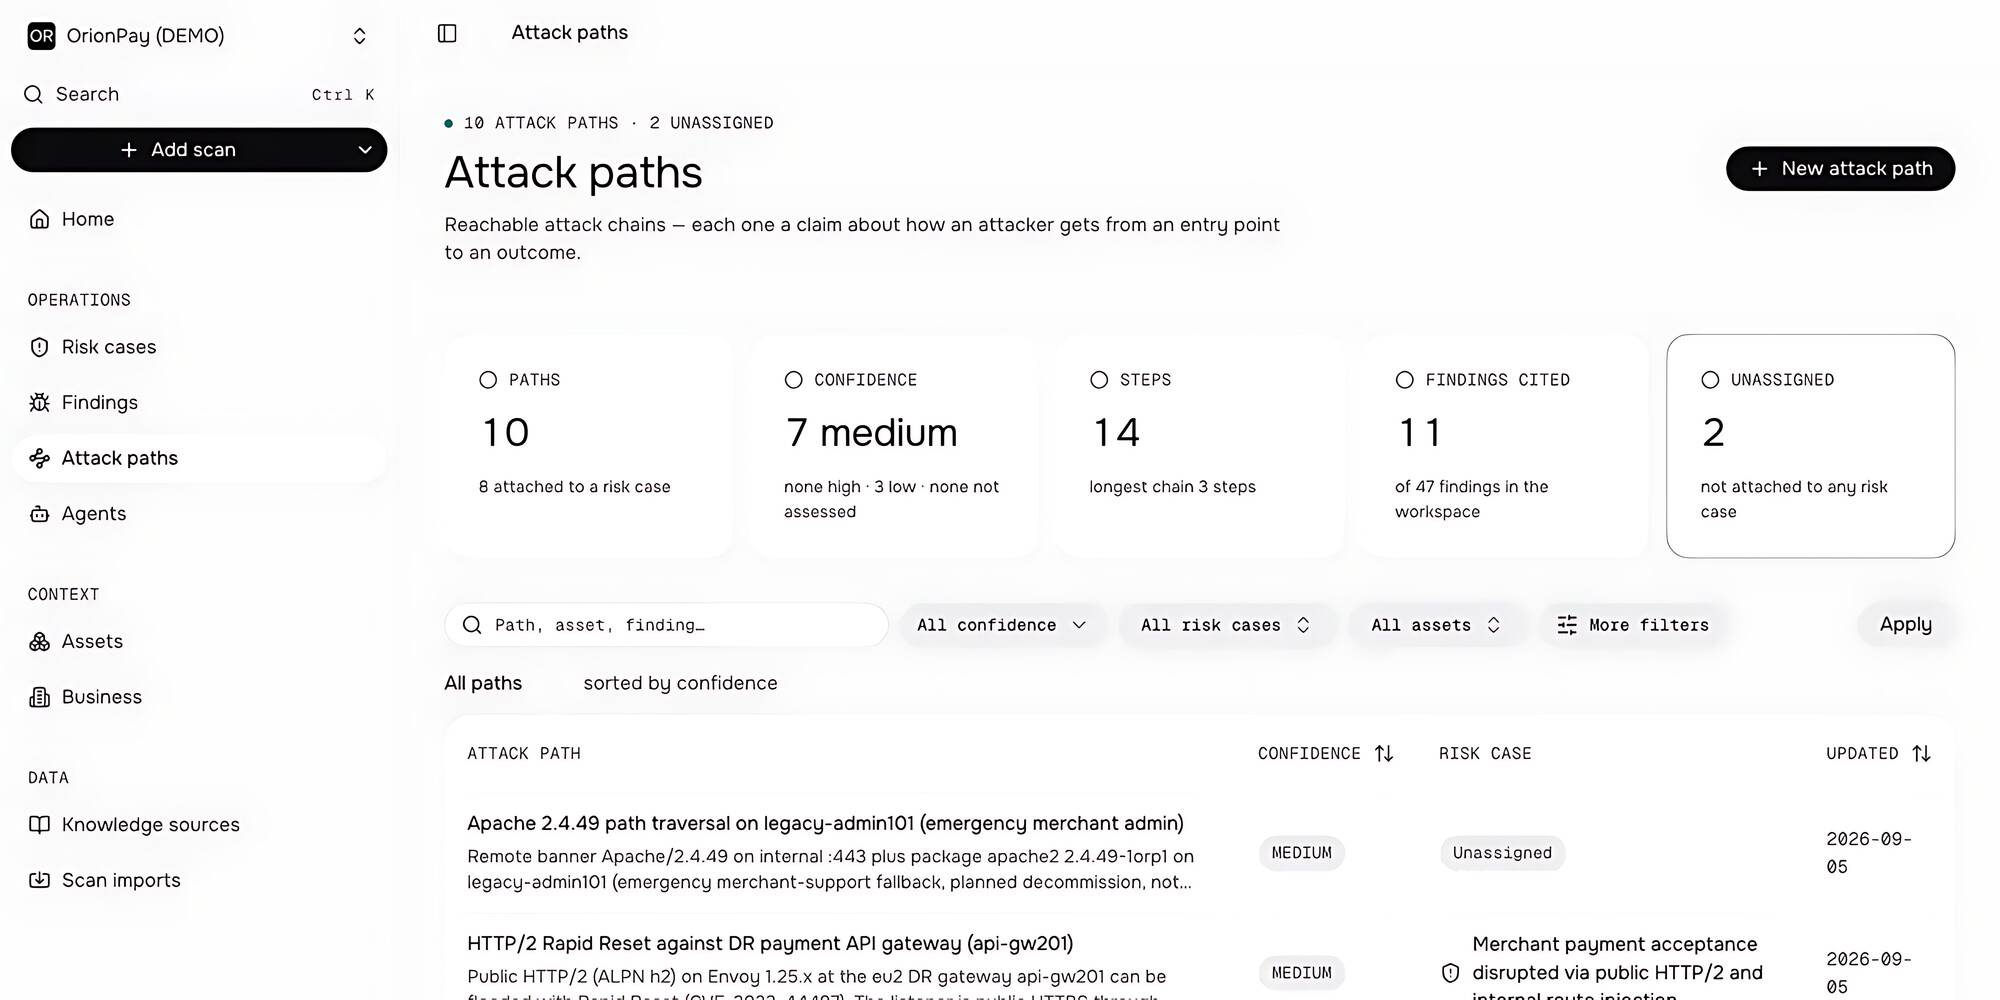
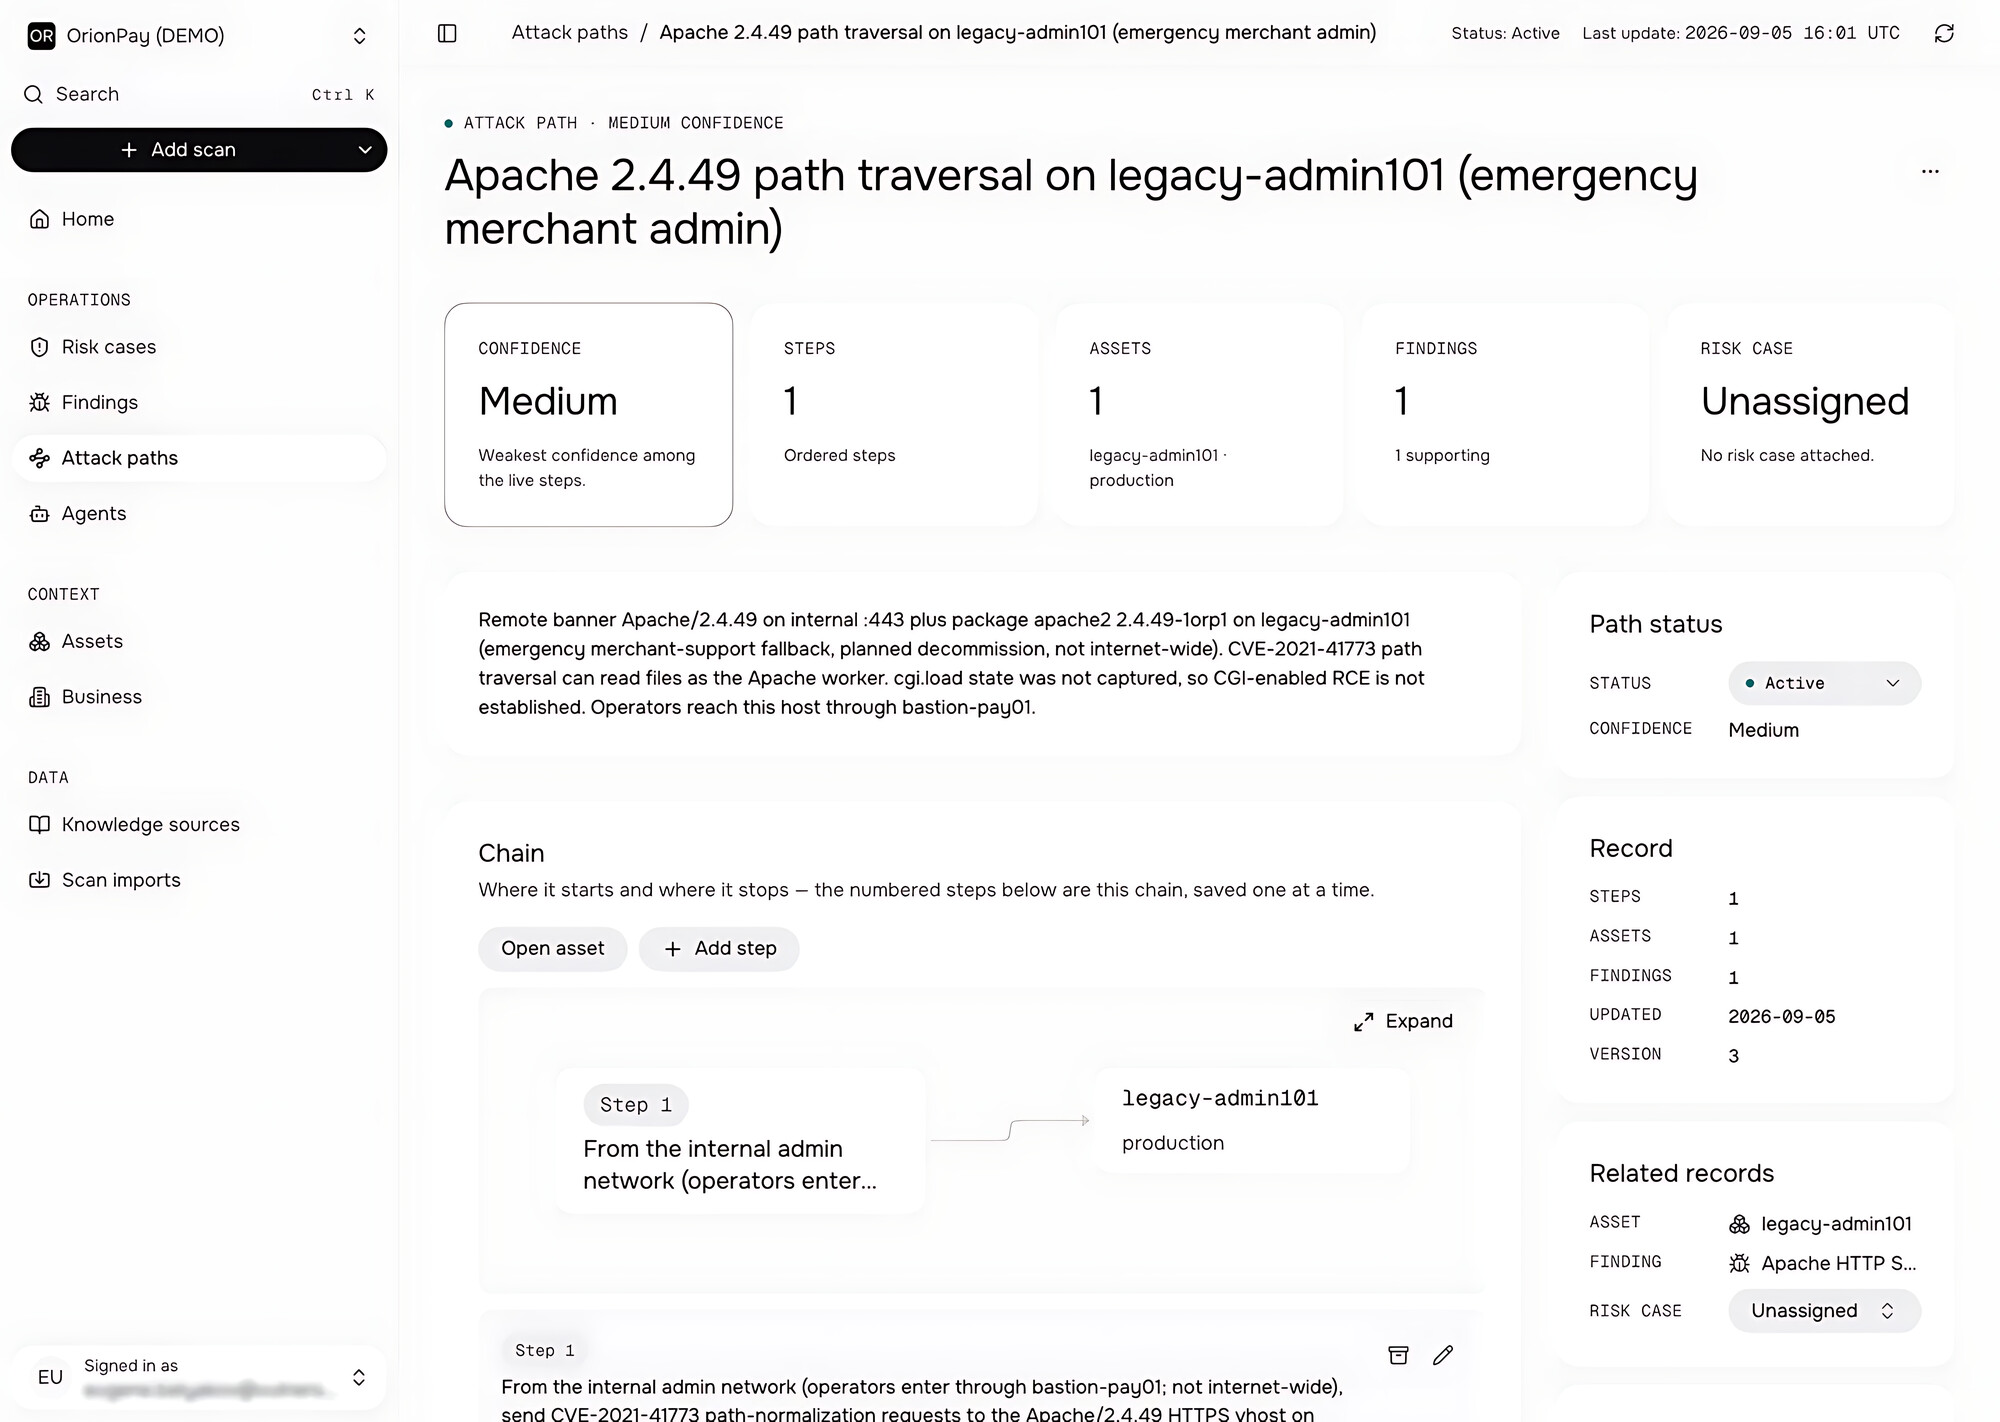
The Vulners team has introduced a new AI-powered product - Cube. The platform provides contextual analysis of vulnerability scan results, correlating technical findings with information about an organization's infrastructure and business processes.

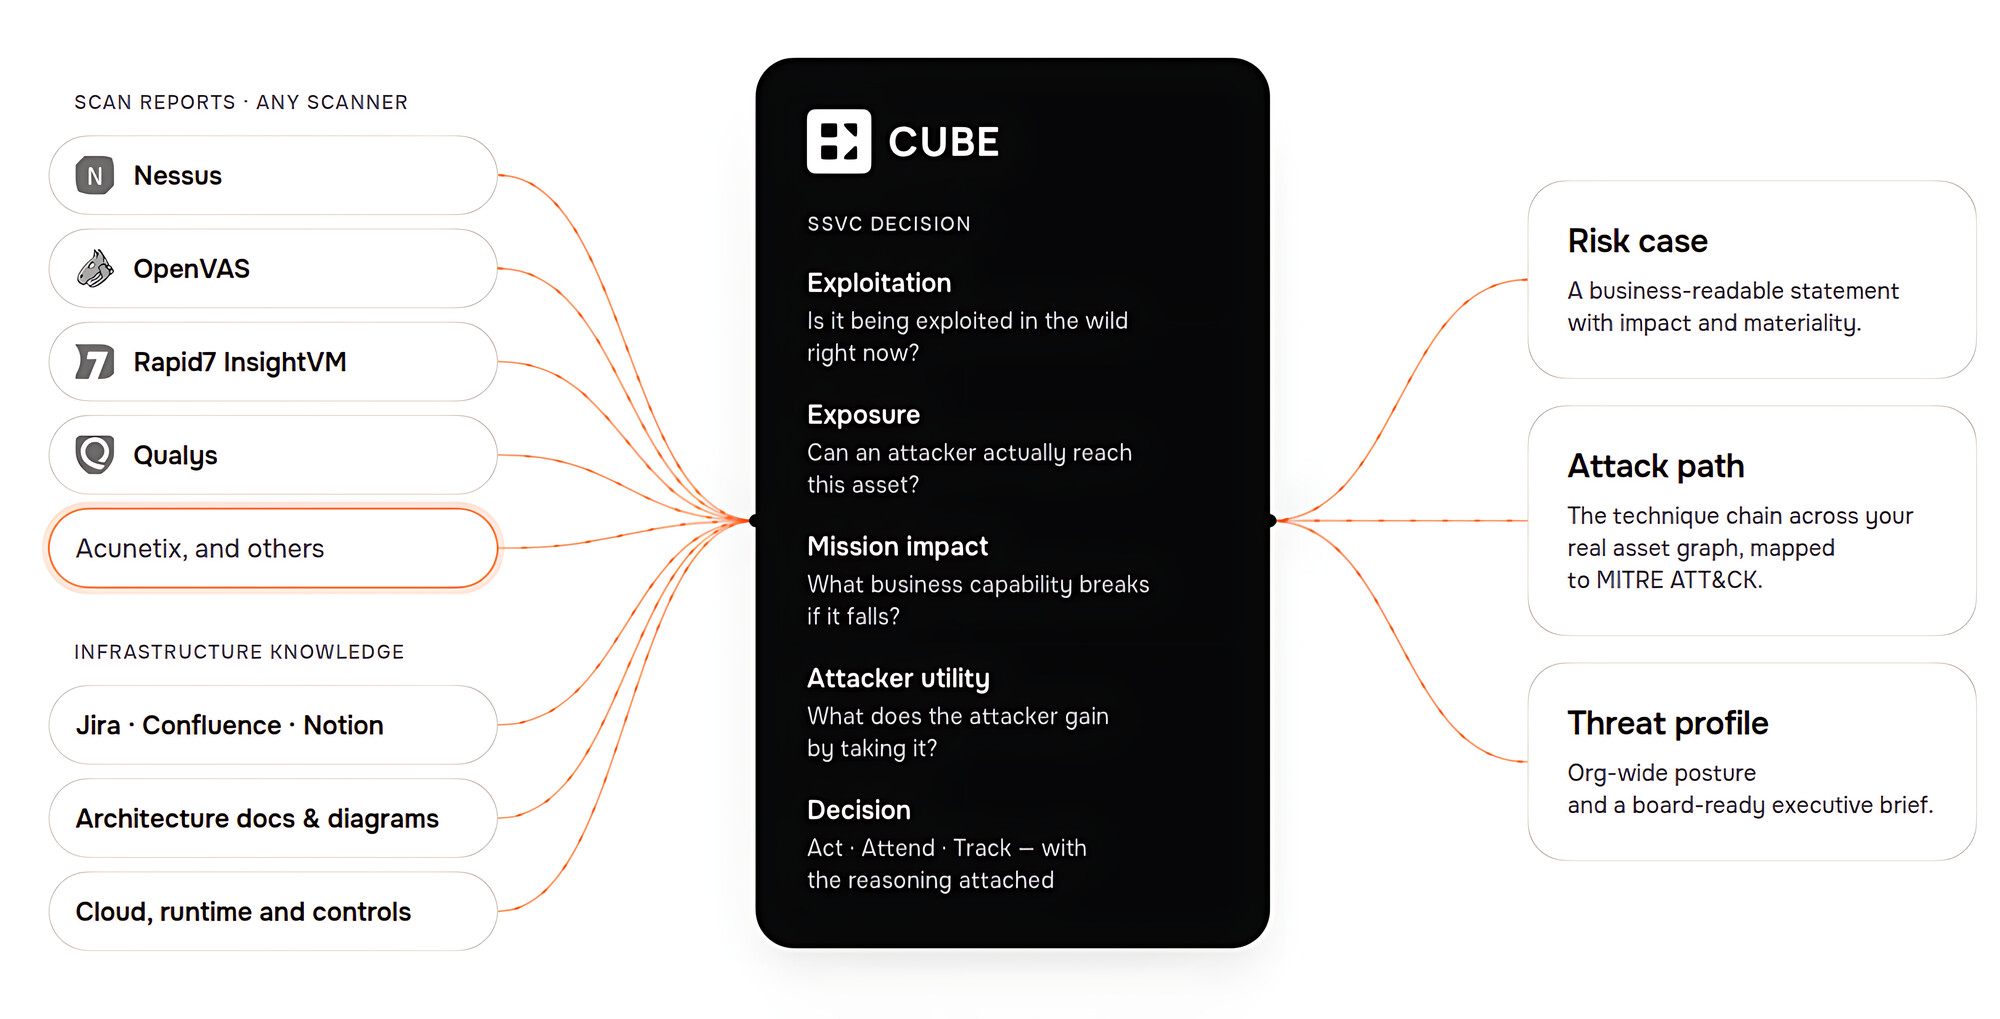
Cube is built around three core layers:

📥 Evidence Layer - collects reports from existing vulnerability scanners, including Nessus, OpenVAS, Qualys, Rapid7 InsightVM, Acunetix, and others. It processes the findings and maps them to actual infrastructure assets.

🗺️ Context Layer - enriches scan results with infrastructure data from architectural documentation, diagrams, task tracker tickets, cloud environments, and business processes. It builds a contextual model of the infrastructure, including a CMDB and network graph, helping identify affected assets, evaluate their exposure, and understand their role in business operations.

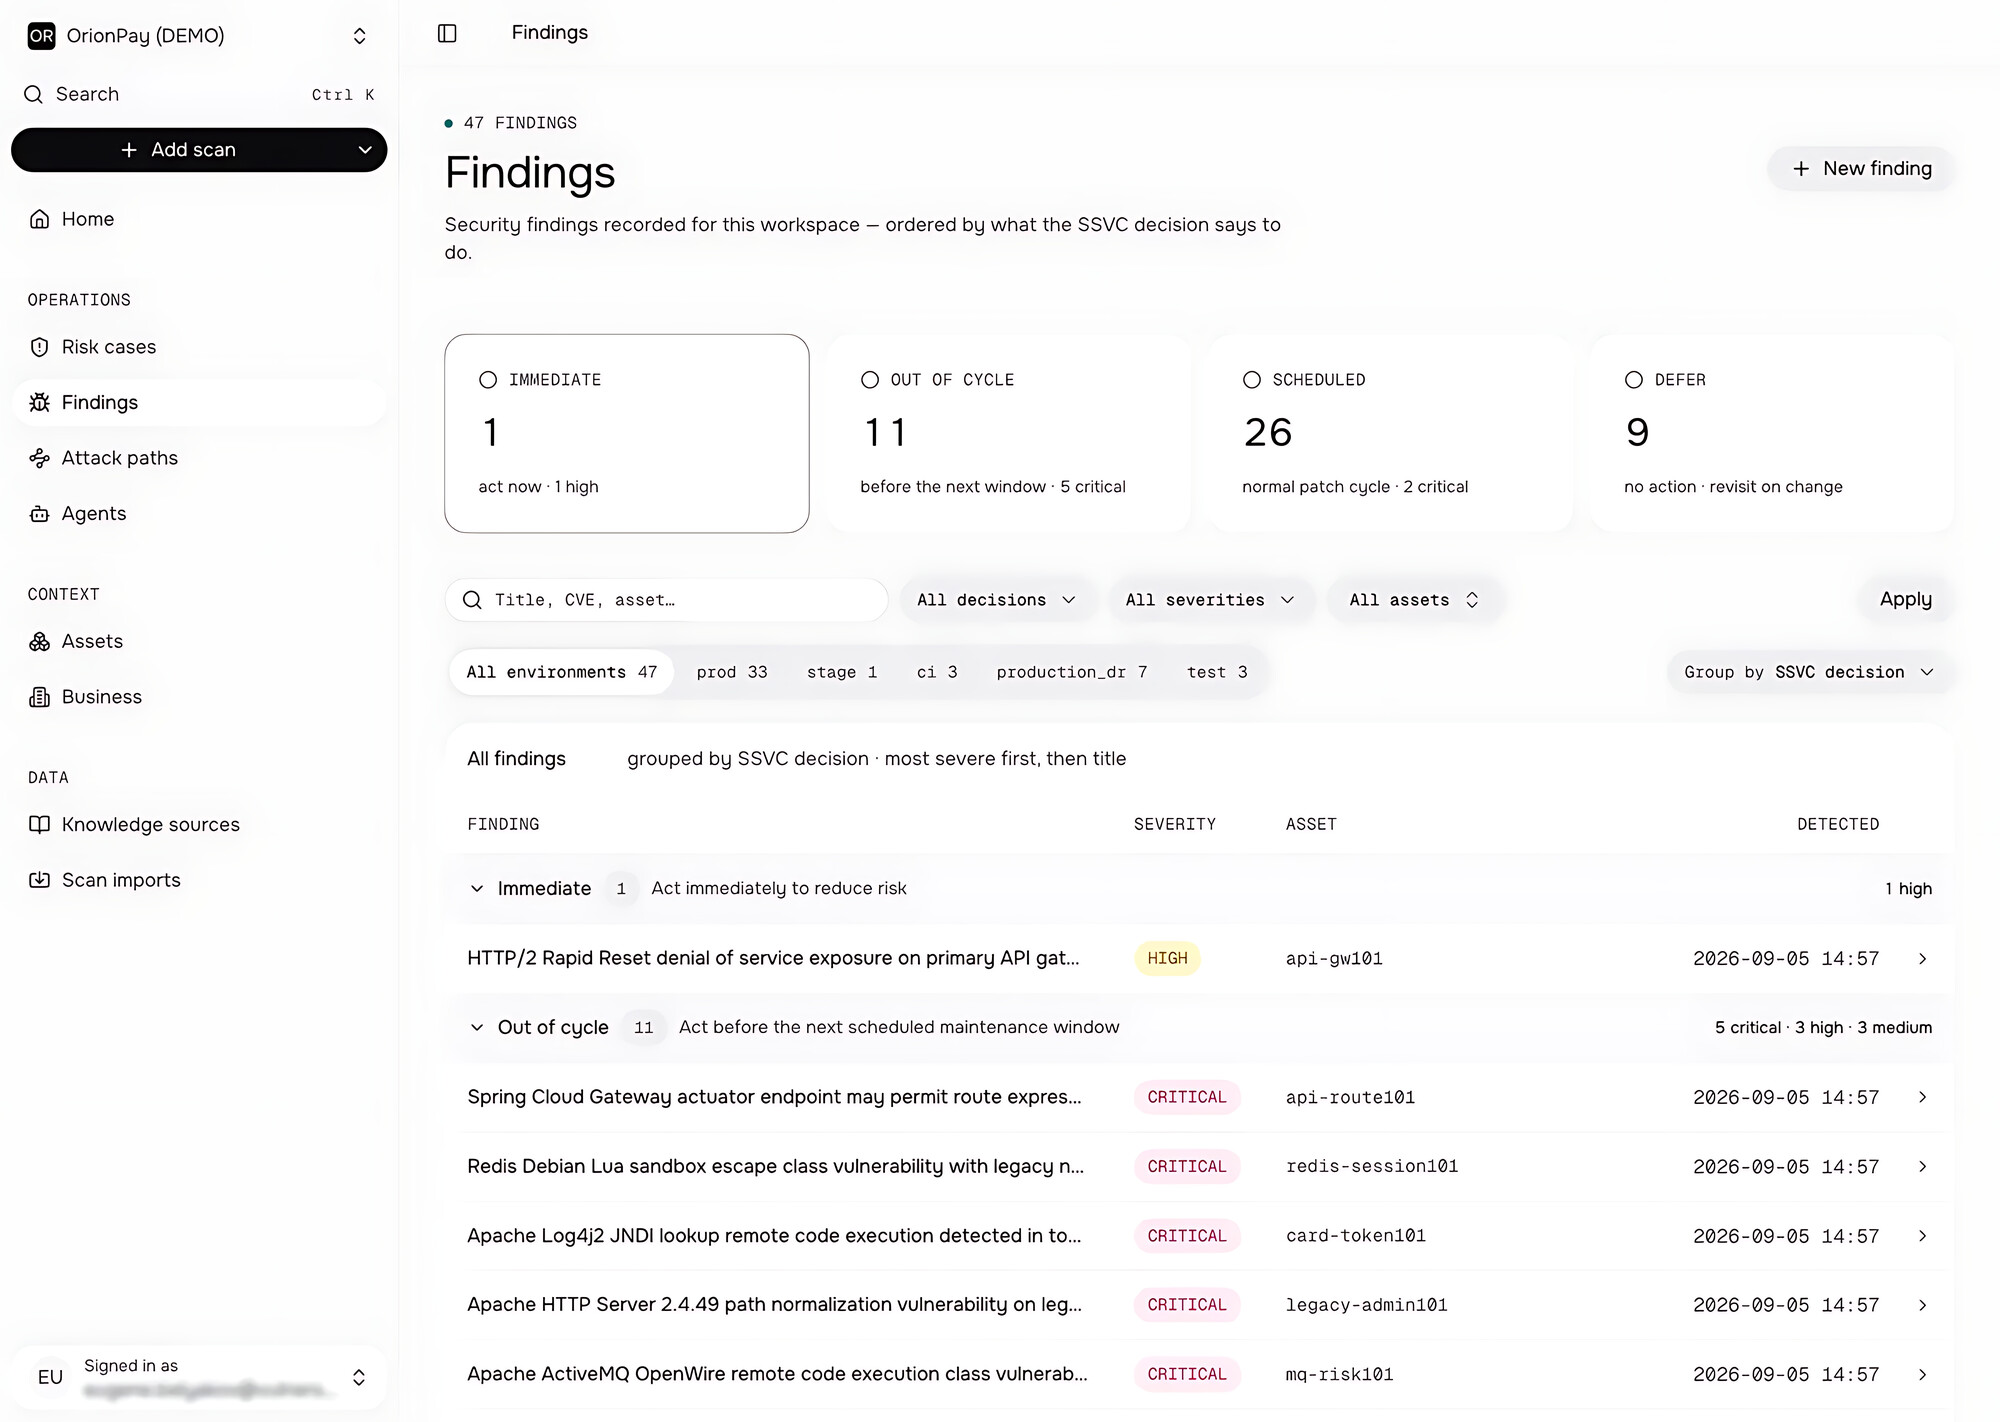
🧠 Decision Layer - uses the CISA SSVC (Stakeholder-Specific Vulnerability Categorization) methodology to prioritize remediation efforts. Unlike CVSS, which focuses on the technical severity of vulnerabilities, SSVC uses a decision tree that takes exploitation conditions and potential business impact into account.

The CISA SSVC model defines four possible decision outcomes:

🟢 Track - vulnerability remediation follows the standard Vulnerability Management process. The vulnerability is monitored and addressed according to standard software update timelines.

🟡 Track* - the vulnerability requires closer monitoring, with its assessment revisited as new information or circumstances emerge.

🟠 Attend - the vulnerability requires increased attention from security teams and relevant management. This may involve bringing in additional experts and notifying key stakeholders. Remediation should be accelerated.

🔴 Act - the vulnerability requires escalation to senior management, with response efforts coordinated across departments. A coordinated action plan is developed, the necessary stakeholders are engaged, and remediation is carried out as soon as possible.

SSVC therefore determines not only which vulnerabilities should be addressed first, but also the level of organizational response required to address them.

Cube provides users with several types of results:

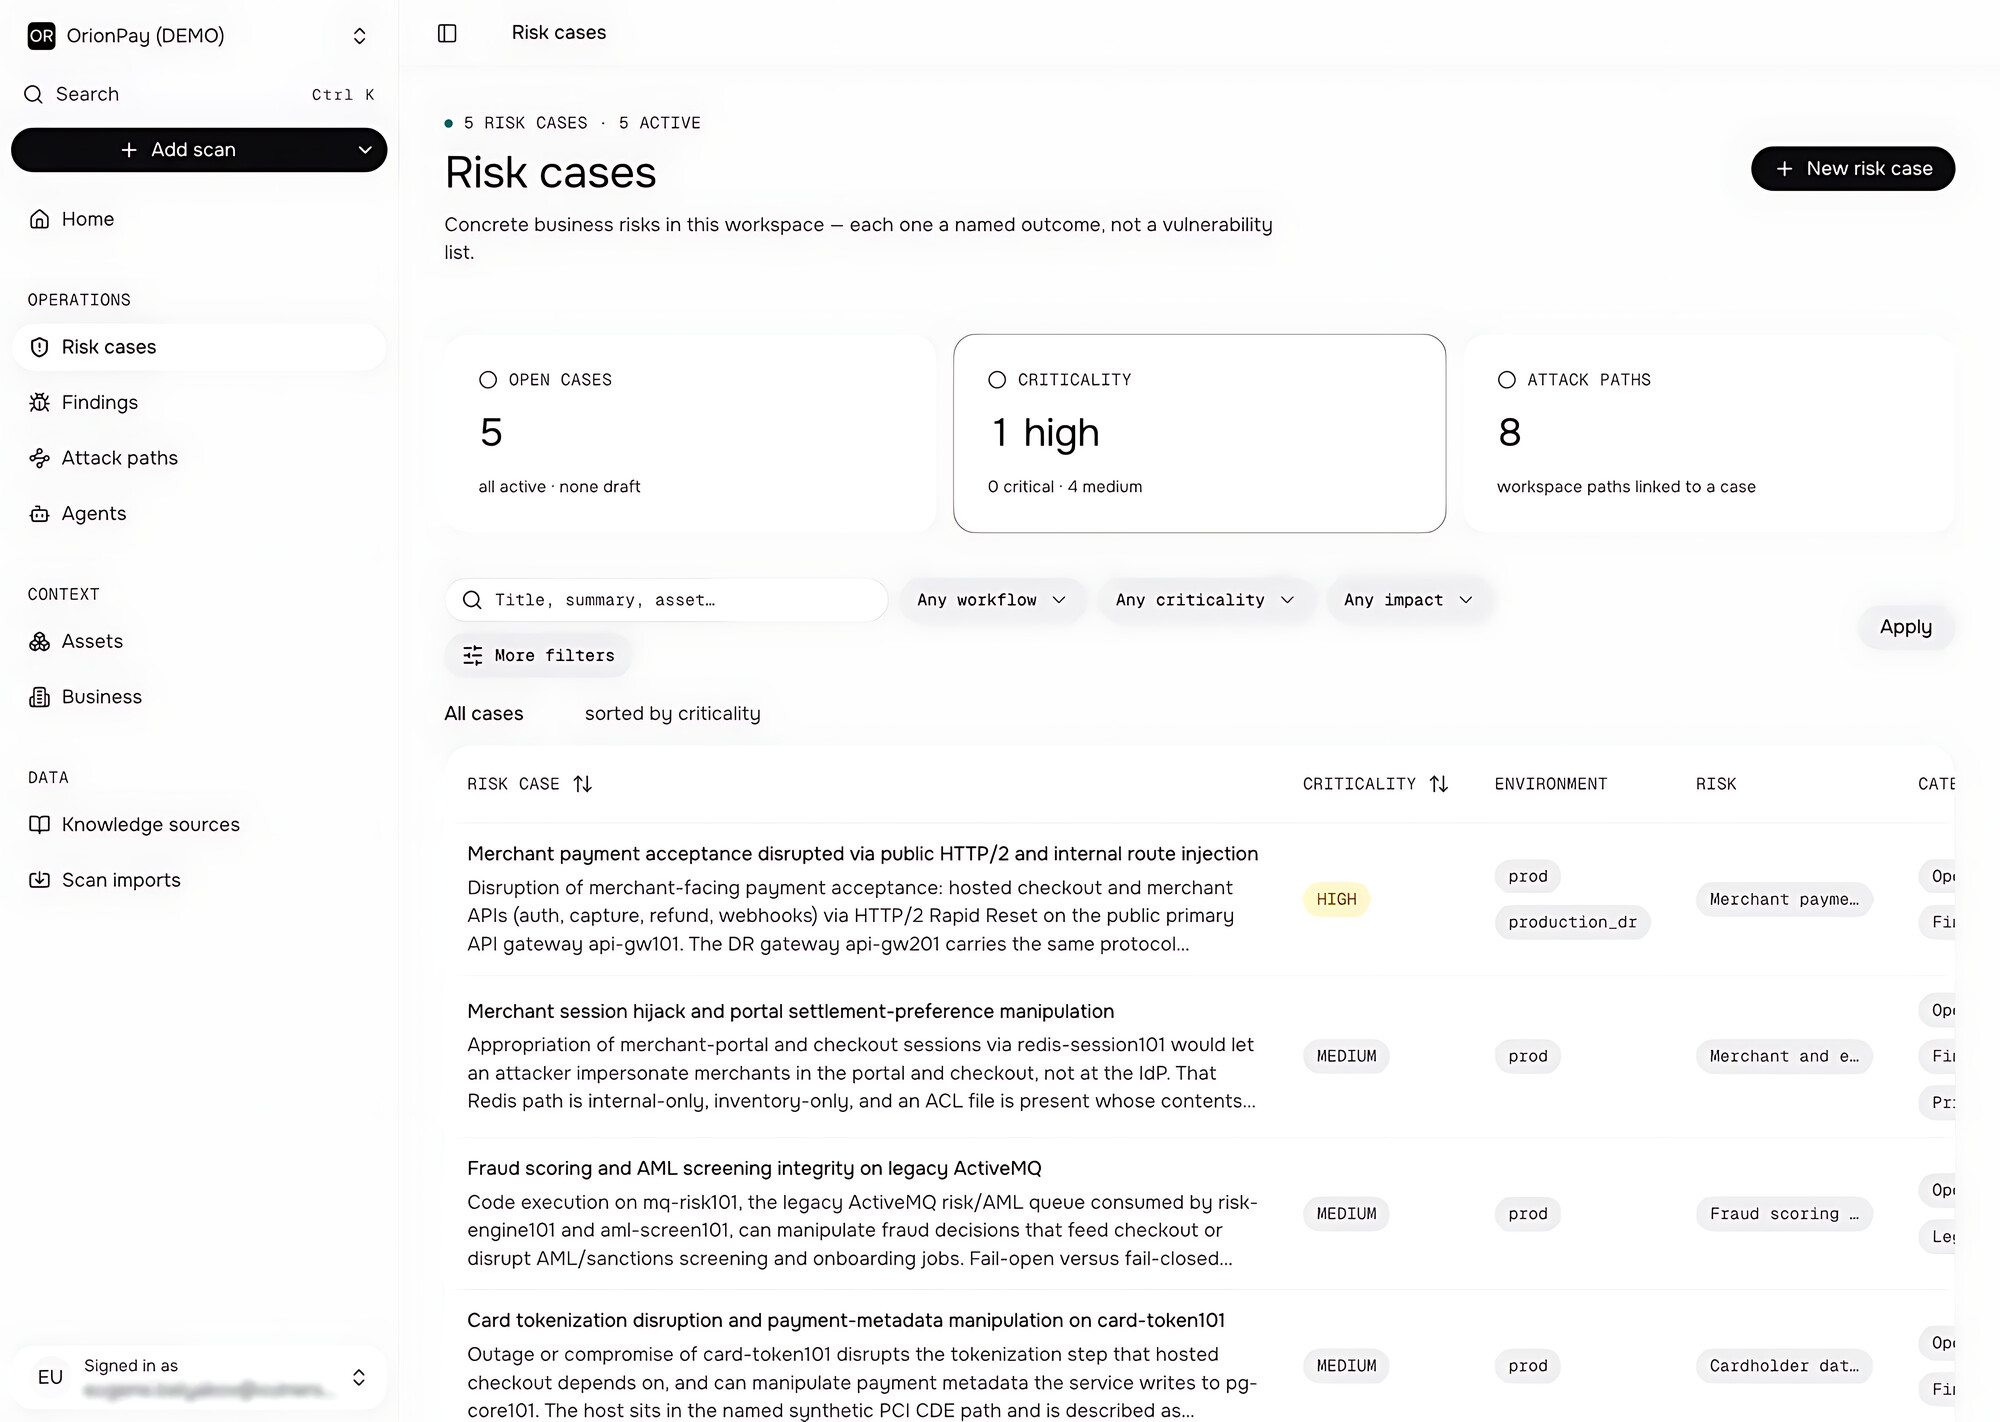
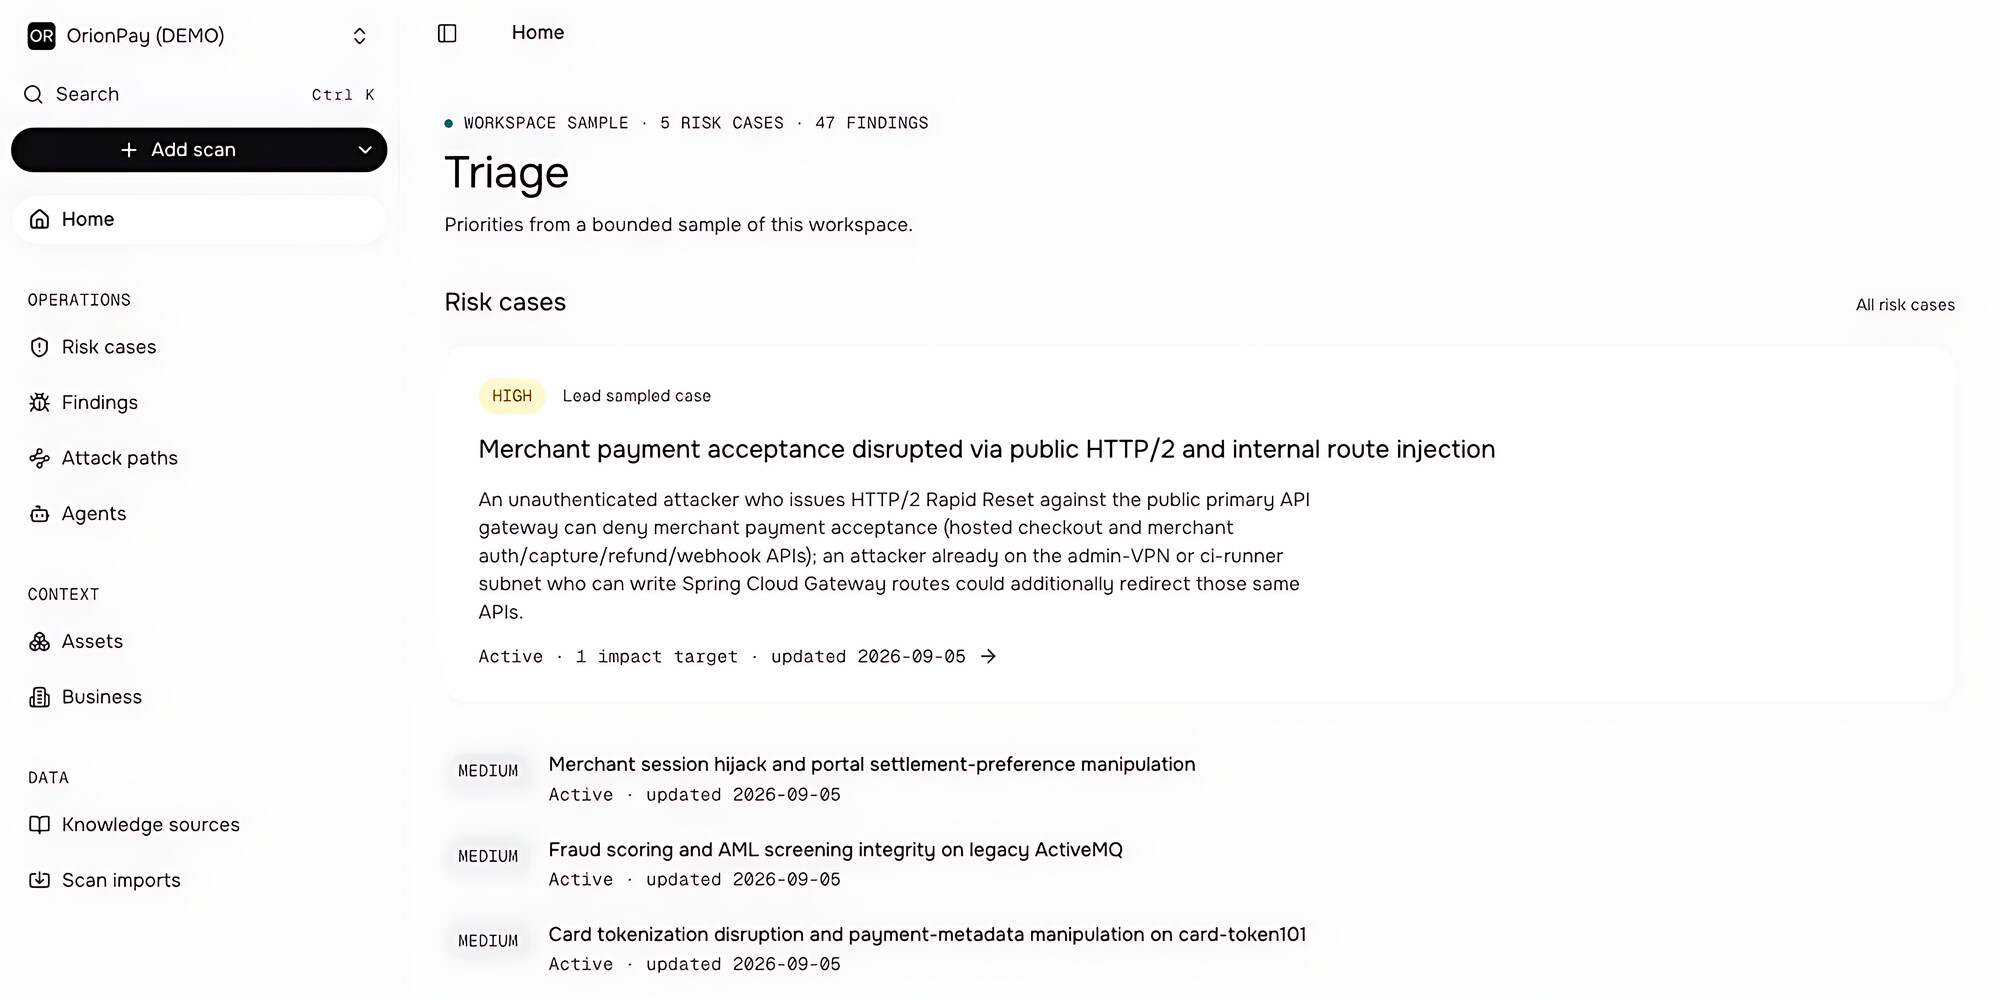
🎯 Risk Cases - grouped findings accompanied by severity ratings and assessments of potential business impact.

🛤️ Attack Paths - potential attack paths between assets, aligned with the MITRE ATT&CK framework.

🛡️ Threat Profile - an overview of the threat landscape and the current state of the infrastructure.

📋 Decision Rationale - explanations of decisions, linked to the original reports, assessments, and infrastructure data.

For example, a vulnerability with a CVSS score of 9.8 on an isolated internal build server may be assigned a lower priority than a vulnerability with a CVSS score of 7.5 on a publicly accessible payment gateway. In the latter case, the potential business impact is significantly greater.

The platform is deployed within the customer's own infrastructure (on-premises) and supports any LLM with an OpenAI- or Anthropic-compatible API, including proprietary models running on the customer's GPU servers. This means Cube does not lock customers into a specific AI provider. Vulners does not charge for token usage, leaving customers in control of their LLM costs. According to Vulners, running the model in a medium-sized infrastructure costs approximately $1,000 per month.

To summarize, Cube enriches traditional Vulnerability Management by linking technical vulnerabilities to infrastructure assets, operational processes, and potential business impact.
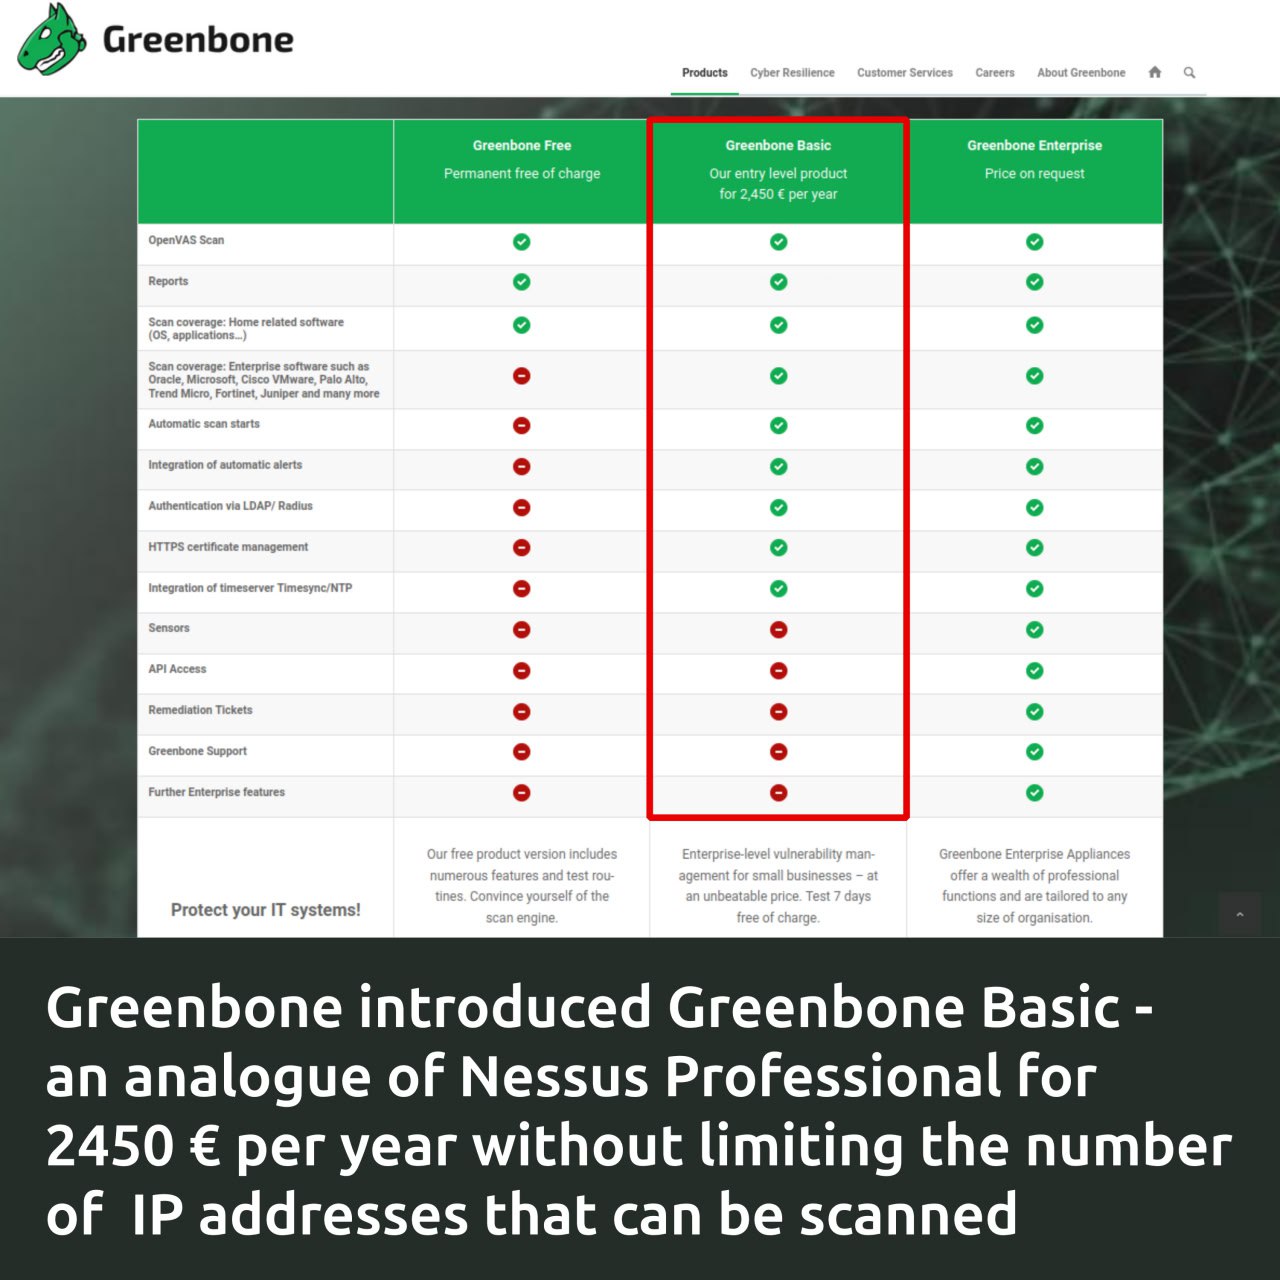
Greenbone introduced the Greenbone Basic vulnerability scanner for SMEs, the price of which is NOT tied to the number of IP addresses that can be scanned

Greenbone introduced the Greenbone Basic vulnerability scanner for SMEs, the price of which is NOT tied to the number of IP addresses that can be scanned

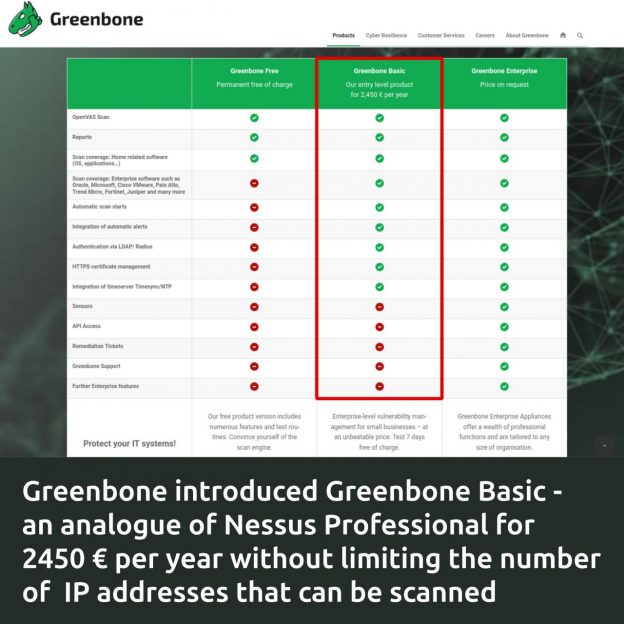
Greenbone introduced the Greenbone Basic vulnerability scanner for SMEs, the price of which is NOT tied to the number of IP addresses that can be scanned. A license for 1 scanner will cost 2450 € per year. It will be delivered as a virtual machine image. There is a comparison table and a data sheet.

Greenbone Basic differences:

🔹 Compared to Greenbone Free, it WILL have a full database of plugins for vulnerability detection, compliance scanning, scan scheduler, alerts, LDAP/Radius authentication, HTTPS certificate management, NTP integration.

🔹 Compared to Greenbone Enterprise, there WILL NOT be the ability to hierarchically connect scanners (sensors). API support, vulnerability remediation tickets, technical support from Greenbone and further enterprise features.

In terms of features, it looks like a real alternative to Tenable's Nessus Professional. Competition in the entry-level fixed-price VM segment is intensifying. 👍

На русском

Vulnerability Management news and publications #2

Vulnerability Management news and publications #2. Hello everyone! This is the second episode of Vulnerability Management news and publications. In fact, this is a collection of my posts from the avleonovcom and avleonovrus telegram channels. Therefore, if you want to read them earlier, subscribe to these channels.

The main idea of ​​this episode. Microsoft is a biased company. In fact, they should now be perceived as another US agency. Does this mean that we need to forget about Microsoft and stop tracking what they do? No, it doesn’t. They do a lot of interesting things that can at least be researched and copied. Does this mean that we need to stop using Microsoft products? In some locations (you know which ones) for sure, in some we can continue to use such products if it is reasonable, but it’s necessary to have a plan B. And this does not only apply to Microsoft. So, it’s time for a flexible approaches. Here we do it this way, there we do it differently. It seems that rather severe fragmentation of the IT market is a long-term trend and it’s necessary to adapt to it.

Alternative video link (for Russia): https://vk.com/video-149273431_456239097

What’s in this episode:

  1. Microsoft released a propaganda report, what does this mean for us?
  2. Microsoft released the Autopatch feature, is it a good idea to use it?
  3. Ridiculous Vulnerability: Hardcoded Password in Confluence Questions
  4. The new Nessus Expert and why it’s probably Tenable’s worst release
  5. Rapid7 Nexpose/InsightVM features added in Q2 2022: what’s good and what’s weird
  6. Palo Alto: Malicious scan 15 minutes after CVE is released. Oh really?
  7. 6 groups of vulnerabilities that are most often used in attacks, according to Palo Alto, and the end of IT globalization

Continue reading →

VMconf 22: Blindspots in the Knowledge Bases of Vulnerability Scanners

VMconf 22: Blindspots in the Knowledge Bases of Vulnerability Scanners. Hello everyone! This video was recorded for the VMconf22 Vulnerability Management conference. I want to talk about the blind spots in the knowledge bases of Vulnerability Scanners and Vulnerability Management products.

This report was presented in Russian at Tenable Security Day 2022. The video is here.

Potential customers rarely worry about the completeness of the Knowledge Base when choosing a Vulnerability Scanner. They usually trust the VM vendors’ claims of the “largest vulnerability base” and the total number of detection plugins. But in fact the completeness is very important. All high-level vulnerability prioritization features are meaningless unless the vulnerability has been reliably detected. In this presentation, I will show the examples of blindspots in the knowledge bases of vulnerability management products, try to describe the causes and what we (as customers and the community) can do about it.

Continue reading →

Vulnerability Intelligence based on media hype. It works? Grafana LFI and Log4j "Log4Shell" RCE

Vulnerability Intelligence based on media hype. It works? Grafana LFI and Log4j “Log4Shell” RCE. Hello everyone! In this episode, I want to talk about vulnerabilities, news and hype. The easiest way to get timely information on the most important vulnerabilities is to just read the news regularly, right? Well, I will try to reflect on this using two examples from last week.

I have a security news telegram channel https://t.me/avleonovnews that is automatically updated by a script using many RSS feeds. And the script even highlights the news associated with vulnerabilities, exploits and attacks.

And last Tuesday, 07.02, a very interesting vulnerability in Grafana was released.

Continue reading →

How to fix "Nessus failed to load the SSH private key" error?

How to fix “Nessus failed to load the SSH private key” error? If you are using Nessus to scan Linux hosts and authenticate by key, you may encounter this problem.

You have generated the keys correctly, placed the public key on a remote server. You can connect to this server using the private key.

ssh -p22 -i private_key user@server.corporation.com

But when scanning with Nessus, you get weird errors in the various plugin outputs:

  • Target Credential Status by Authentication Protocol – Failure for Provided Credentials
  • Nessus failed to load the SSH private key. Is the associated passphrase correct?
  • Failed to parse the given key information.
  • Unable to login to remote host with supplied credential sets.

Continue reading →

PHDays 10: U.S. Sanctions, My Talk on Vulristics, Other Great Talks Related to VM

PHDays 10: U.S. Sanctions, My Talk on Vulristics, Other Great Talks Related to VM. Today I will talk about the Positive Hack Days conference, which took place on May 20 and May 21 in Moscow. I can say that this was and remains the main event for Information Security Practitioners in Russia.

First of all, I have to say a few words about the sanctions. The organizer of the event, Positive Technologies, is under the sanctions of the US Treasury Department since April 2021 among the “COMPANIES IN THE TECHNOLOGY SECTOR SUPPORTING RUSSIAN INTELLIGENCE SERVICES”. In a press release, the Treasury Department wrote that Positive Technologies hosts large-scale conventions that are used as recruiting events for russian special services. Well, I don’t know exactly what they mean. Maybe they mean PHDays or maybe not. But to say this about PHDays is like saying that any major international conference, Black Hat or RSA, is a recruiting event. This is ridiculous. In my humble opinion, these are some dirty political games. It is sad that reputable information security companies and security researchers are suffering from this.

Now let’s talk about my speech at PHDays 10. This year I had the opportunity to talk for an hour about my pet project – Vulristics. This project can help you prioritize known vulnerabilities. Anything that has a CVE id. There is a full video of my speech. I have uploaded this to my YouTube channel.

Russian version.

And a version that was dubbed into English.

So, if you’re interested, I recommend watching the full video. Here I will simply repeat the main points.

Continue reading →