Tag Archives: Metasploit

September Linux Patch Wednesday

September Linux Patch Wednesday

September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.
🗒 Full Vulristics report

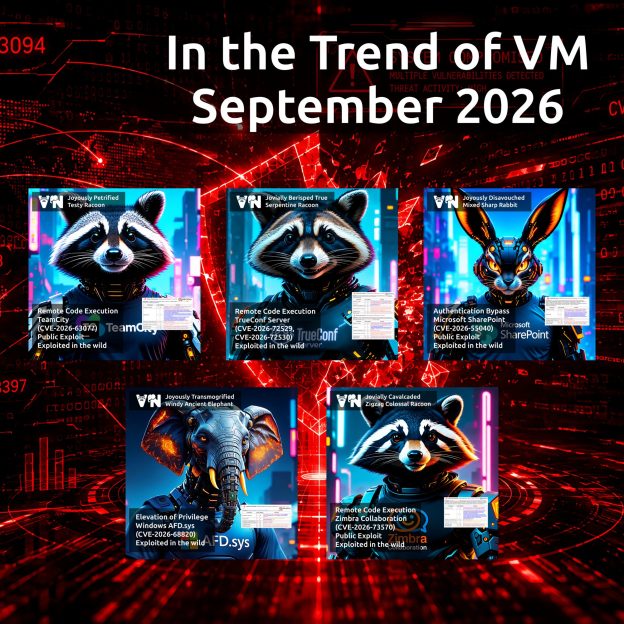
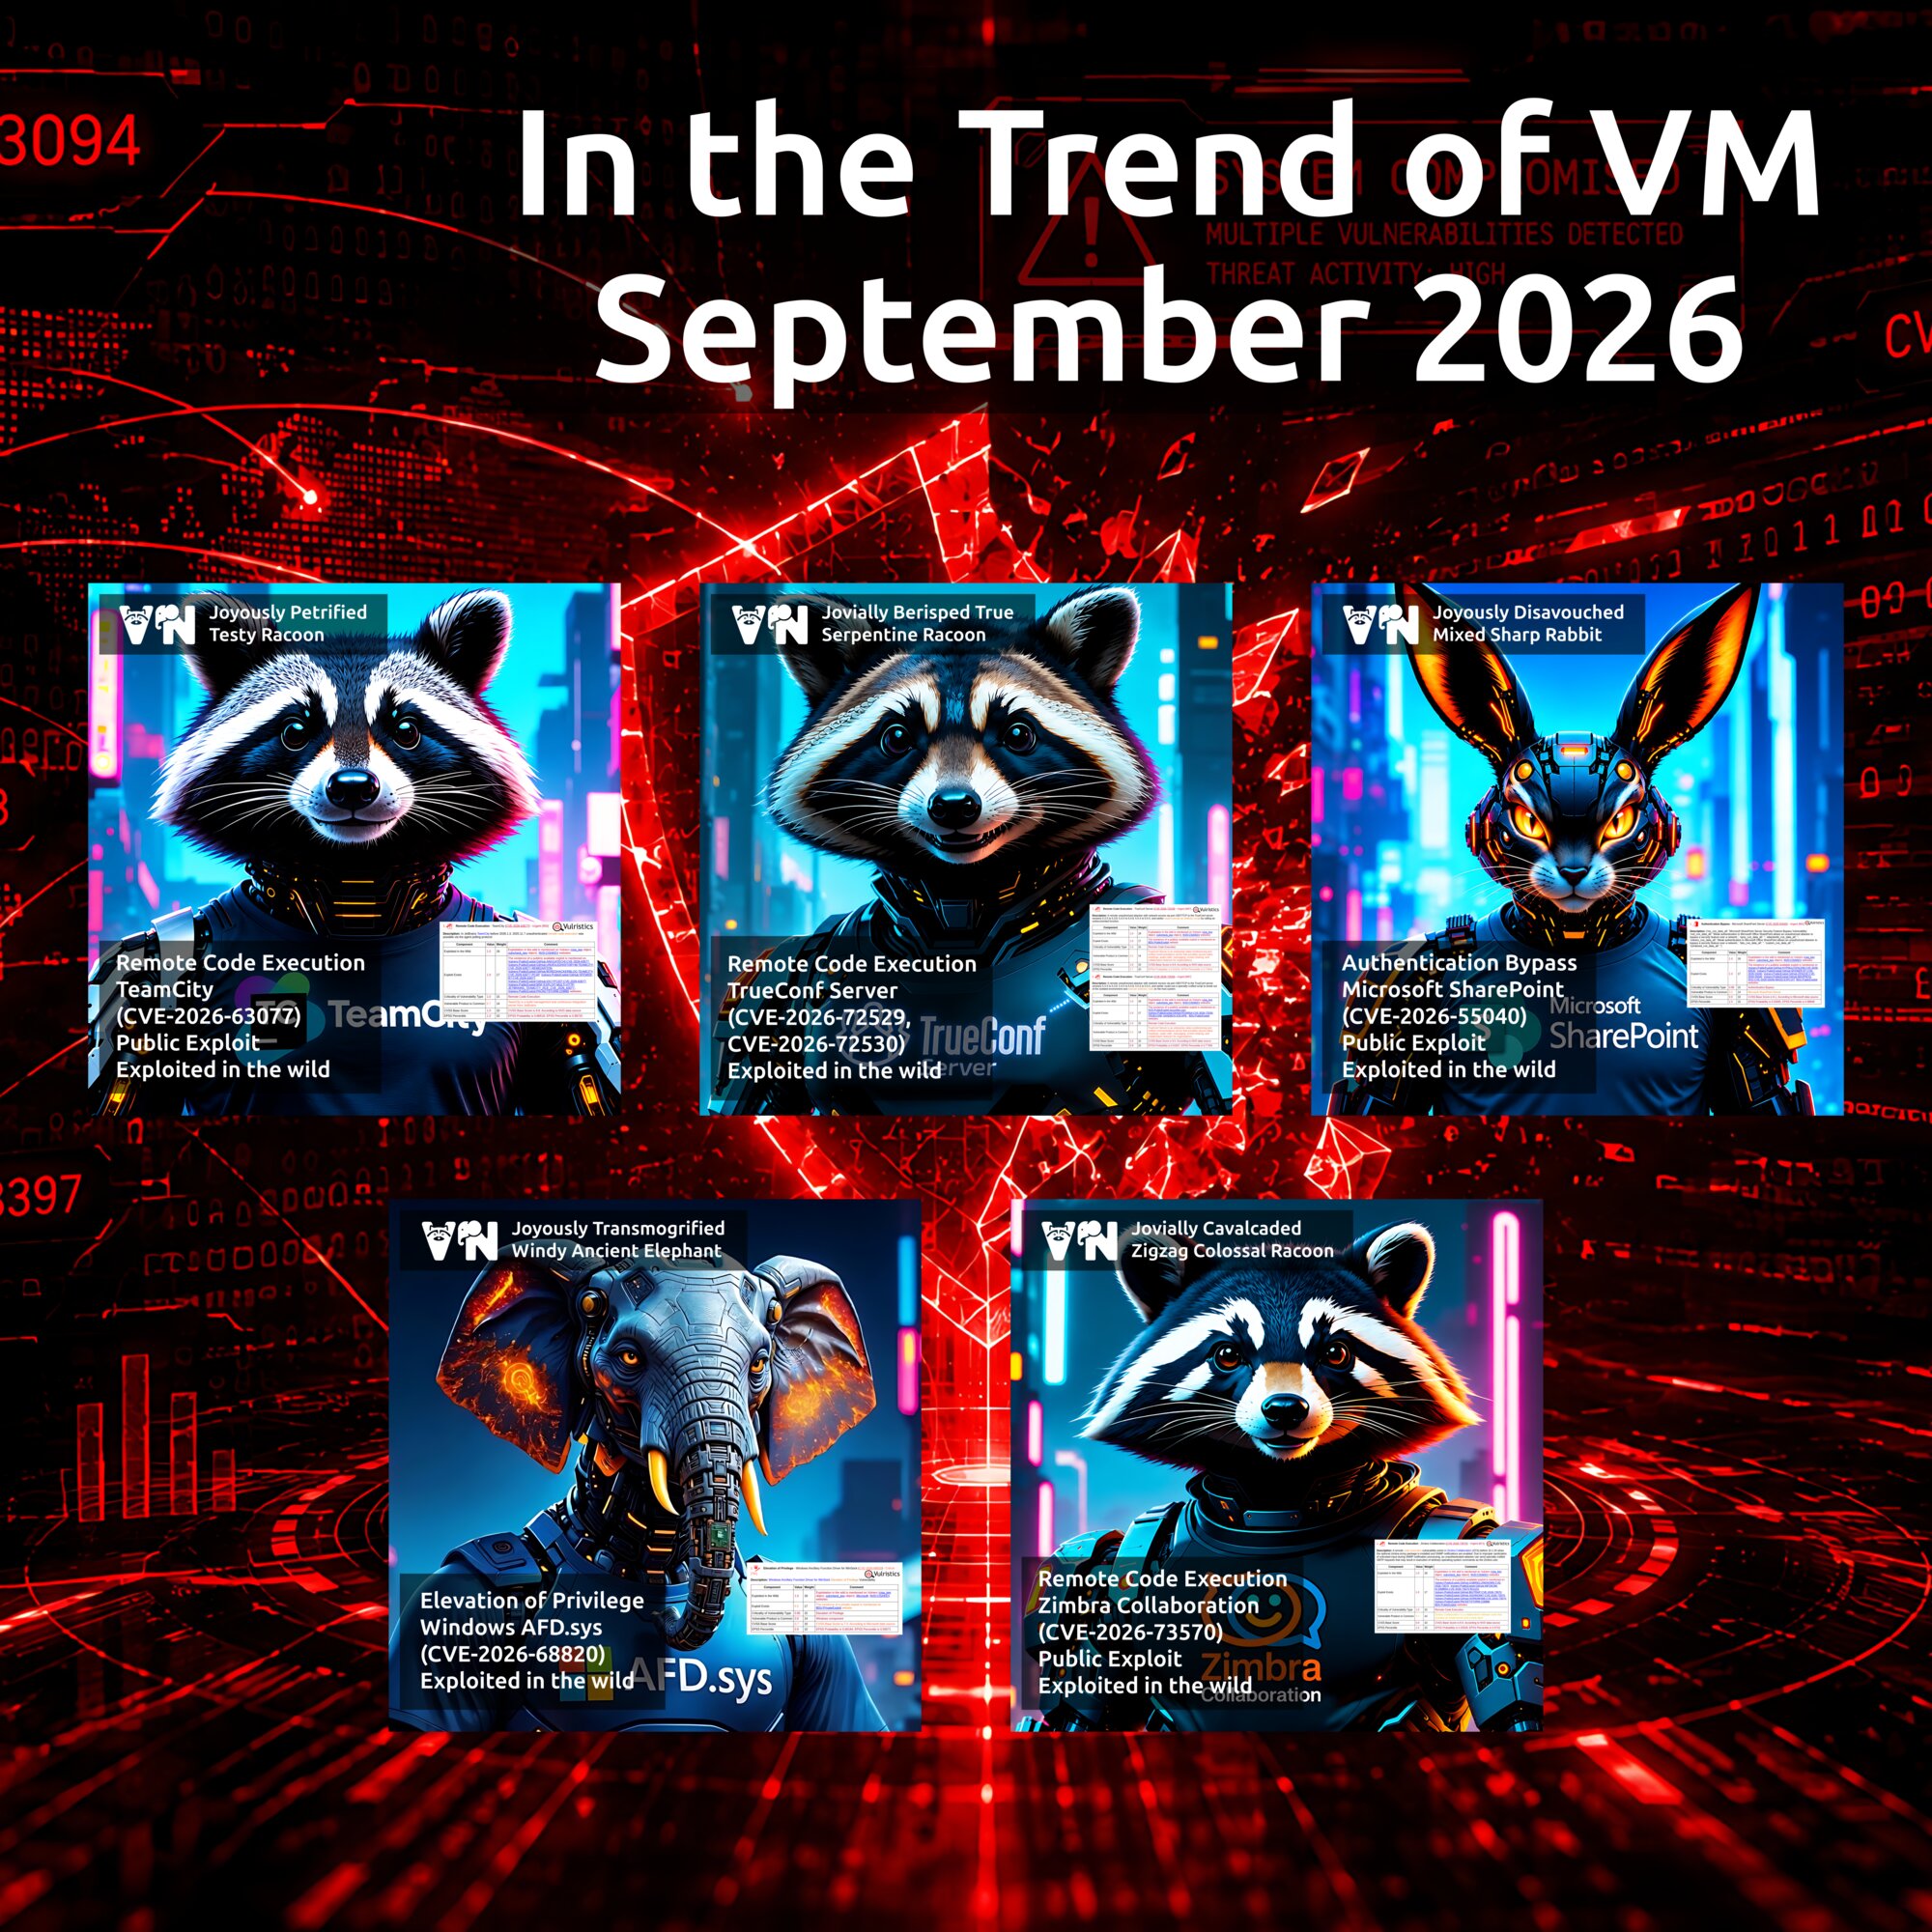
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September In the Trend of VM (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

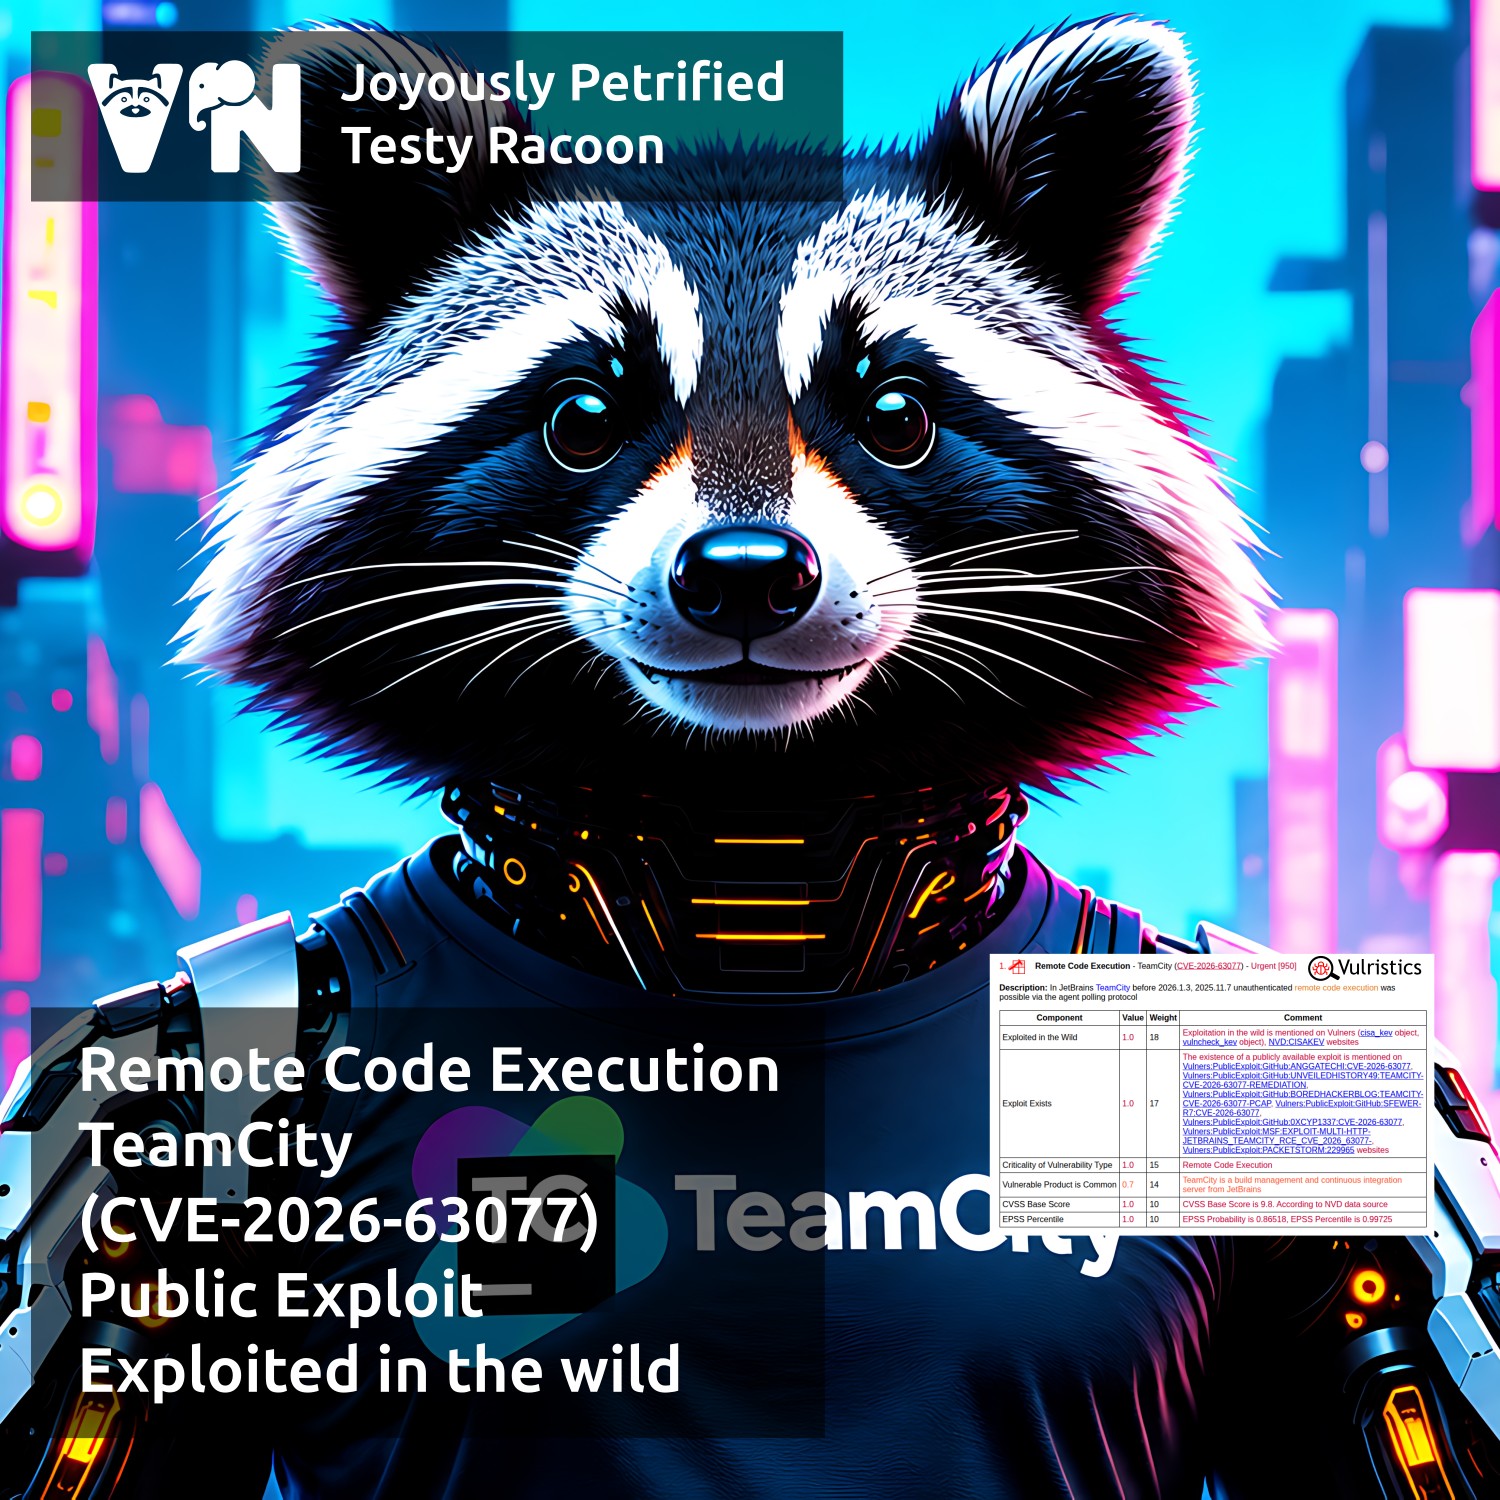
🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.

🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.

🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.

🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability. TeamCity is a proprietary solution developed by JetBrains for automating software build, testing, and deployment processes. TeamCity uses a central server to coordinate builds and separate build agents to execute them. An agent can communicate with the server through the agent polling protocol: it registers with the server, requests the next command, and reports whether the command succeeded or failed. The vulnerability allows an unauthenticated remote attacker with HTTP(S) access to a TeamCity On-Premises server to execute arbitrary operating system commands with the privileges of the TeamCity Server process through the agent polling protocol. The vulnerability is caused by insecure deserialization of XML data (CWE-502). Depending on the privileges of the TeamCity Server process, successful exploitation may allow an attacker to access TeamCity data, configurations, and stored credentials, modify the server state, and potentially compromise the integrity of build artifacts and downstream CI/CD pipelines.

⚙️ A notice about this critical vulnerability was published on the JetBrains blog on July 27. The vulnerability affects all versions of TeamCity On-Premises. To remediate the vulnerability, users should upgrade to version 2025.11.7 or 2026.1.3. As a compensating measure, a security patch plugin can be installed on TeamCity 2017.1 and later to prevent exploitation of the vulnerability. For TeamCity 2017.1-2018.1, the server must be restarted after installing the plugin. Starting with TeamCity 2018.2, the plugin can be enabled without restarting the TeamCity server. As a longer-term security measure, the vendor recommends limiting network access to TeamCity servers to trusted networks, including restricting access to the TeamCity login page and REST API. It is also recommended to run the TeamCity server under an operating system account with the minimum privileges required for normal operation. TeamCity servers should be deployed on dedicated hosts separate from build agents, as described in the documentation.

👾 The vulnerability was added to the CISA KEV on August 5. On August 7, JetBrains published a report confirming exploitation of the vulnerability in the wild. The vendor recommended checking TeamCity logs for com.thoughtworks.xstream.converters.ConversionException messages, which may indicate successful exploitation of the vulnerability and warrant further investigation. After updating the server or installing the security patch plugin, logs can be checked for com.thoughtworks.xstream.security.ForbiddenClassException messages, which indicate that an exploitation attempt was blocked. Unauthorized build agents, particularly those with names beginning with scan, may also indicate exploitation attempts.

🛠 A technical analysis of the vulnerability and a link to a public exploit were published on the Rapid7 blog on August 7. A Metasploit module for simplified exploitation of the vulnerability has been available since August 28.

🌐 According to JetBrains, TeamCity is used by more than 30,000 organizations worldwide across government, technology, financial services, healthcare, and other sectors, including some Fortune 500 companies. As of July 30, Censys had detected approximately 4,500 TeamCity installations exposed to the Internet. Of these, 450 were running versions 2025.11.7 or 2026.1.3. Most of the remaining installations were running earlier versions or did not disclose version information.

June Linux Patch Wednesday

June Linux Patch Wednesday

June Linux Patch Wednesday. A total of 1,888 vulnerabilities (324 in the Linux kernel, and a whopping 728 in Chromium ❗️). For comparison, there were 1,638 vulnerabilities in May. The increase isn't as dramatic as it was from April to May, but it's still a new record. One of the vulnerabilities has been flagged as actively exploited in the wild:

🔻 RCE - Chromium (CVE-2026-11645). Chromium is the open-source web browser project that serves as the foundation for many modern browsers, including Google Chrome, Microsoft Edge, Brave, Opera, and Vivaldi. A publicly available Metasploit module exploits a vulnerability in the web browser's V8 JavaScript engine. The vulnerability is triggered by a specific code pattern that causes type confusion between internal V8 objects, resulting in out-of-bounds memory access. Successful exploitation may lead to remote code execution in the context of the browser process.

There are also 109 vulnerabilities with public exploits or evidence that exploits exist, although there are no signs of active exploitation in real-world attacks yet. Among them, the following stand out:

🔸 EoP - Linux Kernel "CIFSwitch" (CVE-2026-46243). This vulnerability could allow attackers to forge CIFS authentication key descriptions, abuse the kernel's key request mechanism, and gain root privileges.

🔸 EoP - Linux Kernel "PinTheft" (CVE-2026-43494). On a successfully exploited configuration, the chain completes and hands off to the discovered SUID binary with an overwritten first page - yielding a root shell if the race and kernel state align.

🔸 RCE - Apache ActiveMQ (CVE-2026-42588). ActiveMQ is an open-source message broker written in Java. Exploitation of this vulnerability requires valid credentials for the ActiveMQ Web Console. However, the default credentials are admin/admin.

🔸 InfDisc - Squid "Squidbleed" (CVE-2026-47729). Squid is an open-source caching proxy server. The vulnerability causes Squid's FTP parser to read beyond the boundary of a memory buffer, into a region that may contain a previous user's uncleared HTTP request data.

🔸 AuthBypass - Nextcloud (CVE-2026-45156). Nextcloud is an open source content collaboration platform. A missing signature verification in User OIDC allowed a malicious ID4me authority to identify as any user.

🔸 XSS - Nextcloud (CVE-2025-59788). A vulnerability in a reachable files_pdfviewer example directory in Nextcloud allows attackers to execute arbitrary JavaScript in the context of a user's browser via a crafted PDF file to viewer.html.

🔸 XSS - Roundcube (CVE-2026-48849). Roundcube is a free, open-source webmail application. An unsanitized subject field in the draft restored value could lead to stored XSS/HTML/CSS injection on shared mailboxes.

🔸 DoS - ImageMagick (CVE-2026-46522). ImageMagick is an open-source image processing tool used to create, edit, and convert images. Due to a missing check in the MIFF decoder, a crafted file could cause an infinite loop resulting in CPU exhaustion.

🗒 Full Vulristics report

Last Week’s Security news: PrintNightmare patches and Metasploit, Kaseya CVEs, Morgan Stanley Accellion FTA, Cisco BPA and WSA, Philips Vue PACS, CISA RVAs, Lazarus job offers

Last Week’s Security news: PrintNightmare patches and Metasploit, Kaseya CVEs, Morgan Stanley Accellion FTA, Cisco BPA and WSA, Philips Vue PACS, CISA RVAs, Lazarus job offers. Hello guys! The third episode of Last Week’s Security news, July 5 – July 11. There was a lot of news last week. Most of them was again about PrintNightmare and Kaseya.

The updates for PrintNightmare (CVE-2021-34527) were finally released mid-week. It became possible not only to disable the service, but also to update the hosts. This is especially important for desktops that need to print something. But the problem is that these patches can be bypassed. “If you have a system where PointAndPrint NoWarningNoElevationOnInstall = 1, then Microsoft’s patch for #PrintNightmare CVE-2021-34527 does nothing to prevent either LPE or RCE”. Microsoft has updated their security update guide after that: “if you set this reg key to = 1 then the system is vulnerable by design”. It seems that solving this problem requires hardening and registry monitoring.

Continue reading →

Last Week’s Security news: PrintNightmare, Kaseya, Intune, Metasploit Docker escape

Last Week’s Security news: PrintNightmare, Kaseya, Intune, Metasploit Docker escape. Hello guys! The second episode of Last Week’s Security news from June 28 to July 4.

The most interesting vulnerability of the last week is of course Microsoft Print Spooler “PrintNightmare”. By sending an RpcAddPrinterDriverEx() RPC request, for example over SMB, a remote, authenticated attacker may be able to execute arbitrary code with SYSTEM privileges on a vulnerable Windows system. And there is a public PoC exploit for this vulnerability published by the Chinese security firm Sangfor. And there is some strange story. It turns out that Sangfor published an exploit for the 0day vulnerability. But they thought this vulnerability (CVE-2021-1675) had already been patched as part of the June Micorosft Patch Tuesday. And then it turns out that this is a bug in the Microsoft patch. But Microsoft wrote that this is a different, new vulnerability CVE-2021-34527 and so there were no problems with the previous patch. In any case, a patch for this vulnerability has not yet been released and Microsoft is suggesting two Workarounds. Option 1 – Disable the Print Spooler service, Option 2 – Disable inbound remote printing through Group Policy. Do this first for Domain Controllers and other critical Windows servers. All versions of Windows contain the vulnerable code and are susceptible to exploitation. Also note that the new vulnerability has a flag Exploitation Detected on the MS site.

Continue reading →

Vulristics: Microsoft Patch Tuesdays Q1 2021

Vulristics: Microsoft Patch Tuesdays Q1 2021. Hello everyone! It has been 3 months since my last review of Microsoft vulnerabilities for Q4 2020. In this episode I want to review the Microsoft vulnerabilities for the first quarter of 2021. There will be 4 parts: January, February, March and the vulnerabilities that were released between the Patch Tuesdays.

I will be using the reports that I created with my Vulristics tool. This time I’ll try to make the episodes shorter. I will describe only the most critical vulnerabilities. Links to the full reports are at the bottom of the blog post.

Continue reading →