Tag Archives: malware

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability. The Ancillary Function Driver (AFD) is a Windows component that supports Windows Sockets applications and is contained in the afd.sys file. The afd.sys driver runs in kernel mode and manages the Winsock TCP/IP communications protocol. This vulnerability is from the August Microsoft Patch Tuesday. Use-after-free (CWE-416) in the Windows Ancillary Function Driver for WinSock allows an authorized attacker to elevate privileges locally to SYSTEM level. Successful exploitation requires an attacker to win the race condition. As a result, the attacker can gain full control over the Windows host, execute commands with SYSTEM-level privileges, disable security protections, install malware, and access other users' data.

👾 The vulnerability was already being exploited in the wild when it was disclosed as part of Microsoft's August Patch Tuesday on August 11. That same day, it was added to the CISA KEV catalog. Notably, Microsoft listed the Exploit Code Maturity in the CVSS as "Unproven". 🤷‍♂️ Microsoft credited researchers from Check Point for reporting the vulnerability.

Details on how the vulnerability was exploited in attacks were published in a Check Point blog post on August 11. The vulnerability was exploited as part of the "Operation Dream Job" campaign, which targeted organizations worldwide, with a particular focus on the defense sector in Europe and India. The campaign is linked to the Lazarus Group. The campaign begins with targeted phishing messages offering victims attractive job opportunities at well-known companies in the defense, aerospace, and aviation industries. Victims are lured into opening a PDF decoy masquerading as a Lockheed Martin job description. This triggers the execution of a lightweight in-memory loader - MISTPEN. The loader uses the Microsoft Graph API to access OneDrive, from which it retrieves additional modules and runs them in memory. During the initial stages of the infection, the attacker deploys several reconnaissance modules that gather information about the system and running processes. Once the target is deemed of interest, MISTPEN retrieves an additional persistence module, which installs the malware on disk and ensures that MISTPEN is automatically launched after a system reboot. After establishing persistence, MISTPEN loads an in-memory module designed to exploit the CVE-2026-68820 vulnerability. Check Point researchers believe that this vulnerability was already being exploited in the "Operation Dream Job" campaign in early July 2026. Successful exploitation enables the malware to launch FudModule, a Lazarus kernel-level rootkit, with SYSTEM privileges. The final backdoor delivered by MISTPEN - ForestTiger - provides attackers with remote access to the compromised system, allowing them to execute commands, collect host information, and download additional malicious components.

🛠 No public exploits have been observed so far. Some people are offering exploits for sale, but they don't look reliable.

⚙️ Security updates are available for Windows 10, Windows 11, and Windows Server 2019.
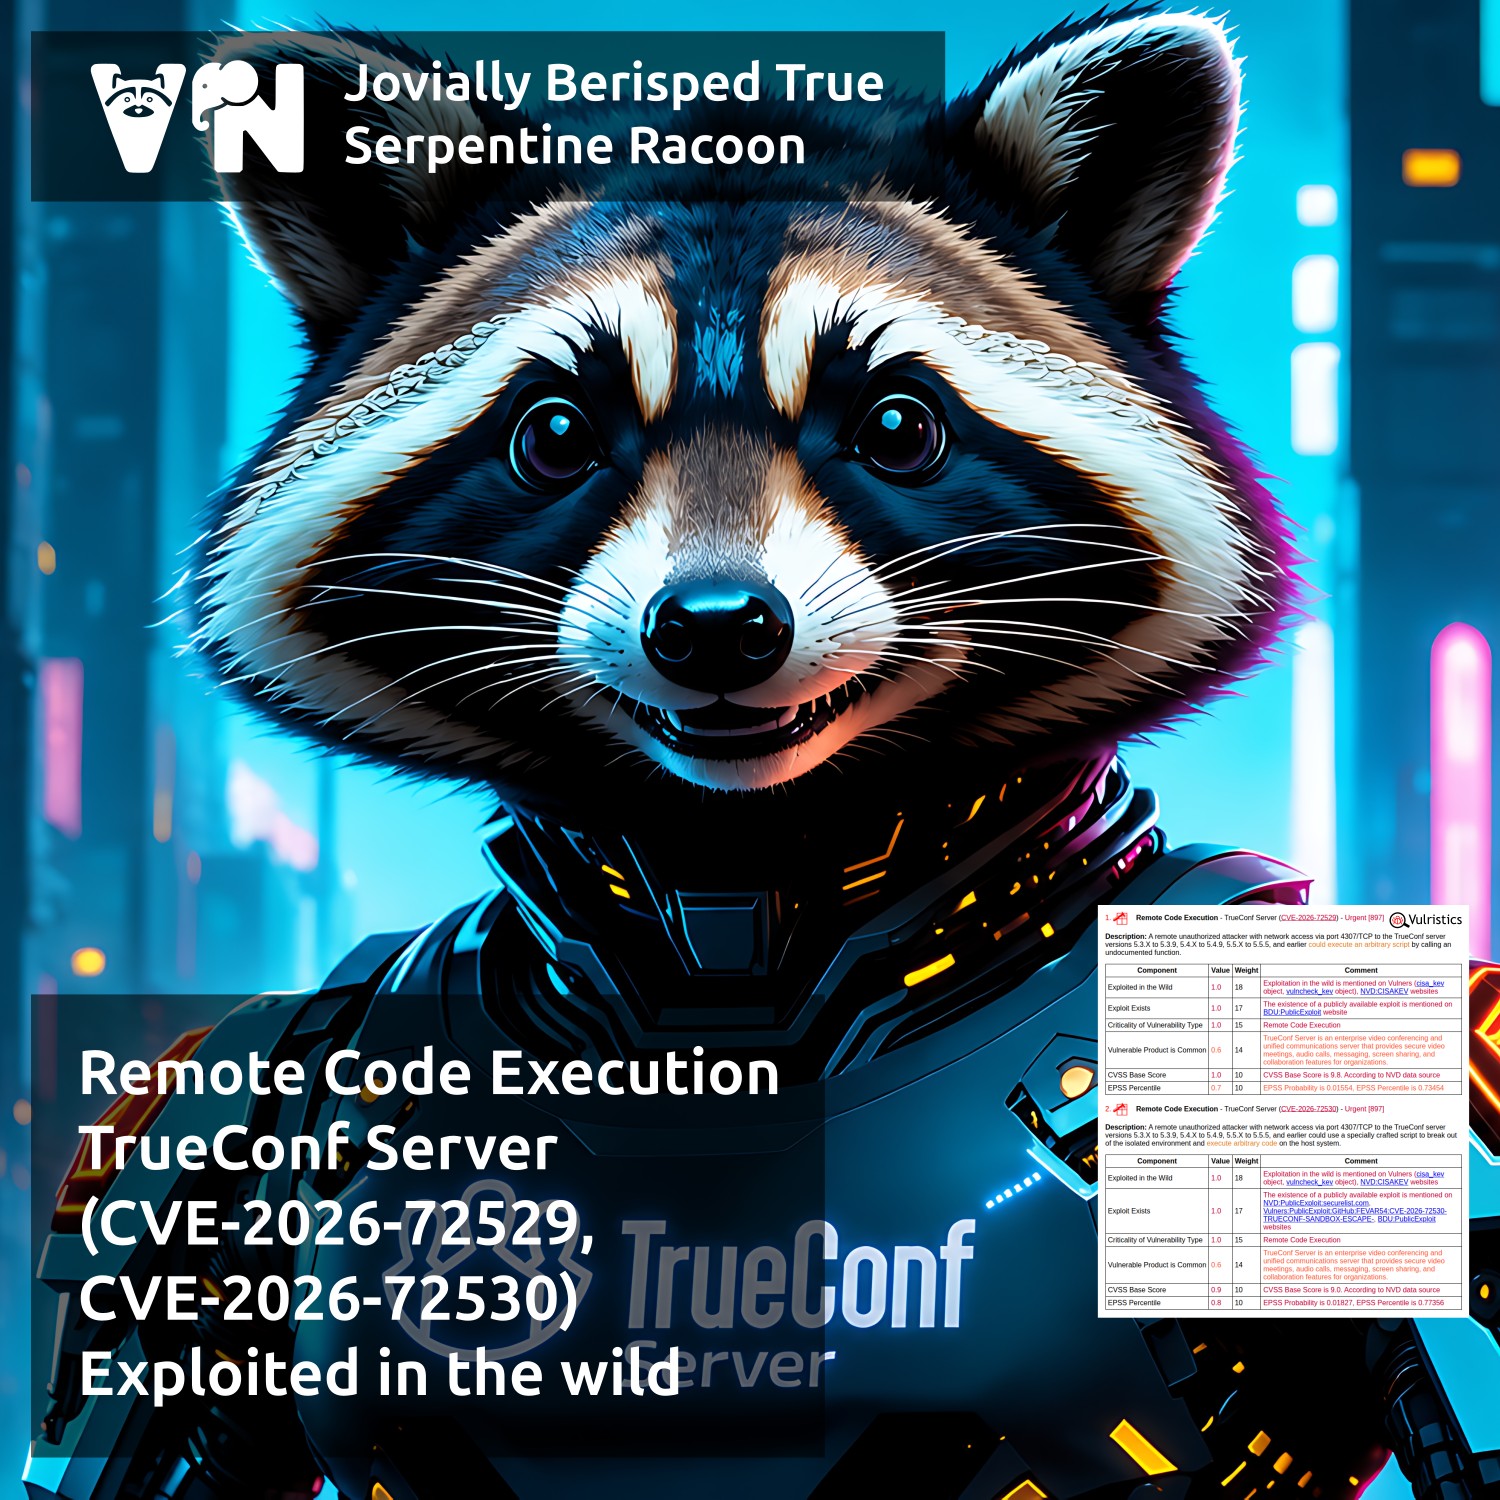
About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.

Attackers are distributing malware on social networks under the guise of the regreSSHion exploit (CVE-2024-6387)

Attackers are distributing malware on social networks under the guise of the regreSSHion exploit (CVE-2024-6387)

Attackers are distributing malware on social networks under the guise of the regreSSHion exploit (CVE-2024-6387). According to Kaspersky Lab experts, this is an attack on cybersecurity specialists. The attackers invite victims to examine an archive that supposedly contains a functional regreSSHion exploit, a list of IP addresses, and some payload.

🔻 The source code resembles a slightly edited version of a non-functional proof-of-concept exploit for this vulnerability that was already public.

🔻 One of the Python scripts simulates the exploitation of the vulnerability on IP addresses from the list. But in reality, it launches malware that achieves persistence in the system and downloads additional payload. The malware modifies /etc/cron.hourly and the operation of the ls command.

If you are examining someone else's code, do so in a securely isolated environment and be aware that you may be attacked this way. 😉

На русском

Vulnerability Life Cycle and Vulnerability Disclosures

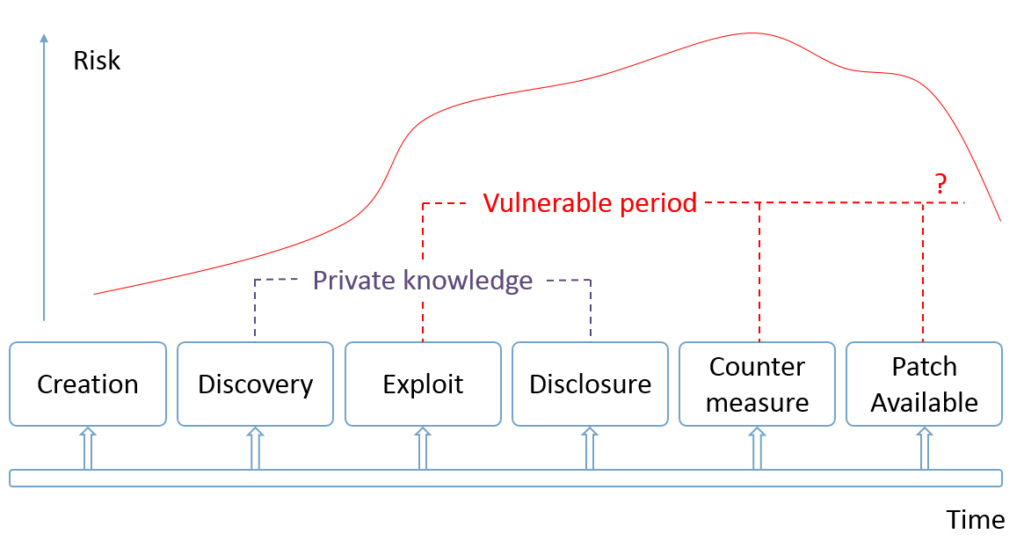
Vulnerability Life Cycle and Vulnerability Disclosures. Vulnerability Life Cycle diagram shows possible states of the vulnerability. In a previous post I suggested to treat vulnerabilities as bugs. Every known vulnerability, as same as every bug, was implemented by some software developer at some moment of time and was fixed at some moment of time later. What happens between this two events?

Vulnerability life-cycle

Right after the vulnerability was implemented in the code by some developer (creation) nobody knows about it. Well, of course, if it was done unintentionally. By the way, making backdoors look like an ordinary vulnerabilities it’s a smart way to do such things. 😉 But let’s say it WAS done unintentionally.

Time passed and some researcher found (discovery) this vulnerability and described it somehow. What’s next? It depends on who was that researcher.

Continue reading

Exploitability attributes of Nessus plugins: good, bad and Vulners

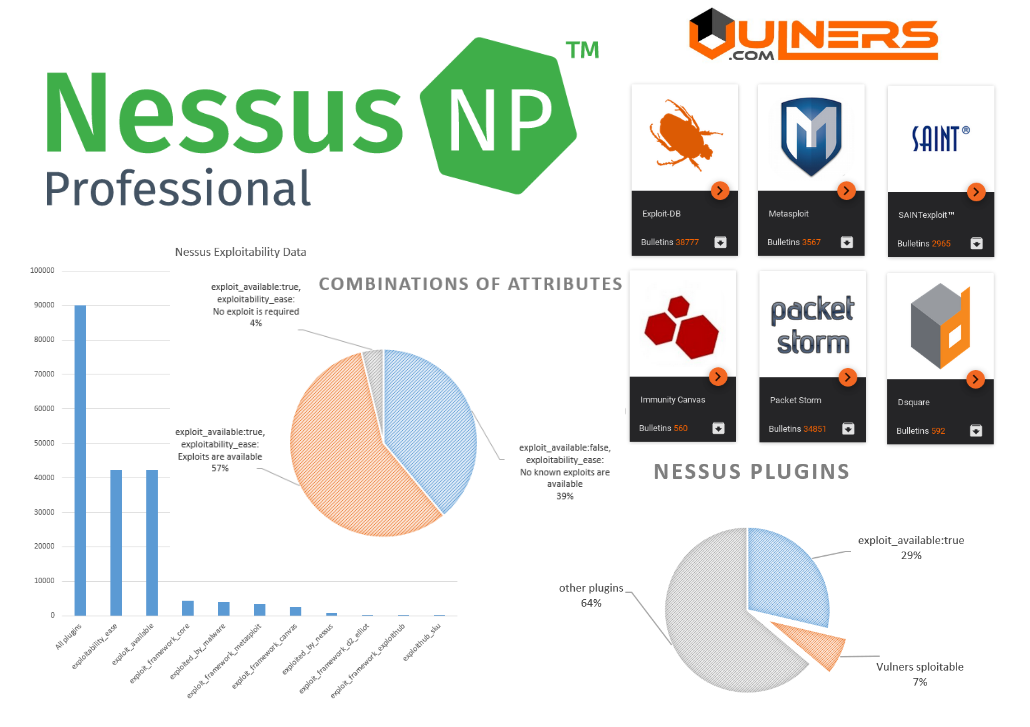
Exploitability attributes of Nessus plugins: good, bad and Vulners. Exploitability is one of the most important criteria for prioritizing vulnerabilities. Let’s see how good is the exploit-related data of Tenable Nessus NASL plugins and whether we can do it better.

Nessus exploitability

What are the attributes related to exploits? To understand this, I parsed all nasl plugins and got the following results.

Continue reading

Dealing with cybersquatting, typosquatting and phishing

Dealing with cybersquatting, typosquatting and phishing. It won’t be a secret to say that phishing remains one of the most effective attack vectors.

For example, your colleague receives by email a malicious web link that looks like a link to your corporate portal and opens it. If your Vulnerability and Patch Management programs are not good enough (see “WannaCry about Vulnerability Management“) and the software on his desktop has some critical and exploitable vulnerabilities in web browser, PDF reader, Microsoft Office, etc., you will probably get compromised host in your network.

This is also a pain for your customers. If someone will be sending messages on behalf of your organization, this can easily lead to fraud and costs in public image. And it will be even harder to detect. You will know about it only if they tell you. And if the attack was not massive, the probability of this is not very high.

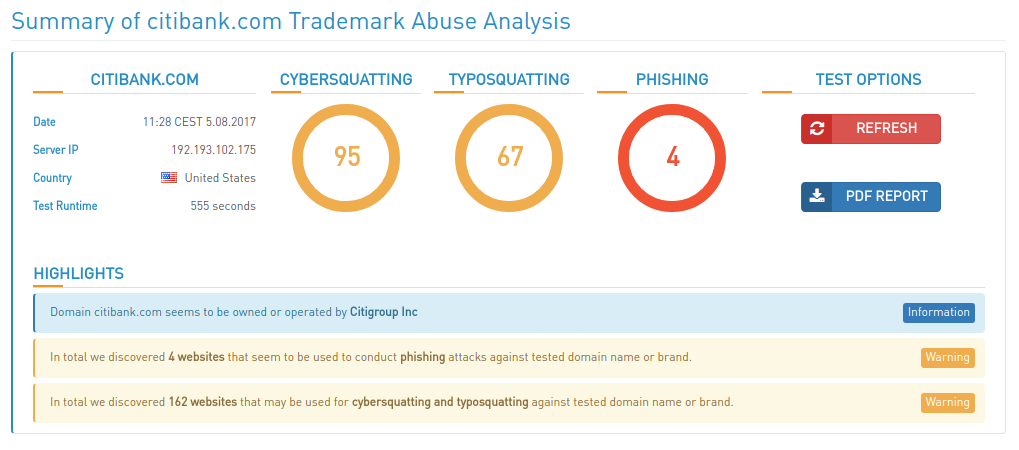
High-Tech Bridge Trademark Abuse Radar summary

What can we do about this?

  • We should definitely raise the awareness among co-workers and clients. They should know that such attacks may occur and carefully check the domain before any click. Especially if the letter seems suspicious.
  • On the other hand, we can also act proactively. Find which domains are similar enough to company brand and can be potentially used for phishing or other types of fraud. Then work with owners or registrars of such domains directly.

However, tracking down potentially malicious domains is not an easy task. Where should we take the lists of  all registered domains? What does “similar enough” really mean? Fortunately, there are services that greatly facilitate this task.

And today I would like to write you about a new free service by High-Tech Bridge – Trademark Abuse Radar. BTW, I already wrote earlier about their cool free service and API for SSL/TLS server testing, you can also check this out 😉

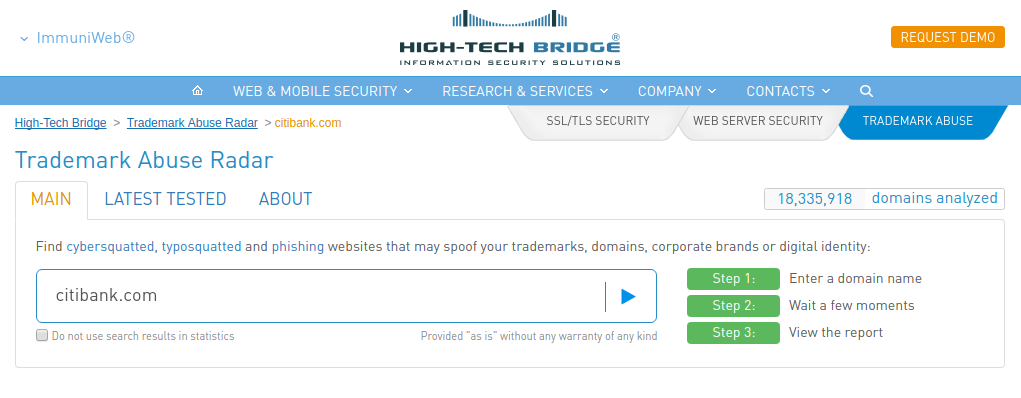
Everything is simple. Just enter the domain name you are interested in and in a few minutes you will receive a full report. No authorization for analysis is required, because the report is built on external and open data.

High-Tech Bridge Trademark Abuse Radar input

I chose the Citibank (citibank.com) as one of the most famous banking brand in the world. Let’s see what Trademark Abuse Radar will find.

Continue reading

Vulnerability Quadrants

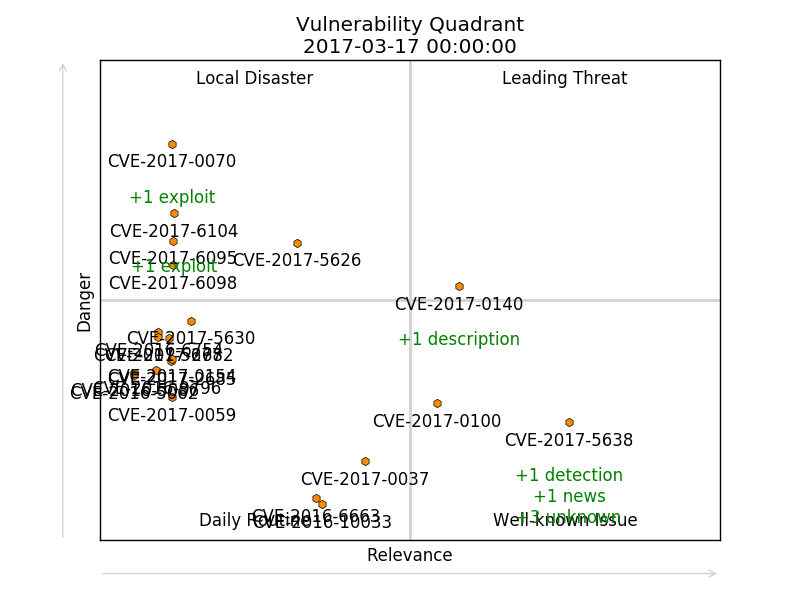
Vulnerability Quadrants. Hi everyone! Today I would like talk about software vulnerabilities. How to find really interesting vulnerabilities in the overall CVE flow. And how to do it automatically.

Vulnerability Quadrant

First of all, let’s talk why we may ever need to analyze software vulnerabilities? How people usually do their Vulnerability Management and Vulnerability Intelligence?

VM strategies

  • Some people have a Vulnerability scanner, scan infrastructure with it, patch founded vulnerabilities and think that this will be enough.
  • Some people pay attention to the vulnerabilities that are widely covered by media.
  • Some people use vulnerability databases and search for the most critical vulnerabilities by some criteria.

Each of these ways have some advantages and some disadvantages.

Continue reading