Tag Archives: exploit

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

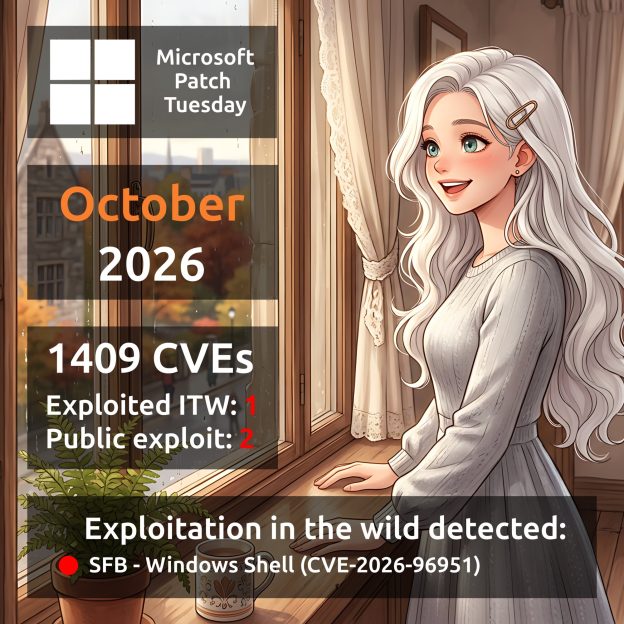
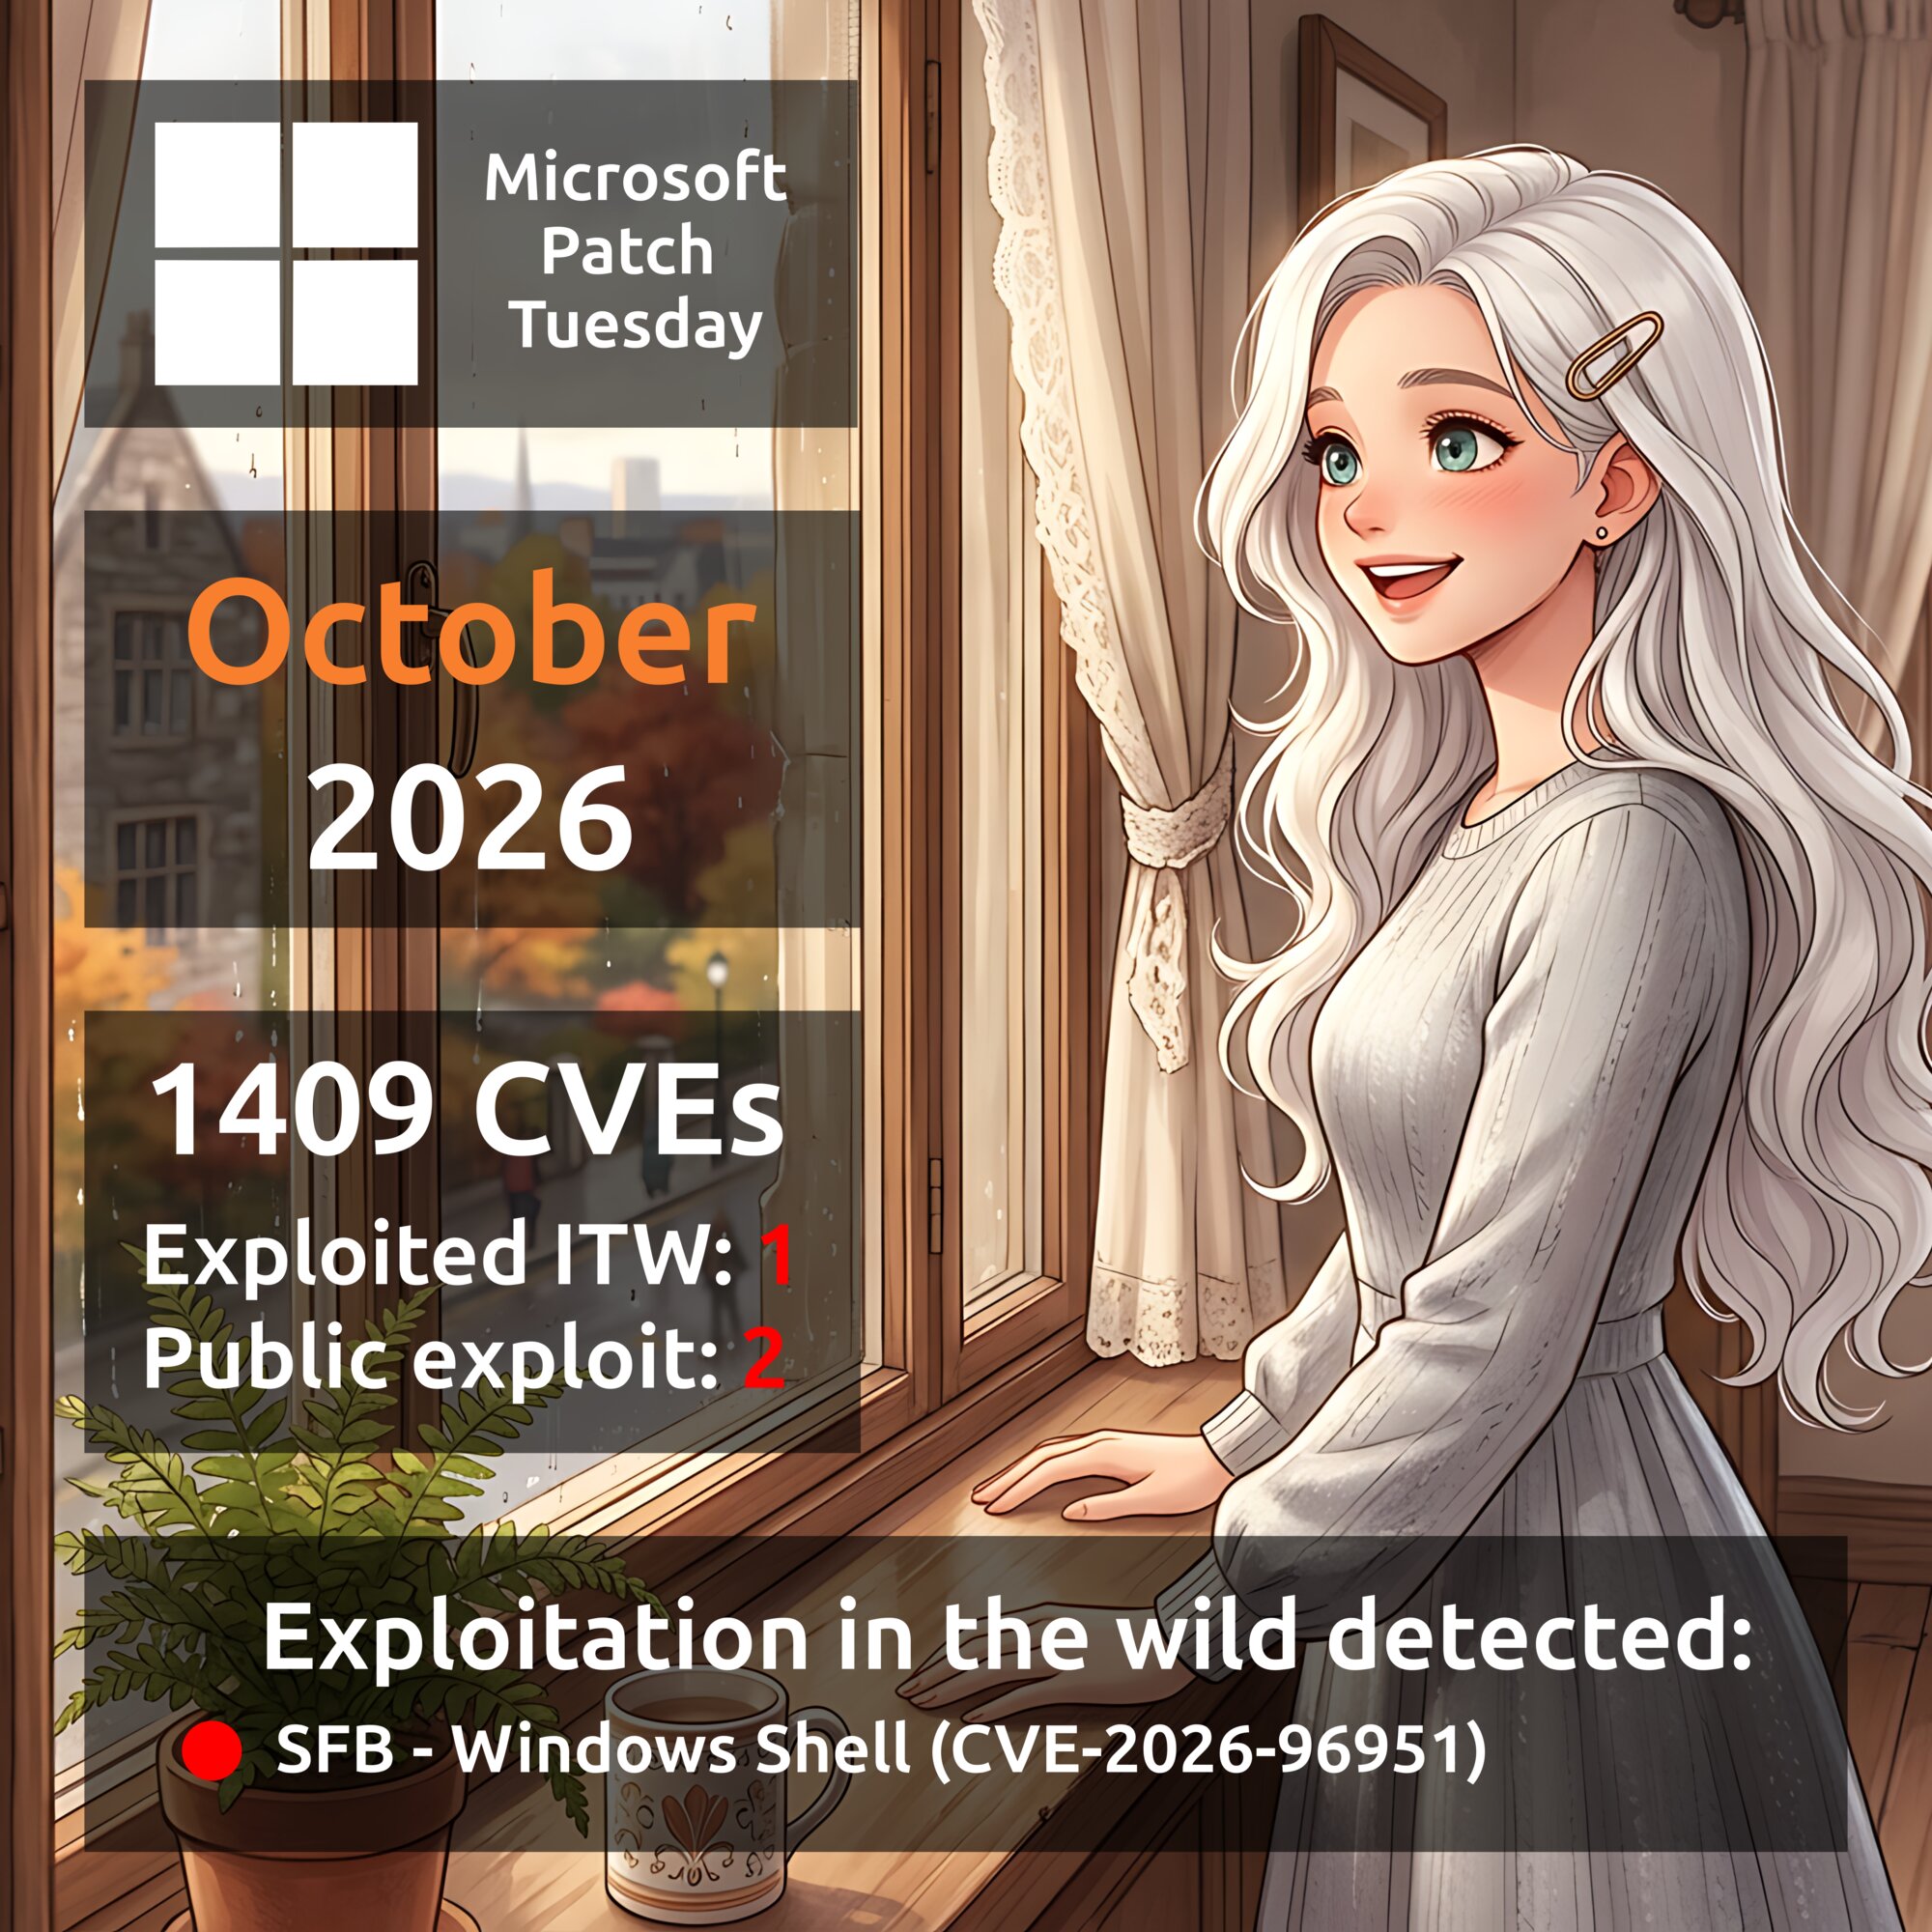
October Microsoft Patch Tuesday. A total of 1,409 vulnerabilities. For comparison, there were 973 in September, an increase of about 45%. 🙈 Thirteen products had fixes for 20 or more vulnerabilities: Microsoft Office Excel (68), Windows Kernel (46), Role: DNS Server (41), Windows Installer (38), Microsoft Office SharePoint (35), Windows Win32k (31), Windows NTFS (26), .NET (25), Microsoft Windows Search Component (23), Microsoft Office Word (22), Windows Error Reporting (21), Windows Broadcast DVR User Service (20), and Microsoft SQL Server (20). A total of 416 vulnerabilities were fixed in these products. That's 30% of all vulnerabilities. One vulnerability is flagged as exploited in the wild:

🔻 SFB - Windows Shell (CVE-2026-96951). The vulnerability allows an attacker to bypass Mark of the Web (MOTW), a Windows feature that marks files downloaded from the Internet. To exploit it, the attacker must trick the user into opening a malicious file or clicking a malicious link.

There are two vulnerabilities with public exploits:

🔸 RCE - Raw Image Extension (CVE-2026-21413). A heap-based buffer overflow in Windows Raw Image Extension allows an attacker to execute arbitrary code remotely using a specially crafted file. A technical write-up of the vulnerability, which NVD classifies as an exploit, was published on the Cisco Talos blog on April 7.

🔸 EoP - Windows Health and Optimized Experiences Service (CVE-2026-85884). Missing authentication for a critical function in Windows Health and Optimized Experiences Service allows a local attacker to gain SYSTEM privileges. A public exploit has been available on GitHub since October 13.

Other notable vulnerabilities include:

🔹 RCE - Microsoft Exchange (CVE-2026-70571). An unauthenticated attacker can send a specially crafted email to a vulnerable Exchange server and execute arbitrary code on the server. The attack requires an in-depth understanding of the target environment. No user interaction is required.

🔹 RCE - Microsoft Office Outlook (CVE-2026-70242, CVE-2026-97749, CVE-2026-97016, CVE-2026-88156, CVE-2026-70291). An attacker can execute arbitrary code on the victim's device by sending a specially crafted email. To exploit the vulnerability, the victim only needs to view the email in Outlook's reading pane without opening it or taking any further action.

🔹 RCE - Windows Domain Name Service (CVE-2026-96113). A heap-based buffer overflow in DNS Server allows an unauthorized attacker to execute code over a network.

🔹 SFB - .NET Framework (CVE-2026-108398). An authenticated attacker can place a specially crafted .NET assembly on an affected system and register it to be loaded by a protected process. This allows the attacker to bypass Windows Defender Application Control (WDAC) restrictions and run unauthorized code within the protected process. No user interaction is required.

🔹 Spoofing - Microsoft Exchange (CVE-2026-70279). An attacker can send a specially crafted link to a user and trick them into opening it. No authentication is required. If the user has administrator privileges, the attacker could act as that user and access or modify the organization's data.

🗒 Full Vulristics report
About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.

September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September In the Trend of VM (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.

🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.

🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.

🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability. TeamCity is a proprietary solution developed by JetBrains for automating software build, testing, and deployment processes. TeamCity uses a central server to coordinate builds and separate build agents to execute them. An agent can communicate with the server through the agent polling protocol: it registers with the server, requests the next command, and reports whether the command succeeded or failed. The vulnerability allows an unauthenticated remote attacker with HTTP(S) access to a TeamCity On-Premises server to execute arbitrary operating system commands with the privileges of the TeamCity Server process through the agent polling protocol. The vulnerability is caused by insecure deserialization of XML data (CWE-502). Depending on the privileges of the TeamCity Server process, successful exploitation may allow an attacker to access TeamCity data, configurations, and stored credentials, modify the server state, and potentially compromise the integrity of build artifacts and downstream CI/CD pipelines.

⚙️ A notice about this critical vulnerability was published on the JetBrains blog on July 27. The vulnerability affects all versions of TeamCity On-Premises. To remediate the vulnerability, users should upgrade to version 2025.11.7 or 2026.1.3. As a compensating measure, a security patch plugin can be installed on TeamCity 2017.1 and later to prevent exploitation of the vulnerability. For TeamCity 2017.1-2018.1, the server must be restarted after installing the plugin. Starting with TeamCity 2018.2, the plugin can be enabled without restarting the TeamCity server. As a longer-term security measure, the vendor recommends limiting network access to TeamCity servers to trusted networks, including restricting access to the TeamCity login page and REST API. It is also recommended to run the TeamCity server under an operating system account with the minimum privileges required for normal operation. TeamCity servers should be deployed on dedicated hosts separate from build agents, as described in the documentation.

👾 The vulnerability was added to the CISA KEV on August 5. On August 7, JetBrains published a report confirming exploitation of the vulnerability in the wild. The vendor recommended checking TeamCity logs for com.thoughtworks.xstream.converters.ConversionException messages, which may indicate successful exploitation of the vulnerability and warrant further investigation. After updating the server or installing the security patch plugin, logs can be checked for com.thoughtworks.xstream.security.ForbiddenClassException messages, which indicate that an exploitation attempt was blocked. Unauthorized build agents, particularly those with names beginning with scan, may also indicate exploitation attempts.

🛠 A technical analysis of the vulnerability and a link to a public exploit were published on the Rapid7 blog on August 7. A Metasploit module for simplified exploitation of the vulnerability has been available since August 28.

🌐 According to JetBrains, TeamCity is used by more than 30,000 organizations worldwide across government, technology, financial services, healthcare, and other sectors, including some Fortune 500 companies. As of July 30, Censys had detected approximately 4,500 TeamCity installations exposed to the Internet. Of these, 450 were running versions 2025.11.7 or 2026.1.3. Most of the remaining installations were running earlier versions or did not disclose version information.

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.

August Linux Patch Wednesday

August Linux Patch Wednesday

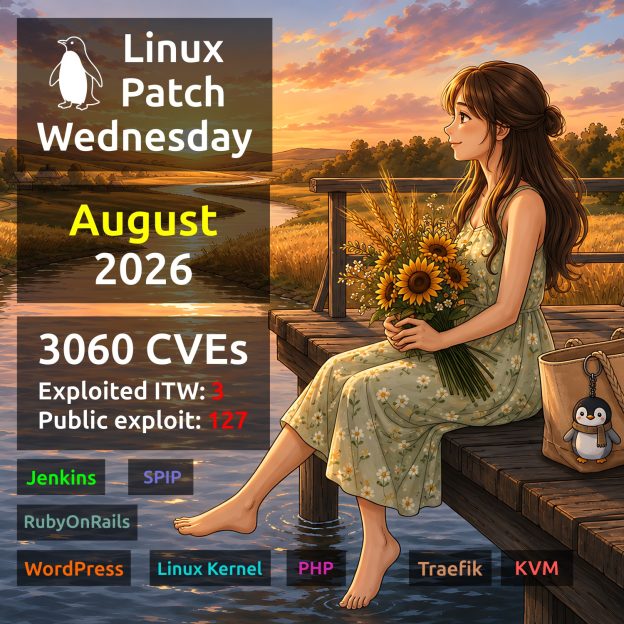
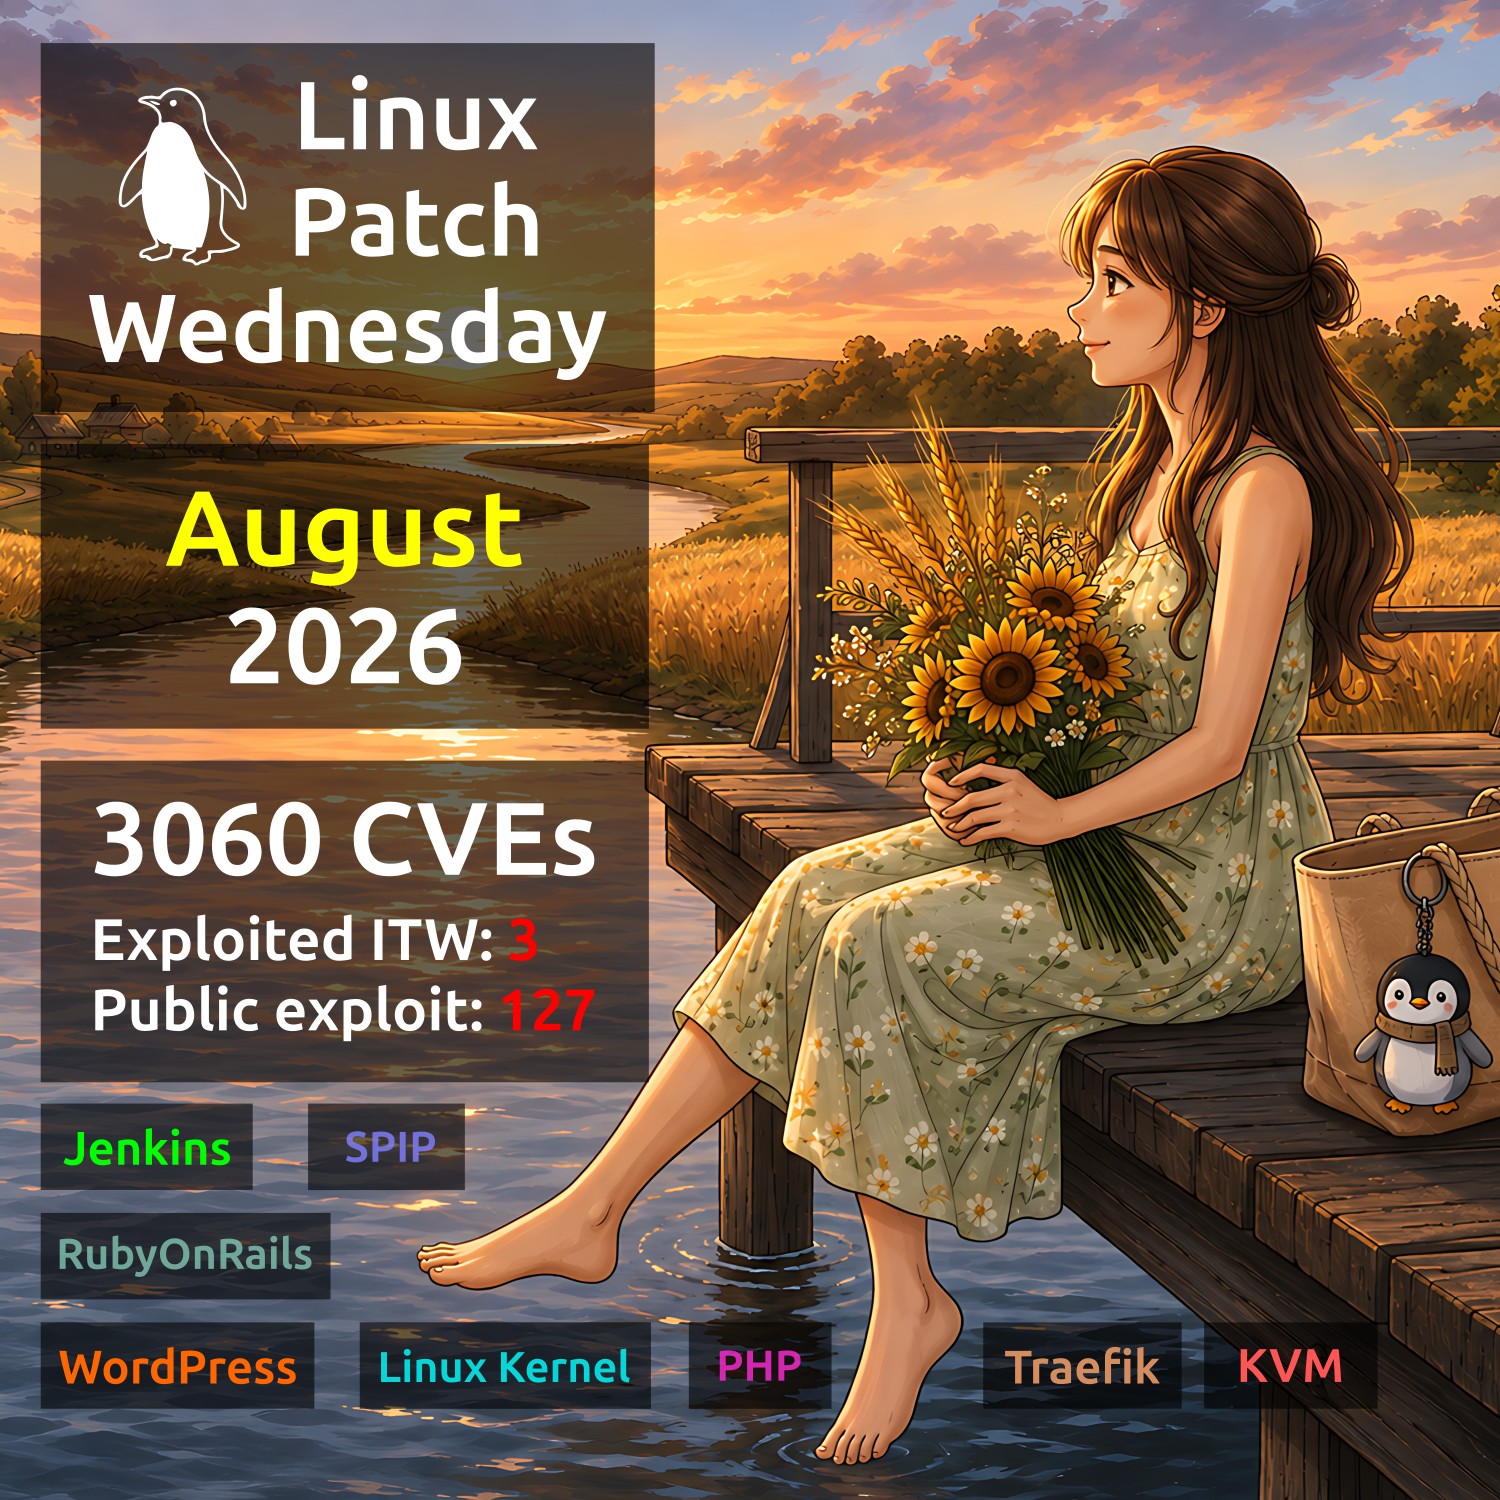
August Linux Patch Wednesday. A total of 3,060 vulnerabilities. For comparison, there were 2,017 in July. That's a 52% increase and another new record. This time, there are 1,354 vulnerabilities in the Linux Kernel and 447 in Chromium. For 3 vulnerabilities, there are signs of exploitation in the wild:

🔻 RCE - Jenkins (CVE-2026-53435). Jenkins is a development automation server used to build, test, and deploy software. The vulnerability allows a remote authenticated attacker to use the Script Console to execute arbitrary code and read files from the Jenkins controller. The vulnerability was added to the VulnCheck KEV on June 15 and fixed in RedOS on August 12.

🔻 CodeInj - WordPress (CVE-2026-60137). WordPress is a popular open-source CMS for creating websites and blogs. The vulnerability leads to a blind SQL injection in the WordPress core, allowing a remote unauthenticated attacker to read user accounts and password hashes from the WordPress database. Code execution is then possible by installing a malicious plugin. Multiple public exploits are available. The vulnerability was added to the CISA KEV catalog on July 21. A fix for the wordpress package in the Debian repository was released on July 23.

🔻 RCE - SPIP (CVE-2026-77647). SPIP is an open-source CMS for creating and collaboratively editing websites. The vulnerability allows an unauthenticated remote attacker to execute arbitrary PHP code. The vulnerability was added to the VulnCheck KEV on August 20. A fix for the spip package in the Debian repository was released on August 18.

Strictly speaking, the report contains one more vulnerability RCE - WinRAR (CVE-2025-8088) that is being exploited in the wild. The vulnerability was fixed in the clamav package in the Alt Linux repository. However, exploitation is only possible on Windows, so it is out of scope.

Another 127 vulnerabilities are not known to be exploited in the wild, but public exploits are available for them, or there are indications that such exploits exist. Notable examples include:

🔸 RCE - Action Pack "KindaRails2Shell" (CVE-2026-66066). Action Pack is a component of Ruby on Rails responsible for handling web requests, routing, and generating responses. An attacker can upload a specially crafted image to a vulnerable application and achieve remote code execution.

🔸 RCE - WordPress "XSS2Shell" (CVE-2026-64638). The attack chain allows an unauthenticated XSS on the login page to be escalated to arbitrary PHP code execution.

🔸 CodeInj - PHP (CVE-2026-17543). Improper escaping of backslashes in attacker-controlled parameters can lead to a trivial SQL injection in PHP.

🔸 EoP - Linux Kernel "Zapscape" (CVE-2026-64561). This KVM escape vulnerability allows an attacker to break out of a virtual machine in KVM/x86 environments and execute commands on the host with root privileges.

🔸 EoP - Linux Kernel "OVSwrap" (CVE-2026-64531), Linux Kernel "SCTPhantom" (CVE-2026-64564), Linux Kernel "Ubuntu PPPoL2TP" (CVE-2026-68398). These vulnerabilities allow a local attacker to escalate privileges to root.

🔸 AuthBypass - Traefik (CVE-2026-48020). Traefik is an HTTP reverse proxy and load balancer. A high-severity vulnerability in the StripPrefix middleware allows an unauthenticated attacker to bypass route-level authentication and authorization.

🗒 Full Vulristics report