Tag Archives: CISA

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

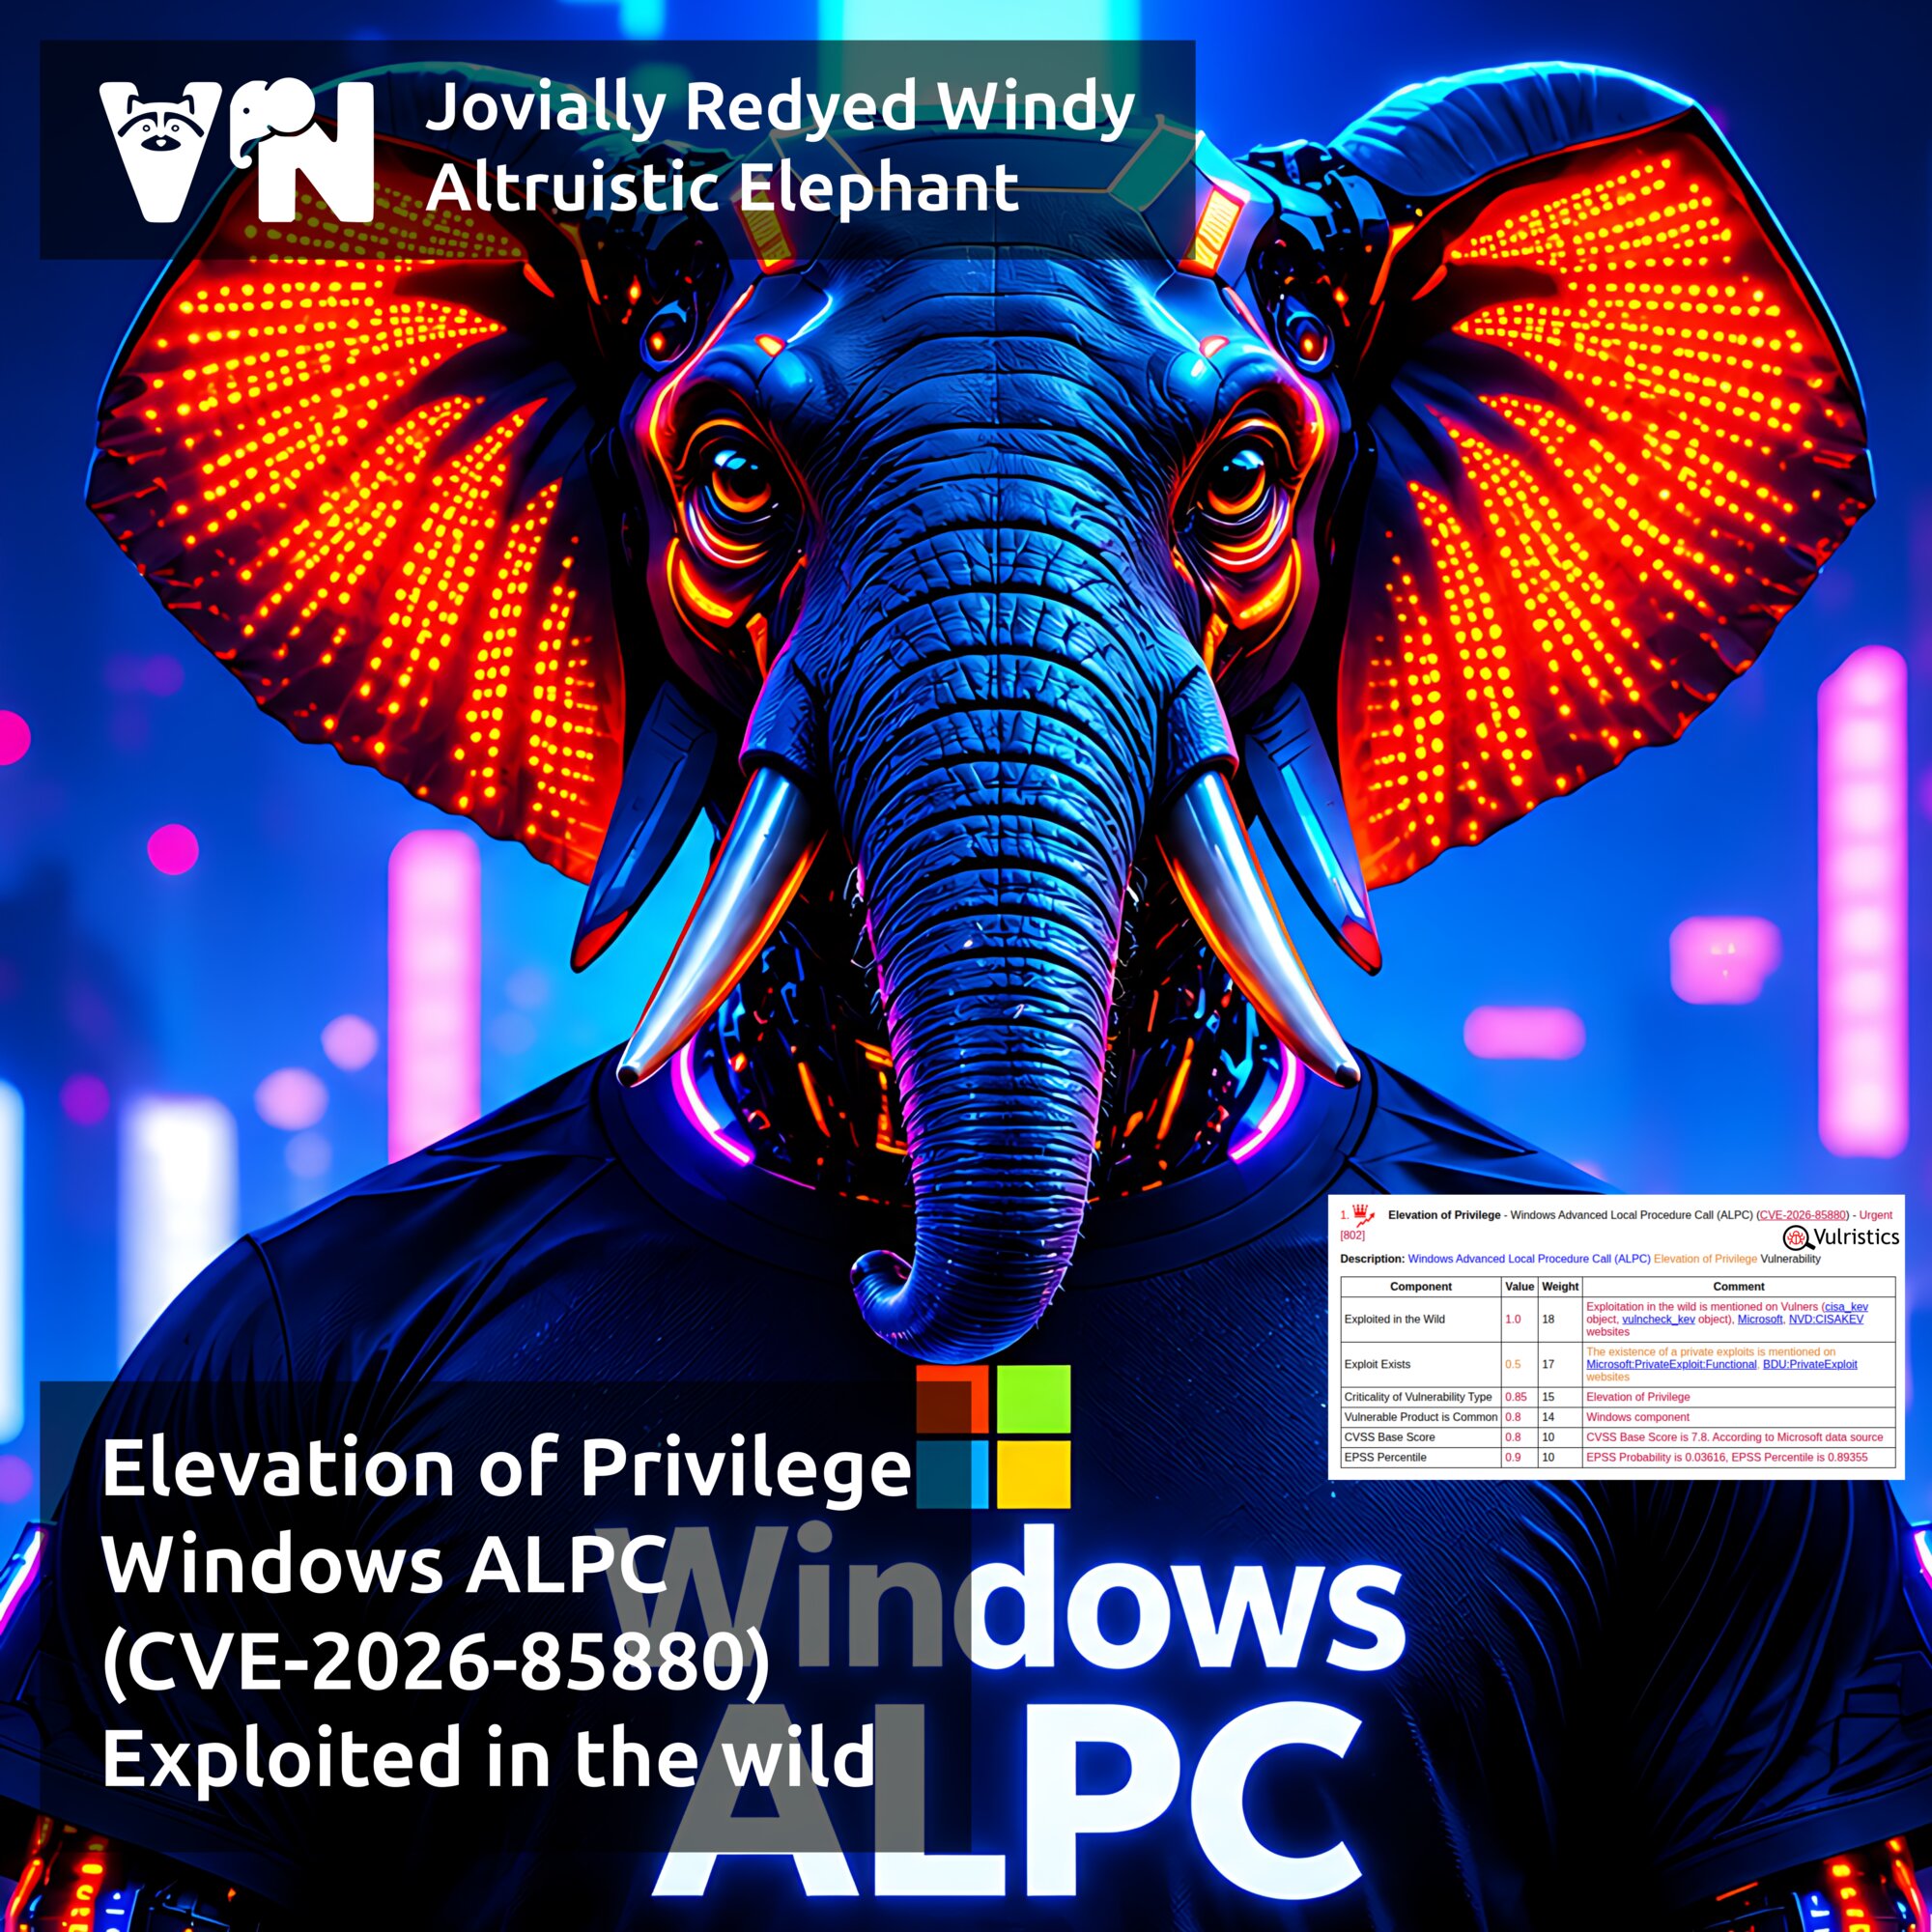
🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability

About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability. Check Point Quantum Security Gateway is an enterprise security gateway and next-generation firewall (NGFW) designed to protect network infrastructure from cyberattacks and unauthorized access. It provides network traffic filtering, intrusion prevention (IPS), application control, and secure VPN connectivity. Improper validation of trust in an X.509 certificate during VPN negotiation on Check Point Quantum Security Gateway may allow an unauthenticated remote attacker to execute arbitrary code on the gateway with the privileges of a system process.

An attacker may use the compromised gateway to perform internal network reconnaissance (including port and service scanning), intercept VPN traffic, steal credentials and configuration files, including certificates, IPsec/VPN keys, and administrator credentials, and compromise VPN tunnels connecting the organization's network to branch offices and partner networks.

The vulnerability also affects Spark Firewall devices, a family of firewalls developed by Check Point primarily to protect the networks of small and medium-sized businesses, branch offices, and remote locations.

⚙️ Security updates and mitigation measures have been available on the vendor's website since September 9.

👾 Check Point experts began observing exploitation attempts on September 12. On September 22, the vulnerability was added to the CISA KEV catalog.

🛠 A public exploit has been available on GitHub since October 7.

🌐 As of October 12, Shodan had identified 11,849 potentially vulnerable Check Point gateways exposed to the Internet, 143 of them in Russia.

September Linux Patch Wednesday

September Linux Patch Wednesday

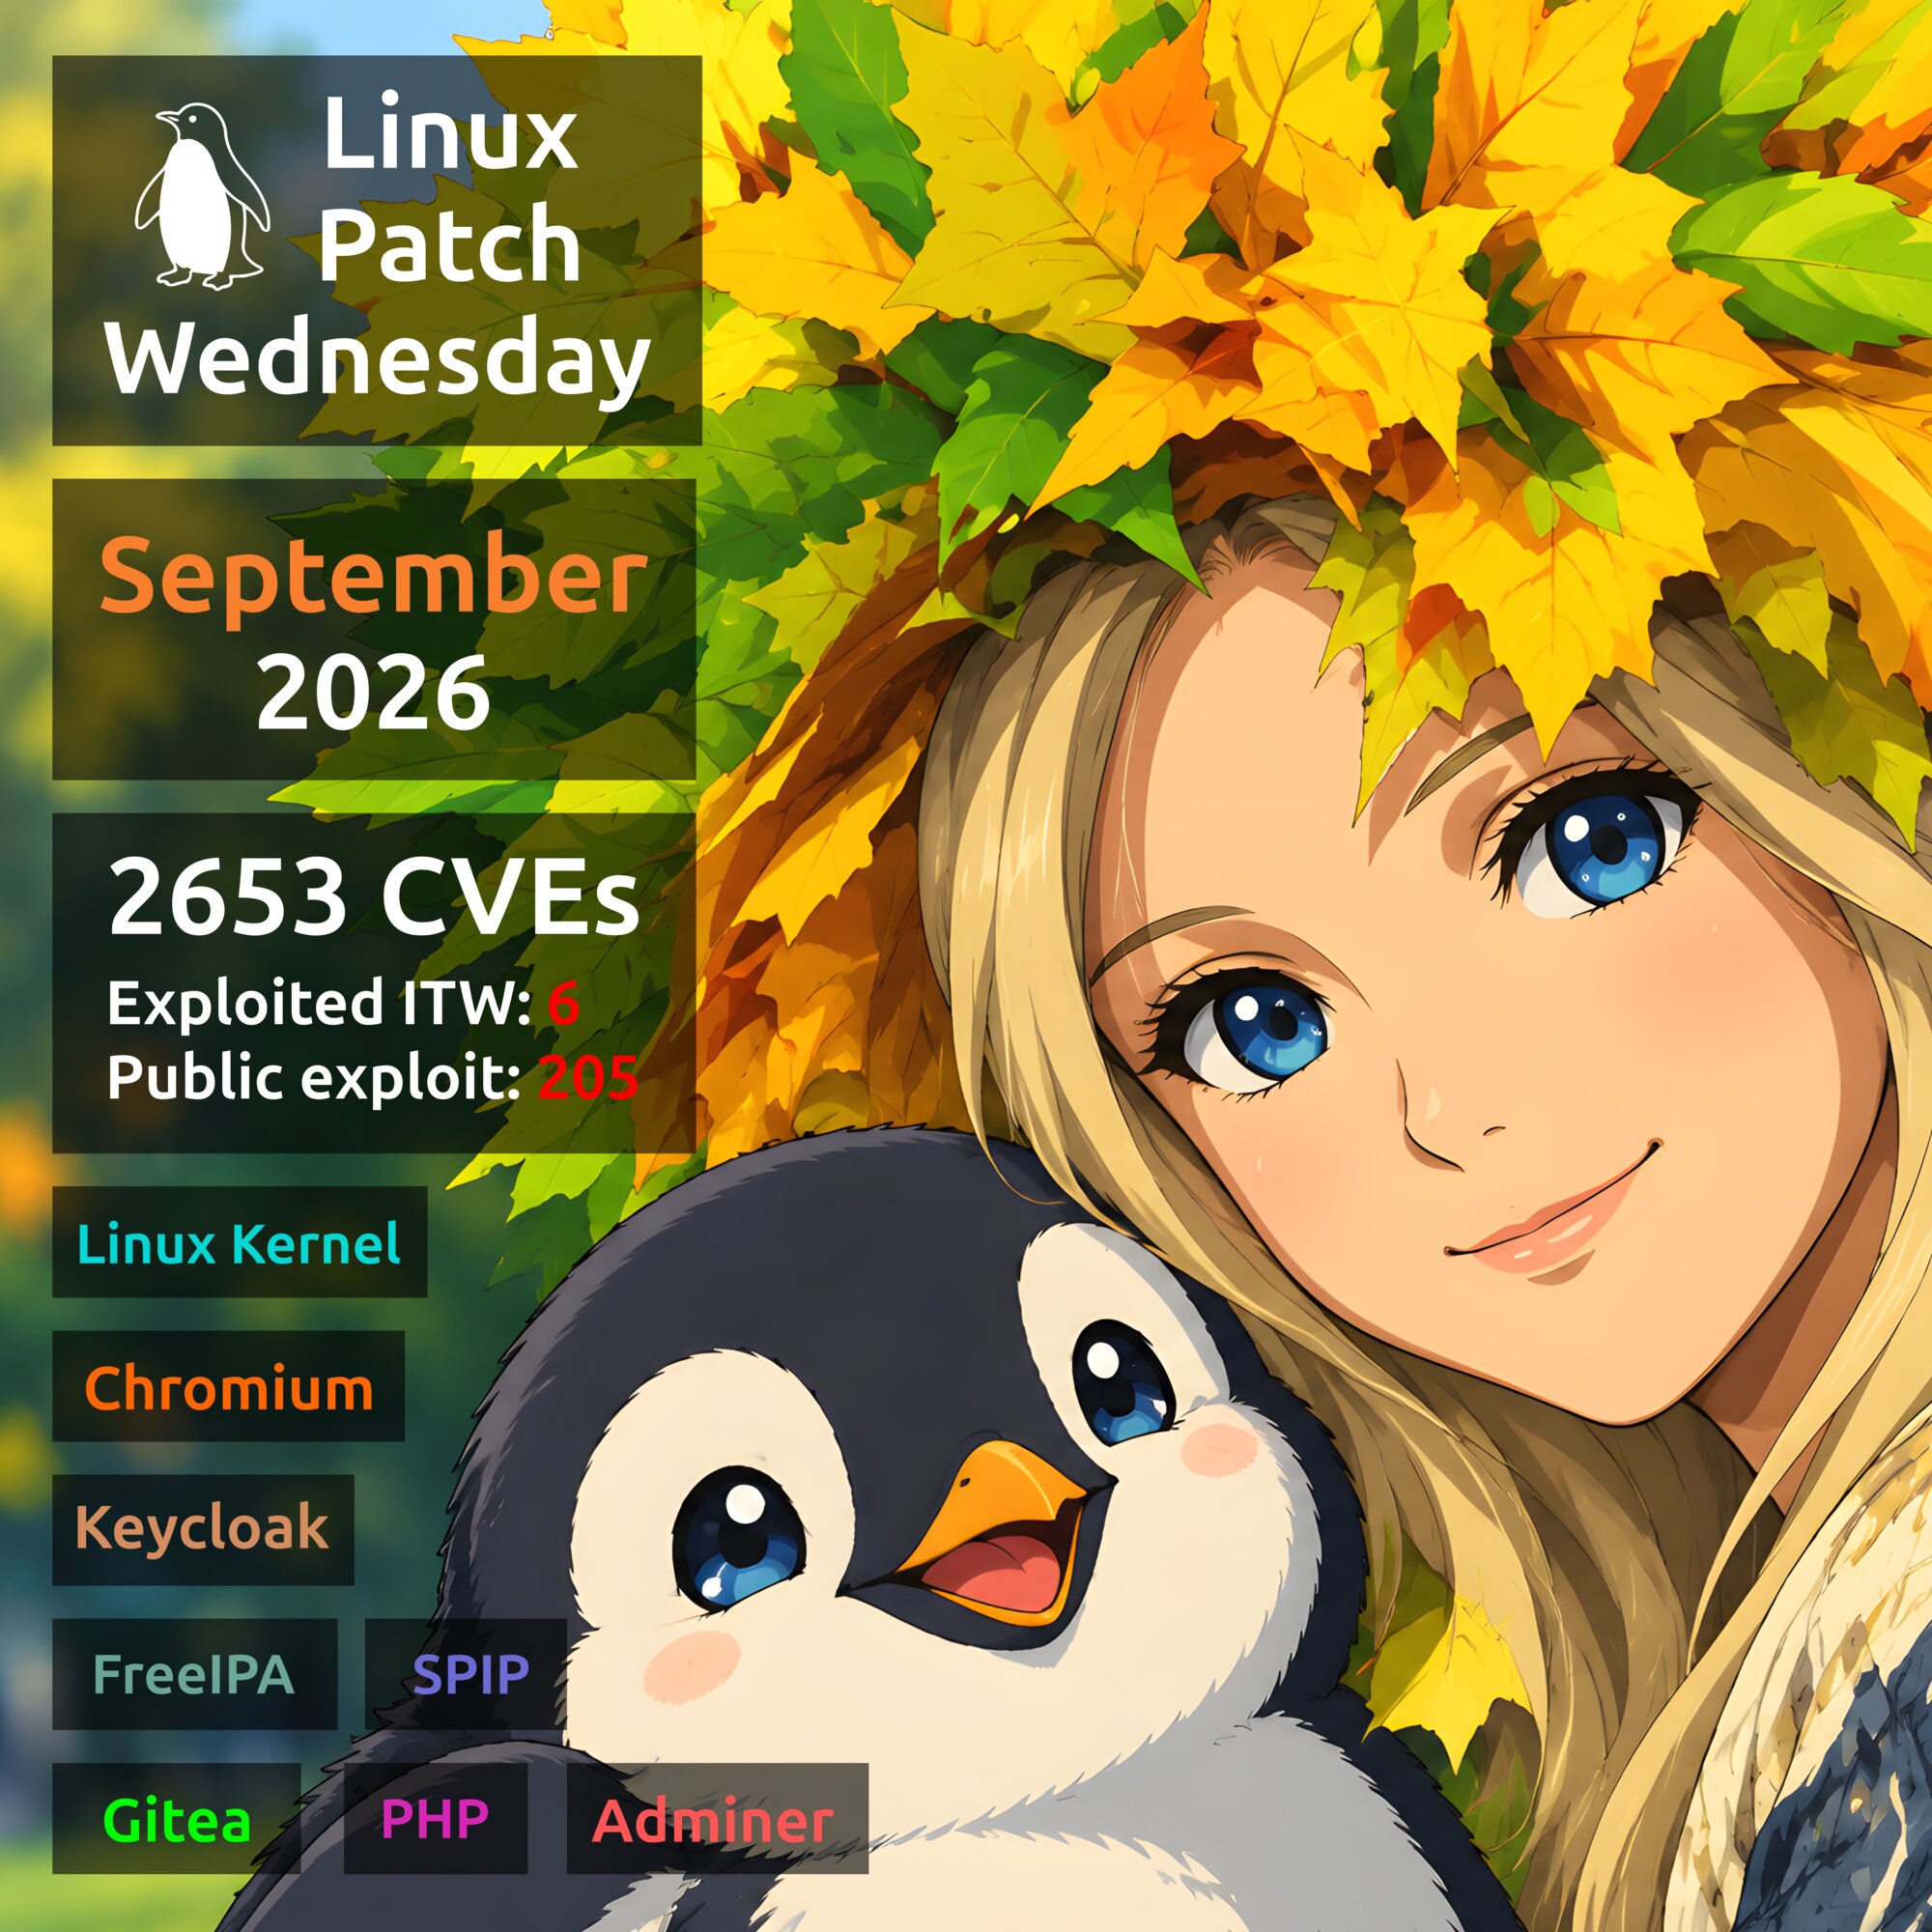
September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.

🗒 Full Vulristics report
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September In the Trend of VM (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.

🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.

🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.

🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability. SharePoint is a web application for corporate intranet portals, document management, and collaboration. This vulnerability was disclosed as part of the July Microsoft Patch Tuesday. A remote unauthenticated attacker can leverage this vulnerability to bypass authentication on a vulnerable SharePoint server and perform operations as a SharePoint site user or administrator. The vulnerability is due to several issues in the JWT token validation pipeline. A JWT (JSON Web Token) is essentially an "electronic pass" that SharePoint uses to determine who a user is and what actions they are authorized to perform. When combined with CVE-2026-63520, the vulnerability allows an attacker to perform remote code execution on a SharePoint server without authentication, with the privileges of the SharePoint service account. As a result, an attacker can gain access to documents and other organizational data stored in SharePoint, modify or delete them, extract credentials, install malware, and establish persistence in the system, and then use the compromised server for further penetration into the organization's internal network.

🛠 The vulnerability was discovered by Stephen Fewer from Rapid7 during SharePoint research conducted in January and March 2026. The research aimed to develop an exploit for the Pwn2Own Berlin competition. AI tools and agentic workflows were actively used throughout the research. Rapid7 published a detailed analysis of the vulnerability and the exploit code on its blog on August 11.

👾 According to VulnCheck, exploitation attempts were detected on honeypots shortly after the exploit was published. The vulnerability was added to the VulnCheck KEV on August 12 and to the CISA KEV on August 18.

⚙️ Updates are available for Microsoft SharePoint Server 2016 (Enterprise), 2019, and Subscription Edition. Note that you need to install the latest SharePoint cumulative updates that include fixes for CVE-2026-55040 and CVE-2026-63520.

🌐 As of August 25, 2026, Censys experts reported around 21,000 on-premises SharePoint installations exposing their version information. According to The Shadowserver Foundation, around 8,500 SharePoint servers were accessible from the Internet each day in September 2026. These are observed servers, and not all of them are necessarily vulnerable. No statistics on vulnerable servers are available.

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability. TeamCity is a proprietary solution developed by JetBrains for automating software build, testing, and deployment processes. TeamCity uses a central server to coordinate builds and separate build agents to execute them. An agent can communicate with the server through the agent polling protocol: it registers with the server, requests the next command, and reports whether the command succeeded or failed. The vulnerability allows an unauthenticated remote attacker with HTTP(S) access to a TeamCity On-Premises server to execute arbitrary operating system commands with the privileges of the TeamCity Server process through the agent polling protocol. The vulnerability is caused by insecure deserialization of XML data (CWE-502). Depending on the privileges of the TeamCity Server process, successful exploitation may allow an attacker to access TeamCity data, configurations, and stored credentials, modify the server state, and potentially compromise the integrity of build artifacts and downstream CI/CD pipelines.

⚙️ A notice about this critical vulnerability was published on the JetBrains blog on July 27. The vulnerability affects all versions of TeamCity On-Premises. To remediate the vulnerability, users should upgrade to version 2025.11.7 or 2026.1.3. As a compensating measure, a security patch plugin can be installed on TeamCity 2017.1 and later to prevent exploitation of the vulnerability. For TeamCity 2017.1-2018.1, the server must be restarted after installing the plugin. Starting with TeamCity 2018.2, the plugin can be enabled without restarting the TeamCity server. As a longer-term security measure, the vendor recommends limiting network access to TeamCity servers to trusted networks, including restricting access to the TeamCity login page and REST API. It is also recommended to run the TeamCity server under an operating system account with the minimum privileges required for normal operation. TeamCity servers should be deployed on dedicated hosts separate from build agents, as described in the documentation.

👾 The vulnerability was added to the CISA KEV on August 5. On August 7, JetBrains published a report confirming exploitation of the vulnerability in the wild. The vendor recommended checking TeamCity logs for com.thoughtworks.xstream.converters.ConversionException messages, which may indicate successful exploitation of the vulnerability and warrant further investigation. After updating the server or installing the security patch plugin, logs can be checked for com.thoughtworks.xstream.security.ForbiddenClassException messages, which indicate that an exploitation attempt was blocked. Unauthorized build agents, particularly those with names beginning with scan, may also indicate exploitation attempts.

🛠 A technical analysis of the vulnerability and a link to a public exploit were published on the Rapid7 blog on August 7. A Metasploit module for simplified exploitation of the vulnerability has been available since August 28.

🌐 According to JetBrains, TeamCity is used by more than 30,000 organizations worldwide across government, technology, financial services, healthcare, and other sectors, including some Fortune 500 companies. As of July 30, Censys had detected approximately 4,500 TeamCity installations exposed to the Internet. Of these, 450 were running versions 2025.11.7 or 2026.1.3. Most of the remaining installations were running earlier versions or did not disclose version information.