Tag Archives: CISA

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.
About Remote Code Execution - Zimbra Collaboration (CVE-2026-73570) vulnerability

About Remote Code Execution - Zimbra Collaboration (CVE-2026-73570) vulnerability

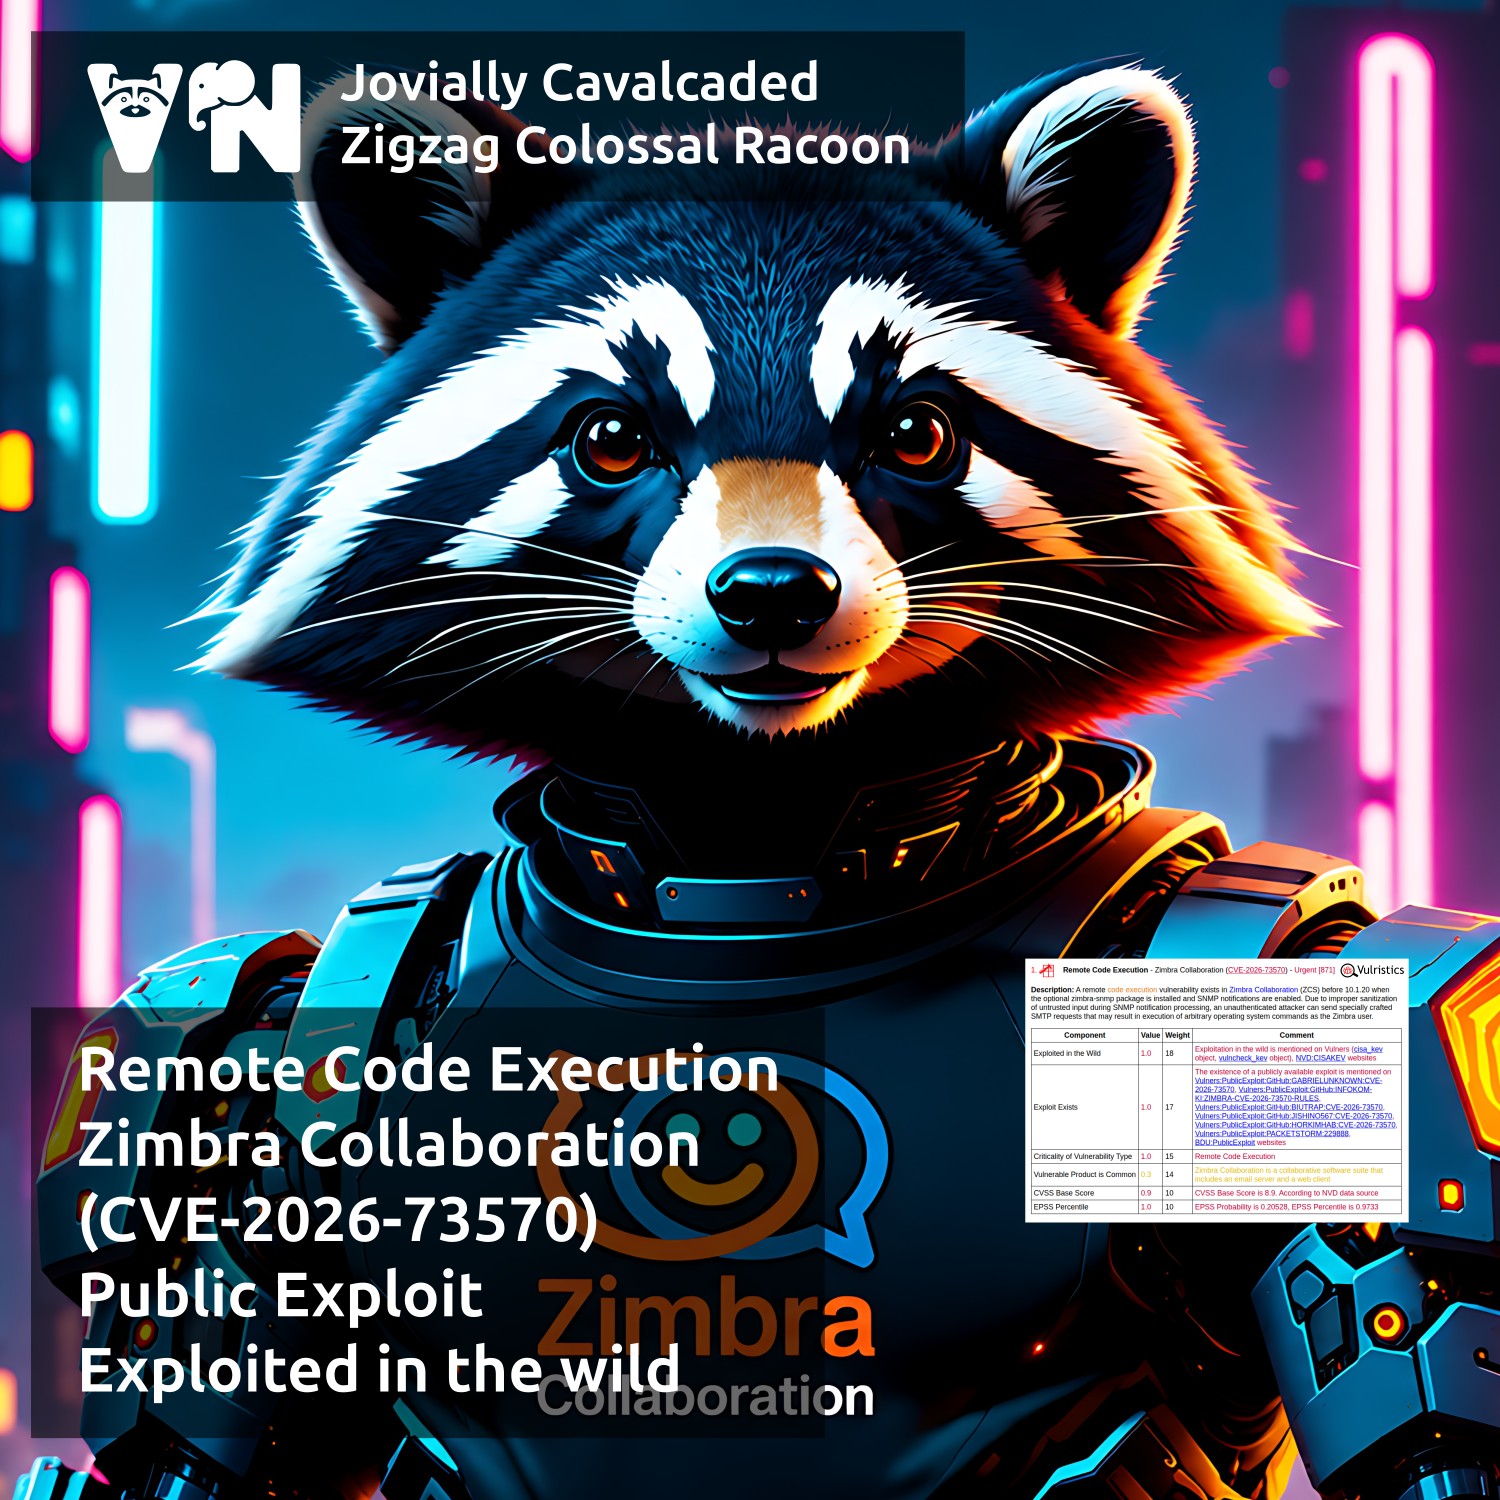
About Remote Code Execution - Zimbra Collaboration (CVE-2026-73570) vulnerability. Zimbra Collaboration is a collaboration software suite that includes a mail server and web client. In terms of functionality, it is comparable to Microsoft Exchange. The vulnerability allows an unauthenticated attacker to send specially crafted SMTP requests that can result in arbitrary operating system command execution with the privileges of the zimbra user. The vulnerability is caused by the lack of proper sanitization of untrusted input when processing data to generate SNMP notifications. Exploitation requires the optional zimbra-snmp package to be installed, SNMP notifications to be enabled, and the swatchdog service to be running.

Successful exploitation allows an attacker to install malware, establish persistence, and use the compromised server as a foothold for further access to the organization's internal infrastructure. An attacker may also gain unauthorized access to corporate emails and other data stored on the system, as well as disrupt Zimbra-related services and business processes.

👾 Experts at CERT Polska reported that the vulnerability was being exploited in the wild on August 17. They recommended checking /var/log/zimbra.log for malicious commands, as well as looking for files created by the zimbra user within the last 30 days in the following directories: /opt/zimbra/jetty/webapps/, /opt/zimbra/jetty_base/webapps/, and /tmp/. The vulnerability was added to the CISA KEV catalog on August 21.

🛠 Public exploits have been available on GitHub since August 24. According to researcher Gabriel P. Lipski's exploit description, an unauthenticated attacker connects to an SMTP port (25, 465, or 587) and sends a standard SMTP session with a command injected into the RCPT TO. Zimbra logs this data in /var/log/zimbra.log regardless of whether the request is accepted or rejected. The swatchdog process then automatically searches the log for lines matching a specific pattern, extracts the attacker-controlled parameter, and passes it to the shell script responsible for sending SNMP notifications without any sanitization. The shell script consequently executes the attacker's command on the host with the privileges of the zimbra operating system user.

⚙️ To remediate the vulnerability, update Zimbra to version 10.1.20 or later. As compensating measures, organizations can disable SNMP notifications, stop the swatchdog service, remove the zimbra-snmp package, and restrict SMTP connections.

🌐 As of August 30, Shadowserver is tracking 5,326 potentially vulnerable hosts, including 172 in Russia. Shadowserver experts also reported the compromise of 274 hosts on August 24.

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August In the Trend of VM (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint. I present the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous July edition, there was just one vulnerability. This time, there are four.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - ViPNet Client (BDU:2026-09885). The first trending vulnerability in a Russian-made product since the beginning of 2026. Its exploitation was discovered by Positive Technologies experts.

🔻 EoP - NT OS Kernel (CVE-2026-42980). The vulnerability allows an attacker to escalate privileges to NT AUTHORITY\SYSTEM level.

🔻 EoP - Microsoft SharePoint (CVE-2026-56164) and RCE - Microsoft SharePoint (CVE-2026-58644). Two actively exploited vulnerabilities in a popular platform for building corporate websites, managing documents, and collaborating.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability.

About Elevation of Privilege - Microsoft SharePoint (CVE-2026-56164) vulnerability. The vulnerability was disclosed in the July Microsoft Patch Tuesday release on July 14. The vulnerability, related to missing authentication for a critical function (CWE-306), allows an unauthenticated attacker to remotely elevate their privileges.

It is quite interesting that the CVSS scores for the vulnerability differ significantly between Microsoft's website and the NVD.

🔹 Microsoft: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N (5.3 MEDIUM)

🔹 NVD: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H (9.8 CRITICAL)

As can be seen, the difference is that Microsof's experts consider the impact of successful exploitation on integrity to be low, while the NVD rates the impact on confidentiality, integrity, and availability as high. This once again highlights the subjective nature of CVSS as a vulnerability prioritization tool. 😉

👾 Microsoft experts flagged this vulnerability as being exploited in the wild on the day of Patch Tuesday. The vulnerability was also added to the CISA KEV catalog on the same day. Microsoft credited Mandiant Incident Response for reporting this vulnerability, which suggests that Mandiant may have been involved in identifying the exploitation activity. There are currently no publicly available details regarding the attacks. However, according to Bleeping Computer, this vulnerability may have been exploited in an attack against the Swiss Federal Office of Information Technology, Systems and Telecommunication (BIT) reported on July 28. During the incident, credentials for around 200 user and technical accounts were compromised on Internet-facing SharePoint servers. The investigation did not reveal any other data breaches. According to BIT, SharePoint vulnerabilities from the July Microsoft Patch Tuesday were exploited on the servers, although the specific CVEs were not disclosed.

🛠 An exploit for the vulnerability has been available on GitHub since August 6. According to the exploit author's description, the vulnerability allows a remote unauthenticated attacker to elevate privileges to the level of Farm Administrator. By abusing request processing and routing mechanisms, an attacker can force a vulnerable server to fall back to an elevated security context instead of rejecting an unauthenticated request. This enables the attacker to access information about site collections, users, and server configuration, add administrators, and execute commands.

⚙️ Updates are available for Microsoft SharePoint Server 2016, 2019, and Subscription Edition. In addition to installing the updates, Microsoft experts recommend enabling the AMSI antimalware scanning interface on the server and setting the Request Body Scan mode to Full to reduce the risk of exploitation.

July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability

July In the Trend of VM (#29): Microsoft Exchange Server vulnerability

July "In the Trend of VM" (#29): Microsoft Exchange Server vulnerability. Here is my traditional monthly roundup of trending vulnerabilities, according to Positive Technologies. The previous June edition featured four vulnerabilities. This time, there's only one.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 XSS - Microsoft Exchange (CVE-2026-42897). The vulnerability allows attackers to execute arbitrary JavaScript in a user's browser when the user opens a malicious email in Outlook Web Access (OWA). A public proof-of-concept exploit is available, and the vulnerability has already been exploited in the wild.

🟥 The full list of trending vulnerabilities is available on the portal

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability

About Cross Site Scripting - Microsoft Exchange (CVE-2026-42897) vulnerability. The vulnerability was fixed on May 14 outside the regular Microsoft Patch Tuesday cycle. Improper neutralization of input during web page generation (CWE-79, XSS) in Microsoft Exchange Server allows an unauthorized attacker to perform spoofing over a network. In practical terms, this means that a remote attacker could exploit this vulnerability by sending a specially crafted email to a user. If the user opens the email in Outlook Web Access and certain interaction conditions are met, arbitrary JavaScript can be executed in the browser context. As a result, the attacker may gain control of the user's mailbox by using an active user session.

👾 Microsoft experts immediately reported signs of active exploitation in the wild for this vulnerability. The vulnerability was added to the CISA KEV on May 15.

⚒️ A public exploit for the vulnerability was published on GitHub on May 15 as well.

⚙️ Initially, mitigation measures were recommended to address the vulnerability, delivered via the Exchange Emergency Mitigation (EM) service or by using the Exchange on-premises Mitigation Tool (EOMT) script. Security updates that fix the vulnerability in Microsoft Exchange Server Subscription Edition RTM, Exchange Server 2016, and Exchange Server 2019 were released almost a month later, on June 9. Microsoft experts recommended keeping the mitigations enabled even after applying the patch, as they provide an additional layer of protection. However, applying these mitigations may cause issues (for example, errors when printing calendars and displaying images in OWA).

⚠️ Please note that Exchange Server 2016 and 2019, which are out of support, are also affected by this vulnerability. Only customers enrolled in the Period 2 Extended Security Update (ESU) program are eligible to receive Exchange Server 2016 and 2019 security updates released between May and October 2026.

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May In the Trend of VM (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. While the previous April edition featured only one vulnerability, this one includes four, covering different technologies and attack scenarios.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Copy Fail" (CVE-2026-31431). The vulnerability allows an attacker to gain root privileges.

🔻 RCE - Apache ActiveMQ (CVE-2026-34197). A vulnerability in a solution widely used in enterprise systems and integration platforms.

🔻 Spoofing - Microsoft SharePoint Server (CVE-2026-32201). A vulnerability in a Microsoft solution widely used in enterprise systems for collaboration, document management, and internal portal development.

🔻 RCE - Adobe Reader (CVE-2026-34621). A vulnerability in a widely used PDF document viewer; actively exploited in phishing attacks.

🟥 The full list of trending vulnerabilities is available on the portal