Tag Archives: APT

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability. The Ancillary Function Driver (AFD) is a Windows component that supports Windows Sockets applications and is contained in the afd.sys file. The afd.sys driver runs in kernel mode and manages the Winsock TCP/IP communications protocol. This vulnerability is from the August Microsoft Patch Tuesday. Use-after-free (CWE-416) in the Windows Ancillary Function Driver for WinSock allows an authorized attacker to elevate privileges locally to SYSTEM level. Successful exploitation requires an attacker to win the race condition. As a result, the attacker can gain full control over the Windows host, execute commands with SYSTEM-level privileges, disable security protections, install malware, and access other users' data.

👾 The vulnerability was already being exploited in the wild when it was disclosed as part of Microsoft's August Patch Tuesday on August 11. That same day, it was added to the CISA KEV catalog. Notably, Microsoft listed the Exploit Code Maturity in the CVSS as "Unproven". 🤷‍♂️ Microsoft credited researchers from Check Point for reporting the vulnerability.

Details on how the vulnerability was exploited in attacks were published in a Check Point blog post on August 11. The vulnerability was exploited as part of the "Operation Dream Job" campaign, which targeted organizations worldwide, with a particular focus on the defense sector in Europe and India. The campaign is linked to the Lazarus Group. The campaign begins with targeted phishing messages offering victims attractive job opportunities at well-known companies in the defense, aerospace, and aviation industries. Victims are lured into opening a PDF decoy masquerading as a Lockheed Martin job description. This triggers the execution of a lightweight in-memory loader - MISTPEN. The loader uses the Microsoft Graph API to access OneDrive, from which it retrieves additional modules and runs them in memory. During the initial stages of the infection, the attacker deploys several reconnaissance modules that gather information about the system and running processes. Once the target is deemed of interest, MISTPEN retrieves an additional persistence module, which installs the malware on disk and ensures that MISTPEN is automatically launched after a system reboot. After establishing persistence, MISTPEN loads an in-memory module designed to exploit the CVE-2026-68820 vulnerability. Check Point researchers believe that this vulnerability was already being exploited in the "Operation Dream Job" campaign in early July 2026. Successful exploitation enables the malware to launch FudModule, a Lazarus kernel-level rootkit, with SYSTEM privileges. The final backdoor delivered by MISTPEN - ForestTiger - provides attackers with remote access to the compromised system, allowing them to execute commands, collect host information, and download additional malicious components.

🛠 No public exploits have been observed so far. Some people are offering exploits for sale, but they don't look reliable.

⚙️ Security updates are available for Windows 10, Windows 11, and Windows Server 2019.
About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.

Security News: Microsoft Patch Tuesday October 2021, Autodiscover, MysterySnail, Exchange, DNS, Apache, HAProxy, VMware vCenter, Moodle

Security News: Microsoft Patch Tuesday October 2021, Autodiscover, MysterySnail, Exchange, DNS, Apache, HAProxy, VMware vCenter, Moodle. Hello everyone! This episode will be about relatively recent critical vulnerabilities. Let’s start with Microsoft Patch Tuesday for October 2021. Specifically, with the vulnerability that I expected there, but it didn’t get there.

Autodiscover leak discovered by Guardicore Labs

“Autodiscover, a protocol used by Microsoft Exchange for automatic configuration of clients such as Microsoft Outlook, has a design flaw that causes the protocol to “leak” web requests to Autodiscover domains outside of the user’s domain but in the same TLD (i.e. Autodiscover.com).” Guardicore Labs acquired multiple Autodiscover domains and have captured 372,072 Windows domain credentials in total. It seems Microsoft have chosen to ignore this issue. No CVE, no Outlook or ActiveSync patches. The only fix is to ban the “Autodiscover.” domains on devices.

Microsoft Patch Tuesday for October 2021

74 vulnerabilities: 1 Critical, 30 High, 43 Medium.

Elevation of Privilege – Windows Kernel (CVE-2021-40449)

It is a use-after-free vulnerability in the NtGdiResetDC function of the Win32k driver. A detailed technical description is available in Kasperky Securelist post, but, in short, the vulnerability can lead to leakage of kernel module addresses in the computer’s memory. This vulnerability is being exploited in the wild by APT MysterySnail. All servers and desktops should be updated.

Continue reading →

Sending FireEye HX data to Splunk

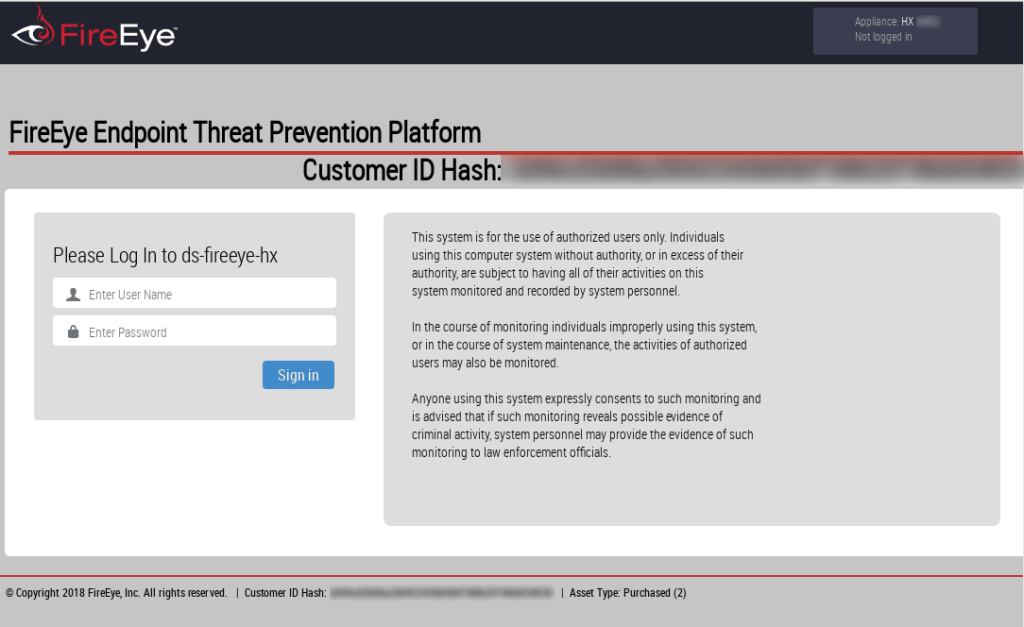
Sending FireEye HX data to Splunk. FireEye HX is an agent-based Endpoint Protection solution. Something like an antivirus, but focused on Advanced Persistent Threats (APT). It has an appliance with GUI where you can manage the agents and see information about detected security incidents.

As with any agent-based solution, it’s necessary to ensure that the agents are installed on every supported host in your network. You may also want to analyze the alerts automatically. And for both purposes you can use Splunk. Let’s see how to do it. 😉

FireEye HX appliance login screen

Note, everything bellow is for FireEye Endpoint Security (HX) 4.0.6 and Splunk 7.0.2. If you use some other version, the things may be quite different.

The main idea is following. We should present FireEye hosts and alerts data in JSON format, add some mandatory fields ans send this packages to Splunk using HTTP Event connector. Then we can process it in Splunk like I’ve shown in “How to correlate different events in Splunk and make dashboards“.

Continue reading →

Microsoft security solutions against ransomware and APT

Microsoft security solutions against ransomware and APT. Last Tuesday I was invited to Microsoft business breakfast “Effective protection against targeted and multilevel attacks”. Here I would like to share some of my thoughts on this. Need to mention that the food was delicious and the restaurant of Russian Geographical Society is a very lovely place. 😉 Thanks, Microsoft!

Microsoft as a security vendor? O RLY?

Microsoft products are not actually my topic. To tell you the truth, personally I’d better live in a world without this massive Windows hegemony in desktop operating systems. I use Linux mostly. And even when I have to work in a Windows environment, it’s much easier for me to do all the work in some Linux virtual machine.

But in the real life almost every office network is build on Microsoft solutions. And if you are doing Vulnerability Management in any organization, you should deal with them too. The good news is that many security features are available out of the box in the MS products that you have already purchased. It’s just important to know about these features and use them right.

One more thing, why it’s interesting to learn more about Microsoft information security products. Microsoft developers, obviously, have direct access to Windows source code and know better how their own OS works. Many things are much easier for them to implement than for other security vendors. So, good chances that you will see in Microsoft products some interesting features, that other vendors don’t have (yet).

Drowning in data

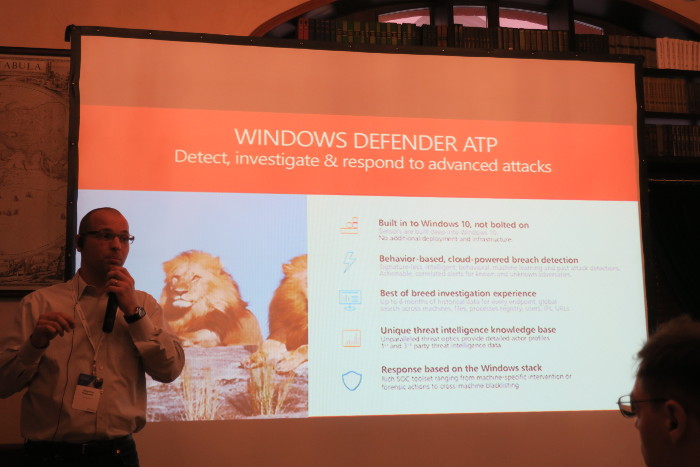
The event began with an opening speech by Andrey Ivanov from Microsoft Russia.

Andrey Ivanov, "Effective protection against targeted and multilevel attacks"

I liked his thesis that “we are drowning in security data”:

  • Threat Intelligence from different sources that need to be implemented in your infrastructure and somehow validated. A good place to mention Vulners.com vulnerability feeds 😉
  • Threat Detection using logs, scanners, various protection tools, etc.
  • The overall number of SIEM inputs is growing faster than our resources. New IT system = new problems of SIEM configuration.

So, it would be nice if somebody, for example OS vendor, will provide all this as a service, right? 😉

Detect the undetectable

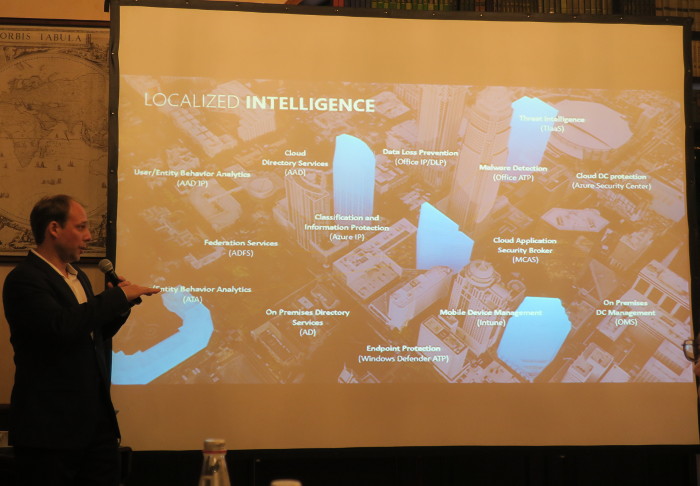
Then there was the keynote by Zbigniew Kukowski – one of the leading Microsoft information security experts.

Zbigniew Kukowski, "Effective protection against targeted and multilevel attacks"

Why is it necessary?

Here is what I would like to note from his report. First of all, great arguments why it is necessary. Ok, this is marketing. But the ability to explain (to sell) necessity of information security is important skill for any information security specialist now. It does not matter if you are working in a  security vendor, integrator or customer.

Zbigniew mentioned an interesting case: some Polish company, that lost $ 4.3 million in recent the Petya attack in 4 days. The cost of Information Security measures will be much less than the potential losses of business.

Another argument – attacks are not the entertainment for some individuals any more. Now it’s a well-organized criminal business. Dozens of people are working on popular malware tools, like Petya. That’s why ransomware tools are so popular now – cyber-criminals just want to return their development costs.

Continue reading →

Why you can't update it all at once?

Why you can’t update it all at once? It’s the second part of our talk with Daniil Svetlov at his radio show “Safe Environment” recorded 29.03.2017. In this part we talk about vulnerabilities in Linux and proprietary software, problems of patch an vulnerability management, and mention some related compliance requirements.

How critical these vulnerabilities are? Are they really exploitable in our infrastructure?

Video with manually transcribed Russian/English subtitles:

Previous part “Programmers are also people who also make mistakes”.

Taking about the fact that if you use fully updated software and do not use some self-written scripts, programs, then in theory everything will be safe.

But recently there was some statistics that critical vulnerabilities stay in Linux kernel about 7 years from the moment they appeared as a result of a programmer’s error till the moment they were found by our white hat researcher.

But it is not clear during these seven years if cybercriminals have found them, used them and how many systems were broken using this vulnerabilities. Not to mention that some special government services may use it too.

For example: The latest Linux kernel flaw (CVE-2017-2636), which existed in the Linux kernel for the past seven years, allows a local unprivileged user to gain root privileges on affected systems or cause a denial of service (system crash). The Hacker News

Well yes. There is such a statistic. There is also some criticism from proprietary software developers. Like you say “many eyes that looks in code will find any error.” This is a quote from Linus Torvalds, if I’m not mistaken.

Not exactly. Linus’s Law is a claim about software development, named in honor of Linus Torvalds and formulated by Eric S. Raymond in his essay and book The Cathedral and the Bazaar (1999).[1][2] The law states that “given enough eyeballs, all bugs are shallow”; or more formally: “Given a large enough beta-tester and co-developer base, almost every problem will be characterized quickly and the fix obvious to someone.” Wikipedia

But in practice, yes, there are really old vulnerabilities that come up after many many years. Because apparently they did not looking for this vulnerabilities well enough.But we still don’t have anything else, except Linux kernel. Therefore, they can say anything, but they will use it anyway. It is in the first place.

Continue reading →