Tag Archives: Debian

September Linux Patch Wednesday

September Linux Patch Wednesday

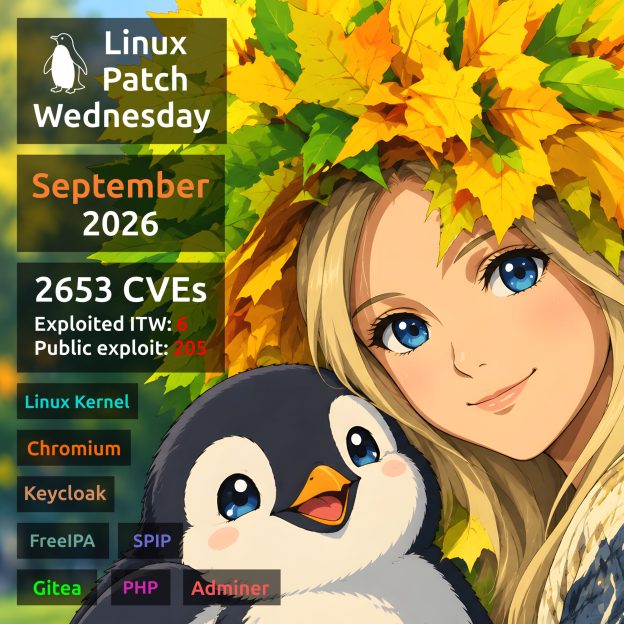
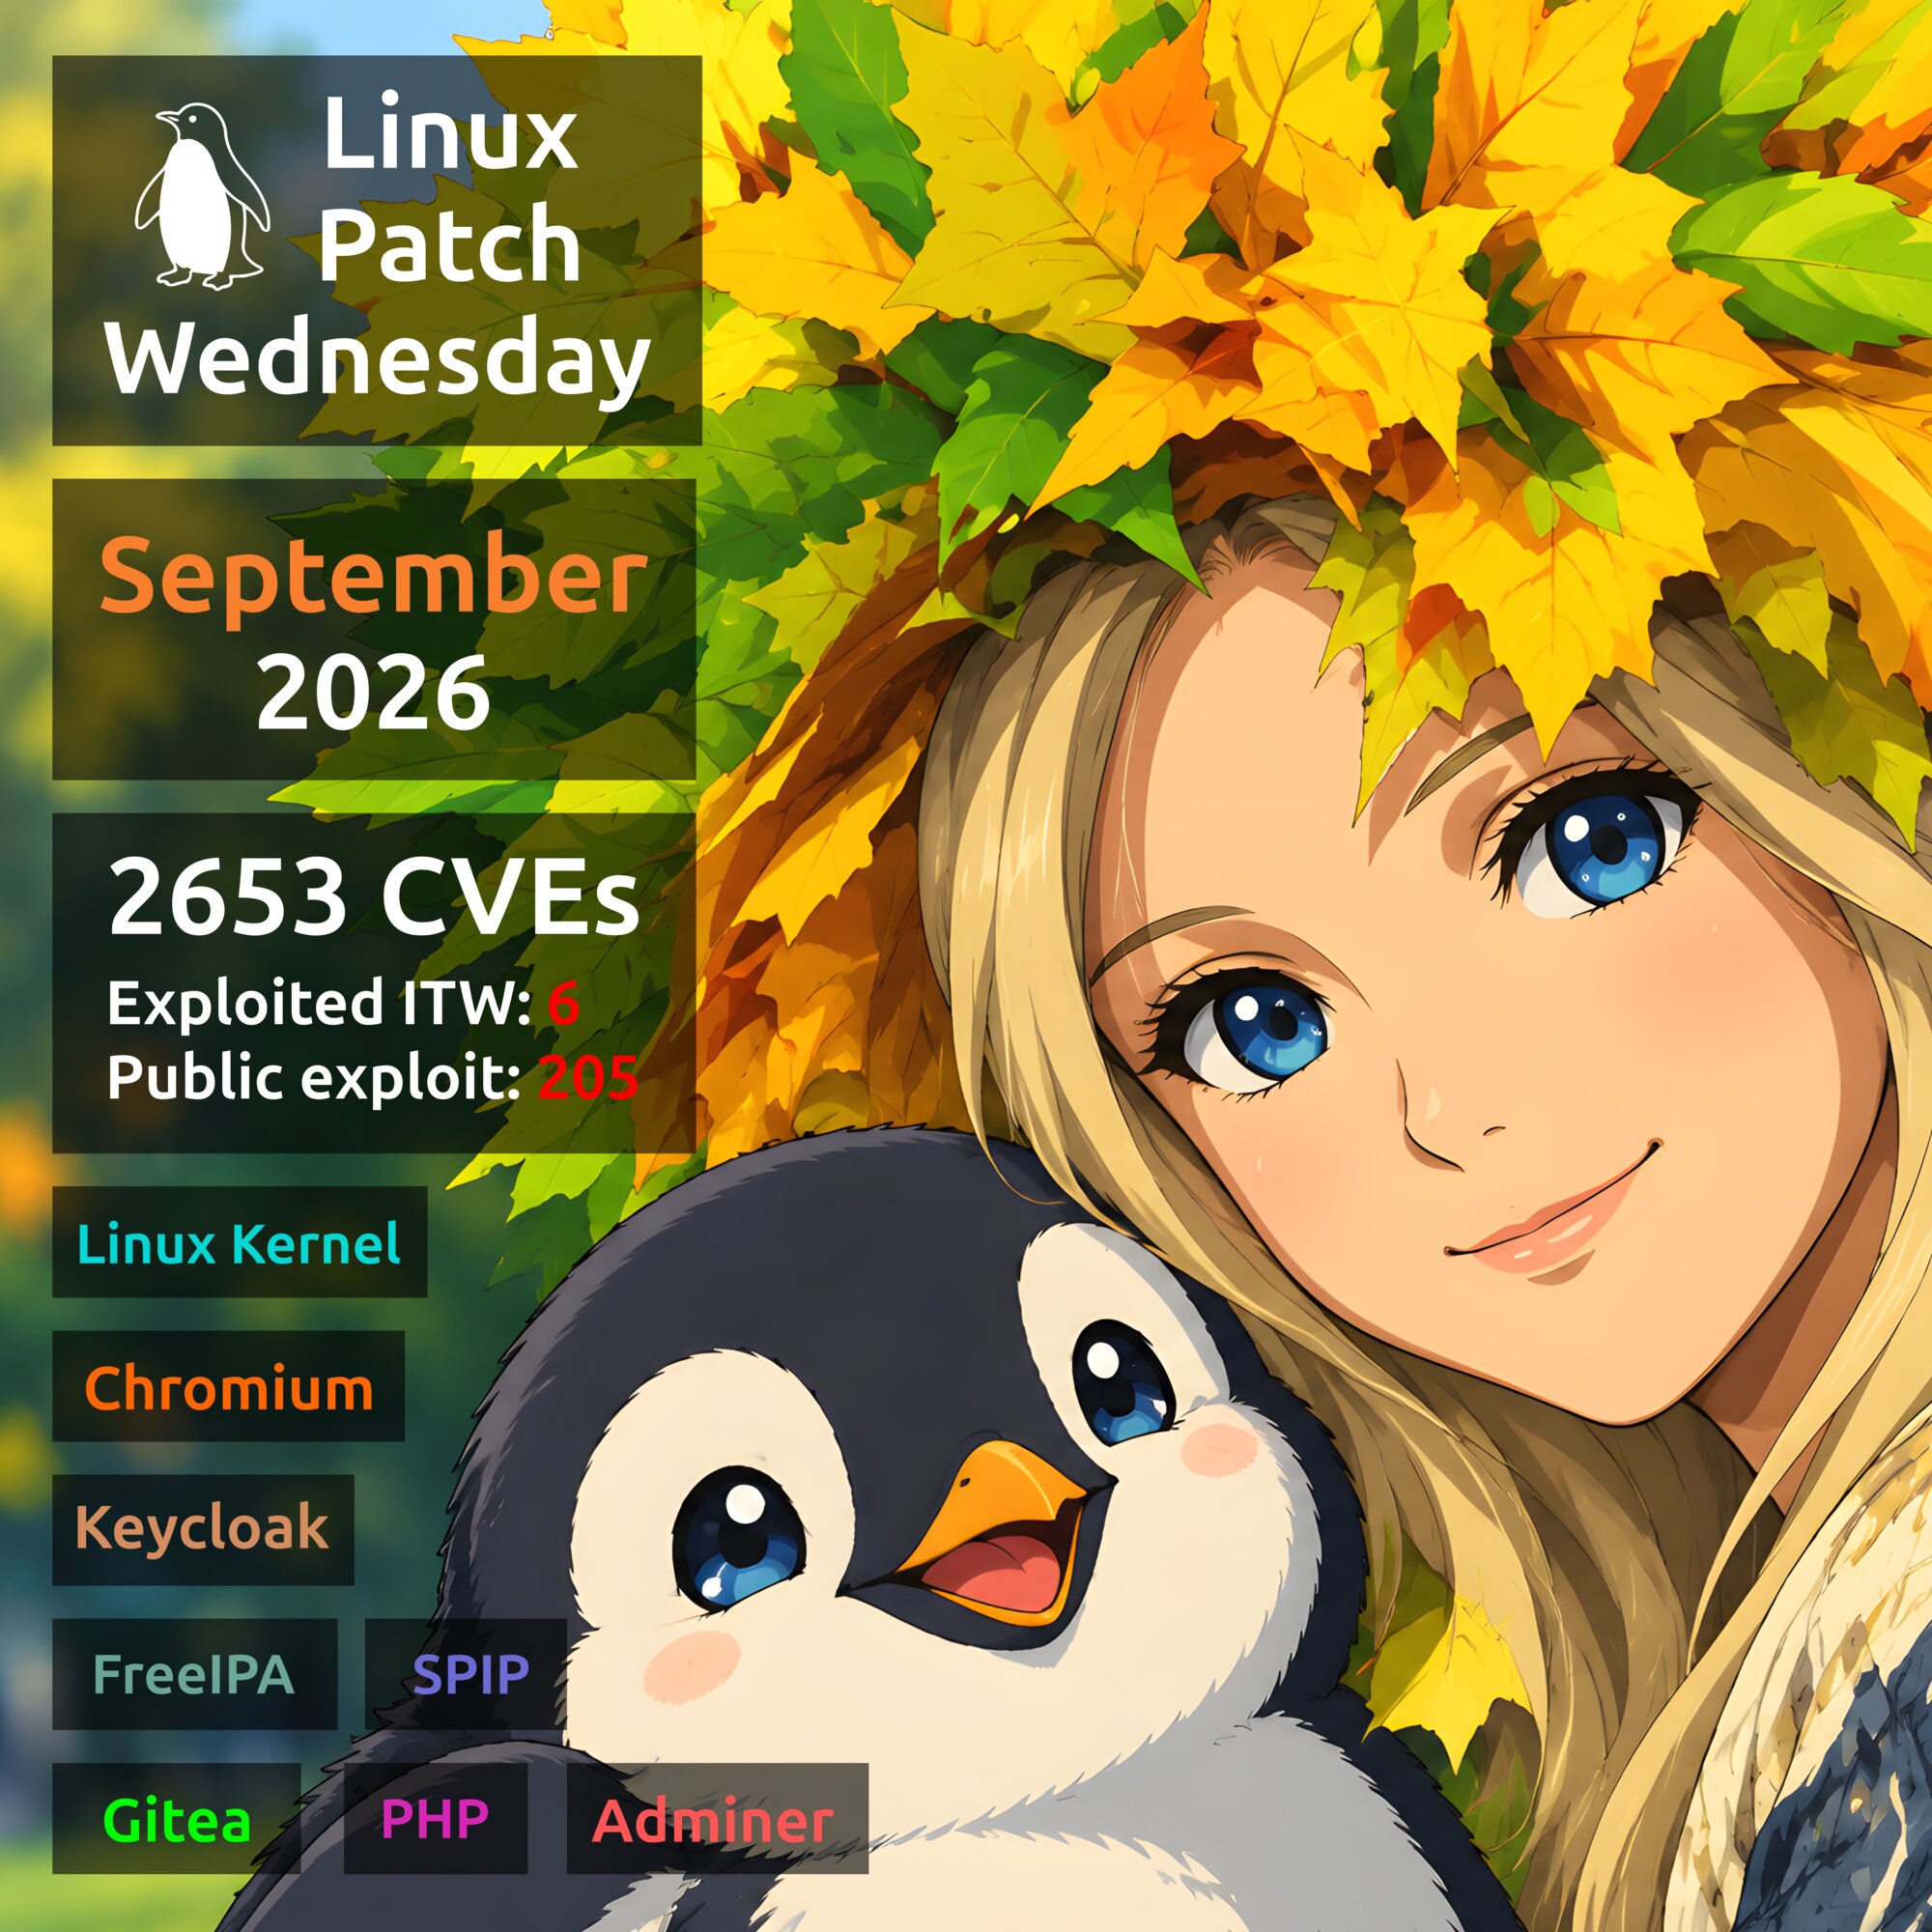
September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.
🗒 Full Vulristics report

August Linux Patch Wednesday

August Linux Patch Wednesday

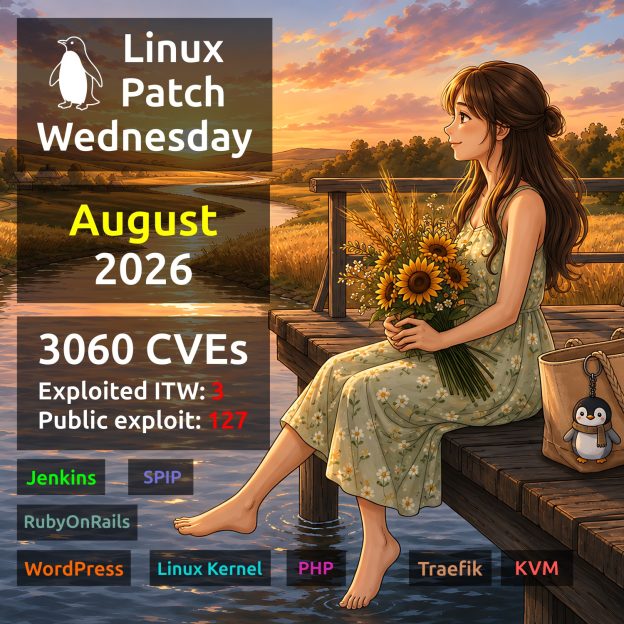
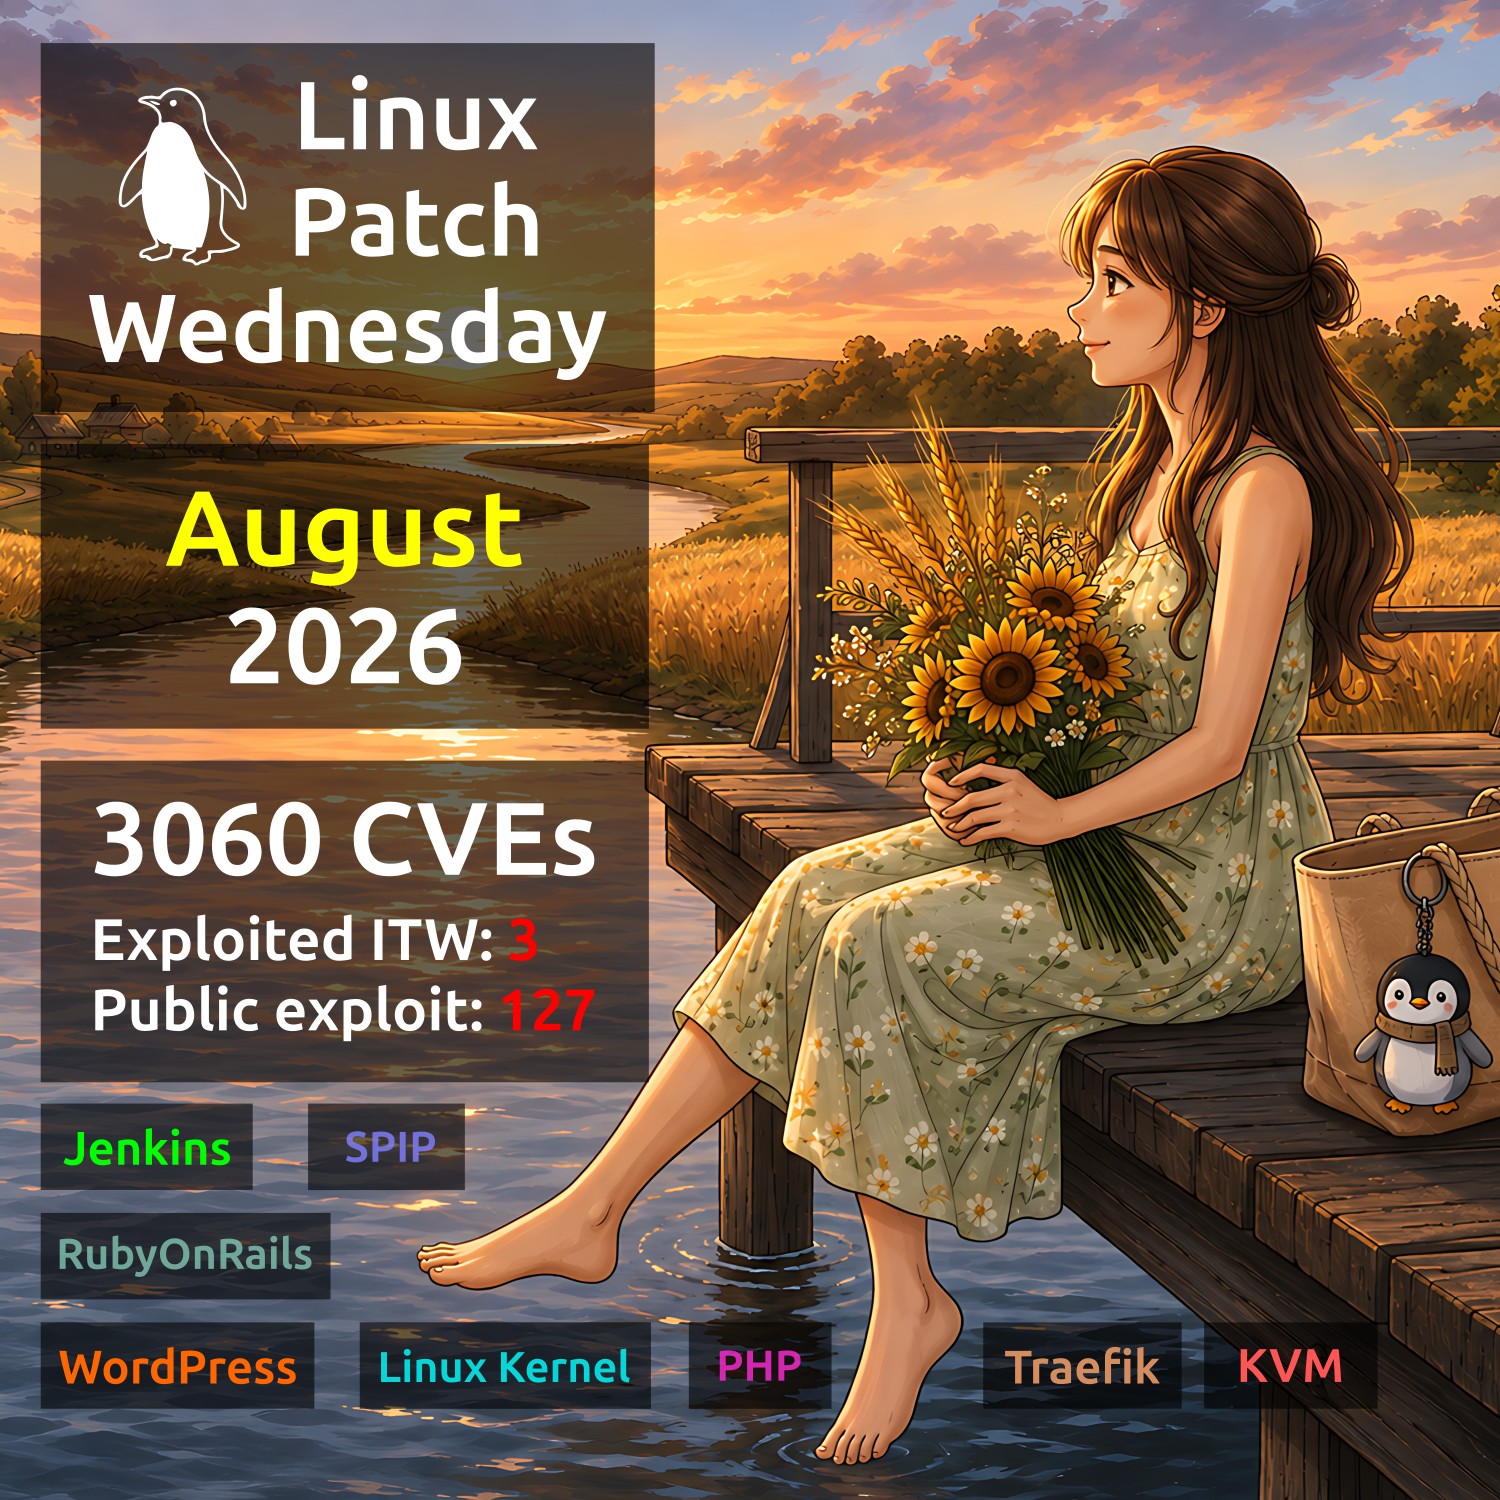
August Linux Patch Wednesday. A total of 3,060 vulnerabilities. For comparison, there were 2,017 in July. That's a 52% increase and another new record. This time, there are 1,354 vulnerabilities in the Linux Kernel and 447 in Chromium. For 3 vulnerabilities, there are signs of exploitation in the wild:

🔻 RCE - Jenkins (CVE-2026-53435). Jenkins is a development automation server used to build, test, and deploy software. The vulnerability allows a remote authenticated attacker to use the Script Console to execute arbitrary code and read files from the Jenkins controller. The vulnerability was added to the VulnCheck KEV on June 15 and fixed in RedOS on August 12.

🔻 CodeInj - WordPress (CVE-2026-60137). WordPress is a popular open-source CMS for creating websites and blogs. The vulnerability leads to a blind SQL injection in the WordPress core, allowing a remote unauthenticated attacker to read user accounts and password hashes from the WordPress database. Code execution is then possible by installing a malicious plugin. Multiple public exploits are available. The vulnerability was added to the CISA KEV catalog on July 21. A fix for the wordpress package in the Debian repository was released on July 23.

🔻 RCE - SPIP (CVE-2026-77647). SPIP is an open-source CMS for creating and collaboratively editing websites. The vulnerability allows an unauthenticated remote attacker to execute arbitrary PHP code. The vulnerability was added to the VulnCheck KEV on August 20. A fix for the spip package in the Debian repository was released on August 18.

Strictly speaking, the report contains one more vulnerability RCE - WinRAR (CVE-2025-8088) that is being exploited in the wild. The vulnerability was fixed in the clamav package in the Alt Linux repository. However, exploitation is only possible on Windows, so it is out of scope.

Another 127 vulnerabilities are not known to be exploited in the wild, but public exploits are available for them, or there are indications that such exploits exist. Notable examples include:

🔸 RCE - Action Pack "KindaRails2Shell" (CVE-2026-66066). Action Pack is a component of Ruby on Rails responsible for handling web requests, routing, and generating responses. An attacker can upload a specially crafted image to a vulnerable application and achieve remote code execution.

🔸 RCE - WordPress "XSS2Shell" (CVE-2026-64638). The attack chain allows an unauthenticated XSS on the login page to be escalated to arbitrary PHP code execution.

🔸 CodeInj - PHP (CVE-2026-17543). Improper escaping of backslashes in attacker-controlled parameters can lead to a trivial SQL injection in PHP.

🔸 EoP - Linux Kernel "Zapscape" (CVE-2026-64561). This KVM escape vulnerability allows an attacker to break out of a virtual machine in KVM/x86 environments and execute commands on the host with root privileges.

🔸 EoP - Linux Kernel "OVSwrap" (CVE-2026-64531), Linux Kernel "SCTPhantom" (CVE-2026-64564), Linux Kernel "Ubuntu PPPoL2TP" (CVE-2026-68398). These vulnerabilities allow a local attacker to escalate privileges to root.

🔸 AuthBypass - Traefik (CVE-2026-48020). Traefik is an HTTP reverse proxy and load balancer. A high-severity vulnerability in the StripPrefix middleware allows an unauthenticated attacker to bypass route-level authentication and authorization.

🗒 Full Vulristics report

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May In the Trend of VM (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. While the previous April edition featured only one vulnerability, this one includes four, covering different technologies and attack scenarios.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Copy Fail" (CVE-2026-31431). The vulnerability allows an attacker to gain root privileges.

🔻 RCE - Apache ActiveMQ (CVE-2026-34197). A vulnerability in a solution widely used in enterprise systems and integration platforms.

🔻 Spoofing - Microsoft SharePoint Server (CVE-2026-32201). A vulnerability in a Microsoft solution widely used in enterprise systems for collaboration, document management, and internal portal development.

🔻 RCE - Adobe Reader (CVE-2026-34621). A vulnerability in a widely used PDF document viewer; actively exploited in phishing attacks.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Linux Kernel "Copy Fail" (CVE-2026-31431) vulnerability

About Elevation of Privilege - Linux Kernel Copy Fail (CVE-2026-31431) vulnerability

About Elevation of Privilege - Linux Kernel "Copy Fail" (CVE-2026-31431) vulnerability. A local privilege escalation vulnerability in the Linux kernel AF_ALG component, which is caused by a memory handling flaw, allows an unprivileged user to escalate privileges to root. By exploiting this vulnerability, an attacker can fully compromise the system: read and modify any files, including passwords and keys, replace system binaries, disable security controls and monitoring tools, stealthily install backdoors and maintain persistence, hide traces of their activity, and use the host as a foothold for attacks on other network assets.

⚙️🛠 On April 1, patches addressing the vulnerability were merged into the main branch of the Linux kernel. On April 22, a CVE identifier was assigned to the vulnerability. On April 29, experts from Theori published an analysis of the vulnerability and a public exploit. The vulnerability's exploitability has been confirmed on up-to-date versions of widely used Linux distributions, including Ubuntu, Amazon Linux, RHEL, and SUSE.

👾 On May 1, the vulnerability was added to the CISA KEV catalog, indicating it is being exploited in the wild.

What distinguishes this vulnerability from similar EOP/LPE issues in Linux?

There have been high-profile privilege escalation vulnerabilities in the Linux kernel. Dirty COW required winning a race condition. Multiple attempts were often needed, and this sometimes led to system crashes. Dirty Pipe was tied to specific versions and required precise pipe buffer manipulation.

But unlike Dirty COW and Dirty Pipe, researchers report that Copy Fail is a straight-line logic flaw. It triggers without races, retries, or crash-prone timing windows.

🧬 Portability. The same exploit script works across all tested distributions and architectures, including Ubuntu, Amazon Linux, Red Hat Enterprise Linux (RHEL), and SUSE Linux Enterprise. No per-distribution offsets. No recompilation. No version checks in the exploit.

✧ Minimalism. The entire exploit is a short Python script using only standard library modules (os, socket, zlib). It requires Python 3.10+ for os.splice. No compiled payloads, no dependency installation.

🥷 Stealth. The write bypasses the ordinary VFS write path. The corrupted page is never marked dirty by the kernel's writeback machinery. Standard file integrity tools that compare on-disk checksums will not detect it, because the on-disk file remains unchanged. Only the in-memory page cache is corrupted.

📦 Cross-container impact. The page cache is shared across all processes on the system, including across container boundaries. Copy Fail is not just a local privilege escalation. It is a container escape primitive and a vector for Kubernetes node compromise.

How to fix the vulnerability?

To remediate the vulnerability, users need to update to Linux kernel versions 6.18.22, 6.19.12, and 7.0. The kernel can be built manually, or users can wait for their Linux distribution vendor to release updated kernel packages. As of May 4, updates have been released for Ubuntu, Debian, RHEL, Fedora, SUSE, CloudLinux, Arch Linux, and ROSA Linux.

As a workaround, researchers suggest blocking the creation of AF_ALG sockets:

echo "install algif_aead /bin/false" > /etc/modprobe.d/disable-algif-aead.conf
rmmod algif_aead 2>/dev/null

November 2023 - January 2024: New Vulristics Features, 3 Months of Microsoft Patch Tuesdays and Linux Patch Wednesdays, Year 2023 in Review

November 2023 – January 2024: New Vulristics Features, 3 Months of Microsoft Patch Tuesdays and Linux Patch Wednesdays, Year 2023 in Review. Hello everyone! It has been 3 months since the last episode. I spent most of this time improving my Vulristics project. So in this episode, let’s take a look at what’s been done.

Alternative video link (for Russia): https://vk.com/video-149273431_456239139

Also, let’s take a look at the Microsoft Patch Tuesdays vulnerabilities, Linux Patch Wednesdays vulnerabilities and some other interesting vulnerabilities that have been released or updated in the last 3 months. Finally, I’d like to end this episode with a reflection on how my 2023 went and what I’d like to do in 2024.

Continue reading →

September 2023: VM courses, Bahasa Indonesia, Russian Podcasts, Goodbye Tinkoff, MS Patch Tuesday, Qualys TOP 20, Linux, Forrester, GigaOm, R-Vision VM

September 2023: VM courses, Bahasa Indonesia, Russian Podcasts, Goodbye Tinkoff, MS Patch Tuesday, Qualys TOP 20, Linux, Forrester, GigaOm, R-Vision VM. Hello everyone! On the last day of September, I decided to record another retrospective episode on how my Vulnerability Management month went.

Alternative video link (for Russia): https://vk.com/video-149273431_456239136

September was quite a busy month for me.

Continue reading →

How Debian OVAL content is structured

How Debian OVAL content is structured. Hello everyone! As we saw in the last episode, the results of vulnerability detection for one host produced by two different APIs can vary greatly. Therefore, in order to find out the truth, it is necessary to understand what vulnerability data is provided by the Linux distribution vendor and how this data is structured.

Alternative video link (for Russia): https://vk.com/video-149273431_456239114

Why is it important to do this? Because using data from a Linux distribution vendor, we can ask vulnerability detection API vendors questions: why are you detecting in a different way than described in this data? And then we will understand what caused the difference. And we will either adjust the API for vulnerability detection, or we will adjust the content of the Linux distribution vendor. Either way, it will be a success! In any case, the transparency of the vulnerability detection process will increase.

Last time we looked at vulnerabilities for Debian host and Debian Docker base image. So let’s continue with Debian. In particular, with the official Debian OVAL (Open Vulnerability and Assessment Language) content.

Debian OVAL content can be downloaded from the https://debian.org/security/oval/ website. For Debian 11.6 it will be https://debian.org/security/oval/oval-definitions-bullseye.xml (~48M).

Continue reading →