Tag Archives: xml

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability

About Remote Code Execution - TeamCity (CVE-2026-63077) vulnerability. TeamCity is a proprietary solution developed by JetBrains for automating software build, testing, and deployment processes. TeamCity uses a central server to coordinate builds and separate build agents to execute them. An agent can communicate with the server through the agent polling protocol: it registers with the server, requests the next command, and reports whether the command succeeded or failed. The vulnerability allows an unauthenticated remote attacker with HTTP(S) access to a TeamCity On-Premises server to execute arbitrary operating system commands with the privileges of the TeamCity Server process through the agent polling protocol. The vulnerability is caused by insecure deserialization of XML data (CWE-502). Depending on the privileges of the TeamCity Server process, successful exploitation may allow an attacker to access TeamCity data, configurations, and stored credentials, modify the server state, and potentially compromise the integrity of build artifacts and downstream CI/CD pipelines.

⚙️ A notice about this critical vulnerability was published on the JetBrains blog on July 27. The vulnerability affects all versions of TeamCity On-Premises. To remediate the vulnerability, users should upgrade to version 2025.11.7 or 2026.1.3. As a compensating measure, a security patch plugin can be installed on TeamCity 2017.1 and later to prevent exploitation of the vulnerability. For TeamCity 2017.1-2018.1, the server must be restarted after installing the plugin. Starting with TeamCity 2018.2, the plugin can be enabled without restarting the TeamCity server. As a longer-term security measure, the vendor recommends limiting network access to TeamCity servers to trusted networks, including restricting access to the TeamCity login page and REST API. It is also recommended to run the TeamCity server under an operating system account with the minimum privileges required for normal operation. TeamCity servers should be deployed on dedicated hosts separate from build agents, as described in the documentation.

👾 The vulnerability was added to the CISA KEV on August 5. On August 7, JetBrains published a report confirming exploitation of the vulnerability in the wild. The vendor recommended checking TeamCity logs for com.thoughtworks.xstream.converters.ConversionException messages, which may indicate successful exploitation of the vulnerability and warrant further investigation. After updating the server or installing the security patch plugin, logs can be checked for com.thoughtworks.xstream.security.ForbiddenClassException messages, which indicate that an exploitation attempt was blocked. Unauthorized build agents, particularly those with names beginning with scan, may also indicate exploitation attempts.

🛠 A technical analysis of the vulnerability and a link to a public exploit were published on the Rapid7 blog on August 7. A Metasploit module for simplified exploitation of the vulnerability has been available since August 28.

🌐 According to JetBrains, TeamCity is used by more than 30,000 organizations worldwide across government, technology, financial services, healthcare, and other sectors, including some Fortune 500 companies. As of July 30, Censys had detected approximately 4,500 TeamCity installations exposed to the Internet. Of these, 450 were running versions 2025.11.7 or 2026.1.3. Most of the remaining installations were running earlier versions or did not disclose version information.
How Debian OVAL content is structured

How Debian OVAL content is structured. Hello everyone! As we saw in the last episode, the results of vulnerability detection for one host produced by two different APIs can vary greatly. Therefore, in order to find out the truth, it is necessary to understand what vulnerability data is provided by the Linux distribution vendor and how this data is structured.

Alternative video link (for Russia): https://vk.com/video-149273431_456239114

Why is it important to do this? Because using data from a Linux distribution vendor, we can ask vulnerability detection API vendors questions: why are you detecting in a different way than described in this data? And then we will understand what caused the difference. And we will either adjust the API for vulnerability detection, or we will adjust the content of the Linux distribution vendor. Either way, it will be a success! In any case, the transparency of the vulnerability detection process will increase.

Last time we looked at vulnerabilities for Debian host and Debian Docker base image. So let’s continue with Debian. In particular, with the official Debian OVAL (Open Vulnerability and Assessment Language) content.

Debian OVAL content can be downloaded from the https://debian.org/security/oval/ website. For Debian 11.6 it will be https://debian.org/security/oval/oval-definitions-bullseye.xml (~48M).

Continue reading

How to Perform a Free Ubuntu Vulnerability Scan with OpenSCAP and Canonical's Official OVAL Content

How to Perform a Free Ubuntu Vulnerability Scan with OpenSCAP and Canonical’s Official OVAL Content. Hello everyone! Five years ago I wrote a blogpost about OpenSCAP. But it was only about the SCAP Workbench GUI application and how to use it to detect security misconfigurations.

Alternative video link (for Russia): https://vk.com/video-149273431_456239104

This time, I will install the OpenSCAP command line tool on Ubuntu and use it to check for vulnerabilities on my local host.

Continue reading

Parsing Nessus v2 XML reports with python

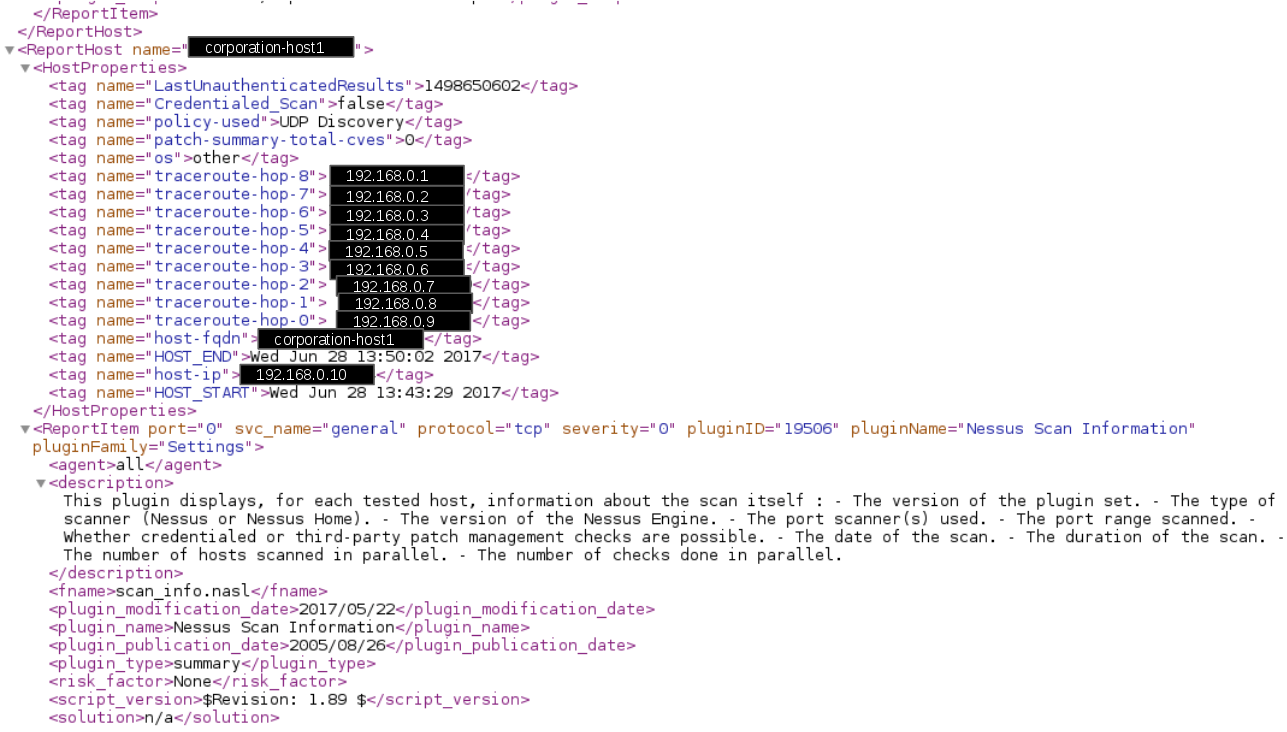
Parsing Nessus v2 XML reports with python. Upd. This is an updated post from 2017. The original script worked pretty well for me until the most recent moment when I needed to get compliance data from Nessus scan reports, and it failed. So I researched how this information is stored in a file, changed my script a bit, and now I want to share it with you.

Previous post about Nessus v2 reports I was writing mainly about the format itself. Now let’s see how you can parse them with Python.

Please don’t work with XML documents the same way you process text files. I adore bash scripting and awk, but that’s an awful idea to use it for XML parsing. In Python you can do it much easier and the script will work much faster. I will use lxml library for this.

So, let’s assume that we have Nessus xml report. We could get it using Nessus API (upd. API is not officially supported in Nessus Professional since version 7) or SecurityCenter API. First of all, we need to read content of the file.

Continue reading

Retrieving data from Splunk Dashboard Panels via API

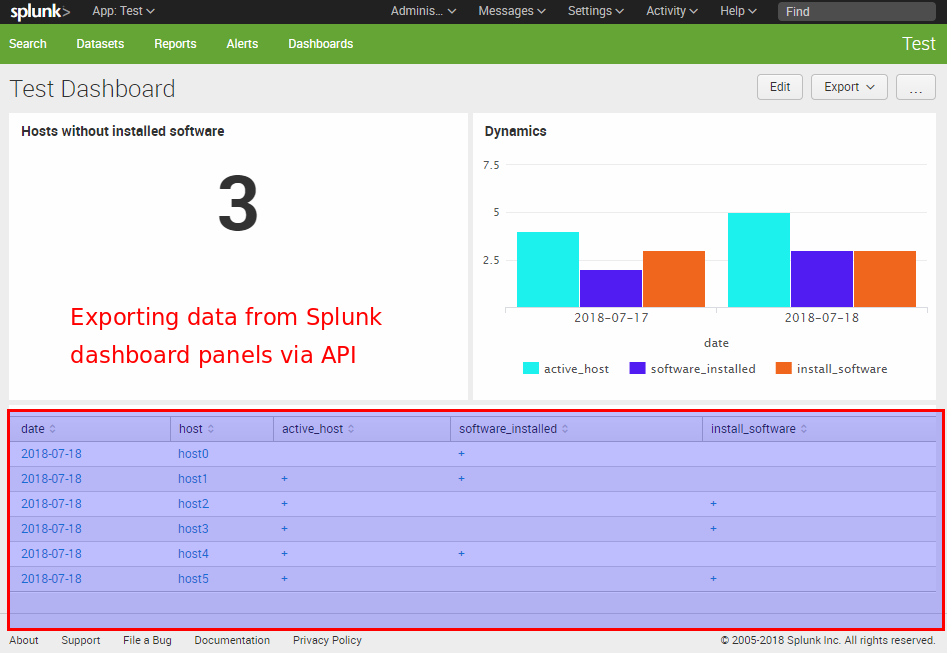
Retrieving data from Splunk Dashboard Panels via API. Fist of all, why might someone want to get data from the panels of a dashboard in Splunk? Why it might be useful? Well, if the script can process everything that human analyst sees on a Splunk dashboard, all the automation comes very natural. You just figure out what routine operations the analyst usually does using the dashboard and repeat his actions in the script as is. It may be the anomaly detection, remediation task creation, reaction on various events, whatever. It really opens endless possibilities without alerts, reports and all this stuff. I’m very excited about this. 🙂

Exporting data from Splunk dashboard

Let’s say we have a Splunk dashboard and want to get data from the table panel using a python script. The problem is that the content of the table that we see is not actually stored anywhere. In fact it is the results of some search query, from the XML representation of the dashboard, executed by Splunk web GUI. To get this data we should execute the same search request.

That’s why we should:

  1. Get XML code of the dashboard
  2. Get the search query for each panel
  3. Process searches based on other searches and get complete search query for each panel
  4. Launch the search request and get the results

First of all, we need to create a special account that will be used for getting data from Splunk. In Web GUI “Access controls -> Users”.

Continue reading

Converting Nmap xml scan reports to json

Converting Nmap xml scan reports to json. Unfortunately, Nmap can not save the results in json. All available output options:

-oN <filespec> (normal output)
-oX <filespec> (XML output)
-oS <filespec> (ScRipT KIdd|3 oUTpuT)
-oG <filespec> (grepable output)
-oA <basename> (Output to all formats)

And processing xml results may not be easy an easy task. Just look how I analyze the contents of the Nessus report in “Parsing Nessus v2 XML reports with python“. Not the most readable code, right? And what alternatives do we have?

Nmap json scan report

Formal XML to json conversion is impossible. Formats are very different. However, there are python modules, for example xmltodict, that can reliably convert XML into Python structures of dictionaries, lists and strings. However, they have to change some names of parameters to avoid collisions. In my opinion this is not a big price for convenience.

So, let’s see how this will work for Nmap command:

nmap -sV -oX nmap_output.xml avleonov.com 1>/dev/null 2>/dev/null

Continue reading

Masking Vulnerability Scan reports

Masking Vulnerability Scan reports. Continuing the series of posts about Kenna (“Analyzing Vulnerability Scan data“, “Connectors and REST API“) and similar services. Is it actually safe to send your vulnerability data to some external cloud service for analysis? Leakage of such information can potentially cause great damage to your organization, right?

Masking Vulnerability Scans

It’s once again a problem of trust to vendor. IMHO, in some cases it may make sense to hide the real hostnames and ip-addresses of the target hosts in scan reports. So, it would be clear for analysis vendor that some critical vulnerability exists somewhere, but it would not be clear where exactly.

To do this, each hostname/ip-address should be replaced to some values of similar type and should be replaced on the same value each time. So the algorithms of Kenna-like service could work with this masked reports. This mean that we need to create a replacement dictionary.

Continue reading