Tag Archives: Windows

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability. The Ancillary Function Driver (AFD) is a Windows component that supports Windows Sockets applications and is contained in the afd.sys file. The afd.sys driver runs in kernel mode and manages the Winsock TCP/IP communications protocol. This vulnerability is from the August Microsoft Patch Tuesday. Use-after-free (CWE-416) in the Windows Ancillary Function Driver for WinSock allows an authorized attacker to elevate privileges locally to SYSTEM level. Successful exploitation requires an attacker to win the race condition. As a result, the attacker can gain full control over the Windows host, execute commands with SYSTEM-level privileges, disable security protections, install malware, and access other users' data.

👾 The vulnerability was already being exploited in the wild when it was disclosed as part of Microsoft's August Patch Tuesday on August 11. That same day, it was added to the CISA KEV catalog. Notably, Microsoft listed the Exploit Code Maturity in the CVSS as "Unproven". 🤷‍♂️ Microsoft credited researchers from Check Point for reporting the vulnerability.

Details on how the vulnerability was exploited in attacks were published in a Check Point blog post on August 11. The vulnerability was exploited as part of the "Operation Dream Job" campaign, which targeted organizations worldwide, with a particular focus on the defense sector in Europe and India. The campaign is linked to the Lazarus Group. The campaign begins with targeted phishing messages offering victims attractive job opportunities at well-known companies in the defense, aerospace, and aviation industries. Victims are lured into opening a PDF decoy masquerading as a Lockheed Martin job description. This triggers the execution of a lightweight in-memory loader - MISTPEN. The loader uses the Microsoft Graph API to access OneDrive, from which it retrieves additional modules and runs them in memory. During the initial stages of the infection, the attacker deploys several reconnaissance modules that gather information about the system and running processes. Once the target is deemed of interest, MISTPEN retrieves an additional persistence module, which installs the malware on disk and ensures that MISTPEN is automatically launched after a system reboot. After establishing persistence, MISTPEN loads an in-memory module designed to exploit the CVE-2026-68820 vulnerability. Check Point researchers believe that this vulnerability was already being exploited in the "Operation Dream Job" campaign in early July 2026. Successful exploitation enables the malware to launch FudModule, a Lazarus kernel-level rootkit, with SYSTEM privileges. The final backdoor delivered by MISTPEN - ForestTiger - provides attackers with remote access to the compromised system, allowing them to execute commands, collect host information, and download additional malicious components.

🛠 No public exploits have been observed so far. Some people are offering exploits for sale, but they don't look reliable.

⚙️ Security updates are available for Windows 10, Windows 11, and Windows Server 2019.

September Microsoft Patch Tuesday

September Microsoft Patch Tuesday

September Microsoft Patch Tuesday. A total of 973 vulnerabilities were addressed - more than twice as many as in August. Seven products had 20 or more vulnerabilities fixed: Windows Biometric Service (64), Microsoft SQL Server (54), Windows DHCP Server (36), Microsoft Office Word (35), Windows NTFS (29), Microsoft Excel (28), and Windows Win32k (24). Vulnerabilities affecting these products account for just under one-third of the total. Two vulnerabilities are known to have been exploited in the wild:

🔻 EoP - Windows Update Stack (CVE-2026-81963). A link following flaw in the Windows Update Stack (CWE-59) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

🔻 EoP - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880). A heap-based buffer overflow flaw in Windows ALPC (CWE-122) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

There are no vulnerabilities with public exploits yet. Of the remaining vulnerabilities, the following can be highlighted:

🔹 RCE - Microsoft Exchange (CVE-2026-55007). A remote, unauthenticated attacker could achieve code execution on a vulnerable Exchange server by sending an email containing a malicious Visio attachment. The code is executed when the server processes the message, without requiring the victim to open it or use the Preview Pane.

🔹 RCE - Remote Desktop Services (CVE-2026-69525). Successful exploitation of this flaw would allow an unauthenticated attacker to execute arbitrary code by exploiting a use-after-free flaw.

🔹 RCE - Windows DNS Server (CVE-2026-69730). According to the advisory, an unauthenticated, remote attacker could send a crafted packet to exploit a use-after-free flaw in Windows DNS in order to achieve remote code execution.

🔹 RCE - Windows USB Mass Storage Class Driver (CVE-2026-68839). Successful exploitation of this vulnerability could allow an attacker the ability to gain remote code execution via an in-network attacker calling arbitrary endpoints.

🔹 RCE - Windows Kerberos (CVE-2026-69676). An authentication-bypass flaw via capture-replay in Windows Kerberos may allow an authenticated attacker to execute code over a network.

🔹 RCE - Windows Key Distribution Center (CVE-2026-69712). A use-after-free flaw in the Windows Key Distribution Center may allow an authenticated attacker to execute code over a network.

🔹 EoP - Microsoft Exchange (CVE-2026-69380). An authenticated attacker with access to a mailbox through a low-privileged user account could exploit this vulnerability to gain access to other mailboxes. Successful exploitation would allow the attacker to send and receive emails on behalf of other Exchange users as well as access attachments.

🗒 Full Vulristics report

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August In the Trend of VM (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint. I present the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous July edition, there was just one vulnerability. This time, there are four.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - ViPNet Client (BDU:2026-09885). The first trending vulnerability in a Russian-made product since the beginning of 2026. Its exploitation was discovered by Positive Technologies experts.

🔻 EoP - NT OS Kernel (CVE-2026-42980). The vulnerability allows an attacker to escalate privileges to NT AUTHORITY\SYSTEM level.

🔻 EoP - Microsoft SharePoint (CVE-2026-56164) and RCE - Microsoft SharePoint (CVE-2026-58644). Two actively exploited vulnerabilities in a popular platform for building corporate websites, managing documents, and collaborating.

🟥 The full list of trending vulnerabilities is available on the portal

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

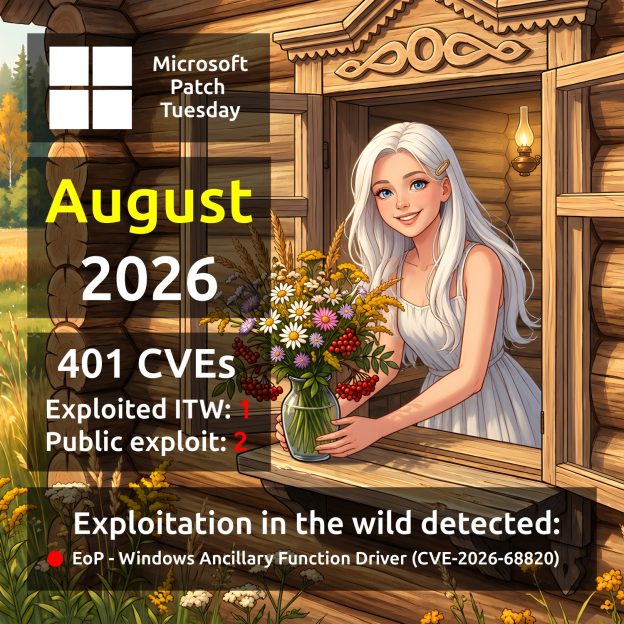
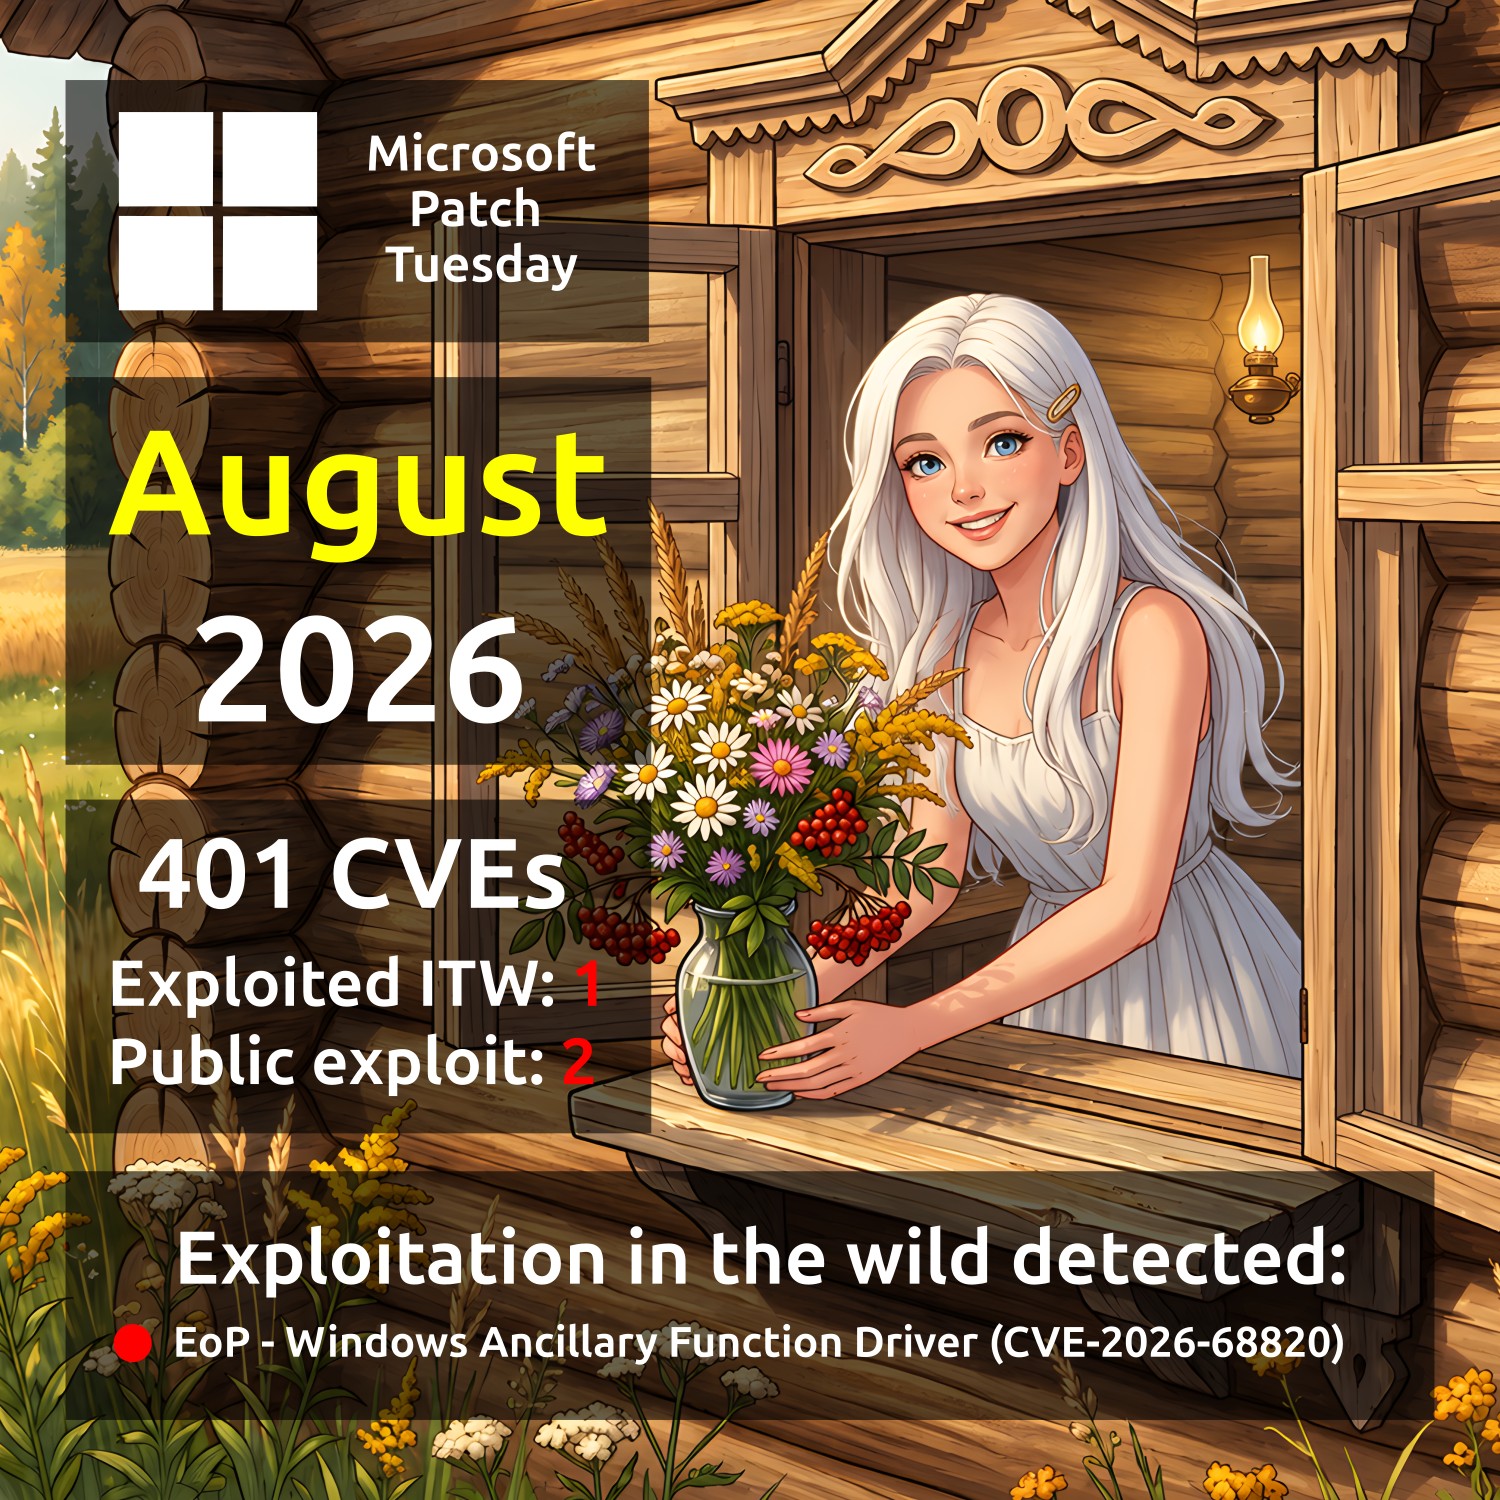
August Microsoft Patch Tuesday. A total of 401 vulnerabilities were addressed - 170 fewer than in July. One of the vulnerabilities is known to be actively exploited in the wild:

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). A local attacker can exploit this vulnerability to gain SYSTEM-level privileges. There is a contradiction in Microsoft's description: the Exploit Code Maturity in CVSS is marked as "Unproven", while at the same time Microsoft states that the vulnerability is being exploited in the wild. 🤷‍♂️

Public exploits are available for two other vulnerabilities:

🔸 EoP - Windows User Profile Service (CVE-2026-62832). This vulnerability allows an authenticated attacker to elevate privileges to ADMINISTRATOR level. Rapid7 believes this vulnerability is related to the LegacyHive exploit, which was published on July 14.

🔸 EoP - Windows Kernel (CVE-2026-62737). This vulnerability allows an authenticated attacker to elevate privileges to SYSTEM level. An exploit has been publicly available since August 11.

Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Windows DNS Server (CVE-2026-62878). This wormable vulnerability allows a remote unauthenticated attacker to execute code on a vulnerable server with elevated privileges. It is recommended to test and install the update as soon as possible, especially on Internet-facing DNS servers.

🔹 RCE - Windows Deployment Services TFTP Server (CVE-2026-62893). This vulnerability, discovered as part of the ZDI (Zero Day Initiative) program, allows an attacker to execute code without authentication or user interaction. TFTP has no authentication mechanism and is available remotely via UDP port 69. Any WDS server serving Windows Imaging Format (WIM) files via TFTP, which is the standard PXE boot scenario, is vulnerable. The issue results from the lack of validation of the existence of an object before performing operations on it. UDP port 69 should be blocked at the perimeter, but attackers could easily use this vulnerability for lateral movement within an organization. If you're using WDS for deployments, test and install this update quickly.

🔹 RCE - Windows DHCP Server (CVE-2026-62823). Successful exploitation of this vulnerability allows a remote unauthenticated attacker to execute arbitrary code from an adjacent network by sending a specially crafted packet that triggers a heap-based buffer overflow.

🔹 EoP - Microsoft Exchange (CVE-2026-62911). This vulnerability allows a remote authenticated attacker (with Privileges Required: Low according to CVSS) to gain control over the mailboxes of all Exchange users, send and read emails, and download attachments. This vulnerability was demonstrated at Pwn2Own Berlin. ZDI researchers provided Microsoft with working exploits.

🔹 RCE - Microsoft QUIC (CVE-2026-62815). This use-after-free vulnerability allows an unauthenticated attacker to execute arbitrary code on a target system by sending a specially crafted network packet. QUIC is an IETF-standardized transport protocol that runs over UDP instead of TCP and serves as the foundation for HTTP/3. The protocol is used by approximately 13.5 million websites.

🔹 Tampering - Windows Container Isolation FS Filter Driver (unionfs.sys) (CVE-2026-72971). This vulnerability reportedly allows an attacker to overwrite certain files. As a result, an attacker could perform an action within a container that could impact the host system.

🗒 Full Vulristics report

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability. Information about this vulnerability was disclosed as part of the June Microsoft Patch Tuesday on June 9. The vulnerability was not specifically highlighted in Microsoft Patch Tuesday reviews published by VM vendors. This Microsoft Windows NT OS Kernel elevation of privilege vulnerability is caused by improper handling of integer values during data construction in the Windows Management Instrumentation (WMI) subsystem, resulting in an out-of-bounds write. Successful exploitation allows a local attacker with low privileges (a standard user account) to escalate privileges to NT AUTHORITY\SYSTEM. Obtaining NT AUTHORITY\SYSTEM privileges grants full control over the affected host, enabling an attacker to execute arbitrary commands, modify security settings, access protected data, and use the compromised host as a foothold for further lateral movement within the target environment.

🛠 On July 7, a detailed write-up describing the exploitation of this vulnerability was published. A public proof-of-concept (PoC) exploit is also available on GitHub.

👾 There is currently no evidence of in-the-wild exploitation of this vulnerability.

July Microsoft Patch Tuesday

July Microsoft Patch Tuesday

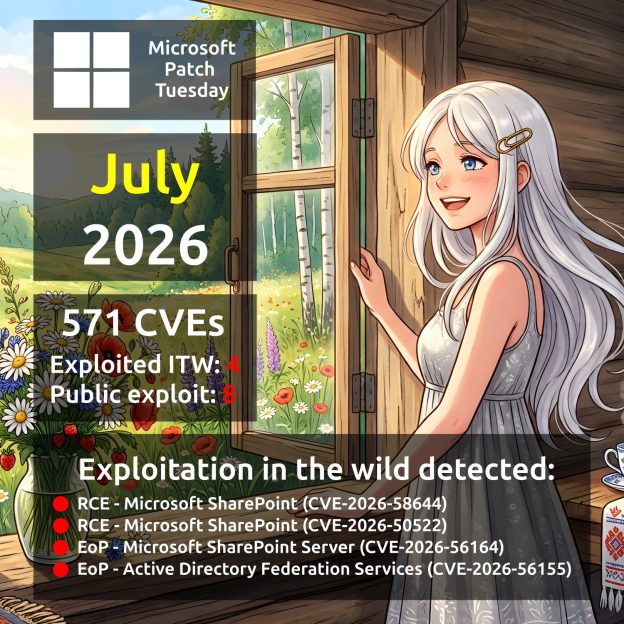
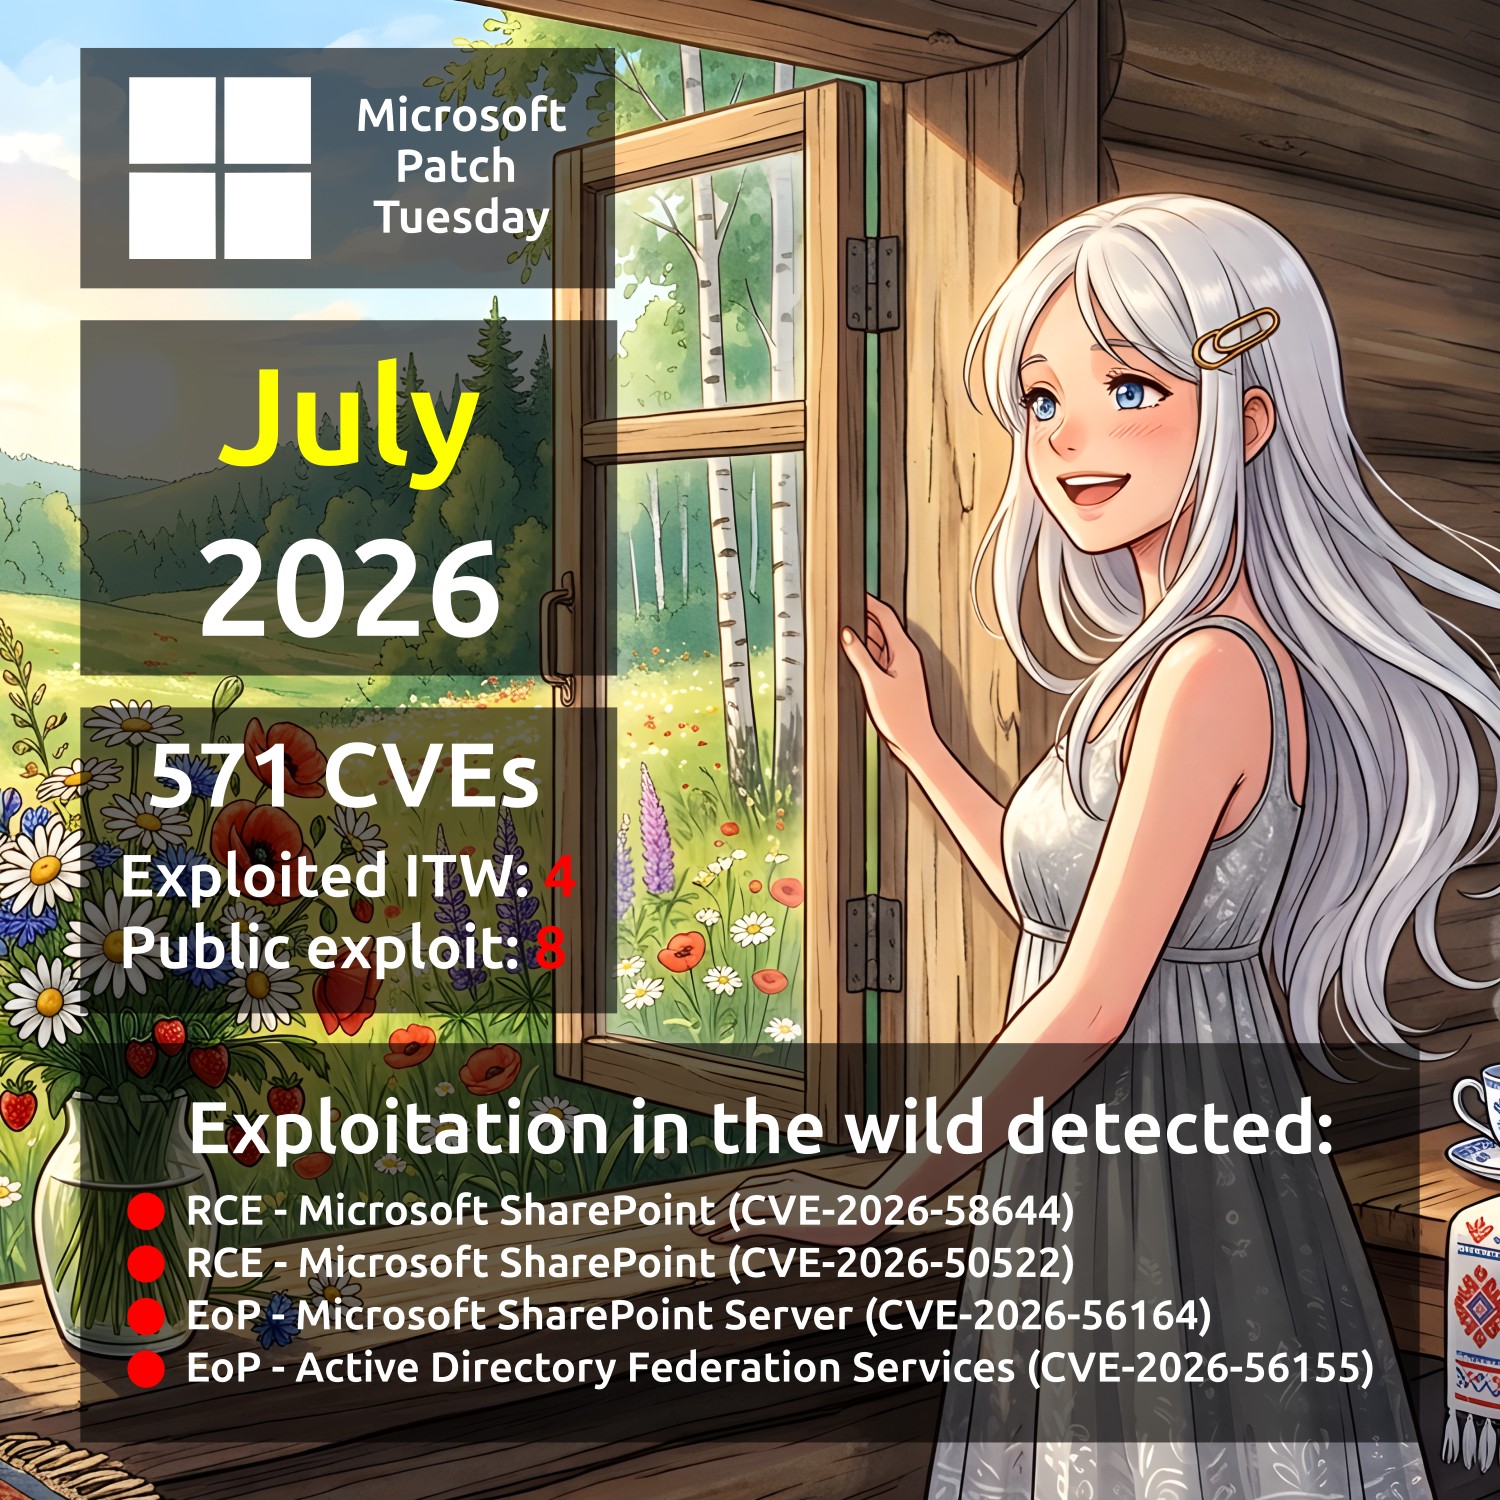
July Microsoft Patch Tuesday. In the second week of July, I was on vacation in St. Petersburg. After that, I got caught up with a bunch of other tasks, so I'm only publishing this roundup now. Better late than never, especially considering how unusual this MSPT turned out to be. 😉 In total, 571 vulnerabilities were addressed - almost three times (❗️) more than in June. There are four vulnerabilities that have been reported as exploited in the wild:

🔻 RCE - Microsoft SharePoint (CVE-2026-58644). An attacker with Site Owner privileges or higher can remotely inject and execute arbitrary code on the SharePoint Server.

🔻 RCE - Microsoft SharePoint (CVE-2026-50522). The vulnerability description is identical to CVE-2026-58644. According to ZDI, the CVE-2026-50522 vulnerability was successfully demonstrated at Pwn2Own Berlin. Despite this, Microsoft rates its Exploit Maturity as "Unknown", even though researchers have already provided a working exploit to the company. This once again shows that organizations should not rely solely on software vendors' assessments and should instead perform their own risk evaluation. If you have Internet-facing SharePoint servers, you should test and deploy the patch addressing this vulnerability as soon as possible.

🔻 EoP - Microsoft SharePoint Server (CVE-2026-56164). Missing authentication for a critical function in Microsoft Office SharePoint could allow an unauthenticated attacker to elevate privileges over a network. Microsoft mentioned in the advisory that enabling the Antimalware Scan Interface (AMSI) on the server and setting the Request Body Scan mode to Full can help mitigate this flaw.

🔻 EoP - Active Directory Federation Services (CVE-2026-56155). Insufficient granularity of access control (CWE-1220) in Active Directory Federation Services (AD FS) allows an authorized attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain administrator privileges.

There are eight more vulnerabilities with publicly available exploits:

🔸 EoP - Windows User Interface Core (CVE-2026-50454). Relative path traversal (CWE-23) allows an authorized attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. The PoC starts from a normal, non-elevated process belonging to a local administrator and opens an interactive command prompt as NT AUTHORITY\SYSTEM.

🔸 EoP - Windows WalletService (CVE-2026-49176). Improper privilege management (CWE-269) allows an authorized attacker to elevate privileges locally. The exploit PoC starts a command prompt as SYSTEM in the active desktop session.

🔸 RCE - Microsoft Message Queuing Queue Manager (CVE-2026-54992). The existing exploit PoC demonstrates denial of service; it does not demonstrate code execution.

🔸 EoP - Windows Narrator Braille (CVE-2026-58635). According to Microsoft's description, an attacker who successfully exploited this vulnerability could execute code in the security context of the NT AUTHORITY\Network Service account. However, the description of the exploit PoC states that an unprivileged attacker would gain NT AUTHORITY\SYSTEM privileges.

🔸 EoP - Windows Cloud Files Mini Filter Driver (CVE-2026-58613). Use after free (CWE-416) in the Windows Cloud Files Mini Filter Driver allows an authorized attacker to elevate privileges locally. An attacker who successfully exploits this vulnerability can gain SYSTEM privileges. Exploitation details are available in the Talos Vulnerability Report TALOS-2026-2426.

🔸 InfDisc - Windows Win32k (CVE-2026-50416). An attacker who successfully exploited this vulnerability could potentially read small portions of heap memory. The exploit PoC description mentions Chrome tabs, Discord, Explorer, Spotify, and tray windows. However, it seems that it will not be possible to intercept passwords using this vulnerability.

🔸 InfDisc - Windows Kernel (CVE-2026-50475). A buffer over-read (CWE-126) in the Windows Kernel allows an authorized attacker to disclose information locally. Exploitation details are available in the Talos Vulnerability Report TALOS-2026-2443.

🔸 EoP - Azure Spring Apps (CVE-2026-50338). An attacker who successfully exploited this vulnerability could gain elevated privileges, potentially allowing them to perform actions beyond their original permissions. According to the author of the exploit PoC, the vulnerability is a Spring Cloud Azure B2C resource server cross-issuer authentication bypass.

Among the remaining vulnerabilities, the following can be highlighted:

🔹 RCE - Windows Remote Desktop Protocol (CVE-2026-56190). An unauthenticated, network-reachable, no user interaction required vulnerability. The root cause is a classic one: the use of an uninitialized resource (CWE-908), meaning specially crafted RDP traffic can interact with memory that was never properly initialized, letting an attacker corrupt memory and potentially steer code execution. RDP Servers are a common target, so audit your systems to see which are internet accessible and start from there.

🔹 RCE - Microsoft Dynamics NAV and Microsoft Dynamics 365 Business Central (On Premises) (CVE-2026-55944). Successful exploitation can be achieved by sending a crafted login request to an affected Dynamics NAV or Business Central server in order to trigger a deserialization of untrusted data vulnerability. Microsoft's advisory cautions that no user-interaction is required, nor is authentication a requirement in order to successfully exploit this vulnerability.

🔹 EoP - Microsoft Windows VMSwitch (CVE-2026-57092). It's a use-after-free that lets a low-privileged attacker escalate to full host compromise across a VM boundary. ZDI reported that a similar exploit was demonstrated on ESXi at Pwn2Own Berlin, but this issue is not limited to ESXi. If you use VMSwitch in Hyper-V deployments (which is likely), test and deploy the fix quickly.

🔹 Spoofing - Microsoft Exchange (CVE-2026-55008). An attacker can send a specially crafted email that runs arbitrary JavaScript when the victim opens it in OWA. No attachment or macro is required - simply viewing the email is enough. If your organization uses OWA, it is recommended to test and deploy the fix as soon as possible.

🔹 RCE - Windows DHCP Server (CVE-2026-50518, CVE-2026-56159, CVE-2026-48564, CVE-2026-50370), Windows DHCP Client (CVE-2026-54128), Windows Message Queuing Service (MSMQ) (CVE-2026-50447), Windows Admin Center (WAC) (CVE-2026-56196), Windows FTP Service (CVE-2026-49172), Windows GDI+ (CVE-2026-50380), Windows Server Network driver (CVE-2026-56188), Microsoft Exchange (CVE-2026-55005), Windows Active Directory Domain Services (CVE-2026-49178), Windows Remote Desktop Client (CVE-2026-50474), Windows Remote Desktop Client (CVE-2026-54990, CVE-2026-58594), Windows TCP/IP (CVE-2026-54999), Windows Print Spooler (CVE-2026-58608), Windows Reliable Multicast Transport Driver (RMCAST) (CVE-2026-54982, CVE-2026-54995), Microsoft SQL Server (CVE-2026-54117), Microsoft Copilot (CVE-2026-48561).

🔹 SFB - Microsoft SharePoint Server (CVE-2026-55040).

🔹 EoP - Windows Server Update Service (WSUS) (CVE-2026-50444), Active Directory Certificate Services (CVE-2026-54121).

There is also a rather curious vulnerability:

RCE - Game: Age of Empires II: Definitive Edition (CVE-2026-50663). 😃 A relative path traversal in Age of Empires II: Definitive Edition Game allows an unauthorized attacker to execute code over a network. Age of Empires II is a cult classic real-time strategy game by Microsoft, set in the medieval era. Players develop chosen civilizations, manage resources, research technologies, and command armies in historical campaigns and multiplayer battles. The Definitive Edition features improved graphics, updated audio, and additional content. If you're still playing this game, be sure to update. 😉

🗒 Full Vulristics Report

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday. Last week I was on vacation in Veliky Novgorod, so I'm publishing this overview only now. A total of 202 vulnerabilities were addressed, approximately twice as many as in May. There are currently no vulnerabilities marked as exploited in the wild. However, there are two vulnerabilities with publicly available exploits:

🔸 RCE - HTTP.sys (CVE-2026-47291). This critical vulnerability allows remote, unauthenticated attackers to execute arbitrary code on affected systems without user interaction. However, systems using the default MaxRequestBytes registry value in the Windows HTTP stack are not affected. If needed, you can change this registry setting to protect systems while testing and deploying the patch. Microsoft's security bulletin includes instructions and a PowerShell script for this workaround.

🔸 DoS - HTTP.sys (CVE-2026-49160). The same exploit is used as for the previous RCE vulnerability.

It is also worth paying attention to vulnerabilities that Microsoft has flagged as having a publicly available exploit:

🔹 SFB - Windows BitLocker (CVE-2026-50507). A successful attacker could bypass the BitLocker Device Encryption feature on the system storage device. An attacker with physical access to the target could exploit this vulnerability to gain access to encrypted data. According to Tenable, this is the "Bitskrieg" vulnerability discovered by the researcher known as Chaotic Eclipse/Nightmare Eclipse.

🔹 SFB - Secure Boot (CVE-2026-48570). An attacker who successfully exploited this vulnerability could bypass Secure Boot. This vulnerability was reported by Alon Leviev (STORM), who is known for previous research related to BootKitty and BlackLotus.

Among the remaining vulnerabilities, the following are worth highlighting:

🔹 RCE - Windows Kernel (CVE-2026-45657). This vulnerability allows remote, unauthenticated attackers to run code with SYSTEM privileges without any user interaction. In other words, it could be used to spread automatically between systems. The issue is caused by how the Windows kernel processes TCP/IP traffic. Microsoft rated this as "Exploitation Less Likely", but security researchers and exploit developers are already analyzing the patch and trying to build an exploit. Test and deploy this patch as soon as possible.

🔹 EoP - Windows Collaborative Translation Framework (CTFMON) (CVE-2026-45586). This vulnerability affects a component used for voice and handwriting recognition. If exploited, an attacker could gain SYSTEM privileges. Microsoft rates this vulnerability as "Exploitation More Likely".

🔹 RCE - Windows Remote Desktop Client (CVE-2026-42909, CVE-2026-42913, CVE-2026-42985, CVE-2026-42992, CVE-2026-42993, CVE-2026-44799, CVE-2026-44801, CVE-2026-47289, CVE-2026-47653, CVE-2026-47654, CVE-2026-48563). Successful exploitation would require a victim to connect to an attacker-controlled server using an affected version of the Remote Desktop Client. This action could trigger a heap-based buffer overflow, resulting in remote code execution.

🔹 RCE - DHCP Client Service (CVE-2026-44815). This vulnerability allows remote, unauthenticated attackers to execute code on affected systems without user interaction. Because the DHCP client is widely enabled across Windows systems, this vulnerability presents a broad attack surface. Organizations should prioritize testing and deploying the patch for this vulnerability as soon as possible.

🗒 Full Vulristics report