
Tag Archives: RCE

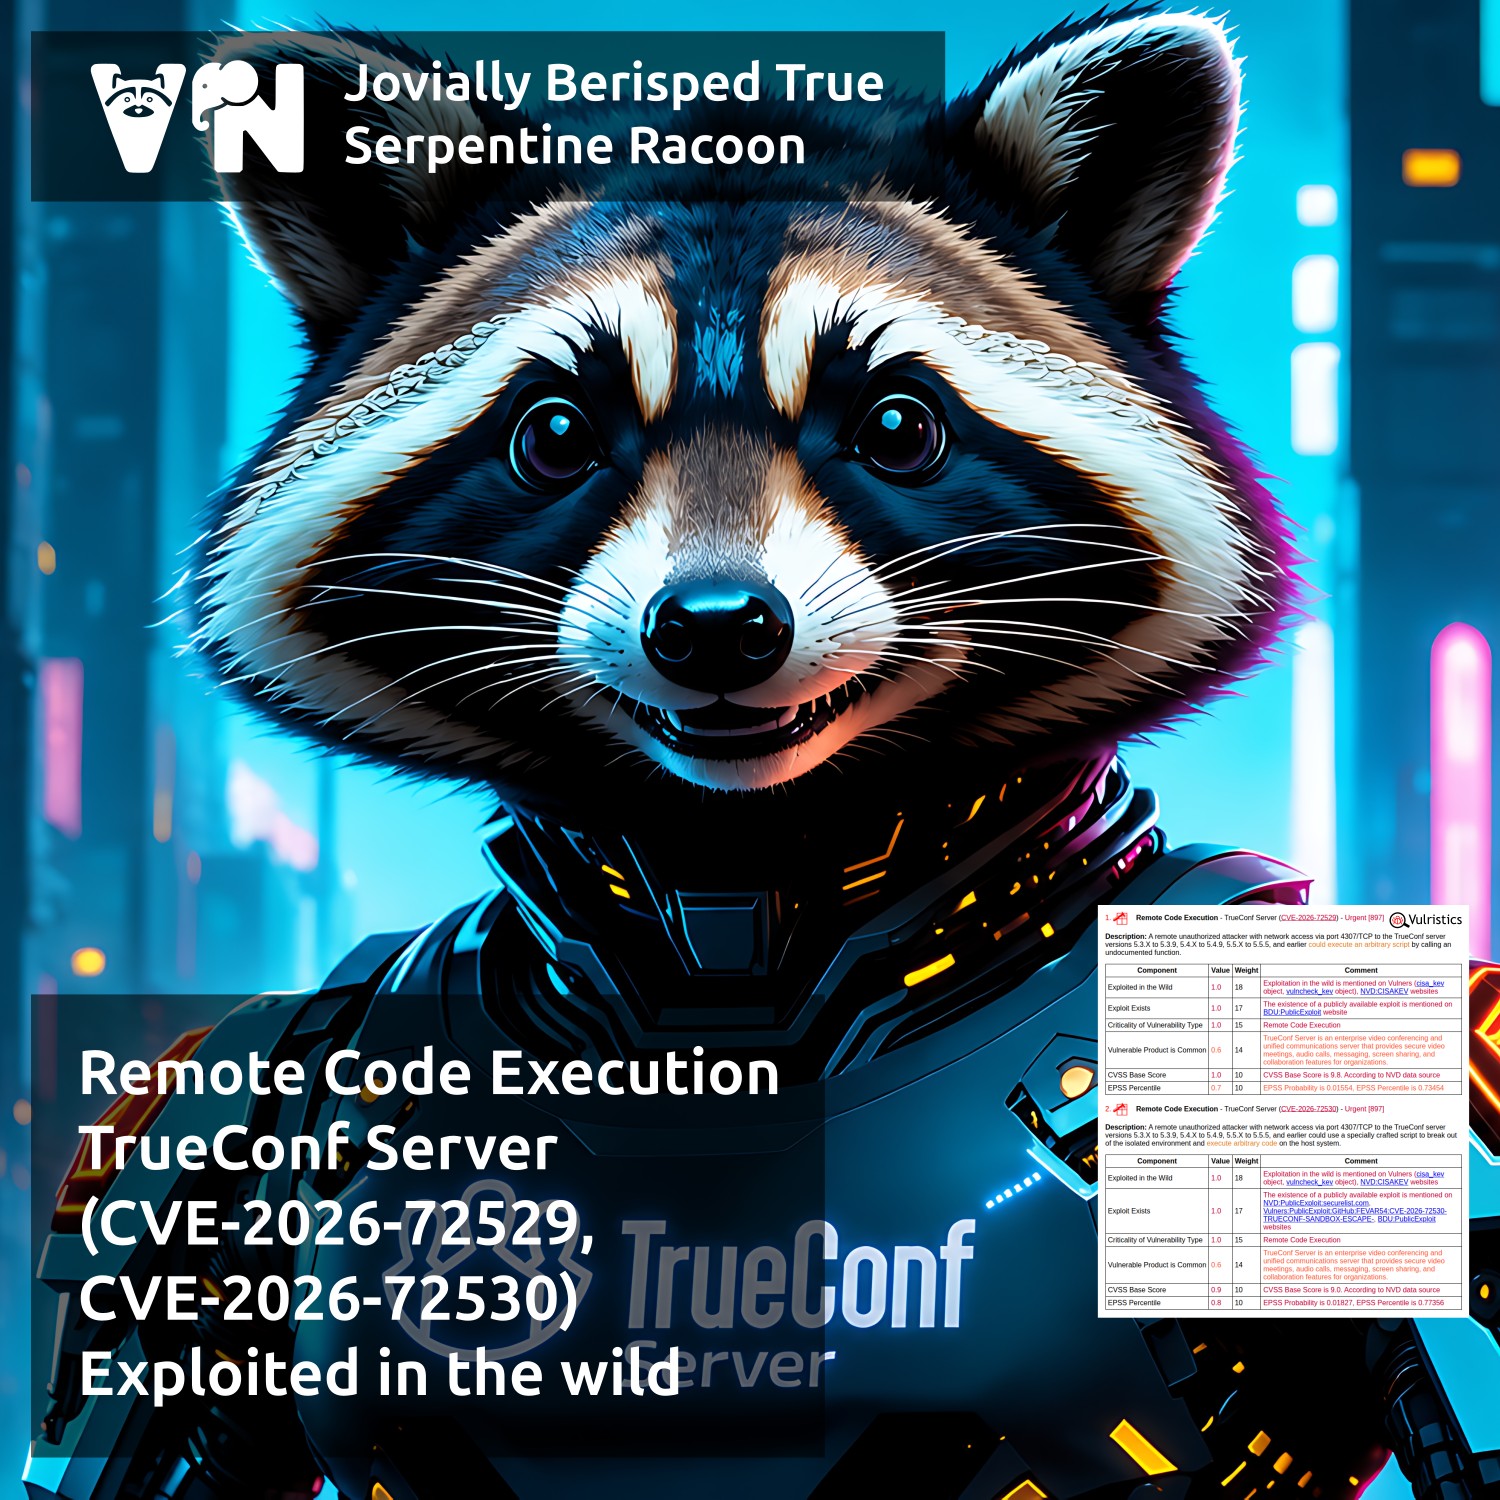
About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday. Last week I was on vacation in Veliky Novgorod, so I'm publishing this overview only now. A total of 202 vulnerabilities were addressed, approximately twice as many as in May. There are currently no vulnerabilities marked as exploited in the wild. However, there are two vulnerabilities with publicly available exploits:

🔸 RCE - HTTP.sys (CVE-2026-47291). This critical vulnerability allows remote, unauthenticated attackers to execute arbitrary code on affected systems without user interaction. However, systems using the default MaxRequestBytes registry value in the Windows HTTP stack are not affected. If needed, you can change this registry setting to protect systems while testing and deploying the patch. Microsoft's security bulletin includes instructions and a PowerShell script for this workaround.

🔸 DoS - HTTP.sys (CVE-2026-49160). The same exploit is used as for the previous RCE vulnerability.

It is also worth paying attention to vulnerabilities that Microsoft has flagged as having a publicly available exploit:

🔹 SFB - Windows BitLocker (CVE-2026-50507). A successful attacker could bypass the BitLocker Device Encryption feature on the system storage device. An attacker with physical access to the target could exploit this vulnerability to gain access to encrypted data. According to Tenable, this is the "Bitskrieg" vulnerability discovered by the researcher known as Chaotic Eclipse/Nightmare Eclipse.

🔹 SFB - Secure Boot (CVE-2026-48570). An attacker who successfully exploited this vulnerability could bypass Secure Boot. This vulnerability was reported by Alon Leviev (STORM), who is known for previous research related to BootKitty and BlackLotus.

Among the remaining vulnerabilities, the following are worth highlighting:

🔹 RCE - Windows Kernel (CVE-2026-45657). This vulnerability allows remote, unauthenticated attackers to run code with SYSTEM privileges without any user interaction. In other words, it could be used to spread automatically between systems. The issue is caused by how the Windows kernel processes TCP/IP traffic. Microsoft rated this as "Exploitation Less Likely", but security researchers and exploit developers are already analyzing the patch and trying to build an exploit. Test and deploy this patch as soon as possible.

🔹 EoP - Windows Collaborative Translation Framework (CTFMON) (CVE-2026-45586). This vulnerability affects a component used for voice and handwriting recognition. If exploited, an attacker could gain SYSTEM privileges. Microsoft rates this vulnerability as "Exploitation More Likely".

🔹 RCE - Windows Remote Desktop Client (CVE-2026-42909, CVE-2026-42913, CVE-2026-42985, CVE-2026-42992, CVE-2026-42993, CVE-2026-44799, CVE-2026-44801, CVE-2026-47289, CVE-2026-47653, CVE-2026-47654, CVE-2026-48563). Successful exploitation would require a victim to connect to an attacker-controlled server using an affected version of the Remote Desktop Client. This action could trigger a heap-based buffer overflow, resulting in remote code execution.

🔹 RCE - DHCP Client Service (CVE-2026-44815). This vulnerability allows remote, unauthenticated attackers to execute code on affected systems without user interaction. Because the DHCP client is widely enabled across Windows systems, this vulnerability presents a broad attack surface. Organizations should prioritize testing and deploying the patch for this vulnerability as soon as possible.

🗒 Full Vulristics report

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper. Hello everyone! This month I decided NOT to make an episode completely dedicated to Microsoft Patch Tuesday. Instead, this episode will be an answer to the question of how my Vulnerability Management month went. A retrospection of some kind.

Alternative video link (for Russia): https://vk.com/video-149273431_456239134

Continue reading →

Microsoft Patch Tuesday July 2023: Vulristics improvements, Office RCE, SFB SmartScreen and Outlook, EoP MSHTML and ERS, other RCEs

Microsoft Patch Tuesday July 2023: Vulristics improvements, Office RCE, SFB SmartScreen and Outlook, EoP MSHTML and ERS, other RCEs. Hello everyone! This episode will be about Microsoft Patch Tuesday for July 2023, including vulnerabilities that were added between June and July Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239131

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities.

Continue reading →

Microsoft Patch Tuesday June 2023: Edge type confusion, Git RCE, OneNote Spoofing, PGM RCE, Exchange RCE, SharePoint EoP

Microsoft Patch Tuesday June 2023: Edge type confusion, Git RCE, OneNote Spoofing, PGM RCE, Exchange RCE, SharePoint EoP. Hello everyone! This episode will be about Microsoft Patch Tuesday for June 2023, including vulnerabilities that were added between May and June Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239127

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Tenable, Rapid7, ZDI Patch Tuesday reviews. This time there were only 3 vulnerabilities used in attacks or with a public exploit. And only one of them is more or less relevant.

Continue reading →

Microsoft Patch Tuesday May 2023: Microsoft Edge, BlackLotus Secure Boot SFB, OLE RCE, Win32k EoP, NFS RCE, PGM RCE, LDAP RCE, SharePoint RCE

Microsoft Patch Tuesday May 2023: Microsoft Edge, BlackLotus Secure Boot SFB, OLE RCE, Win32k EoP, NFS RCE, PGM RCE, LDAP RCE, SharePoint RCE. Hello everyone! This episode will be about Microsoft Patch Tuesday for May 2023, including vulnerabilities that were added between April and May Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239126

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Tenable, Rapid7, ZDI Patch Tuesday reviews.

It’s been a long time since we’ve had such tiny Patch Tuesday. 57 CVEs, including CVEs appeared during the month. And only 38 without them! 😄

Continue reading →

Microsoft Patch Tuesday April 2023: CLFS EoP, Word RCE, MSMQ QueueJumper RCE, PCL6, DNS, DHCP

Microsoft Patch Tuesday April 2023: CLFS EoP, Word RCE, MSMQ QueueJumper RCE, PCL6, DNS, DHCP. Hello everyone! This episode will be about Microsoft Patch Tuesday for April 2023, including vulnerabilities that were added between March and April Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239123

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Tenable, Rapid7, ZDI Patch Tuesday reviews. And this is the first Patch Tuesday report since I added EPSS support to Vulristics. 😉

Compared to March, Microsoft Patch Tuesday for April 2023 is kind of weak. 🙄

Continue reading →