Tag Archives: Kaspersky

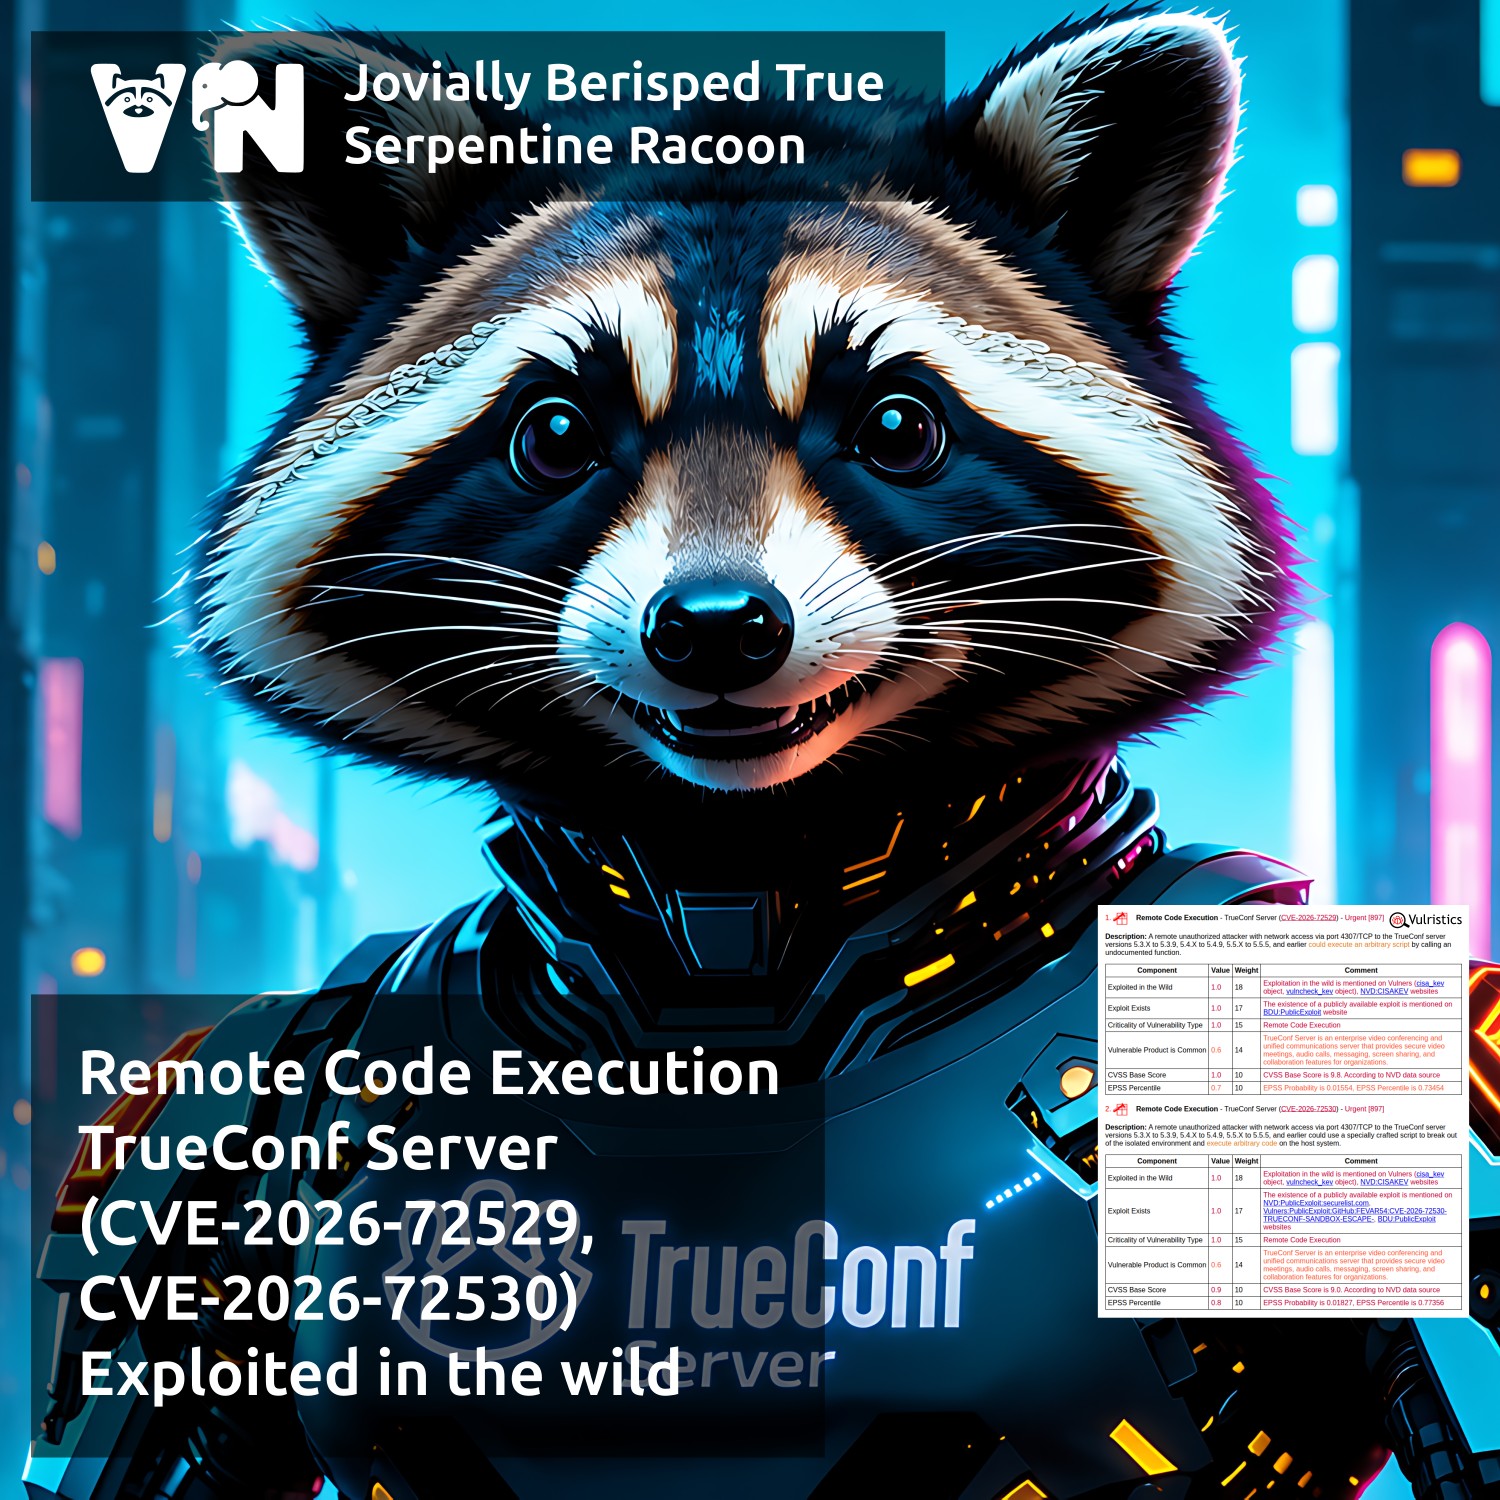
About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.
New episode "In The Trend of VM" (#10): 8 trending vulnerabilities of November, zero budget VM and who should look for patches

New episode "In The Trend of VM" (#10): 8 trending vulnerabilities of November, zero budget VM and who should look for patches. The competition for the best question on the topic of VM continues. 😉🎁

📹 Video on YouTube, LinkedIn
🗞 Post on Habr (rus)
🗒 Digest on the PT website

Content:

🔻 00:29 Spoofing - Windows NTLM (CVE-2024-43451)
🔻 01:16 Elevation of Privilege - Windows Task Scheduler (CVE-2024-49039)
🔻 02:16 Spoofing - Microsoft Exchange (CVE-2024-49040)
🔻 03:03 Elevation of Privilege - needrestart (CVE-2024-48990)
🔻 04:11 Remote Code Execution - FortiManager "FortiJump" (CVE-2024-47575)
🔻 05:19 Authentication Bypass - PAN-OS (CVE-2024-0012)
🔻 06:32 Elevation of Privilege - PAN-OS (CVE-2024-9474)
🔻 07:42 Path Traversal - Zyxel firewall (CVE-2024-11667)
🔻 08:37 Is it possible to Manage Vulnerabilities with no budget?
🔻 09:53 Should a VM specialist specify a patch to install on the host in a Vulnerability Remediation task?
🔻 10:51 Full digest of trending vulnerabilities
🔻 11:18 Backstage

На русском

About Spoofing - Microsoft Exchange (CVE-2024-49040) vulnerability

About Spoofing - Microsoft Exchange (CVE-2024-49040) vulnerability

About Spoofing - Microsoft Exchange (CVE-2024-49040) vulnerability. The vulnerability is from the November Microsoft Patch Tuesday. An incorrectly formulated P2 FROM header processing policy allows an attacker to make his email address look legitimate to the victim (for example, like a work colleague's address). Which, of course, significantly increases the effectiveness of phishing attacks. 😏🪝 The vulnerabilities affect Exchange Server 2019 and Exchange Server 2016.

Microsoft has paused the rollout of the initial patches published on November 12. Their installation led to crashes. New fixes were published by Microsoft only on November 27.

👾 Kaspersky has already observed attempts to exploit this vulnerability. They wrote about this in a blog post on November 26.

На русском

Attackers are distributing malware on social networks under the guise of the regreSSHion exploit (CVE-2024-6387)

Attackers are distributing malware on social networks under the guise of the regreSSHion exploit (CVE-2024-6387)

Attackers are distributing malware on social networks under the guise of the regreSSHion exploit (CVE-2024-6387). According to Kaspersky Lab experts, this is an attack on cybersecurity specialists. The attackers invite victims to examine an archive that supposedly contains a functional regreSSHion exploit, a list of IP addresses, and some payload.

🔻 The source code resembles a slightly edited version of a non-functional proof-of-concept exploit for this vulnerability that was already public.

🔻 One of the Python scripts simulates the exploitation of the vulnerability on IP addresses from the list. But in reality, it launches malware that achieves persistence in the system and downloads additional payload. The malware modifies /etc/cron.hourly and the operation of the ls command.

If you are examining someone else's code, do so in a securely isolated environment and be aware that you may be attacked this way. 😉

На русском

Microsoft Patch Tuesday July 2023: Vulristics improvements, Office RCE, SFB SmartScreen and Outlook, EoP MSHTML and ERS, other RCEs

Microsoft Patch Tuesday July 2023: Vulristics improvements, Office RCE, SFB SmartScreen and Outlook, EoP MSHTML and ERS, other RCEs. Hello everyone! This episode will be about Microsoft Patch Tuesday for July 2023, including vulnerabilities that were added between June and July Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239131

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities.

Continue reading

Is it possible to detect Zero Day vulnerabilities with Vulnerability Management solutions?

Is it possible to detect Zero Day vulnerabilities with Vulnerability Management solutions? Hello everyone! In my English-language telegram chat avleonovchat, the question was asked: “How to find zero day vulnerabilities with Qualys?” Apparently this question can be expanded. Not just with Qualys, but with any VM solution in general. And is it even possible? There was an interesting discussion.

Alternative video link (for Russia): https://vk.com/video-149273431_456239109

Image generated by Stable Diffusion 2.1: “calendar on the wall cyber security vulnerability zero day”

The question is not so straightforward. To answer it, we need to define what a Zero Day vulnerability is. If we look at wikipedia, then historically “0” is the number of days a vendor has to fix a vulnerability.

“Eventually the term was applied to the vulnerabilities that allowed this hacking, and to the number of days that the vendor has had to fix them.”

Continue reading

Microsoft Patch Tuesday August 2022: DogWalk, Exchange EOPs, 13 potentially dangerous, 2 funny, 3 mysterious vulnerabilities

Microsoft Patch Tuesday August 2022: DogWalk, Exchange EOPs, 13 potentially dangerous, 2 funny, 3 mysterious vulnerabilities. Hello everyone! In this episode, let’s take a look at the Microsoft Patch Tuesday August 2022 vulnerabilities. I use my Vulristics vulnerability prioritization tool as usual. I take comments for vulnerabilities from Tenable, Qualys, Rapid7, ZDI and Kaspersky blog posts. Also, as usual, I take into account the vulnerabilities added between the July and August Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239098

There were 147 vulnerabilities. Urgent: 1, Critical: 0, High: 36, Medium: 108, Low: 2.

There was a lot of great stuff this Patch Tuesday. There was a critical exploited in the wild MSDT DogWalk vulnerability, 3 critical Exchange vulnerabilities that could be easily missed in prioritization, 13 potentially dangerous vulnerabilities, 2 funny vulnerabilities and 3 mysterious ones. Let’s take a closer look.

Continue reading