Tag Archives: CVE

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability

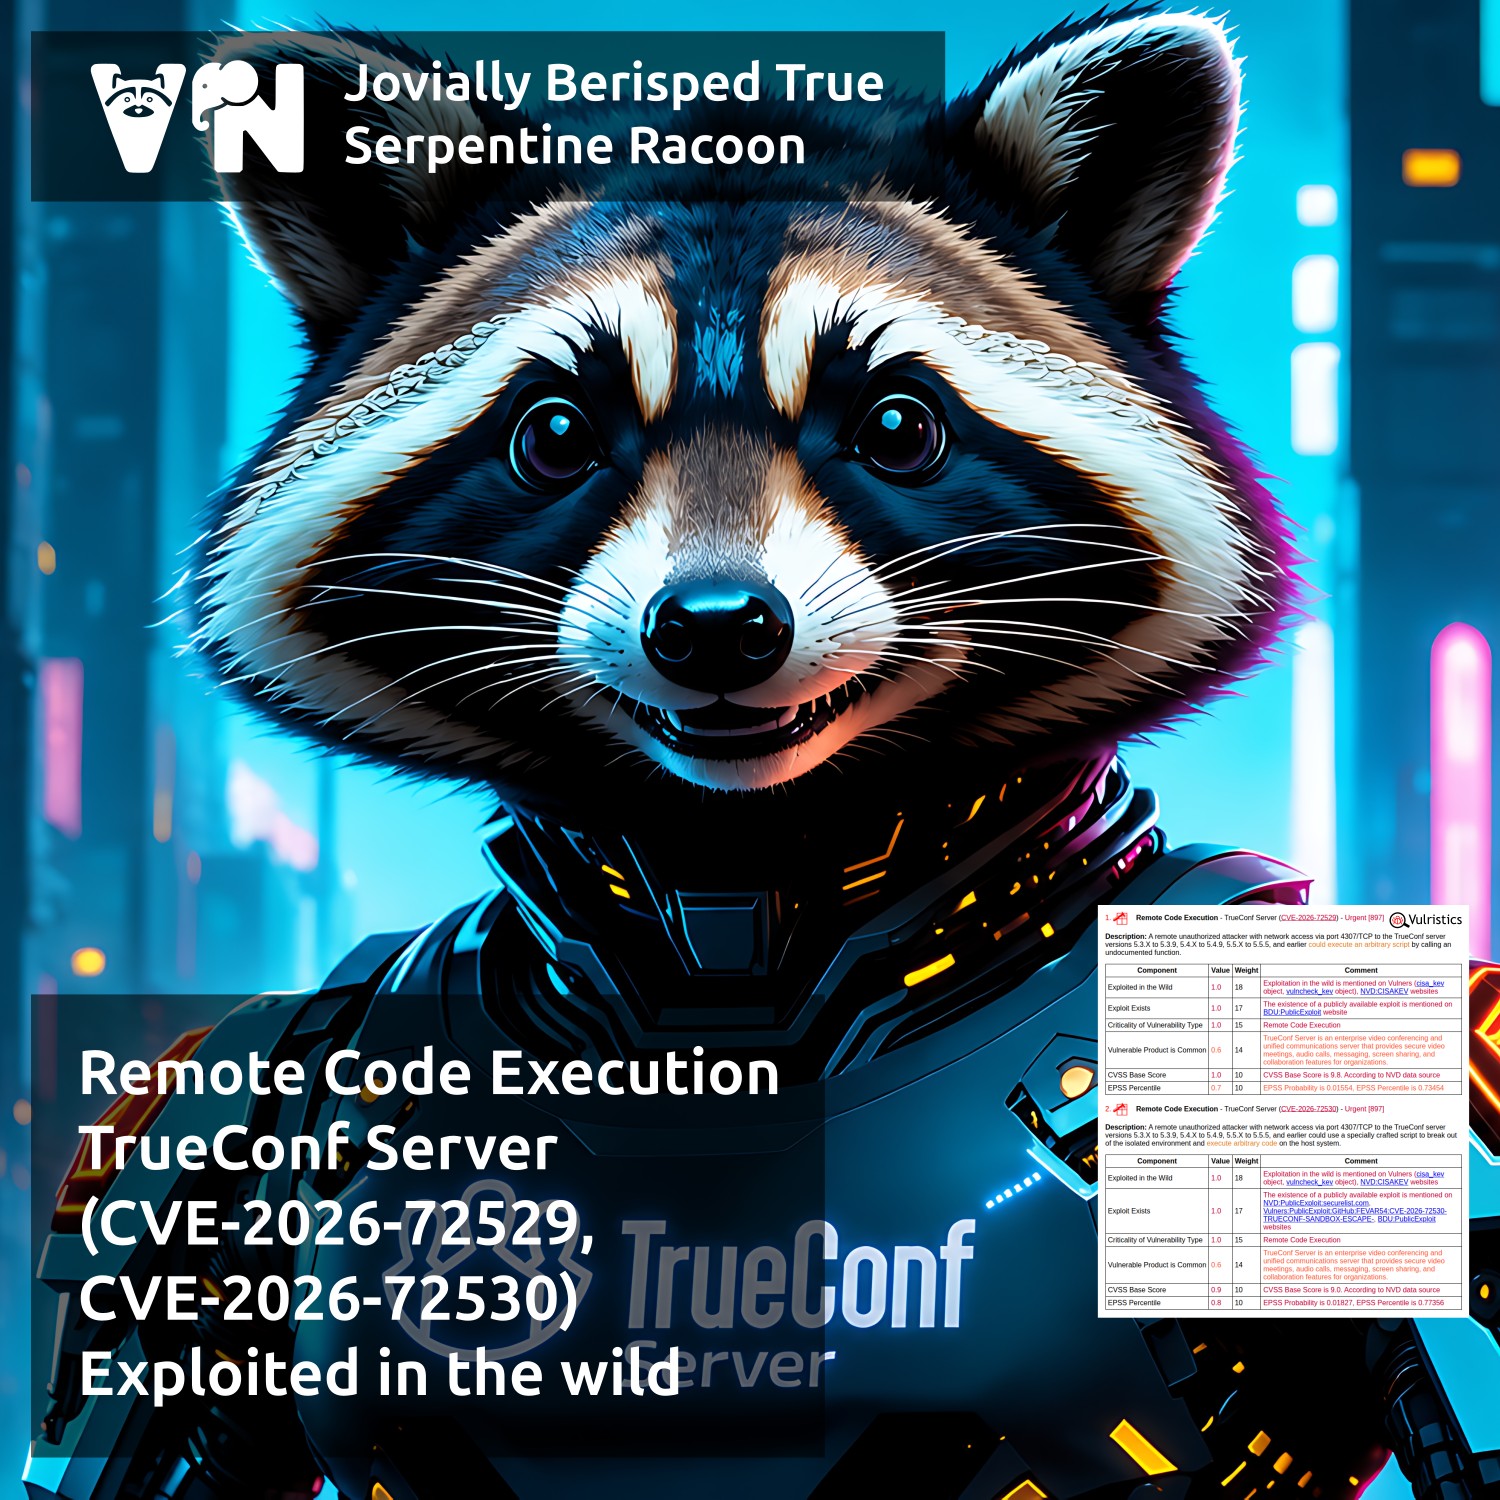
About Remote Code Execution - TrueConf Server (CVE-2026-72529, CVE-2026-72530) vulnerability. TrueConf Server is a Russian on-premises corporate messaging and UltraHD video conferencing platform. The attack chain consists of two critical vulnerabilities. The first vulnerability, CVE-2026-72529, is caused by missing authentication for a critical function (CWE-306) and allows an unauthenticated remote attacker with network access to TCP port 4307 (open by default, according to TrueConf documentation) to invoke an undocumented TrueConf Server function and execute an arbitrary script within an isolated environment ("sandbox") where potentially dangerous libraries are unavailable. The second vulnerability, CVE-2026-72530, allows an attacker to perform code injection (CWE-94), escape the isolated environment, and execute arbitrary code on the host operating system with the highest privileges. Among other things, an attacker can delete TrueConf event log entries associated with exploitation activity.

⚙️ Security fixes for these vulnerabilities were released on June 18, 2026. The affected versions are 5.3.x below 5.3.9, 5.4.x below 5.4.9, 5.5.x below 5.5.5, as well as the 5.2 branch and earlier versions (upgrading legacy versions requires contacting technical support). Re-registration of the server is not required when upgrading within the 5.3-5.5 branches. However, the vendor strongly recommends creating a backup before installing the update. If an immediate upgrade is not possible, access to TCP port 4307 should be restricted to trusted networks.

👾 Kaspersky ICS CERT experts have disclosed details of the vulnerability exploitation chain in a post published on August 12. Since July 2026, threat actors have been exploiting CVE-2026-72529 and CVE-2026-72530 in attacks targeting Russian organizations. The attackers first gained network access to TrueConf Server through TCP port 4307 and used CVE-2026-72529 to execute a script within the sandbox. They then exploited CVE-2026-72530 to escape the sandbox and execute code with NT AUTHORITY\SYSTEM privileges. This enabled them to replace one of the TrueConf Server files with a web shell of their own. The attackers then used the web shell to gather information about the organization's IT infrastructure, gain privileged access to the TrueConf Server database, and replace legitimate TrueConf Client installers with malicious versions containing the PhantomCore malware. Users were subsequently prompted to download what appeared to be a new version of the TrueConf Client, which was in fact malicious.

IMPORTANT: Even if your organization does not use TrueConf, your employees may have connected to compromised TrueConf servers used by contractors or business partners to participate in online conferences. In doing so, they may have inadvertently installed a malicious version of the TrueConf client on their workstations.

The PhantomCore malware, associated with the Head Mare APT group, launches automatically when the system starts and allows attackers to execute arbitrary commands, effectively giving them full control over the compromised host. Kaspersky researchers also identified a new backdoor used in the attacks, which they named PhantomGraph. Both vulnerabilities, CVE-2026-72529 and CVE-2026-72530, were added to the CISA KEV on August 20, 2026.

🛠 A public exploit for CVE-2026-72530 was published on GitHub on August 26. So far, no public exploit for the complete CVE-2026-72529/CVE-2026-72530 exploitation chain has been observed, despite the corresponding flags in the BDU FSTEC vulnerability database.

🌐 TrueConf Server is widely used both in Russia and internationally, including by government agencies, as well as organizations in the financial, industrial, healthcare, and education sectors.
Microsoft is beginning to add CVEs to address security flaws in its cloud services

Microsoft is beginning to add CVEs to address security flaws in its cloud services

Microsoft is beginning to add CVEs to address security flaws in its cloud services. It's not as straightforward. Assume a cloud CRM has a vulnerability. The vendor instantly corrected it for everyone, and clients didn't need to take any action. What good is it to issue a CVE for this? 🤔

But Microsoft believes it's required for greater transparency, and the new rules require CNAs (CVE Numbering Authorities) to add vulnerabilities that could cause significant harm, regardless of whether customers have to take action to fix the vulnerabilities or not. 🤷‍♂️

Microsoft promises to mark such vulnerabilities, such as CVE-2024-35260 "CVE requires no customer action to resolve". There will be a special tag in CVEorg as well.

Whether or not it is necessary to register cloud service vulnerabilities as CVE is a controversial issue. But it is a fact that, due to this practice, the number of identifiers in CVEorg/NVD will grow much faster. 🤷‍♂️

На русском

An idea worth a million Hamster coins

An idea worth a million Hamster coins

An idea worth a million Hamster coins. 🐹😅 Website/app to tap on CVEs. But it will make sense to tap not on all CVEs, but only on those that should have a confirmed exploit or sign of exploitation in the wild within the next week.

🪙 When such a sign or exploit does appear, distribute coins to those who have been tapping on this vulnerability for the last week. In proportion to the number of taps, the criticality of the vulnerability, etc.

📈 And based on the analysis of these taps, it will be possible to make forecasts on the exploitability of vulnerabilities. With the help of AI, of course.

I am sure that this will work much better than EPSS and social network fortune tellers. 😅

На русском

November 2023 - January 2024: New Vulristics Features, 3 Months of Microsoft Patch Tuesdays and Linux Patch Wednesdays, Year 2023 in Review

November 2023 – January 2024: New Vulristics Features, 3 Months of Microsoft Patch Tuesdays and Linux Patch Wednesdays, Year 2023 in Review. Hello everyone! It has been 3 months since the last episode. I spent most of this time improving my Vulristics project. So in this episode, let’s take a look at what’s been done.

Alternative video link (for Russia): https://vk.com/video-149273431_456239139

Also, let’s take a look at the Microsoft Patch Tuesdays vulnerabilities, Linux Patch Wednesdays vulnerabilities and some other interesting vulnerabilities that have been released or updated in the last 3 months. Finally, I’d like to end this episode with a reflection on how my 2023 went and what I’d like to do in 2024.

Continue reading →

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper. Hello everyone! This month I decided NOT to make an episode completely dedicated to Microsoft Patch Tuesday. Instead, this episode will be an answer to the question of how my Vulnerability Management month went. A retrospection of some kind.

Alternative video link (for Russia): https://vk.com/video-149273431_456239134

Continue reading →

How Debian OVAL content is structured

How Debian OVAL content is structured. Hello everyone! As we saw in the last episode, the results of vulnerability detection for one host produced by two different APIs can vary greatly. Therefore, in order to find out the truth, it is necessary to understand what vulnerability data is provided by the Linux distribution vendor and how this data is structured.

Alternative video link (for Russia): https://vk.com/video-149273431_456239114

Why is it important to do this? Because using data from a Linux distribution vendor, we can ask vulnerability detection API vendors questions: why are you detecting in a different way than described in this data? And then we will understand what caused the difference. And we will either adjust the API for vulnerability detection, or we will adjust the content of the Linux distribution vendor. Either way, it will be a success! In any case, the transparency of the vulnerability detection process will increase.

Last time we looked at vulnerabilities for Debian host and Debian Docker base image. So let’s continue with Debian. In particular, with the official Debian OVAL (Open Vulnerability and Assessment Language) content.

Debian OVAL content can be downloaded from the https://debian.org/security/oval/ website. For Debian 11.6 it will be https://debian.org/security/oval/oval-definitions-bullseye.xml (~48M).

Continue reading →

Vulristics May 2022 Update: CVSS redefinitions and bulk adding Microsoft products from MS CVE data

Vulristics May 2022 Update: CVSS redefinitions and bulk adding Microsoft products from MS CVE data. Hello everyone! In this episode, I want to talk about the latest updates to my open source vulnerability prioritization project Vulristics.

Alternative video link (for Russia): https://vk.com/video-149273431_456239088

CVSS redefinitions

A fairly common problem: we have a CVE without an available CVSS vector and score. For example, this was the case with CVE-2022-1364 Type Confusion in V8 (Chromium). This vulnerability does not exist in NVD.

Continue reading →