Category Archives: Vulnerability

About Remote Code Execution - GitLab (CVE-2026-110264) vulnerability

About Remote Code Execution - GitLab (CVE-2026-110264) vulnerability

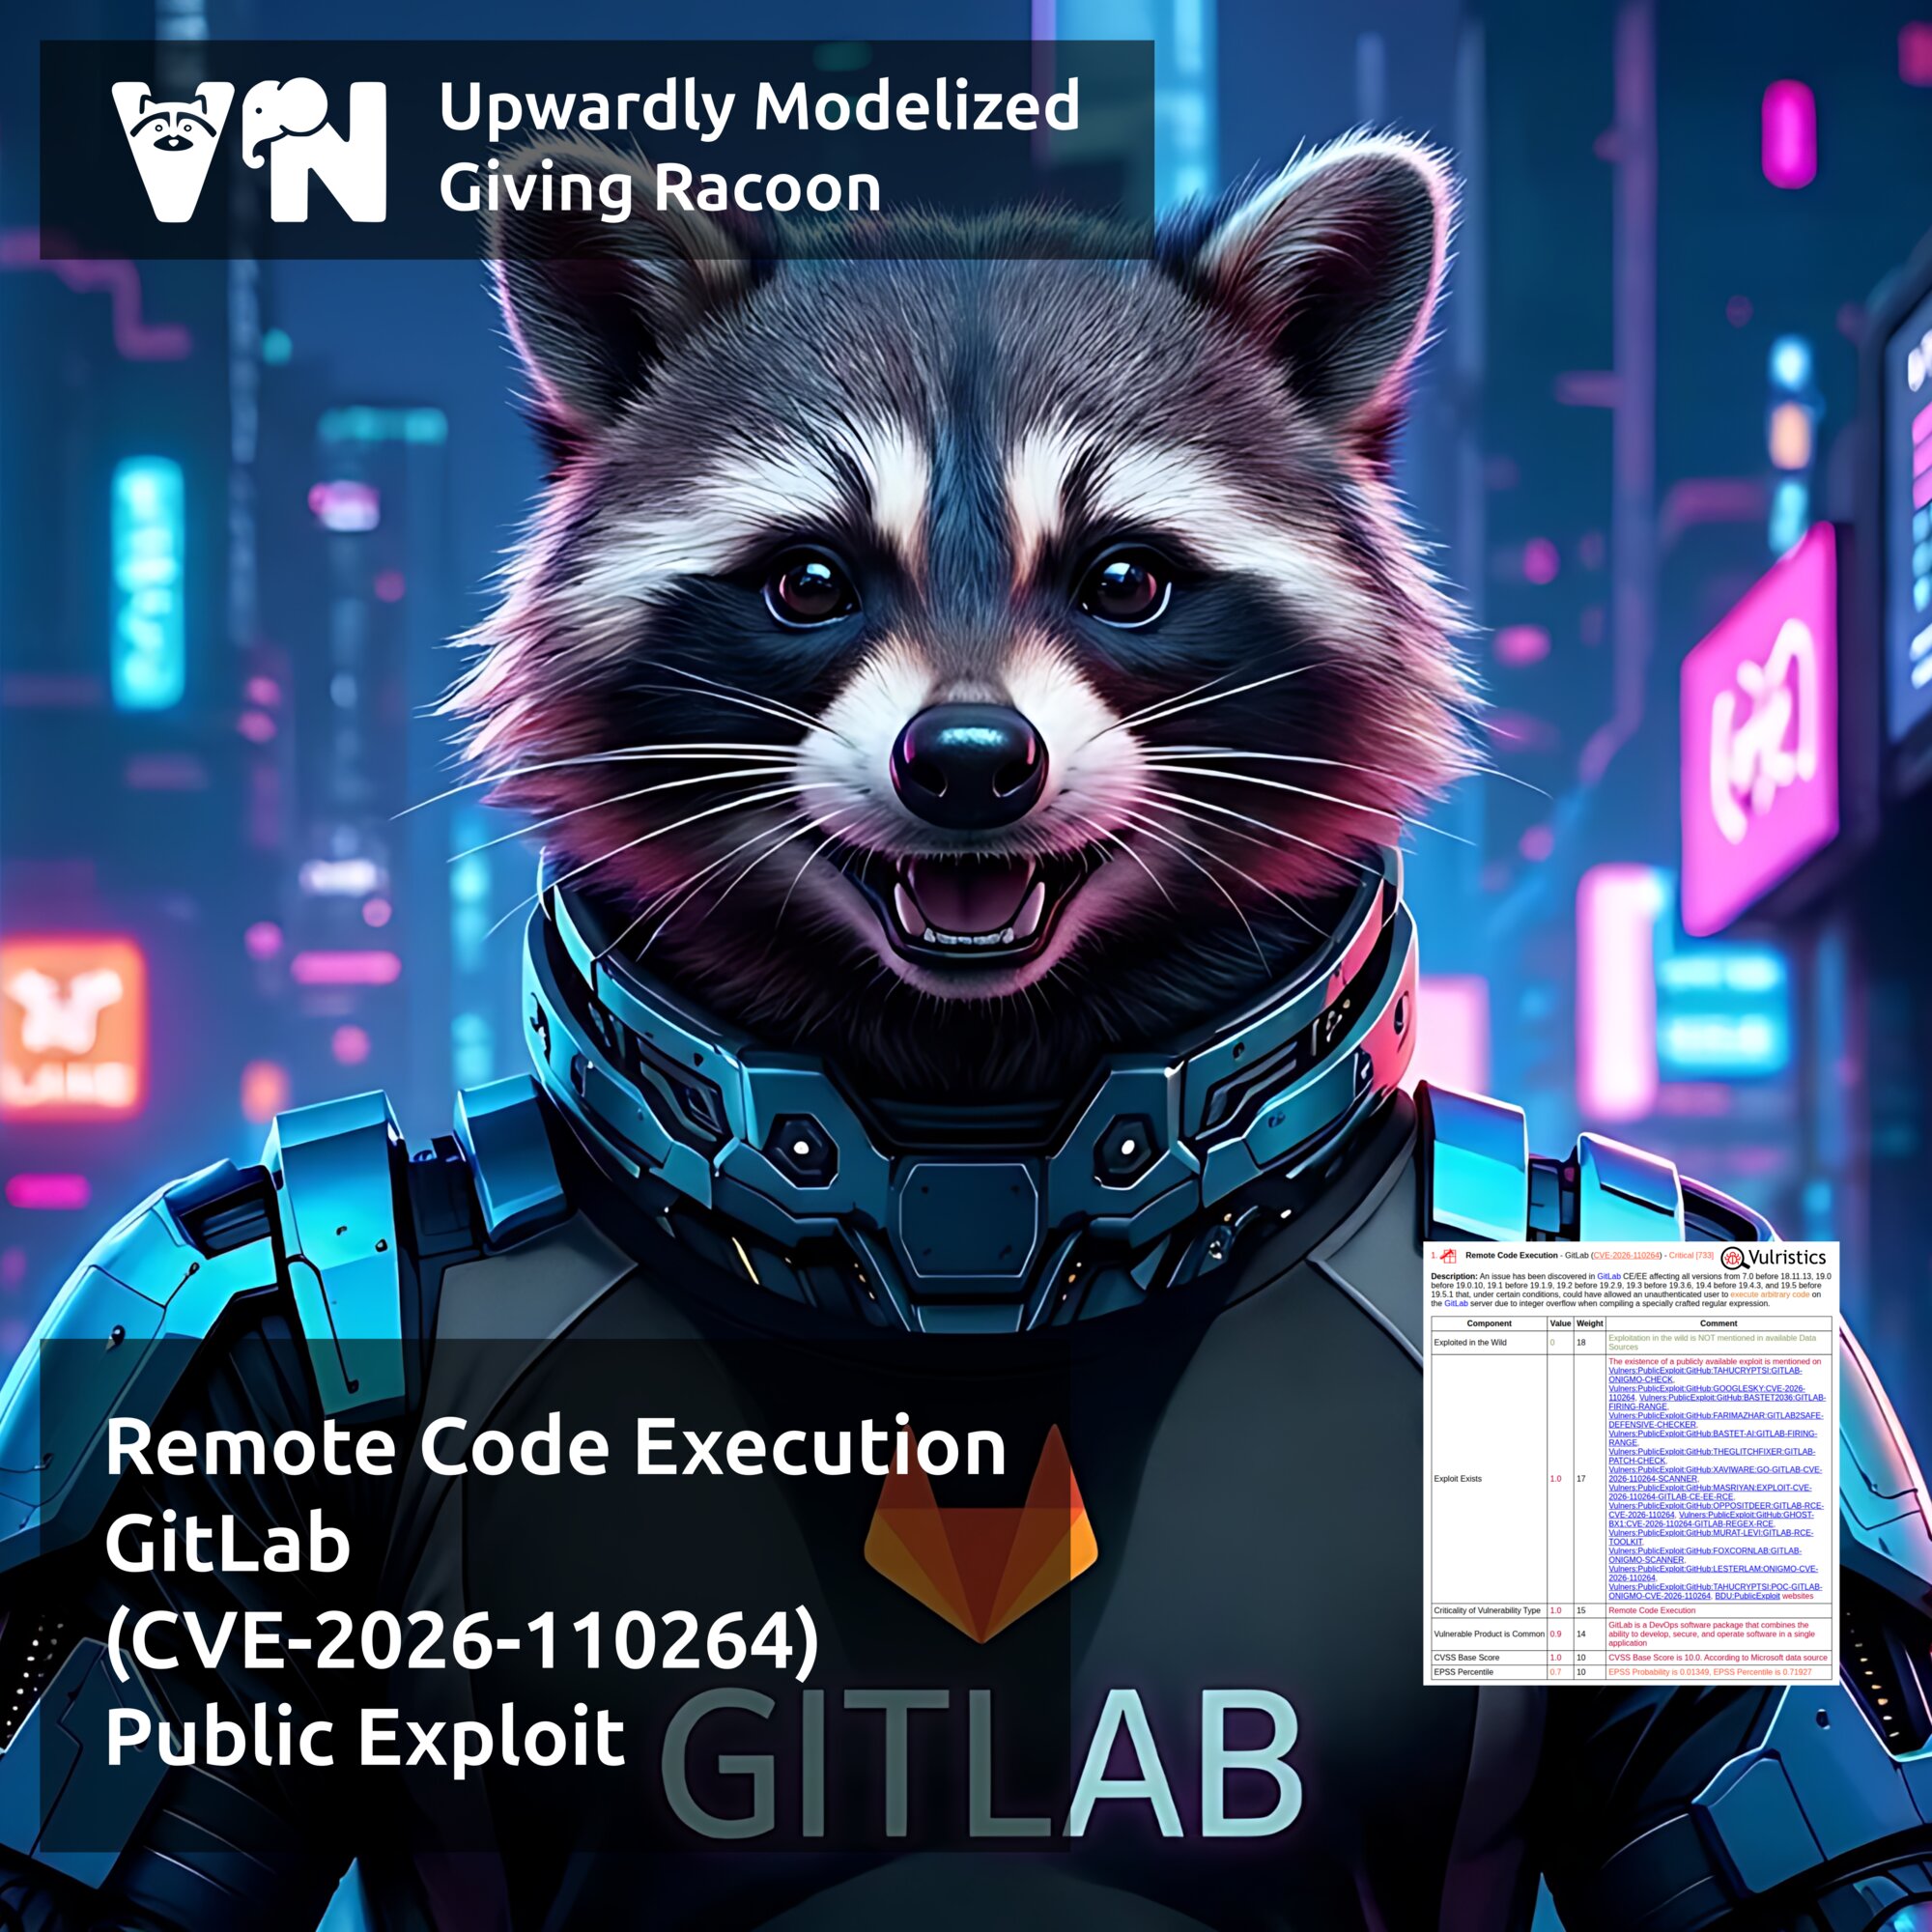
About Remote Code Execution - GitLab (CVE-2026-110264) vulnerability. GitLab is a platform for hosting code, collaborative software development, project management, and automating application testing and releases. GitLab CE is the free, open-source version of the platform, while GitLab EE is the enterprise version with additional features. Under certain conditions, the vulnerability in GitLab CE/EE allows an unauthenticated attacker to execute arbitrary code on the server. The vulnerability existed in GitLab for approximately 12 years and affected GitLab CE/EE versions 7.0 and later.

The vulnerability is caused by the following issue. GitLab uses the Ruby programming language to implement a significant part of its server-side logic. In particular, the platform's backend is built on Ruby on Rails, a web framework written in Ruby. Ruby also uses additional libraries and built-in components to perform various tasks. One of these is Onigmo, a regular expression engine responsible for searching and processing text based on predefined patterns. According to Censys research, the vulnerability is related to the processing of Org mode files with the .org extension. When converting these files to HTML, GitLab uses the org-ruby library, which processes user-defined keywords in documents, such as #+TODO:. An attacker can provide a specially crafted value for such a keyword, triggering an overflow in the Onigmo regular expression engine, resulting in memory corruption. Under certain conditions, this can lead to arbitrary code execution on the GitLab server. To exploit the vulnerability, an attacker needs to upload a specially crafted file to a public project. For example, if self-registration is enabled and users are allowed to create public projects, an attacker can register an account and create their own project. Once the file is uploaded, the vulnerable handler can be triggered simply by opening the file's preview page without authentication.

A compromised GitLab server may give an attacker access to project source code, access tokens, credentials, and other sensitive information. After gaining control of the server, an attacker may modify source code or build processes to inject malicious code into distributed applications. In addition, a compromised GitLab server can serve as a starting point for further attacks against the organization's internal infrastructure.

⚙️ The vulnerability has been fixed in versions 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, and 18.11.13. Infrastructure managed by GitLab itself, including GitLab.com and GitLab Dedicated, is already protected against this vulnerability. If GitLab was installed from unofficial packages and uses a custom Ruby version, updating GitLab alone is not sufficient. This applies, for example, to custom-built GitLab versions and installations using custom container images. In such cases, Ruby must also be updated separately to version 3.3.13, 3.4.12, or 4.0.9 or later. This is because the fix for CVE-2026-110264 was implemented directly in Ruby, not in the GitLab code. The fix is already included in the official GitLab Linux packages and container images.

The GitLab security team has released two detection rules to identify potential attacks against self-hosted GitLab instances: Onigmo native worker crash and Org mode render error burst.

🛠 PoC exploits have been available on GitHub since October 22.

👾 There is currently no evidence that the vulnerability has been exploited in the wild.

🌐 According to Shadowserver, more than 10,000 vulnerable GitLab instances are exposed to the Internet.
About Remote Code Execution - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619) vulnerabilities

About Remote Code Execution - PHP PHP2Shell (CVE-2026-109618, CVE-2026-109619) vulnerabilities

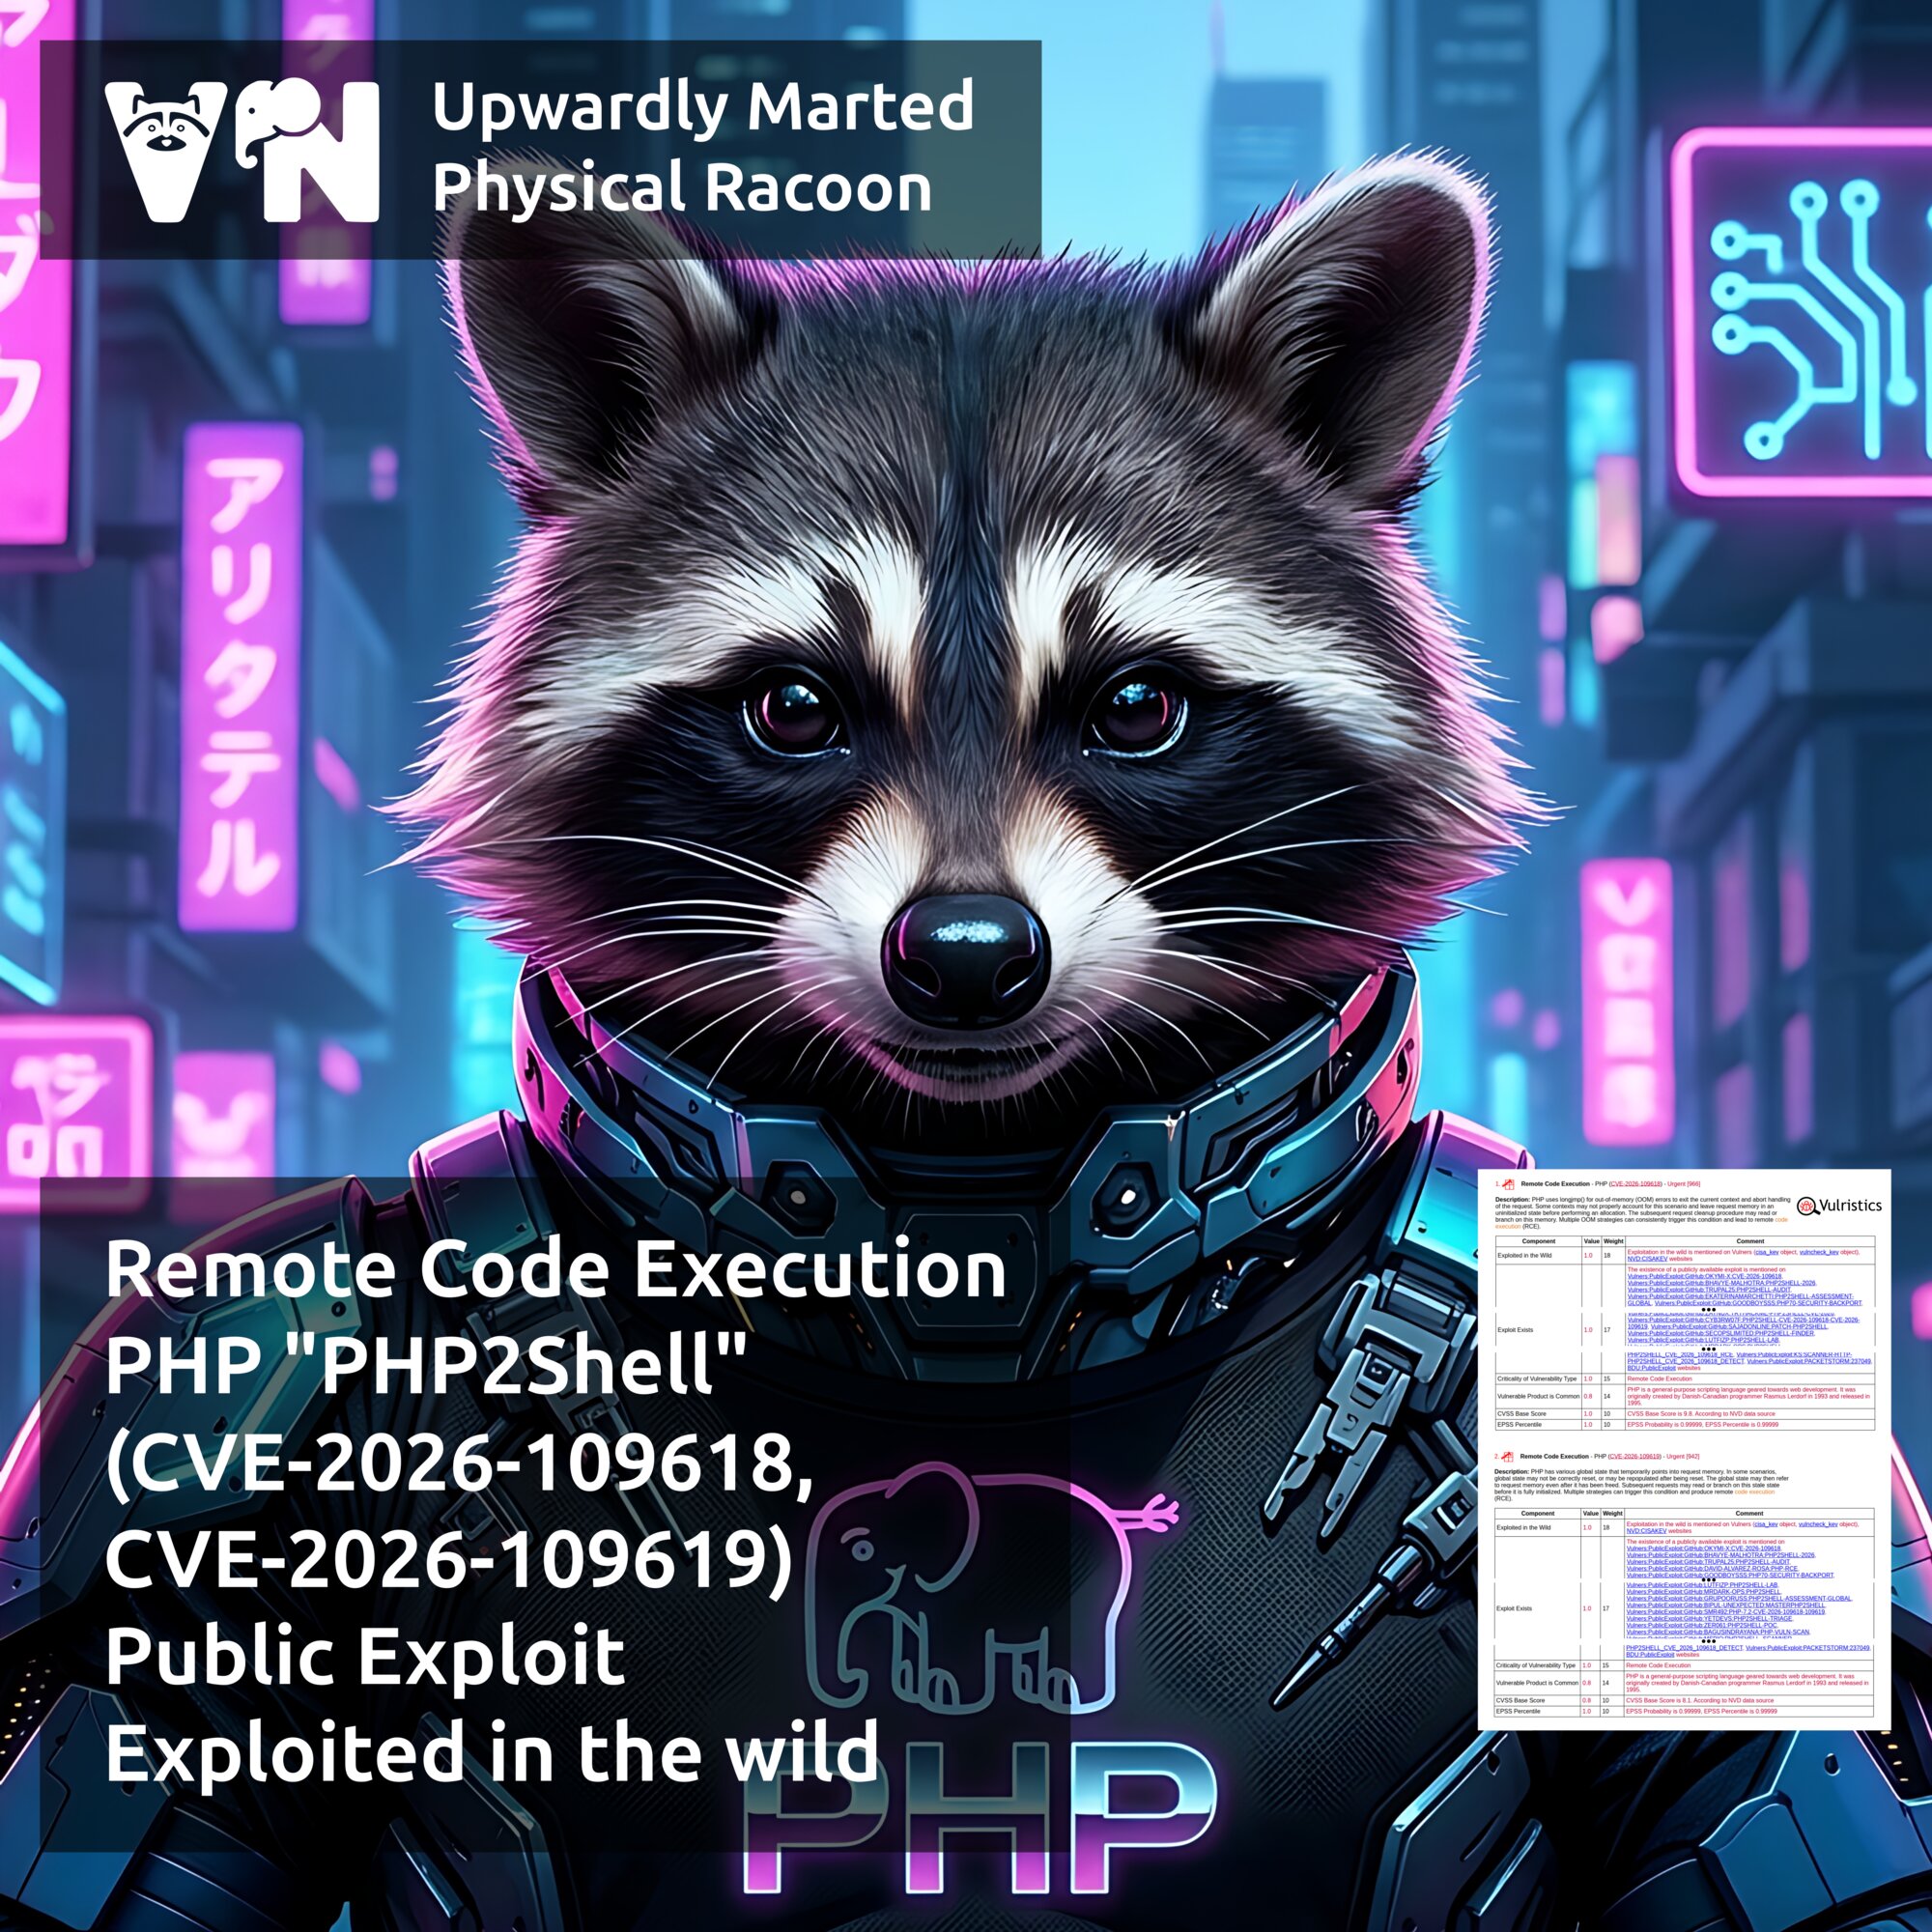
About Remote Code Execution - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619) vulnerabilities. PHP is a popular server-side programming language. The vulnerabilities, covered in the October Linux Patch Wednesday, allow unauthenticated remote code execution through specially crafted requests. CVE-2026-109618 is caused by improper OOM error handling, while CVE-2026-109619 is caused by a use-after-free vulnerability in PHP's global data structures. Exploitation can lead to system compromise, data theft, malware installation, and access to internal networks.

⚙️ The PHP Foundation had known about the root cause since 2024 but prioritized a fix only on August 11, 2026. Updates planned for October 22 were released a day early due to an embargo breach. Users should upgrade to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, or install patched Linux distribution packages. For unsupported branches, migration to a supported version is recommended. Meanwhile, restrict Internet access and apply configuration-based workarounds. For network devices, install vendor fixes or apply recommended mitigations.

Positive Technologies implemented protections using PT AF, PT NAD, and PT NGFW, and released detection rules for MaxPatrol VM.

🛠 GitHub hosts over 1,000 public PHP2Shell exploit repositories, but achieving RCE against a specific target remains difficult. Exploitation requires a tailored exploit compatible with the target's PHP build, SAPI, extensions, and runtime configuration.

👾 Both vulnerabilities were added to CISA KEV on October 26. Confirmed exploitation remains limited, mostly involving network devices.

On October 26, Dream Group reported attacks on Palo Alto Networks devices in the US, Japan, Taiwan, and South Korea. Attackers identified 240 targets among 19,000 devices and compromised 24 firewalls and one management server. Three reportedly belonged to US government infrastructure. The attacks exploited PHP2Shell and the Linux kernel LPE vulnerability Fragnesia (CVE-2026-46300). Attackers stole service account credentials, user and group lists, network configurations, and private keys.

On November 12, Check Point experts reported attacks against Security Gateway devices that had started on October 30. By exploiting PHP2Shell and the DynamicCLI LPE vulnerability (CVE-2026-123039), attackers gained initial access, escalated their privileges, and installed the TSGA backdoor along with its network component, TSProxy. During the destructive phase of the attacks, they also gained SSH access to a VMware ESXi host and executed the destroy_v6 wiper.

🌐 According to Censys data, 27 million PHP services exposed to the Internet remain unpatched. In addition, the vulnerabilities affect products from numerous vendors, including Palo Alto Networks, Check Point, Netgate, Coolify, and Cisco.

November Microsoft Patch Tuesday

November Microsoft Patch Tuesday

November Microsoft Patch Tuesday. A total of 1,093 vulnerabilities. For comparison, there were 1,409 in October, a decrease of 22.4%. Ten products had 20 or more vulnerabilities fixed: Microsoft Office Excel (64), Microsoft Office Word (61), Microsoft SQL Server (50), Windows Advanced Rasterization Platform (37), Windows Installer (36), Windows Graphics Kernel (35), Windows Kernel (28), Microsoft Office SharePoint (26), Windows DNS (21), Windows Print Spooler Components (20). Together, these products had 378 vulnerabilities fixed, or slightly more than one-third (34.6%) of the total. One vulnerability is flagged as having been exploited in the wild:

🔻 Spoofing - Microsoft Outlook (CVE-2026-124194). Microsoft Outlook is a Microsoft application for managing email, calendars, scheduling meetings, organizing contacts, and setting reminders. An attacker sends a specially crafted message file and convinces a user to open it. Outlook then connects to an attacker-controlled network location without showing the usual external-content warning, which discloses the user’s NTLMv2 hash. The attacker can use that hash to authenticate as the user. The Preview Pane is not an attack vector. A public exploit for the vulnerability is available on GitHub.

There are two vulnerabilities with public exploits, but no evidence of exploitation in the wild has been observed so far.

🔸 EoP - Microsoft Windows App Store (CVE-2026-119987). Microsoft Store (Windows App Store) is Microsoft's official app store for finding, downloading, and installing applications, games, and other digital content on Windows devices. Untrusted search path in Microsoft Windows App Store allows an authorized attacker to elevate privileges locally. A PoC was published on GitHub but later removed. A copy is available on Vulners.

🔸 EoP - Windows AppX Deployment Service (CVE-2026-116714). Windows AppX Deployment Service is a Windows system service responsible for installing, updating, and removing applications. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

Other notable vulnerabilities include:

🔹 RCE - Windows LDAP (CVE-2026-119958). Windows LDAP is a service and protocol used to search and manage information about users, computers, and other resources in an enterprise network. An out-of-bounds write vulnerability allows an unauthorized attacker to execute arbitrary code by sending specially crafted LDAP requests over the network.

🔹 RCE - Windows Search / Exchange Server (CVE-2026-116928). An unauthenticated attacker could exploit the Windows Search component used by Microsoft Exchange Server (Microsoft's server platform for managing enterprise email, calendars, contacts, and shared meeting scheduling) by sending an email containing a specially crafted attachment. Exchange automatically processes the attachment for indexing, so the recipient does not need to open the email or attachment. Successful exploitation could allow the attacker to execute code with the permissions of the affected processing service.

🔹 RCE - Microsoft Exchange (CVE-2026-118207). An authenticated attacker with low-level access to an affected server could send a specially crafted request to execute code on the server. User interaction is not required.

🔹 RCE - Windows Active Directory Domain Services (CVE-2026-118146). Windows Active Directory Domain Services is a Windows service for centrally managing users, computers, and access to enterprise network resources. An authenticated attacker with low-level access to an affected server could send a specially crafted request to execute code on the server. User interaction is not required.

🔹 RCE - Windows Virtual Filtering Platform (VFP) (CVE-2026-95962). Windows Virtual Filtering Platform (VFP) is a Windows system component responsible for processing and filtering network traffic. Use after free bug allows an unauthorized attacker to execute code by sending a specially crafted packet to the affected service over the network.

🔹 RCE - Windows Schannel (CVE-2026-119952). Windows Schannel is a Windows system component that provides secure network connections and encryption of transmitted data. An unauthenticated attacker could exploit this vulnerability by sending a specially crafted packet to an affected service over the network. Successful exploitation could allow the attacker to execute code on the target system. No authentication or user interaction is required.

🔹 EoP - Microsoft SharePoint Server (CVE-2026-120002). Microsoft SharePoint Server is Microsoft's enterprise platform for creating intranet portals, storing and collaborating on documents, sharing information, and managing business workflows within an organization. An authenticated attacker with site read access and membership in the relevant SharePoint Secure Store target application could send a specially crafted network request to an affected SharePoint server. Successful exploitation could cause SharePoint to perform unauthorized actions on a connected business service using shared credentials. No additional user interaction is required.

🗒 Full Vulristics report

October Linux Patch Wednesday

October Linux Patch Wednesday

October Linux Patch Wednesday. There are 4,946 vulnerabilities in total. By comparison, there were 2,653 in September. That's an 86% increase! This time, there are 1,954 vulnerabilities in the Linux Kernel and 814 in Chromium. Together, they make up 56% of all vulnerabilities.

Six vulnerabilities show signs of being exploited in the wild:

🔻 RCE - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619). PHP is a popular programming language widely used for web application development. CVE-2026-109618 is an out-of-memory (OOM) handling vulnerability that allows remote code execution when an application receives a specially crafted request. CVE-2026-109619 is a use-after-free vulnerability that allows PHP to access stale references to freed memory, potentially leading to remote code execution. Linux distributions began releasing patches on the day the vulnerabilities were disclosed, October 21. More than 470 links to public exploits are available on GitHub. Both vulnerabilities were added to the CISA KEV on October 26.

🔻 SFB - Linux Kernel "PwnEscape" (CVE-2026-99999). The vulnerability affects the Linux kernel's networking stack and allows an attacker inside a KVM guest virtual machine to corrupt the host kernel's memory. This could expose sensitive host memory contents or cause the host system to crash. Researchers demonstrated a complete escape from a guest VM to the host. Linux distributions began releasing patched packages on October 16, and public exploits appeared on GitHub the same day. The vulnerability was added to the VulnCheck KEV on October 19.

🔻 RCE - WordPress (CVE-2026-87902). WordPress is a popular content management system (CMS) for building websites and blogs. Under certain conditions, this vulnerability allows an unauthenticated attacker to execute arbitrary code remotely on the server. Public exploits have been available on GitHub since September 22. The vulnerability was added to the CISA KEV on September 25. Debian released patched packages on September 28.

🔻 XSS - WordPress "Comment2Shell" (CVE-2026-93485). The vulnerability allows an unauthenticated attacker to inject JavaScript code through a specially crafted comment. The code is executed in the browser when an administrator views the comment, allowing the attacker to hijack his session and potentially execute arbitrary code on the server. The vulnerability was added to the VulnCheck KEV on September 18. Public exploits have been available on GitHub since September 22. Patched packages have been available in Debian since September 28.

🔻 AFR - Gradio (CVE-2026-28414). Gradio is a Python library for quickly building machine learning interfaces. The vulnerability allows unauthenticated attackers to read arbitrary files from a Windows server running Python 3.13 or later, even when Gradio authentication is enabled. A public exploit appeared on February 27. The vulnerability was added to the VulnCheck KEV on May 31. ALT Linux has been providing patched packages since October 1.

Another 335 vulnerabilities have no known signs of exploitation in the wild, but public exploits are available for them. Notable examples include:

🔸 EoP - Linux Kernel (CVE-2026-98260). This use-after-free vulnerability in the POSIX CPU timers mechanism allows a local unprivileged user to escalate privileges to root. Researcher v4bel demonstrated a root shell on Ubuntu 26.04 running kernel 7.0.0-30-generic as part of the Infinity Core project. The exploit is also reported to enable container escapes and privilege escalation on Android. Patched packages have been available since October 15. A public exploit was published on GitHub on October 17.

🔸 RCE - Pillow (CVE-2026-112900). Pillow is a Python library for image processing. An attacker can upload an EPS file to execute arbitrary code on the server. Patched packages have been available in Debian since October 21. Public exploits have been available on GitHub since October 23.

🗒 Full Vulristics report (ZIP; 1.7 MB)

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday. A total of 1,409 vulnerabilities. For comparison, there were 973 in September, an increase of about 45%. 🙈 Thirteen products had fixes for 20 or more vulnerabilities: Microsoft Office Excel (68), Windows Kernel (46), Role: DNS Server (41), Windows Installer (38), Microsoft Office SharePoint (35), Windows Win32k (31), Windows NTFS (26), .NET (25), Microsoft Windows Search Component (23), Microsoft Office Word (22), Windows Error Reporting (21), Windows Broadcast DVR User Service (20), and Microsoft SQL Server (20). A total of 416 vulnerabilities were fixed in these products. That's 30% of all vulnerabilities. One vulnerability is flagged as exploited in the wild:

🔻 SFB - Windows Shell (CVE-2026-96951). The vulnerability allows an attacker to bypass Mark of the Web (MOTW), a Windows feature that marks files downloaded from the Internet. To exploit it, the attacker must trick the user into opening a malicious file or clicking a malicious link.

There are two vulnerabilities with public exploits:

🔸 RCE - Raw Image Extension (CVE-2026-21413). A heap-based buffer overflow in Windows Raw Image Extension allows an attacker to execute arbitrary code remotely using a specially crafted file. A technical write-up of the vulnerability, which NVD classifies as an exploit, was published on the Cisco Talos blog on April 7.

🔸 EoP - Windows Health and Optimized Experiences Service (CVE-2026-85884). Missing authentication for a critical function in Windows Health and Optimized Experiences Service allows a local attacker to gain SYSTEM privileges. A public exploit has been available on GitHub since October 13.

Other notable vulnerabilities include:

🔹 RCE - Microsoft Exchange (CVE-2026-70571). An unauthenticated attacker can send a specially crafted email to a vulnerable Exchange server and execute arbitrary code on the server. The attack requires an in-depth understanding of the target environment. No user interaction is required.

🔹 RCE - Microsoft Office Outlook (CVE-2026-70242, CVE-2026-97749, CVE-2026-97016, CVE-2026-88156, CVE-2026-70291). An attacker can execute arbitrary code on the victim's device by sending a specially crafted email. To exploit the vulnerability, the victim only needs to view the email in Outlook's reading pane without opening it or taking any further action.

🔹 RCE - Windows Domain Name Service (CVE-2026-96113). A heap-based buffer overflow in DNS Server allows an unauthorized attacker to execute code over a network.

🔹 SFB - .NET Framework (CVE-2026-108398). An authenticated attacker can place a specially crafted .NET assembly on an affected system and register it to be loaded by a protected process. This allows the attacker to bypass Windows Defender Application Control (WDAC) restrictions and run unauthorized code within the protected process. No user interaction is required.

🔹 Spoofing - Microsoft Exchange (CVE-2026-70279). An attacker can send a specially crafted link to a user and trick them into opening it. No authentication is required. If the user has administrator privileges, the attacker could act as that user and access or modify the organization's data.

🗒 Full Vulristics report

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.