Tag Archives: LDAP

September Linux Patch Wednesday

September Linux Patch Wednesday

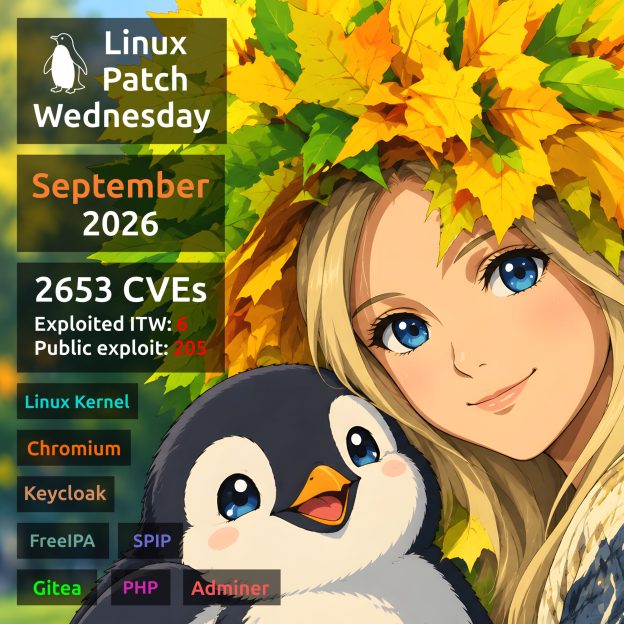
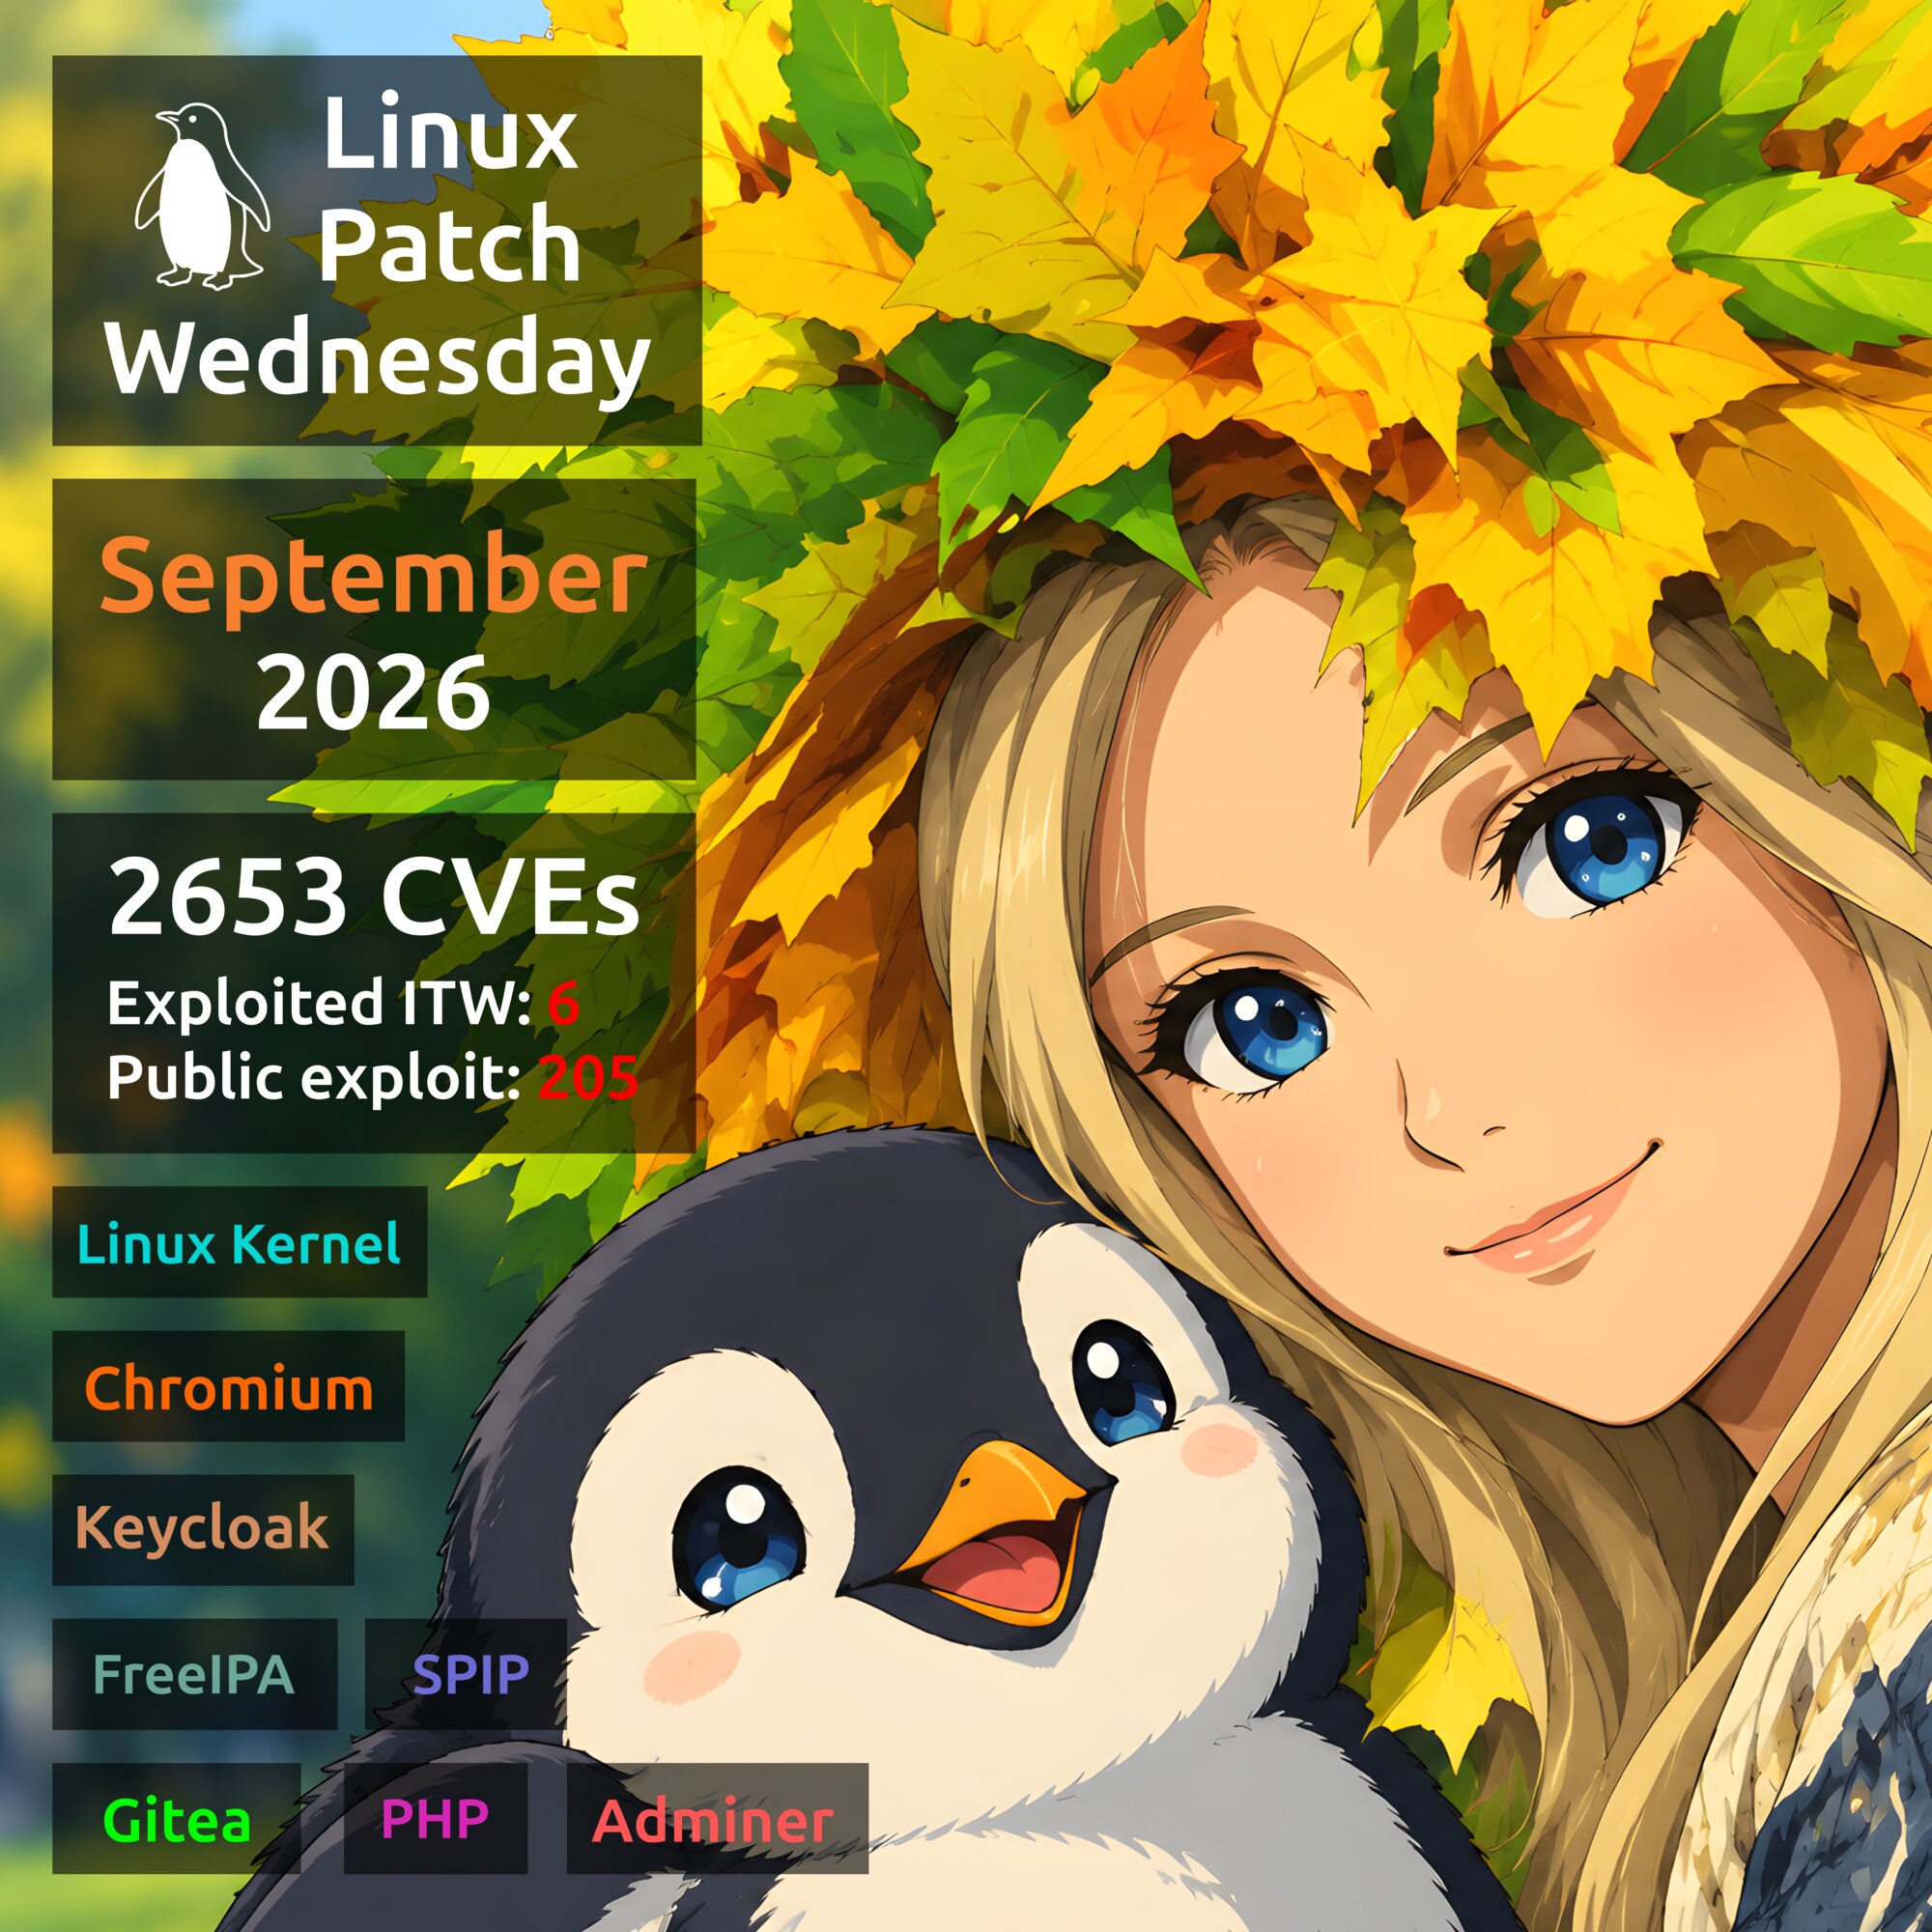
September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.
🗒 Full Vulristics report

New episode "In the Trend of VM" (#12): 8 February CVEs & Why the Darknet Matters for VM Specialists

New episode "In the Trend of VM" (#12): 8 February CVEs & Why the Darknet Matters for VM Specialists. Now with a new design and new video editing. 😉

📹 Video on YouTube and LinkedIn
🗞 Post on Habr (rus)
🗒 Digest on the PT website

Content:

🔻 00:00 Greetings
🔻 00:23 Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112)
🔻 01:35 Remote Code Execution - Microsoft Configuration Manager (CVE-2024-43468)
🔻 02:38 Remote Code Execution - Windows OLE (CVE-2025-21298)
🔻 03:55 Elevation of Privilege - Windows Hyper-V NT Kernel Integration VSP (CVE-2025-21333, CVE-2025-21334, CVE-2025-21335)
🔻 05:02 Authentication Bypass – FortiOS/FortiProxy (CVE-2024-55591)
🔻 06:16 Remote Code Execution - 7-Zip (CVE-2025-0411)
🔻 07:27 Should a VM specialist be aware of what is happening in the Darknet?
🔻 08:48 About the digest of trending vulnerabilities

На русском

About Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112)

About Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112)

About Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112). The vulnerability is from the December Microsoft Patch Tuesday. Three weeks later, on January 1, researchers from SafeBreach released a write-up on this vulnerability, labeled as LDAPNightmare, and an exploit PoC.

The exploit causes a forced reboot of Windows servers. One prerequisite: the victim domain controller's DNS server must have Internet connectivity.

The attack flow starts with sending a DCE/RPC request to the victim server, causing the LSASS (Local Security Authority Subsystem Service) to crash and force a reboot when an attacker sends a specially crafted CLDAP (Connectionless Lightweight Directory Access Protocol) referral response packet.

But this is all about DoS, why RCE? 🤔 Researchers note that RCE can be achieved by modifying the CLDAP packet.

На русском

Microsoft Patch Tuesday May 2023: Microsoft Edge, BlackLotus Secure Boot SFB, OLE RCE, Win32k EoP, NFS RCE, PGM RCE, LDAP RCE, SharePoint RCE

Microsoft Patch Tuesday May 2023: Microsoft Edge, BlackLotus Secure Boot SFB, OLE RCE, Win32k EoP, NFS RCE, PGM RCE, LDAP RCE, SharePoint RCE. Hello everyone! This episode will be about Microsoft Patch Tuesday for May 2023, including vulnerabilities that were added between April and May Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239126

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Tenable, Rapid7, ZDI Patch Tuesday reviews.

It’s been a long time since we’ve had such tiny Patch Tuesday. 57 CVEs, including CVEs appeared during the month. And only 38 without them! 😄

Continue reading →

Microsoft Patch Tuesday January 2023: ALPC EoP, Win Backup EoP, LocalPotato, Exchange, Remote RCEs

Microsoft Patch Tuesday January 2023: ALPC EoP, Win Backup EoP, LocalPotato, Exchange, Remote RCEs. Hello everyone! This episode will be about Microsoft Patch Tuesday for January 2023, including vulnerabilities that were added between December and January Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239115

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Nessus, Rapid7 and ZDI Patch Tuesday reviews.

Continue reading →

Microsoft Patch Tuesday June 2022: Follina RCE, NFSV4.1 RCE, LDAP RCEs and bad patches

Microsoft Patch Tuesday June 2022: Follina RCE, NFSV4.1 RCE, LDAP RCEs and bad patches. Hello everyone! This will be an episode about the Microsoft vulnerabilities that were released on June Patch Tuesday and also between May and June Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239094

On June Patch Tuesday, June 14, 56 vulnerabilities were released. Between May and June Patch Tuesdays, 38 vulnerabilities were released. This gives us 94 vulnerabilities in the report.

Continue reading →

Microsoft Patch Tuesday May 2022: Edge RCE, PetitPotam LSA Spoofing, bad patches

Microsoft Patch Tuesday May 2022: Edge RCE, PetitPotam LSA Spoofing, bad patches. Hello everyone! This episode will be about Microsoft Patch Tuesday for May 2022. Sorry for the delay, this month has been quite intense. As usual, I’m using my Vulristics project and going through not only the vulnerabilities that were presented on May 10th, but all the MS vulnerabilities presented by Microsoft since the previous Patch Tuesday, April 12th.

Alternative video link (for Russia): https://vk.com/video-149273431_456239089

I have set direct links in comments_links.txt for Qualys, ZDI and Kaspersky blog posts.

Continue reading →