Tag Archives: Android

October Linux Patch Wednesday

October Linux Patch Wednesday

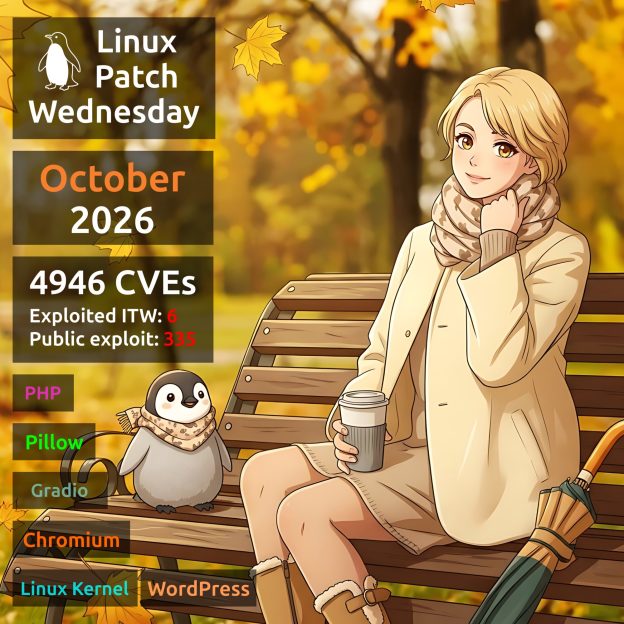
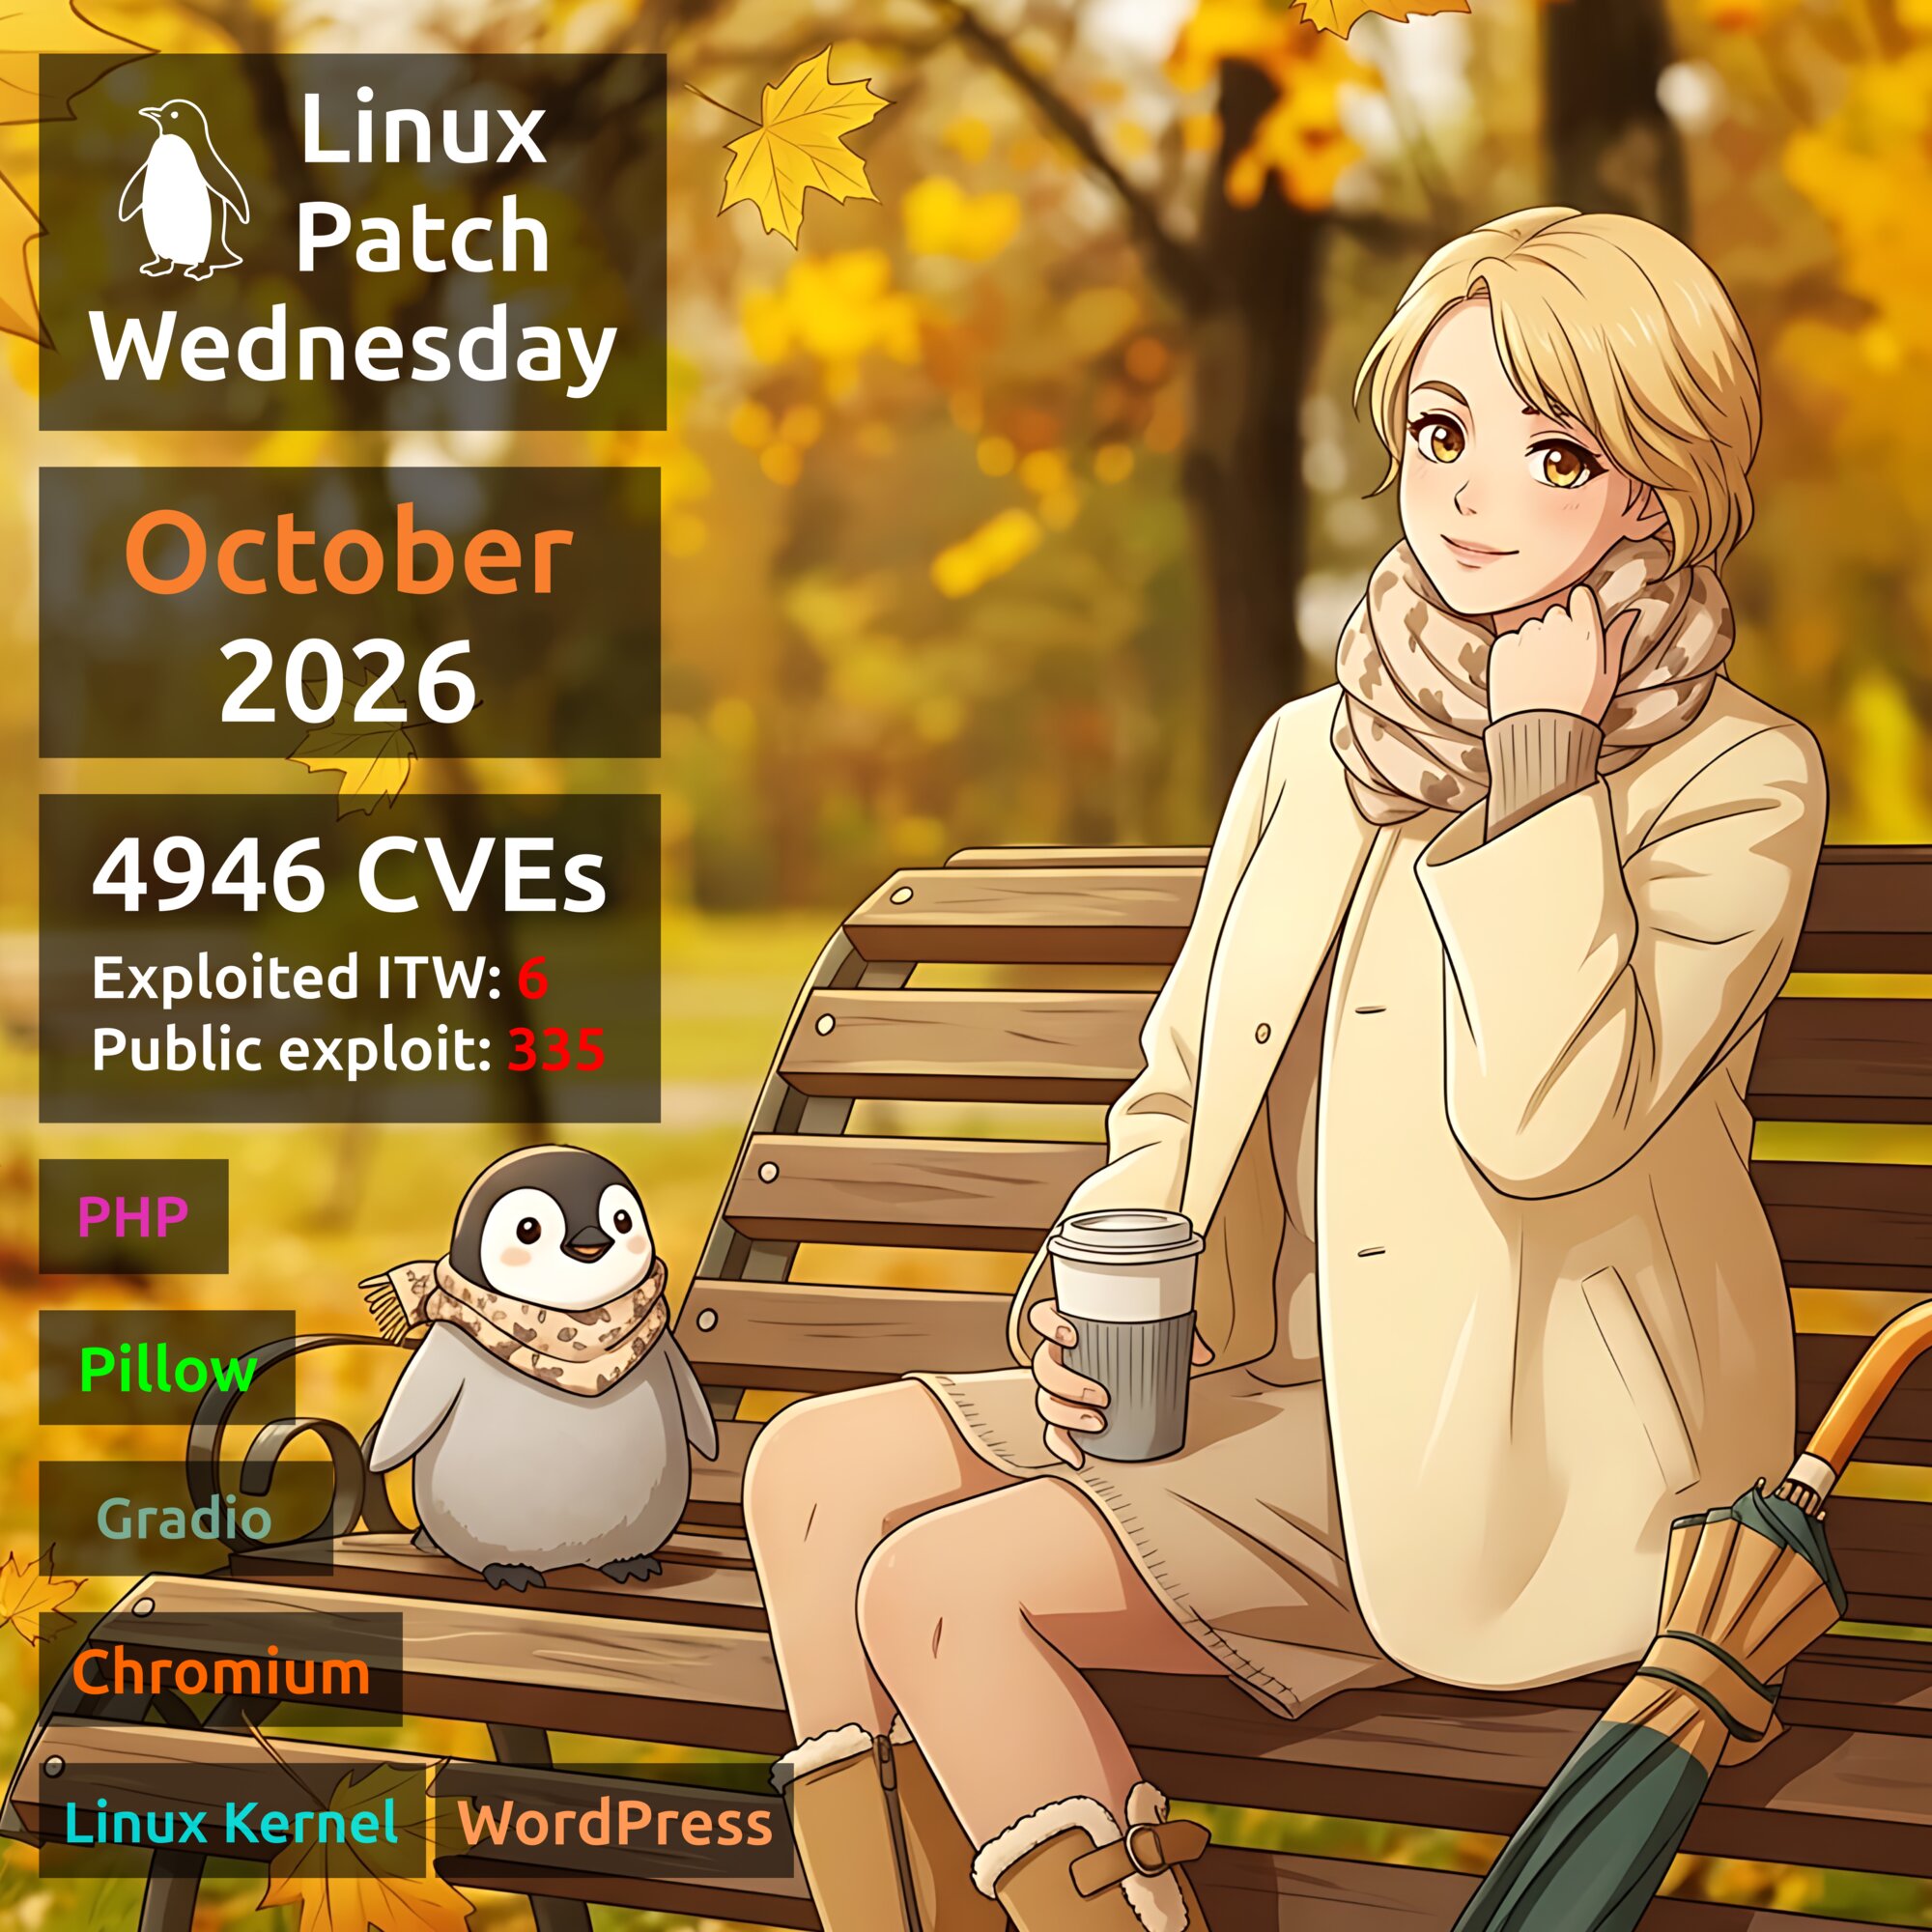
October Linux Patch Wednesday. There are 4,946 vulnerabilities in total. By comparison, there were 2,653 in September. That's an 86% increase! This time, there are 1,954 vulnerabilities in the Linux Kernel and 814 in Chromium. Together, they make up 56% of all vulnerabilities.

Six vulnerabilities show signs of being exploited in the wild:

🔻 RCE - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619). PHP is a popular programming language widely used for web application development. CVE-2026-109618 is an out-of-memory (OOM) handling vulnerability that allows remote code execution when an application receives a specially crafted request. CVE-2026-109619 is a use-after-free vulnerability that allows PHP to access stale references to freed memory, potentially leading to remote code execution. Linux distributions began releasing patches on the day the vulnerabilities were disclosed, October 21. More than 470 links to public exploits are available on GitHub. Both vulnerabilities were added to the CISA KEV on October 26.

🔻 SFB - Linux Kernel "PwnEscape" (CVE-2026-99999). The vulnerability affects the Linux kernel's networking stack and allows an attacker inside a KVM guest virtual machine to corrupt the host kernel's memory. This could expose sensitive host memory contents or cause the host system to crash. Researchers demonstrated a complete escape from a guest VM to the host. Linux distributions began releasing patched packages on October 16, and public exploits appeared on GitHub the same day. The vulnerability was added to the VulnCheck KEV on October 19.

🔻 RCE - WordPress (CVE-2026-87902). WordPress is a popular content management system (CMS) for building websites and blogs. Under certain conditions, this vulnerability allows an unauthenticated attacker to execute arbitrary code remotely on the server. Public exploits have been available on GitHub since September 22. The vulnerability was added to the CISA KEV on September 25. Debian released patched packages on September 28.

🔻 XSS - WordPress "Comment2Shell" (CVE-2026-93485). The vulnerability allows an unauthenticated attacker to inject JavaScript code through a specially crafted comment. The code is executed in the browser when an administrator views the comment, allowing the attacker to hijack his session and potentially execute arbitrary code on the server. The vulnerability was added to the VulnCheck KEV on September 18. Public exploits have been available on GitHub since September 22. Patched packages have been available in Debian since September 28.

🔻 AFR - Gradio (CVE-2026-28414). Gradio is a Python library for quickly building machine learning interfaces. The vulnerability allows unauthenticated attackers to read arbitrary files from a Windows server running Python 3.13 or later, even when Gradio authentication is enabled. A public exploit appeared on February 27. The vulnerability was added to the VulnCheck KEV on May 31. ALT Linux has been providing patched packages since October 1.

Another 335 vulnerabilities have no known signs of exploitation in the wild, but public exploits are available for them. Notable examples include:

🔸 EoP - Linux Kernel (CVE-2026-98260). This use-after-free vulnerability in the POSIX CPU timers mechanism allows a local unprivileged user to escalate privileges to root. Researcher v4bel demonstrated a root shell on Ubuntu 26.04 running kernel 7.0.0-30-generic as part of the Infinity Core project. The exploit is also reported to enable container escapes and privilege escalation on Android. Patched packages have been available since October 15. A public exploit was published on GitHub on October 17.

🔸 RCE - Pillow (CVE-2026-112900). Pillow is a Python library for image processing. An attacker can upload an EPS file to execute arbitrary code on the server. Patched packages have been available in Debian since October 21. Public exploits have been available on GitHub since October 23.

🗒 Full Vulristics report (ZIP; 1.7 MB)
Last Week’s Security news: Exploits for ForgeRock, vSphere, Apache Tomcat, new Print Spooler vuln, Kaseya Patch and REvil, SolarWinds, Schneider Electric, Bulletins

Last Week’s Security news: Exploits for ForgeRock, vSphere, Apache Tomcat, new Print Spooler vuln, Kaseya Patch and REvil, SolarWinds, Schneider Electric, Bulletins. Hello guys! The fourth episode of Last Week’s Security news, July 12 – July 18.

I would like to start with some new public exploits. I think these 4 are the most interesting.

  • If you remember, 2 weeks ago I mentioned the ForgeRock Access Manager and OpenAM vulnerability (CVE-2021-35464). Now there is a public RCE exploit for it. ForgeRock OpenAM server is a popular access management solution for web applications. Michael Stepankin, Researcher: “In short, RCE is possible thanks to unsafe Java deserialization in the Jato framework used by OpenAM”. And now this vulnerability is Under Active Attack. “The [Australian Cyber Security Centre] has observed actors exploiting this vulnerability to compromise multiple hosts and deploy additional malware and tools,” the organization said in an alert. ACSC didn’t disclose the nature of the attacks, how widespread they are, or the identities of the threat actors exploiting them”.
  • A new exploit for vSphere Client (CVE-2021-21985). The vSphere Client (HTML5) contains a remote code execution vulnerability due to lack of input validation in the Virtual SAN Health Check plug-in which is enabled by default in vCenter Server. A malicious actor with network access to port 443 may exploit this issue to execute commands with unrestricted privileges on the underlying operating system that hosts vCenter Server.
  • Apache Tomcat 9.0.0.M1 – Open Redirect (CVE-2018-11784). “When the default servlet in Apache Tomcat […] returned a redirect to a directory […] a specially crafted URL could be used to cause the redirect to be generated to any URI of the attackers choice”.
  • Apache Tomcat 9.0.0.M1 – Cross-Site Scripting (CVE-2019-0221). “The SSI printenv command in Apache Tomcat […] echoes user provided data without escaping and is, therefore, vulnerable to XSS”. However, in real life this is unlikely to be used. “SSI is disabled by default. The printenv command is intended for debugging and is unlikely to be present in a production website”.

Continue reading →

Getting Hosts from Microsoft Intune MDM using Python

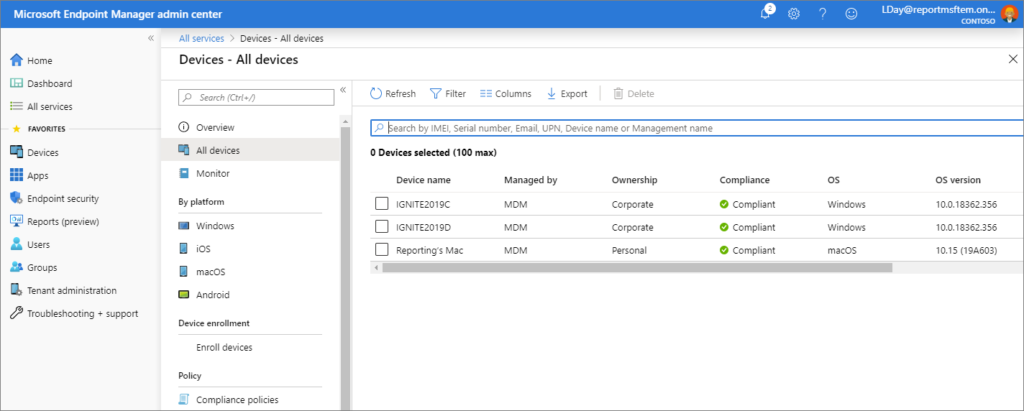
Getting Hosts from Microsoft Intune MDM using Python. Today I want to talk about Microsoft Intune. It is a Mobile Device Management platform.

Well, I think that the importance of MDM systems has become much higher than it was before the days of covid-19. Simply because a lot more people now work remotely using corporate laptops. And if these people don’t connect to the corporate network using a VPN, you most likely won’t see any activity from their devices in Active Directory. This means that you will not understand whether the device is active or not. And it will be impossible to get the correct security metrics for these devices.

Mobile device management is a solution to this problem as it maintains a connection between the laptop and the cloud server. MDM can collect various parameters from hosts, but for me the most important parameter is the timestamp. I will not describe all the features of Microsoft Intune here. Simply because at this stage they are not very interesting to me. The task I needed to solve was how to get the timestamp of the last activity for all hosts in Microsoft Intune using the official API. And since this is poorly documented, I want to share it with you.

Continue reading →

Qualys Security Conference Virtual 2018. New Agents, Patch Management and Free Services

Qualys Security Conference Virtual 2018. New Agents, Patch Management and Free Services. Today I attended a very interesting online event – Qualys Security Conference Virtual 2018. It consisted of 11 webinars, began at 18:00 and will end at 03:45 Moscow time. Not the most convenient timing for Russia, but it was worth it. 🙂

Qualys Security Conference 2018

Last time I was at offline QSC event in 2016, so for me it was especially interesting to learn about the new features of Qualys platform.

Continue reading →

Somebody is watching you: IP camera, TV and Emma Watson's smartphone

Somebody is watching you: IP camera, TV and Emma Watson’s smartphone. Today I want to talk today about privacy in a most natural sense. You probably have an internet-connected device with camera an microphone: smartphone, tablet, smart TV, ip camera, baby monitor, etc.

– Can it be used to record video/audio and spy on you?
– Of course, yes!
– Only government and device vendor has resources to do it?
– Not really

Somebody is watching you

The sad truth is: most of internet-connected devices have security problems, and, unlike traditional desktops and servers, it’s much harder to patch them. Even if the vendor fixed the issue. The customers, average people, just don’t bother themselves to do it. Each week it’s become easier to access user data and even get full control over device. Hackers and pranksters may do it just for lulz, because they can.

Let’s see it on concrete examples.

Continue reading →