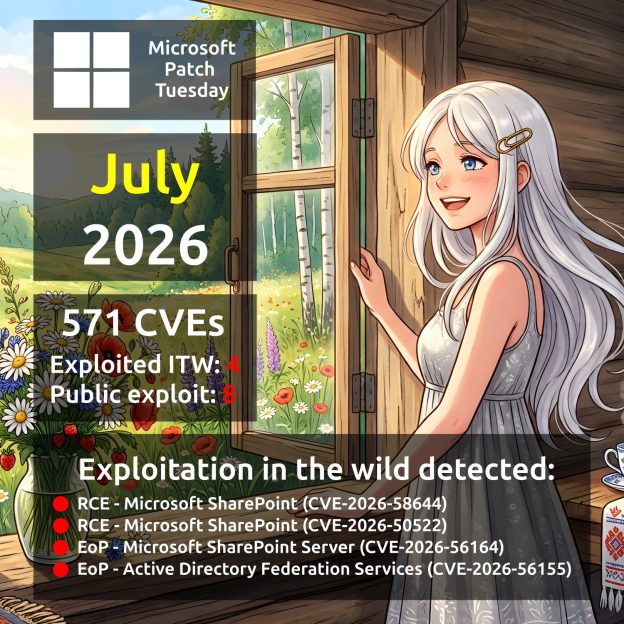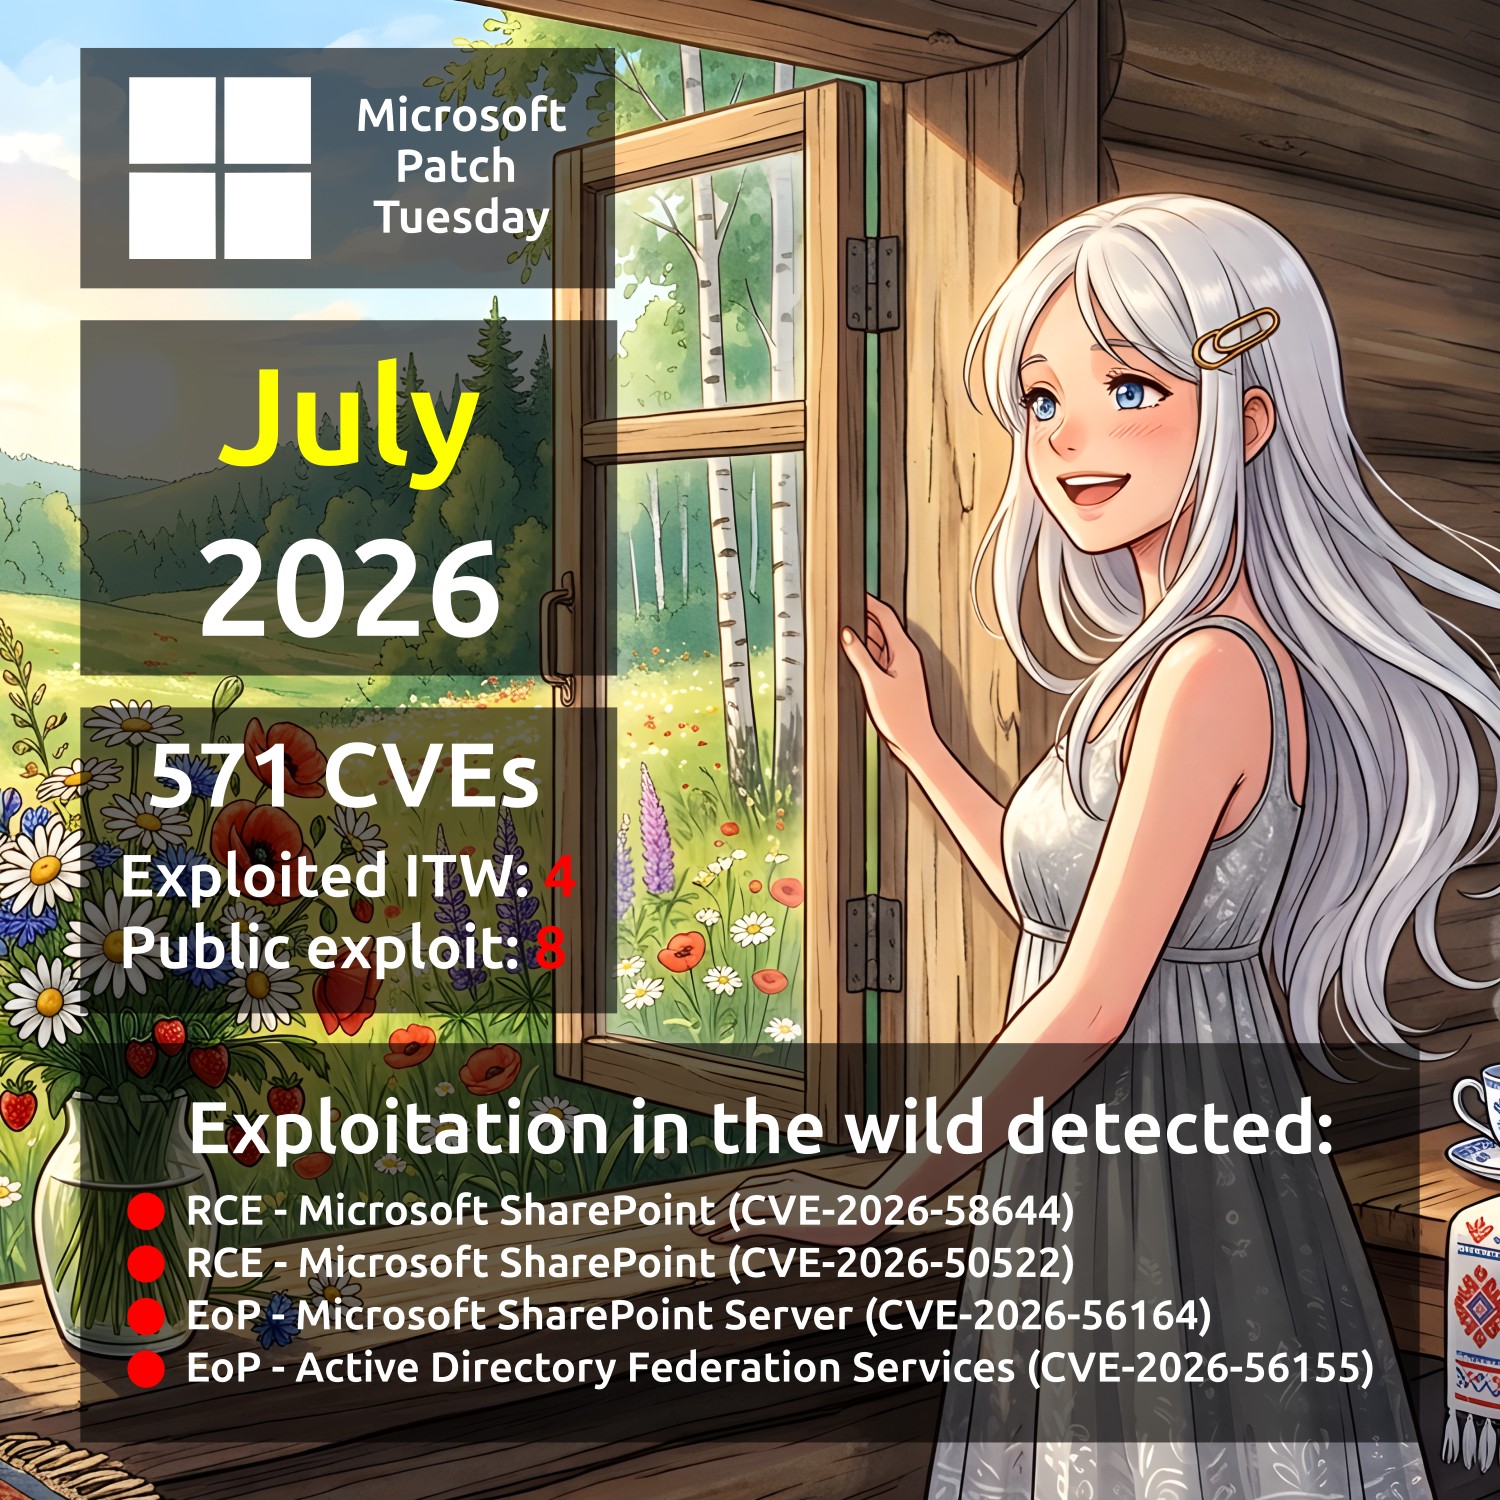
July Microsoft Patch Tuesday. In the second week of July, I was on vacation in St. Petersburg. After that, I got caught up with a bunch of other tasks, so I'm only publishing this roundup now. Better late than never, especially considering how unusual this MSPT turned out to be. 😉 In total, 571 vulnerabilities were addressed - almost three times (❗️) more than in June. There are four vulnerabilities that have been reported as exploited in the wild:
🔻 RCE - Microsoft SharePoint (CVE-2026-58644). An attacker with Site Owner privileges or higher can remotely inject and execute arbitrary code on the SharePoint Server.
🔻 RCE - Microsoft SharePoint (CVE-2026-50522). The vulnerability description is identical to CVE-2026-58644. According to ZDI, the CVE-2026-50522 vulnerability was successfully demonstrated at Pwn2Own Berlin. Despite this, Microsoft rates its Exploit Maturity as "Unknown", even though researchers have already provided a working exploit to the company. This once again shows that organizations should not rely solely on software vendors' assessments and should instead perform their own risk evaluation. If you have Internet-facing SharePoint servers, you should test and deploy the patch addressing this vulnerability as soon as possible.
🔻 EoP - Microsoft SharePoint Server (CVE-2026-56164). Missing authentication for a critical function in Microsoft Office SharePoint could allow an unauthenticated attacker to elevate privileges over a network. Microsoft mentioned in the advisory that enabling the Antimalware Scan Interface (AMSI) on the server and setting the Request Body Scan mode to Full can help mitigate this flaw.
🔻 EoP - Active Directory Federation Services (CVE-2026-56155). Insufficient granularity of access control (CWE-1220) in Active Directory Federation Services (AD FS) allows an authorized attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain administrator privileges.
There are eight more vulnerabilities with publicly available exploits:
🔸 EoP - Windows User Interface Core (CVE-2026-50454). Relative path traversal (CWE-23) allows an authorized attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. The PoC starts from a normal, non-elevated process belonging to a local administrator and opens an interactive command prompt as NT AUTHORITY\SYSTEM.
🔸 EoP - Windows WalletService (CVE-2026-49176). Improper privilege management (CWE-269) allows an authorized attacker to elevate privileges locally. The exploit PoC starts a command prompt as SYSTEM in the active desktop session.
🔸 RCE - Microsoft Message Queuing Queue Manager (CVE-2026-54992). The existing exploit PoC demonstrates denial of service; it does not demonstrate code execution.
🔸 EoP - Windows Narrator Braille (CVE-2026-58635). According to Microsoft's description, an attacker who successfully exploited this vulnerability could execute code in the security context of the NT AUTHORITY\Network Service account. However, the description of the exploit PoC states that an unprivileged attacker would gain NT AUTHORITY\SYSTEM privileges.
🔸 EoP - Windows Cloud Files Mini Filter Driver (CVE-2026-58613). Use after free (CWE-416) in the Windows Cloud Files Mini Filter Driver allows an authorized attacker to elevate privileges locally. An attacker who successfully exploits this vulnerability can gain SYSTEM privileges. Exploitation details are available in the Talos Vulnerability Report TALOS-2026-2426.
🔸 InfDisc - Windows Win32k (CVE-2026-50416). An attacker who successfully exploited this vulnerability could potentially read small portions of heap memory. The exploit PoC description mentions Chrome tabs, Discord, Explorer, Spotify, and tray windows. However, it seems that it will not be possible to intercept passwords using this vulnerability.
🔸 InfDisc - Windows Kernel (CVE-2026-50475). A buffer over-read (CWE-126) in the Windows Kernel allows an authorized attacker to disclose information locally. Exploitation details are available in the Talos Vulnerability Report TALOS-2026-2443.
🔸 EoP - Azure Spring Apps (CVE-2026-50338). An attacker who successfully exploited this vulnerability could gain elevated privileges, potentially allowing them to perform actions beyond their original permissions. According to the author of the exploit PoC, the vulnerability is a Spring Cloud Azure B2C resource server cross-issuer authentication bypass.
Among the remaining vulnerabilities, the following can be highlighted:
🔹 RCE - Windows Remote Desktop Protocol (CVE-2026-56190). An unauthenticated, network-reachable, no user interaction required vulnerability. The root cause is a classic one: the use of an uninitialized resource (CWE-908), meaning specially crafted RDP traffic can interact with memory that was never properly initialized, letting an attacker corrupt memory and potentially steer code execution. RDP Servers are a common target, so audit your systems to see which are internet accessible and start from there.
🔹 RCE - Microsoft Dynamics NAV and Microsoft Dynamics 365 Business Central (On Premises) (CVE-2026-55944). Successful exploitation can be achieved by sending a crafted login request to an affected Dynamics NAV or Business Central server in order to trigger a deserialization of untrusted data vulnerability. Microsoft's advisory cautions that no user-interaction is required, nor is authentication a requirement in order to successfully exploit this vulnerability.
🔹 EoP - Microsoft Windows VMSwitch (CVE-2026-57092). It's a use-after-free that lets a low-privileged attacker escalate to full host compromise across a VM boundary. ZDI reported that a similar exploit was demonstrated on ESXi at Pwn2Own Berlin, but this issue is not limited to ESXi. If you use VMSwitch in Hyper-V deployments (which is likely), test and deploy the fix quickly.
🔹 Spoofing - Microsoft Exchange (CVE-2026-55008). An attacker can send a specially crafted email that runs arbitrary JavaScript when the victim opens it in OWA. No attachment or macro is required - simply viewing the email is enough. If your organization uses OWA, it is recommended to test and deploy the fix as soon as possible.
🔹 RCE - Windows DHCP Server (CVE-2026-50518, CVE-2026-56159, CVE-2026-48564, CVE-2026-50370), Windows DHCP Client (CVE-2026-54128), Windows Message Queuing Service (MSMQ) (CVE-2026-50447), Windows Admin Center (WAC) (CVE-2026-56196), Windows FTP Service (CVE-2026-49172), Windows GDI+ (CVE-2026-50380), Windows Server Network driver (CVE-2026-56188), Microsoft Exchange (CVE-2026-55005), Windows Active Directory Domain Services (CVE-2026-49178), Windows Remote Desktop Client (CVE-2026-50474), Windows Remote Desktop Client (CVE-2026-54990, CVE-2026-58594), Windows TCP/IP (CVE-2026-54999), Windows Print Spooler (CVE-2026-58608), Windows Reliable Multicast Transport Driver (RMCAST) (CVE-2026-54982, CVE-2026-54995), Microsoft SQL Server (CVE-2026-54117), Microsoft Copilot (CVE-2026-48561).
🔹 SFB - Microsoft SharePoint Server (CVE-2026-55040).
🔹 EoP - Windows Server Update Service (WSUS) (CVE-2026-50444), Active Directory Certificate Services (CVE-2026-54121).
There is also a rather curious vulnerability:
RCE - Game: Age of Empires II: Definitive Edition (CVE-2026-50663). 😃 A relative path traversal in Age of Empires II: Definitive Edition Game allows an unauthorized attacker to execute code over a network. Age of Empires II is a cult classic real-time strategy game by Microsoft, set in the medieval era. Players develop chosen civilizations, manage resources, research technologies, and command armies in historical campaigns and multiplayer battles. The Definitive Edition features improved graphics, updated audio, and additional content. If you're still playing this game, be sure to update. 😉
🗒 Full Vulristics Report