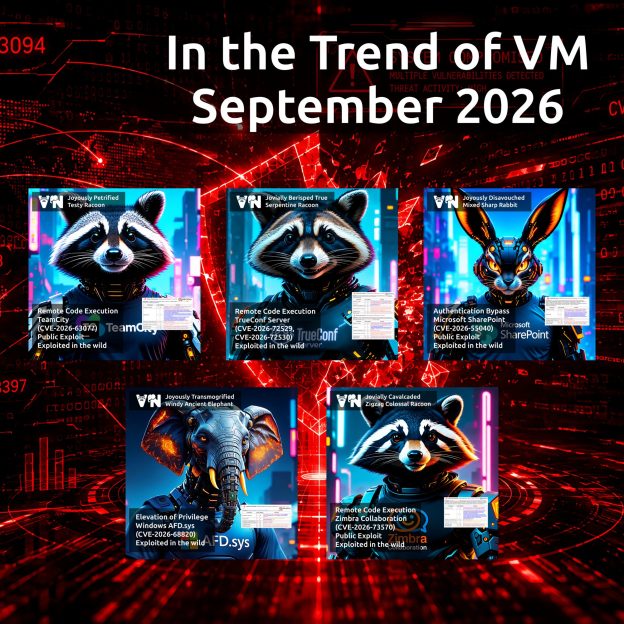
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.
🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)
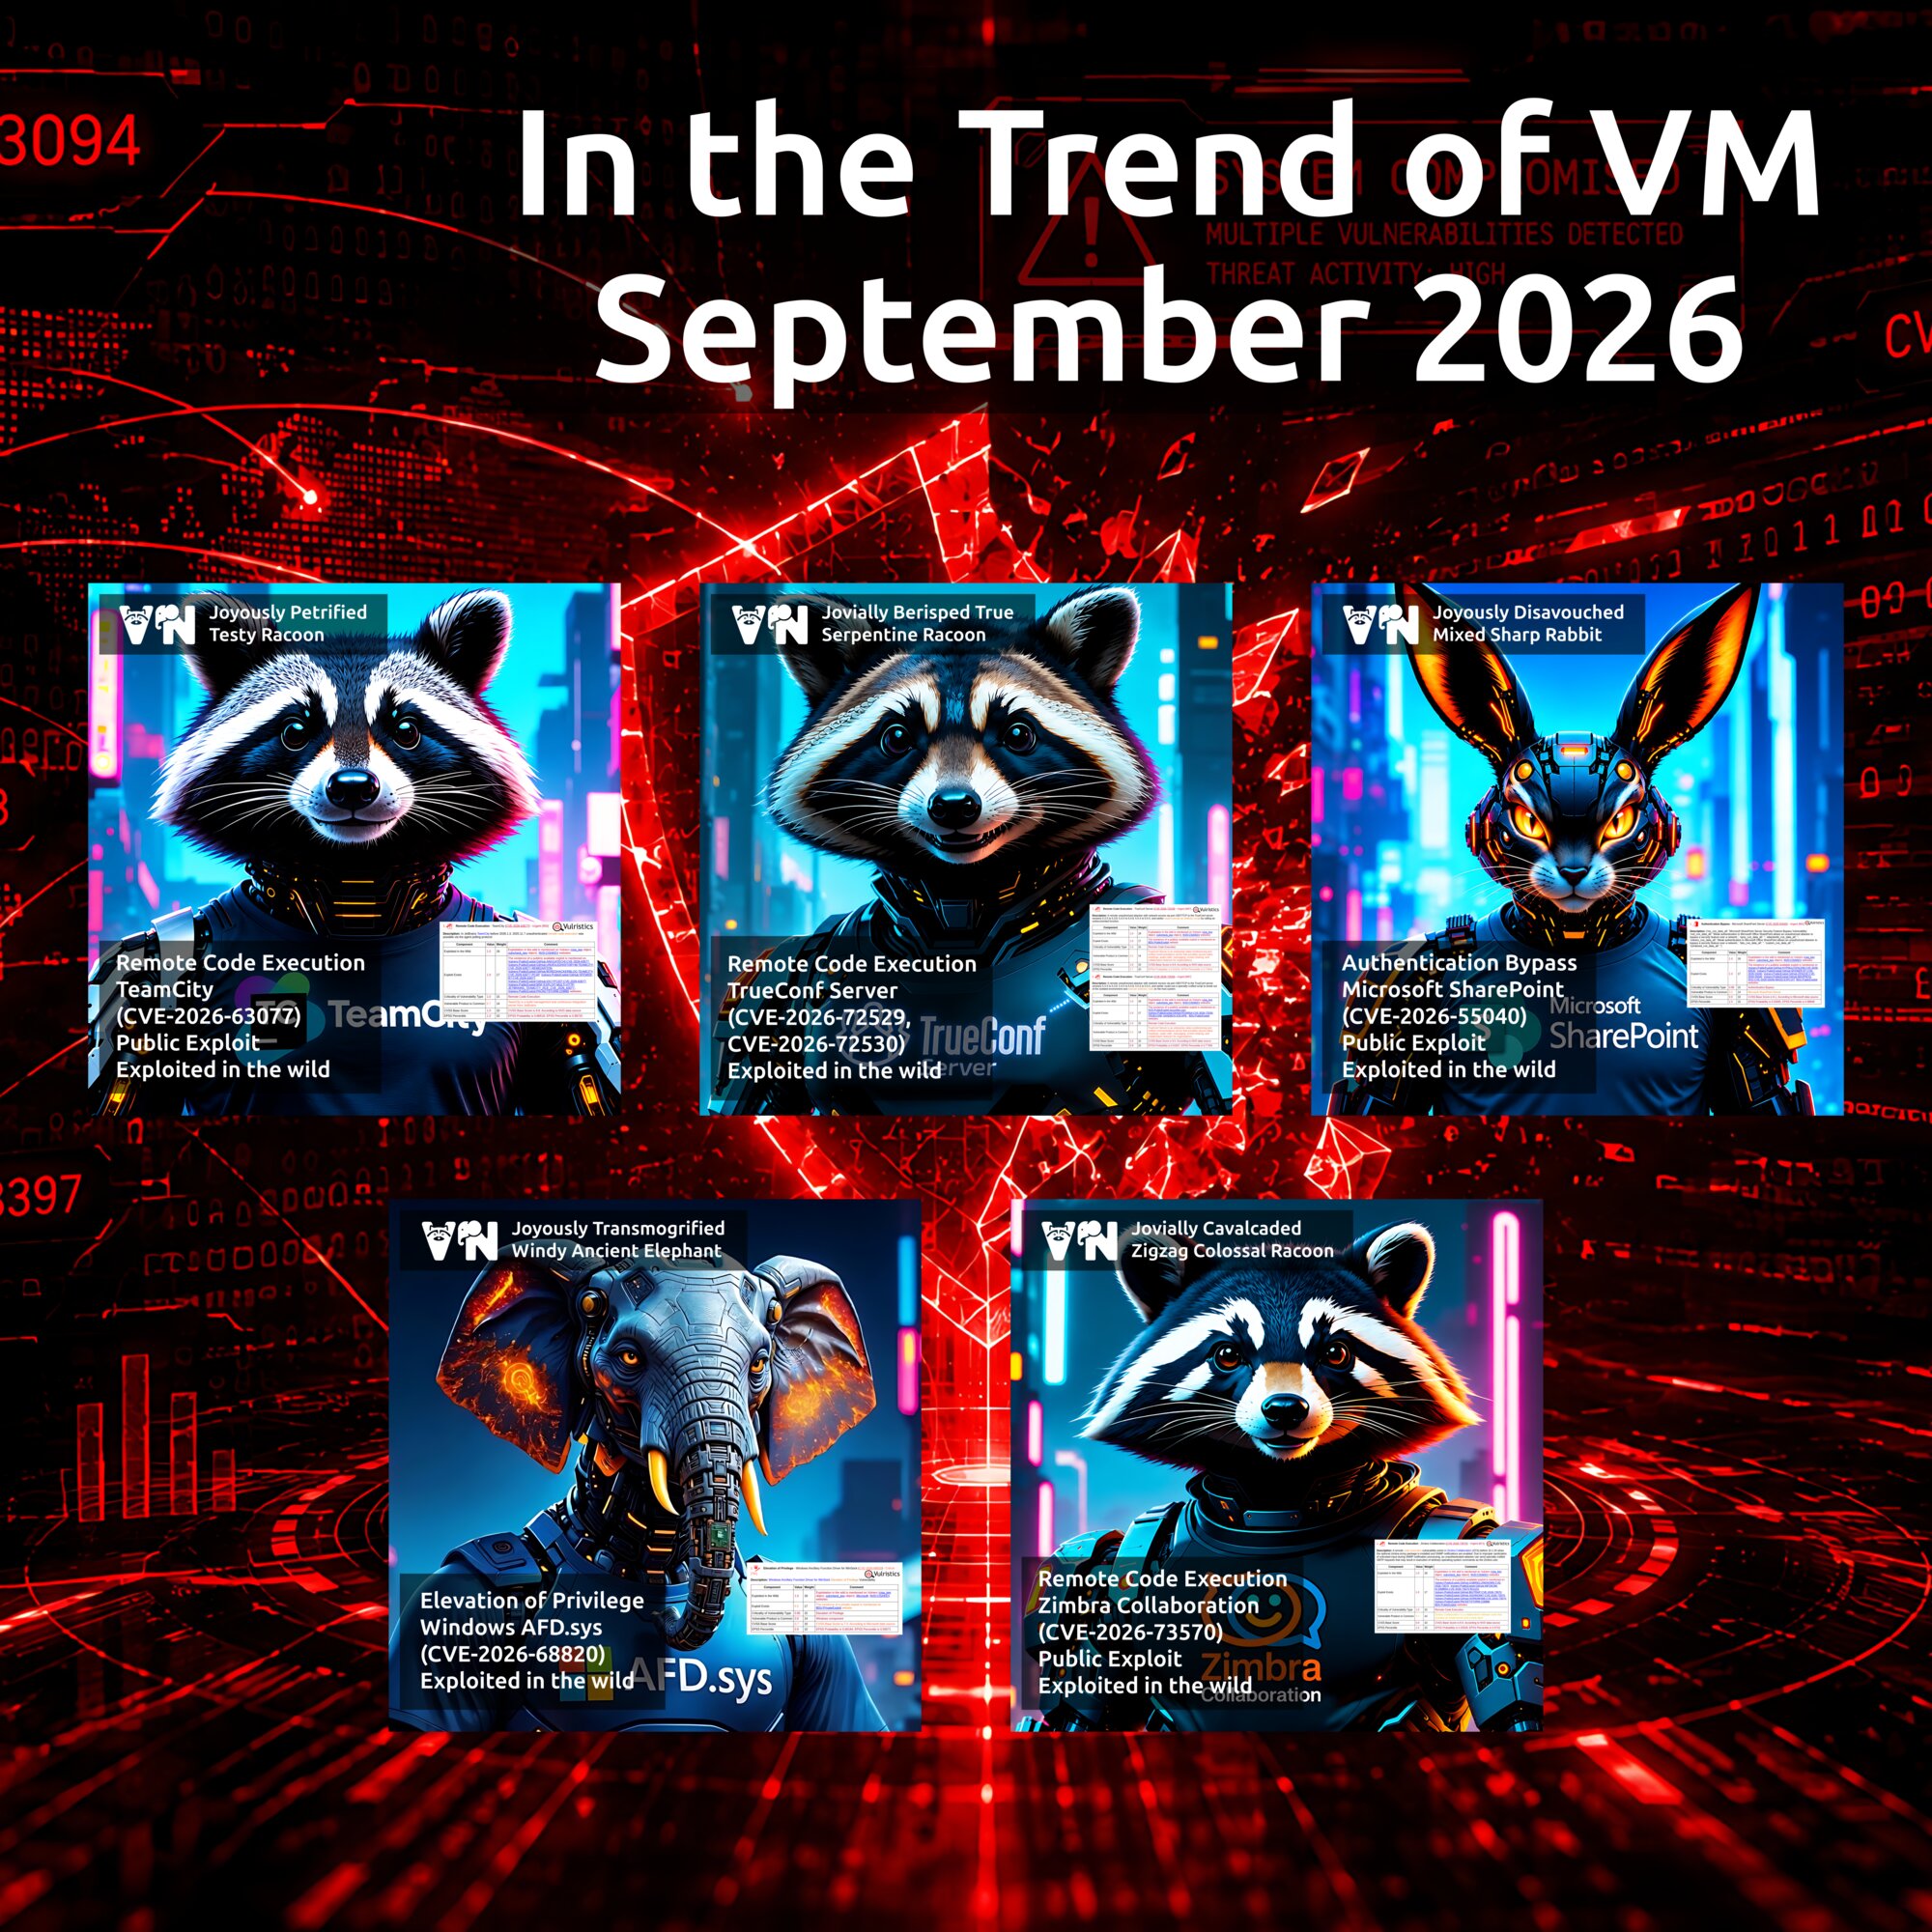
🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.
🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.
🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.
🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.
🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.
🟥 The full list of trending vulnerabilities is available on the portal
Hi! My name is Alexander and I am a Vulnerability Management specialist. You can read more about me here. Currently, the best way to follow me is my Telegram channel @avleonovcom. You can discuss my posts or ask questions at @avleonovchat.
А всех русскоязычных я приглашаю подписаться на мой канал @avleonovrus "Управление Уязвимостями и прочее" в MAX или в Telegram.