Tag Archives: CyberSecurity

September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September In the Trend of VM (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

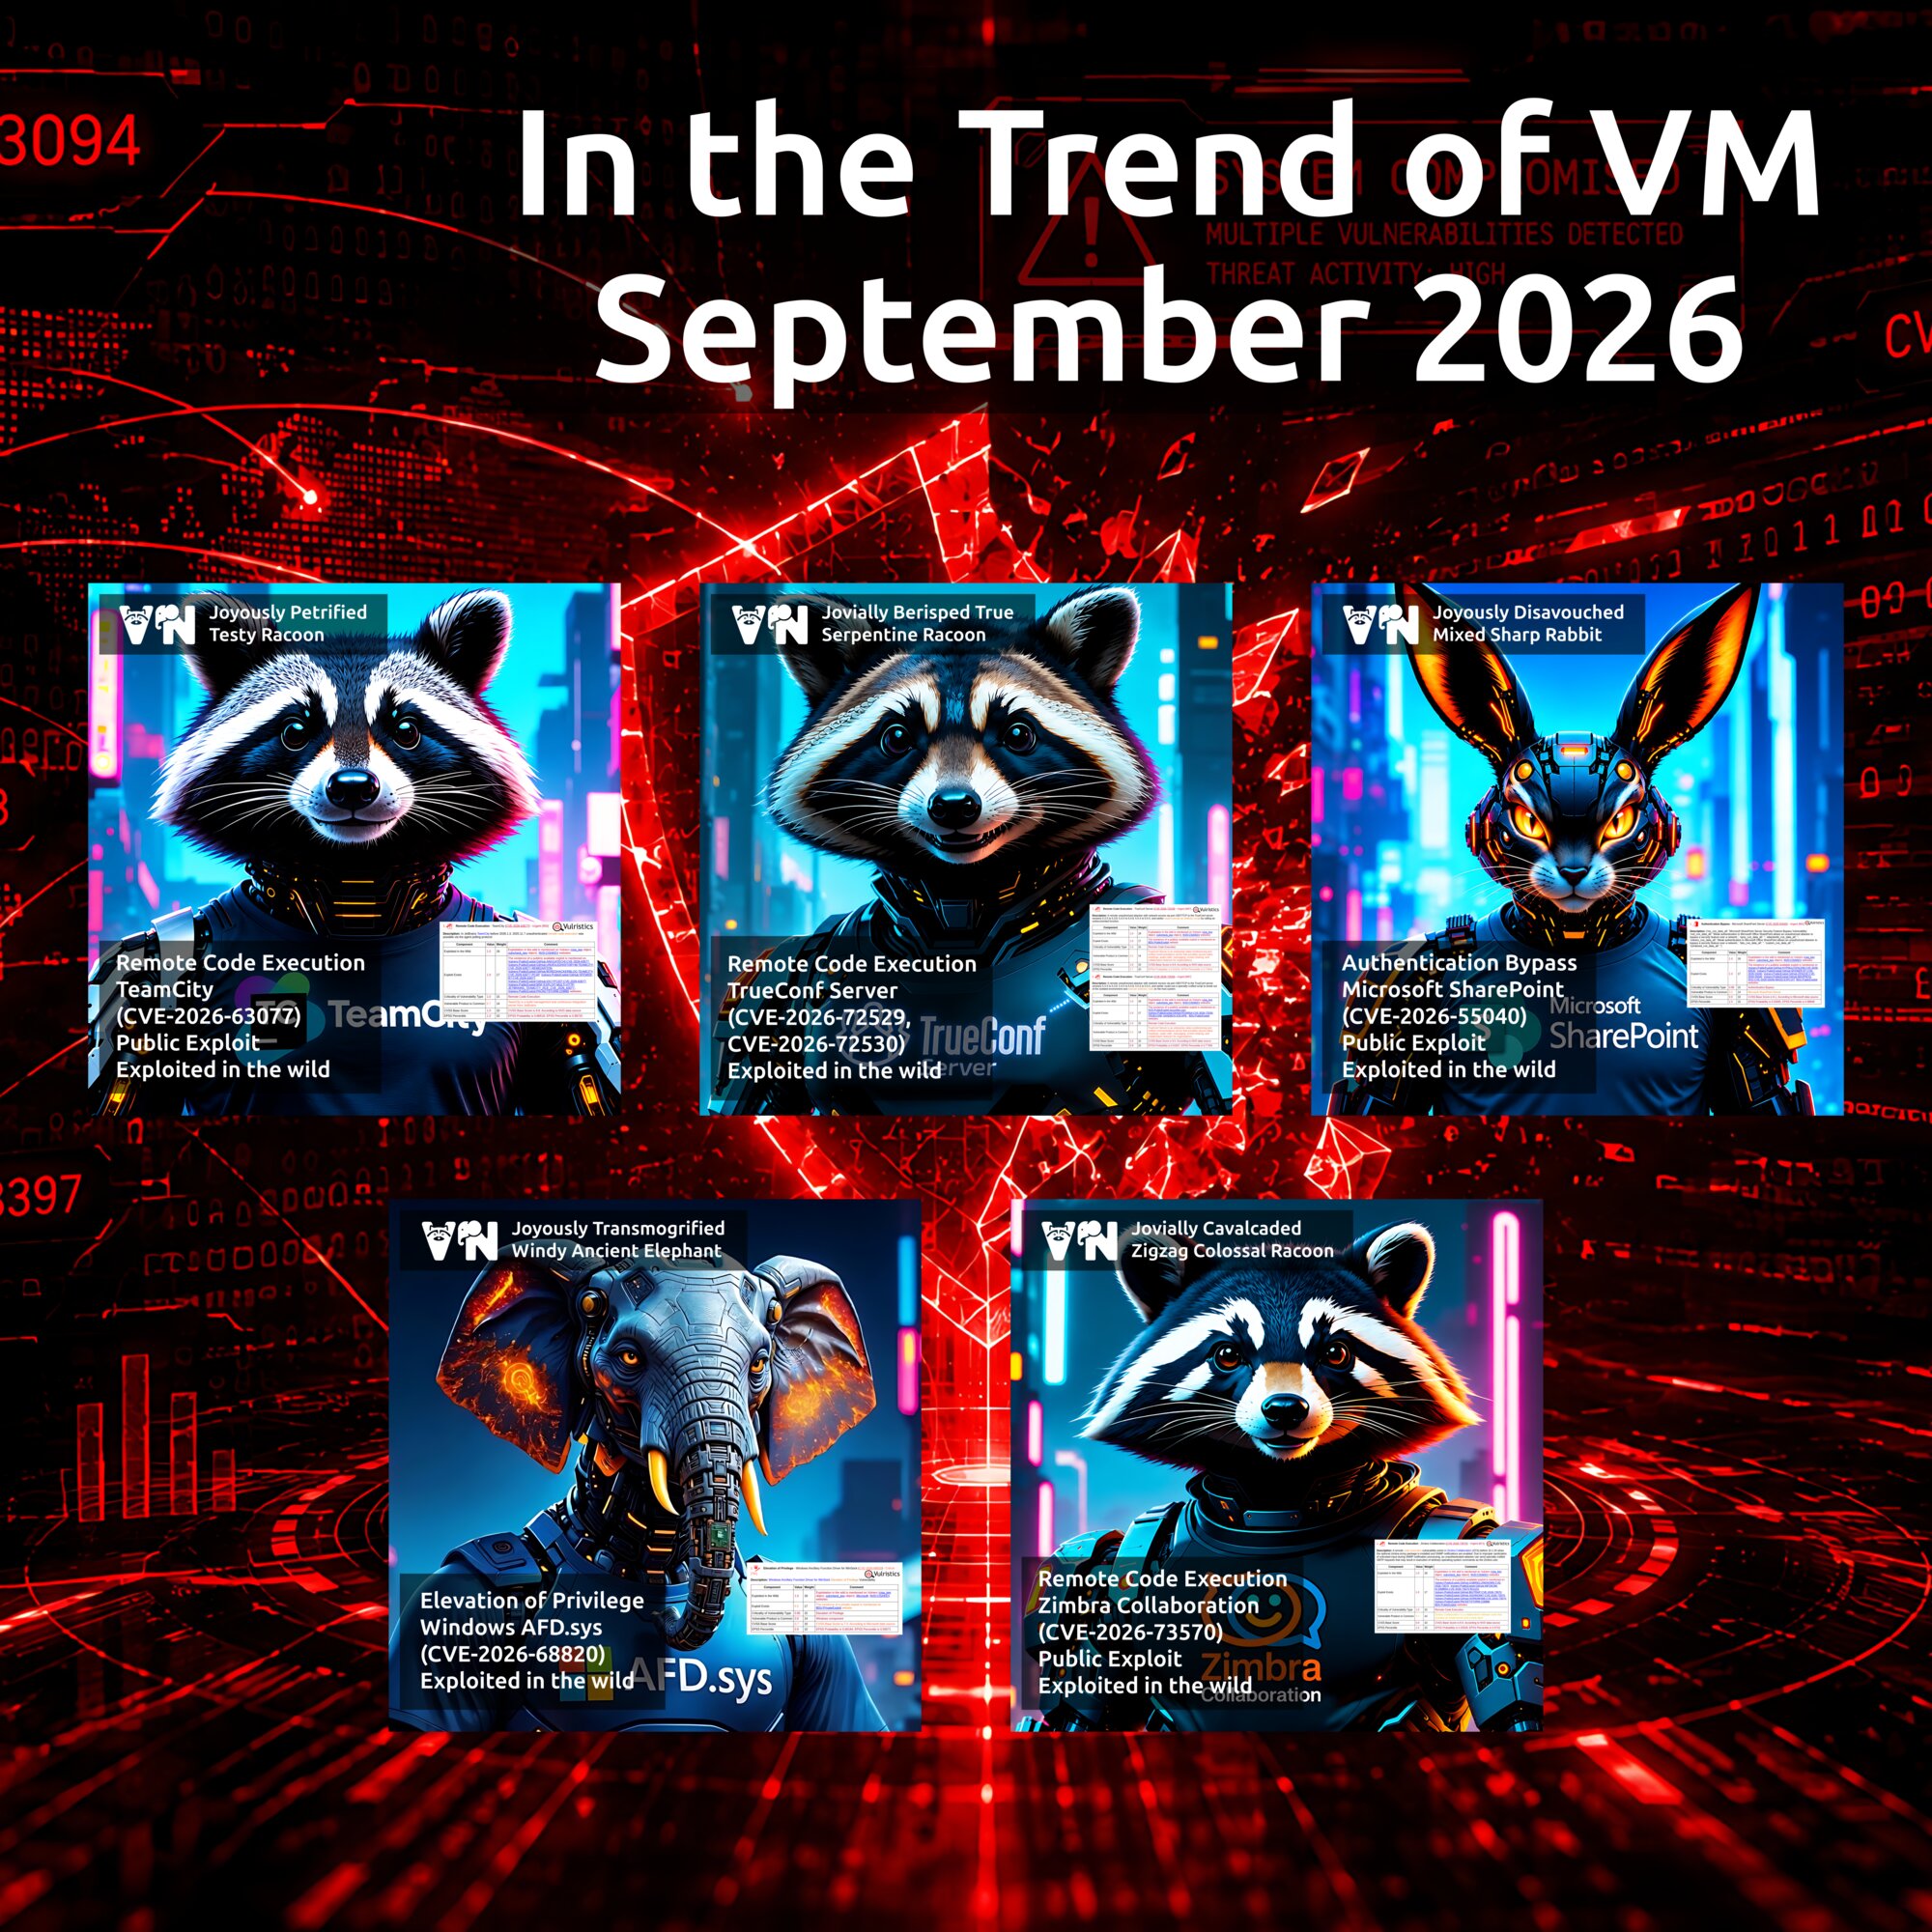
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.

🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.

🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.

🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal
About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability. SharePoint is a web application for corporate intranet portals, document management, and collaboration. This vulnerability was disclosed as part of the July Microsoft Patch Tuesday. A remote unauthenticated attacker can leverage this vulnerability to bypass authentication on a vulnerable SharePoint server and perform operations as a SharePoint site user or administrator. The vulnerability is due to several issues in the JWT token validation pipeline. A JWT (JSON Web Token) is essentially an "electronic pass" that SharePoint uses to determine who a user is and what actions they are authorized to perform. When combined with CVE-2026-63520, the vulnerability allows an attacker to perform remote code execution on a SharePoint server without authentication, with the privileges of the SharePoint service account. As a result, an attacker can gain access to documents and other organizational data stored in SharePoint, modify or delete them, extract credentials, install malware, and establish persistence in the system, and then use the compromised server for further penetration into the organization's internal network.

🛠 The vulnerability was discovered by Stephen Fewer from Rapid7 during SharePoint research conducted in January and March 2026. The research aimed to develop an exploit for the Pwn2Own Berlin competition. AI tools and agentic workflows were actively used throughout the research. Rapid7 published a detailed analysis of the vulnerability and the exploit code on its blog on August 11.

👾 According to VulnCheck, exploitation attempts were detected on honeypots shortly after the exploit was published. The vulnerability was added to the VulnCheck KEV on August 12 and to the CISA KEV on August 18.

⚙️ Updates are available for Microsoft SharePoint Server 2016 (Enterprise), 2019, and Subscription Edition. Note that you need to install the latest SharePoint cumulative updates that include fixes for CVE-2026-55040 and CVE-2026-63520.

🌐 As of August 25, 2026, Censys experts reported around 21,000 on-premises SharePoint installations exposing their version information. According to The Shadowserver Foundation, around 8,500 SharePoint servers were accessible from the Internet each day in September 2026. These are observed servers, and not all of them are necessarily vulnerable. No statistics on vulnerable servers are available.