Tag Archives: VulnCheck

September Linux Patch Wednesday

September Linux Patch Wednesday

September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.
🗒 Full Vulristics report

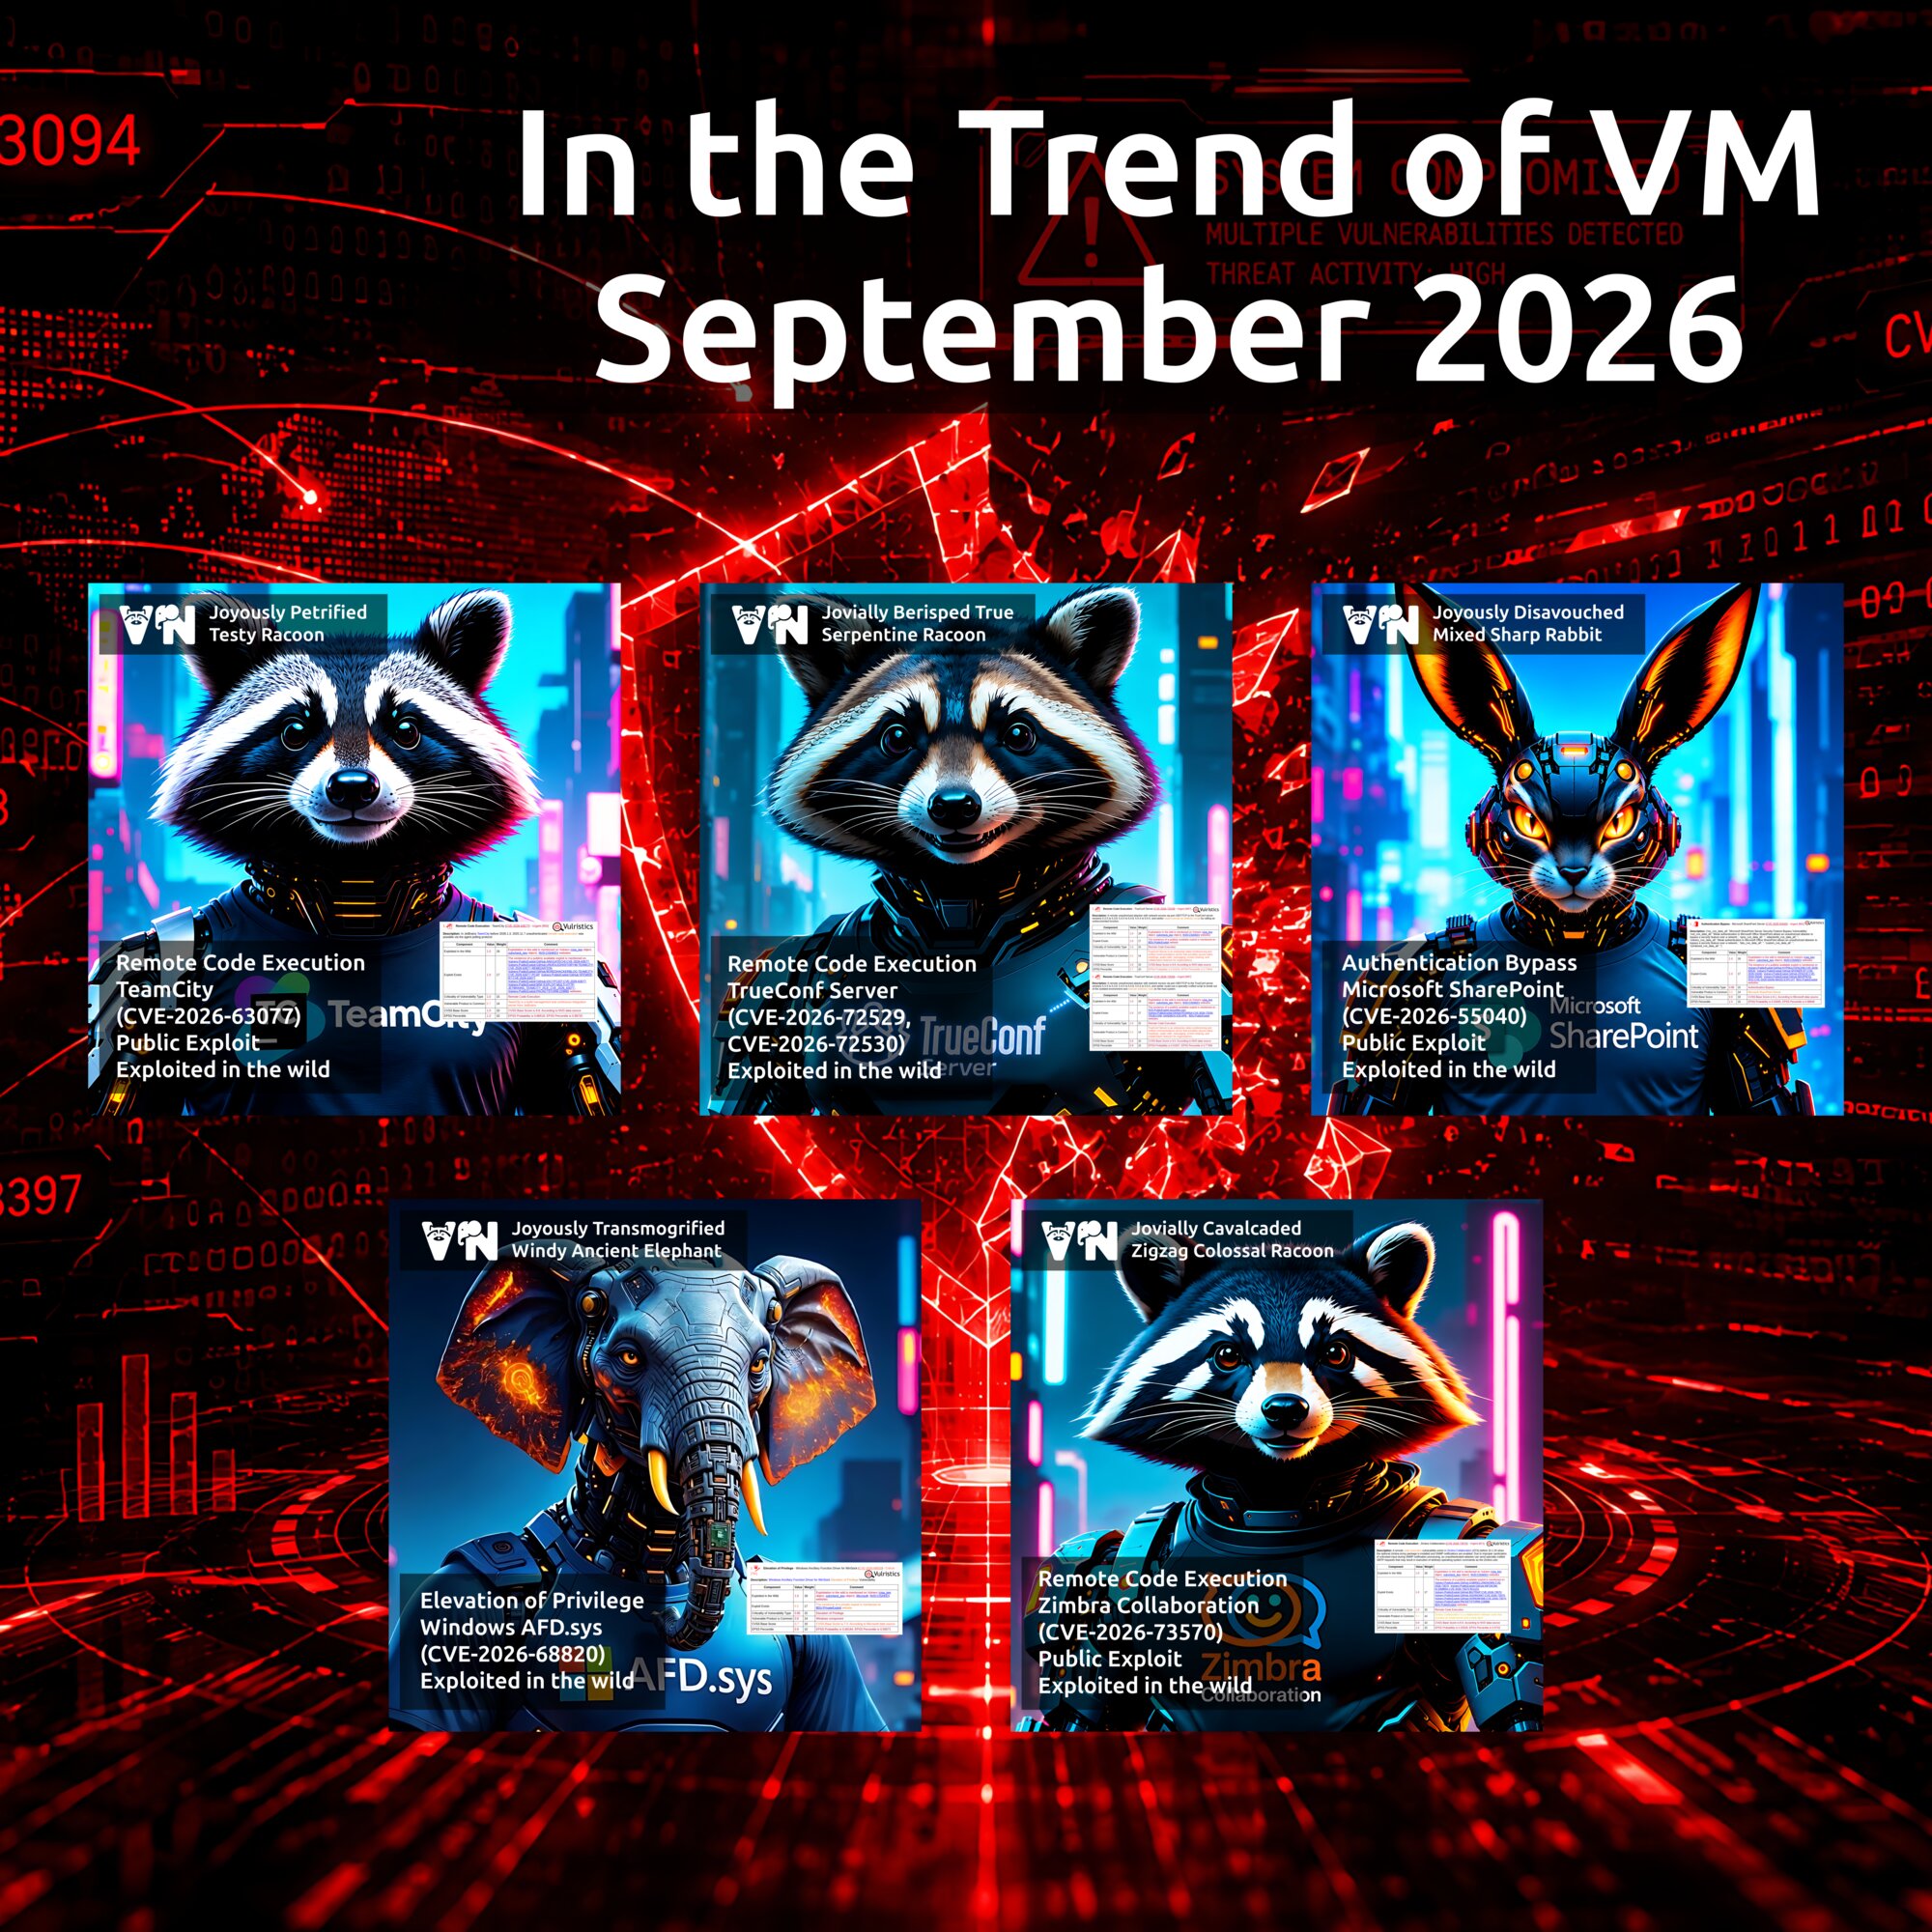
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September In the Trend of VM (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

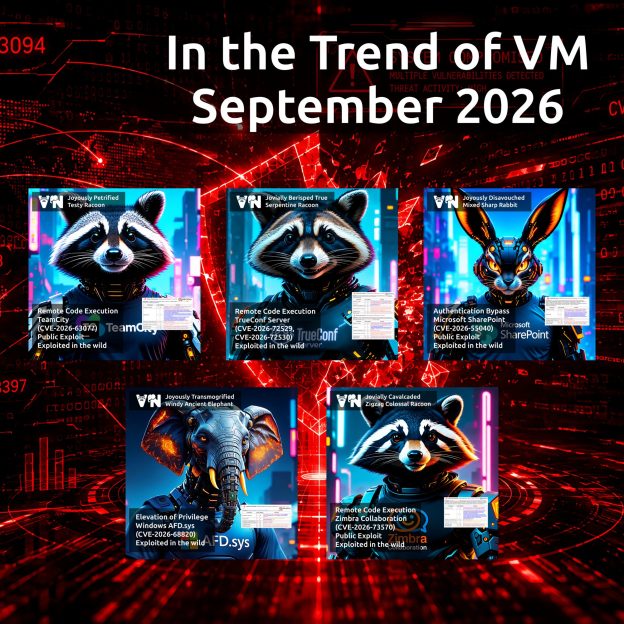
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.

🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.

🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.

🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability

About Authentication Bypass - Microsoft SharePoint (CVE-2026-55040) vulnerability. SharePoint is a web application for corporate intranet portals, document management, and collaboration. This vulnerability was disclosed as part of the July Microsoft Patch Tuesday. A remote unauthenticated attacker can leverage this vulnerability to bypass authentication on a vulnerable SharePoint server and perform operations as a SharePoint site user or administrator. The vulnerability is due to several issues in the JWT token validation pipeline. A JWT (JSON Web Token) is essentially an "electronic pass" that SharePoint uses to determine who a user is and what actions they are authorized to perform. When combined with CVE-2026-63520, the vulnerability allows an attacker to perform remote code execution on a SharePoint server without authentication, with the privileges of the SharePoint service account. As a result, an attacker can gain access to documents and other organizational data stored in SharePoint, modify or delete them, extract credentials, install malware, and establish persistence in the system, and then use the compromised server for further penetration into the organization's internal network.

🛠 The vulnerability was discovered by Stephen Fewer from Rapid7 during SharePoint research conducted in January and March 2026. The research aimed to develop an exploit for the Pwn2Own Berlin competition. AI tools and agentic workflows were actively used throughout the research. Rapid7 published a detailed analysis of the vulnerability and the exploit code on its blog on August 11.

👾 According to VulnCheck, exploitation attempts were detected on honeypots shortly after the exploit was published. The vulnerability was added to the VulnCheck KEV on August 12 and to the CISA KEV on August 18.

⚙️ Updates are available for Microsoft SharePoint Server 2016 (Enterprise), 2019, and Subscription Edition. Note that you need to install the latest SharePoint cumulative updates that include fixes for CVE-2026-55040 and CVE-2026-63520.

🌐 As of August 25, 2026, Censys experts reported around 21,000 on-premises SharePoint installations exposing their version information. According to The Shadowserver Foundation, around 8,500 SharePoint servers were accessible from the Internet each day in September 2026. These are observed servers, and not all of them are necessarily vulnerable. No statistics on vulnerable servers are available.

About Remote Code Execution - XWiki Platform (CVE-2025-24893) vulnerability

About Remote Code Execution - XWiki Platform (CVE-2025-24893) vulnerability

About Remote Code Execution - XWiki Platform (CVE-2025-24893) vulnerability. XWiki is a free and open-source wiki platform written in Java, with a strong focus on extensibility. It supports WYSIWYG visual editing, importing and exporting documents in OpenDocument format, adding annotations and tags, as well as flexible access rights management. The vulnerability allows an attacker with guest-level privileges to execute arbitrary code on the server by sending a crafted SolrSearch request.

⚙️ The vulnerability was fixed in versions 15.10.11, 16.4.1 and 16.5.0RC1, released in July 2024.

🛠 A proof-of-concept (POC) exploit was available in the original task to fix ZDI-CAN-23994, as well as in the security bulletin published on February 20, 2025. There are now more than 30 exploit variants on GitHub.

👾 On October 28, VulnCheck reported that the vulnerability was being exploited in the wild to deploy cryptominers. On October 30, it was added to the CISA KEV catalog.

На русском

I looked at VulnCheck KEV

I looked at VulnCheck KEV
I looked at VulnCheck KEVI looked at VulnCheck KEVI looked at VulnCheck KEVI looked at VulnCheck KEVI looked at VulnCheck KEVI looked at VulnCheck KEV

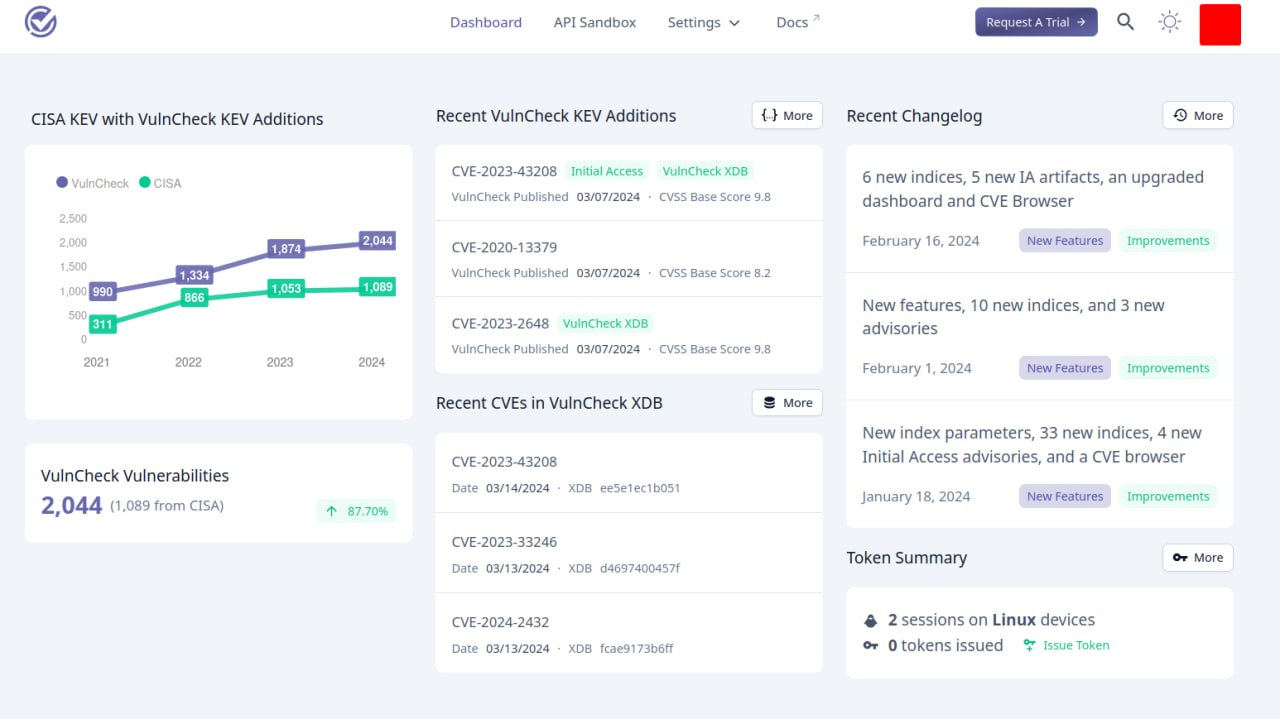
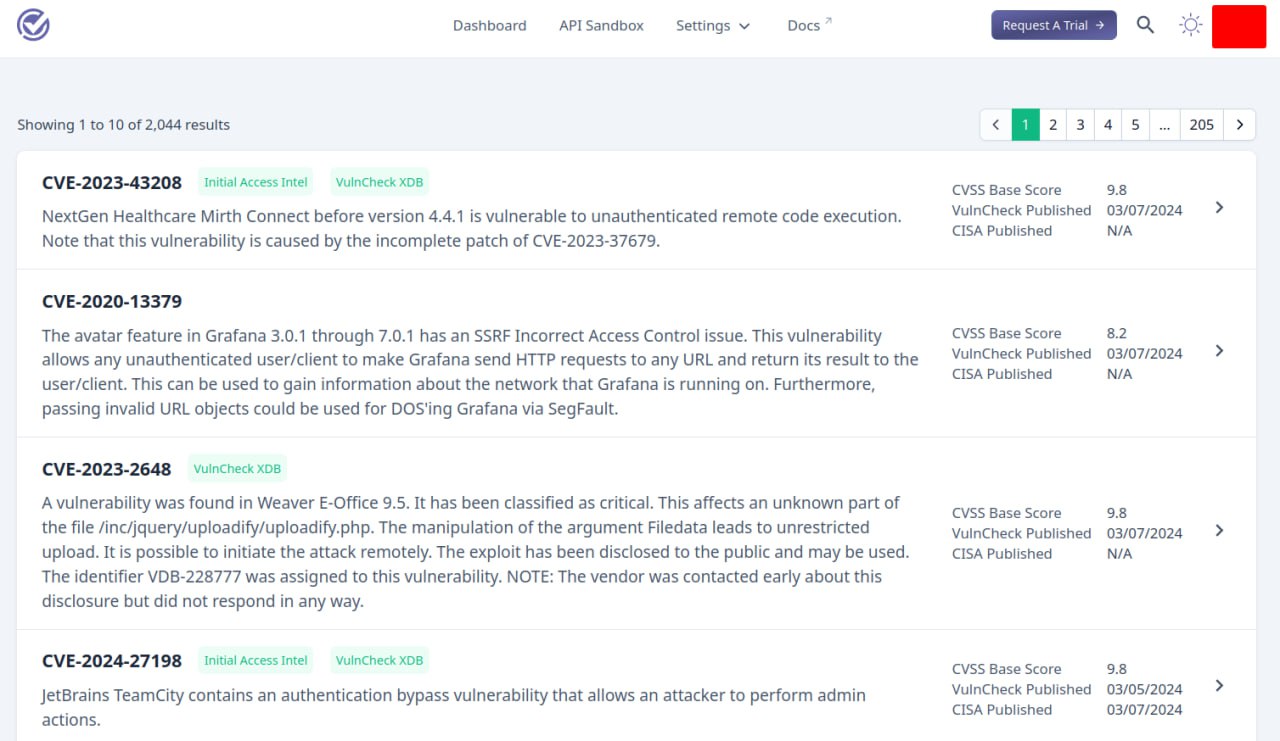
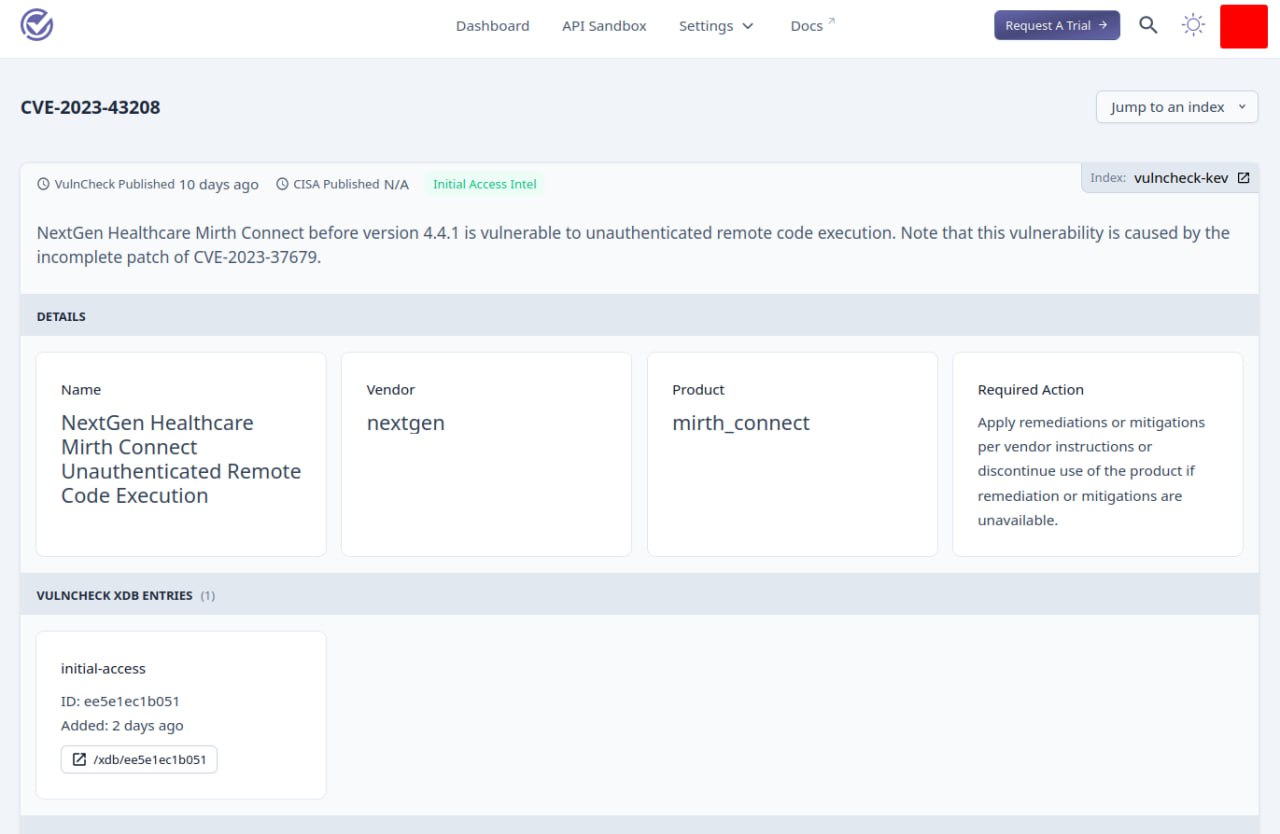
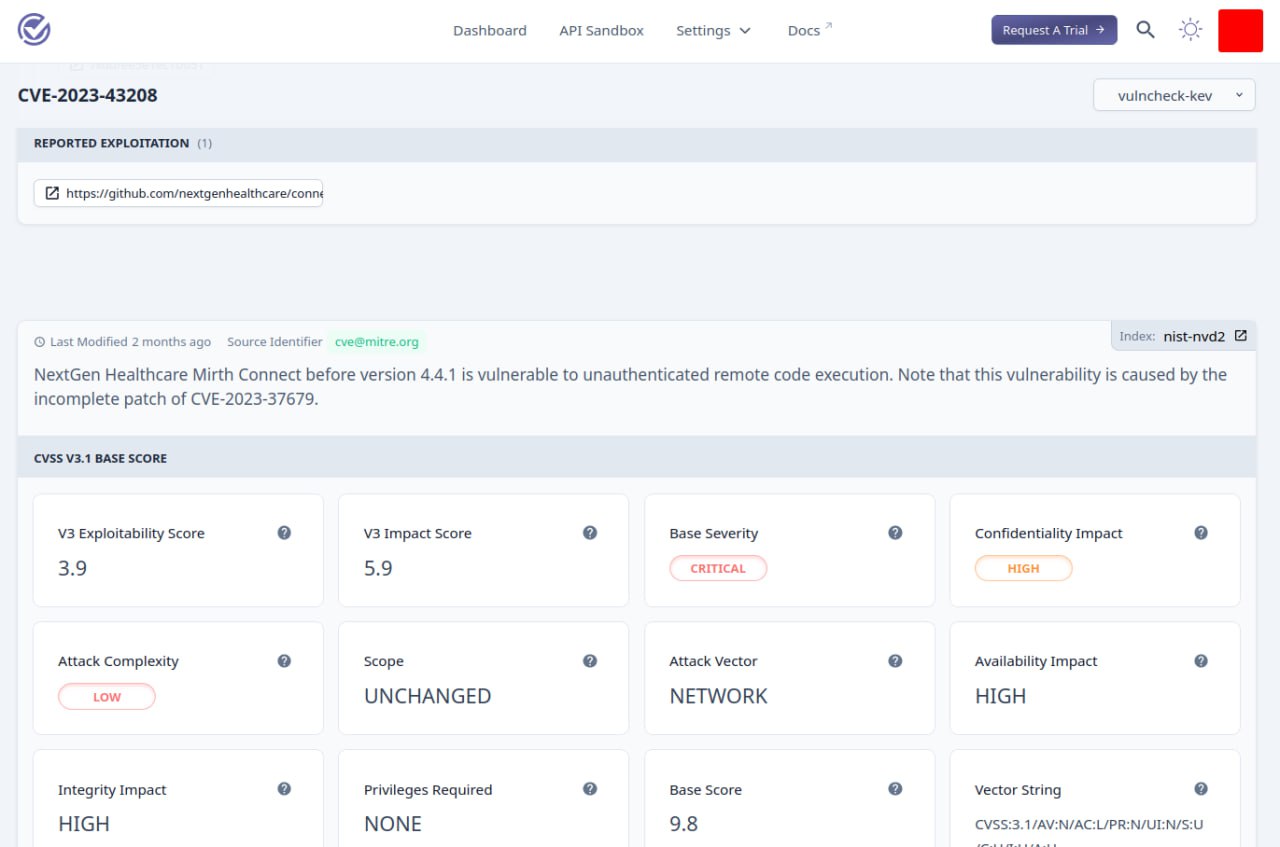
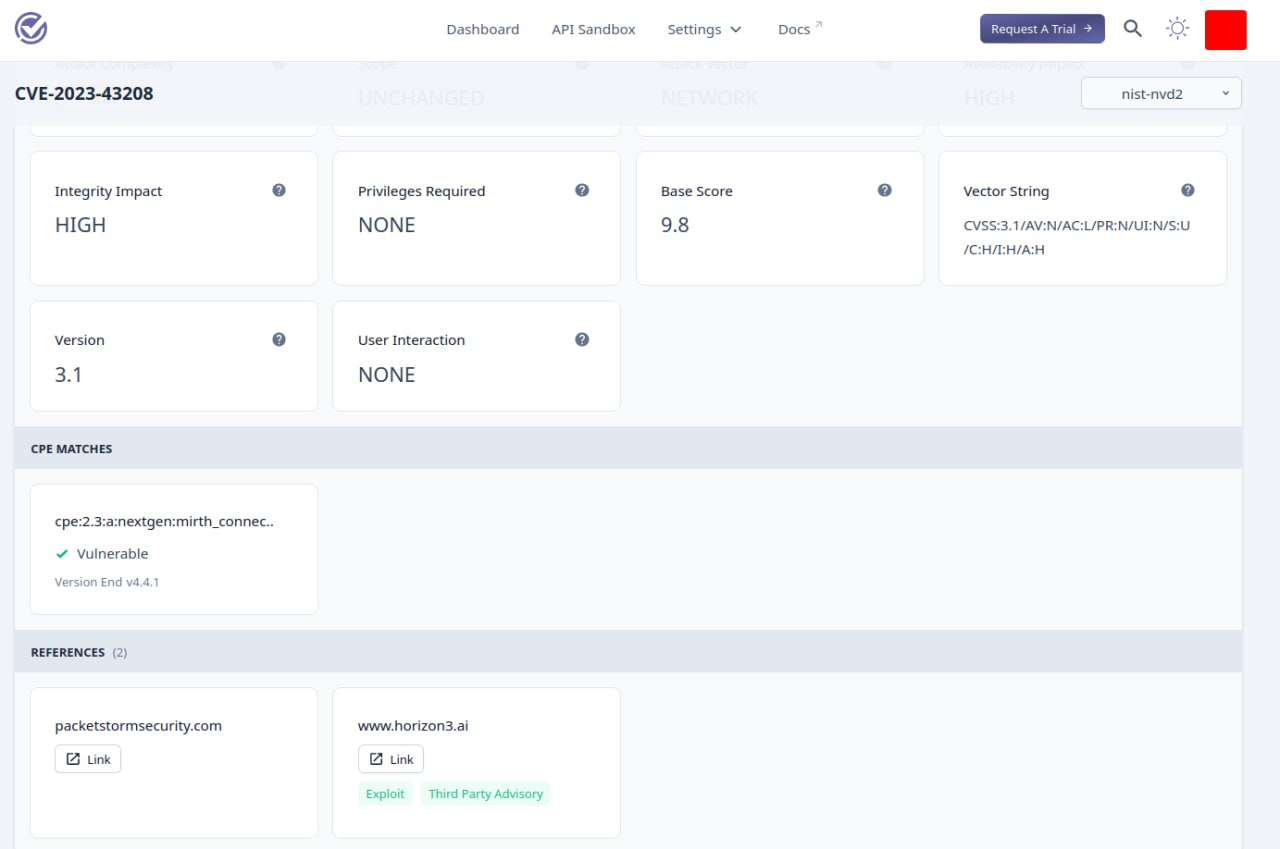
I looked at VulnCheck KEV. This is an analogue of CISA KEV (Know Exploited Vulnerabilities) by VulnCheck.

🔹 Unlike the public CISA KEV, only registered users have access to VulnCheck KEV. The VulnCheck website is accessible from Russian IPs 🇷🇺, but when registering they write that "account is currently under review" (in fact requests are simply blocked 🥸). Requests from non-Russian IPs are registered automatically. 🌝
🔹 There are ~2 times more CVEs in the database than in CISA KEV.
🔹 There are no standard tools for downloading all these CVEs via web-gui. 🤷‍♂️
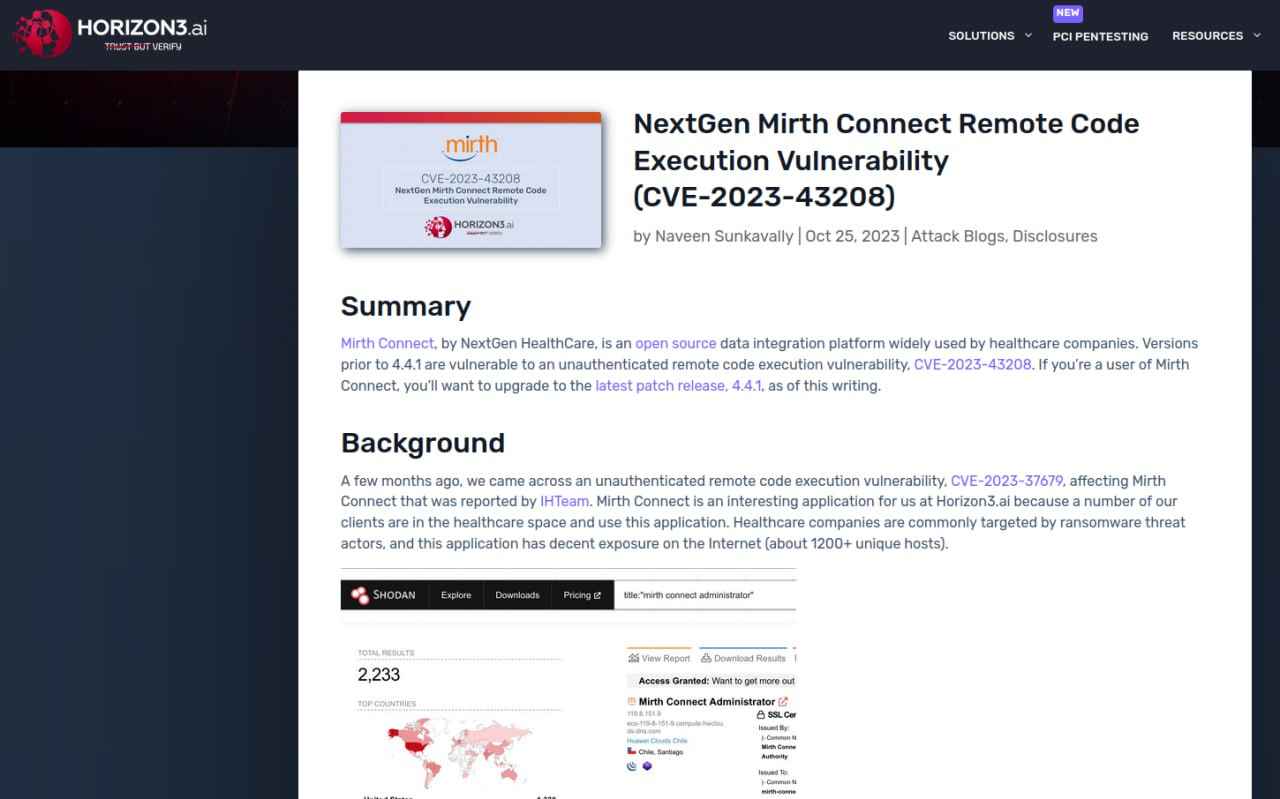
🔹 There are links to exploits for CVEs that look good. 👌
🔹 There are signs of exploitation in the wild. Sometimes it's clear, like "Outbreak Alerts 2023" pdf report. Sometimes it’s strange, like a link to a Shadowserver dashboard or a non-related blog post. 🤷‍♂️

The selection of CVEs is quite interesting, but the rationale for exploitation in the wild needs to be improved. 😉

На русском