Tag Archives: V8

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

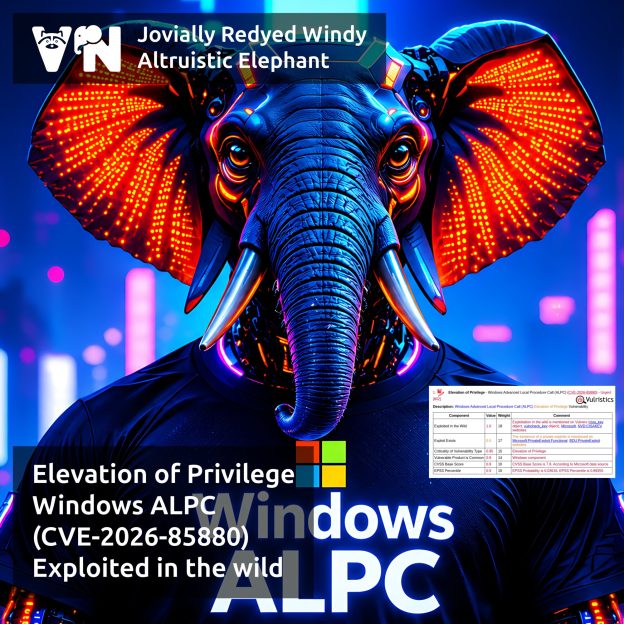
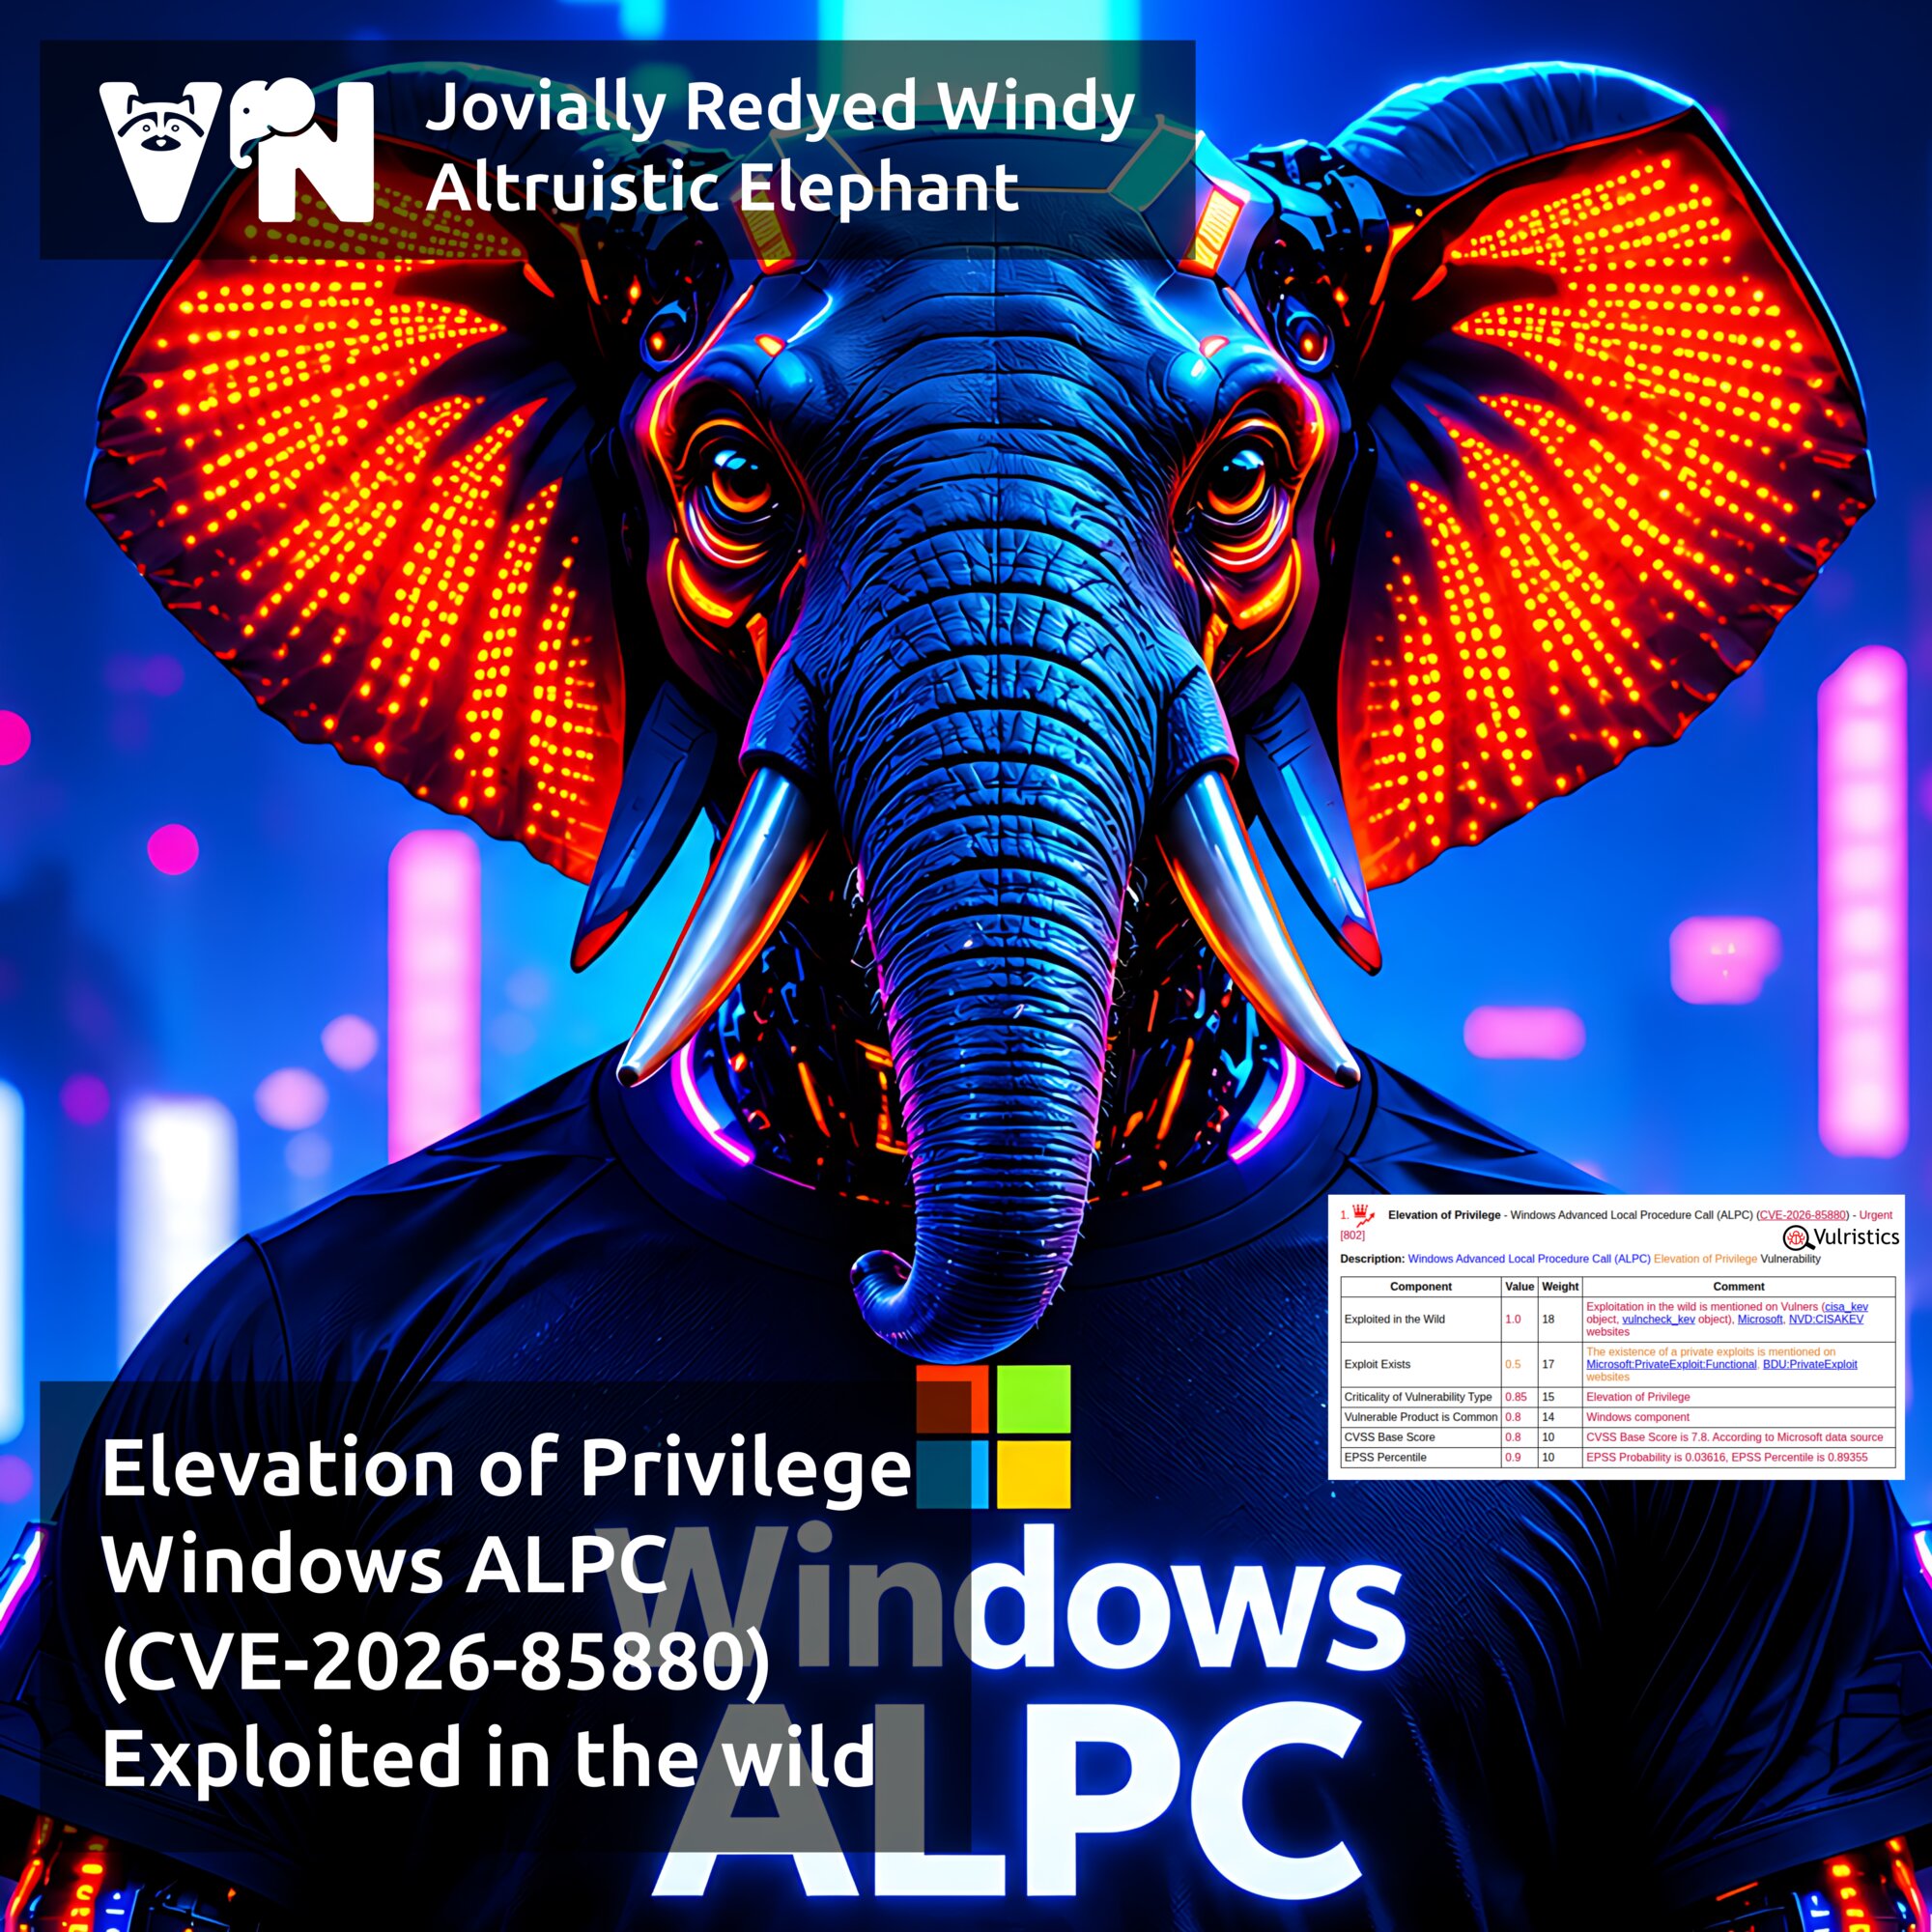
🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.

September Linux Patch Wednesday

September Linux Patch Wednesday

September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.

🗒 Full Vulristics report

June Linux Patch Wednesday

June Linux Patch Wednesday

June Linux Patch Wednesday. A total of 1,888 vulnerabilities (324 in the Linux kernel, and a whopping 728 in Chromium ❗️). For comparison, there were 1,638 vulnerabilities in May. The increase isn't as dramatic as it was from April to May, but it's still a new record. One of the vulnerabilities has been flagged as actively exploited in the wild:

🔻 RCE - Chromium (CVE-2026-11645). Chromium is the open-source web browser project that serves as the foundation for many modern browsers, including Google Chrome, Microsoft Edge, Brave, Opera, and Vivaldi. A publicly available Metasploit module exploits a vulnerability in the web browser's V8 JavaScript engine. The vulnerability is triggered by a specific code pattern that causes type confusion between internal V8 objects, resulting in out-of-bounds memory access. Successful exploitation may lead to remote code execution in the context of the browser process.

There are also 109 vulnerabilities with public exploits or evidence that exploits exist, although there are no signs of active exploitation in real-world attacks yet. Among them, the following stand out:

🔸 EoP - Linux Kernel "CIFSwitch" (CVE-2026-46243). This vulnerability could allow attackers to forge CIFS authentication key descriptions, abuse the kernel's key request mechanism, and gain root privileges.

🔸 EoP - Linux Kernel "PinTheft" (CVE-2026-43494). On a successfully exploited configuration, the chain completes and hands off to the discovered SUID binary with an overwritten first page - yielding a root shell if the race and kernel state align.

🔸 RCE - Apache ActiveMQ (CVE-2026-42588). ActiveMQ is an open-source message broker written in Java. Exploitation of this vulnerability requires valid credentials for the ActiveMQ Web Console. However, the default credentials are admin/admin.

🔸 InfDisc - Squid "Squidbleed" (CVE-2026-47729). Squid is an open-source caching proxy server. The vulnerability causes Squid's FTP parser to read beyond the boundary of a memory buffer, into a region that may contain a previous user's uncleared HTTP request data.

🔸 AuthBypass - Nextcloud (CVE-2026-45156). Nextcloud is an open source content collaboration platform. A missing signature verification in User OIDC allowed a malicious ID4me authority to identify as any user.

🔸 XSS - Nextcloud (CVE-2025-59788). A vulnerability in a reachable files_pdfviewer example directory in Nextcloud allows attackers to execute arbitrary JavaScript in the context of a user's browser via a crafted PDF file to viewer.html.

🔸 XSS - Roundcube (CVE-2026-48849). Roundcube is a free, open-source webmail application. An unsanitized subject field in the draft restored value could lead to stored XSS/HTML/CSS injection on shared mailboxes.

🔸 DoS - ImageMagick (CVE-2026-46522). ImageMagick is an open-source image processing tool used to create, edit, and convert images. Due to a missing check in the MIFF decoder, a crafted file could cause an infinite loop resulting in CPU exhaustion.

🗒 Full Vulristics report
Microsoft Patch Tuesday December 2022: SPNEGO RCE, Mark of the Web Bypass, Edge Memory Corruptions

Microsoft Patch Tuesday December 2022: SPNEGO RCE, Mark of the Web Bypass, Edge Memory Corruptions. Hello everyone! This episode will be about Microsoft Patch Tuesday for December 2022, including vulnerabilities that were added between November and December Patch Tuesdays. As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities.

Alternative video link (for Russia): https://vk.com/video-149273431_456239112

But let’s start with an older vulnerability. This will be another example why vulnerability prioritization is a tricky thing and you should patch everything. In the September Microsoft Patch Tuesday there was a vulnerability Information Disclosure – SPNEGO Extended Negotiation (NEGOEX) Security Mechanism (CVE-2022-37958), which was completely unnoticed by everyone. Not a single VM vendor paid attention to it in their reviews. I didn’t pay attention either.

Continue reading →