Tag Archives: PrivilegeEscalation

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

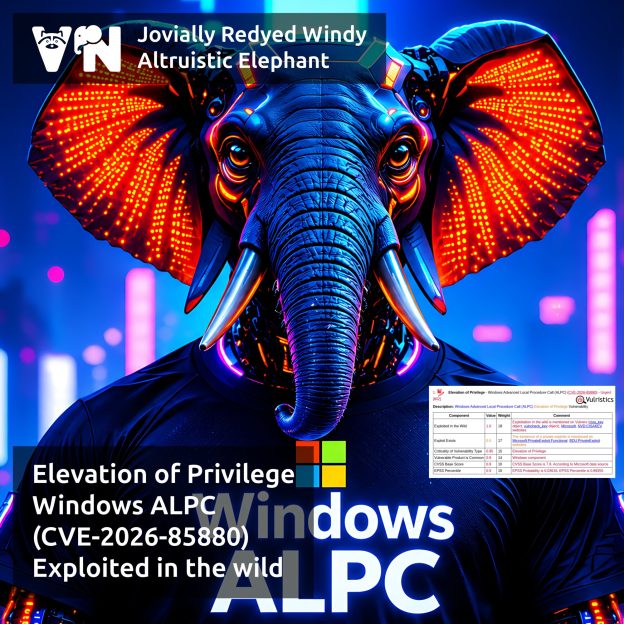
🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August In the Trend of VM (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint. I present the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous July edition, there was just one vulnerability. This time, there are four.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - ViPNet Client (BDU:2026-09885). The first trending vulnerability in a Russian-made product since the beginning of 2026. Its exploitation was discovered by Positive Technologies experts.

🔻 EoP - NT OS Kernel (CVE-2026-42980). The vulnerability allows an attacker to escalate privileges to NT AUTHORITY\SYSTEM level.

🔻 EoP - Microsoft SharePoint (CVE-2026-56164) and RCE - Microsoft SharePoint (CVE-2026-58644). Two actively exploited vulnerabilities in a popular platform for building corporate websites, managing documents, and collaborating.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability. Information about this vulnerability was disclosed as part of the June Microsoft Patch Tuesday on June 9. The vulnerability was not specifically highlighted in Microsoft Patch Tuesday reviews published by VM vendors. This Microsoft Windows NT OS Kernel elevation of privilege vulnerability is caused by improper handling of integer values during data construction in the Windows Management Instrumentation (WMI) subsystem, resulting in an out-of-bounds write. Successful exploitation allows a local attacker with low privileges (a standard user account) to escalate privileges to NT AUTHORITY\SYSTEM. Obtaining NT AUTHORITY\SYSTEM privileges grants full control over the affected host, enabling an attacker to execute arbitrary commands, modify security settings, access protected data, and use the compromised host as a foothold for further lateral movement within the target environment.

🛠 On July 7, a detailed write-up describing the exploitation of this vulnerability was published. A public proof-of-concept (PoC) exploit is also available on GitHub.

👾 There is currently no evidence of in-the-wild exploitation of this vulnerability.

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday. Last week I was on vacation in Veliky Novgorod, so I'm publishing this overview only now. A total of 202 vulnerabilities were addressed, approximately twice as many as in May. There are currently no vulnerabilities marked as exploited in the wild. However, there are two vulnerabilities with publicly available exploits:

🔸 RCE - HTTP.sys (CVE-2026-47291). This critical vulnerability allows remote, unauthenticated attackers to execute arbitrary code on affected systems without user interaction. However, systems using the default MaxRequestBytes registry value in the Windows HTTP stack are not affected. If needed, you can change this registry setting to protect systems while testing and deploying the patch. Microsoft's security bulletin includes instructions and a PowerShell script for this workaround.

🔸 DoS - HTTP.sys (CVE-2026-49160). The same exploit is used as for the previous RCE vulnerability.

It is also worth paying attention to vulnerabilities that Microsoft has flagged as having a publicly available exploit:

🔹 SFB - Windows BitLocker (CVE-2026-50507). A successful attacker could bypass the BitLocker Device Encryption feature on the system storage device. An attacker with physical access to the target could exploit this vulnerability to gain access to encrypted data. According to Tenable, this is the "Bitskrieg" vulnerability discovered by the researcher known as Chaotic Eclipse/Nightmare Eclipse.

🔹 SFB - Secure Boot (CVE-2026-48570). An attacker who successfully exploited this vulnerability could bypass Secure Boot. This vulnerability was reported by Alon Leviev (STORM), who is known for previous research related to BootKitty and BlackLotus.

Among the remaining vulnerabilities, the following are worth highlighting:

🔹 RCE - Windows Kernel (CVE-2026-45657). This vulnerability allows remote, unauthenticated attackers to run code with SYSTEM privileges without any user interaction. In other words, it could be used to spread automatically between systems. The issue is caused by how the Windows kernel processes TCP/IP traffic. Microsoft rated this as "Exploitation Less Likely", but security researchers and exploit developers are already analyzing the patch and trying to build an exploit. Test and deploy this patch as soon as possible.

🔹 EoP - Windows Collaborative Translation Framework (CTFMON) (CVE-2026-45586). This vulnerability affects a component used for voice and handwriting recognition. If exploited, an attacker could gain SYSTEM privileges. Microsoft rates this vulnerability as "Exploitation More Likely".

🔹 RCE - Windows Remote Desktop Client (CVE-2026-42909, CVE-2026-42913, CVE-2026-42985, CVE-2026-42992, CVE-2026-42993, CVE-2026-44799, CVE-2026-44801, CVE-2026-47289, CVE-2026-47653, CVE-2026-47654, CVE-2026-48563). Successful exploitation would require a victim to connect to an attacker-controlled server using an affected version of the Remote Desktop Client. This action could trigger a heap-based buffer overflow, resulting in remote code execution.

🔹 RCE - DHCP Client Service (CVE-2026-44815). This vulnerability allows remote, unauthenticated attackers to execute code on affected systems without user interaction. Because the DHCP client is widely enabled across Windows systems, this vulnerability presents a broad attack surface. Organizations should prioritize testing and deploying the patch for this vulnerability as soon as possible.

🗒 Full Vulristics report