Tag Archives: WindowsKernel

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities

October In the Trend of VM (#32): Windows and Check Point vulnerabilities

October "In the Trend of VM" (#32): Windows and Check Point vulnerabilities. Here is the latest edition of Positive Technologies' traditional monthly roundup of trending vulnerabilities. The previous September edition featured six vulnerabilities. This time, there are just two.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Windows ALPC (CVE-2026-85880). A vulnerability in Windows' interprocess communication mechanism that is exploited in the wild to escalate privileges to SYSTEM. The exploit is included in the BlueMoon exploit kit.

🔻 RCE - Check Point Quantum Security Gateway (CVE-2026-85102). A vulnerability in Check Point's enterprise security gateways that allows an unauthenticated remote attacker to execute arbitrary code. The vulnerability is being actively exploited in the wild, and public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

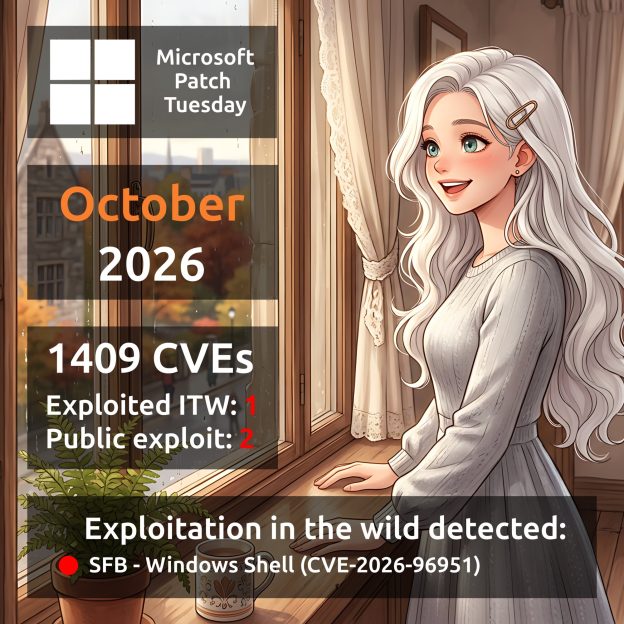
October Microsoft Patch Tuesday. A total of 1,409 vulnerabilities. For comparison, there were 973 in September, an increase of about 45%. 🙈 Thirteen products had fixes for 20 or more vulnerabilities: Microsoft Office Excel (68), Windows Kernel (46), Role: DNS Server (41), Windows Installer (38), Microsoft Office SharePoint (35), Windows Win32k (31), Windows NTFS (26), .NET (25), Microsoft Windows Search Component (23), Microsoft Office Word (22), Windows Error Reporting (21), Windows Broadcast DVR User Service (20), and Microsoft SQL Server (20). A total of 416 vulnerabilities were fixed in these products. That's 30% of all vulnerabilities. One vulnerability is flagged as exploited in the wild:

🔻 SFB - Windows Shell (CVE-2026-96951). The vulnerability allows an attacker to bypass Mark of the Web (MOTW), a Windows feature that marks files downloaded from the Internet. To exploit it, the attacker must trick the user into opening a malicious file or clicking a malicious link.

There are two vulnerabilities with public exploits:

🔸 RCE - Raw Image Extension (CVE-2026-21413). A heap-based buffer overflow in Windows Raw Image Extension allows an attacker to execute arbitrary code remotely using a specially crafted file. A technical write-up of the vulnerability, which NVD classifies as an exploit, was published on the Cisco Talos blog on April 7.

🔸 EoP - Windows Health and Optimized Experiences Service (CVE-2026-85884). Missing authentication for a critical function in Windows Health and Optimized Experiences Service allows a local attacker to gain SYSTEM privileges. A public exploit has been available on GitHub since October 13.

Other notable vulnerabilities include:

🔹 RCE - Microsoft Exchange (CVE-2026-70571). An unauthenticated attacker can send a specially crafted email to a vulnerable Exchange server and execute arbitrary code on the server. The attack requires an in-depth understanding of the target environment. No user interaction is required.

🔹 RCE - Microsoft Office Outlook (CVE-2026-70242, CVE-2026-97749, CVE-2026-97016, CVE-2026-88156, CVE-2026-70291). An attacker can execute arbitrary code on the victim's device by sending a specially crafted email. To exploit the vulnerability, the victim only needs to view the email in Outlook's reading pane without opening it or taking any further action.

🔹 RCE - Windows Domain Name Service (CVE-2026-96113). A heap-based buffer overflow in DNS Server allows an unauthorized attacker to execute code over a network.

🔹 SFB - .NET Framework (CVE-2026-108398). An authenticated attacker can place a specially crafted .NET assembly on an affected system and register it to be loaded by a protected process. This allows the attacker to bypass Windows Defender Application Control (WDAC) restrictions and run unauthorized code within the protected process. No user interaction is required.

🔹 Spoofing - Microsoft Exchange (CVE-2026-70279). An attacker can send a specially crafted link to a user and trick them into opening it. No authentication is required. If the user has administrator privileges, the attacker could act as that user and access or modify the organization's data.

🗒 Full Vulristics report
About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability

About Elevation of Privilege - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880) vulnerability. ALPC is an internal Windows mechanism for high-speed message exchange between processes. It is used by Windows system components. This vulnerability was addressed in the September Microsoft Patch Tuesday. An attacker who can execute code in a low-privilege AppContainer could exploit this vulnerability locally to escape the sandbox and elevate privileges on the affected system. No additional user interaction is required. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. With SYSTEM privileges, the attacker may attempt to disable or bypass antivirus software and other Windows security tools, steal credentials and authentication tokens, maintain persistence on the system, and expand the attack across the corporate network, including by deploying malware.

👾 Microsoft experts reported evidence of in-the-wild exploitation on the day the September MSPT updates were released (September 8). On the same day, the vulnerability was added to the CISA KEV catalog. On September 9, Proofpoint experts reported on the BlueMoon exploit kit, which had been used in attacks since August 28. BlueMoon exploited three vulnerabilities in sequence: CVE-2026-85046 (a type confusion vulnerability in Chromium V8), CVE-2026-87491 (a V8 sandbox escape), and CVE-2026-85880 (a Windows kernel privilege escalation vulnerability in ALPC, with WNF - the Windows Notification Facility - also involved in exploitation). The exploit kit was used in attacks targeting US non-governmental organizations (NGOs), mining and materials companies, US aerospace companies, an unnamed manufacturing company in Vietnam, and government, consulting, and financial organizations in Indonesia and Singapore.

🛠 No public exploits have been observed so far.

⚙️ Security updates are available for Windows 10 versions 1607, 1809, 21H2, and 22H2, as well as Windows Server 2012, 2012 R2, 2016, 2019, and 2022.

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability

About Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2026-68820) vulnerability. The Ancillary Function Driver (AFD) is a Windows component that supports Windows Sockets applications and is contained in the afd.sys file. The afd.sys driver runs in kernel mode and manages the Winsock TCP/IP communications protocol. This vulnerability is from the August Microsoft Patch Tuesday. Use-after-free (CWE-416) in the Windows Ancillary Function Driver for WinSock allows an authorized attacker to elevate privileges locally to SYSTEM level. Successful exploitation requires an attacker to win the race condition. As a result, the attacker can gain full control over the Windows host, execute commands with SYSTEM-level privileges, disable security protections, install malware, and access other users' data.

👾 The vulnerability was already being exploited in the wild when it was disclosed as part of Microsoft's August Patch Tuesday on August 11. That same day, it was added to the CISA KEV catalog. Notably, Microsoft listed the Exploit Code Maturity in the CVSS as "Unproven". 🤷‍♂️ Microsoft credited researchers from Check Point for reporting the vulnerability.

Details on how the vulnerability was exploited in attacks were published in a Check Point blog post on August 11. The vulnerability was exploited as part of the "Operation Dream Job" campaign, which targeted organizations worldwide, with a particular focus on the defense sector in Europe and India. The campaign is linked to the Lazarus Group. The campaign begins with targeted phishing messages offering victims attractive job opportunities at well-known companies in the defense, aerospace, and aviation industries. Victims are lured into opening a PDF decoy masquerading as a Lockheed Martin job description. This triggers the execution of a lightweight in-memory loader - MISTPEN. The loader uses the Microsoft Graph API to access OneDrive, from which it retrieves additional modules and runs them in memory. During the initial stages of the infection, the attacker deploys several reconnaissance modules that gather information about the system and running processes. Once the target is deemed of interest, MISTPEN retrieves an additional persistence module, which installs the malware on disk and ensures that MISTPEN is automatically launched after a system reboot. After establishing persistence, MISTPEN loads an in-memory module designed to exploit the CVE-2026-68820 vulnerability. Check Point researchers believe that this vulnerability was already being exploited in the "Operation Dream Job" campaign in early July 2026. Successful exploitation enables the malware to launch FudModule, a Lazarus kernel-level rootkit, with SYSTEM privileges. The final backdoor delivered by MISTPEN - ForestTiger - provides attackers with remote access to the compromised system, allowing them to execute commands, collect host information, and download additional malicious components.

🛠 No public exploits have been observed so far. Some people are offering exploits for sale, but they don't look reliable.

⚙️ Security updates are available for Windows 10, Windows 11, and Windows Server 2019.

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August In the Trend of VM (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint

August "In the Trend of VM" (#30): vulnerabilities in ViPNet Client, the Microsoft Windows kernel, and Microsoft SharePoint. I present the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. In the previous July edition, there was just one vulnerability. This time, there are four.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - ViPNet Client (BDU:2026-09885). The first trending vulnerability in a Russian-made product since the beginning of 2026. Its exploitation was discovered by Positive Technologies experts.

🔻 EoP - NT OS Kernel (CVE-2026-42980). The vulnerability allows an attacker to escalate privileges to NT AUTHORITY\SYSTEM level.

🔻 EoP - Microsoft SharePoint (CVE-2026-56164) and RCE - Microsoft SharePoint (CVE-2026-58644). Two actively exploited vulnerabilities in a popular platform for building corporate websites, managing documents, and collaborating.

🟥 The full list of trending vulnerabilities is available on the portal

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday. A total of 401 vulnerabilities were addressed - 170 fewer than in July. One of the vulnerabilities is known to be actively exploited in the wild:

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). A local attacker can exploit this vulnerability to gain SYSTEM-level privileges. There is a contradiction in Microsoft's description: the Exploit Code Maturity in CVSS is marked as "Unproven", while at the same time Microsoft states that the vulnerability is being exploited in the wild. 🤷‍♂️

Public exploits are available for two other vulnerabilities:

🔸 EoP - Windows User Profile Service (CVE-2026-62832). This vulnerability allows an authenticated attacker to elevate privileges to ADMINISTRATOR level. Rapid7 believes this vulnerability is related to the LegacyHive exploit, which was published on July 14.

🔸 EoP - Windows Kernel (CVE-2026-62737). This vulnerability allows an authenticated attacker to elevate privileges to SYSTEM level. An exploit has been publicly available since August 11.

Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Windows DNS Server (CVE-2026-62878). This wormable vulnerability allows a remote unauthenticated attacker to execute code on a vulnerable server with elevated privileges. It is recommended to test and install the update as soon as possible, especially on Internet-facing DNS servers.

🔹 RCE - Windows Deployment Services TFTP Server (CVE-2026-62893). This vulnerability, discovered as part of the ZDI (Zero Day Initiative) program, allows an attacker to execute code without authentication or user interaction. TFTP has no authentication mechanism and is available remotely via UDP port 69. Any WDS server serving Windows Imaging Format (WIM) files via TFTP, which is the standard PXE boot scenario, is vulnerable. The issue results from the lack of validation of the existence of an object before performing operations on it. UDP port 69 should be blocked at the perimeter, but attackers could easily use this vulnerability for lateral movement within an organization. If you're using WDS for deployments, test and install this update quickly.

🔹 RCE - Windows DHCP Server (CVE-2026-62823). Successful exploitation of this vulnerability allows a remote unauthenticated attacker to execute arbitrary code from an adjacent network by sending a specially crafted packet that triggers a heap-based buffer overflow.

🔹 EoP - Microsoft Exchange (CVE-2026-62911). This vulnerability allows a remote authenticated attacker (with Privileges Required: Low according to CVSS) to gain control over the mailboxes of all Exchange users, send and read emails, and download attachments. This vulnerability was demonstrated at Pwn2Own Berlin. ZDI researchers provided Microsoft with working exploits.

🔹 RCE - Microsoft QUIC (CVE-2026-62815). This use-after-free vulnerability allows an unauthenticated attacker to execute arbitrary code on a target system by sending a specially crafted network packet. QUIC is an IETF-standardized transport protocol that runs over UDP instead of TCP and serves as the foundation for HTTP/3. The protocol is used by approximately 13.5 million websites.

🔹 Tampering - Windows Container Isolation FS Filter Driver (unionfs.sys) (CVE-2026-72971). This vulnerability reportedly allows an attacker to overwrite certain files. As a result, an attacker could perform an action within a container that could impact the host system.

🗒 Full Vulristics report
About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability

About Elevation of Privilege - NT OS Kernel (CVE-2026-42980) vulnerability. Information about this vulnerability was disclosed as part of the June Microsoft Patch Tuesday on June 9. The vulnerability was not specifically highlighted in Microsoft Patch Tuesday reviews published by VM vendors. This Microsoft Windows NT OS Kernel elevation of privilege vulnerability is caused by improper handling of integer values during data construction in the Windows Management Instrumentation (WMI) subsystem, resulting in an out-of-bounds write. Successful exploitation allows a local attacker with low privileges (a standard user account) to escalate privileges to NT AUTHORITY\SYSTEM. Obtaining NT AUTHORITY\SYSTEM privileges grants full control over the affected host, enabling an attacker to execute arbitrary commands, modify security settings, access protected data, and use the compromised host as a foothold for further lateral movement within the target environment.

🛠 On July 7, a detailed write-up describing the exploitation of this vulnerability was published. A public proof-of-concept (PoC) exploit is also available on GitHub.

👾 There is currently no evidence of in-the-wild exploitation of this vulnerability.