
Tag Archives: MicrosoftWord

September Microsoft Patch Tuesday

September Microsoft Patch Tuesday

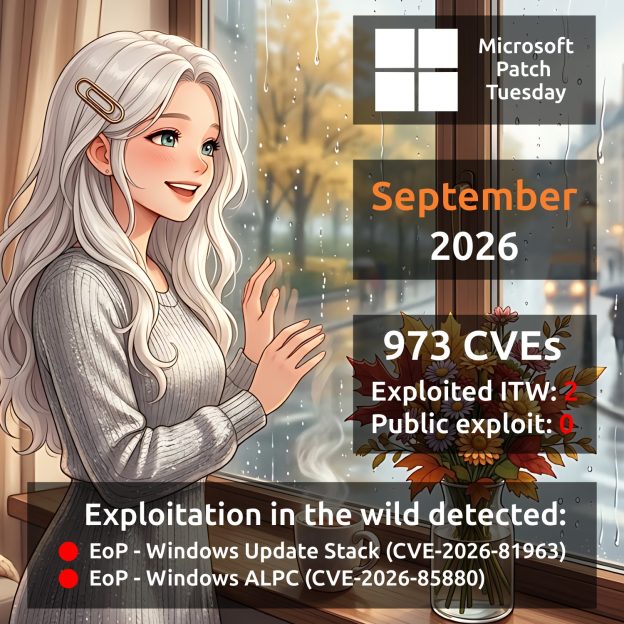
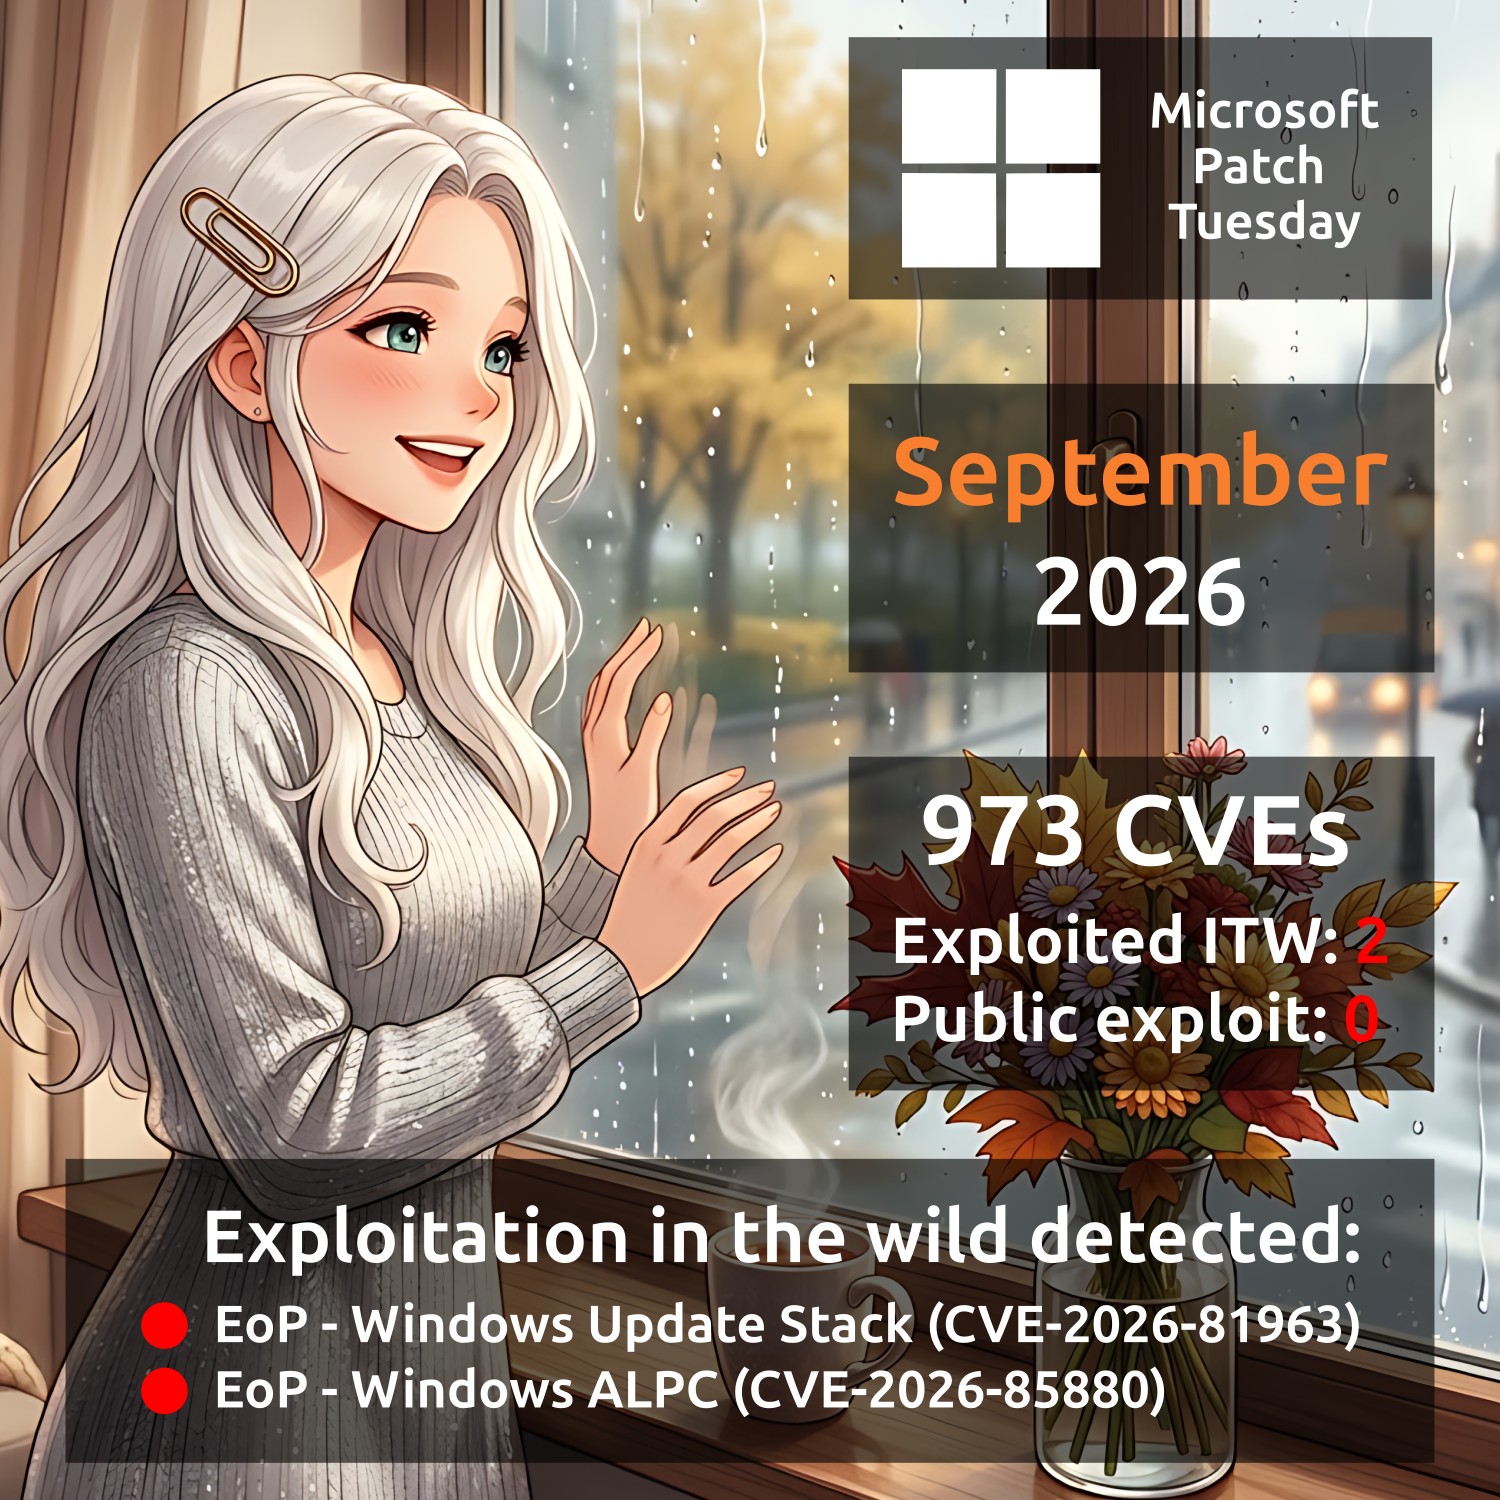
September Microsoft Patch Tuesday. A total of 973 vulnerabilities were addressed - more than twice as many as in August. Seven products had 20 or more vulnerabilities fixed: Windows Biometric Service (64), Microsoft SQL Server (54), Windows DHCP Server (36), Microsoft Office Word (35), Windows NTFS (29), Microsoft Excel (28), and Windows Win32k (24). Vulnerabilities affecting these products account for just under one-third of the total. Two vulnerabilities are known to have been exploited in the wild:

🔻 EoP - Windows Update Stack (CVE-2026-81963). A link following flaw in the Windows Update Stack (CWE-59) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

🔻 EoP - Windows Advanced Local Procedure Call (ALPC) (CVE-2026-85880). A heap-based buffer overflow flaw in Windows ALPC (CWE-122) may allow an authenticated attacker to elevate privileges locally. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.

There are no vulnerabilities with public exploits yet. Of the remaining vulnerabilities, the following can be highlighted:

🔹 RCE - Microsoft Exchange (CVE-2026-55007). A remote, unauthenticated attacker could achieve code execution on a vulnerable Exchange server by sending an email containing a malicious Visio attachment. The code is executed when the server processes the message, without requiring the victim to open it or use the Preview Pane.

🔹 RCE - Remote Desktop Services (CVE-2026-69525). Successful exploitation of this flaw would allow an unauthenticated attacker to execute arbitrary code by exploiting a use-after-free flaw.

🔹 RCE - Windows DNS Server (CVE-2026-69730). According to the advisory, an unauthenticated, remote attacker could send a crafted packet to exploit a use-after-free flaw in Windows DNS in order to achieve remote code execution.

🔹 RCE - Windows USB Mass Storage Class Driver (CVE-2026-68839). Successful exploitation of this vulnerability could allow an attacker the ability to gain remote code execution via an in-network attacker calling arbitrary endpoints.

🔹 RCE - Windows Kerberos (CVE-2026-69676). An authentication-bypass flaw via capture-replay in Windows Kerberos may allow an authenticated attacker to execute code over a network.

🔹 RCE - Windows Key Distribution Center (CVE-2026-69712). A use-after-free flaw in the Windows Key Distribution Center may allow an authenticated attacker to execute code over a network.

🔹 EoP - Microsoft Exchange (CVE-2026-69380). An authenticated attacker with access to a mailbox through a low-privileged user account could exploit this vulnerability to gain access to other mailboxes. Successful exploitation would allow the attacker to send and receive emails on behalf of other Exchange users as well as access attachments.

🗒 Full Vulristics report

May Microsoft Patch Tuesday

May Microsoft Patch Tuesday

May Microsoft Patch Tuesday. A total of 119 vulnerabilities, approximately 1.5 times fewer than in April. There are currently no vulnerabilities marked as actively exploited in the wild. However, there is one vulnerability with a public exploit:

🔸 EoP - Windows Kernel (CVE-2026-40369). A detailed write-up and exploit for this vulnerability were published on May 14, two days after the May MSPT. The researcher describes exploitation of the vulnerability as follows: "A single syscall from any unprivileged process — including inside Chrome's renderer sandbox — can increment arbitrary kernel memory addresses. No race conditions. No heap spray. No special tokens. 100% deterministic privilege escalation to SYSTEM."

Among the remaining ones, the following stand out:

🔹 RCE - Windows DNS Client (CVE-2026-41096). A ZDI analyst commented on this vulnerability as follows: "This patch fixes a heap-based buffer overflow in the DNS Client triggered by a malicious DNS response. No authentication or user interaction needed, and since the DNS Client runs on virtually every Windows machine, the attack surface is enormous. An attacker with a position to influence DNS responses (MitM, rogue server) could achieve unauthenticated RCE across your enterprise."

🔹 RCE - Windows Netlogon (CVE-2026-41089). The vulnerability allows an unauthenticated remote attacker to execute arbitrary code on a domain controller by sending a specially crafted network request. Exploitation does not require credentials or user interaction, which classifies this vulnerability as wormable. Compromise of a domain controller means full compromise of the organization's entire domain. A Rapid7 analyst added in their commentary: "No privileges or user interaction are required, and attack complexity is low, which suggests that creation of a reliable exploit might not be especially difficult for anyone with knowledge of the specific mechanism. Microsoft assesses exploitation as less likely, but since those exploitability assessments are provided without an accompanying explanation, it's not clear how much reassurance defenders should take. Anyone who remembers the much-discussed CVE-2020-1472 (aka ZeroLogon) back in 2020 will note that CVE-2026-41089 offers an attacker more immediate control of a domain controller. Patches are available for all versions of Windows Server from 2012 onwards."

🔹 RCE - Windows TCP/IP (CVE-2026-40415). Commentary from a ZDI analyst: "This bug in the TCP/IP stack results from a use-after-free (UAF) and could allow a remote, unauthenticated threat actor to execute code without user interaction. That makes this another wormable bug. However, this one is much less likely to be exploited. The target needs to be under sustained low-memory (memory pressure) conditions, which is pretty rare."

🔹 RCE - Microsoft Word (CVE-2026-40361, CVE-2026-40364, CVE-2026-40366, CVE-2026-40367). An attacker can exploit these vulnerabilities through social engineering by sending a malicious file to a targeted victim. Successful exploitation would grant the attacker arbitrary code execution. Microsoft researchers note that the Preview Pane is an attack vector for each of these vulnerabilities.

🔹 RCE - Microsoft Office (CVE-2026-40363, CVE-2026-42831). A heap-based buffer overflow vulnerability in Microsoft Office may allow an unauthorized attacker to remotely execute arbitrary code.

🔹 RCE - Windows GDI (CVE-2026-35421). A heap-based buffer overflow vulnerability in the Windows GDI component may allow an unauthorized attacker to remotely execute arbitrary code.

🔹 RCE - Microsoft Dynamics 365 On-Premises (CVE-2026-42898). Commentary from a ZDI analyst: "It allows any authenticated user to execute code with a scope change, meaning exploitation can break out and affect resources beyond the vulnerable component itself. Scope changes are pretty rare, so if you're running Dynamics 365 On-Prem, definitely test and deploy this patch quickly."

🔹 EoP - Windows Kernel (CVE-2026-33841, CVE-2026-35420, CVE-2026-40369). CVE-2026-33841 and CVE-2026-40369 are rated "Exploitation More Likely". A local attacker can use these vulnerabilities to elevate privileges to SYSTEM level. In the case of CVE-2026-33841, the attacker can elevate privileges to Medium/High integrity level.

🗒 Full Vulristics report