Tag Archives: ContainerEscape

October Linux Patch Wednesday

October Linux Patch Wednesday

October Linux Patch Wednesday. There are 4,946 vulnerabilities in total. By comparison, there were 2,653 in September. That's an 86% increase! This time, there are 1,954 vulnerabilities in the Linux Kernel and 814 in Chromium. Together, they make up 56% of all vulnerabilities.

Six vulnerabilities show signs of being exploited in the wild:

🔻 RCE - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619). PHP is a popular programming language widely used for web application development. CVE-2026-109618 is an out-of-memory (OOM) handling vulnerability that allows remote code execution when an application receives a specially crafted request. CVE-2026-109619 is a use-after-free vulnerability that allows PHP to access stale references to freed memory, potentially leading to remote code execution. Linux distributions began releasing patches on the day the vulnerabilities were disclosed, October 21. More than 470 links to public exploits are available on GitHub. Both vulnerabilities were added to the CISA KEV on October 26.

🔻 SFB - Linux Kernel "PwnEscape" (CVE-2026-99999). The vulnerability affects the Linux kernel's networking stack and allows an attacker inside a KVM guest virtual machine to corrupt the host kernel's memory. This could expose sensitive host memory contents or cause the host system to crash. Researchers demonstrated a complete escape from a guest VM to the host. Linux distributions began releasing patched packages on October 16, and public exploits appeared on GitHub the same day. The vulnerability was added to the VulnCheck KEV on October 19.

🔻 RCE - WordPress (CVE-2026-87902). WordPress is a popular content management system (CMS) for building websites and blogs. Under certain conditions, this vulnerability allows an unauthenticated attacker to execute arbitrary code remotely on the server. Public exploits have been available on GitHub since September 22. The vulnerability was added to the CISA KEV on September 25. Debian released patched packages on September 28.

🔻 XSS - WordPress "Comment2Shell" (CVE-2026-93485). The vulnerability allows an unauthenticated attacker to inject JavaScript code through a specially crafted comment. The code is executed in the browser when an administrator views the comment, allowing the attacker to hijack his session and potentially execute arbitrary code on the server. The vulnerability was added to the VulnCheck KEV on September 18. Public exploits have been available on GitHub since September 22. Patched packages have been available in Debian since September 28.

🔻 AFR - Gradio (CVE-2026-28414). Gradio is a Python library for quickly building machine learning interfaces. The vulnerability allows unauthenticated attackers to read arbitrary files from a Windows server running Python 3.13 or later, even when Gradio authentication is enabled. A public exploit appeared on February 27. The vulnerability was added to the VulnCheck KEV on May 31. ALT Linux has been providing patched packages since October 1.

Another 335 vulnerabilities have no known signs of exploitation in the wild, but public exploits are available for them. Notable examples include:

🔸 EoP - Linux Kernel (CVE-2026-98260). This use-after-free vulnerability in the POSIX CPU timers mechanism allows a local unprivileged user to escalate privileges to root. Researcher v4bel demonstrated a root shell on Ubuntu 26.04 running kernel 7.0.0-30-generic as part of the Infinity Core project. The exploit is also reported to enable container escapes and privilege escalation on Android. Patched packages have been available since October 15. A public exploit was published on GitHub on October 17.

🔸 RCE - Pillow (CVE-2026-112900). Pillow is a Python library for image processing. An attacker can upload an EPS file to execute arbitrary code on the server. Patched packages have been available in Debian since October 21. Public exploits have been available on GitHub since October 23.

🗒 Full Vulristics report (ZIP; 1.7 MB)
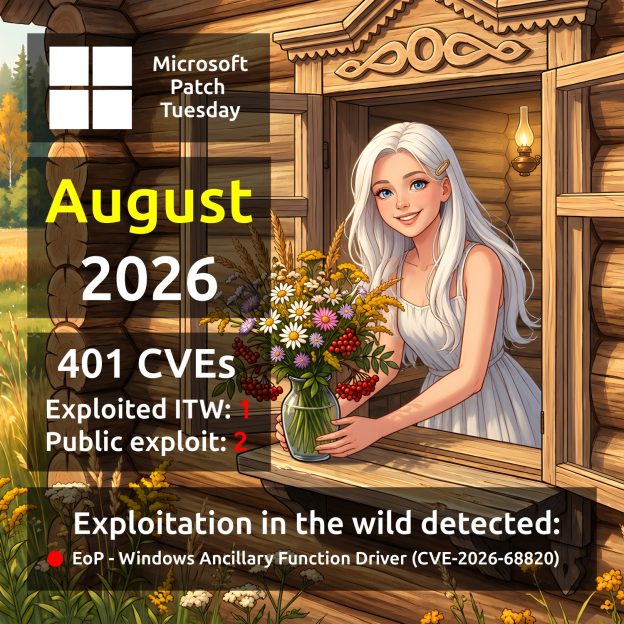
August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday. A total of 401 vulnerabilities were addressed - 170 fewer than in July. One of the vulnerabilities is known to be actively exploited in the wild:

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). A local attacker can exploit this vulnerability to gain SYSTEM-level privileges. There is a contradiction in Microsoft's description: the Exploit Code Maturity in CVSS is marked as "Unproven", while at the same time Microsoft states that the vulnerability is being exploited in the wild. 🤷‍♂️

Public exploits are available for two other vulnerabilities:

🔸 EoP - Windows User Profile Service (CVE-2026-62832). This vulnerability allows an authenticated attacker to elevate privileges to ADMINISTRATOR level. Rapid7 believes this vulnerability is related to the LegacyHive exploit, which was published on July 14.

🔸 EoP - Windows Kernel (CVE-2026-62737). This vulnerability allows an authenticated attacker to elevate privileges to SYSTEM level. An exploit has been publicly available since August 11.

Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Windows DNS Server (CVE-2026-62878). This wormable vulnerability allows a remote unauthenticated attacker to execute code on a vulnerable server with elevated privileges. It is recommended to test and install the update as soon as possible, especially on Internet-facing DNS servers.

🔹 RCE - Windows Deployment Services TFTP Server (CVE-2026-62893). This vulnerability, discovered as part of the ZDI (Zero Day Initiative) program, allows an attacker to execute code without authentication or user interaction. TFTP has no authentication mechanism and is available remotely via UDP port 69. Any WDS server serving Windows Imaging Format (WIM) files via TFTP, which is the standard PXE boot scenario, is vulnerable. The issue results from the lack of validation of the existence of an object before performing operations on it. UDP port 69 should be blocked at the perimeter, but attackers could easily use this vulnerability for lateral movement within an organization. If you're using WDS for deployments, test and install this update quickly.

🔹 RCE - Windows DHCP Server (CVE-2026-62823). Successful exploitation of this vulnerability allows a remote unauthenticated attacker to execute arbitrary code from an adjacent network by sending a specially crafted packet that triggers a heap-based buffer overflow.

🔹 EoP - Microsoft Exchange (CVE-2026-62911). This vulnerability allows a remote authenticated attacker (with Privileges Required: Low according to CVSS) to gain control over the mailboxes of all Exchange users, send and read emails, and download attachments. This vulnerability was demonstrated at Pwn2Own Berlin. ZDI researchers provided Microsoft with working exploits.

🔹 RCE - Microsoft QUIC (CVE-2026-62815). This use-after-free vulnerability allows an unauthenticated attacker to execute arbitrary code on a target system by sending a specially crafted network packet. QUIC is an IETF-standardized transport protocol that runs over UDP instead of TCP and serves as the foundation for HTTP/3. The protocol is used by approximately 13.5 million websites.

🔹 Tampering - Windows Container Isolation FS Filter Driver (unionfs.sys) (CVE-2026-72971). This vulnerability reportedly allows an attacker to overwrite certain files. As a result, an attacker could perform an action within a container that could impact the host system.

🗒 Full Vulristics report

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May In the Trend of VM (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. While the previous April edition featured only one vulnerability, this one includes four, covering different technologies and attack scenarios.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Copy Fail" (CVE-2026-31431). The vulnerability allows an attacker to gain root privileges.

🔻 RCE - Apache ActiveMQ (CVE-2026-34197). A vulnerability in a solution widely used in enterprise systems and integration platforms.

🔻 Spoofing - Microsoft SharePoint Server (CVE-2026-32201). A vulnerability in a Microsoft solution widely used in enterprise systems for collaboration, document management, and internal portal development.

🔻 RCE - Adobe Reader (CVE-2026-34621). A vulnerability in a widely used PDF document viewer; actively exploited in phishing attacks.

🟥 The full list of trending vulnerabilities is available on the portal

About Elevation of Privilege - Linux Kernel "Copy Fail" (CVE-2026-31431) vulnerability

About Elevation of Privilege - Linux Kernel Copy Fail (CVE-2026-31431) vulnerability

About Elevation of Privilege - Linux Kernel "Copy Fail" (CVE-2026-31431) vulnerability. A local privilege escalation vulnerability in the Linux kernel AF_ALG component, which is caused by a memory handling flaw, allows an unprivileged user to escalate privileges to root. By exploiting this vulnerability, an attacker can fully compromise the system: read and modify any files, including passwords and keys, replace system binaries, disable security controls and monitoring tools, stealthily install backdoors and maintain persistence, hide traces of their activity, and use the host as a foothold for attacks on other network assets.

⚙️🛠 On April 1, patches addressing the vulnerability were merged into the main branch of the Linux kernel. On April 22, a CVE identifier was assigned to the vulnerability. On April 29, experts from Theori published an analysis of the vulnerability and a public exploit. The vulnerability's exploitability has been confirmed on up-to-date versions of widely used Linux distributions, including Ubuntu, Amazon Linux, RHEL, and SUSE.

👾 On May 1, the vulnerability was added to the CISA KEV catalog, indicating it is being exploited in the wild.

What distinguishes this vulnerability from similar EOP/LPE issues in Linux?

There have been high-profile privilege escalation vulnerabilities in the Linux kernel. Dirty COW required winning a race condition. Multiple attempts were often needed, and this sometimes led to system crashes. Dirty Pipe was tied to specific versions and required precise pipe buffer manipulation.

But unlike Dirty COW and Dirty Pipe, researchers report that Copy Fail is a straight-line logic flaw. It triggers without races, retries, or crash-prone timing windows.

🧬 Portability. The same exploit script works across all tested distributions and architectures, including Ubuntu, Amazon Linux, Red Hat Enterprise Linux (RHEL), and SUSE Linux Enterprise. No per-distribution offsets. No recompilation. No version checks in the exploit.

✧ Minimalism. The entire exploit is a short Python script using only standard library modules (os, socket, zlib). It requires Python 3.10+ for os.splice. No compiled payloads, no dependency installation.

🥷 Stealth. The write bypasses the ordinary VFS write path. The corrupted page is never marked dirty by the kernel's writeback machinery. Standard file integrity tools that compare on-disk checksums will not detect it, because the on-disk file remains unchanged. Only the in-memory page cache is corrupted.

📦 Cross-container impact. The page cache is shared across all processes on the system, including across container boundaries. Copy Fail is not just a local privilege escalation. It is a container escape primitive and a vector for Kubernetes node compromise.

How to fix the vulnerability?

To remediate the vulnerability, users need to update to Linux kernel versions 6.18.22, 6.19.12, and 7.0. The kernel can be built manually, or users can wait for their Linux distribution vendor to release updated kernel packages. As of May 4, updates have been released for Ubuntu, Debian, RHEL, Fedora, SUSE, CloudLinux, Arch Linux, and ROSA Linux.

As a workaround, researchers suggest blocking the creation of AF_ALG sockets:

echo "install algif_aead /bin/false" > /etc/modprobe.d/disable-algif-aead.conf
rmmod algif_aead 2>/dev/null