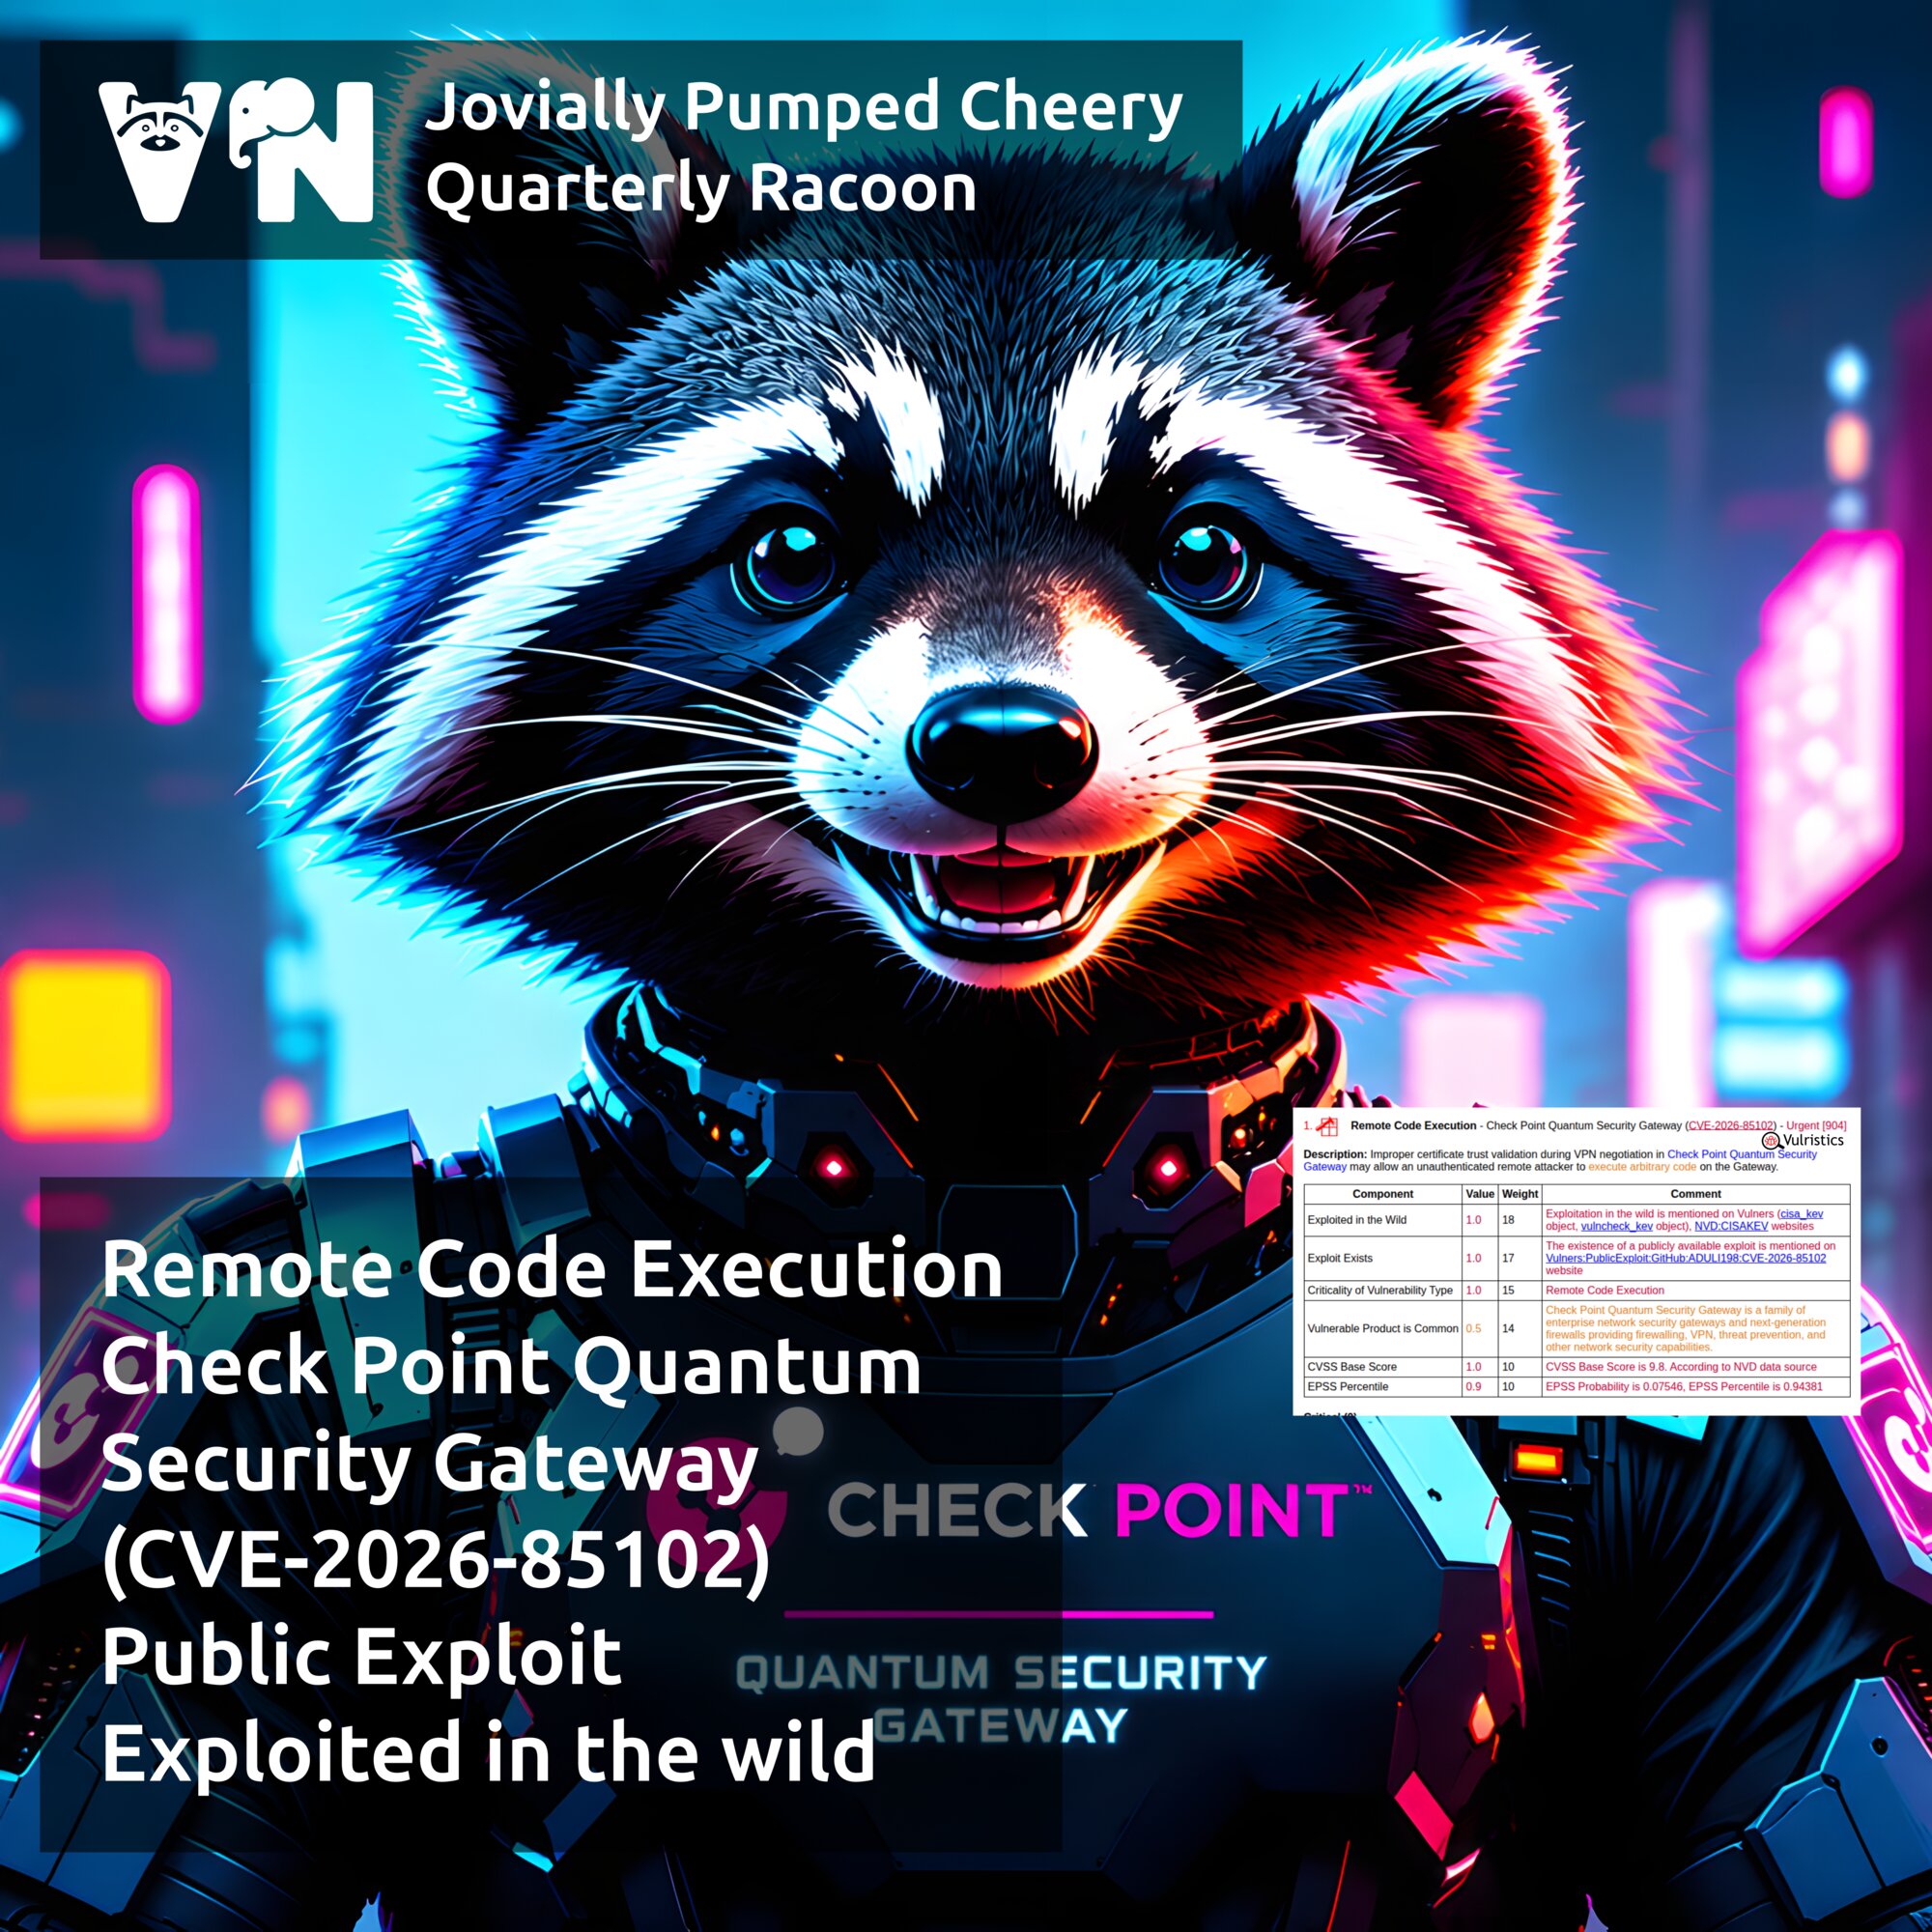
About Remote Code Execution - Check Point Quantum Security Gateway (CVE-2026-85102) vulnerability. Check Point Quantum Security Gateway is an enterprise security gateway and next-generation firewall (NGFW) designed to protect network infrastructure from cyberattacks and unauthorized access. It provides network traffic filtering, intrusion prevention (IPS), application control, and secure VPN connectivity. Improper validation of trust in an X.509 certificate during VPN negotiation on Check Point Quantum Security Gateway may allow an unauthenticated remote attacker to execute arbitrary code on the gateway with the privileges of a system process.
An attacker may use the compromised gateway to perform internal network reconnaissance (including port and service scanning), intercept VPN traffic, steal credentials and configuration files, including certificates, IPsec/VPN keys, and administrator credentials, and compromise VPN tunnels connecting the organization's network to branch offices and partner networks.
The vulnerability also affects Spark Firewall devices, a family of firewalls developed by Check Point primarily to protect the networks of small and medium-sized businesses, branch offices, and remote locations.
⚙️ Security updates and mitigation measures have been available on the vendor's website since September 9.
👾 Check Point experts began observing exploitation attempts on September 12. On September 22, the vulnerability was added to the CISA KEV catalog.
🛠 A public exploit has been available on GitHub since October 7.
🌐 As of October 12, Shodan had identified 11,849 potentially vulnerable Check Point gateways exposed to the Internet, 143 of them in Russia.