Tag Archives: SPIP

September Linux Patch Wednesday

September Linux Patch Wednesday

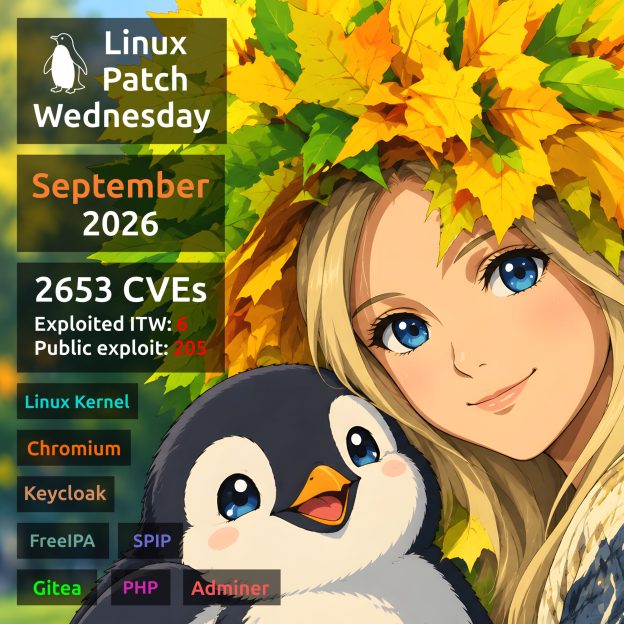
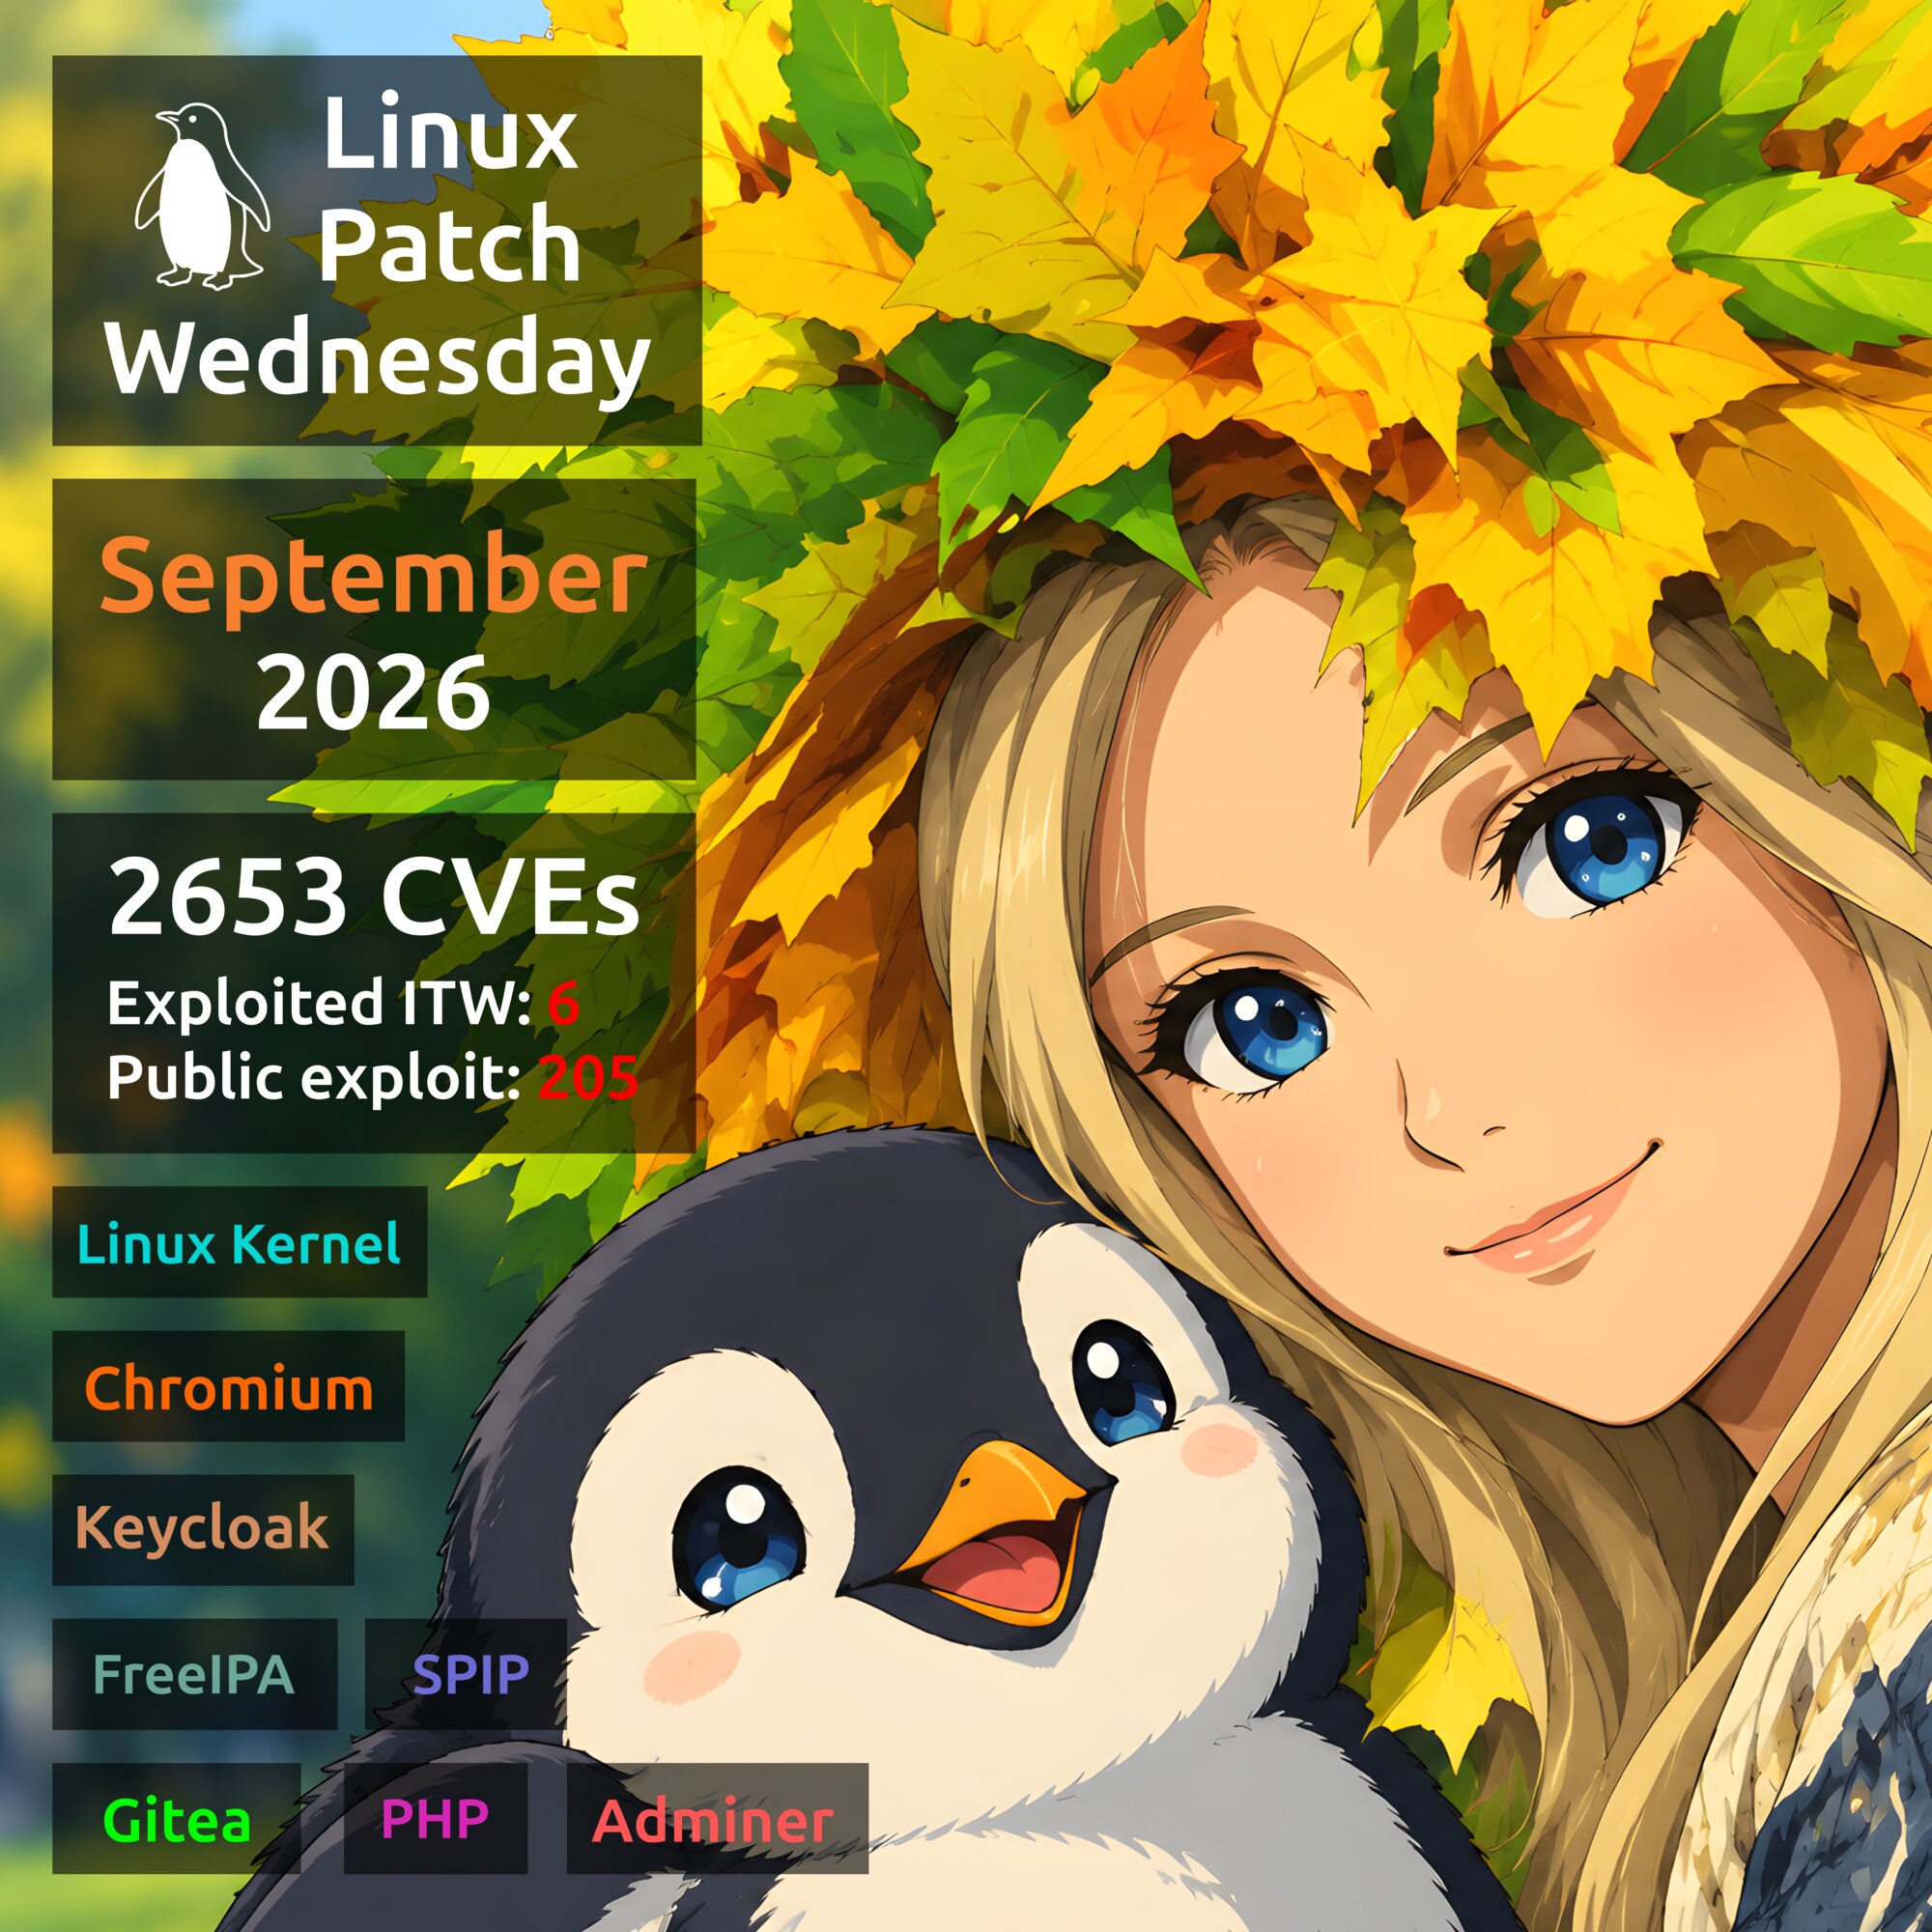
September Linux Patch Wednesday. There are 2,653 vulnerabilities in total. For comparison, in August, there were 3,060 - 13% more. This time, the Linux Kernel has 812 vulnerabilities, and Chromium has 644. There are signs of exploitation in the wild for 6 vulnerabilities:

🔻 RCE - Gitea (CVE-2026-60004). Gitea is a popular platform for hosting Git repositories on your own servers. An attacker with basic write access to a repository can run arbitrary shell commands as the Gitea OS user. With open registration enabled by default, even an unauthenticated attacker can get the required access by creating an account and a repository. The vulnerability was added to CISA KEV on August 25. A campaign exploiting the vulnerability to install the XMRig cryptominer has been observed. Public exploits have been available on GitHub since July 29. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Gitea (CVE-2026-20896). The vulnerability allows a remote attacker to bypass authentication and log in to Gitea as another user, including an administrator. The vulnerability was added to VulnCheck KEV on July 6. Public exploits have been available on GitHub since July 2. The vulnerability was fixed in ALT Linux packages on August 27.

🔻 AuthBypass - Keycloak (CVE-2026-18963). Keycloak is a popular platform for identity and access management (IAM/SSO). A vulnerability in the password reset mechanism allows an unauthenticated remote attacker to reset any user's password and take over their account without email confirmation. The vulnerability was added to VulnCheck KEV on August 25. Public exploits have been available on GitHub since August 20. The vulnerability was fixed in ALT Linux packages on August 20.

🔻 RCE - Chromium (CVE-2026-85046, CVE-2026-87491). Chromium is a web browser project that forms the basis of Google Chrome and other browsers. Vulnerabilities in the V8 JavaScript engine allow a remote attacker to execute arbitrary code within the browser sandbox if a user opens a malicious HTML page. Both vulnerabilities are exploited in the wild and were added to the CISA KEV on September 4 and September 9. Public exploits have been available on GitHub since September 4. The vulnerabilities have been fixed in ALT Linux and Debian packages since September 5.

🔻 RCE - SPIP (CVE-2026-77806). SPIP is an open-source CMS for creating and collaboratively editing websites. The critical vulnerability allows an unauthenticated remote attacker to execute arbitrary code on the server. The vulnerability was added to VulnCheck KEV on August 21. A Metasploit module is available. The vulnerability has been fixed in Debian packages since August 21.

For another 205 vulnerabilities, there are currently no signs of exploitation in the wild, but public exploits are available. Among them, the following stand out:

🔸 AuthBypass - FreeIPA (CVE-2026-76578). FreeIPA is a solution for centralized identity and access management in Linux infrastructures (LDAP/Kerberos). A remote, unauthenticated attacker can obtain membership in the FreeIPA administrator group and perform administrative operations against the directory and, on SID-enabled deployments, other IdM services. A public exploit has been available on GitHub since September 9. The vulnerability was fixed in ALT Linux packages on September 7.

🔸 RCE - PHP/Adminer (CVE-2026-56705). Adminer is a popular web-based tool for database administration, often deployed alongside PHP applications. The vulnerability allows an unauthenticated remote attacker to write PHP code to the web server's document root and execute it, thereby achieving RCE. A public exploit has been available on GitHub since August 25. The vulnerability has been fixed in Debian packages since September 16.
🗒 Full Vulristics report

August Linux Patch Wednesday

August Linux Patch Wednesday

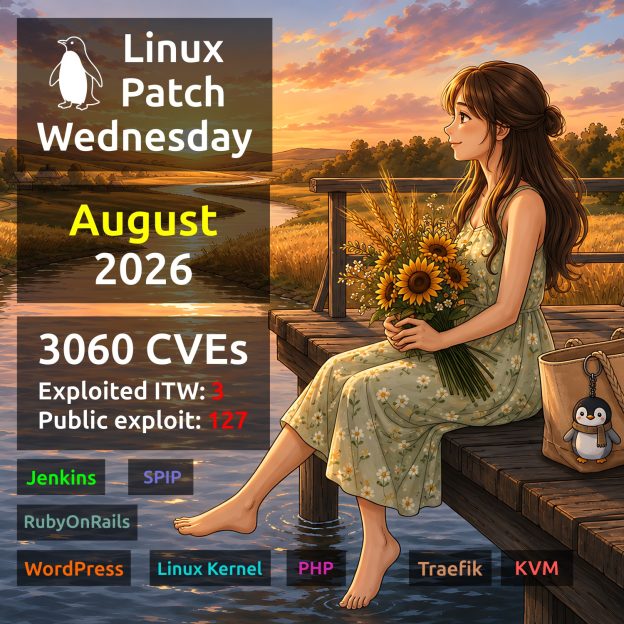
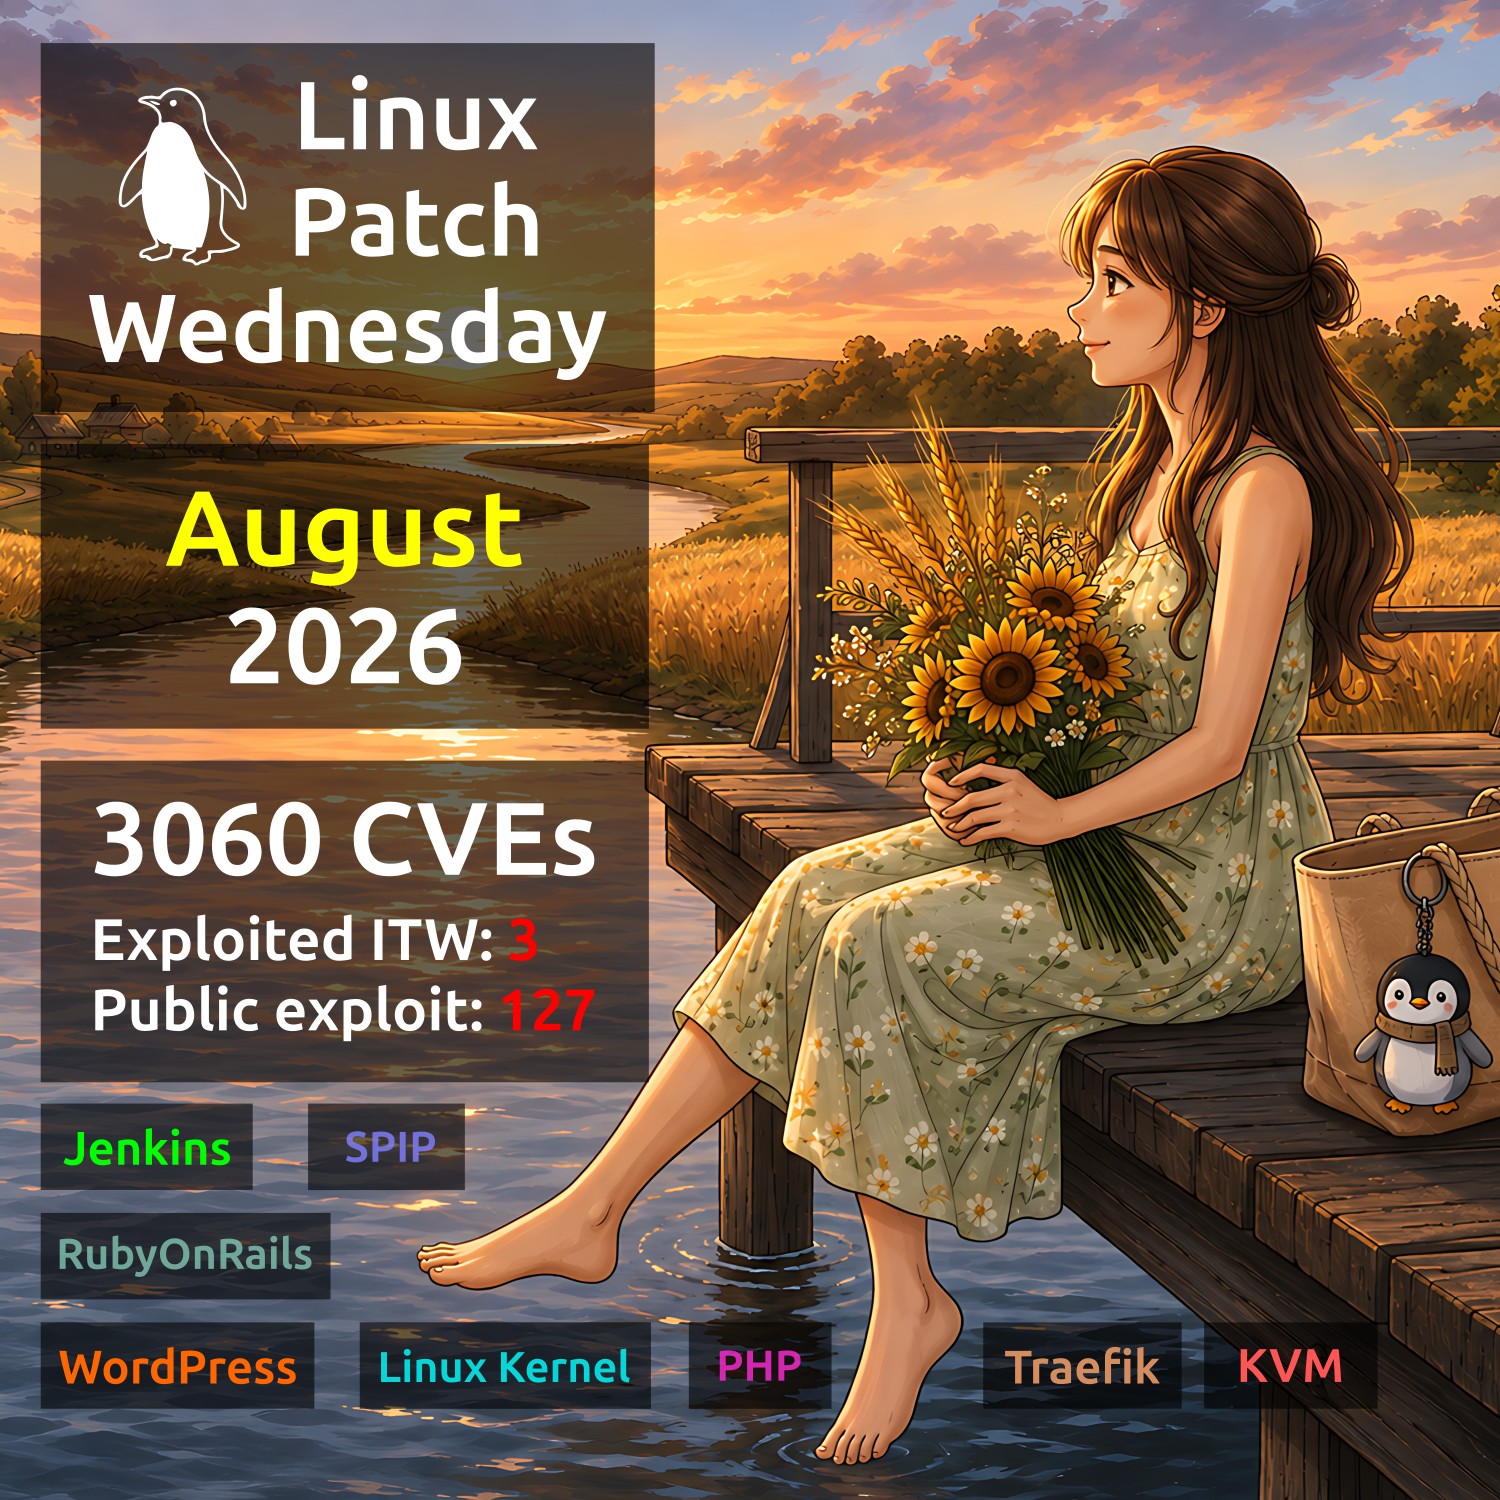
August Linux Patch Wednesday. A total of 3,060 vulnerabilities. For comparison, there were 2,017 in July. That's a 52% increase and another new record. This time, there are 1,354 vulnerabilities in the Linux Kernel and 447 in Chromium. For 3 vulnerabilities, there are signs of exploitation in the wild:

🔻 RCE - Jenkins (CVE-2026-53435). Jenkins is a development automation server used to build, test, and deploy software. The vulnerability allows a remote authenticated attacker to use the Script Console to execute arbitrary code and read files from the Jenkins controller. The vulnerability was added to the VulnCheck KEV on June 15 and fixed in RedOS on August 12.

🔻 CodeInj - WordPress (CVE-2026-60137). WordPress is a popular open-source CMS for creating websites and blogs. The vulnerability leads to a blind SQL injection in the WordPress core, allowing a remote unauthenticated attacker to read user accounts and password hashes from the WordPress database. Code execution is then possible by installing a malicious plugin. Multiple public exploits are available. The vulnerability was added to the CISA KEV catalog on July 21. A fix for the wordpress package in the Debian repository was released on July 23.

🔻 RCE - SPIP (CVE-2026-77647). SPIP is an open-source CMS for creating and collaboratively editing websites. The vulnerability allows an unauthenticated remote attacker to execute arbitrary PHP code. The vulnerability was added to the VulnCheck KEV on August 20. A fix for the spip package in the Debian repository was released on August 18.

Strictly speaking, the report contains one more vulnerability RCE - WinRAR (CVE-2025-8088) that is being exploited in the wild. The vulnerability was fixed in the clamav package in the Alt Linux repository. However, exploitation is only possible on Windows, so it is out of scope.

Another 127 vulnerabilities are not known to be exploited in the wild, but public exploits are available for them, or there are indications that such exploits exist. Notable examples include:

🔸 RCE - Action Pack "KindaRails2Shell" (CVE-2026-66066). Action Pack is a component of Ruby on Rails responsible for handling web requests, routing, and generating responses. An attacker can upload a specially crafted image to a vulnerable application and achieve remote code execution.

🔸 RCE - WordPress "XSS2Shell" (CVE-2026-64638). The attack chain allows an unauthenticated XSS on the login page to be escalated to arbitrary PHP code execution.

🔸 CodeInj - PHP (CVE-2026-17543). Improper escaping of backslashes in attacker-controlled parameters can lead to a trivial SQL injection in PHP.

🔸 EoP - Linux Kernel "Zapscape" (CVE-2026-64561). This KVM escape vulnerability allows an attacker to break out of a virtual machine in KVM/x86 environments and execute commands on the host with root privileges.

🔸 EoP - Linux Kernel "OVSwrap" (CVE-2026-64531), Linux Kernel "SCTPhantom" (CVE-2026-64564), Linux Kernel "Ubuntu PPPoL2TP" (CVE-2026-68398). These vulnerabilities allow a local attacker to escalate privileges to root.

🔸 AuthBypass - Traefik (CVE-2026-48020). Traefik is an HTTP reverse proxy and load balancer. A high-severity vulnerability in the StripPrefix middleware allows an unauthenticated attacker to bypass route-level authentication and authorization.

🗒 Full Vulristics report

March Linux Patch Wednesday

March Linux Patch Wednesday

March Linux Patch Wednesday. In March, Linux vendors began addressing 575 vulnerabilities, which is 57 fewer than in February. Of these, 93 are in the Linux Kernel (⬇️ a significant decrease - there were 305 in February). There are two vulnerabilities with signs of in-the-wild exploitation:

🔻 RCE - Chromium (CVE-2026-3909, CVE-2026-3910)

Additionally, for 130 (❗️) vulnerabilities, public exploits are available or there are indications of their existence. Notable ones include:

🔸 RCE - Caddy (CVE-2026-27590), NLTK (CVE-2025-14009), Rollup (CVE-2026-27606), GVfs (CVE-2026-28296), SPIP (CVE-2026-27475), OpenStack Vitrage (CVE-2026-28370)
🔸 AuthBypass - Curl (CVE-2026-3783), coTURN (CVE-2026-27624), Libsoup (CVE-2026-3099)
🔸 InfDisc - Glances (CVE-2026-30928, CVE-2026-32596)
🔸 PathTrav - gSOAP (CVE-2019-25355), basic-ftp (CVE-2026-27699)
🔸 EoP - Snapd (CVE-2026-3888), GNU Inetutils (CVE-2026-28372)
🔸 SFB - Caddy (CVE-2026-27585, CVE-2026-27587/88/89), Keycloak (CVE-2026-1529), PyJWT (CVE-2026-32597), Authlib (CVE-2026-27962, CVE-2026-28498, CVE-2026-28802)
🔸 CodeInj - lxml_html_clean (CVE-2026-28350), ormar (CVE-2026-26198)
🔸 SSRF - Libsoup (CVE-2026-3632)

🗒 Full Vulristics report

March Linux Patch Wednesday

March Linux Patch Wednesday

March Linux Patch Wednesday. Total vulnerabilities: 1083. 😱 879 in the Linux Kernel. 🤦‍♂️ Two vulnerabilities show signs of exploitation in the wild:

🔻 Code Injection - GLPI (CVE-2022-35914). An old vulnerability from CISA KEV, but first patched on March 3 in RedOS Linux.
🔻 Memory Corruption - Safari (CVE-2025-24201). Fixed in WebKitGTK packages in Linux repositories.

There are 19 vulnerabilities with publicly available exploits. Notable ones:

🔸 Remote Code Execution - Apache Tomcat (CVE-2025-24813)
🔸 Command Injection - SPIP (CVE-2024-8517)
🔸 Memory Corruption - Assimp (CVE-2025-2152)
🔸 Memory Corruption - libxml2 (CVE-2025-27113)

The Elevation of Privilege vulnerability in the Linux Kernel (CVE-2022-49264) has no public exploit yet. However, it resembles well-known PwnKit (CVE-2021-4034).

🗒 Full Vulristics report

На русском