Tag Archives: CERTPolska

September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

September In the Trend of VM (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration

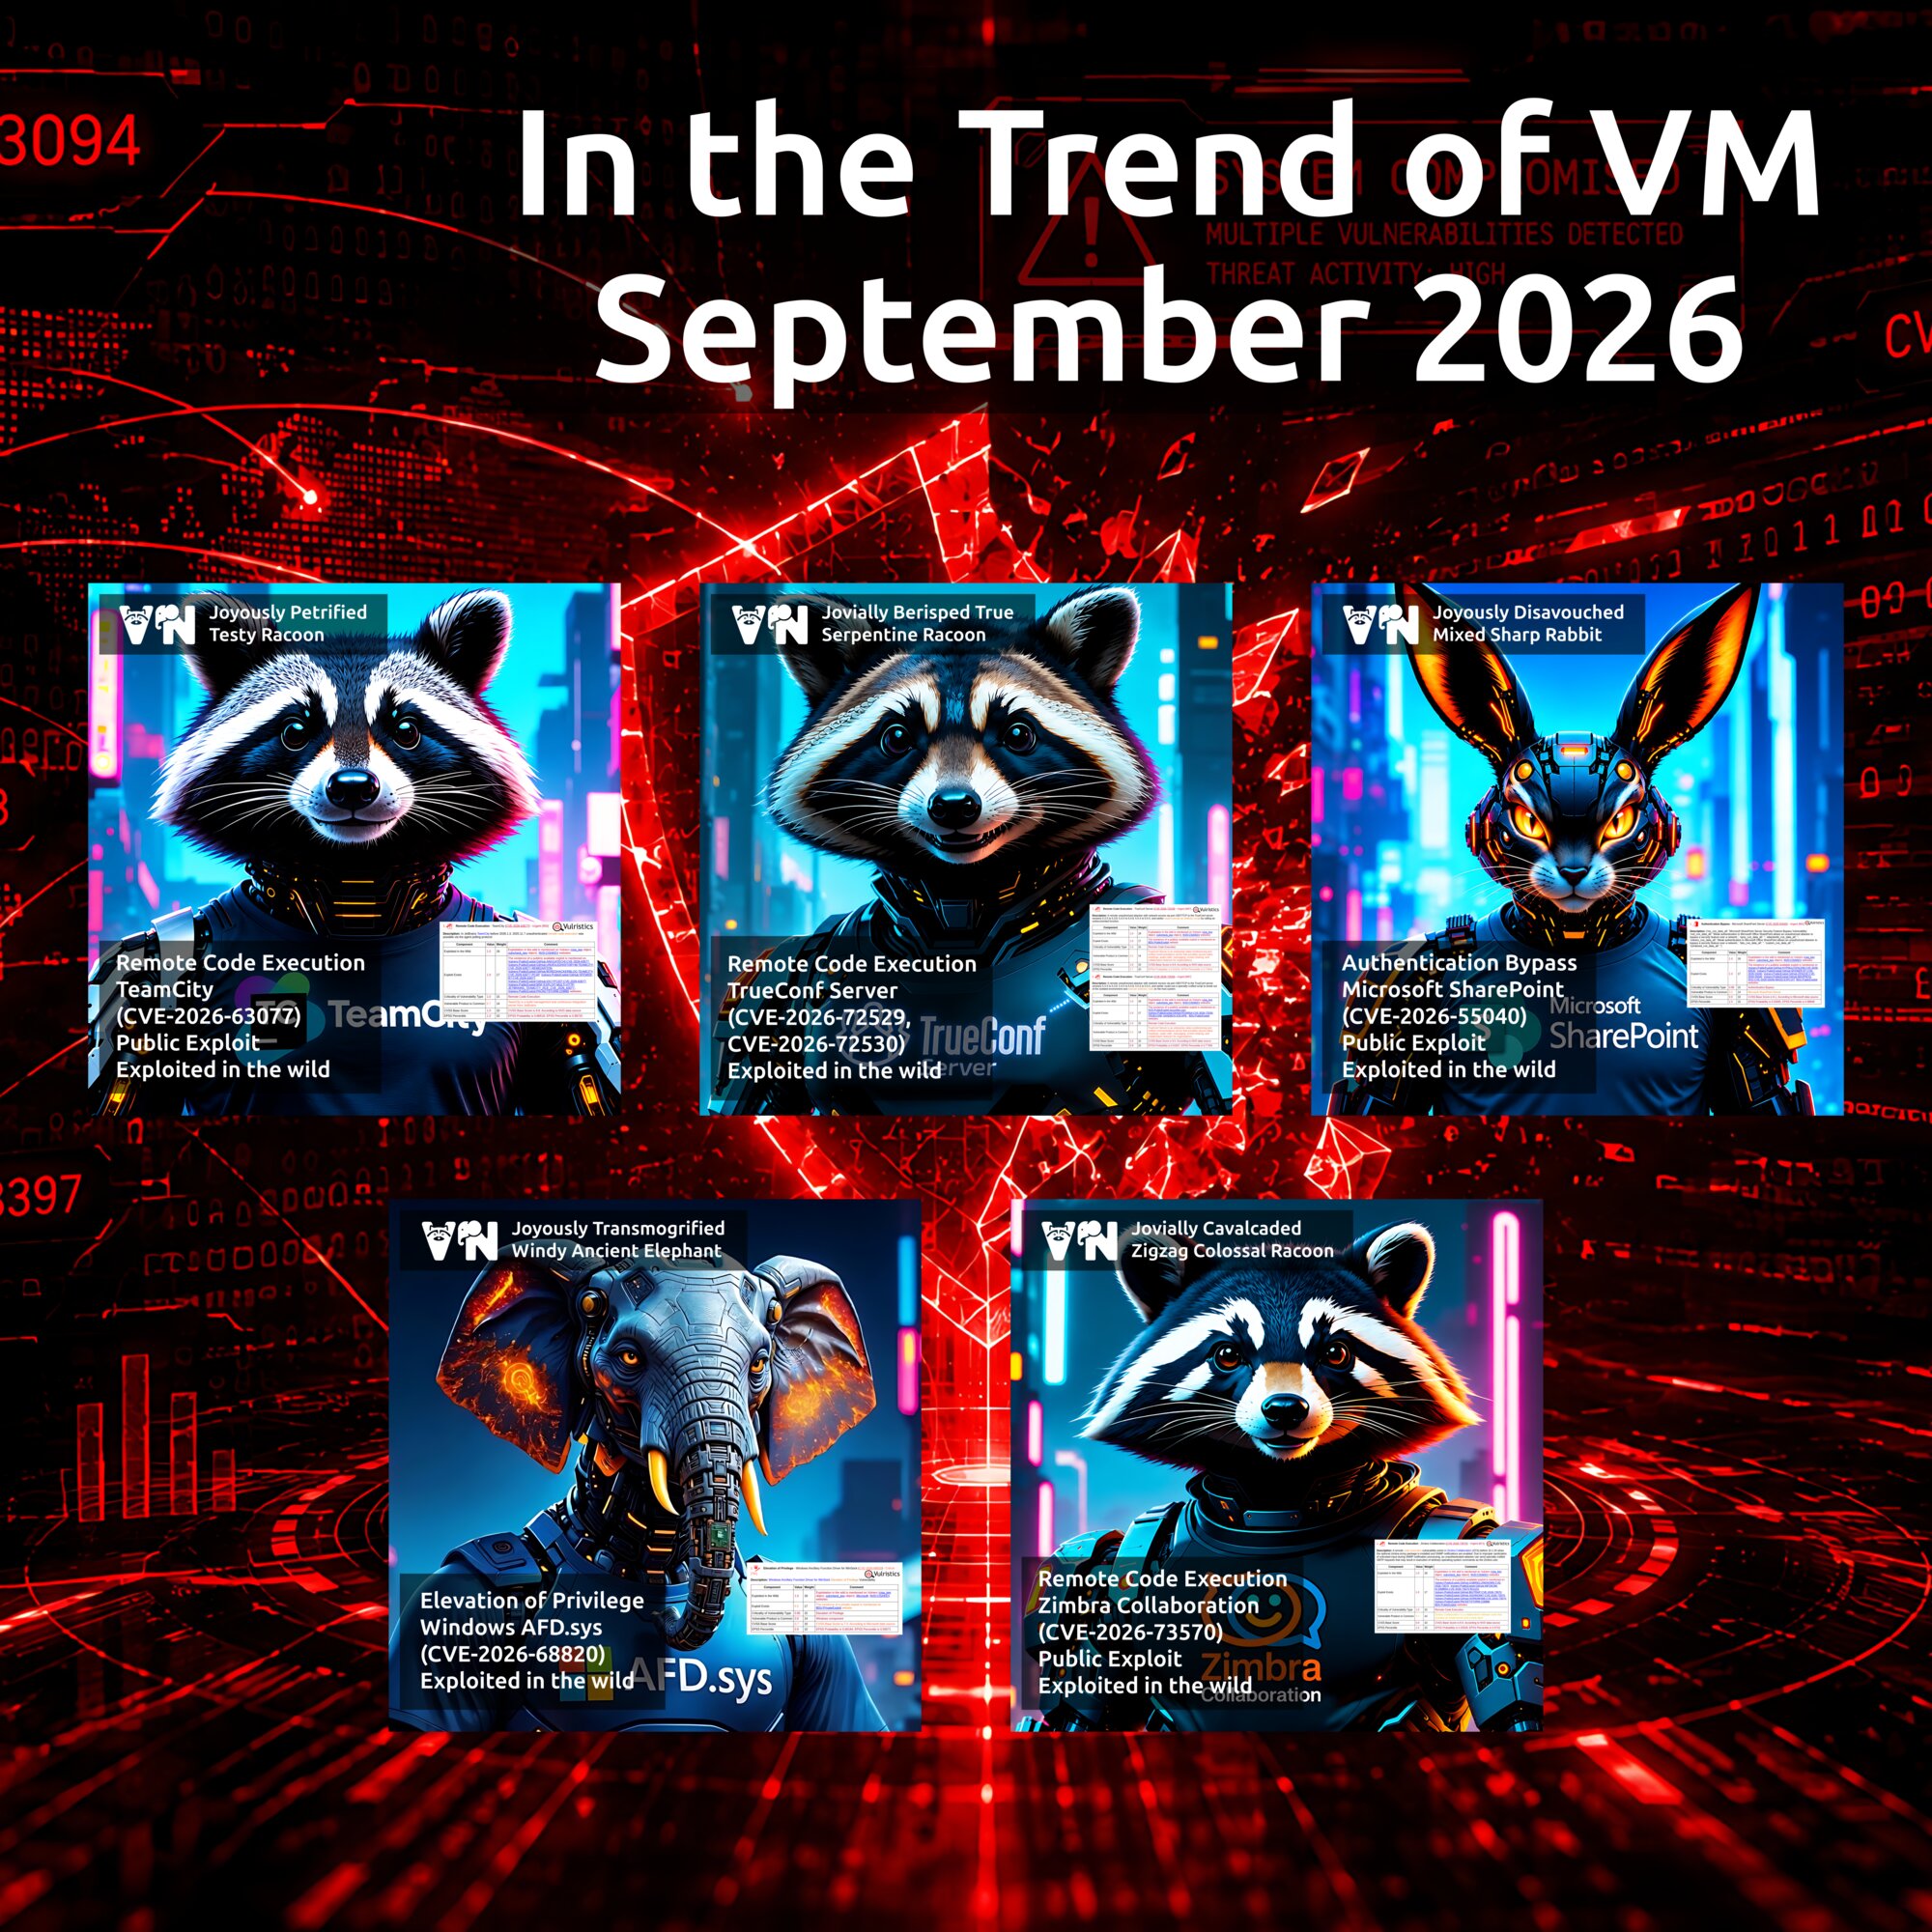
September "In the Trend of VM" (#31): vulnerabilities in TeamCity, TrueConf, SharePoint, Windows, and Zimbra Collaboration. Here is the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. The previous August edition featured four vulnerabilities. This time, there are six.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 RCE - TeamCity (CVE-2026-63077). An actively exploited vulnerability in JetBrains' proprietary solution for automating software build, testing, and deployment. Public exploits are available.

🔻 RCE - TrueConf Server (CVE-2026-72529, CVE-2026-72530). An actively exploited chain of vulnerabilities in a Russian corporate messaging and UltraHD video conferencing platform.

🔻 AuthBypass - Microsoft SharePoint (CVE-2026-55040). An actively exploited vulnerability in Microsoft's web application for deploying corporate intranet portals, managing documents, and collaboration. Public exploits are available.

🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2026-68820). An actively exploited vulnerability in a Windows component that provides support for the Winsock TCP/IP networking protocol.

🔻 RCE - Zimbra Collaboration (CVE-2026-73570). An actively exploited vulnerability in a collaboration software suite that includes a mail server and web client. Public exploits are available.

🟥 The full list of trending vulnerabilities is available on the portal
About Remote Code Execution - Zimbra Collaboration (CVE-2026-73570) vulnerability

About Remote Code Execution - Zimbra Collaboration (CVE-2026-73570) vulnerability

About Remote Code Execution - Zimbra Collaboration (CVE-2026-73570) vulnerability. Zimbra Collaboration is a collaboration software suite that includes a mail server and web client. In terms of functionality, it is comparable to Microsoft Exchange. The vulnerability allows an unauthenticated attacker to send specially crafted SMTP requests that can result in arbitrary operating system command execution with the privileges of the zimbra user. The vulnerability is caused by the lack of proper sanitization of untrusted input when processing data to generate SNMP notifications. Exploitation requires the optional zimbra-snmp package to be installed, SNMP notifications to be enabled, and the swatchdog service to be running.

Successful exploitation allows an attacker to install malware, establish persistence, and use the compromised server as a foothold for further access to the organization's internal infrastructure. An attacker may also gain unauthorized access to corporate emails and other data stored on the system, as well as disrupt Zimbra-related services and business processes.

👾 Experts at CERT Polska reported that the vulnerability was being exploited in the wild on August 17. They recommended checking /var/log/zimbra.log for malicious commands, as well as looking for files created by the zimbra user within the last 30 days in the following directories: /opt/zimbra/jetty/webapps/, /opt/zimbra/jetty_base/webapps/, and /tmp/. The vulnerability was added to the CISA KEV catalog on August 21.

🛠 Public exploits have been available on GitHub since August 24. According to researcher Gabriel P. Lipski's exploit description, an unauthenticated attacker connects to an SMTP port (25, 465, or 587) and sends a standard SMTP session with a command injected into the RCPT TO. Zimbra logs this data in /var/log/zimbra.log regardless of whether the request is accepted or rejected. The swatchdog process then automatically searches the log for lines matching a specific pattern, extracts the attacker-controlled parameter, and passes it to the shell script responsible for sending SNMP notifications without any sanitization. The shell script consequently executes the attacker's command on the host with the privileges of the zimbra operating system user.

⚙️ To remediate the vulnerability, update Zimbra to version 10.1.20 or later. As compensating measures, organizations can disable SNMP notifications, stop the swatchdog service, remove the zimbra-snmp package, and restrict SMTP connections.

🌐 As of August 30, Shadowserver is tracking 5,326 potentially vulnerable hosts, including 172 in Russia. Shadowserver experts also reported the compromise of 274 hosts on August 24.