Tag Archives: Vulristics

July Microsoft Patch Tuesday

July Microsoft Patch Tuesday

July Microsoft Patch Tuesday. A total of 152 vulnerabilities - twice as many as in June. Of these, 15 vulnerabilities were added between the June and July MSPT. One vulnerability is exploited in the wild:

🔻 Memory Corruption - Chromium (CVE-2025-6554)

One vulnerability has an exploit available on GitHub:

🔸 EoP - Windows Update Service (CVE-2025-48799). This vulnerability may be exploited on Windows 11/10 hosts with two or more hard drives.

Notable among the rest:

🔹 RCE - CDPService (CVE-2025-49724), KDC Proxy Service (CVE-2025-49735), SharePoint (CVE-2025-49704, CVE-2025-49701), Hyper-V DDA (CVE-2025-48822), MS Office (CVE-2025-49695), NEGOEX (CVE-2025-47981), MS SQL Server (CVE-2025-49717)
🔹 InfDisc - MS SQL Server (CVE-2025-49719)
🔹 EoP - MS VHD (CVE-2025-49689), TCP/IP Driver (CVE-2025-49686), Win32k (CVE-2025-49727, CVE-2025-49733, CVE-2025-49667), Graphics Component (CVE-2025-49732, CVE-2025-49744)

🗒 Full Vulristics report

На русском

June Linux Patch Wednesday

June Linux Patch Wednesday

June Linux Patch Wednesday. This time, there are 598 vulnerabilities, almost half as many as in May. Of these, 355 are in the Linux Kernel. There are signs of exploitation in the wild for 3 vulnerabilities (CISA KEV).

🔻 SFB - Chromium (CVE-2025-2783)
🔻 MemCor - Chromium (CVE-2025-5419)
🔻 CodeInj - Hibernate Validator (CVE-2025-35036). This vulnerability is exploited in attacks on Ivanti EPMM (CVE-2025-4428).

Additionally, for 40 (❗️) vulnerabilities public exploits are available or there are signs of their existence. Notable among them are:

🔸 RCE - Roundcube (CVE-2025-49113)
🔸 EoP - libblockdev (CVE-2025-6019)
🔸 DoS - Apache Tomcat (CVE-2025-48988), Apache Commons FileUpload (CVE-2025-48976)
🔸 InfDisc - HotelDruid (CVE-2025-44203)
🔸 DoS - ModSecurity (CVE-2025-47947)

🗒 Full Vulristics report

На русском

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday. A total of 81 vulnerabilities, roughly the same as in May. Among them, 15 vulnerabilities were added between the May and June MSPT. There are 3 vulnerabilities with signs of exploitation in the wild:

🔻 RCE - WEBDAV/Internet Shortcut Files (CVE-2025-33053). For successful exploitation, the victim must click on a malicious .url file.
🔻 SFB - Chromium (CVE-2025-4664)
🔻 Memory Corruption - Chromium (CVE-2025-5419)

There's a PoC for one of the vulnerabilities on GitHub, but I doubt it actually works:

🔸 EoP - Microsoft Edge (CVE-2025-47181)

Other notable ones include:

🔹 RCE - Microsoft Office (CVE-2025-47162, CVE-2025-47164, CVE-2025-47167, CVE-2025-47953), KPSSVC (CVE-2025-33071), SharePoint (CVE-2025-47172), Outlook (CVE-2025-47171)
🔹 EoP - SMB Client (CVE-2025-33073), CLFS (CVE-2025-32713), Netlogon (CVE-2025-33070)

🗒 Full Vulristics report

На русском

Vulnerabilities of Western logistics

Vulnerabilities of Western logistics

Vulnerabilities of Western logistics. On May 21, Western intelligence agencies released joint advisory AA25-141A about attacks targeting infrastructure of Western logistics and tech companies. Alongside the usual Five Eyes, intelligence services from Germany, Czech Republic, Poland, Denmark, Estonia, France, and the Netherlands also contributed.

The document mentions the exploitation of vulnerabilities:

🔻 Remote Code Execution - WinRAR (CVE-2023-38831)
🔻 Elevation of Privilege - Microsoft Outlook (CVE-2023-23397)
🔻 Remote Code Execution - Roundcube (CVE-2020-12641)
🔻 Code Injection - Roundcube (CVE-2021-44026)
🔻 Cross Site Scripting - Roundcube (CVE-2020-35730)

Patches, exploits, and signs of in-the-wild exploitation have been available for years for these vulnerabilities. 🤦‍♂️🤷‍♂️

🗒 Vulristics Report

На русском

May

May

May Linux Patch Wednesday. This time: 1091 vulnerabilities. Of those, 716 are in the Linux Kernel. 🤯 5 vulnerabilities are exploited in the wild:

🔻 RCE - PHP CSS Parser (CVE-2020-13756). In AttackerKB, an exploit exists.
🔻 DoS - Apache ActiveMQ (CVE-2025-27533). In AttackerKB, an exploit exists.
🔻 SFB - Chromium (CVE-2025-4664). In CISA KEV.
🔻 PathTrav - buildkit (CVE-2024-23652) and MemCor - buildkit (CVE-2024-23651). In BDU FSTEC.

For 52 (❗️) more, there are signs of existing public exploits. Two trending vulnerabilities I've mentioned before::

🔸 RCE - Kubernetes "IngressNightmare" (CVE-2025-1974 and 4 others)
🔸 RCE - Erlang/OTP (CVE-2025-32433)

Exploits for these are also notable:

🔸 EoP - Linux Kernel (CVE-2023-53033)
🔸 XSS - Horde IMP (CVE-2025-30349)
🔸 PathTrav - tar-fs (CVE-2024-12905)
🔸 SFB - kitty (CVE-2025-43929)
🔸 DoS - libxml2 (CVE-2025-32414)

🗒 Full Vulristics report

На русском

I'm done preparing the slides for my talk about Vulristics at PHDays

I'm done preparing the slides for my talk about Vulristics at PHDays

I'm done preparing the slides for my talk about Vulristics at PHDays. 😇 I'll be speaking on the last day of the festival - Saturday, May 24, at 16:00 in Popov Hall 25. If you're there at that time, I'd be glad to see you. If not - join online! 😉

I'll have an hour to dive into Vulristics, vulnerability analysis & prioritization. 🤩 I'll walk through the Vulristics report structure, typical tasks (like analyzing Microsoft Patch Tuesday, Linux Patch Wednesday, individual trending CVEs, and vulnerability sets), how the work with data sources is organized, the challenges of accurately detecting vulnerability types and vulnerable products. Finally, I'll discuss Vulristics integration into pipelines. Feel free to use the code - Vulristics is MIT-licensed. 🆓

➡️ Talk on the PHDays website – you can download the .ics calendar file there 😉
⏰ May 24, 2025, 16:00 (MSK)
📍 Luzhniki, Popov Hall 25

На русском

May Microsoft Patch Tuesday

May Microsoft Patch Tuesday

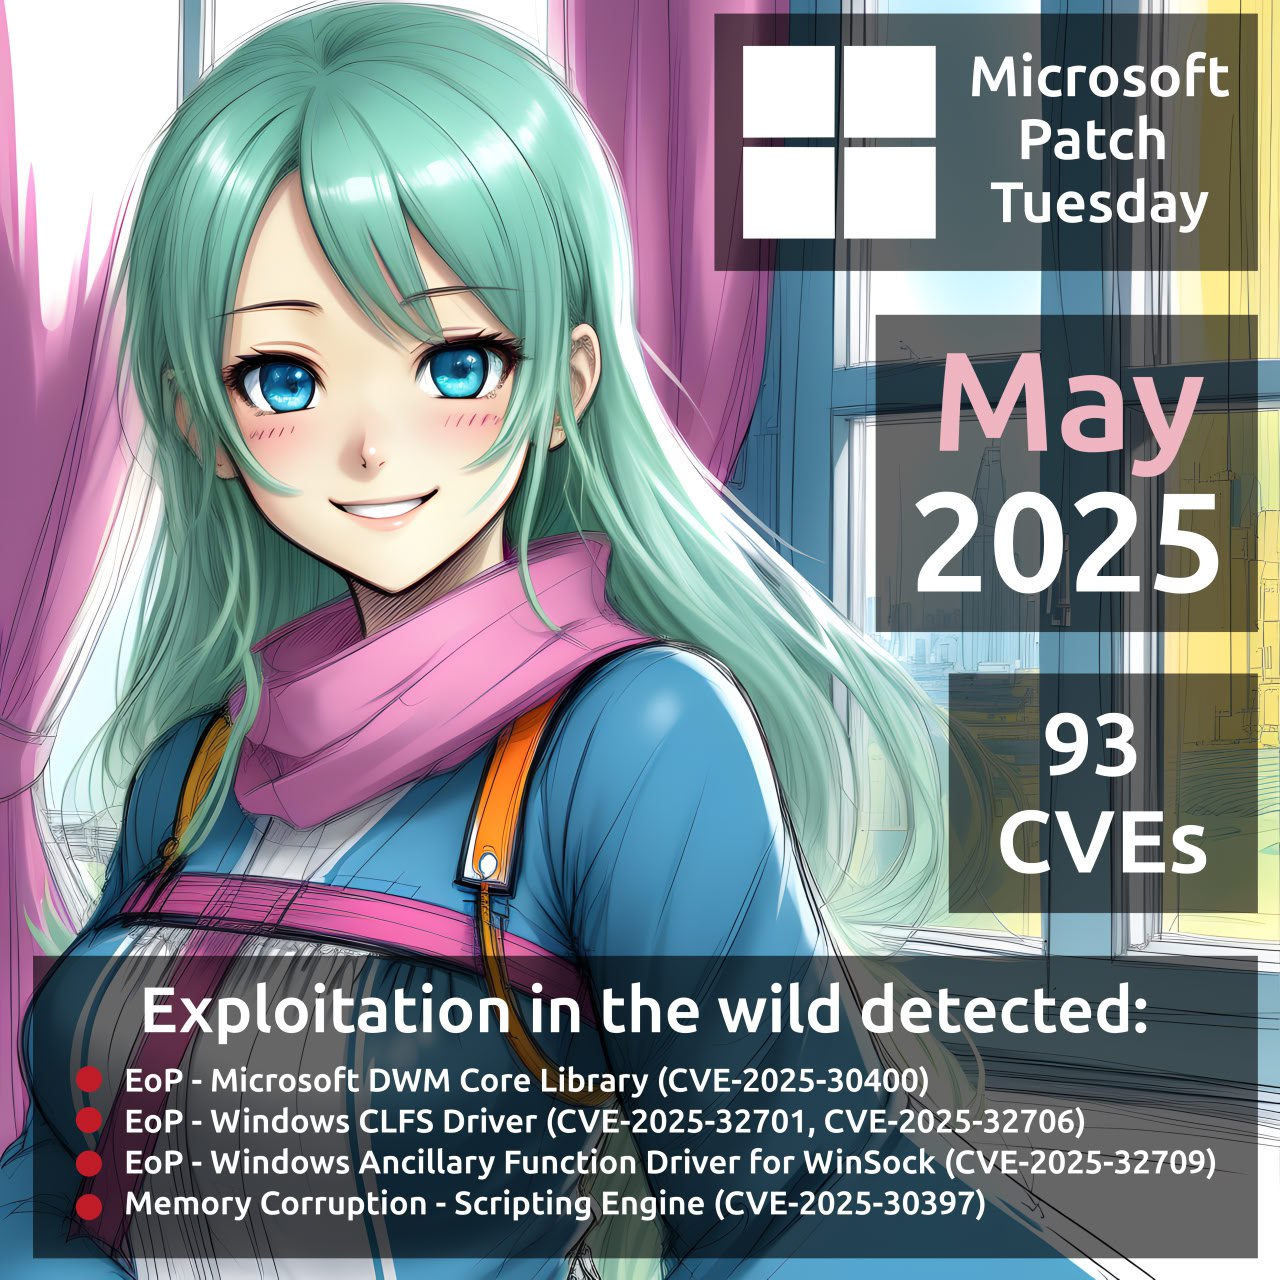
May Microsoft Patch Tuesday. A total of 93 vulnerabilities - about 1.5 times fewer than in April. Of these, 22 were added between the April and May MSPT. There are 5 vulnerabilities show signs of in-the-wild exploitation:

🔻 EoP - Microsoft DWM Core Library (CVE-2025-30400)
🔻 EoP - Windows CLFS Driver (CVE-2025-32701, CVE-2025-32706)
🔻 EoP - Windows Ancillary Function Driver for WinSock (CVE-2025-32709)
🔻 Memory Corruption - Scripting Engine (CVE-2025-30397). RCE when clicking a malicious link. Exploitation requires the "Allow sites to be reloaded in Internet Explorer" option.

There are currently no vulnerabilities with public exploits.

Notable among the rest:

🔹 RCE - Remote Desktop Client (CVE-2025-29966, CVE-2025-29967), Office (CVE-2025-30377, CVE-2025-30386), Graphics Component (CVE-2025-30388), Visual Studio (CVE-2025-32702)
🔹 EoP - Kernel Streaming (CVE-2025-24063), CLFS Driver (CVE-2025-30385)

🗒 Full Vulristics report

На русском