Tag Archives: Vulristics

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

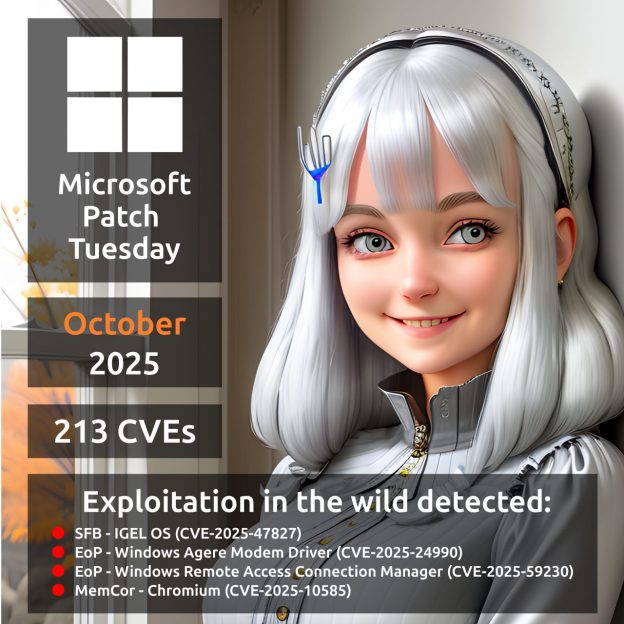
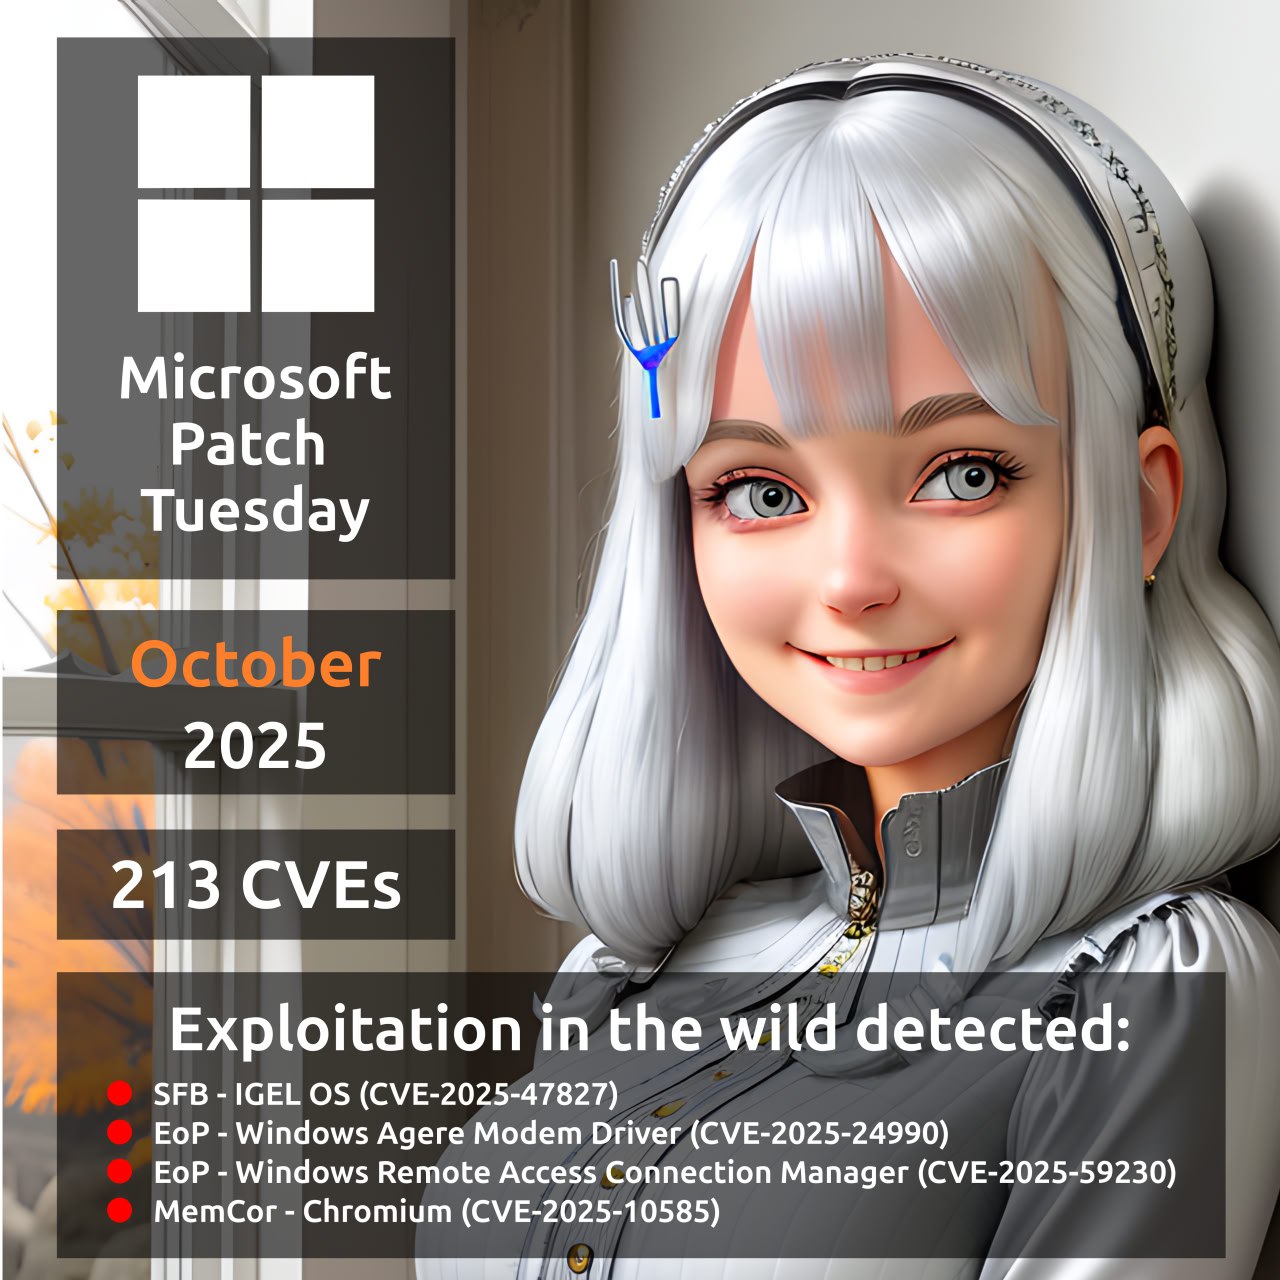
October Microsoft Patch Tuesday. A total of 213 vulnerabilities - twice as many as in September. Of these, 41 vulnerabilities were added between the September and October MSPT. There are four vulnerabilities with evidence of exploitation in the wild:

🔻 SFB - IGEL OS (CVE-2025-47827) - public exploit available
🔻 EoP - Windows Agere Modem Driver (CVE-2025-24990)
🔻 EoP - Windows Remote Access Connection Manager (CVE-2025-59230)
🔻 MemCor - Chromium (CVE-2025-10585)

Another vulnerability with a public PoC exploit:

🔸 RCE - Unity Runtime (CVE-2025-59489)

Among the remaining vulnerabilities with no public exploits or signs of exploitation in the wild, the following stand out:

🔹 RCE - WSUS (CVE-2025-59287), Microsoft Office (CVE-2025-59227, CVE-2025-59234)
🔹 EoP - Windows Agere Modem Driver (CVE-2025-24052), Windows Cloud Files Mini Filter Driver (CVE-2025-55680)
🗒 Full Vulristics Report

На русском

Vulners has added information on exploits

Vulners has added information on exploits

Vulners has added information on exploits. But wasn’t that already available before? After all, Vulristics takes most of its exploit-related data from Vulners! 🤔

That’s true. ✅ But previously an exploit in Vulners was always a Vulners object from a specific collection. For example, an exploit page from ExploitDB. The centralized, collection-based approach works great for sources like vulnerability databases, security bulletins, and exploit packs.

However, quite often an exploit PoC is found in random places - for example, in a researcher’s blog post or on a vendor’s page. For such cases, Vulners now also stores exploits as sets of links in the vulnerability metadata. 🔗🧩 These links are collected from various sources, including NVD, GitHub, and Gitee.

The number of sources will expand, exploit information in Vulners will become more complete, and tools like Vulristics will be able to prioritize vulnerabilities even better based on that. 🧰📈

На русском

September Linux Patch Wednesday

September Linux Patch Wednesday

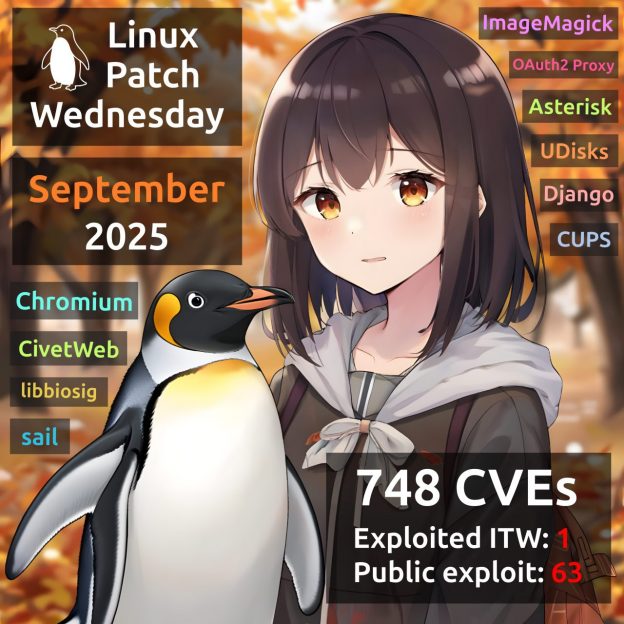
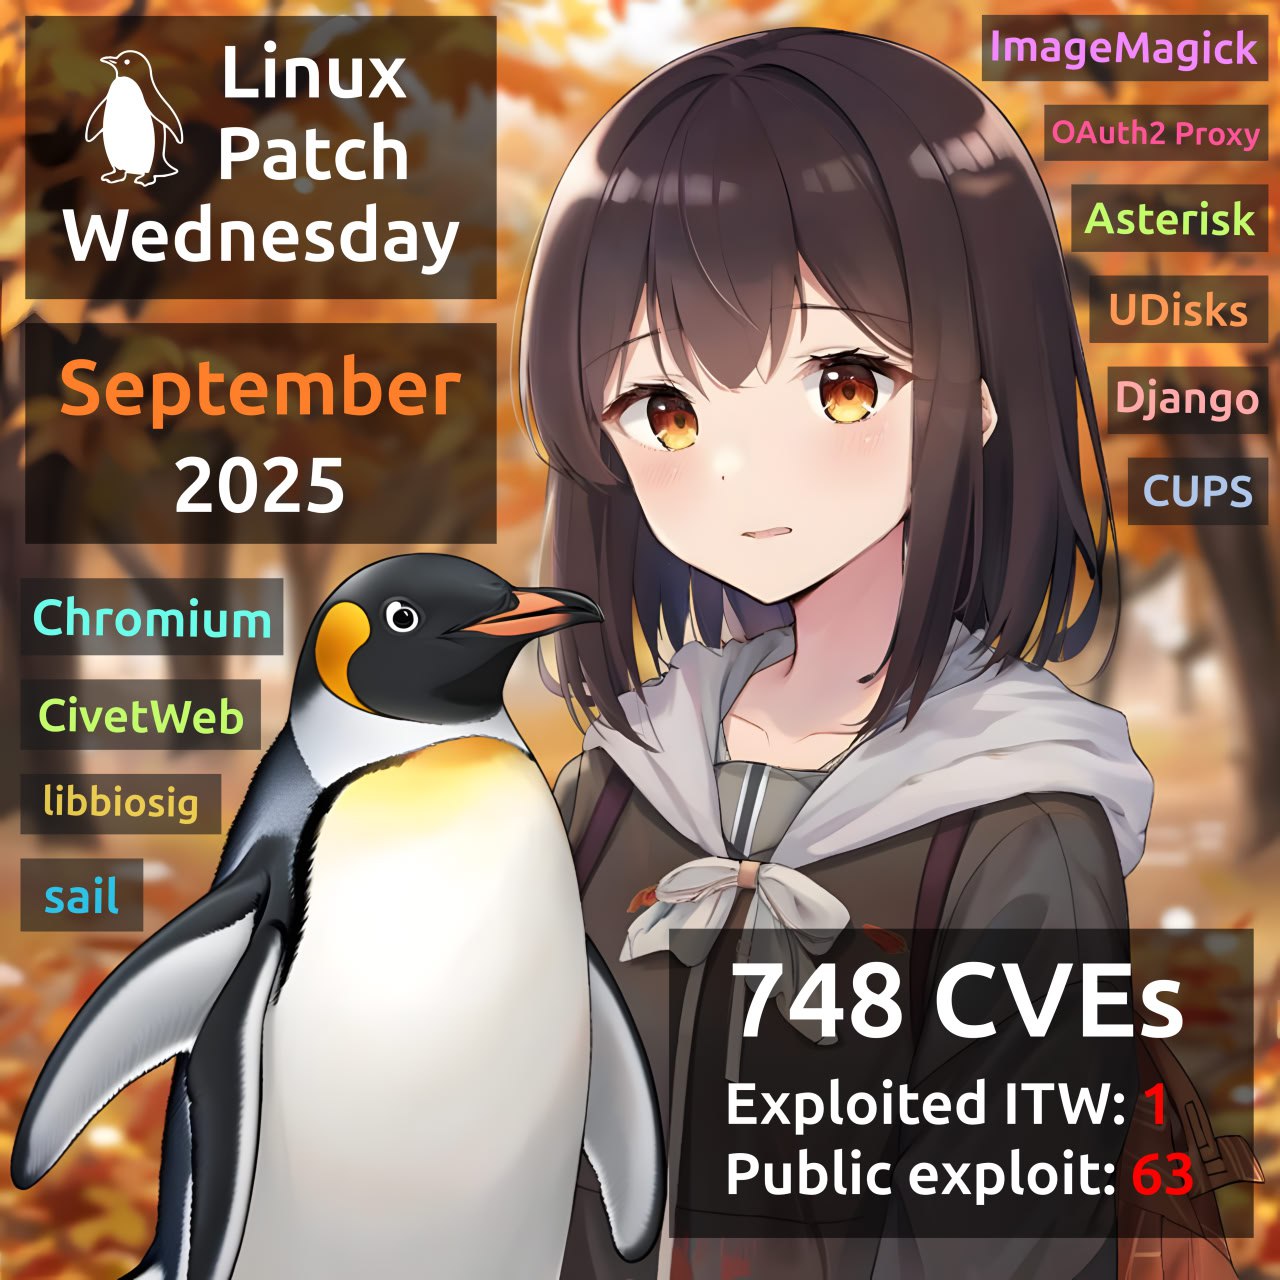
September Linux Patch Wednesday. In September, Linux vendors began addressing 748 vulnerabilities, slightly fewer than in August. Of these, 552 are in the Linux Kernel. The share of Linux Kernel vulnerabilities is growing! One vulnerability shows signs of being actively exploited (CISA KEV):

🔻 MemCor - Chromium (CVE-2025-10585). Public exploits are available.

For 63 (❗️) vulnerabilities, public exploits are available or there are signs they exist. Notable ones include:

🔸 RCE - CivetWeb (CVE-2025-55763), ImageMagick (CVE-2025-55298), Asterisk (CVE-2025-49832), libbiosig (CVE-2025-46411 and 22 other CVEs), sail (CVE-2025-32468 and 7 other CVEs)
🔸 AuthBypass - OAuth2 Proxy (CVE-2025-54576), CUPS (CVE-2025-58060)
🔸 EoP - UDisks (CVE-2025-8067)
🔸 SQLi - Django (CVE-2025-57833)
🔸 SFB - CUPS (CVE-2025-58364)

🗒 Full Vulristics report

На русском

September Microsoft Patch Tuesday

September Microsoft Patch Tuesday

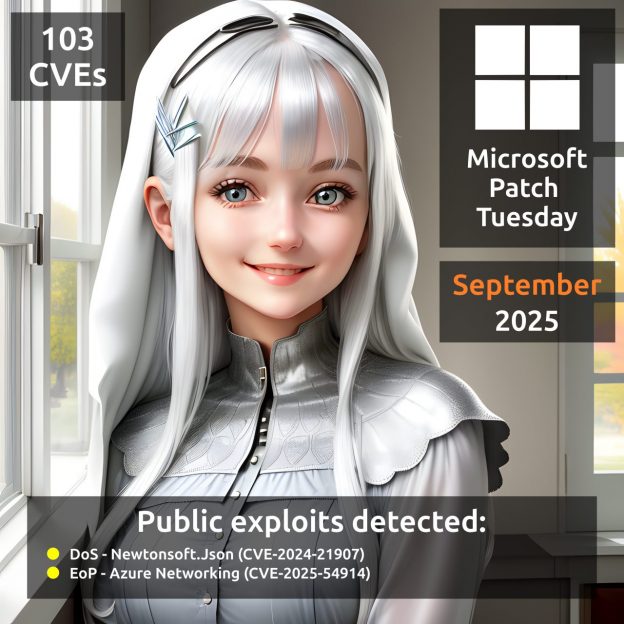
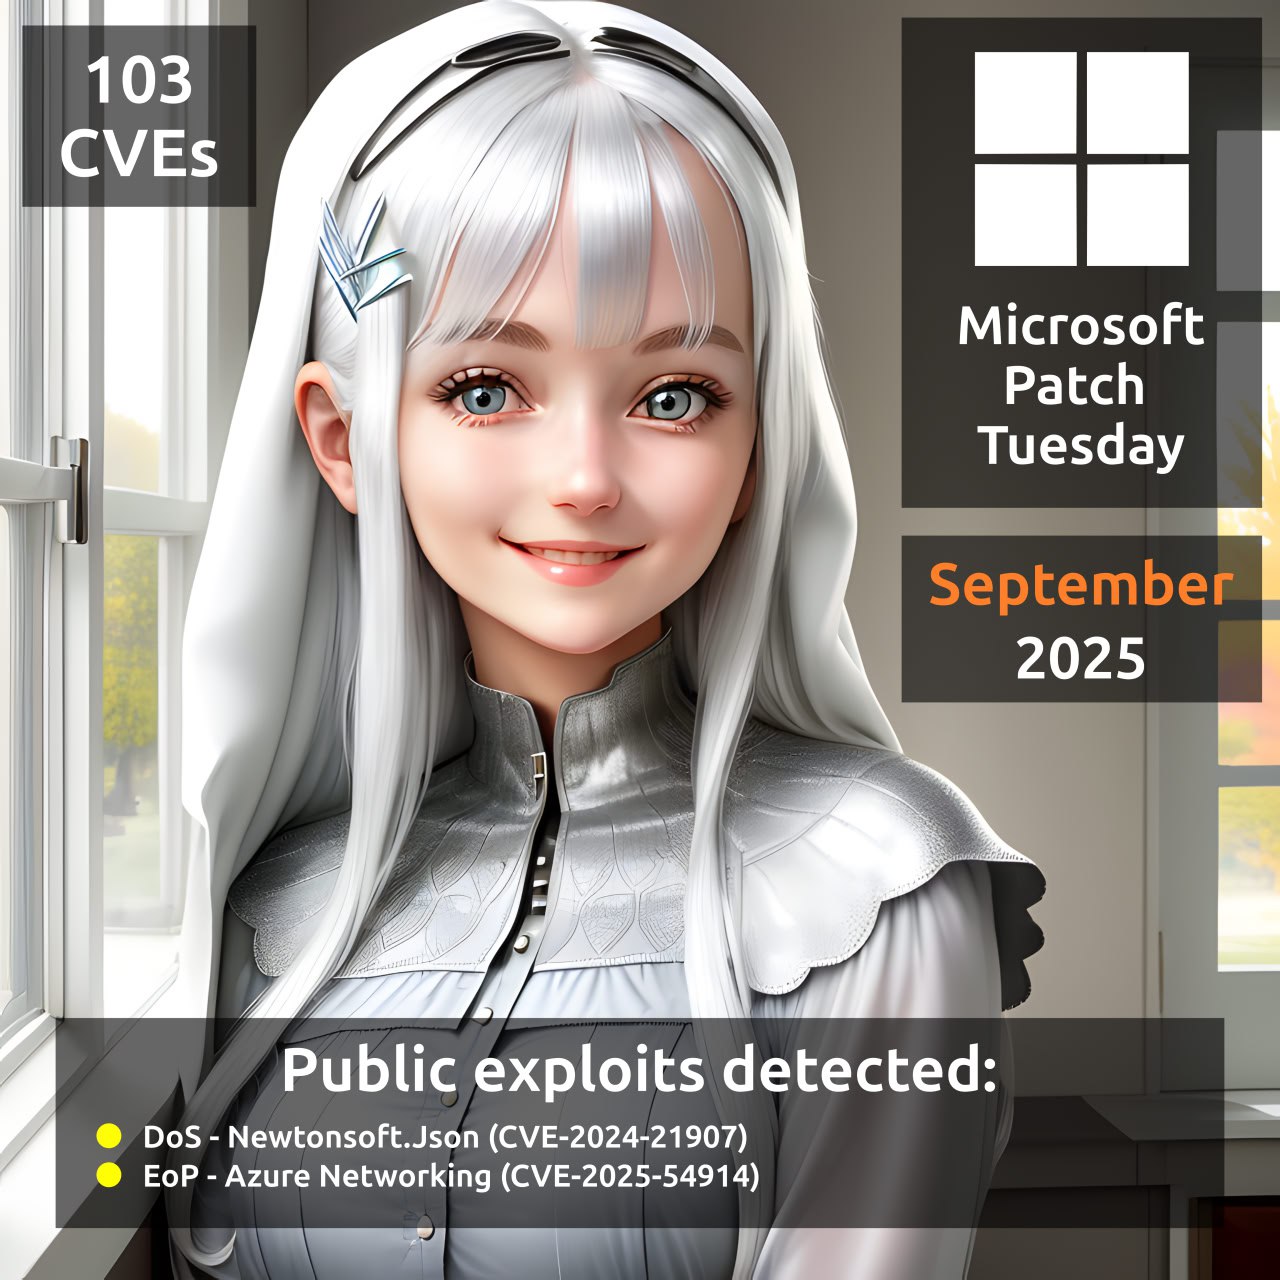
September Microsoft Patch Tuesday. A total of 103 vulnerabilities, 29 fewer than in August. Of these, 25 vulnerabilities were added between the August and September MSPT. So far, no vulnerabilities are known to be exploited in the wild. Two have public PoC exploits:

🔸 DoS - Newtonsoft.Json (CVE-2024-21907)
🔸 EoP - Azure Networking (CVE-2025-54914)

Notable among the other vulnerabilities without public exploits:

🔹 RCE - Microsoft Office (CVE-2025-54910), Windows Graphics Component (CVE-2025-55228), NTFS (CVE-2025-54916), SharePoint (CVE-2025-54897), Microsoft HPC Pack (CVE-2025-55232), Hyper-V (CVE-2025-55224), Graphics Kernel (CVE-2025-55226, CVE-2025-55236)
🔹 EoP - Windows NTLM (CVE-2025-54918), Windows Kernel (CVE-2025-54110), Windows SMB (CVE-2025-55234), Windows TCP/IP Driver (CVE-2025-54093), Hyper-V (CVE-2025-54091, CVE-2025-54092, CVE-2025-54098, CVE-2025-54115)

🗒 Full Vulristics report

На русском

August Linux Patch Wednesday

August Linux Patch Wednesday

August Linux Patch Wednesday. I’m late with this LPW since I was improving the generation of LPW bulletin lists and the operation of Vulristics. 🙂 In August, Linux vendors addressed 867 vulnerabilities, nearly twice July’s total, including 455 in the Linux Kernel. One vulnerability is confirmed exploited in the wild (CISA KEV):

🔻 SFB - Chromium (CVE-2025-6558) - an exploited SFB in Chromium for the fourth month in a row. 🙄

Public exploits are available or suspected for 72 (❗️) vulnerabilities. The most important are:

🔸 RCE - WordPress (CVE-2024-31211) - from last year, but recently fixed in Debian; Kubernetes (CVE-2025-53547), NVIDIA Container Toolkit (CVE-2025-23266), Kafka (CVE-2025-27819)
🔸 Command Injection - Kubernetes (CVE-2024-7646)
🔸 Code Injection - PostgreSQL (CVE-2025-8714/8715), Kafka (CVE-2025-27817)
🔸 Arbitrary File Writing - 7-Zip (CVE-2025-55188)

🗒 Full Vulristics report

На русском

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday. A total of 132 vulnerabilities, 20 fewer than in July. Of these, 25 were added between the July and August MSPT. Three are actively exploited, including two related to the trending SharePoint "ToolShell" flaw, exploited since July 17.

🔻 RCE - Microsoft SharePoint Server (CVE-2025-53770)
🔻 Spoofing - Microsoft SharePoint Server (CVE-2025-53771)

Another actively exploited vulnerability affects Chromium:

🔻SFB - Chromium (CVE-2025-6558)

Notable among the rest, without public exploits or exploitation signs, are:

🔹 RCE - SharePoint (CVE-2025-49712), GDI+ (CVE-2025-53766), Windows Graphics Component (CVE-2025-50165), DirectX Graphics Kernel (CVE-2025-50176), Microsoft Office (CVE-2025-53731, CVE-2025-53740), MSMQ (CVE-2025-53144, CVE-2025-53145, CVE-2025-50177)
🔹 EoP - Kerberos (CVE-2025-53779), NTLM (CVE-2025-53778)

🗒 Full Vulristics report

На русском

July Linux Patch Wednesday

July Linux Patch Wednesday

July Linux Patch Wednesday. This time, there are 470 vulnerabilities, slightly fewer than in June. Of these, 291 are in the Linux Kernel. One vulnerability shows signs of being exploited in the wild (CISA KEV):

🔻 SFB - Chromium (CVE-2025-6554)

There are also 36 (❗️) vulnerabilities for which public exploits are available or suspected to exist. Notable among them:

🔸 RCE - Redis (CVE-2025-32023), pgAdmin (CVE-2024-3116), Git (CVE-2025-48384)
🔸 EoP - Sudo (CVE-2025-32462, CVE-2025-32463)
🔸 PathTrav - Tar (CVE-2025-45582)
🔸 XSS - jQuery (CVE-2012-6708)
🔸 SFB - PHP (CVE-2025-1220)
🔸 DoS - LuaJIT (CVE-2024-25177), Linux Kernel (CVE-2025-38089)
🔸 MemCor - DjVuLibre (CVE-2025-53367)

🗒 Full Vulristics report

На русском