Category Archives: Topics

End of CentOS Linux. Where to migrate?

End of CentOS Linux. Where to migrate? Hello everyone! As you probably know, CentOS Linux, the main Enterprise-level Linux server distribution, will soon disappear. It wasn’t hard to predict when RedHat acquired CentOS in 2014, and now it is actually happening. End of life of CentOS Linux 8 was 31.12.2021. There won’t be CentOS Linux as downstream for RedHat anymore. Only CentOS Stream, that will be upstream for RedHat, more or less a testing distro like Fedora.

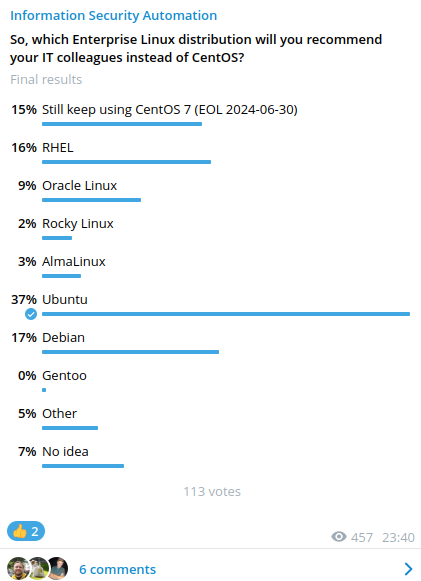
Of course, it is a matter of debate whether security guys can actually decide which Linux distributions a company will use and set that as a requirement. But in any case, the security guys will definitely take part in the decision. I made a poll in my Telegram channel. 113 people voted. So, let’s take a look at the results and discuss which of the Linux distributions we can recommend to IT teams.
Continue reading →

Microsoft Patch Tuesday January 2022

Microsoft Patch Tuesday January 2022. Hello everyone! This episode will be about Microsoft Patch Tuesday for January 2022. Traditionally, I will use my open source Vulristics tool for analysis. This time I didn’t make any changes to how connectors work. The report generation worked correctly on the first try.

python3.8 vulristics.py --report-type "ms_patch_tuesday" --mspt-year 2022 --mspt-month "January" --rewrite-flag "True"

The only thing I have improved is the detection of types of vulnerabilities and vulnerable products. “Unknown Vulnerability Type” was for two vulnerabilities, so I added the “Elevation Of Privilege” и “Cross-Site Scripting” spelling options. I added detections for 13 products and 19 Windows components. I also corrected the method for sorting vulnerabilities with the same Vulristics score. Previously, such vulnerabilities were sorted by CVE id, now they are sorted by vulnerability type and product. This allows you to see the clusters of similar vulnerabilities.

Continue reading →

Log4j "Log4Shell" RCE explained (CVE-2021-44228)

Log4j “Log4Shell” RCE explained (CVE-2021-44228). Hello everyone! I decided to make a separate episode about Log4Shell. Of course, there have already been many reviews of this vulnerability. But I do it primarily for myself. It seems to me that serious problems with Log4j and similar libraries will be with us for a long time. Therefore, it would be interesting to document how it all began. So what is the root cause of Log4Shell?

Logs

Generally speaking, the IT infrastructure of any company deals with streams of input data. From user requests to a corporate website to integration with banking APIs and cloud services. A lot of data gets into the infrastructure of the company, is transferred from system to system, periodically getting into the logs. These logs are required to verify that the systems are functioning correctly.

Continue reading →

Microsoft Patch Tuesday December 2021

Microsoft Patch Tuesday December 2021. Hello everyone! It’s even strange to talk about other vulnerabilities, while everyone is so focused on vulnerabilities in log4j. But life doesn’t stop. Other vulnerabilities appear every day. And of course, there are many critical ones among them that require immediate patching. This episode will be about Microsoft Patch Tuesday for December 2021.

I will traditionally use my open source Vulristics tool for analysis.

Continue reading →

Vulnerability Intelligence based on media hype. It works? Grafana LFI and Log4j "Log4Shell" RCE

Vulnerability Intelligence based on media hype. It works? Grafana LFI and Log4j “Log4Shell” RCE. Hello everyone! In this episode, I want to talk about vulnerabilities, news and hype. The easiest way to get timely information on the most important vulnerabilities is to just read the news regularly, right? Well, I will try to reflect on this using two examples from last week.

I have a security news telegram channel https://t.me/avleonovnews that is automatically updated by a script using many RSS feeds. And the script even highlights the news associated with vulnerabilities, exploits and attacks.

And last Tuesday, 07.02, a very interesting vulnerability in Grafana was released.

Continue reading →

Vulristics Command Line Interface, improved Product & Vuln. Type Detections and Microsoft Patch Tuesday November 2021

Vulristics Command Line Interface, improved Product & Vuln. Type Detections and Microsoft Patch Tuesday November 2021. Hello everyone! In this episode I want to highlight the latest changes in my Vulristics project. For those who don’t know, this is a utility for prioritizing CVE vulnerabilities based on data from various sources.. Currently Microsoft, NVD, Vulners, AttackerKB.

Command Line Interface

I started working on the CLI for Vulristics. Of course, it is not normal to edit scripts every time to release a report.

Continue reading →

Security News: Microsoft Patch Tuesday October 2021, Autodiscover, MysterySnail, Exchange, DNS, Apache, HAProxy, VMware vCenter, Moodle

Security News: Microsoft Patch Tuesday October 2021, Autodiscover, MysterySnail, Exchange, DNS, Apache, HAProxy, VMware vCenter, Moodle. Hello everyone! This episode will be about relatively recent critical vulnerabilities. Let’s start with Microsoft Patch Tuesday for October 2021. Specifically, with the vulnerability that I expected there, but it didn’t get there.

Autodiscover leak discovered by Guardicore Labs

“Autodiscover, a protocol used by Microsoft Exchange for automatic configuration of clients such as Microsoft Outlook, has a design flaw that causes the protocol to “leak” web requests to Autodiscover domains outside of the user’s domain but in the same TLD (i.e. Autodiscover.com).” Guardicore Labs acquired multiple Autodiscover domains and have captured 372,072 Windows domain credentials in total. It seems Microsoft have chosen to ignore this issue. No CVE, no Outlook or ActiveSync patches. The only fix is to ban the “Autodiscover.” domains on devices.

Microsoft Patch Tuesday for October 2021

74 vulnerabilities: 1 Critical, 30 High, 43 Medium.

Elevation of Privilege – Windows Kernel (CVE-2021-40449)

It is a use-after-free vulnerability in the NtGdiResetDC function of the Win32k driver. A detailed technical description is available in Kasperky Securelist post, but, in short, the vulnerability can lead to leakage of kernel module addresses in the computer’s memory. This vulnerability is being exploited in the wild by APT MysterySnail. All servers and desktops should be updated.

Continue reading →