Tag Archives: PatchTuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday

June Microsoft Patch Tuesday. Last week I was on vacation in Veliky Novgorod, so I'm publishing this overview only now. A total of 202 vulnerabilities were addressed, approximately twice as many as in May. There are currently no vulnerabilities marked as exploited in the wild. However, there are two vulnerabilities with publicly available exploits:

🔸 RCE - HTTP.sys (CVE-2026-47291). This critical vulnerability allows remote, unauthenticated attackers to execute arbitrary code on affected systems without user interaction. However, systems using the default MaxRequestBytes registry value in the Windows HTTP stack are not affected. If needed, you can change this registry setting to protect systems while testing and deploying the patch. Microsoft's security bulletin includes instructions and a PowerShell script for this workaround.

🔸 DoS - HTTP.sys (CVE-2026-49160). The same exploit is used as for the previous RCE vulnerability.

It is also worth paying attention to vulnerabilities that Microsoft has flagged as having a publicly available exploit:

🔹 SFB - Windows BitLocker (CVE-2026-50507). A successful attacker could bypass the BitLocker Device Encryption feature on the system storage device. An attacker with physical access to the target could exploit this vulnerability to gain access to encrypted data. According to Tenable, this is the "Bitskrieg" vulnerability discovered by the researcher known as Chaotic Eclipse/Nightmare Eclipse.

🔹 SFB - Secure Boot (CVE-2026-48570). An attacker who successfully exploited this vulnerability could bypass Secure Boot. This vulnerability was reported by Alon Leviev (STORM), who is known for previous research related to BootKitty and BlackLotus.

Among the remaining vulnerabilities, the following are worth highlighting:

🔹 RCE - Windows Kernel (CVE-2026-45657). This vulnerability allows remote, unauthenticated attackers to run code with SYSTEM privileges without any user interaction. In other words, it could be used to spread automatically between systems. The issue is caused by how the Windows kernel processes TCP/IP traffic. Microsoft rated this as "Exploitation Less Likely", but security researchers and exploit developers are already analyzing the patch and trying to build an exploit. Test and deploy this patch as soon as possible.

🔹 EoP - Windows Collaborative Translation Framework (CTFMON) (CVE-2026-45586). This vulnerability affects a component used for voice and handwriting recognition. If exploited, an attacker could gain SYSTEM privileges. Microsoft rates this vulnerability as "Exploitation More Likely".

🔹 RCE - Windows Remote Desktop Client (CVE-2026-42909, CVE-2026-42913, CVE-2026-42985, CVE-2026-42992, CVE-2026-42993, CVE-2026-44799, CVE-2026-44801, CVE-2026-47289, CVE-2026-47653, CVE-2026-47654, CVE-2026-48563). Successful exploitation would require a victim to connect to an attacker-controlled server using an affected version of the Remote Desktop Client. This action could trigger a heap-based buffer overflow, resulting in remote code execution.

🔹 RCE - DHCP Client Service (CVE-2026-44815). This vulnerability allows remote, unauthenticated attackers to execute code on affected systems without user interaction. Because the DHCP client is widely enabled across Windows systems, this vulnerability presents a broad attack surface. Organizations should prioritize testing and deploying the patch for this vulnerability as soon as possible.

🗒 Full Vulristics report

May Microsoft Patch Tuesday

May Microsoft Patch Tuesday

May Microsoft Patch Tuesday. A total of 119 vulnerabilities, approximately 1.5 times fewer than in April. There are currently no vulnerabilities marked as actively exploited in the wild. However, there is one vulnerability with a public exploit:

🔸 EoP - Windows Kernel (CVE-2026-40369). A detailed write-up and exploit for this vulnerability were published on May 14, two days after the May MSPT. The researcher describes exploitation of the vulnerability as follows: "A single syscall from any unprivileged process — including inside Chrome's renderer sandbox — can increment arbitrary kernel memory addresses. No race conditions. No heap spray. No special tokens. 100% deterministic privilege escalation to SYSTEM."

Among the remaining ones, the following stand out:

🔹 RCE - Windows DNS Client (CVE-2026-41096). A ZDI analyst commented on this vulnerability as follows: "This patch fixes a heap-based buffer overflow in the DNS Client triggered by a malicious DNS response. No authentication or user interaction needed, and since the DNS Client runs on virtually every Windows machine, the attack surface is enormous. An attacker with a position to influence DNS responses (MitM, rogue server) could achieve unauthenticated RCE across your enterprise."

🔹 RCE - Windows Netlogon (CVE-2026-41089). The vulnerability allows an unauthenticated remote attacker to execute arbitrary code on a domain controller by sending a specially crafted network request. Exploitation does not require credentials or user interaction, which classifies this vulnerability as wormable. Compromise of a domain controller means full compromise of the organization's entire domain. A Rapid7 analyst added in their commentary: "No privileges or user interaction are required, and attack complexity is low, which suggests that creation of a reliable exploit might not be especially difficult for anyone with knowledge of the specific mechanism. Microsoft assesses exploitation as less likely, but since those exploitability assessments are provided without an accompanying explanation, it's not clear how much reassurance defenders should take. Anyone who remembers the much-discussed CVE-2020-1472 (aka ZeroLogon) back in 2020 will note that CVE-2026-41089 offers an attacker more immediate control of a domain controller. Patches are available for all versions of Windows Server from 2012 onwards."

🔹 RCE - Windows TCP/IP (CVE-2026-40415). Commentary from a ZDI analyst: "This bug in the TCP/IP stack results from a use-after-free (UAF) and could allow a remote, unauthenticated threat actor to execute code without user interaction. That makes this another wormable bug. However, this one is much less likely to be exploited. The target needs to be under sustained low-memory (memory pressure) conditions, which is pretty rare."

🔹 RCE - Microsoft Word (CVE-2026-40361, CVE-2026-40364, CVE-2026-40366, CVE-2026-40367). An attacker can exploit these vulnerabilities through social engineering by sending a malicious file to a targeted victim. Successful exploitation would grant the attacker arbitrary code execution. Microsoft researchers note that the Preview Pane is an attack vector for each of these vulnerabilities.

🔹 RCE - Microsoft Office (CVE-2026-40363, CVE-2026-42831). A heap-based buffer overflow vulnerability in Microsoft Office may allow an unauthorized attacker to remotely execute arbitrary code.

🔹 RCE - Windows GDI (CVE-2026-35421). A heap-based buffer overflow vulnerability in the Windows GDI component may allow an unauthorized attacker to remotely execute arbitrary code.

🔹 RCE - Microsoft Dynamics 365 On-Premises (CVE-2026-42898). Commentary from a ZDI analyst: "It allows any authenticated user to execute code with a scope change, meaning exploitation can break out and affect resources beyond the vulnerable component itself. Scope changes are pretty rare, so if you're running Dynamics 365 On-Prem, definitely test and deploy this patch quickly."

🔹 EoP - Windows Kernel (CVE-2026-33841, CVE-2026-35420, CVE-2026-40369). CVE-2026-33841 and CVE-2026-40369 are rated "Exploitation More Likely". A local attacker can use these vulnerabilities to elevate privileges to SYSTEM level. In the case of CVE-2026-33841, the attacker can elevate privileges to Medium/High integrity level.

🗒 Full Vulristics report

April Microsoft Patch Tuesday

April Microsoft Patch Tuesday

April Microsoft Patch Tuesday. A total of 167 vulnerabilities, about twice as many as in March. There is one vulnerability already being exploited in the wild:

🔻 Spoofing - Microsoft SharePoint Server (CVE-2026-32201). ZDI experts say "Spoofing bugs in SharePoint often manifest as cross-site scripting (XSS) bugs". "An attacker who successfully exploited the vulnerability could view some sensitive information (Confidentiality), make changes to disclosed information (Integrity), but cannot limit access to the resource (Availability)". There is no info yet about how widely it is being used in attacks, but you should not delay patching, especially if SharePoint is exposed to the Internet.

Formally, there are no public exploits yet. However, there are strong indications that a public exploit may already exist for one vulnerability.

🔸 EoP - Microsoft Defender (CVE-2026-33825). "Insufficient granularity of access control" in Microsoft Defender allows a logged-in attacker to gain higher privileges on a local system. Tenable and ZDI say the bug looks similar to the BlueHammer zero-day, for which a public exploit was released on GitHub on April 3. The researcher who published it, Chaotic Eclipse, criticized Microsoft’s disclosure process. ZDI says the exploit is real, but exploitation is unstable and not always reliable.

Other important issues:

🔹 RCE - Windows Active Directory (CVE-2026-33826). To exploit this, the attacker must have an account. The attacker sends a specially crafted RPC request to a vulnerable server, which can lead to code execution. Microsoft says the attacker must be in the same restricted Active Directory domain as the target system.

🔹 RCE - Windows Internet Key Exchange (IKE) Service Extensions (CVE-2026-33824). ZDI says this vulnerability is wormable, meaning it could allow malware to spread automatically between systems. It affects systems with IKE enabled, which creates a large attack surface. Microsoft recommends blocking UDP ports 500 and 4500 at the network edge. However, attackers inside the network can still use it for lateral movement. Patch quickly if you use IKE.

🔹 RCE - Windows TCP/IP (CVE-2026-33827). ZDI also says this may be wormable, especially on systems using IPv6 and IPSec. A race condition makes it harder to exploit, but similar bugs are often exploited at Pwn2Own, so you should not rely on that difficulty. If you use IPv6, test and deploy the patch quickly before exploits appear.

🔹 EoP - Windows Push Notifications (CVE-2026-26167). This Patch Tuesday includes several sandbox escape vulnerabilities, including in Push Notifications, AFD for Winsock, Windows Management Services, and User Interface Core. CVE-2026-26167 (Push Notifications) is the most important because it is the only one with low attack complexity. The others require winning a race condition (AC:H).

🔹 Spoofing - Remote Desktop (CVE-2026-26151). Weak warnings in the Remote Desktop interface allow a network attacker to trick a user into opening a specially crafted file, leading to spoofing. The issue was found by the UK National Cyber Security Centre (NCSC).

🗒 Full Vulristics report

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday. A total of 79 vulnerabilities, about one and a half times more than in February. What's truly unusual is that this time there were no vulnerabilities with signs of exploitation in the wild or a public exploit! 🤔 At least not yet. 😏

The following vulnerabilities can be highlighted:

🔹 RCE - Print Spooler (CVE-2026-23669), Office (CVE-2026-26110, CVE-2026-26113), Excel (CVE-2026-26107, CVE-2026-26108, CVE-2026-26109, CVE-2026-26112), SharePoint Server (CVE-2026-26106, CVE-2026-26114)
🔹 EoP - SQL Server (CVE-2026-21262, CVE-2026-26115, CVE-2026-26116), Windows Kernel (CVE-2026-24287, CVE-2026-24289, CVE-2026-26132), Windows Win32k (CVE-2026-24285), SMB Server (CVE-2026-24294, CVE-2026-26128), Windows Graphics Component (CVE-2026-23668), .NET (CVE-2026-26131)
🔹 DoS - .NET (CVE-2026-26127)

🗒 Full Vulristics report

На русском

February Microsoft Patch Tuesday

February Microsoft Patch Tuesday

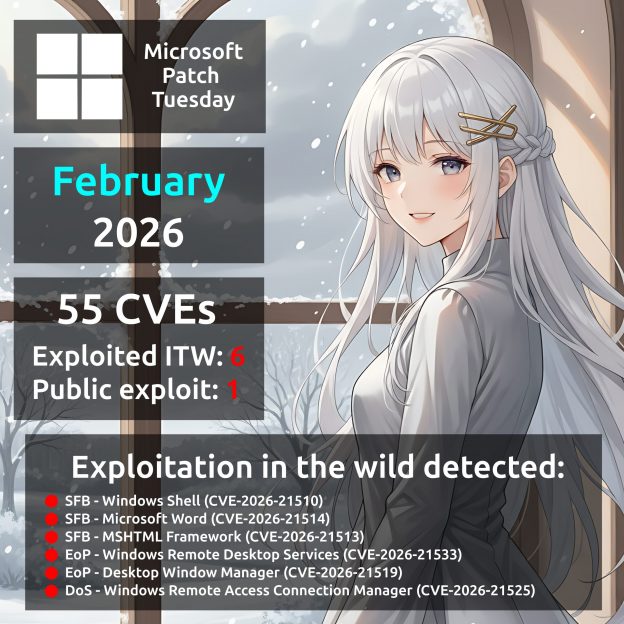
February Microsoft Patch Tuesday. A total of 55 vulnerabilities, half as many as in January. There are as many as six (❗️) vulnerabilities being exploited in the wild:

🔻 SFB/RCE - Windows Shell (CVE-2026-21510)
🔻 SFB/RCE - Microsoft Word (CVE-2026-21514)
🔻 SFB - MSHTML Framework (CVE-2026-21513)
🔻 EoP - Windows Remote Desktop Services (CVE-2026-21533)
🔻 EoP - Desktop Window Manager (CVE-2026-21519)
🔻 DoS - Windows Remote Access Connection Manager (CVE-2026-21525)

There is also one vulnerability with a public exploit:

🔸 DoS - libjpeg (CVE-2023-2804)

Notable remaining vulnerabilities:

🔹 RCE - Windows Notepad (CVE-2026-20841)
🔹 Spoofing - Outlook (CVE-2026-21511)
🔹 EoP - Windows Kernel (CVE-2026-21231, CVE-2026-21239, CVE-2026-21245), Windows AFD.sys (CVE-2026-21236, CVE-2026-21238, CVE-2026-21241)

🗒 Full Vulristics report

На русском

January Microsoft Patch Tuesday

January Microsoft Patch Tuesday

January Microsoft Patch Tuesday. A total of 114 vulnerabilities, twice as many as in December. There is one vulnerability with evidence of in-the-wild exploitation:

🔻 InfDisc - Desktop Window Manager (CVE-2026-20805)

There are also two vulnerabilities with public exploits:

🔸 RCE - Windows Deployment Services (CVE-2026-0386)
🔸 EoP - Windows Agere Soft Modem Driver (CVE-2023-31096)

Other notable vulnerabilities include:

🔹 RCE - Microsoft Office (CVE-2026-20952, CVE-2026-20953), Windows NTFS (CVE-2026-20840, CVE-2026-20922)
🔹 EoP - Desktop Windows Manager (CVE-2026-20871), Windows Virtualization-Based Security (VBS) Enclave (CVE-2026-20876)
🔹 SFB - Secure Boot Certificate Expiration (CVE-2026-21265)

Also noteworthy, reported by Positive Technologies:

🟥 EoP - Windows Telephony Service (CVE-2026-20931)

🗒 Full Vulristics report

На русском

December Microsoft Patch Tuesday

December Microsoft Patch Tuesday

December Microsoft Patch Tuesday. A total of 56 vulnerabilities were fixed - 9 fewer than in November. There is one vulnerability with confirmed in-the-wild exploitation:

🔻 EoP - Windows Cloud Files Mini Filter Driver (CVE-2025-62221)

There are currently no vulnerabilities with publicly available exploits. Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Microsoft Office (CVE-2025-62554, CVE-2025-62557), Microsoft PowerShell (CVE-2025-54100), Microsoft Outlook (CVE-2025-62562), GitHub Copilot for JetBrains (CVE-2025-64671)
🔹 EoP - Windows Win32k (CVE-2025-62458), Windows Cloud Files Mini Filter Driver (CVE-2025-62454, CVE-2025-62457), Windows Common Log File System Driver (CVE-2025-62470), Windows Remote Access Connection Manager (CVE-2025-62472), Windows Storage (CVE-2025-59516)

🗒 Full Vulristics report

На русском