Tag Archives: Rapid7

An introduction to Rapid7 Nexpose API

An introduction to Rapid7 Nexpose API. Another nice thing about Nexpose is that this vulnerability scanner has an open API. And even free Nexpose Community Edition supports it.
Rapid7 Nexpose API

It’s a really generous gift from Rapid7. That means that you can use Nexpose to scan your environment, easily manage it from your scripts and make any vulnerability assessment and remediation logic you need.

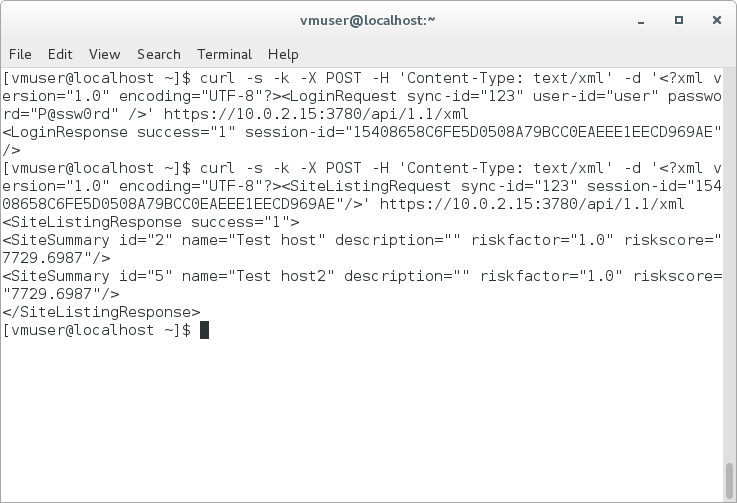
I haven’t found manuals about using Nexpose API to automate basic vulnerability management tasks and decided to write my own. Hope somebody will find it useful. All examples will be in form of curl requests.

Working with Nexpose API is nothing more than sending xml Post-requests to the https://[Nexpose Host]:3780/api/[API Version]/xml and receiving xml responses.
Continue reading →
Testing Rapid7 Nexpose CE vulnerability scanner

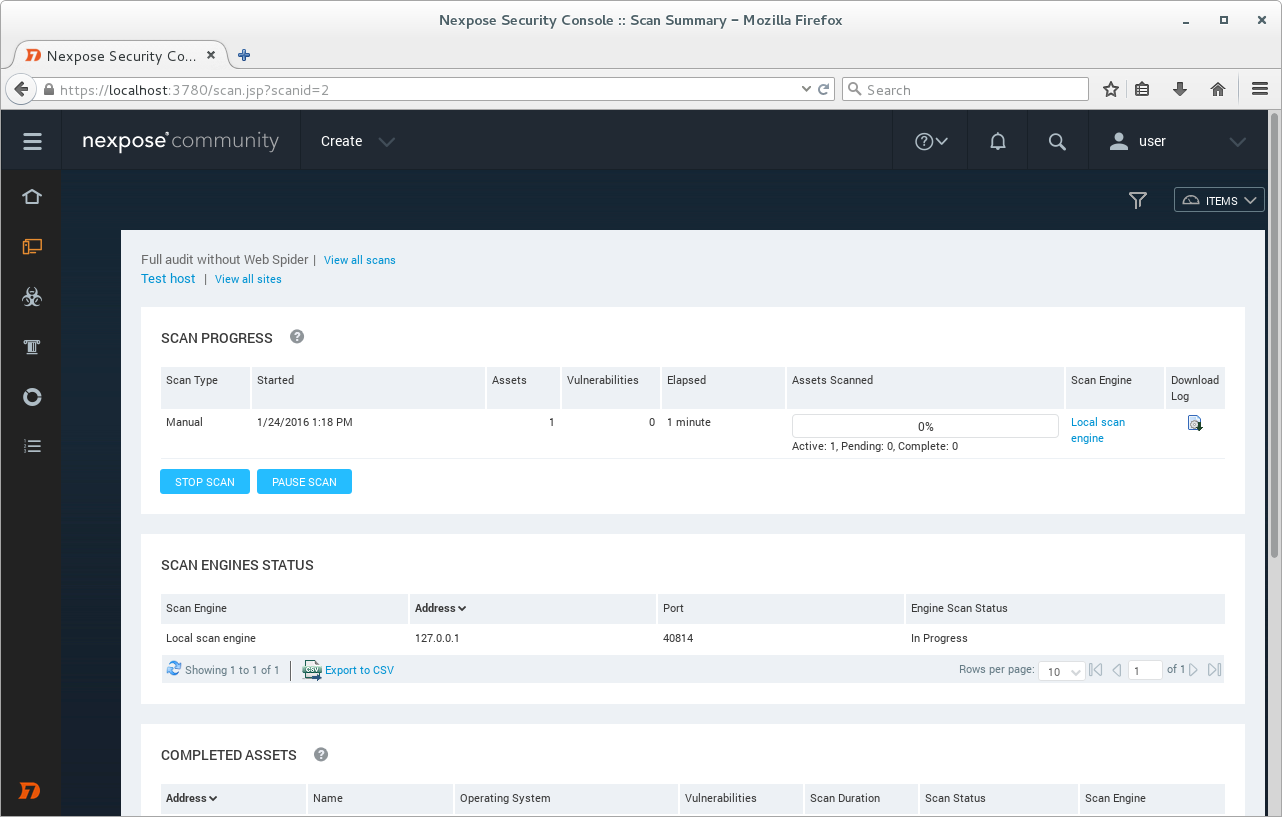
Testing Rapid7 Nexpose CE vulnerability scanner. Today I want to write about another great vulnerability management solution – Nexpose Community Edition by Rapid7. What makes it special? Nexpose CE is a fully functional network vulnerability scanner that can be used for free not only by home users (Nessus Home, for example, has such restrictions), but also by the companies.

Nexpose Community Edition by Rapid7

However, the company should be quite small. By using Nexpose Community Edition you have a permission to scan only 32 ip addresses. But it could be any kind of host: Linux and Windows, Unix and network equipment. And you can scan it as often as you like, with different profiles and produce wide range of reports.

Continue reading →