Tag Archives: Windows

About Elevation of Privilege - Windows Kernel Streaming WOW Thunk Service Driver (CVE-2024-38144) vulnerability

About Elevation of Privilege - Windows Kernel Streaming WOW Thunk Service Driver (CVE-2024-38144) vulnerability

About Elevation of Privilege - Windows Kernel Streaming WOW Thunk Service Driver (CVE-2024-38144) vulnerability. The vulnerability is from the August Microsoft Patch Tuesday. It wasn't highlighted in reviews; all we knew was that a local attacker could gain SYSTEM privileges.

Three and a half months later, on November 27, SSD Secure Disclosure released a write-up with exploit code. This vulnerability was exploited at TyphoonPWN 2024, earning the researcher a $70,000 prize.

SSD stated in their write-up that communications with Microsoft were problematic and noted that "at the time of trying this on the latest version of Windows 11, the vulnerability still worked". It's unclear if this "time of trying" was before the August MSPT or just before the write-up was released in November. If the second option, the vulnerability might still be a 0day. 🤔🤷‍♂️

No reports of this vulnerability being exploited in attacks yet.
На русском

About Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112)

About Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112)

About Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112). The vulnerability is from the December Microsoft Patch Tuesday. Three weeks later, on January 1, researchers from SafeBreach released a write-up on this vulnerability, labeled as LDAPNightmare, and an exploit PoC.

The exploit causes a forced reboot of Windows servers. One prerequisite: the victim domain controller's DNS server must have Internet connectivity.

The attack flow starts with sending a DCE/RPC request to the victim server, causing the LSASS (Local Security Authority Subsystem Service) to crash and force a reboot when an attacker sends a specially crafted CLDAP (Connectionless Lightweight Directory Access Protocol) referral response packet.

But this is all about DoS, why RCE? 🤔 Researchers note that RCE can be achieved by modifying the CLDAP packet.

На русском

New episode "In The Trend of VM" (#10): 8 trending vulnerabilities of November, zero budget VM and who should look for patches

New episode "In The Trend of VM" (#10): 8 trending vulnerabilities of November, zero budget VM and who should look for patches. The competition for the best question on the topic of VM continues. 😉🎁

📹 Video on YouTube, LinkedIn
🗞 Post on Habr (rus)
🗒 Digest on the PT website

Content:

🔻 00:29 Spoofing - Windows NTLM (CVE-2024-43451)
🔻 01:16 Elevation of Privilege - Windows Task Scheduler (CVE-2024-49039)
🔻 02:16 Spoofing - Microsoft Exchange (CVE-2024-49040)
🔻 03:03 Elevation of Privilege - needrestart (CVE-2024-48990)
🔻 04:11 Remote Code Execution - FortiManager "FortiJump" (CVE-2024-47575)
🔻 05:19 Authentication Bypass - PAN-OS (CVE-2024-0012)
🔻 06:32 Elevation of Privilege - PAN-OS (CVE-2024-9474)
🔻 07:42 Path Traversal - Zyxel firewall (CVE-2024-11667)
🔻 08:37 Is it possible to Manage Vulnerabilities with no budget?
🔻 09:53 Should a VM specialist specify a patch to install on the host in a Vulnerability Remediation task?
🔻 10:51 Full digest of trending vulnerabilities
🔻 11:18 Backstage

На русском

December Microsoft Patch Tuesday

December Microsoft Patch Tuesday

December Microsoft Patch Tuesday. 89 CVEs, of which 18 were added since November MSPT. 1 vulnerability with signs of exploitation in the wild:

🔻 EoP - Windows Common Log File System Driver (CVE-2024-49138). There are no details about this vulnerability yet.

Strictly speaking, there was another vulnerability that was exploited in the wild: EoP - Microsoft Partner Network (CVE-2024-49035). But this is an already fixed vulnerability in the Microsoft website and I'm not even sure that it was worth creating a CVE. 🤔

For the remaining vulnerabilities, there are no signs of exploitation in the wild, nor exploits (even private ones).

I can highlight:

🔹 RCE - Windows LDAP (CVE-2024-49112, CVE-2024-49127)
🔹 RCE - Windows LSASS (CVE-2024-49126)
🔹 RCE - Windows Remote Desktop Services (CVE-2024-49106 и ещё 8 CVE)
🔹 RCE - Microsoft MSMQ (CVE-2024-49122, CVE-2024-49118)
🔹 RCE - Microsoft SharePoint (CVE-2024-49070)

🗒 Full Vulristics report

На русском

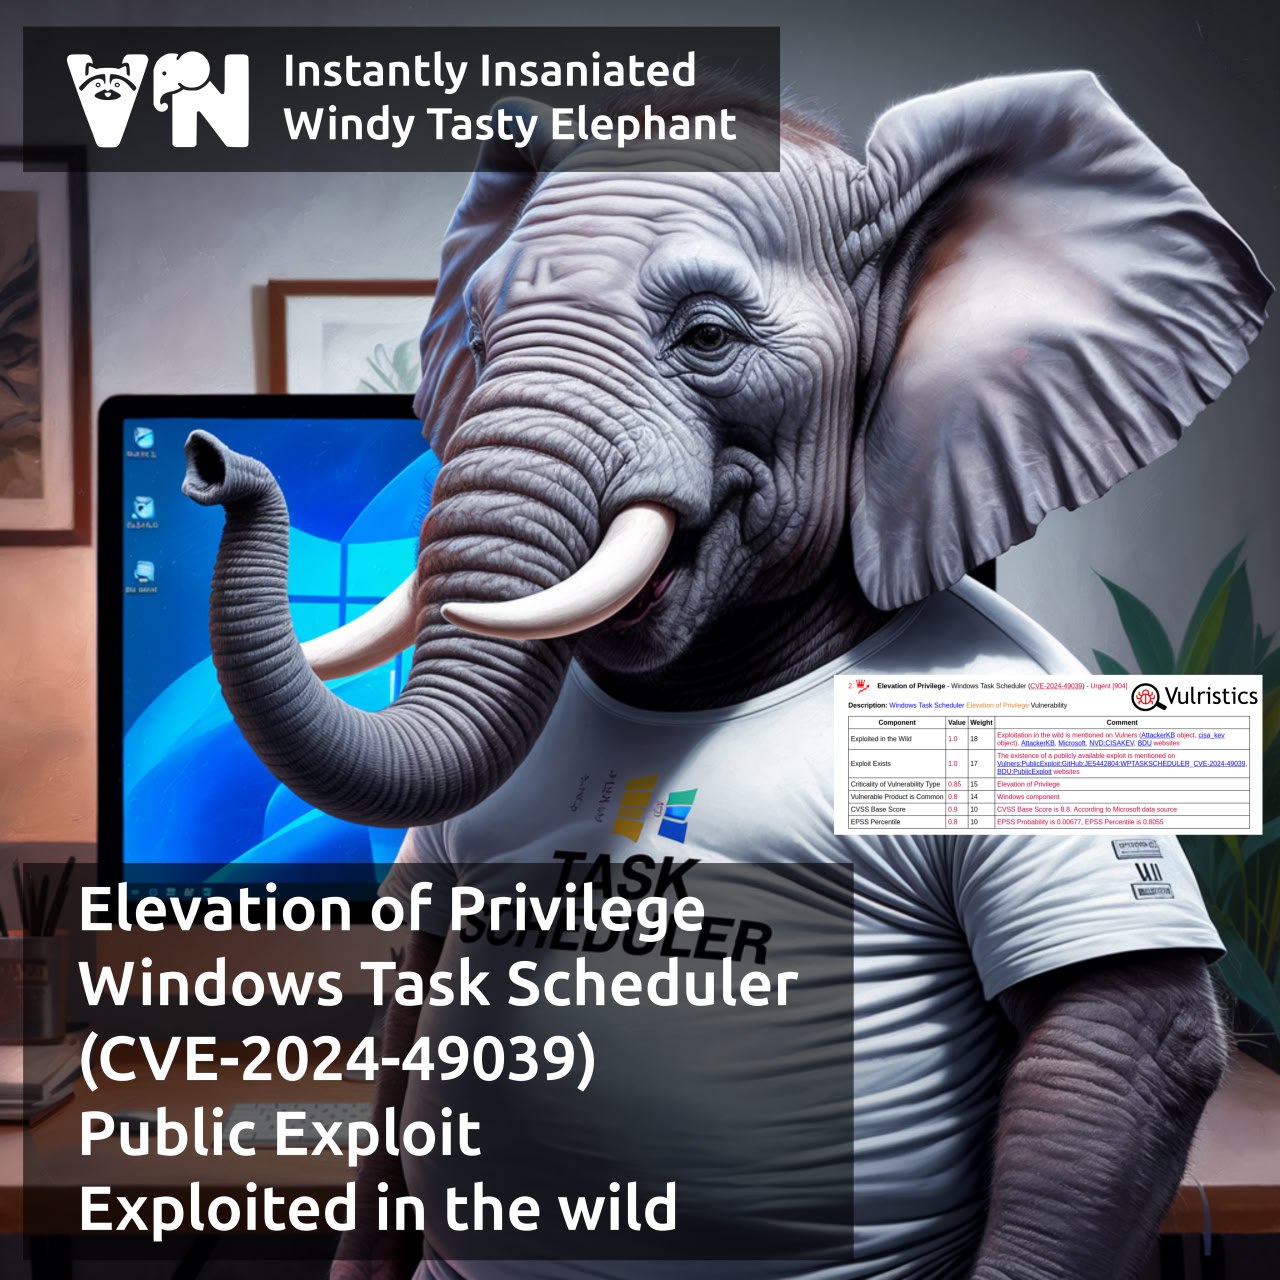
About Elevation of Privilege - Windows Task Scheduler (CVE-2024-49039) vulnerability

About Elevation of Privilege - Windows Task Scheduler (CVE-2024-49039) vulnerability

About Elevation of Privilege - Windows Task Scheduler (CVE-2024-49039) vulnerability. It was released on November Microsoft Patch Tuesday and showed signs of exploitation in the wild right away. To exploit the vulnerability, an authenticated attacker runs a specially crafted application on the target system. The attack can be performed from an AppContainer restricted environment. Using this vulnerability, an attacker can elevate their privileges to Medium Integrity level and gain the ability to execute RPC functions that are restricted to privileged accounts only.

ESET reports that the vulnerability allowed the RomCom attackers to execute malicious code outside the Firefox sandbox and then launch hidden PowerShell processes to download and run malware from C&C servers.

👾 There is a backdoor code on GitHub that exploits this vulnerability.

На русском

November Microsoft Patch Tuesday

November Microsoft Patch Tuesday

November Microsoft Patch Tuesday. 125 CVEs, 35 of which were added since October MSPT. 2 vulnerabilities with signs of exploitation in the wild:

🔻 Elevation of Privilege - Windows Task Scheduler (CVE-2024-49039)
🔻 Disclosure/Spoofing - NTLM Hash (CVE-2024-43451)

No signs of exploitation, but with a private PoC of the exploit:

🔸 Remote Code Execution - Microsoft Edge (CVE-2024-43595, CVE-2024-43596)
🔸 Authentication Bypass - Azure Functions (CVE-2024-38204)
🔸 Authentication Bypass - Microsoft Dataverse (CVE-2024-38139)
🔸 Spoofing - Microsoft Exchange (CVE-2024-49040)

Among the rest can be highlighted:

🔹Remote Code Execution - Windows Kerberos (CVE-2024-43639)
🔹Elevation of Privilege - Windows Win32k (CVE-2024-43636)
🔹Elevation of Privilege - Windows DWM Core Library (CVE-2024-43629)
🔹Elevation of Privilege - Windows NT OS Kernel (CVE-2024-43623)

🗒 Full Vulristics report

На русском

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday

October Microsoft Patch Tuesday. 146 CVEs, of which 28 were added since September MSPT. 2 vulnerabilities with signs of exploitation in the wild:

🔻 Remote Code Execution - Microsoft Management Console (CVE-2024-43572)
🔻 Spoofing - Windows MSHTML Platform (CVE-2024-43573)

Without signs of exploitation in the wild, but with a public PoC exploit:

🔸 Remote Code Execution - Open Source Curl (CVE-2024-6197)

Private exploits exist for:

🔸 Information Disclosure - Microsoft Edge (CVE-2024-38222)
🔸 Security Feature Bypass - Windows Hyper-V (CVE-2024-20659)

Among the rest can be highlighted:

🔹 Remote Code Execution - Remote Desktop Protocol Server (CVE-2024-43582)
🔹 Remote Code Execution - Windows Remote Desktop Client (CVE-2024-43533, CVE-2024-43599)
🔹 Remote Code Execution - Windows Routing and Remote Access Service (RRAS) (CVE-2024-38212 and 11 more CVEs)

🗒 Full Vulristics report

На русском