Tag Archives: Windows

Big Microsoft day: EOL for Win7, Win2008 and crypt32.dll

Big Microsoft day: EOL for Win7, Win2008 and crypt32.dll. Big Microsoft day. End-of-life for Windows 7 desktops and Windows 2008 servers (strictly speaking Windows Server 2008 R2). I think that today many security guys had a fun task to count how many host hosts with win7 and win2008 they still have in the organization. So, Asset Management is a necessity! ?
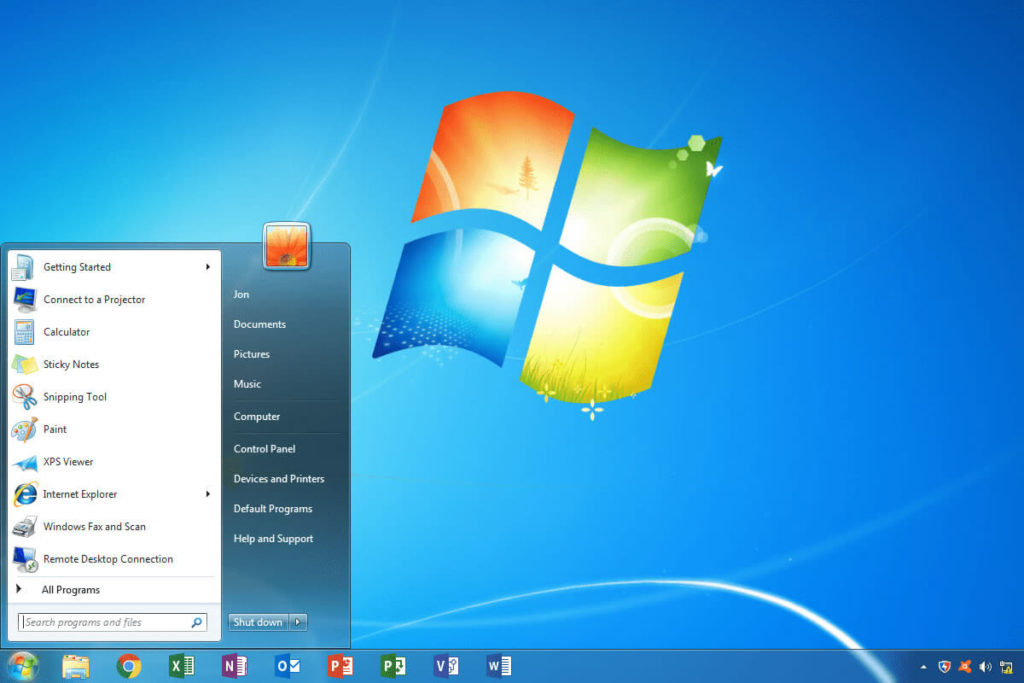
Windows 7 desktop

Now an interesting time should begin, when critical unpatched vulnerabilities may appear for these operation systems. At the same time, the number of hosts with Windows 7 and Windows 2008 will be still big enough for massive attacks. ? Although I think that Microsoft will continue to release patches for the most critical vulnerabilities, like they did it for WinXP. Upd. Also note, that for Windows Server 2008/2008r2 it’s also possible to purchase an extended three years  security update subscription.
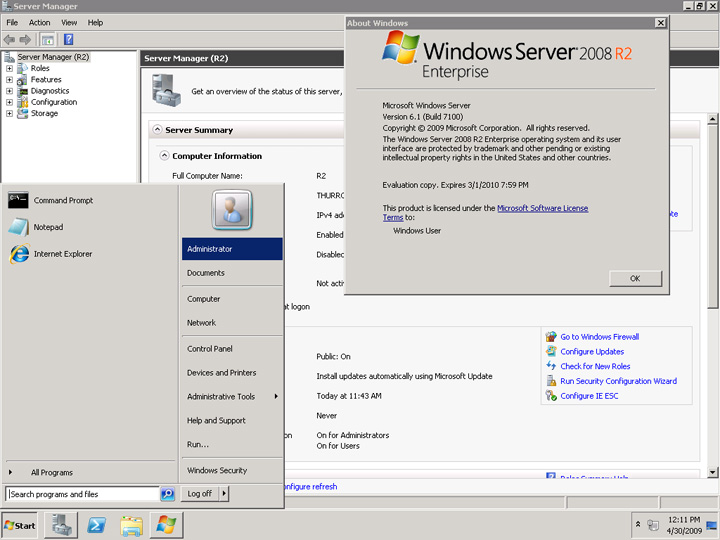
Windows 2008 server

The second interesting topic is the mysterious vulnerability in crypt32.dll (this dll appeared in Windows more than 20 years ago), which might somehow affect authentication and digital signatures in Windows.
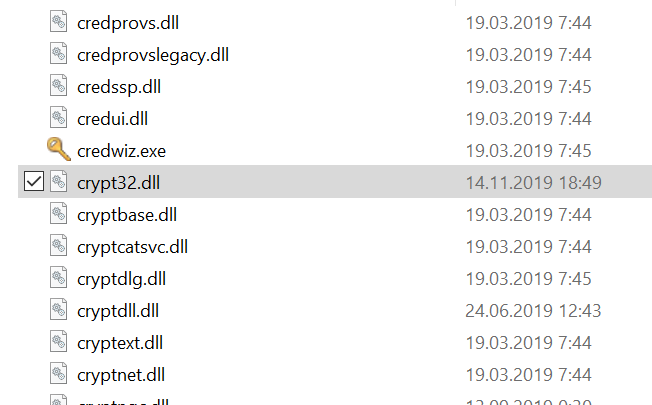
crypt32.dll

Far now it has been only a rumor, but soon it will become clear how dangerous it is and how it can be used.

upd. 15.01. So, what about this vulnerability in crypt32.dll. Now it has the name NSACrypt (because NSA reported it) and the id CVE-2020-0601. It’s not for all versions of Windows, only for Windows 10, Windows Server 2016 and Windows Server 2019.
Continue reading →

Vulnerability Management vendors and Vulnerability Remediation problems

Vulnerability Management vendors and Vulnerability Remediation problems. It’s not a secret, that Vulnerability Management vendors don’t pay much attention to the actual process of fixing vulnerabilities, that they detect in the infrastructure (Vulnerability Remediation). Although it seems to be the main goal of VM products: to make vulnerabilities fixed and whole IT infrastructure more secure, right?

In fact, most of VM vendors see their job in finding a potential problem and providing a link to the Software Vendor’s website page with the remediation description. How exactly the remediation will be done is not their business.

Vulnerability Management vendors and Vulnerability Remediation

The reason is clear. Remediation is a painful topic and it’s difficult to sell it as a ready-made solution. And even when Vulnerability Vendors try to sell it this way, it turns out pretty ugly and does not really work. Mainly because the Remediation feature is sold to the Security Team, and the IT Team will have to use it.

Continue reading →

Why Asset Management is so important for Vulnerability Management and Infrastructure Security?

Why Asset Management is so important for Vulnerability Management and Infrastructure Security? When people ask me how should they start building Vulnerability Management process in their organization (well, sometimes it happens), I advice them to create an effective Asset Management process first. Because it’s the foundation of the whole Infrastructure Security.

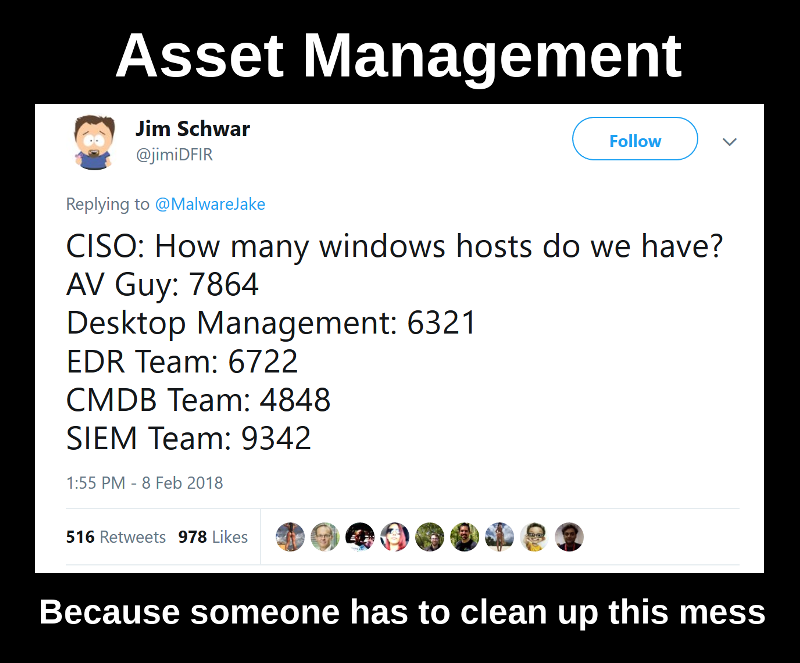
Asset Management. Because someone has to clean up this mess.

The term “Asset Management” has different meanings and if you start to google it, you will get some results related mainly to finance sphere. I use this term as Qualys and Tenable. For me Asset Management is the process of dealing with network hosts.

So, what should you do in situation described in the tweet above, when you don’t know exactly how many Windows hosts you have in your corporate IT environment? And, more importantly, why do you need to know?

Continue reading →

Vulnerability Management at Tinkoff Fintech School

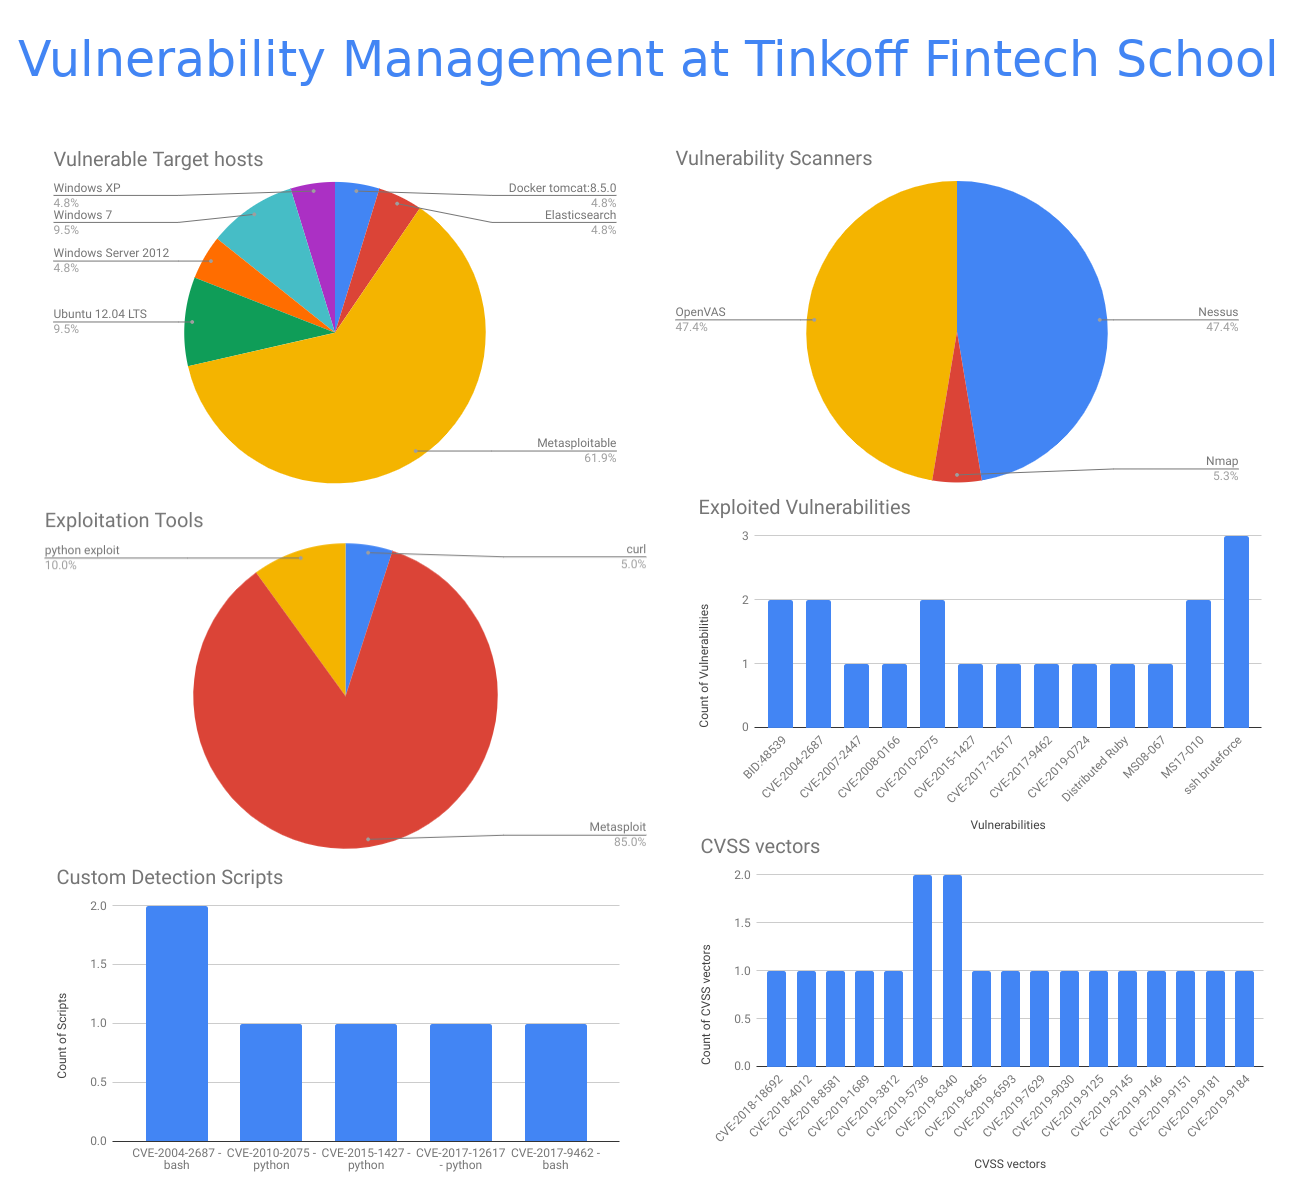
Vulnerability Management at Tinkoff Fintech School. In the last three weeks, I participated in Tinkoff Fintech School – educational program for university students. Together with my colleagues, we prepared a three-month practical Information Security course: 1 lecture per week with tests and home tasks.

Each lecture is given by a member of our security team, specialized in one of the following modules: Vulnerability Management, Application Security, Infrastructure Security, Network Security, Virtualization Security, Banking Systems Security, Blue & Red-teaming, etc.

Vulnerability Management at Tinkoff Fintech School

The course is still ongoing, but my Vulnerability Management module is over. Therefore, I want to share my impressions and some statistics.

Continue reading →

Making CVE-1999-0016 (landc) vulnerability detection script for Windows NT

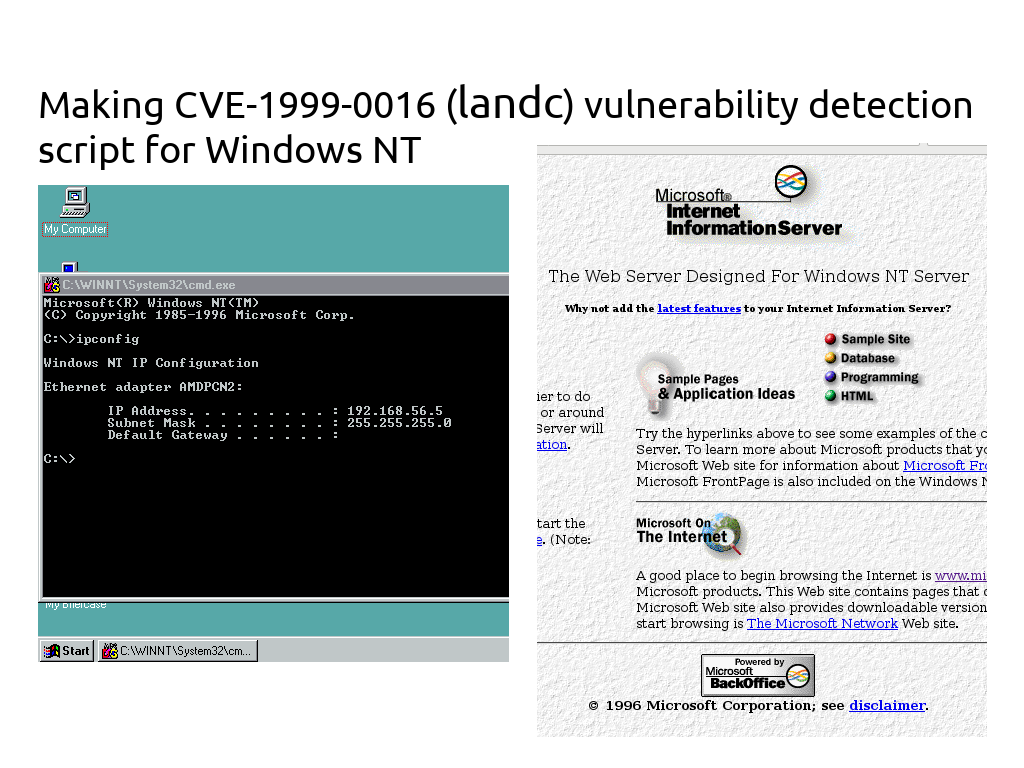
Making CVE-1999-0016 (landc) vulnerability detection script for Windows NT. The fair question is why in 2018 someone might want to deal with Windows NT and vulnerabilities in it. Now Windows NT is a great analogue of DVWA (Damn Vulnerable Web Application), but for operating systems. There are a lot of well-described vulnerabilities with ready-made exploits. A great tool for practising.

Making CVE-1999-0016 (landc) vulnerability detection script for Windows NT

Well, despite the fact that this operating system is not supported since 2004, it can be used in some weird legacy systems. 😉

Continue reading →

Qualys Security Conference Virtual 2018. New Agents, Patch Management and Free Services

Qualys Security Conference Virtual 2018. New Agents, Patch Management and Free Services. Today I attended a very interesting online event – Qualys Security Conference Virtual 2018. It consisted of 11 webinars, began at 18:00 and will end at 03:45 Moscow time. Not the most convenient timing for Russia, but it was worth it. 🙂

Qualys Security Conference 2018

Last time I was at offline QSC event in 2016, so for me it was especially interesting to learn about the new features of Qualys platform.

Continue reading →

CISO Forum and the problems of Vulnerability Databases

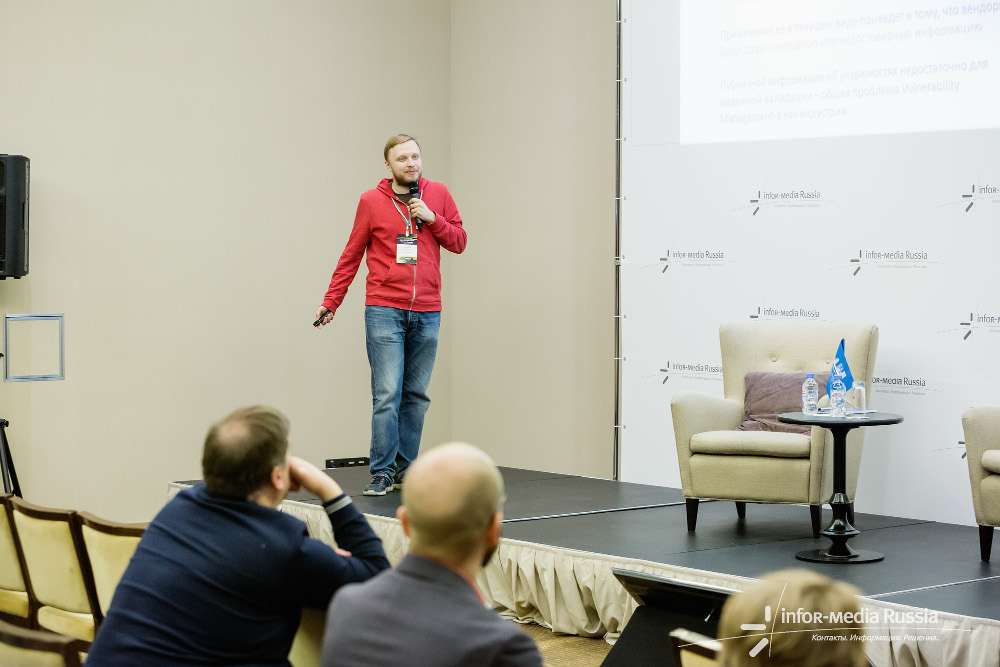
CISO Forum and the problems of Vulnerability Databases. Last Tuesday, April 24,  I was at “CISO FORUM 2020: glance to the future“. I presented there my report “Vulnerability Databases: sifting thousands tons of verbal ore”. In this post, I’ll briefly talk about this report and about the event itself.

CISO Forum 2020

My speech was the last in the program. At the same time, in a parallel stream, there was another interesting presentation by the most famous Russian information security blogger. Thus, there was a real danger of speaking in an empty room. 🙂 But everything went well. There were about 30 spectators and we had an active QA session afterwards.

As I wrote earlier, I started preparing my CyberCentral presentation several months before the event. I did not want to tell the same story again at CISO Forum and PHDays. So I prepared 2 different presentations. At CyberCentral, I was talking about Vulnerability Scanners. And at CISO Forum I was talking mainly about Vulnerable Databases. Of course, I reused some materials, but the accents were different.

Continue reading →