Tag Archives: Windows

March episode "In the Trend of VM" (#13): vulnerabilities of Microsoft, PAN-OS, СommuniGate and who should patch hosts with deployed application

March episode "In the Trend of VM" (#13): vulnerabilities of Microsoft, PAN-OS, СommuniGate and who should patch hosts with deployed application. I'm posting the translated video with a big delay, but it's better than never. 😉

📹 Video on YouTube and LinkedIn
🗞 Post on Habr (rus)
🗒 Digest on the PT website

Content:

🔻 00:00 Greetings
🔻 00:31 Elevation of Privilege - Windows Ancillary Function Driver for WinSock (CVE-2025-21418)
🔻 01:12 Elevation of Privilege - Windows Storage (CVE-2025-21391)
🔻 01:53 Authentication Bypass - PAN-OS (CVE-2025-0108)
🔻 03:09 Remote Code Execution - CommuniGate Pro (BDU:2025-01331)
🔻 04:27 The VM riddle: who should patch hosts with a deployed application?
🔻 07:11 About the digest of trending vulnerabilities
На русском

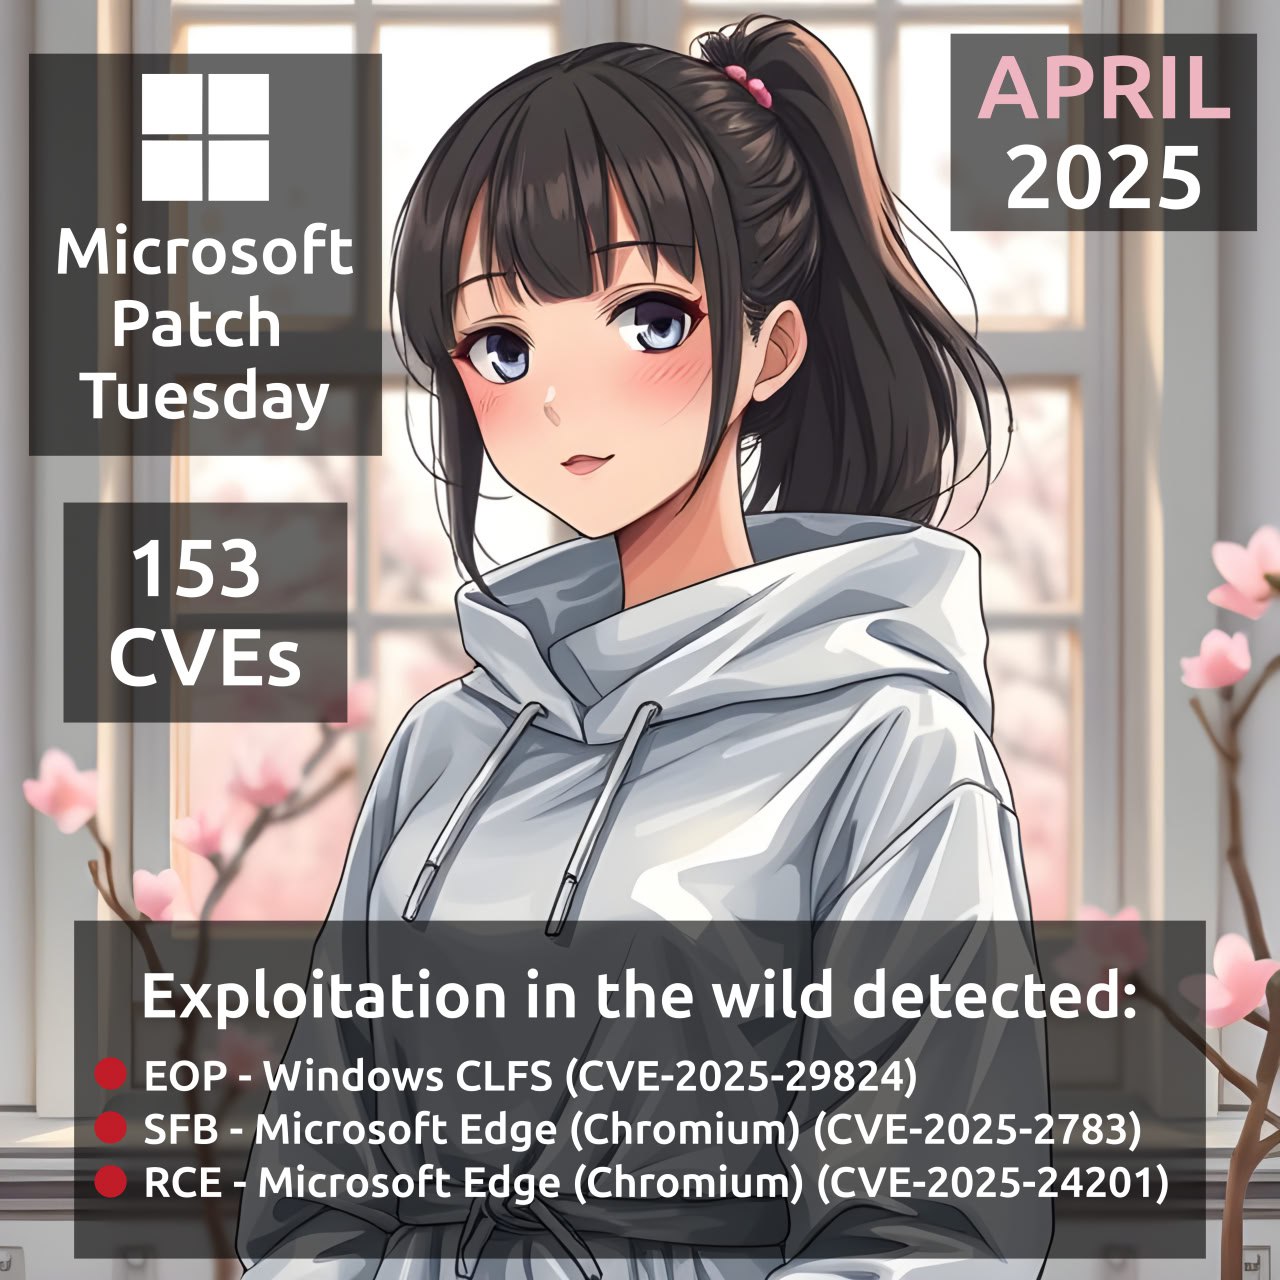
April Microsoft Patch Tuesday

April Microsoft Patch Tuesday

April Microsoft Patch Tuesday. A total of 153 vulnerabilities, 2 times more than in March. Of these, 32 were added between the March and April MSPTs. Three vulnerabilities show signs of exploitation in the wild:

🔻 EoP - Windows Common Log File System Driver (CVE-2025-29824). An attacker can gain SYSTEM privileges. No technical details yet.
🔻 SFB - Microsoft Edge (CVE-2025-2783). Sandbox escape with an existing PoC exploit.
🔻 RCE - Microsoft Edge (CVE-2025-24201). Originally reported as a WebKit vuln on Apple OSes. 🤷‍♂️

Microsoft also patched vulnerabilities in Kubernetes with known exploits (CVE-2025-1974, CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, CVE-2025-24513)

Other notable ones:

🔹 RCE - LDAP (CVE-2025-26670, CVE-2025-26663), TCP/IP (CVE-2025-26686), Microsoft Office (CVE-2025-29794, CVE-2025-29793), RDS (CVE-2025-27480, CVE-2025-27482), Hyper-V (CVE-2025-27491)
🔹 SFB - Kerberos (CVE-2025-29809)

🗒 Full Vulristics report

На русском

About Elevation of Privilege - Windows Cloud Files Mini Filter Driver (CVE-2024-30085) vulnerability

About Elevation of Privilege - Windows Cloud Files Mini Filter Driver (CVE-2024-30085) vulnerability

About Elevation of Privilege - Windows Cloud Files Mini Filter Driver (CVE-2024-30085) vulnerability. cldflt.sys is a Windows Cloud Files Mini Filter driver responsible for representing cloud-stored files and folders as if they were located on the local machine. The vulnerability in this driver, fixed as part of the June 2024 Microsoft Patch Tuesday, allows an attacker to gain SYSTEM privileges. The root cause of the vulnerability is a Heap-based Buffer Overflow (CWE-122).

🔻 A private exploit was presented at the TyphoonPWN 2024 competition on May 30, 2024. It was used as part of an exploit chain to achieve a VMware Workstation Guest-to-Host escape.

🔻 On December 19, 2024, a technical write-up and exploit code were published on the SSD Secure Disclosure website.

🔻 On March 3, a blog post by Positive Technologies was published that examines the roots of the vulnerability and exploitation techniques.

На русском

About Spoofing - Windows File Explorer (CVE-2025-24071) vulnerability

About Spoofing - Windows File Explorer (CVE-2025-24071) vulnerability

About Spoofing - Windows File Explorer (CVE-2025-24071) vulnerability. The vulnerability is from the March Microsoft Patch Tuesday. The VM vendors didn't highlight it in their reviews. A week later, on March 18, researcher 0x6rss published a write-up and a PoC exploit. According to him, the vulnerability is exploited in the wild, and the exploit has likely been available for purchase since November 2024.

The point is this. When Windows File Explorer detects a .library-ms file in a folder, it automatically starts parsing it. If the file contains a link to a remote SMB share, an NTLM authentication handshake begins. An attacker controlling the SMB share can intercept the NTLMv2 hash, crack it, or use it in pass-the-hash attacks.

But how does an attacker deliver such a file to the victim? It turns out that just extracting a ZIP/RAR archive with the file is enough to trigger the exploit. No need to open the file.

This is super effective for phishing. 😱

На русском

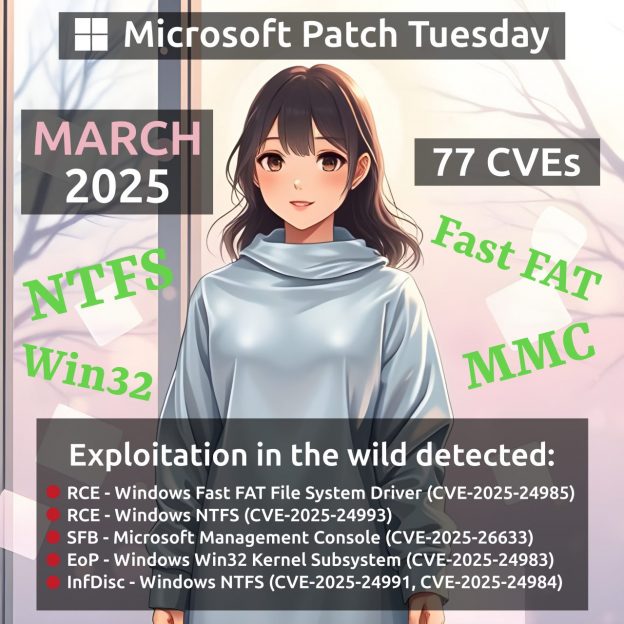
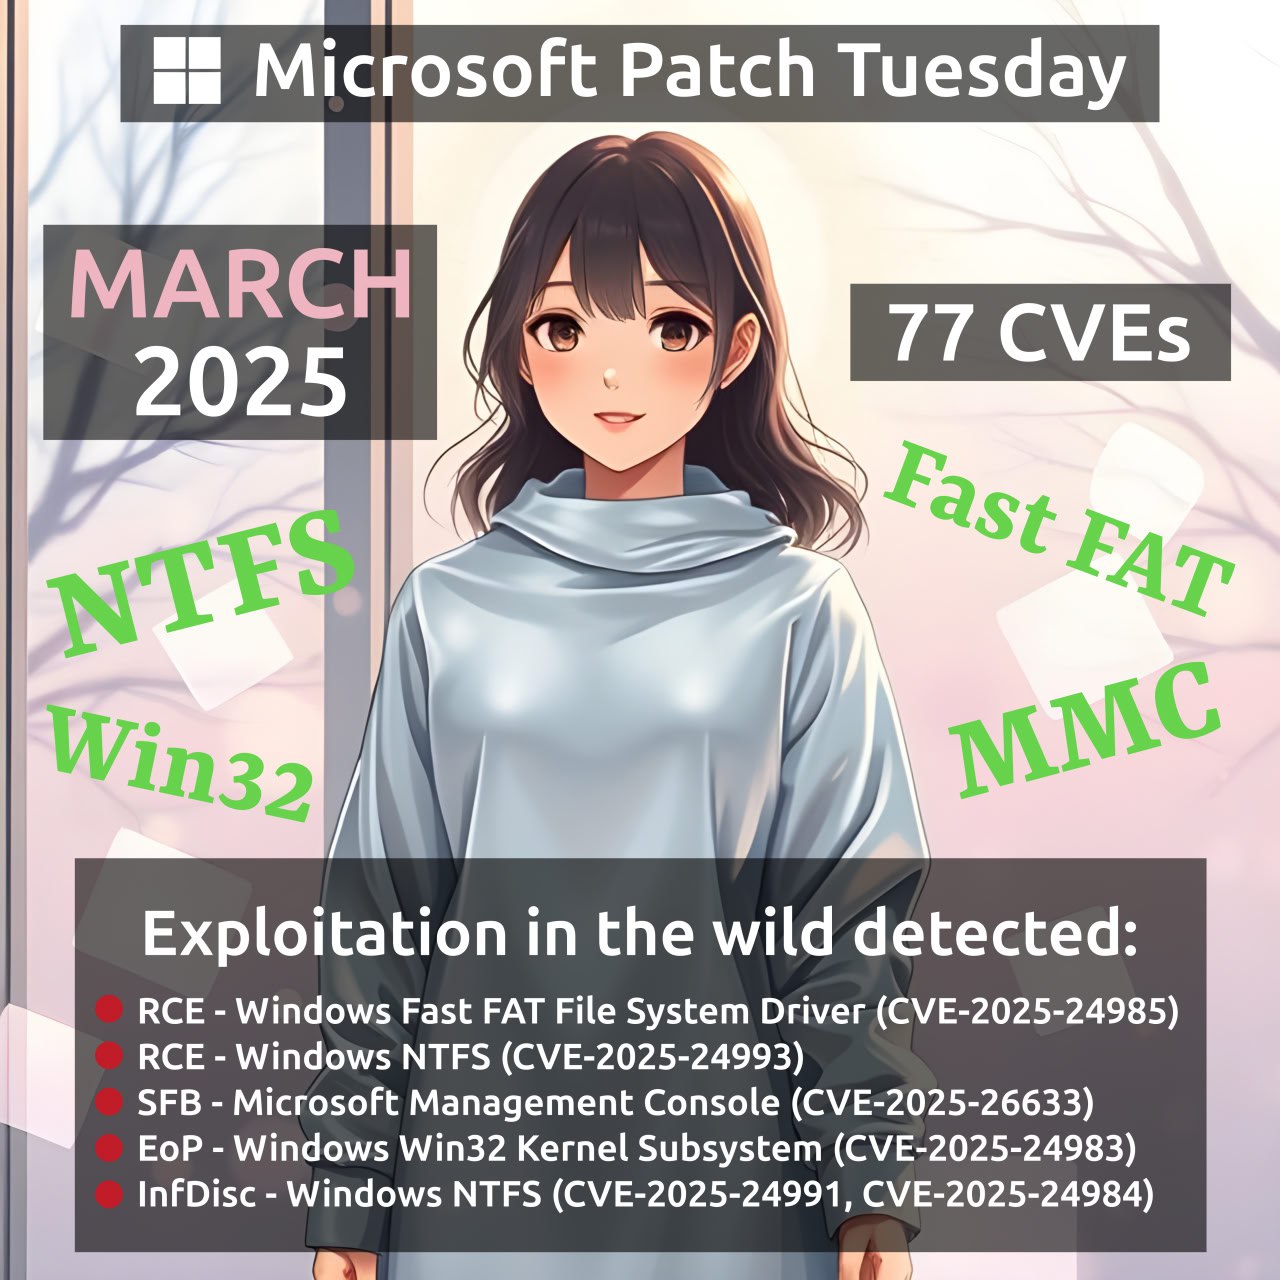
March Microsoft Patch Tuesday

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday. 77 CVEs, 20 of which were added during the month. 7 vulnerabilities with signs of exploitation in the wild:

🔻 RCE - Windows Fast FAT File System Driver (CVE-2025-24985)
🔻 RCE - Windows NTFS (CVE-2025-24993)
🔻 SFB - Microsoft Management Console (CVE-2025-26633)
🔻 EoP - Windows Win32 Kernel Subsystem (CVE-2025-24983)
🔻 InfDisc - Windows NTFS (CVE-2025-24991, CVE-2025-24984)
🔻 AuthBypass - Power Pages (CVE-2025-24989) - in Microsoft web service, can be ignored

There are no vulnerabilities with public exploits, there are 2 more with private ones:

🔸 RCE - Bing (CVE-2025-21355) - in Microsoft web service, can be ignored
🔸 SFB - Windows Kernel (CVE-2025-21247)

Among the others:

🔹 RCE - Windows Remote Desktop Client (CVE-2025-26645) and Services (CVE-2025-24035, CVE-2025-24045), MS Office (CVE-2025-26630), WSL2 (CVE-2025-24084)
🔹 EoP - Windows Win32 Kernel Subsystem (CVE-2025-24044)

🗒 Full Vulristics report

На русском

New episode "In the Trend of VM" (#12): 8 February CVEs & Why the Darknet Matters for VM Specialists

New episode "In the Trend of VM" (#12): 8 February CVEs & Why the Darknet Matters for VM Specialists. Now with a new design and new video editing. 😉

📹 Video on YouTube and LinkedIn
🗞 Post on Habr (rus)
🗒 Digest on the PT website

Content:

🔻 00:00 Greetings
🔻 00:23 Remote Code Execution - Windows Lightweight Directory Access Protocol (LDAP) (CVE-2024-49112)
🔻 01:35 Remote Code Execution - Microsoft Configuration Manager (CVE-2024-43468)
🔻 02:38 Remote Code Execution - Windows OLE (CVE-2025-21298)
🔻 03:55 Elevation of Privilege - Windows Hyper-V NT Kernel Integration VSP (CVE-2025-21333, CVE-2025-21334, CVE-2025-21335)
🔻 05:02 Authentication Bypass – FortiOS/FortiProxy (CVE-2024-55591)
🔻 06:16 Remote Code Execution - 7-Zip (CVE-2025-0411)
🔻 07:27 Should a VM specialist be aware of what is happening in the Darknet?
🔻 08:48 About the digest of trending vulnerabilities
На русском

New episode "In The Trend of VM" (#11): vulnerabilities that became trending in December and the final report on trending vulnerabilities for 2024

New episode "In The Trend of VM" (#11): vulnerabilities that became trending in December and the final report on trending vulnerabilities for 2024. I made this episode exclusively for the Telegram channel @avleonovcom "Vulnerability Management and More". 😉

📹 Video on YouTube, LinkedIn
🗞 Post on Habr (rus)
🗒 Digest on the PT website

Content:

🔻 00:00 Greetings
🔻 00:28 Elevation of Privilege - Windows Kernel Streaming WOW Thunk Service Driver (CVE-2024-38144)
🔻 01:30 Elevation of Privilege - Windows Common Log File System Driver (CVE-2024-49138)
🔻 02:37 Remote Code Execution - Apache Struts (CVE-2024-53677)
🔻 03:31 Authentication Bypass - Hunk Companion WordPress plugin (CVE-2024-11972)
🔻 04:44 Trending vulnerabilities for 2024

👾 08:10 Channel mascot 😅

На русском