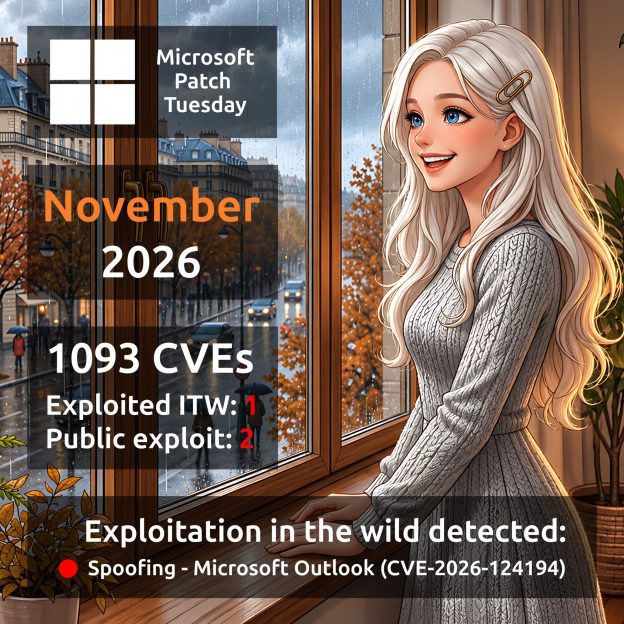
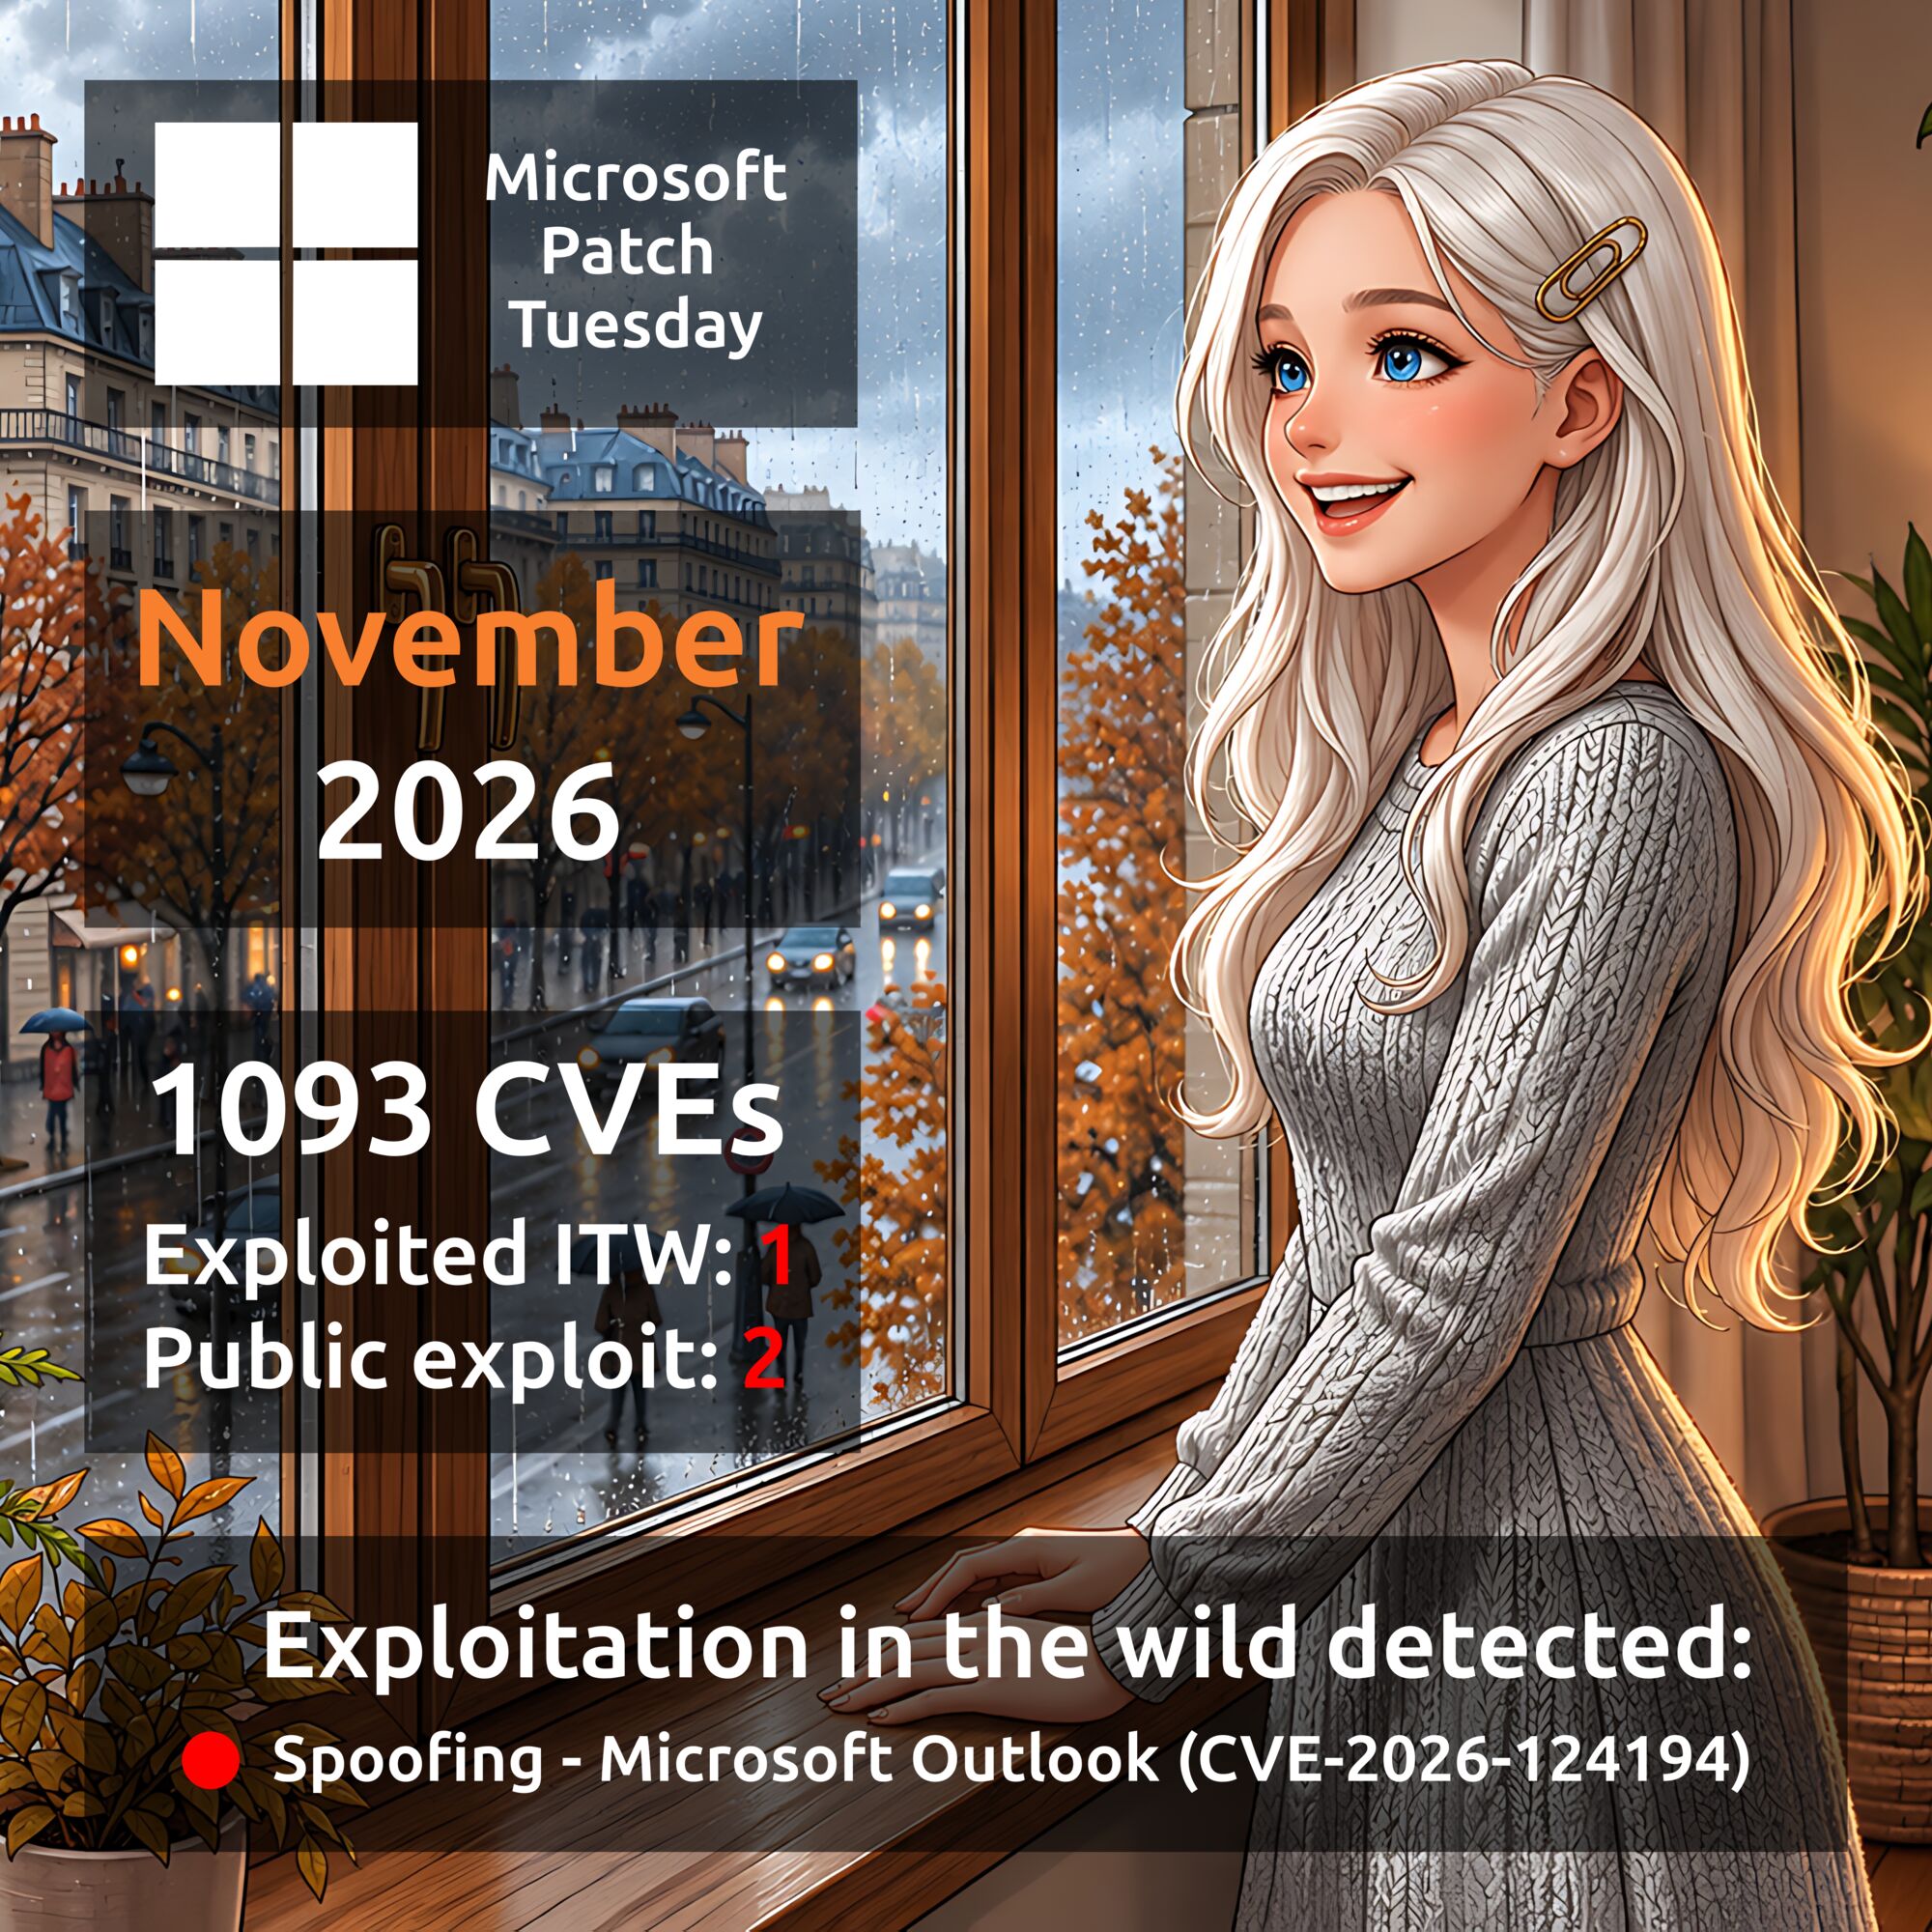
November Microsoft Patch Tuesday. A total of 1,093 vulnerabilities. For comparison, there were 1,409 in October, a decrease of 22.4%. Ten products had 20 or more vulnerabilities fixed: Microsoft Office Excel (64), Microsoft Office Word (61), Microsoft SQL Server (50), Windows Advanced Rasterization Platform (37), Windows Installer (36), Windows Graphics Kernel (35), Windows Kernel (28), Microsoft Office SharePoint (26), Windows DNS (21), Windows Print Spooler Components (20). Together, these products had 378 vulnerabilities fixed, or slightly more than one-third (34.6%) of the total. One vulnerability is flagged as having been exploited in the wild:
🔻 Spoofing - Microsoft Outlook (CVE-2026-124194). Microsoft Outlook is a Microsoft application for managing email, calendars, scheduling meetings, organizing contacts, and setting reminders. An attacker sends a specially crafted message file and convinces a user to open it. Outlook then connects to an attacker-controlled network location without showing the usual external-content warning, which discloses the user’s NTLMv2 hash. The attacker can use that hash to authenticate as the user. The Preview Pane is not an attack vector. A public exploit for the vulnerability is available on GitHub.
There are two vulnerabilities with public exploits, but no evidence of exploitation in the wild has been observed so far.
🔸 EoP - Microsoft Windows App Store (CVE-2026-119987). Microsoft Store (Windows App Store) is Microsoft's official app store for finding, downloading, and installing applications, games, and other digital content on Windows devices. Untrusted search path in Microsoft Windows App Store allows an authorized attacker to elevate privileges locally. A PoC was published on GitHub but later removed. A copy is available on Vulners.
🔸 EoP - Windows AppX Deployment Service (CVE-2026-116714). Windows AppX Deployment Service is a Windows system service responsible for installing, updating, and removing applications. An attacker who successfully exploited this vulnerability could gain SYSTEM privileges.
Other notable vulnerabilities include:
🔹 RCE - Windows LDAP (CVE-2026-119958). Windows LDAP is a service and protocol used to search and manage information about users, computers, and other resources in an enterprise network. An out-of-bounds write vulnerability allows an unauthorized attacker to execute arbitrary code by sending specially crafted LDAP requests over the network.
🔹 RCE - Windows Search / Exchange Server (CVE-2026-116928). An unauthenticated attacker could exploit the Windows Search component used by Microsoft Exchange Server (Microsoft's server platform for managing enterprise email, calendars, contacts, and shared meeting scheduling) by sending an email containing a specially crafted attachment. Exchange automatically processes the attachment for indexing, so the recipient does not need to open the email or attachment. Successful exploitation could allow the attacker to execute code with the permissions of the affected processing service.
🔹 RCE - Microsoft Exchange (CVE-2026-118207). An authenticated attacker with low-level access to an affected server could send a specially crafted request to execute code on the server. User interaction is not required.
🔹 RCE - Windows Active Directory Domain Services (CVE-2026-118146). Windows Active Directory Domain Services is a Windows service for centrally managing users, computers, and access to enterprise network resources. An authenticated attacker with low-level access to an affected server could send a specially crafted request to execute code on the server. User interaction is not required.
🔹 RCE - Windows Virtual Filtering Platform (VFP) (CVE-2026-95962). Windows Virtual Filtering Platform (VFP) is a Windows system component responsible for processing and filtering network traffic. Use after free bug allows an unauthorized attacker to execute code by sending a specially crafted packet to the affected service over the network.
🔹 RCE - Windows Schannel (CVE-2026-119952). Windows Schannel is a Windows system component that provides secure network connections and encryption of transmitted data. An unauthenticated attacker could exploit this vulnerability by sending a specially crafted packet to an affected service over the network. Successful exploitation could allow the attacker to execute code on the target system. No authentication or user interaction is required.
🔹 EoP - Microsoft SharePoint Server (CVE-2026-120002). Microsoft SharePoint Server is Microsoft's enterprise platform for creating intranet portals, storing and collaborating on documents, sharing information, and managing business workflows within an organization. An authenticated attacker with site read access and membership in the relevant SharePoint Secure Store target application could send a specially crafted network request to an affected SharePoint server. Successful exploitation could cause SharePoint to perform unauthorized actions on a connected business service using shared credentials. No additional user interaction is required.