Tag Archives: Microsoft

About Remote Code Execution - Microsoft Office (CVE-2026-21509) vulnerability

About Remote Code Execution - Microsoft Office (CVE-2026-21509) vulnerability

About Remote Code Execution - Microsoft Office (CVE-2026-21509) vulnerability. The vulnerability was urgently fixed on January 26, outside the regular Microsoft Patch Tuesday. Microsoft classified it as a Security Feature Bypass, but in fact, it is more of a Remote Code Execution. The vulnerability involves bypassing OLE (Object Linking and Embedding) security features in Microsoft 365 and Microsoft Office. It is exploited when opening malicious Office files (Preview Pane is safe).

⚙️ In Office 2021+, protection is enabled automatically via server-side changes after restarting the applications. For Office 2016/2019, updates must be installed or registry changes applied.

👾 Microsoft reports that the vulnerability is being exploited in the wild.

🛠 No public exploits are available yet.
На русском

January "In the Trend of VM" (#23): vulnerabilities in Windows, React and MongoDB

January In the Trend of VM (#23): vulnerabilities in Windows, React and MongoDB

January "In the Trend of VM" (#23): vulnerabilities in Windows, React and MongoDB. Traditional monthly roundup of trending vulnerabilities. Launching the 2026 season. 🙂

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

In total, three vulnerabilities:

🔻 EoP - Windows Cloud Files Mini Filter Driver (CVE-2025-62221)
🔻 RCE - React Server Components "React2Shell" (CVE-2025-55182)
🔻 InfDisc - MongoDB "MongoBleed" (CVE-2025-14847)

🟥 Trending Vulnerabilities Portal

На русском

About Information Disclosure - Desktop Window Manager (CVE-2026-20805) vulnerability

About Information Disclosure - Desktop Window Manager (CVE-2026-20805) vulnerability

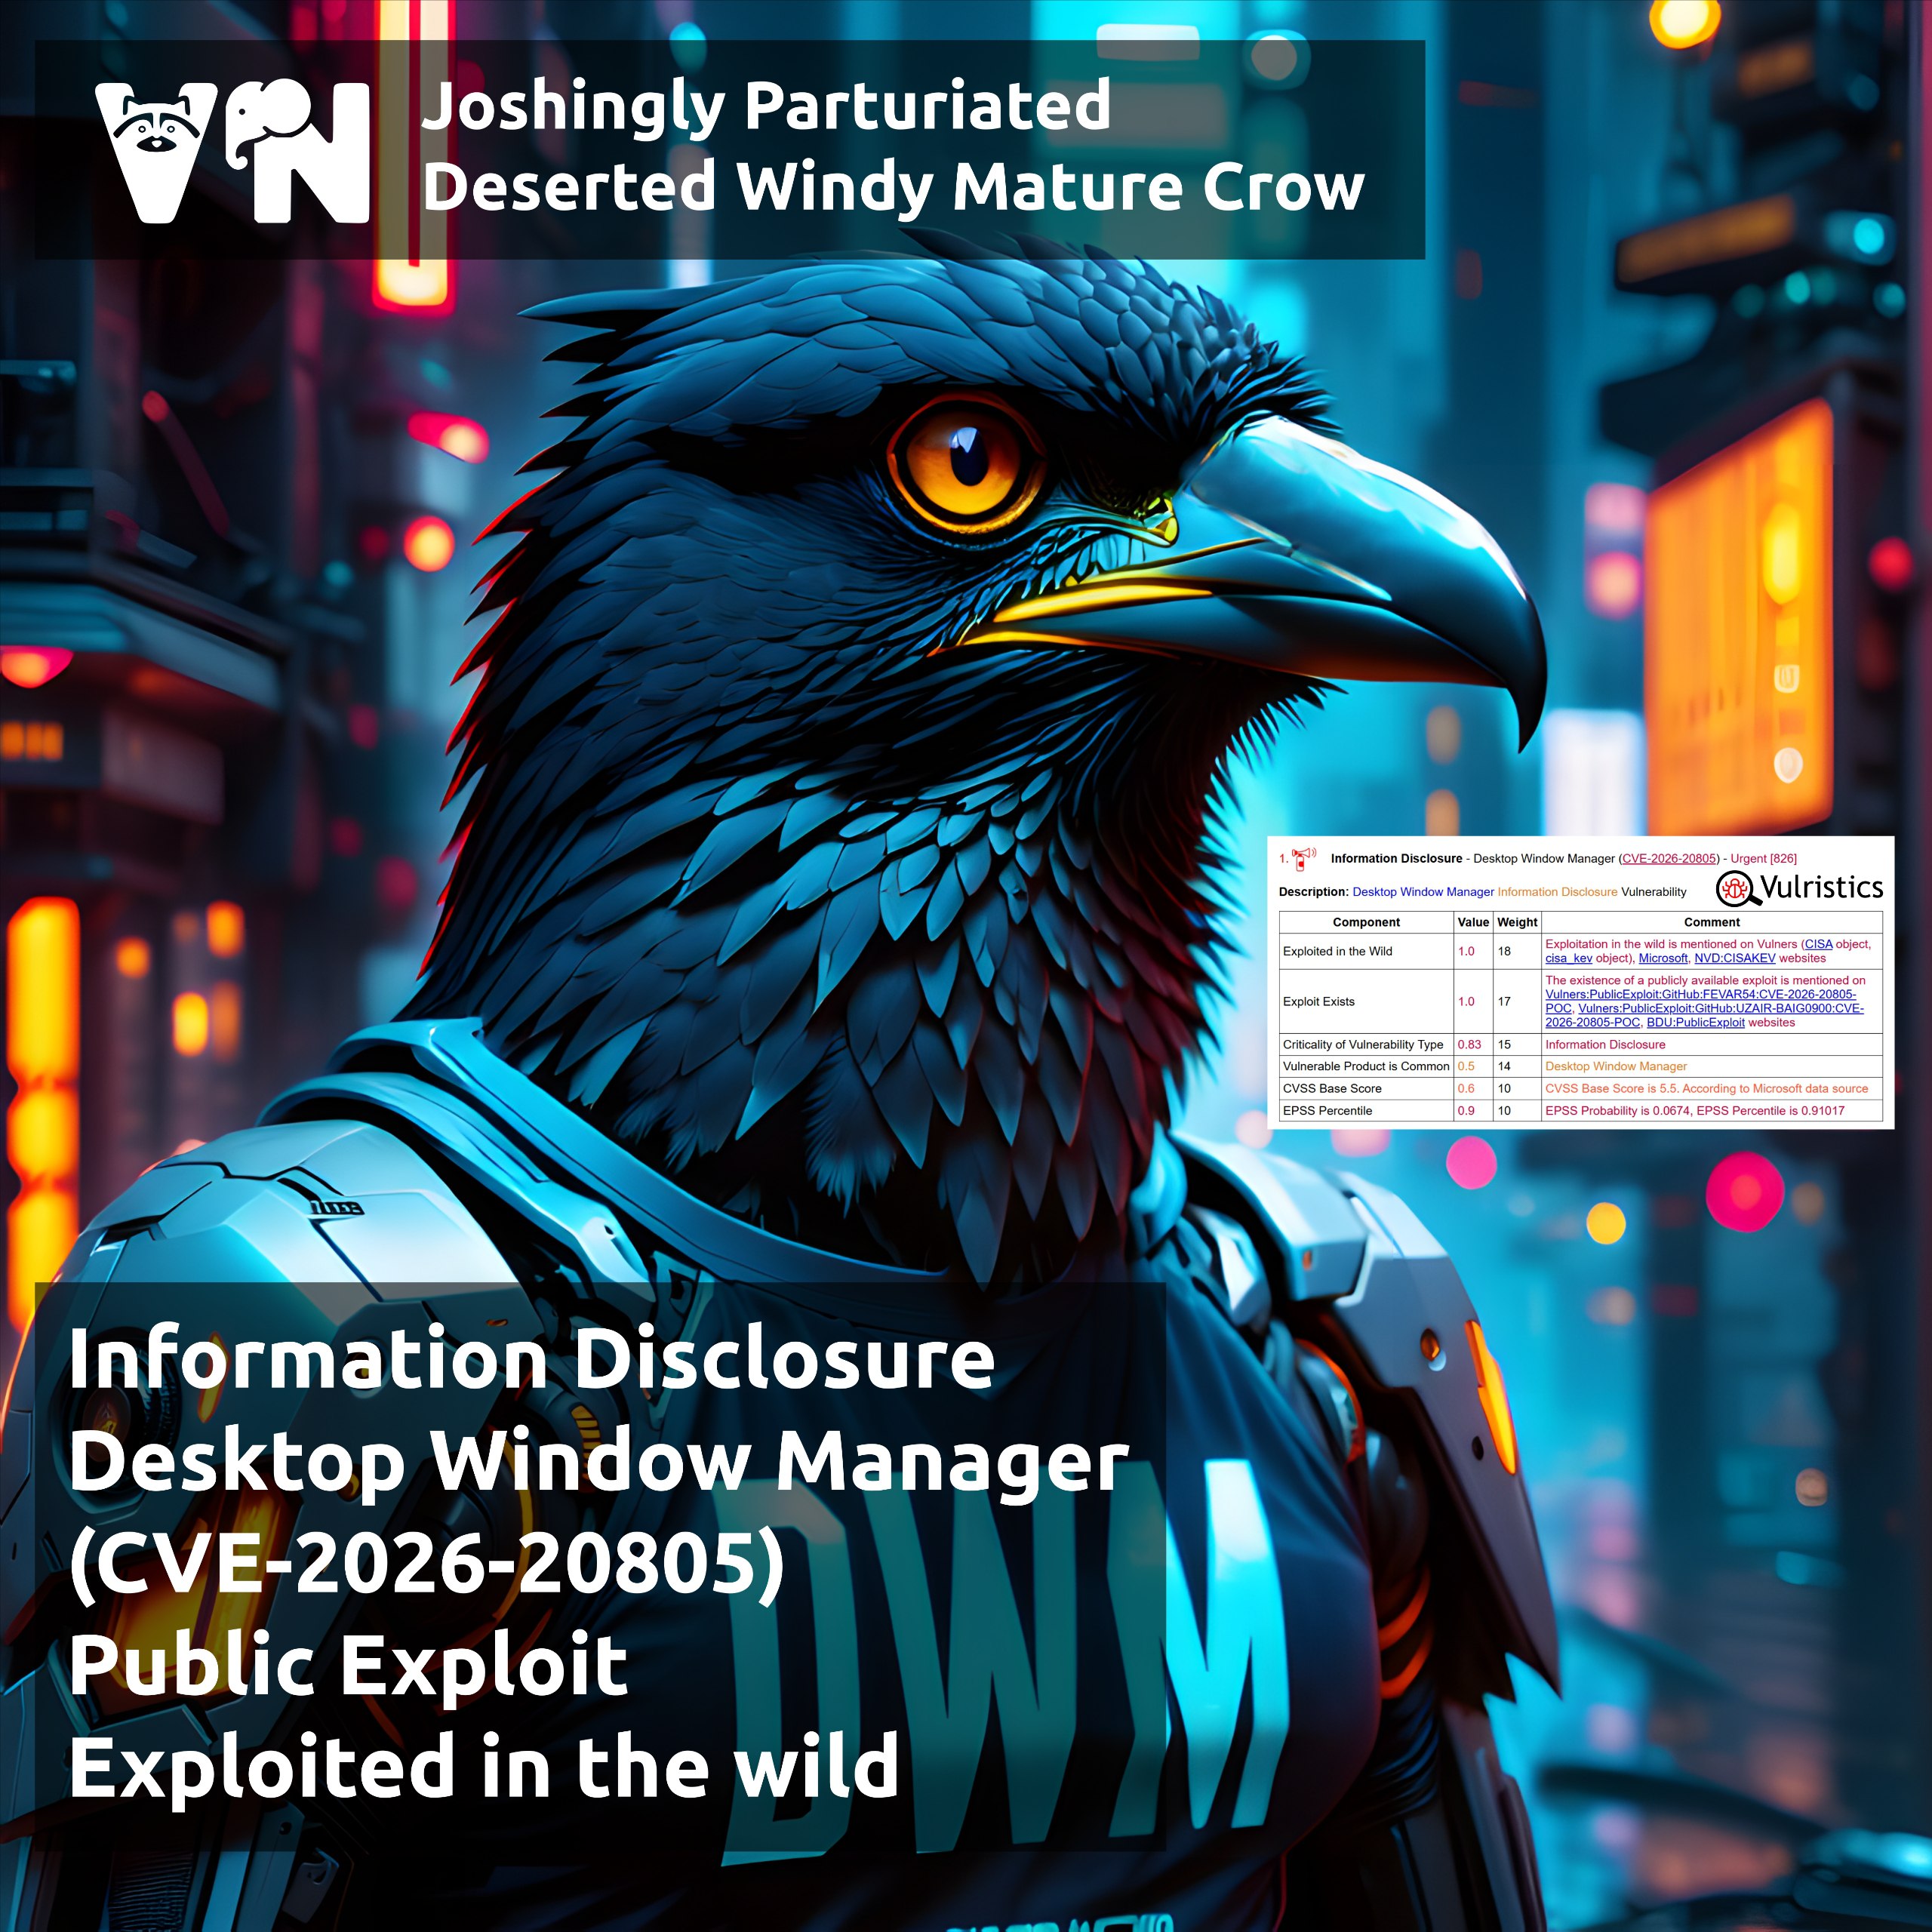
About Information Disclosure - Desktop Window Manager (CVE-2026-20805) vulnerability. Desktop Window Manager is a compositing window manager that has been part of Windows since Windows Vista. Exploitation of the vulnerability, which was addressed in the January Microsoft Patch Tuesday, allows a local attacker to disclose the "section address from a remote ALPC port which is user-mode memory".

👾 Microsoft noted that this vulnerability is being exploited in attacks. The vulnerability was added to CISA’s KEV catalog on January 13. There are no public details about the attacks yet, but Rapid7 experts suggest that the disclosed memory address can be used to bypass ASLR, "increasing the chance of developing a stable elevation of privilege exploit for DWM".

🛠 Public exploit PoCs have been available on GitHub since January 14.

На русском

About Elevation of Privilege - Windows Cloud Files Mini Filter Driver (CVE-2025-62221) vulnerability

About Elevation of Privilege - Windows Cloud Files Mini Filter Driver (CVE-2025-62221) vulnerability

About Elevation of Privilege - Windows Cloud Files Mini Filter Driver (CVE-2025-62221) vulnerability. cldflt.sys is the Windows Cloud Files Mini Filter driver whose purpose is to present files and folders stored in the cloud as if they were located on the local computer. A vulnerability in this driver, fixed as part of Microsoft's December Patch Tuesday, allows a local attacker to obtain SYSTEM privileges. The root cause of the vulnerability is a Use After Free issue (CWE-416).

⚙️ The vulnerability was discovered by Microsoft researchers (from MSTIC and MSRC). Updates are available for Windows 10/11 and Windows Server 2019/2022/2025.

👾 The vulnerability has been exploited in the wild and added to the CISA KEV catalog. No attack details are available yet.

🛠 Since December 10, alleged exploit repositories briefly appeared on GitHub and were later removed; exploit sale offers have also been observed (possibly fraudulent).

На русском

January Microsoft Patch Tuesday

January Microsoft Patch Tuesday

January Microsoft Patch Tuesday. A total of 114 vulnerabilities, twice as many as in December. There is one vulnerability with evidence of in-the-wild exploitation:

🔻 InfDisc - Desktop Window Manager (CVE-2026-20805)

There are also two vulnerabilities with public exploits:

🔸 RCE - Windows Deployment Services (CVE-2026-0386)
🔸 EoP - Windows Agere Soft Modem Driver (CVE-2023-31096)

Other notable vulnerabilities include:

🔹 RCE - Microsoft Office (CVE-2026-20952, CVE-2026-20953), Windows NTFS (CVE-2026-20840, CVE-2026-20922)
🔹 EoP - Desktop Windows Manager (CVE-2026-20871), Windows Virtualization-Based Security (VBS) Enclave (CVE-2026-20876)
🔹 SFB - Secure Boot Certificate Expiration (CVE-2026-21265)

Also noteworthy, reported by Positive Technologies:

🟥 EoP - Windows Telephony Service (CVE-2026-20931)

🗒 Full Vulristics report

На русском

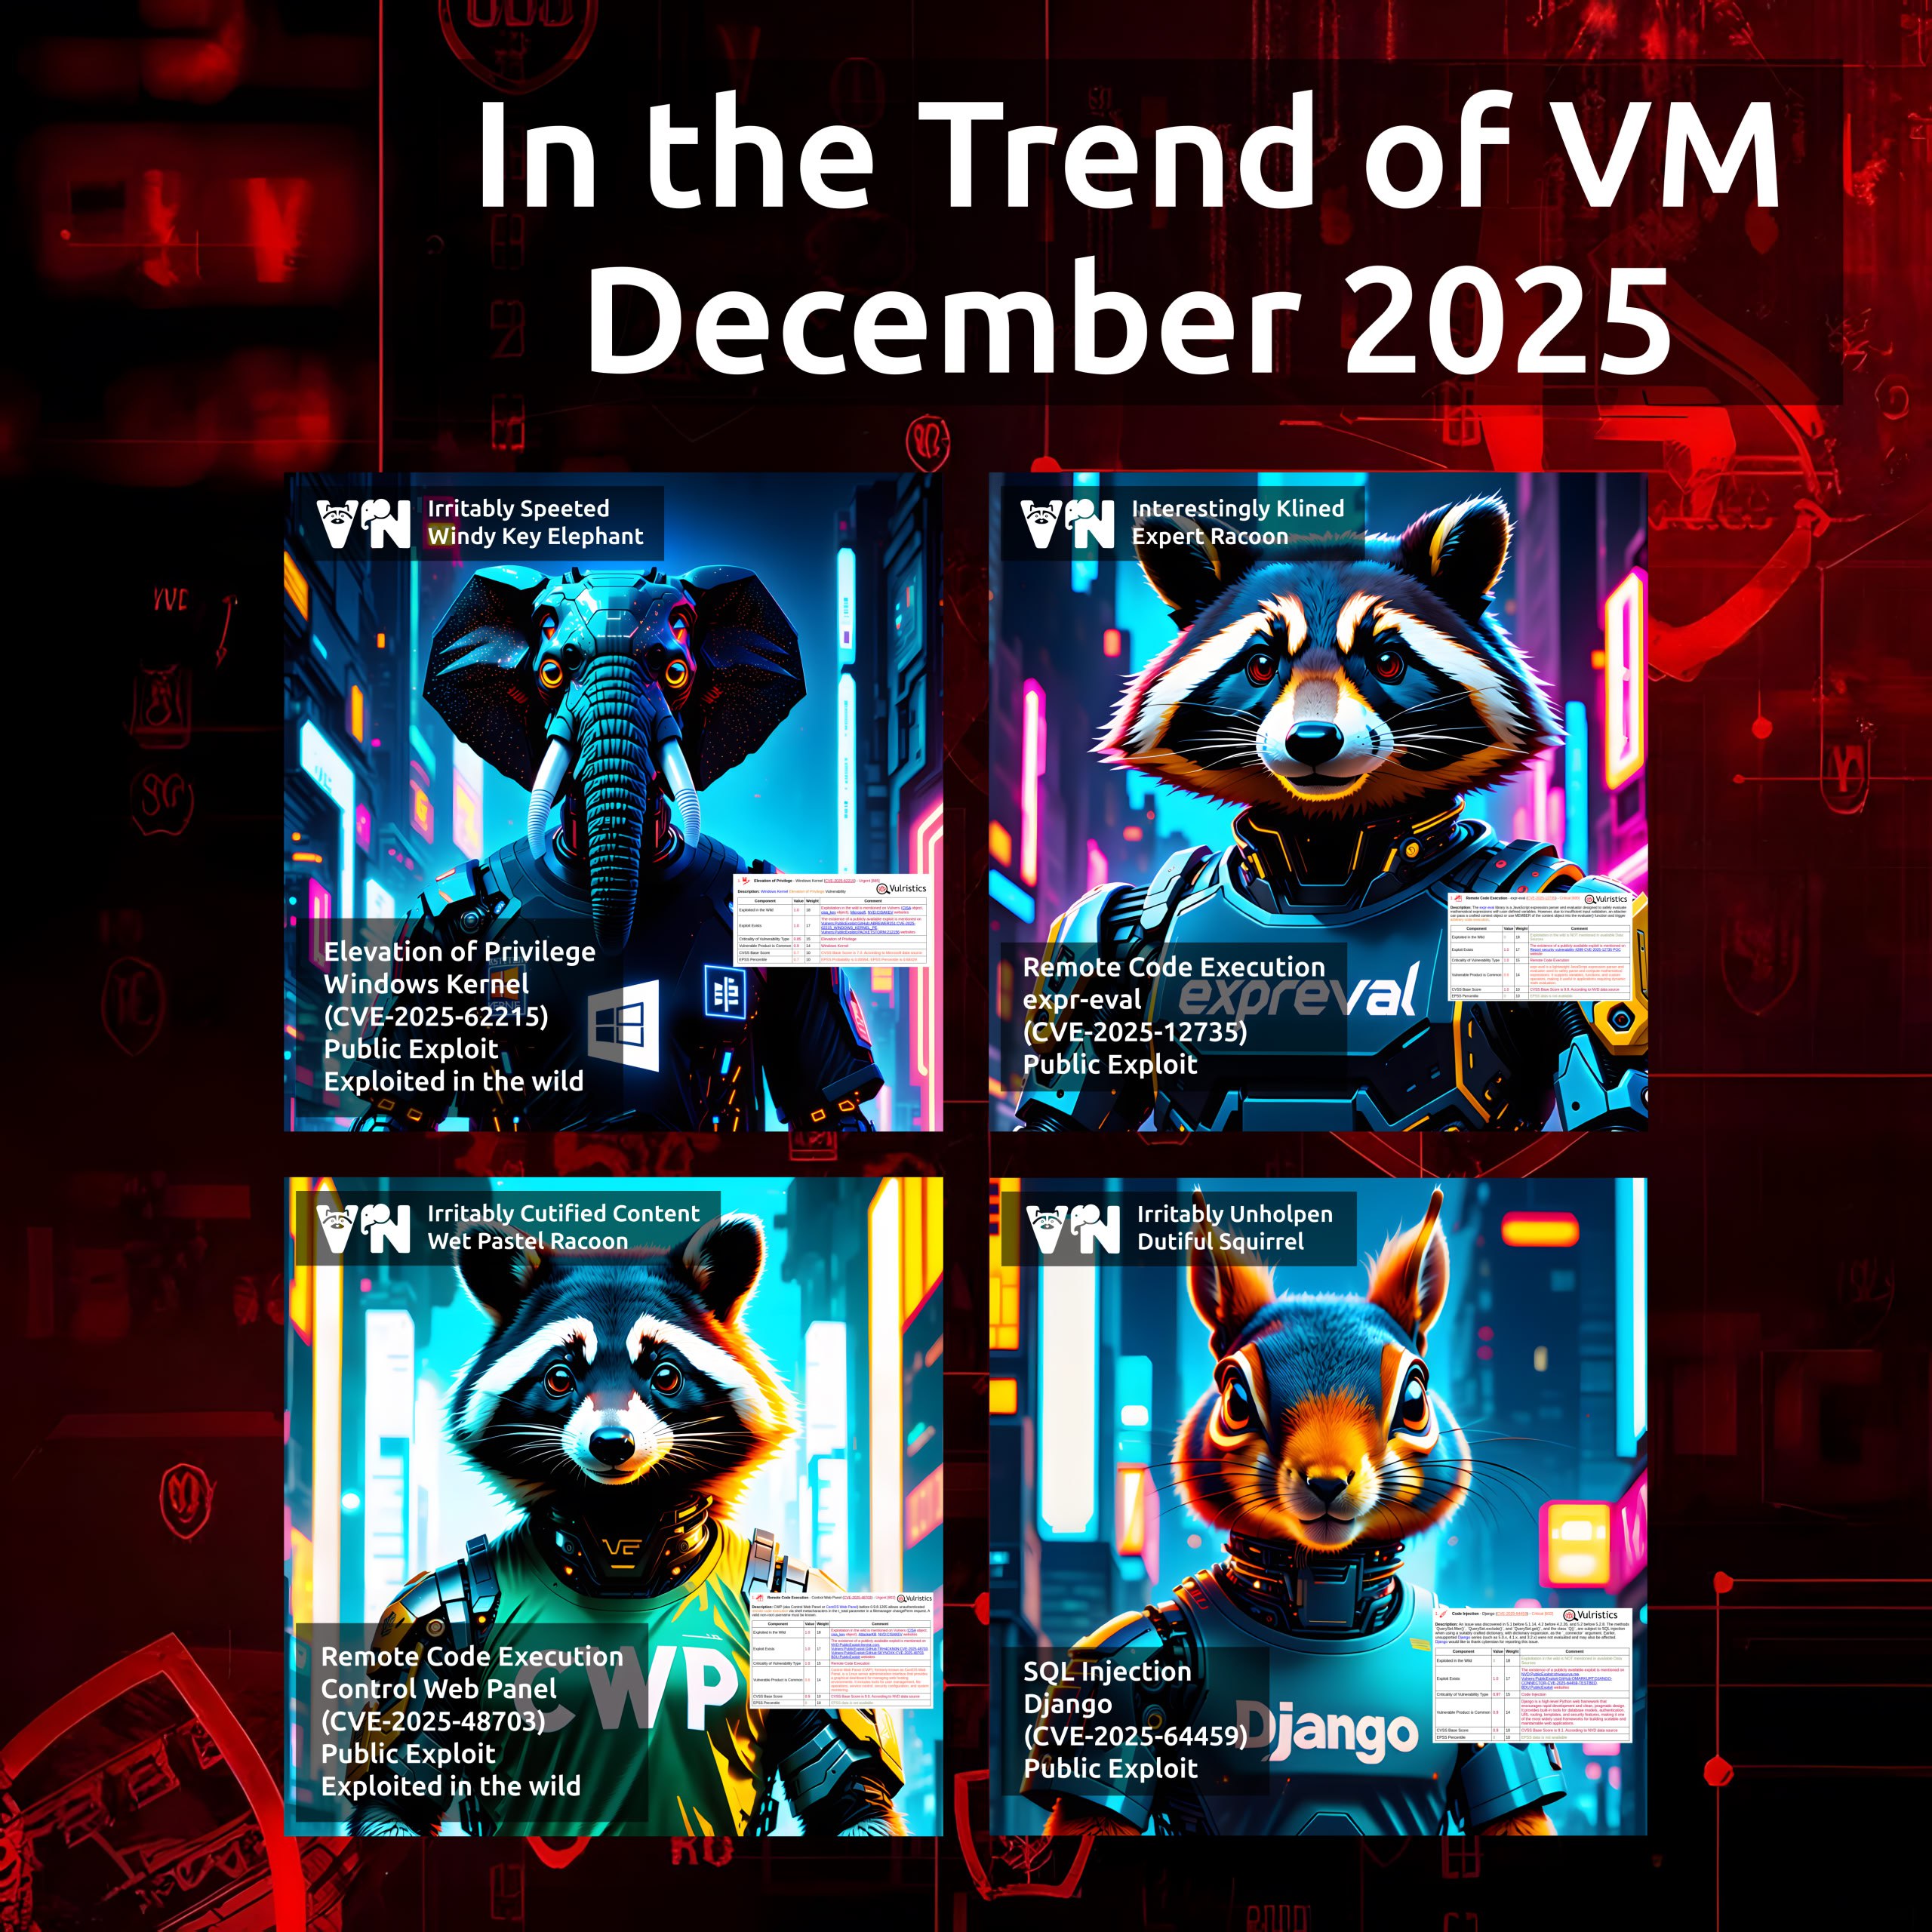
December "In the Trend of VM" (#22): vulnerabilities in Windows, the expr-eval library, Control Web Panel, and Django

December In the Trend of VM (#22): vulnerabilities in Windows, the expr-eval library, Control Web Panel, and Django

December "In the Trend of VM" (#22): vulnerabilities in Windows, the expr-eval library, Control Web Panel, and Django. A traditional monthly roundup of trending vulnerabilities - this time, a fairly compact one. 💽

🗞 Post on Habr (rus)
🗞 Post on SecurityLab (rus)
🗒 Digest on the PT website (rus)

Four vulnerabilities in total:

🔻 EoP - Windows Kernel (CVE-2025-62215)
🔻 RCE - expr-eval (CVE-2025-12735)
🔻 RCE - Control Web Panel (CVE-2025-48703)
🔻 SQLi - Django (CVE-2025-64459)

🟥 Trending Vulnerabilities Portal

На русском

December Microsoft Patch Tuesday

December Microsoft Patch Tuesday

December Microsoft Patch Tuesday. A total of 56 vulnerabilities were fixed - 9 fewer than in November. There is one vulnerability with confirmed in-the-wild exploitation:

🔻 EoP - Windows Cloud Files Mini Filter Driver (CVE-2025-62221)

There are currently no vulnerabilities with publicly available exploits. Among the remaining vulnerabilities, the following stand out:

🔹 RCE - Microsoft Office (CVE-2025-62554, CVE-2025-62557), Microsoft PowerShell (CVE-2025-54100), Microsoft Outlook (CVE-2025-62562), GitHub Copilot for JetBrains (CVE-2025-64671)
🔹 EoP - Windows Win32k (CVE-2025-62458), Windows Cloud Files Mini Filter Driver (CVE-2025-62454, CVE-2025-62457), Windows Common Log File System Driver (CVE-2025-62470), Windows Remote Access Connection Manager (CVE-2025-62472), Windows Storage (CVE-2025-59516)

🗒 Full Vulristics report

На русском