Tag Archives: python

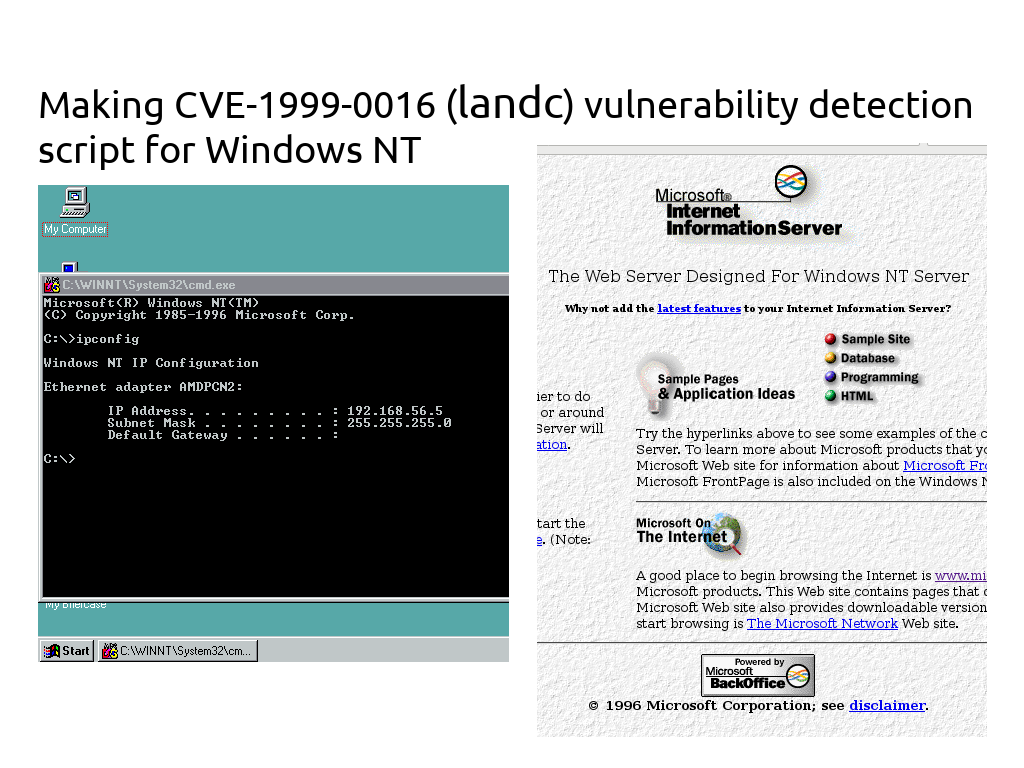
Making CVE-1999-0016 (landc) vulnerability detection script for Windows NT

Making CVE-1999-0016 (landc) vulnerability detection script for Windows NT. The fair question is why in 2018 someone might want to deal with Windows NT and vulnerabilities in it. Now Windows NT is a great analogue of DVWA (Damn Vulnerable Web Application), but for operating systems. There are a lot of well-described vulnerabilities with ready-made exploits. A great tool for practising.

Making CVE-1999-0016 (landc) vulnerability detection script for Windows NT

Well, despite the fact that this operating system is not supported since 2004, it can be used in some weird legacy systems. 😉

Continue reading →

Accelerating Splunk Dashboards with Base Searches and Saved Searches

Accelerating Splunk Dashboards with Base Searches and Saved Searches. Let’s say we have a Splunk dashboard with multiple panels. Each panel has its own search request and all of these requests work independently and simultaneously. If they are complex enough, rendering the dashboard may take quite a long time and some panels may even fall by timeout.

Accelerating Splunk Dashboards

How to avoid this? The first step is to understand how the searches are related. May be it is possible to select some base searches, and reuse their results in other child-searches. It’s also possible to get cached results from the “Saved Searches” (another name of Reports in Splunk GUI).

Continue reading →

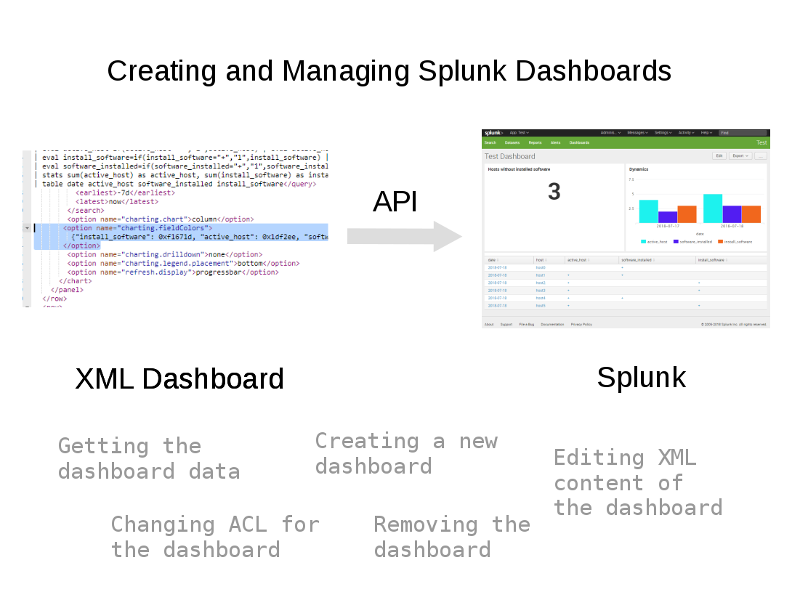
How to create and manage Splunk dashboards via API

How to create and manage Splunk dashboards via API. In the previous post “How to correlate different events in Splunk and make dashboards” I mentioned that Splunk dashboards can be presented in a simple XML form. You can generate it with some script and then copy-past it in Splunk GUI.

Splunk dashboard manage api

However, this manual operations can make the process of debugging dashboards really annoying. It would be much easier to send dashboard XML content to Splunk using Splunk API. And it is actually possible. 🙂

Continue reading →

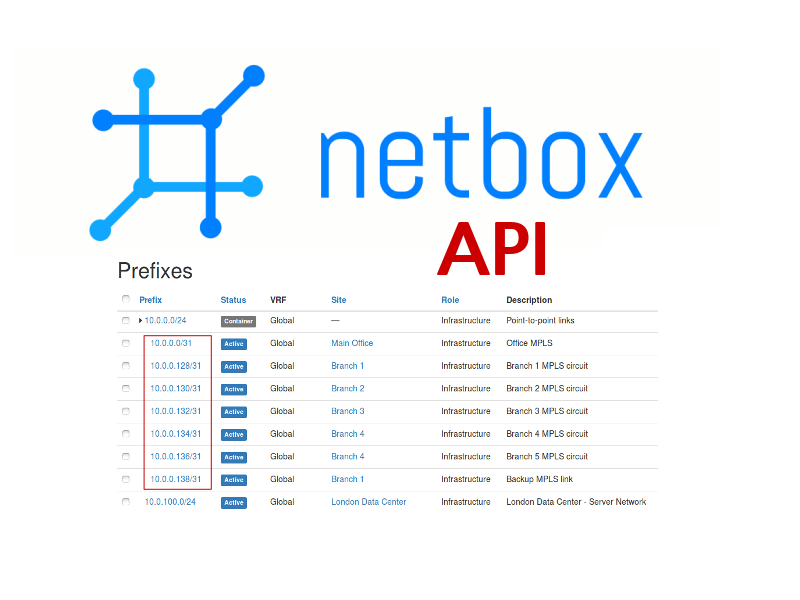
Retrieving IT Asset lists from NetBox via API

Retrieving IT Asset lists from NetBox via API. A little bit more about IT Asset Inventory of Internal Network, that your IT team can provide. 😉

I have recently worked with NetBox – an open source IP address management (IPAM) and data center infrastructure management (DCIM) solution developed by well-known cloud hosting provider DigitalOcean.

NetBox api

It’s not really about security, not even a CMDB. But, security team still might be interested in NetBox, because it makes possible to track the hosts in some critical subnet without active scanning, providing great visibility of assets. Here I will show a small example of NetBox API usage.

Continue reading →

Asset Inventory for Internal Network: problems with Active Scanning and advantages of Splunk

Asset Inventory for Internal Network: problems with Active Scanning and advantages of Splunk. In the previous post, I was writing about Asset Inventory and Vulnerability Scanning on the Network Perimeter. Now it’s time to write about the Internal Network.

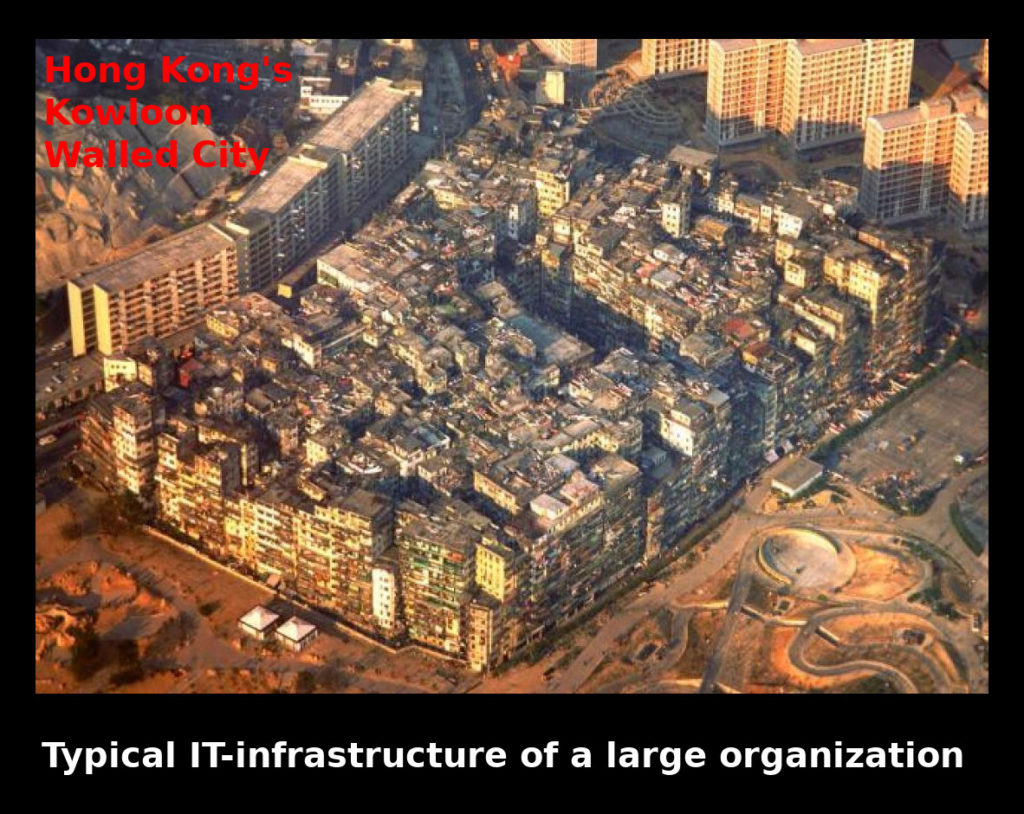
Typical IT-infrastructure of a large organization

I see a typical IT-infrastructure of a large organization as monstrous favela, like Kowloon Walled City in Hong Kong. At the beginning it was probably wisely designed, but for years it  was highly effected by spontaneous development processes in various projects as well as multiple acquisitions. And now very few people in the organization really understand how it all works and who owns each peace.

There is a common belief that we can use Active Network Scanning for Asset Inventory in the organization. Currently, I’m not a big fan of this approach, and I will try to explain here the disadvantages of this method and mention some alternatives.

Continue reading →

Asset Inventory for Network Perimeter: from Declarations to Active Scanning

Asset Inventory for Network Perimeter: from Declarations to Active Scanning. In the previous post, I shared some of my thoughts about the good Asset Inventory system. Of course, for me as a Security Specialist, it would be great if IT will provide such magical system. 🙂 But such an ideal situation is rarely possible. So now let’s see how to build an Asset Inventory system using the resources of Information Security team.

There are no special secrets. It’s necessary to get information about the assets from all available IT systems and then get the rest of the data using our own Assessment tools. I would like to start with hosts on Network Perimeter. The Network Perimeter targets are available at any time for hacker attacks, that’s why this part of the network is the most critical.
Asset Inventory for Network Perimeter

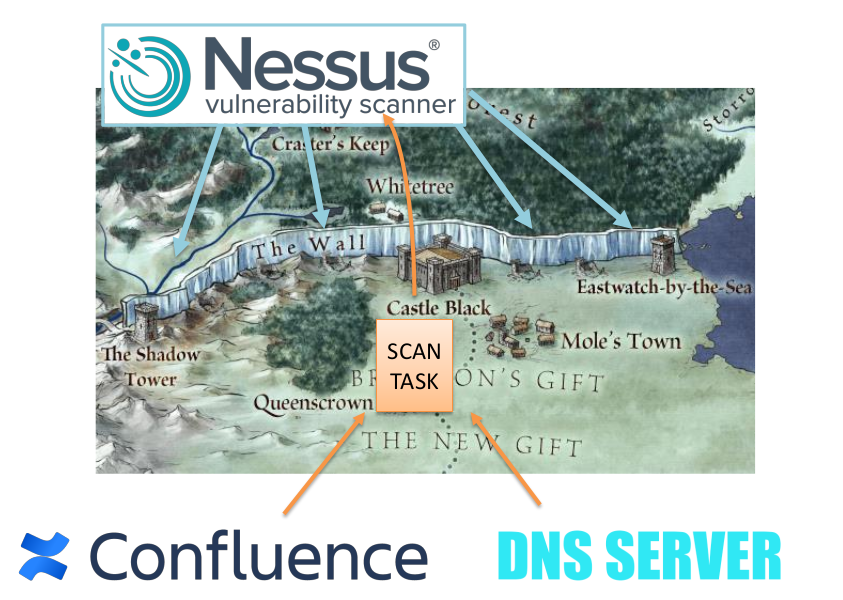
Network Perimeter is like the Wall in the Game of Thrones. The same white walkers are hiding behind the wall and our task is to find the breaches in the wall faster than potential intruders. “Night gathers, and now my watch begins”. (c)

Perimeter is changing constantly. And we should understand at any time what hosts are currently exposed in every office and every external hosting platform.

We can get information about external hosts using some Vulnerability Scanner located on external host in the Internet. I have already wrote about it briefly in  Vulnerability Management for Network Perimeter. Here I would like focus on how we can understand which hosts should be scanned and what useful information we can get from the raw scan results.

Continue reading →
Sending tables from Atlassian Confluence to Splunk

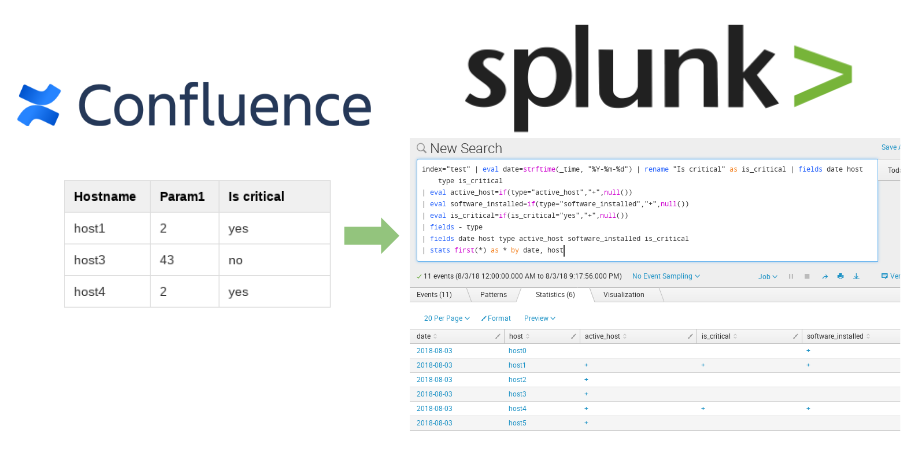
Sending tables from Atlassian Confluence to Splunk. Sometimes when we make automated analysis with Splunk, it might be necessary to use information that was entered or edited manually. For example, the classification of network hosts: do they belong to the PCI-DSS Scope or another group critical hosts or not.

Sending tables from Atlassian Confluence to Splunk

In this case, Confluence can be quite a convenient tool for maintaining such a registry. Page with a table can be created very quickly and multiple employees can immediately start working with it.

Let’s see how to convert such table, export it to Splunk and use it with other data.

Continue reading →