Tag Archives: CISAKEV

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May In the Trend of VM (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader

May "In the Trend of VM" (#27): high-profile vulnerabilities in Linux, ActiveMQ, SharePoint, and Adobe Acrobat Reader. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. While the previous April edition featured only one vulnerability, this one includes four, covering different technologies and attack scenarios.

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

🔻 EoP - Linux Kernel "Copy Fail" (CVE-2026-31431). The vulnerability allows an attacker to gain root privileges.

🔻 RCE - Apache ActiveMQ (CVE-2026-34197). A vulnerability in a solution widely used in enterprise systems and integration platforms.

🔻 Spoofing - Microsoft SharePoint Server (CVE-2026-32201). A vulnerability in a Microsoft solution widely used in enterprise systems for collaboration, document management, and internal portal development.

🔻 RCE - Adobe Reader (CVE-2026-34621). A vulnerability in a widely used PDF document viewer; actively exploited in phishing attacks.

🟥 The full list of trending vulnerabilities is available on the portal

About Remote Code Execution - Apache ActiveMQ (CVE-2026-34197) vulnerability

About Remote Code Execution - Apache ActiveMQ (CVE-2026-34197) vulnerability

About Remote Code Execution - Apache ActiveMQ (CVE-2026-34197) vulnerability. Apache ActiveMQ is a popular open-source message broker written in Java. Its main purpose is to send messages between different services, systems, and microservices without a direct connection between them.

This vulnerability is from the April Linux Patch Wednesday. Details about this vulnerability were published on April 7 in the HORIZON3.ai company blog. They claim that the Apache ActiveMQ Classic vulnerability has been hiding in plain sight for 13 years. An attacker can invoke a management operation through ActiveMQ's Jolokia API to trick the broker into fetching a remote configuration file and running arbitrary OS commands. As a result, the attacker can gain access to sensitive information, including messages, credentials, and configuration files, deploy malware, or use the compromised server to conduct further attacks within the internal infrastructure.

The vulnerability requires credentials, but default credentials (admin:admin) are common in many environments. On some versions (6.0.0–6.1.1), no credentials are required at all due to another vulnerability, CVE-2024-32114, which inadvertently exposes the Jolokia API without authentication. In those versions, CVE-2026-34197 is effectively an unauthenticated RCE.

🛠 Public exploits have been available on GitHub since April 8.

👾 Indicators of exploitation in the wild were observed by FortiGuard experts on April 13. The vulnerability was added to the CISA KEV catalog on April 16.

🌐 According to data from The Shadowserver Foundation, as of May 14, approximately 7,000 vulnerable Apache ActiveMQ servers remain exposed on the internet.

⚙️ According to the vendor bulletin, the vulnerability has been fixed in ActiveMQ versions 5.19.4 and 6.2.3. However, according to HORIZON3.ai, it was fixed in 5.19.6 and 6.2.5. It is better to install newer versions. 😉

Про уязвимость Spoofing - Microsoft SharePoint Server (CVE-2026-32201)

Про уязвимость Spoofing - Microsoft SharePoint Server (CVE-2026-32201)

About Spoofing - Microsoft SharePoint Server (CVE-2026-32201) vulnerability. A vulnerability from the April Microsoft Patch Tuesday. The description provided by Microsoft experts is extremely vague: "Improper input validation in Microsoft Office SharePoint allows an unauthorized attacker to perform spoofing over a network. An attacker who successfully exploited the vulnerability could view some sensitive information (Confidentiality), make changes to disclosed information (Integrity), but cannot limit access to the resource (Availability)." Spoofing is an attack in which a threat actor forges data, an address, an identifier, or a trusted source in order to impersonate a legitimate user, service, or system.

What is actually hidden behind this description? In the April review on MSPT, a ZDI expert noted that vulnerabilities of this kind in SharePoint are often associated with XSS attacks.

🛠 On April 23, an exploit was published on GitHub, whose author claims that the vulnerability can be summarized as follows: "An unauthenticated attacker can send a specially crafted HTTP request to inject malicious JavaScript (reflected XSS), which executes in the security context of the SharePoint site."

In other words, the attacker sends a specially crafted request to the SharePoint server, causing SharePoint to generate a malicious link on behalf of a trusted source. The attacker then passes this link to the user. When the user opens such a link, the injected malicious JavaScript executes in the context of SharePoint, which can be used to steal data from the current session, intercept authentication tokens, as well as perform actions on behalf of the user through the user's active session.

👾 Microsoft experts noted the vulnerability as being exploited in the wild on the day of publication of the April Microsoft Patch Tuesday, April 14. The vulnerability was added to the CISA KEV. On the same day, researchers from Defused reported coordinated reconnaissance activity targeting vulnerable SharePoint servers, which was carried out from four IP addresses between April 1 and April 11.

⚙️ Updates are available for Microsoft SharePoint Server 2016, 2019, and Subscription Edition.

About Elevation of Privilege - Linux Kernel "Copy Fail" (CVE-2026-31431) vulnerability

About Elevation of Privilege - Linux Kernel Copy Fail (CVE-2026-31431) vulnerability

About Elevation of Privilege - Linux Kernel "Copy Fail" (CVE-2026-31431) vulnerability. A local privilege escalation vulnerability in the Linux kernel AF_ALG component, which is caused by a memory handling flaw, allows an unprivileged user to escalate privileges to root. By exploiting this vulnerability, an attacker can fully compromise the system: read and modify any files, including passwords and keys, replace system binaries, disable security controls and monitoring tools, stealthily install backdoors and maintain persistence, hide traces of their activity, and use the host as a foothold for attacks on other network assets.

⚙️🛠 On April 1, patches addressing the vulnerability were merged into the main branch of the Linux kernel. On April 22, a CVE identifier was assigned to the vulnerability. On April 29, experts from Theori published an analysis of the vulnerability and a public exploit. The vulnerability's exploitability has been confirmed on up-to-date versions of widely used Linux distributions, including Ubuntu, Amazon Linux, RHEL, and SUSE.

👾 On May 1, the vulnerability was added to the CISA KEV catalog, indicating it is being exploited in the wild.

What distinguishes this vulnerability from similar EOP/LPE issues in Linux?

There have been high-profile privilege escalation vulnerabilities in the Linux kernel. Dirty COW required winning a race condition. Multiple attempts were often needed, and this sometimes led to system crashes. Dirty Pipe was tied to specific versions and required precise pipe buffer manipulation.

But unlike Dirty COW and Dirty Pipe, researchers report that Copy Fail is a straight-line logic flaw. It triggers without races, retries, or crash-prone timing windows.

🧬 Portability. The same exploit script works across all tested distributions and architectures, including Ubuntu, Amazon Linux, Red Hat Enterprise Linux (RHEL), and SUSE Linux Enterprise. No per-distribution offsets. No recompilation. No version checks in the exploit.

✧ Minimalism. The entire exploit is a short Python script using only standard library modules (os, socket, zlib). It requires Python 3.10+ for os.splice. No compiled payloads, no dependency installation.

🥷 Stealth. The write bypasses the ordinary VFS write path. The corrupted page is never marked dirty by the kernel's writeback machinery. Standard file integrity tools that compare on-disk checksums will not detect it, because the on-disk file remains unchanged. Only the in-memory page cache is corrupted.

📦 Cross-container impact. The page cache is shared across all processes on the system, including across container boundaries. Copy Fail is not just a local privilege escalation. It is a container escape primitive and a vector for Kubernetes node compromise.

How to fix the vulnerability?

To remediate the vulnerability, users need to update to Linux kernel versions 6.18.22, 6.19.12, and 7.0. The kernel can be built manually, or users can wait for their Linux distribution vendor to release updated kernel packages. As of May 4, updates have been released for Ubuntu, Debian, RHEL, Fedora, SUSE, CloudLinux, Arch Linux, and ROSA Linux.

As a workaround, researchers suggest blocking the creation of AF_ALG sockets:

echo "install algif_aead /bin/false" > /etc/modprobe.d/disable-algif-aead.conf
rmmod algif_aead 2>/dev/null
April "In the Trend of VM" (#26): one Microsoft SharePoint vulnerability

April In the Trend of VM (#26): one Microsoft SharePoint vulnerability

April "In the Trend of VM" (#26): one Microsoft SharePoint vulnerability. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. Once again, it is single-vendor, Microsoft-related, and this time it could not be more compact. While the previous March edition had four trending vulnerabilities, this April edition has only one. In the upcoming May edition, we expect at least three trending vulnerabilities. 😉

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

This vulnerability is from the January Microsoft Patch Tuesday:

🔻 RCE - Microsoft SharePoint (CVE-2026-20963). The vulnerability was initially considered less critical due to an authentication requirement PR:L, but after Microsoft’s reassessment it turned out that authentication is not required for exploitation PR:N. The vulnerability has been added to the CISA KEV, meaning attackers are already exploiting it in the wild. There are no public exploits yet.

🟥 The full list of trending vulnerabilities is available on the portal

April Linux Patch Wednesday

April Linux Patch Wednesday

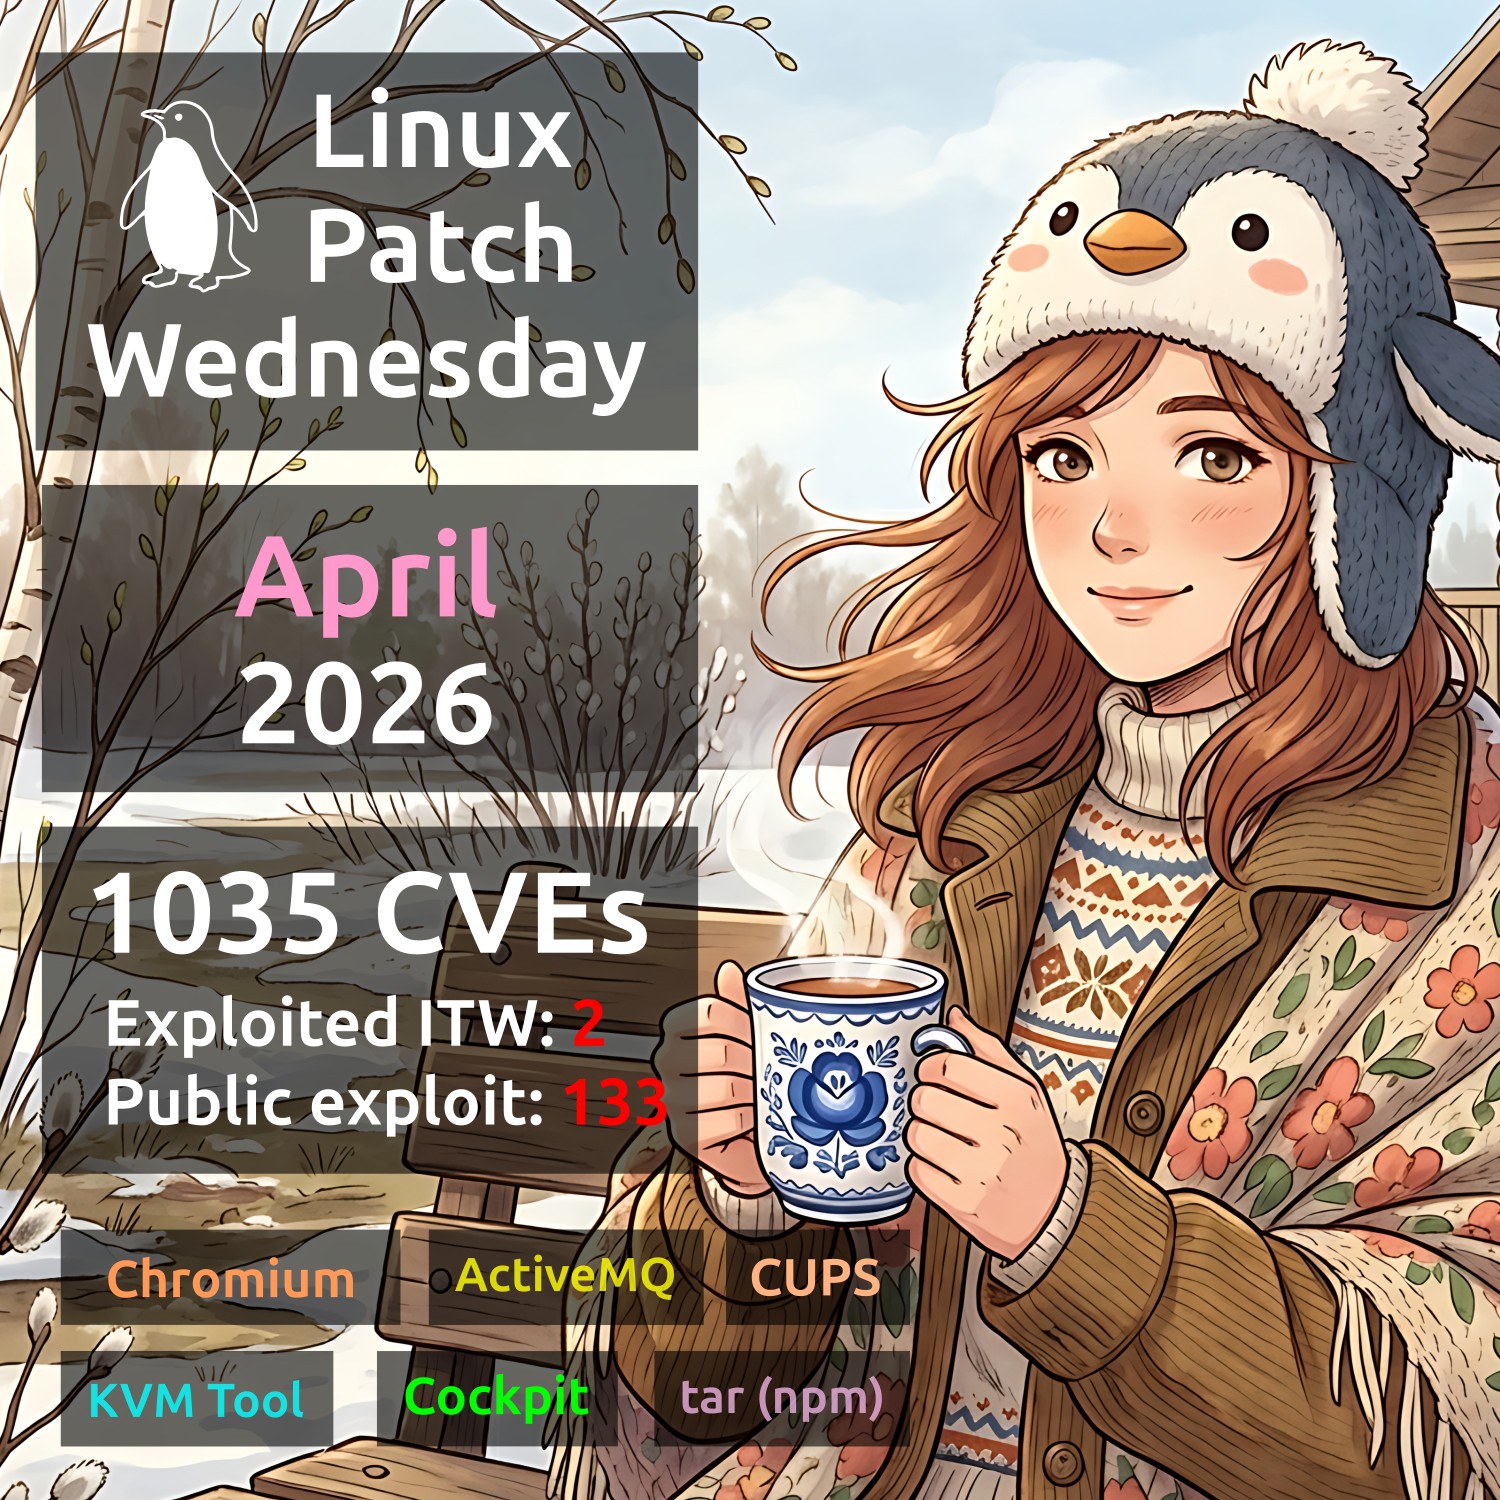
April Linux Patch Wednesday. In April, Linux vendors addressed 1,035 vulnerabilities - nearly twice as many as in March. One might assume that most of these would again be Linux Kernel vulnerabilities, but that's not the case! Linux Kernel vulnerabilities were relatively few - just 209. The remaining vulnerabilities are distributed across more than 200 affected products. Notably, two vulnerabilities show evidence of active exploitation in the wild:

🔻 RCE - Apache ActiveMQ (CVE-2026-34197). Remote code execution is possible via the Jolokia API (/api/jolokia/) with no authentication required. The vulnerability remained hidden in the codebase for 13 years before being discovered using AI. Listed in the CISA KEV since April 16. Numerous exploits are available on GitHub.

🔻 RCE - Chromium (CVE-2026-5281). A use-after-free vulnerability in Dawn (Chromium's graphics layer and WebGPU implementation) affects Google Chrome versions prior to 146.0.7680.178. A remote attacker who has gained control of the rendering process can execute arbitrary code via a specially crafted HTML page. Listed in the CISA KEV since April 1.

Public exploits are available, or signs of their existence have been observed, for another 133 (❗️) vulnerabilities. The most notable ones, in my opinion:

🔸 RCE - Cockpit (CVE-2026-4631). Cockpit is a web‑based tool for server administration in Linux systems, enabling users to manage servers, containers, storage, and network configurations through a browser interface. An attacker with network access to the Cockpit web service can send a single HTTP request to the login page, injecting malicious SSH options or commands and executing code on the Cockpit server - all without valid credentials.

🔸 RCE - CUPS (CVE-2026-34990 + CVE-2026-34980). CUPS (Common UNIX Printing System) is a printing system for Unix‑like operating systems, including Linux and macOS. A chain of these vulnerabilities allows a remote attacker without authentication to overwrite files with root permissions over the network, effectively gaining root access on a typical Linux system.

🔸 RCE - KVM Tool (CVE-2021-45464). KVM Tool is a lightweight tool for running virtual machines based on KVM (Kernel‑based Virtual Machine) in Linux. KVM Tool prior to commit 39181fc contains an out‑of‑bounds write vulnerability, allowing a guest OS user to execute arbitrary code on the host machine.

🔸 PathTrav - tar (npm) (CVE-2026-31802, CVE-2026-24842). Prior to version 7.5.11, the npm package allowed creating a symbolic link pointing outside the extraction directory, leading to file overwrites.

Other vulnerabilities worth paying attention to:

🔸 RCE - Handlebars (CVE-2026-33937), tiemu (CVE-2017-20225), Netwide Assembler (CVE-2026-6067), openexr (CVE-2026-34545), Axios (CVE-2026-40175), hdf5 (CVE-2026-29043)
🔸 CodeInj - GLPI (CVE-2025-66417), glances (CVE-2026-30930, CVE-2026-32611), Handlebars (CVE-2026-33938, CVE-2026-33940), dynaconf (CVE-2026-33154), icalendar (CVE-2026-33635)
🔸 SFB - ormar (CVE-2026-27953), cpp-httplib (CVE-2026-34441), Safari (CVE-2026-20643), rack (CVE-2026-34835), wolfssl (CVE-2026-5194), Traefik (CVE-2026-32695), glances (CVE-2026-32632, CVE-2026-32634), Vert.x-Web (CVE-2026-1002), ecdsa (CVE-2026-33936), glibc (CVE-2026-4438), incus (CVE-2026-33542), Mongoose (CVE-2026-2968)
🔸 AuthBypass - scitokens_cpp_library (CVE-2026-32725, CVE-2026-32726), Node.js pbkdf2 (CVE-2026-32633), rack-session (CVE-2026-39324), Traefik (CVE-2026-33433), grpc (CVE-2026-33186), nltk (CVE-2026-33231)
🔸 ArbFileWrite - Rust (CVE-2026-33056)
🔸 CmdInj - Netty (CVE-2026-33870), awstats (CVE-2025-63261)
🔸 EoP - Keycloak (CVE-2026-4636), QEMU (CVE-2026-33711), glances (CVE-2026-33641)

🗒 Full Vulristics report

About Remote Code Execution - Adobe Reader (CVE-2026-34621) vulnerability

About Remote Code Execution - Adobe Reader (CVE-2026-34621) vulnerability

About Remote Code Execution - Adobe Reader (CVE-2026-34621) vulnerability. Adobe Acrobat Reader (from 2003 to 2015, "Adobe Reader") is a free PDF viewer developed by Adobe. Versions are available for Windows, macOS, Android, and iOS. The remote code execution vulnerability in Adobe Acrobat for Windows and macOS is caused by improper handling of object prototype attributes (CWE-1321 - "Prototype Pollution"). Successful exploitation of the vulnerability allows an attacker to execute arbitrary code on the target system when the victim opens a specially crafted document.

👾 Researcher Haifei Li, the developer of EXPMON - a sandbox-based system designed to detect file-based zero-days and hard-to-detect exploits - reported the vulnerability and the existence of a working exploit on April 7. Earlier, on March 26, an unknown individual uploaded a malicious PDF sample named yummy_adobe_exploit_uwu.pdf to the public EXPMON service.

According to the analysis results, the sample behaved like an initial exploit capable of collecting and transmitting various types of information to the attacker, potentially followed by arbitrary code execution (RCE) and sandbox escape (SBX) exploits. It used a zero-day vulnerability in Adobe Reader that allowed it to invoke privileged Acrobat APIs. The exploit was confirmed to work on the latest version of Acrobat. Specifically, it abused the "util.readFileIntoStream()" API, which allows arbitrary files accessible to the isolated Reader process to be read from the local system. This enabled the malware to collect a wide range of information from the victim's machine and steal data from local files. The "RSS.addFeed()" API was used to send the collected information to a remote server and retrieve additional JavaScript code for execution. Such a mechanism allows attackers to gather user information, steal local data, perform advanced fingerprinting, and further develop the attack. If the target matched the attacker's criteria, an additional exploit could then be delivered to achieve RCE or SBX. However, during testing, the researcher was unable to obtain the additional exploit payload - although the server was reachable, it did not respond. This may have been caused by several factors. For example, the local testing environments may not have matched the specific criteria expected by the attacker.

On April 8, another malicious file sample was discovered on VirusTotal. The file had originally been uploaded on November 28, 2025, indicating that this 0day/APT campaign had been active for at least four months.

On April 9, researcher Gi7w0rm reported signs of active exploitation of the vulnerability in attacks. The attacks used malicious Russian-language documents disguised as materials related to Russia's oil and gas sector as phishing lures. Based on the observed targeting, the campaign appears to have been aimed at specific Russian organizations.

On April 13, the vulnerability was added to the CISA KEV catalog.

⚙️ The Adobe security bulletin was published on April 12. Affected versions include Acrobat DC 26.001.21367 and earlier, Acrobat Reader DC 26.001.21367 and earlier, and Acrobat 2024 24.001.30356 and earlier. The vulnerability has been fixed in Acrobat DC 26.001.21411, Acrobat Reader DC 26.001.21411, and Acrobat 2024 (Windows: 24.001.30362/Mac: 24.001.30360).

Adobe recommends that users of affected versions update their applications via “Help > Check for Updates”, which triggers the automatic update process. Alternatively, users can download the Acrobat Reader installer directly from Adobe's official portal.

The bulletin notes that Adobe is aware of active exploitation of vulnerability CVE-2026-34621 in the wild.

🛠 No public exploits have been observed so far.

💡 PDF files received from untrusted or unexpected sources should always be treated with caution and opened in isolated (sandboxed) environments. 😉