Tag Archives: Nessus

What's wrong with patch-based Vulnerability Management checks?

What’s wrong with patch-based Vulnerability Management checks? My last post about Guinea Pigs and Vulnerability Management products may seem unconvincing without some examples. So, let’s review one. It’s a common problem that exists among nearly all VM vendors, I will demonstrate it on Tenable Nessus.

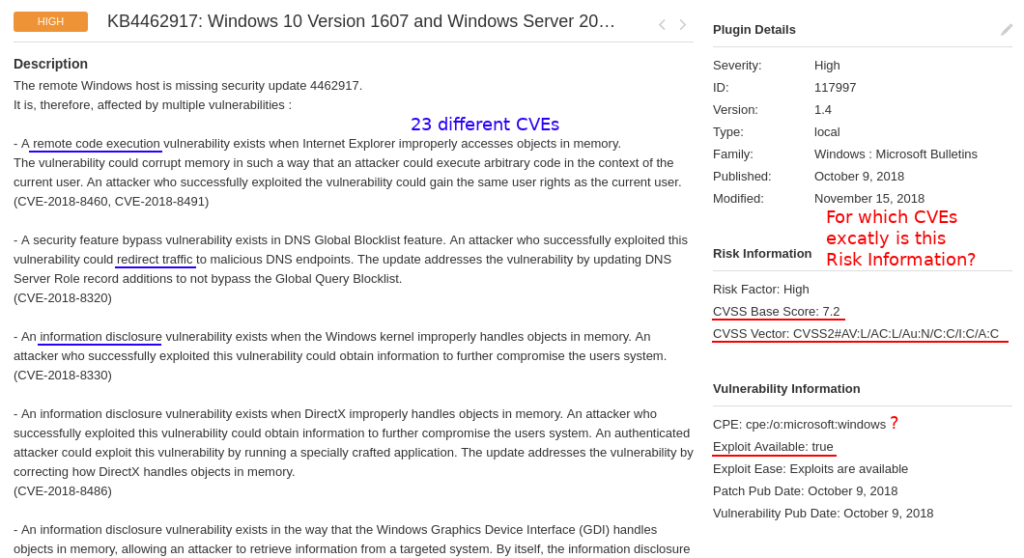
If you perform vulnerability scans, you most likely seen these pretty huge checks in your scan results like “KB4462917: Winsdows 10 Version 1607 and Windows Server 2016 October 2018 Security Update“. This particular Nessus plugin detects 23 CVEs at once.
What's wrong with patch-centric Vulnerability Management?

And, as you can see, it has formalized “Risk Information” data in the right column. There is only one CVSS score and vector, one CPE, one exploitability flag, one criticality level. Probably because of architectural limitations of the scanner. So, two very simple questions:

  • for which CVE (of these 23) is this formalized Risk Information block?
  • for which CVE (of these 23) exploit is available?

Ok, maybe they show CVSS for the most critical (by their logic) CVE. Maybe they somehow combine this parameter from data for different CVEs. But in most cases this will be inaccurate. Risk information data for every of these 23 vulnerabilities should be presented independently.

As you can see on the screenshot, one of these vulnerabilities is RCE the other is Information Disclosure. Vulnerability Management solution tells us that there is an exploit. Is this exploit for RCE or DoS? You should agree, that it can be crucial for vulnerability prioritization. And more than this, in the example there are 7 different RCEs in Internet Explorer, MSXML parser, Windows Hyper-V, etc. All this mean different attack scenarios. How is it possible to show it Vulnerability Scanner like one entity with one CVSS and exploitability flag? What can the user get from this? How to search in all this?
Continue reading →

New Advanced Dynamic Scan Policy Template in Nessus 8

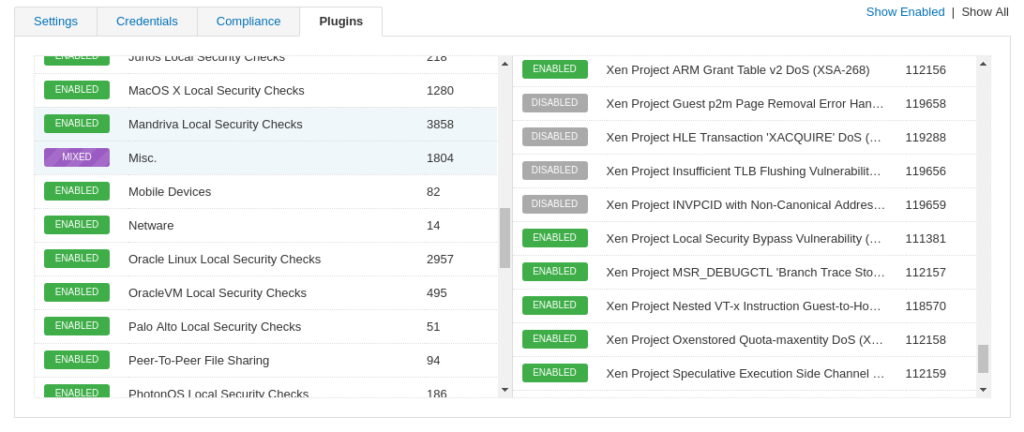
New Advanced Dynamic Scan Policy Template in Nessus 8. According to Nessus 8.1.0 release notes, Tenable finally solved the problem with Mixed Plugin groups. At least partially. I will briefly describe the problem. Let’s say we found out that some Nessus plugins crash our target systems. This happens rarely, but it happens. So, we decided to disable these plugins in the scan policy:

Mixed Plugins

Ok, problem is solved. But here is the question: what will happen with the new NASL plugins that will be added by Tenable in the same group, for example Misc.?

The answer is quite sad: Nessus doesn’t know if they should enabled of disabled, so they will be disabled in the scan policy by default. And this can lead to some False-Negatives. For example, on this screenshot you can see a fresh plugin “Xen Project Guest p2m Page Removal Error Handling DoS (XSA-277)” Published: December 13, 2018 was automatically disabled.

Previously, it was necessary to monitor this situation and add these plugins to Enabled manually or via API. But now with a new Dynamic Scan Policy template, this might be changed.

Continue reading →

Adding custom NASL plugins to Tenable Nessus

Adding custom NASL plugins to Tenable Nessus. Making custom NASL scripts (plugins) for Nessus is a pretty complicated process. Basically, NASL (Nessus Attack Scripting Language) is an internal instrument of Tenable and it seem that they are not really interested in sharing it with the community. The only publicly available official documentation, NASL Reference Guide and NASL2 reference manual, was written at least 13 years ago. Certainly many things changed since then in the actual product.

Adding custom NASL plugins to Tenable Nessus

However, it’s still possible to add custom NASL scripts into the plugin set of your Nessus server. Let’s see how to do it. Everything was tested in the latest Nessus 8.

Continue reading →

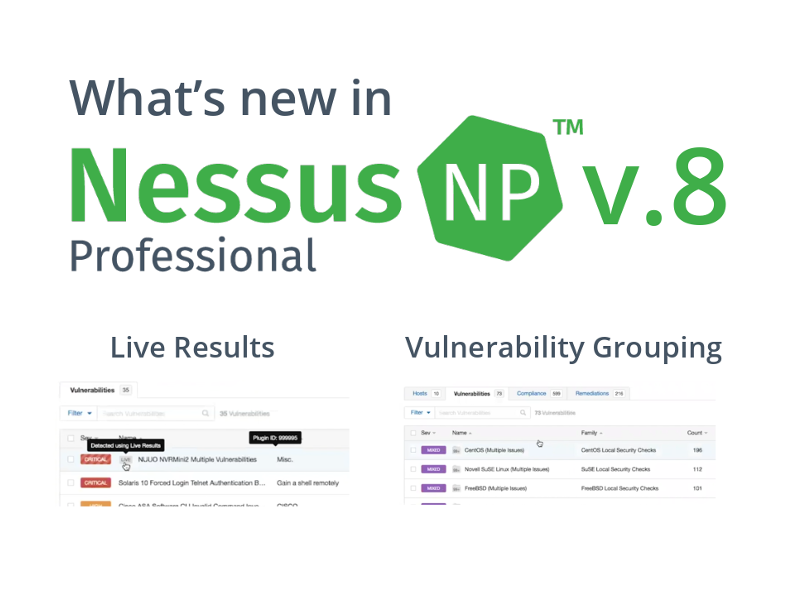
What's new in Nessus 8

What’s new in Nessus 8. Today Tenable released a new version of their famous vulnerability scanner – Nessus 8. The existing scanner nodes don’t see the updates yet, but the installation binaries are already available. So you may try to install it.

What's new in Tenable Nessus 8

This major release will be way more positive than the previous one. Of course Tenable did NOT return the multi-user mode and API in Nessus Professional. But on the other hand, they did NOT cut the functionality even further. They even added new features in GUI. And, what is the most important, they did NOT switch to the assets-based licensing (at least yet). 🙂

Continue reading →

Asset Inventory for Internal Network: problems with Active Scanning and advantages of Splunk

Asset Inventory for Internal Network: problems with Active Scanning and advantages of Splunk. In the previous post, I was writing about Asset Inventory and Vulnerability Scanning on the Network Perimeter. Now it’s time to write about the Internal Network.

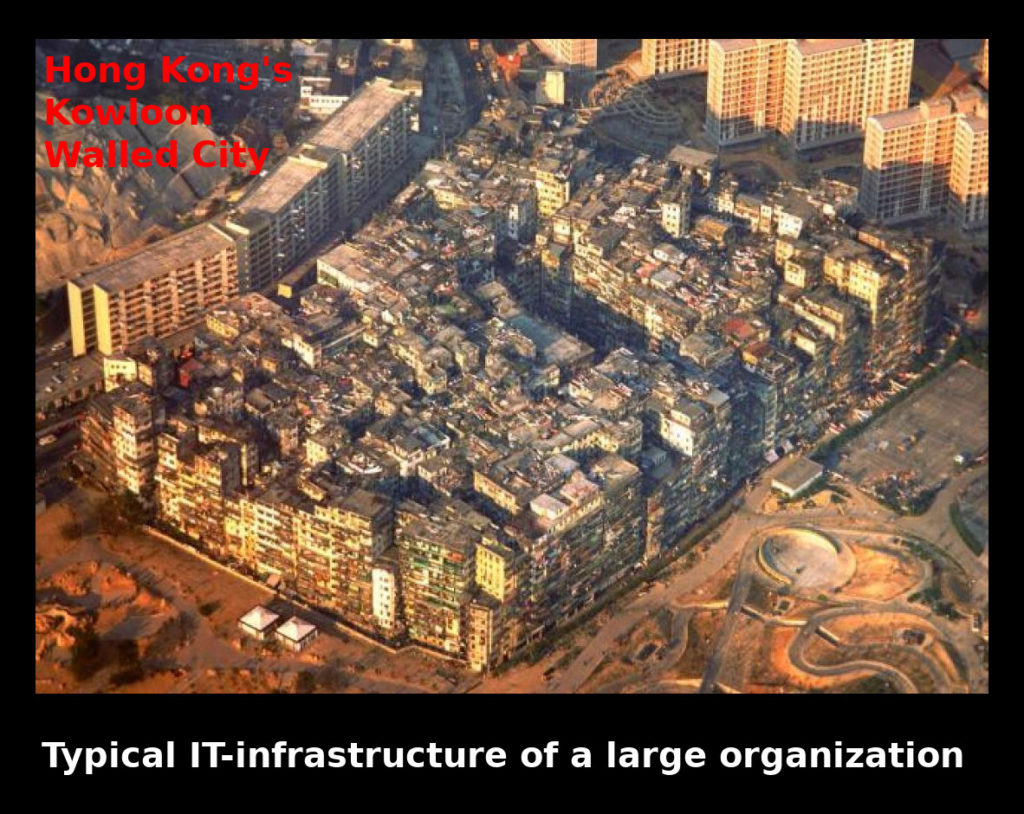
Typical IT-infrastructure of a large organization

I see a typical IT-infrastructure of a large organization as monstrous favela, like Kowloon Walled City in Hong Kong. At the beginning it was probably wisely designed, but for years it  was highly effected by spontaneous development processes in various projects as well as multiple acquisitions. And now very few people in the organization really understand how it all works and who owns each peace.

There is a common belief that we can use Active Network Scanning for Asset Inventory in the organization. Currently, I’m not a big fan of this approach, and I will try to explain here the disadvantages of this method and mention some alternatives.

Continue reading →

Asset Inventory for Network Perimeter: from Declarations to Active Scanning

Asset Inventory for Network Perimeter: from Declarations to Active Scanning. In the previous post, I shared some of my thoughts about the good Asset Inventory system. Of course, for me as a Security Specialist, it would be great if IT will provide such magical system. 🙂 But such an ideal situation is rarely possible. So now let’s see how to build an Asset Inventory system using the resources of Information Security team.

There are no special secrets. It’s necessary to get information about the assets from all available IT systems and then get the rest of the data using our own Assessment tools. I would like to start with hosts on Network Perimeter. The Network Perimeter targets are available at any time for hacker attacks, that’s why this part of the network is the most critical.

Asset Inventory for Network Perimeter

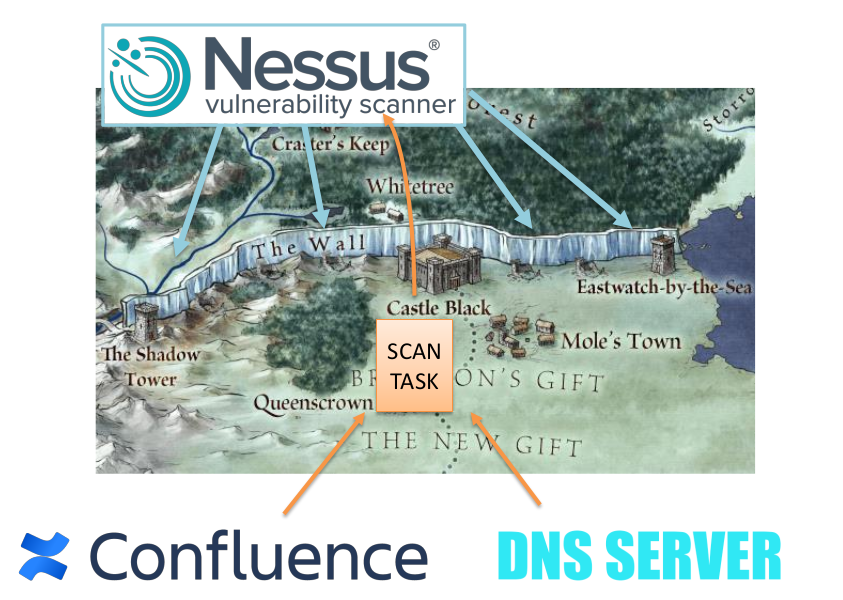
Network Perimeter is like the Wall in the Game of Thrones. The same white walkers are hiding behind the wall and our task is to find the breaches in the wall faster than potential intruders. “Night gathers, and now my watch begins”. (c)

Perimeter is changing constantly. And we should understand at any time what hosts are currently exposed in every office and every external hosting platform.

We can get information about external hosts using some Vulnerability Scanner located on external host in the Internet. I have already wrote about it briefly in  Vulnerability Management for Network Perimeter. Here I would like focus on how we can understand which hosts should be scanned and what useful information we can get from the raw scan results.

Continue reading →

Free High-Tech Bridge ImmuniWeb Application Discovery service

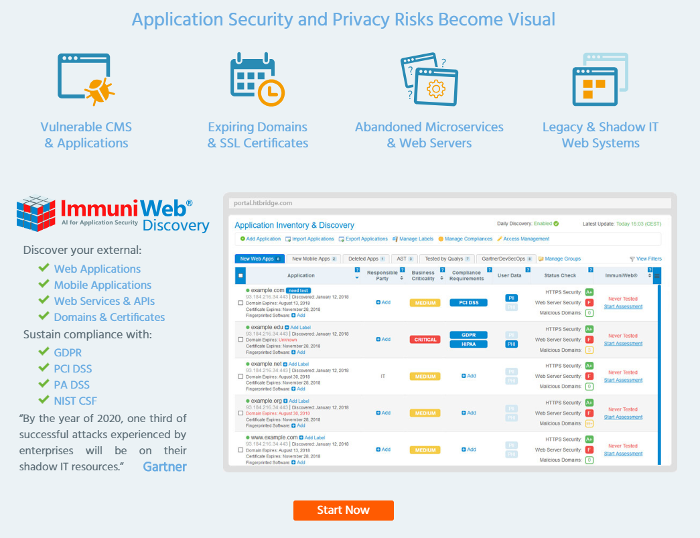
Free High-Tech Bridge ImmuniWeb Application Discovery service. Today I would like to talk about another service for application security analysis by High-Tech Bridge. It’s called ImmuniWeb Application Discovery.

This service can get information about your web and mobile applications available from the Internet. Believe me, this is not so obvious for a large organization. And, what is especially pleasant, it works automatically and free of charge. 😉

High-Tech Bridge ImmuniWeb Free Application Discovery

ImmuniWeb Application Discovery will also show the basic security problems with SSL connection, web-server headers, potential phishing issues for all founded web services. You can read more about this part in my posts about High-Tech Bridge services and APIs for SSL/TLS server testing and for searching cybersquatting, typosquatting and phishing domains.

From the same interface you can order an advanced audit of your web applications by High-Tech Bridge as well.

Continue reading →